

CredNinja
 raikia/credninja
A multithreaded tool designed to identify if credentials are valid, invalid, or local admin valid credentials within a network at-scale via SMB, plus…
information-gatheringlateral-movementpenetration-testing
raikia/credninjaA multithreaded tool designed to identify if credentials are valid, invalid, or local admin valid credentials within a network at-scale via SMB, plus…
 dafthack/check-localadminhash
Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 spiderlabs/portia
Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…
 punk-security/smbeagle
SMBeagle - Fileshare auditing tool.
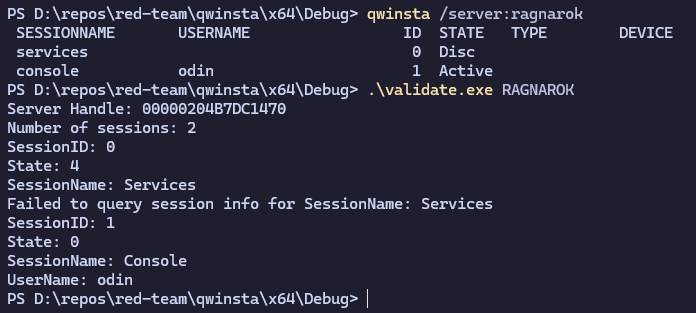 0xv1n/remotesessionenum
Remotely Enumerate sessions using undocumented Windows Station APIs
 34zy/nerv0usr4bbit
Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
 k8gege/ladon
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
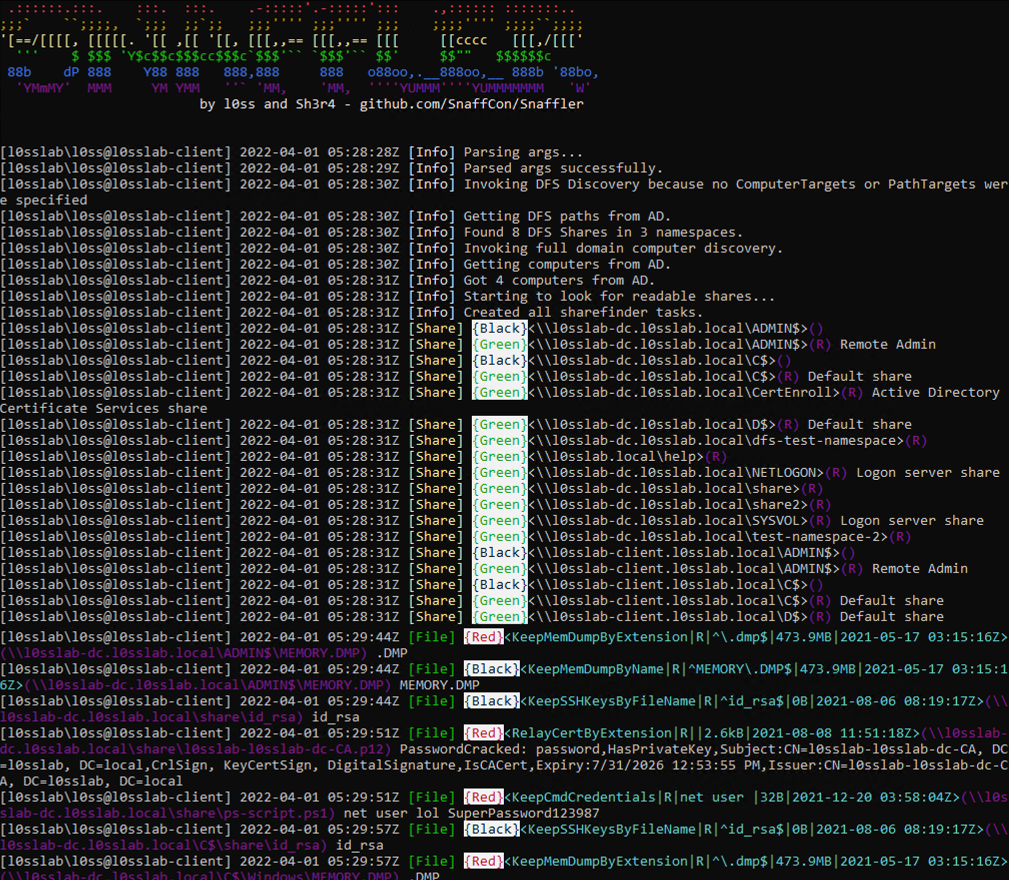 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 tevora-threat/sharpview
C# implementation of harmj0y's PowerView
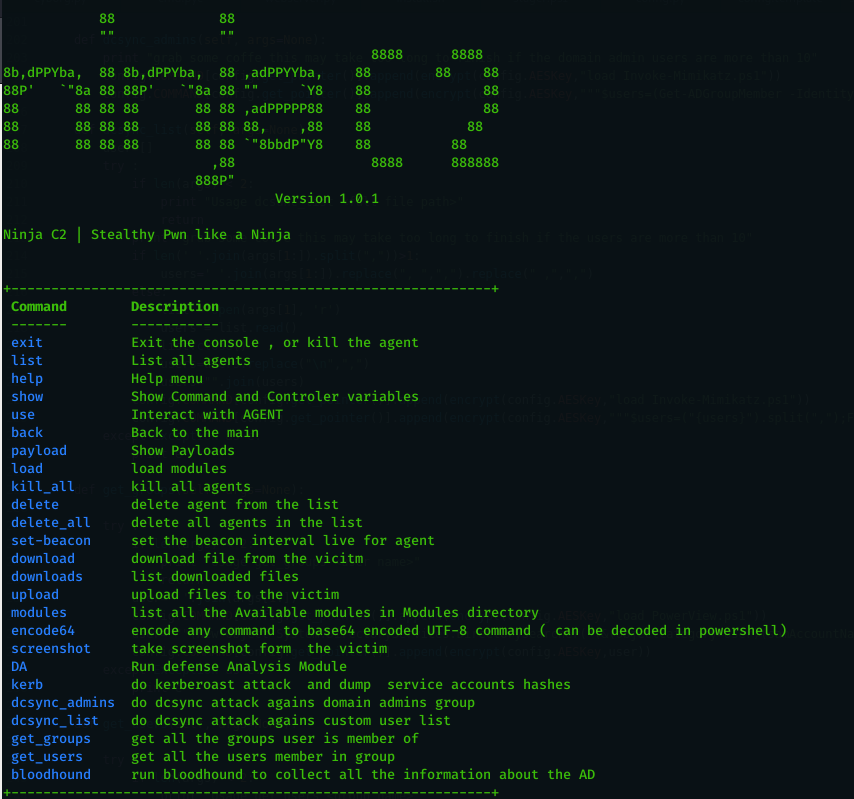 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…