DEFCON-CICD-pipelines-workshop

Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…

Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…

POC for CVE-2025-33053 WebDav Exploit, demonstrating how the vulnerability can be triggered in a real environment. This repository focuses on…

Docker CVE-2022-37708

ingress-nginx admission controller RCE escalation PoC

AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…

Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.

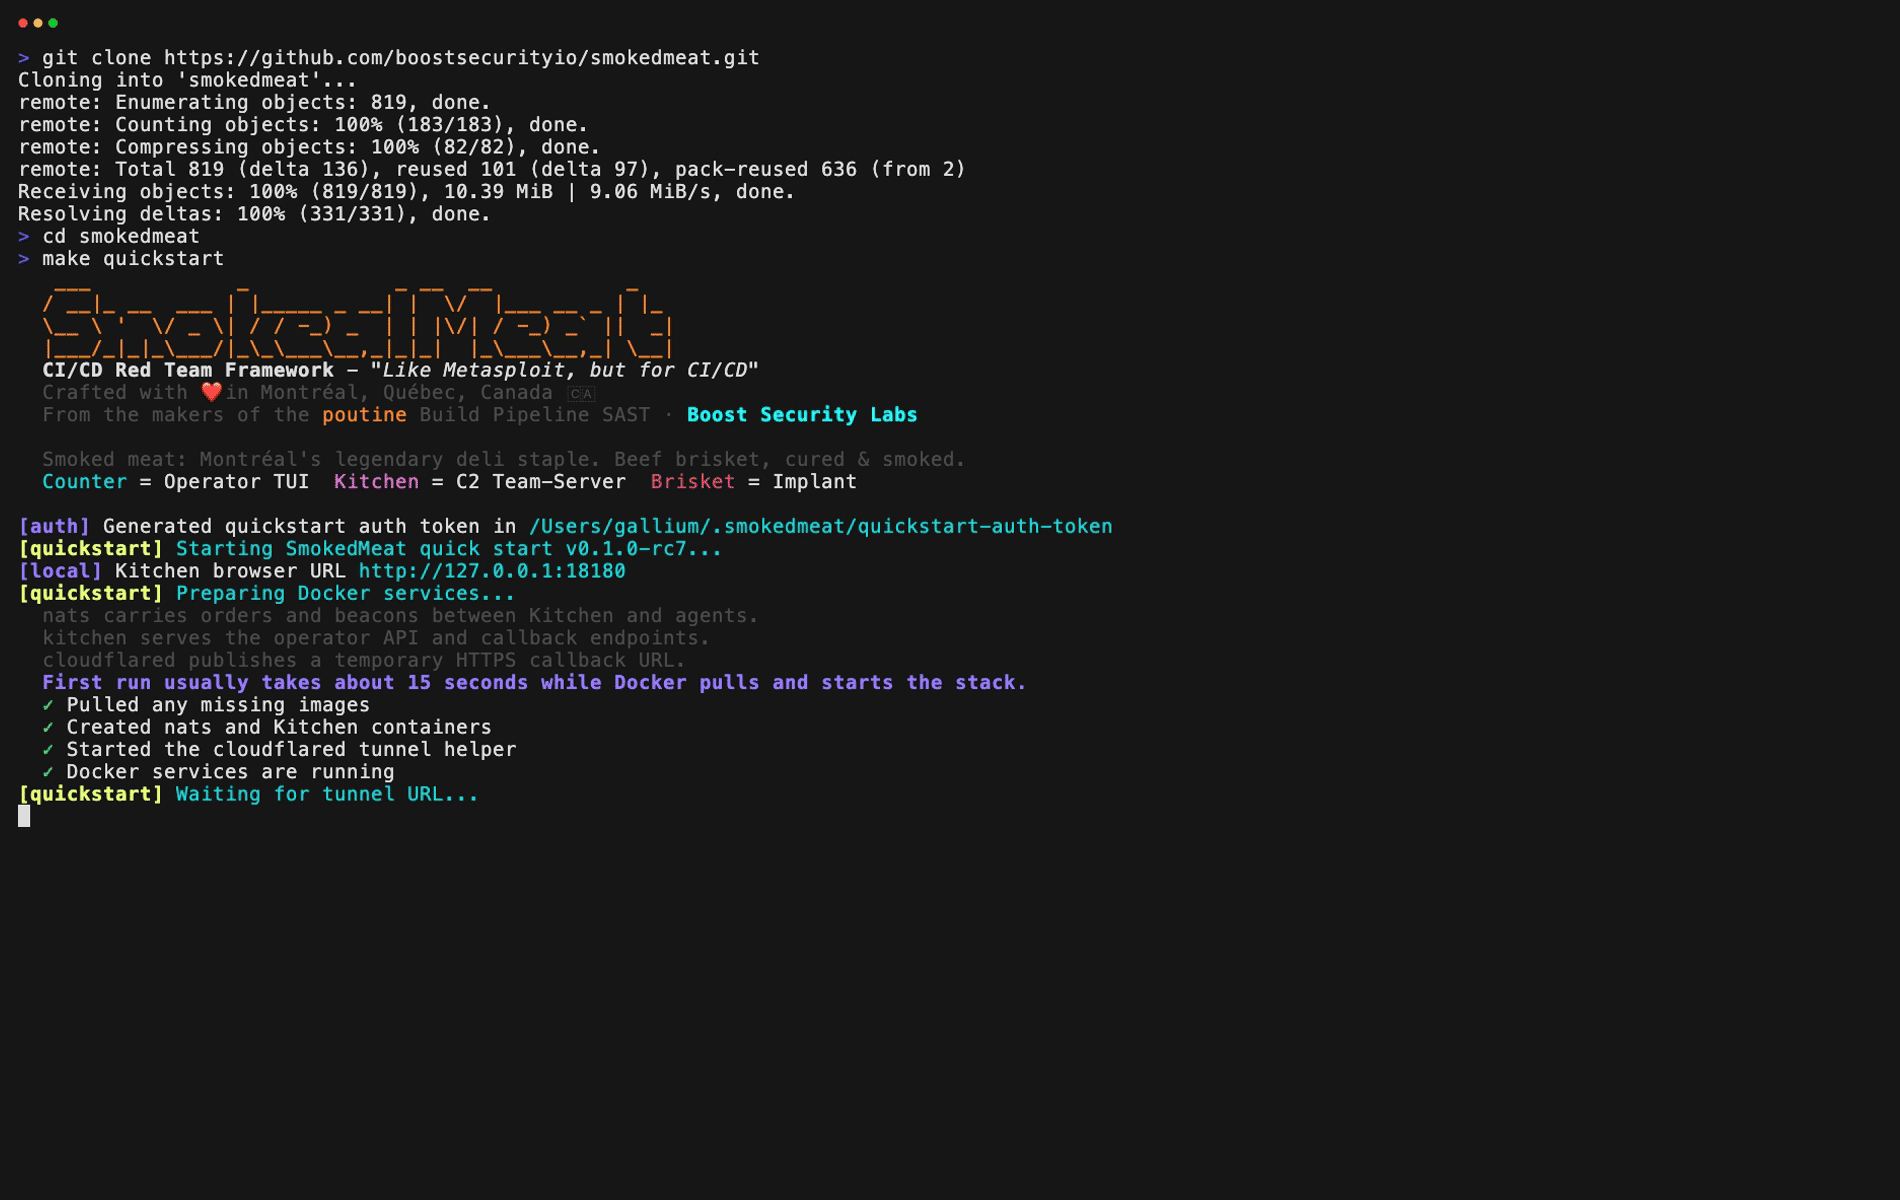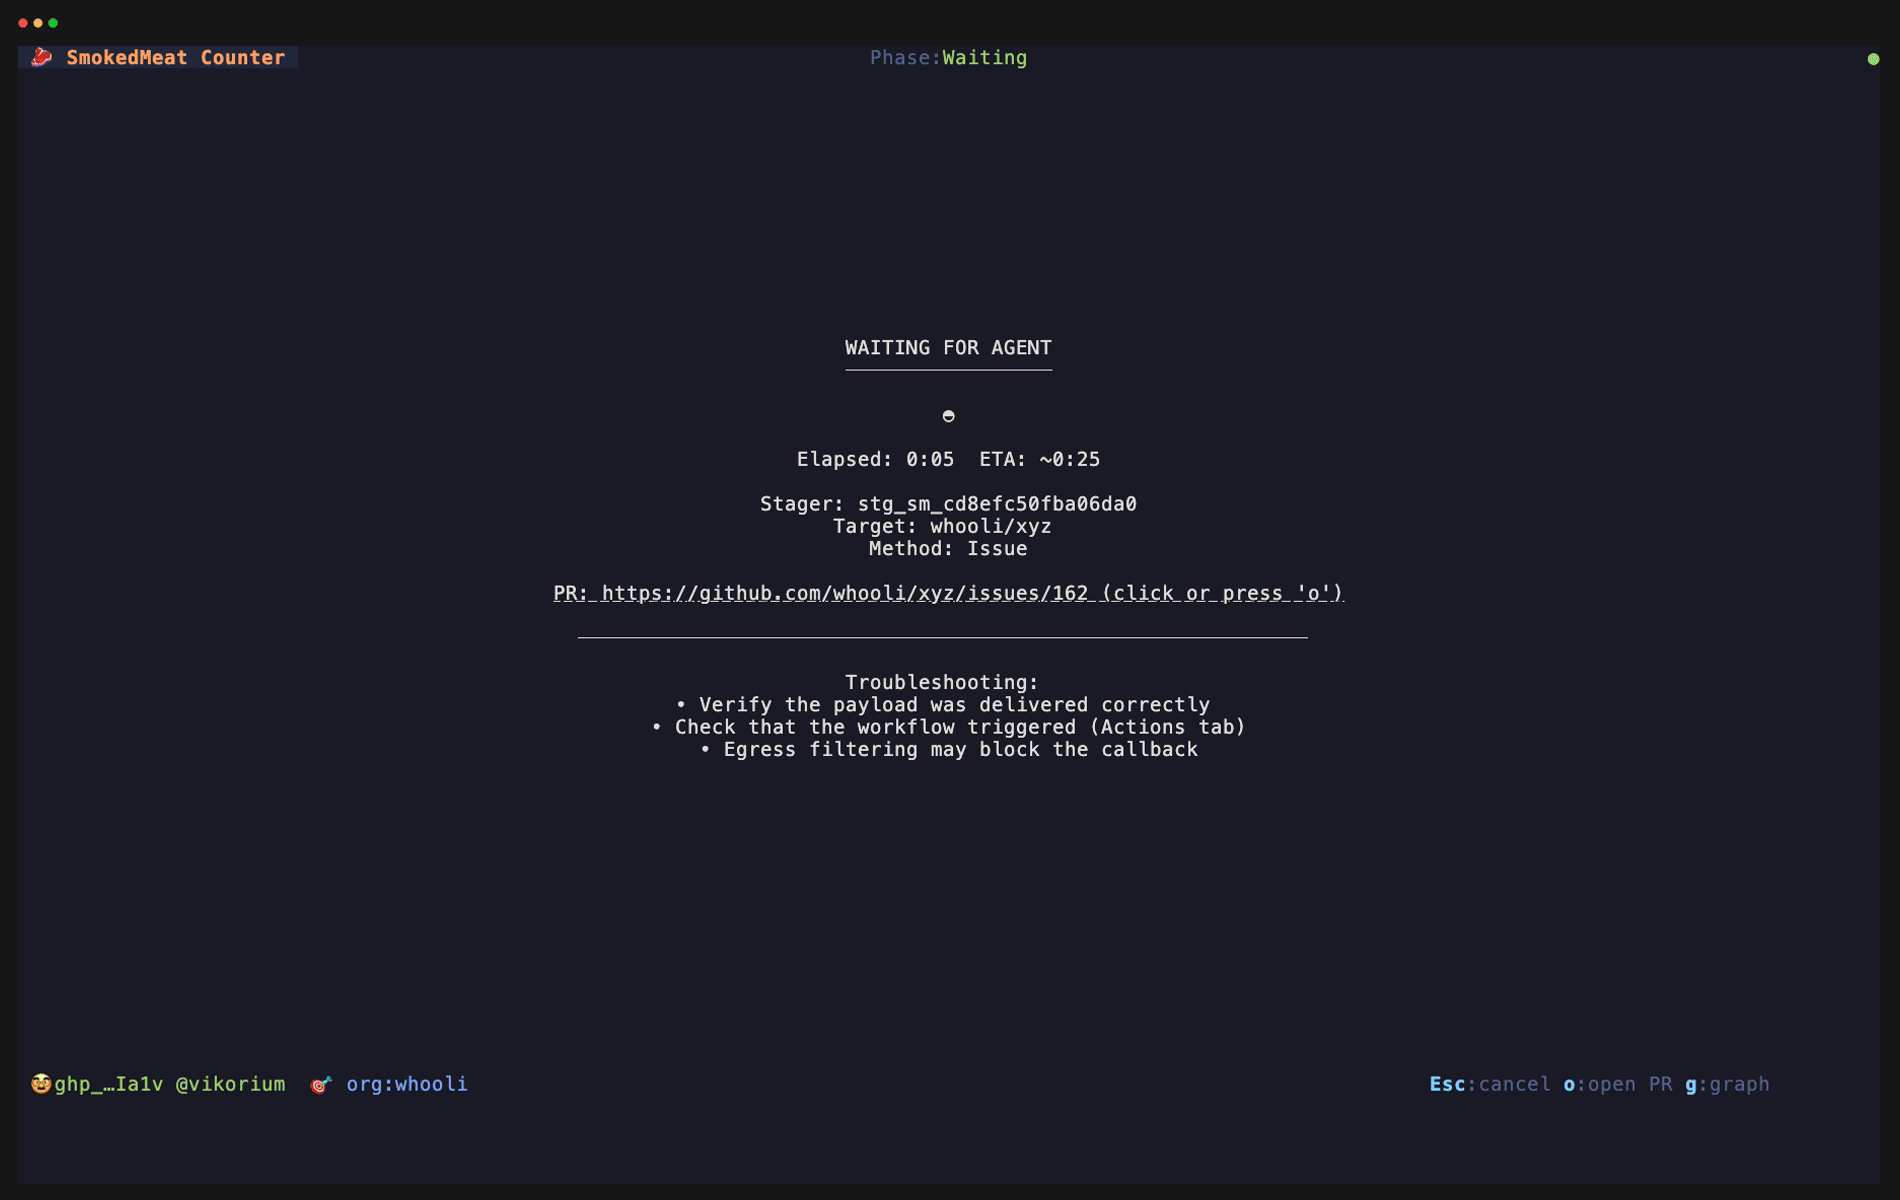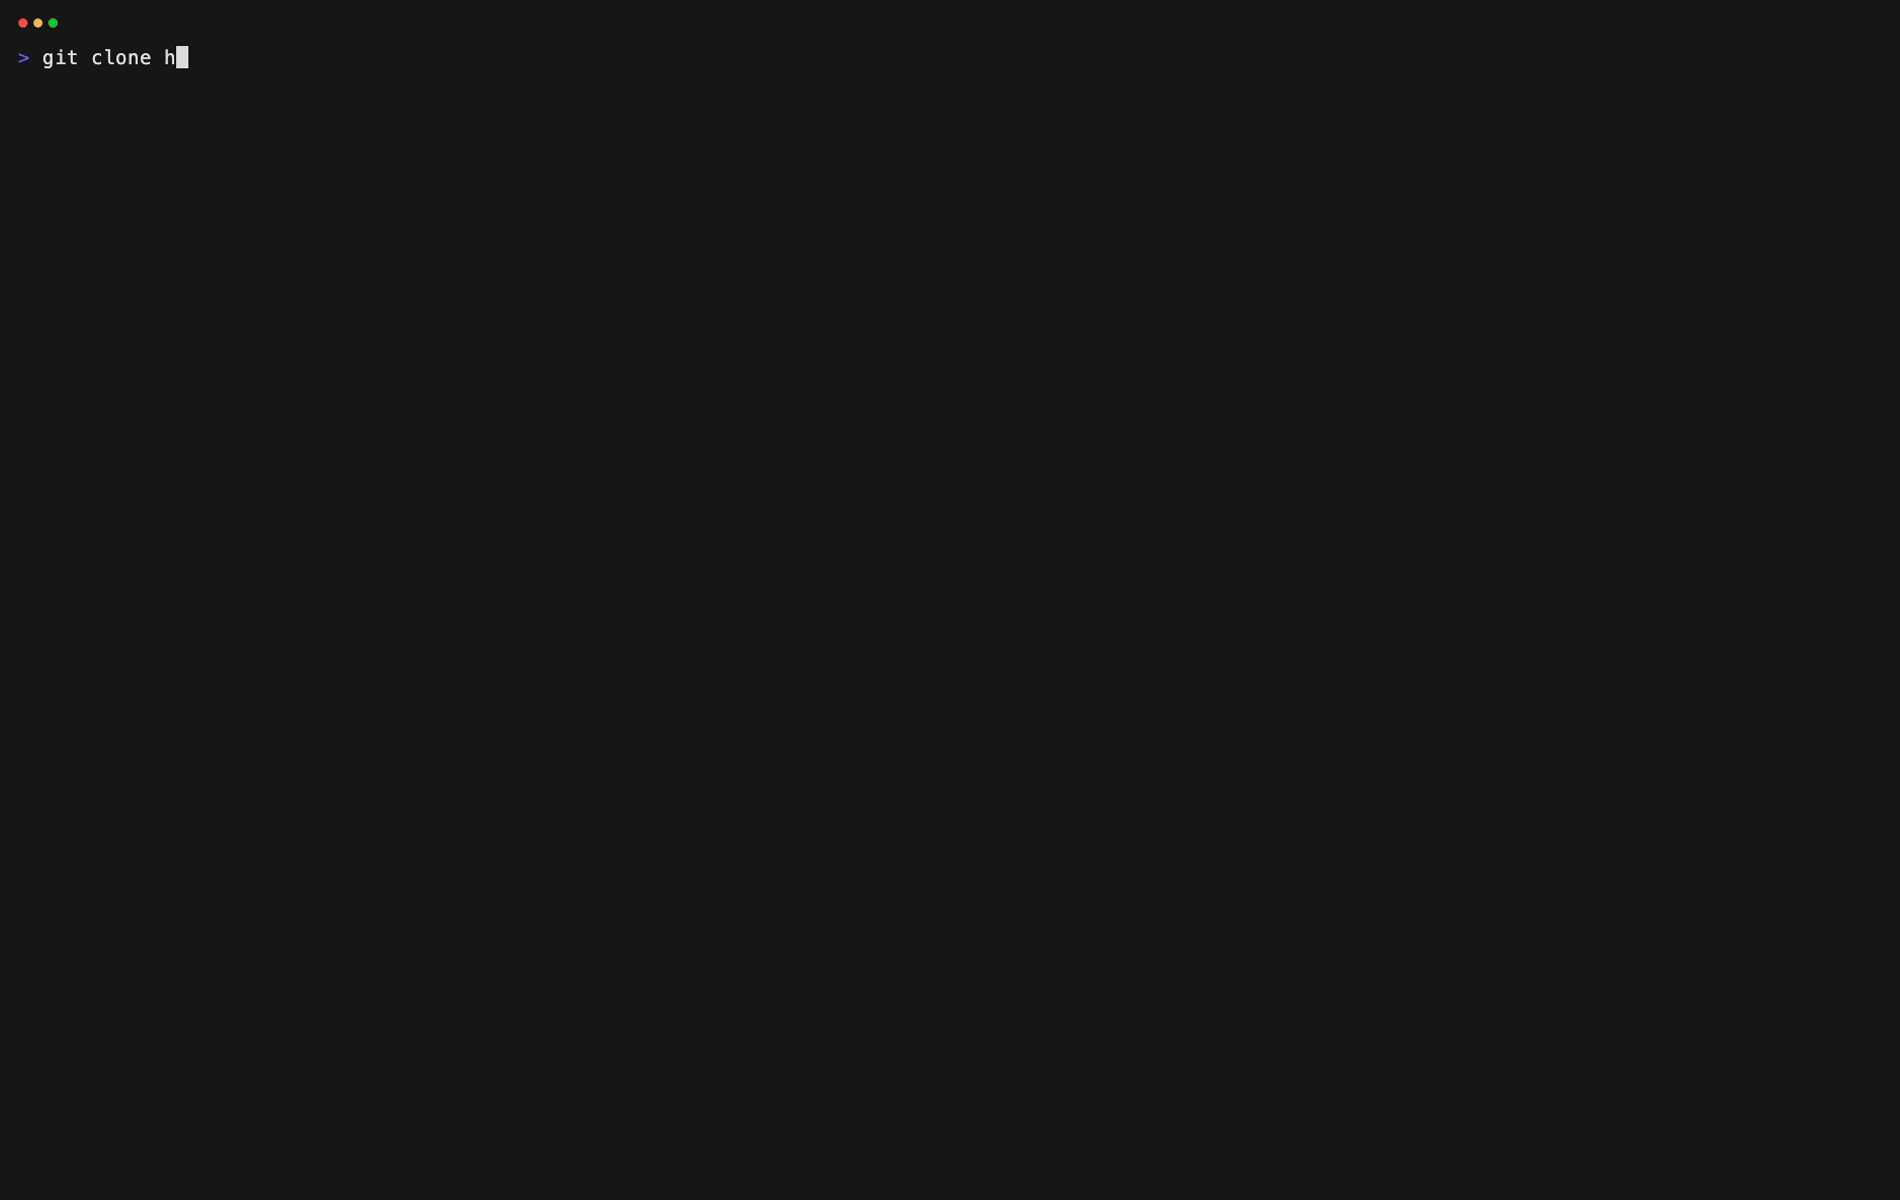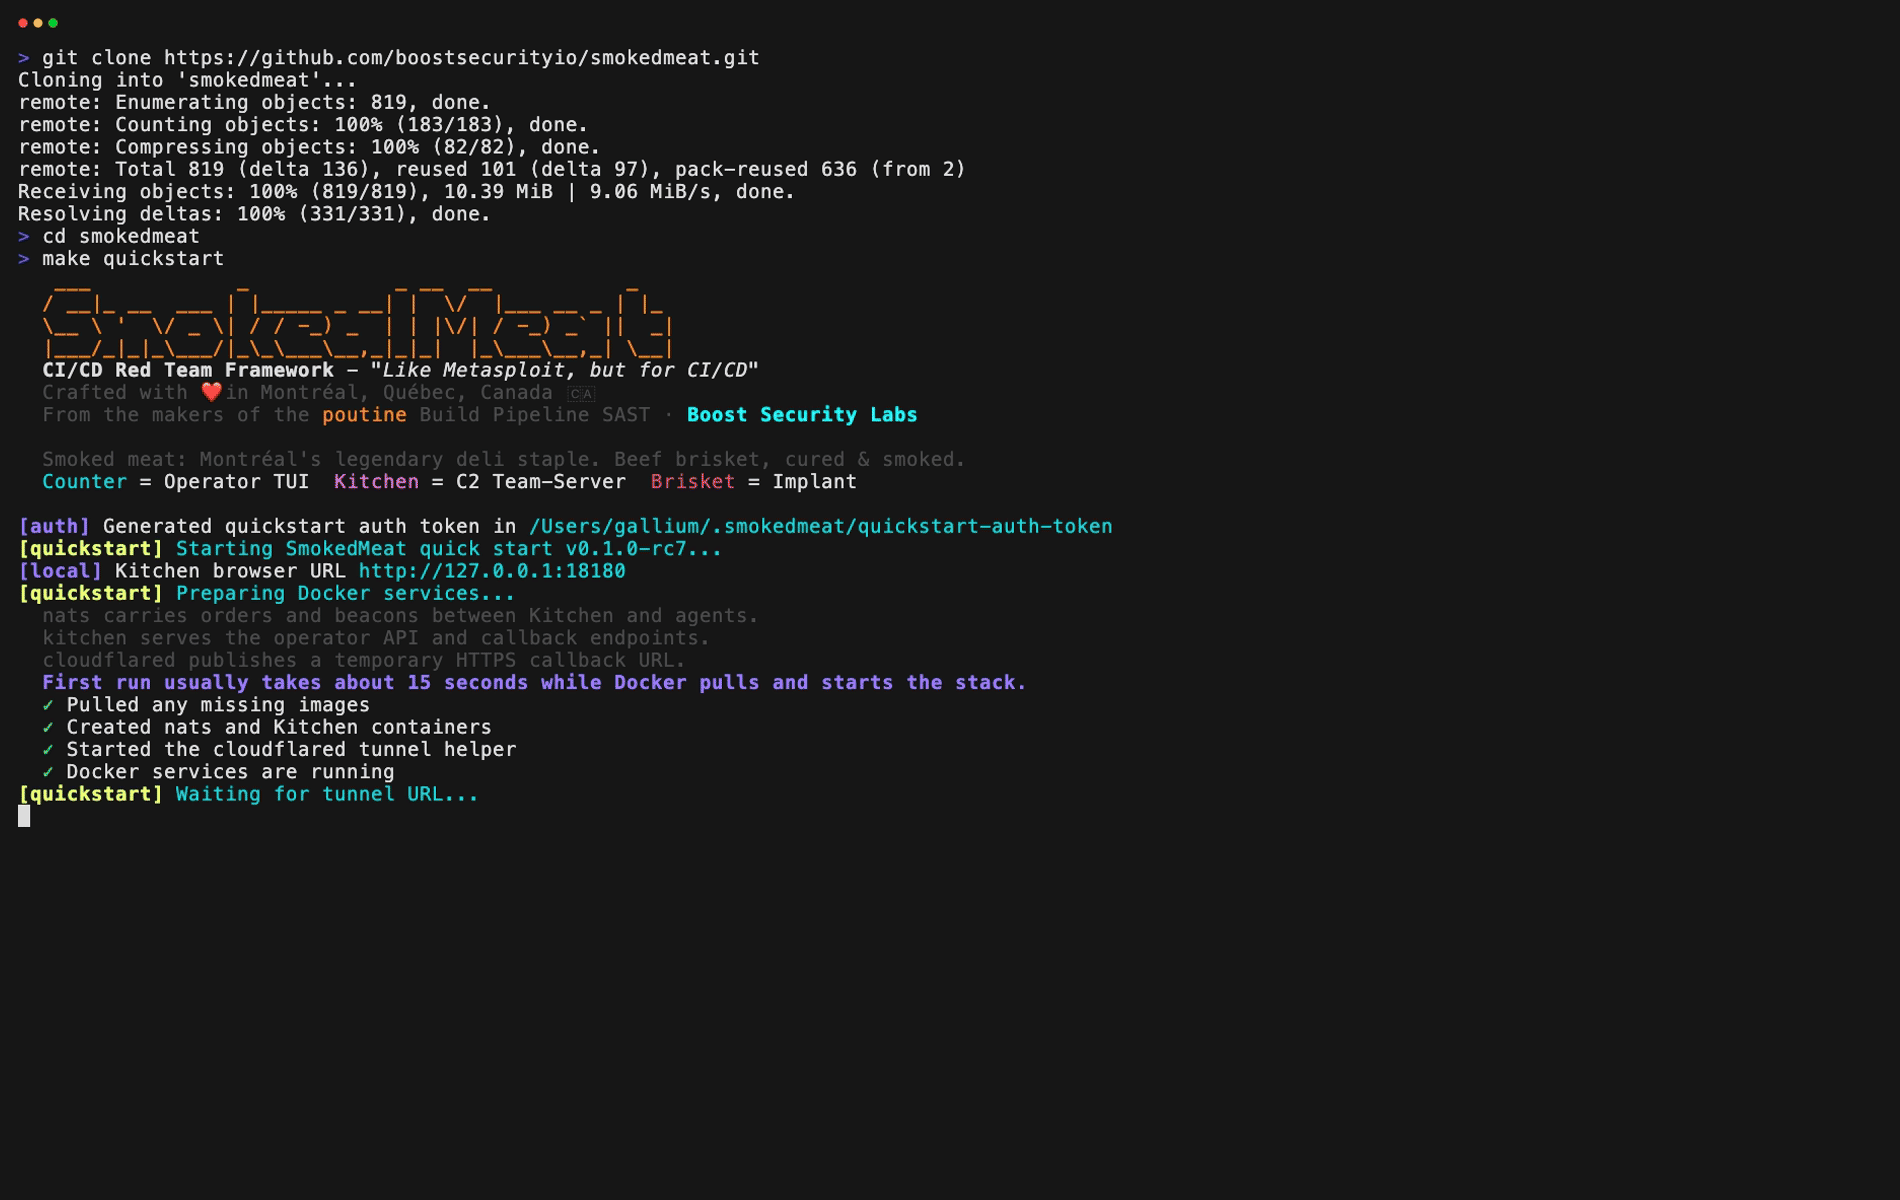
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…

Autonomous Hacking Agent for Red Team


R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

SMBeagle - Fileshare auditing tool.

Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…

CVE-2021-21220 Exploitation infrastructure