
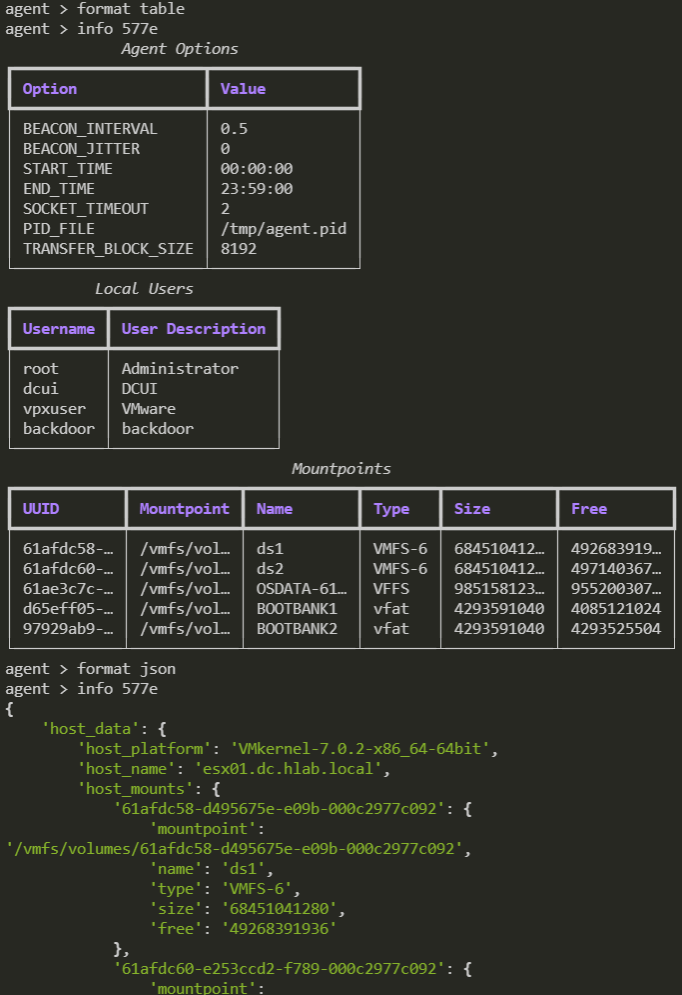
reave
 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
command-and-controldata-exfiltrationexploit-frameworks+8
psmths/reaveWIP Post-exploitation framework tailored for hypervisors.
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
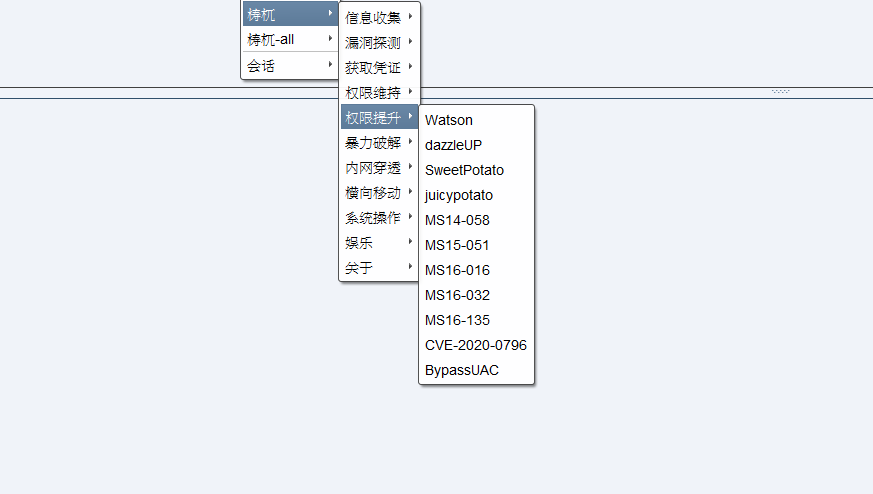 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
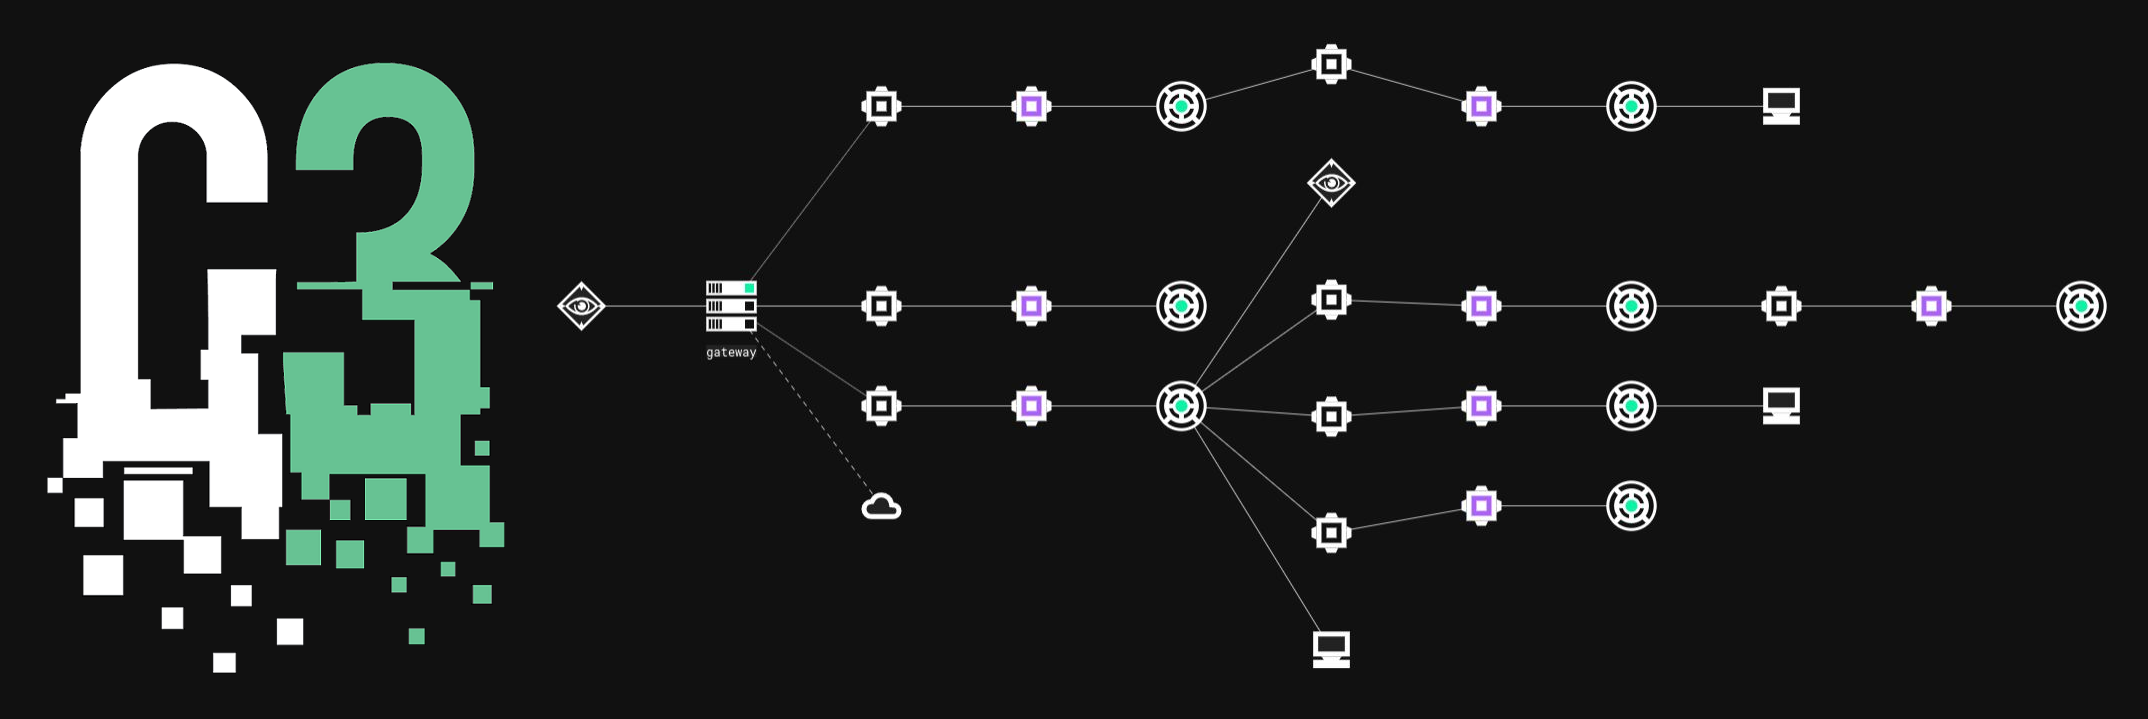 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
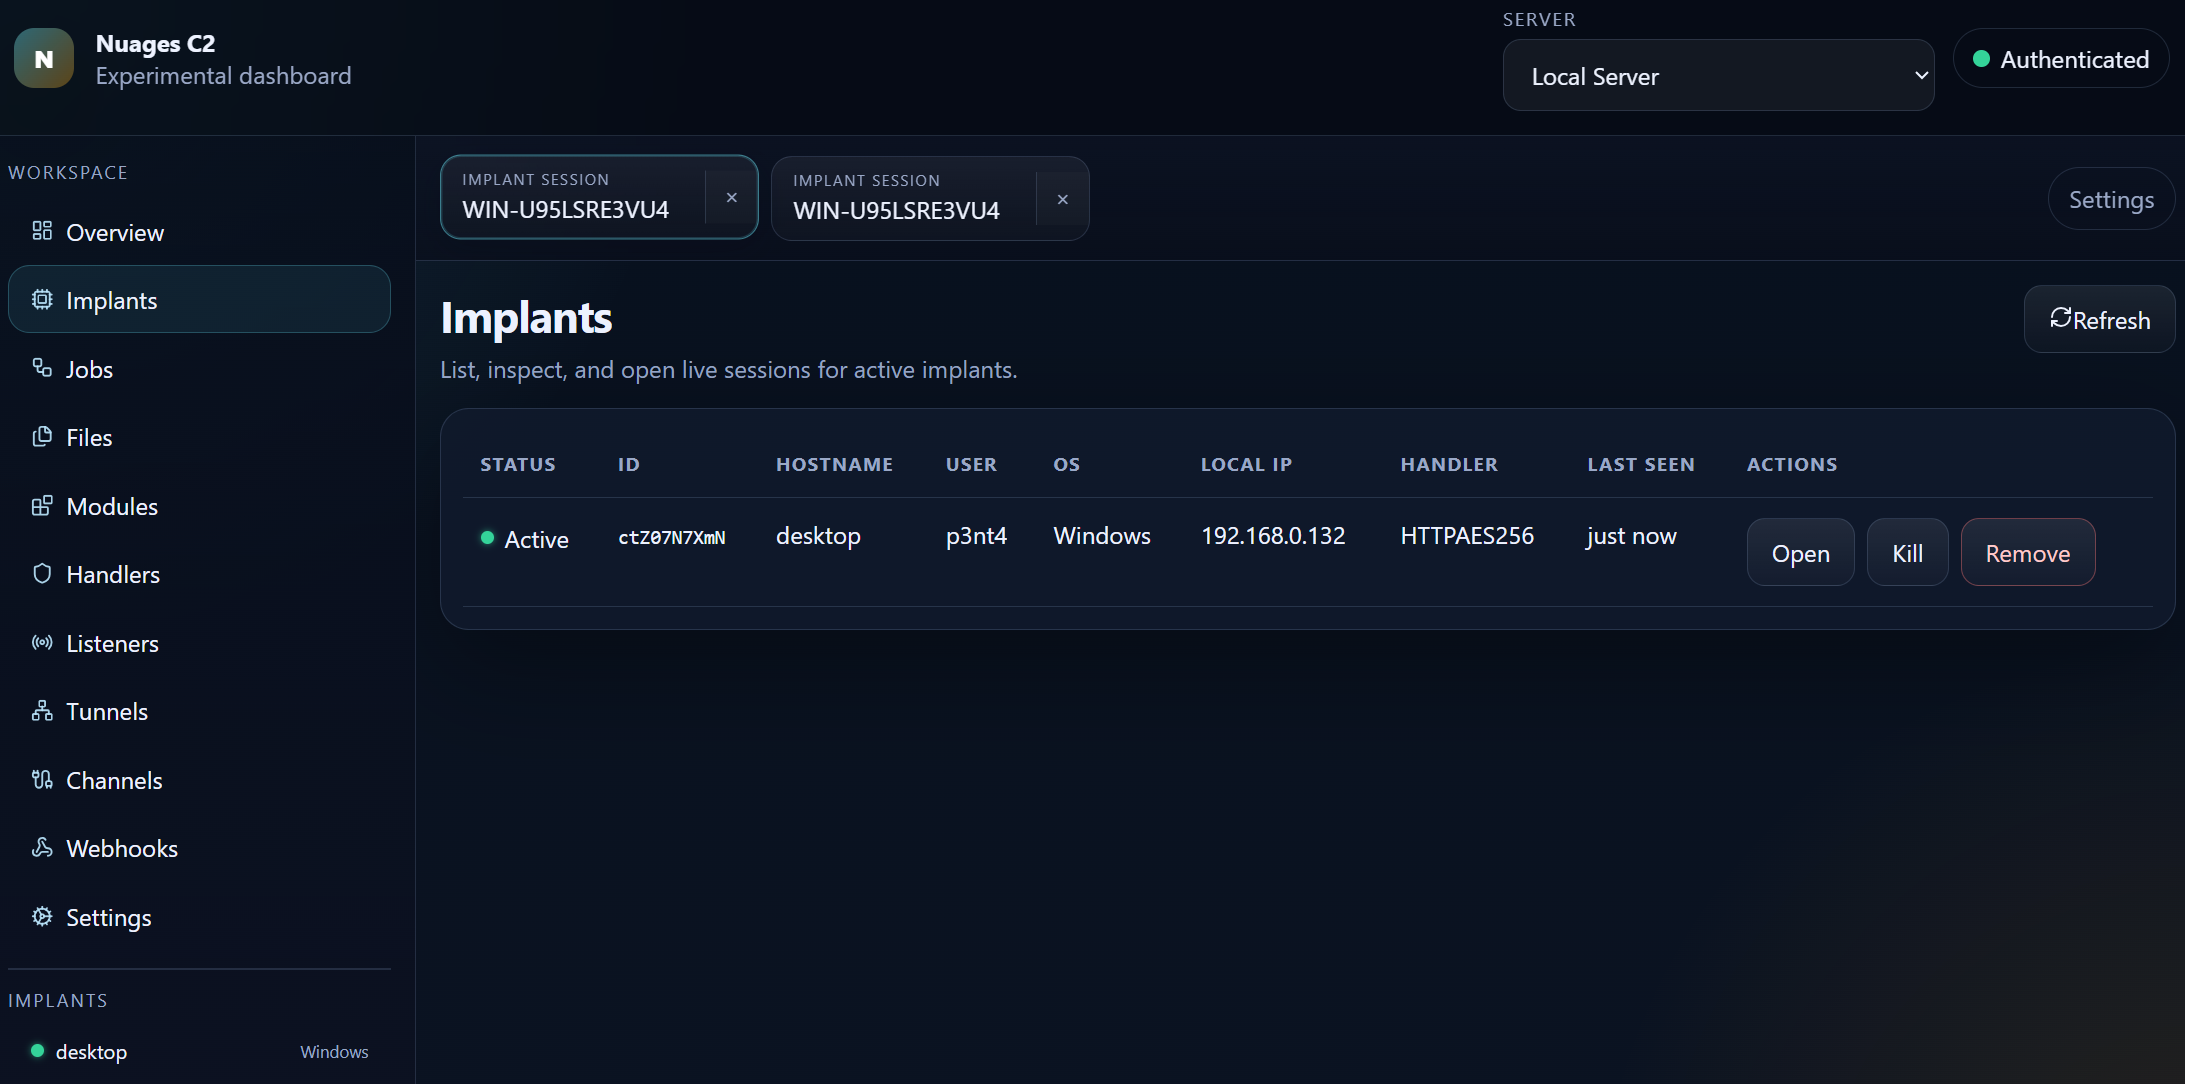
 dragoqcc/cruciblec2
A C# Command & Control framework
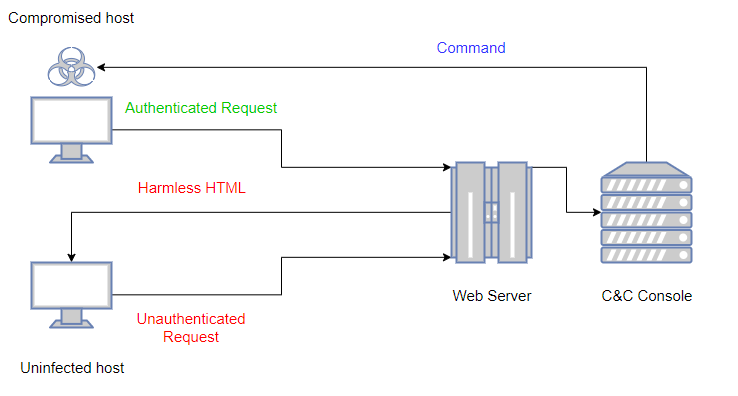 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
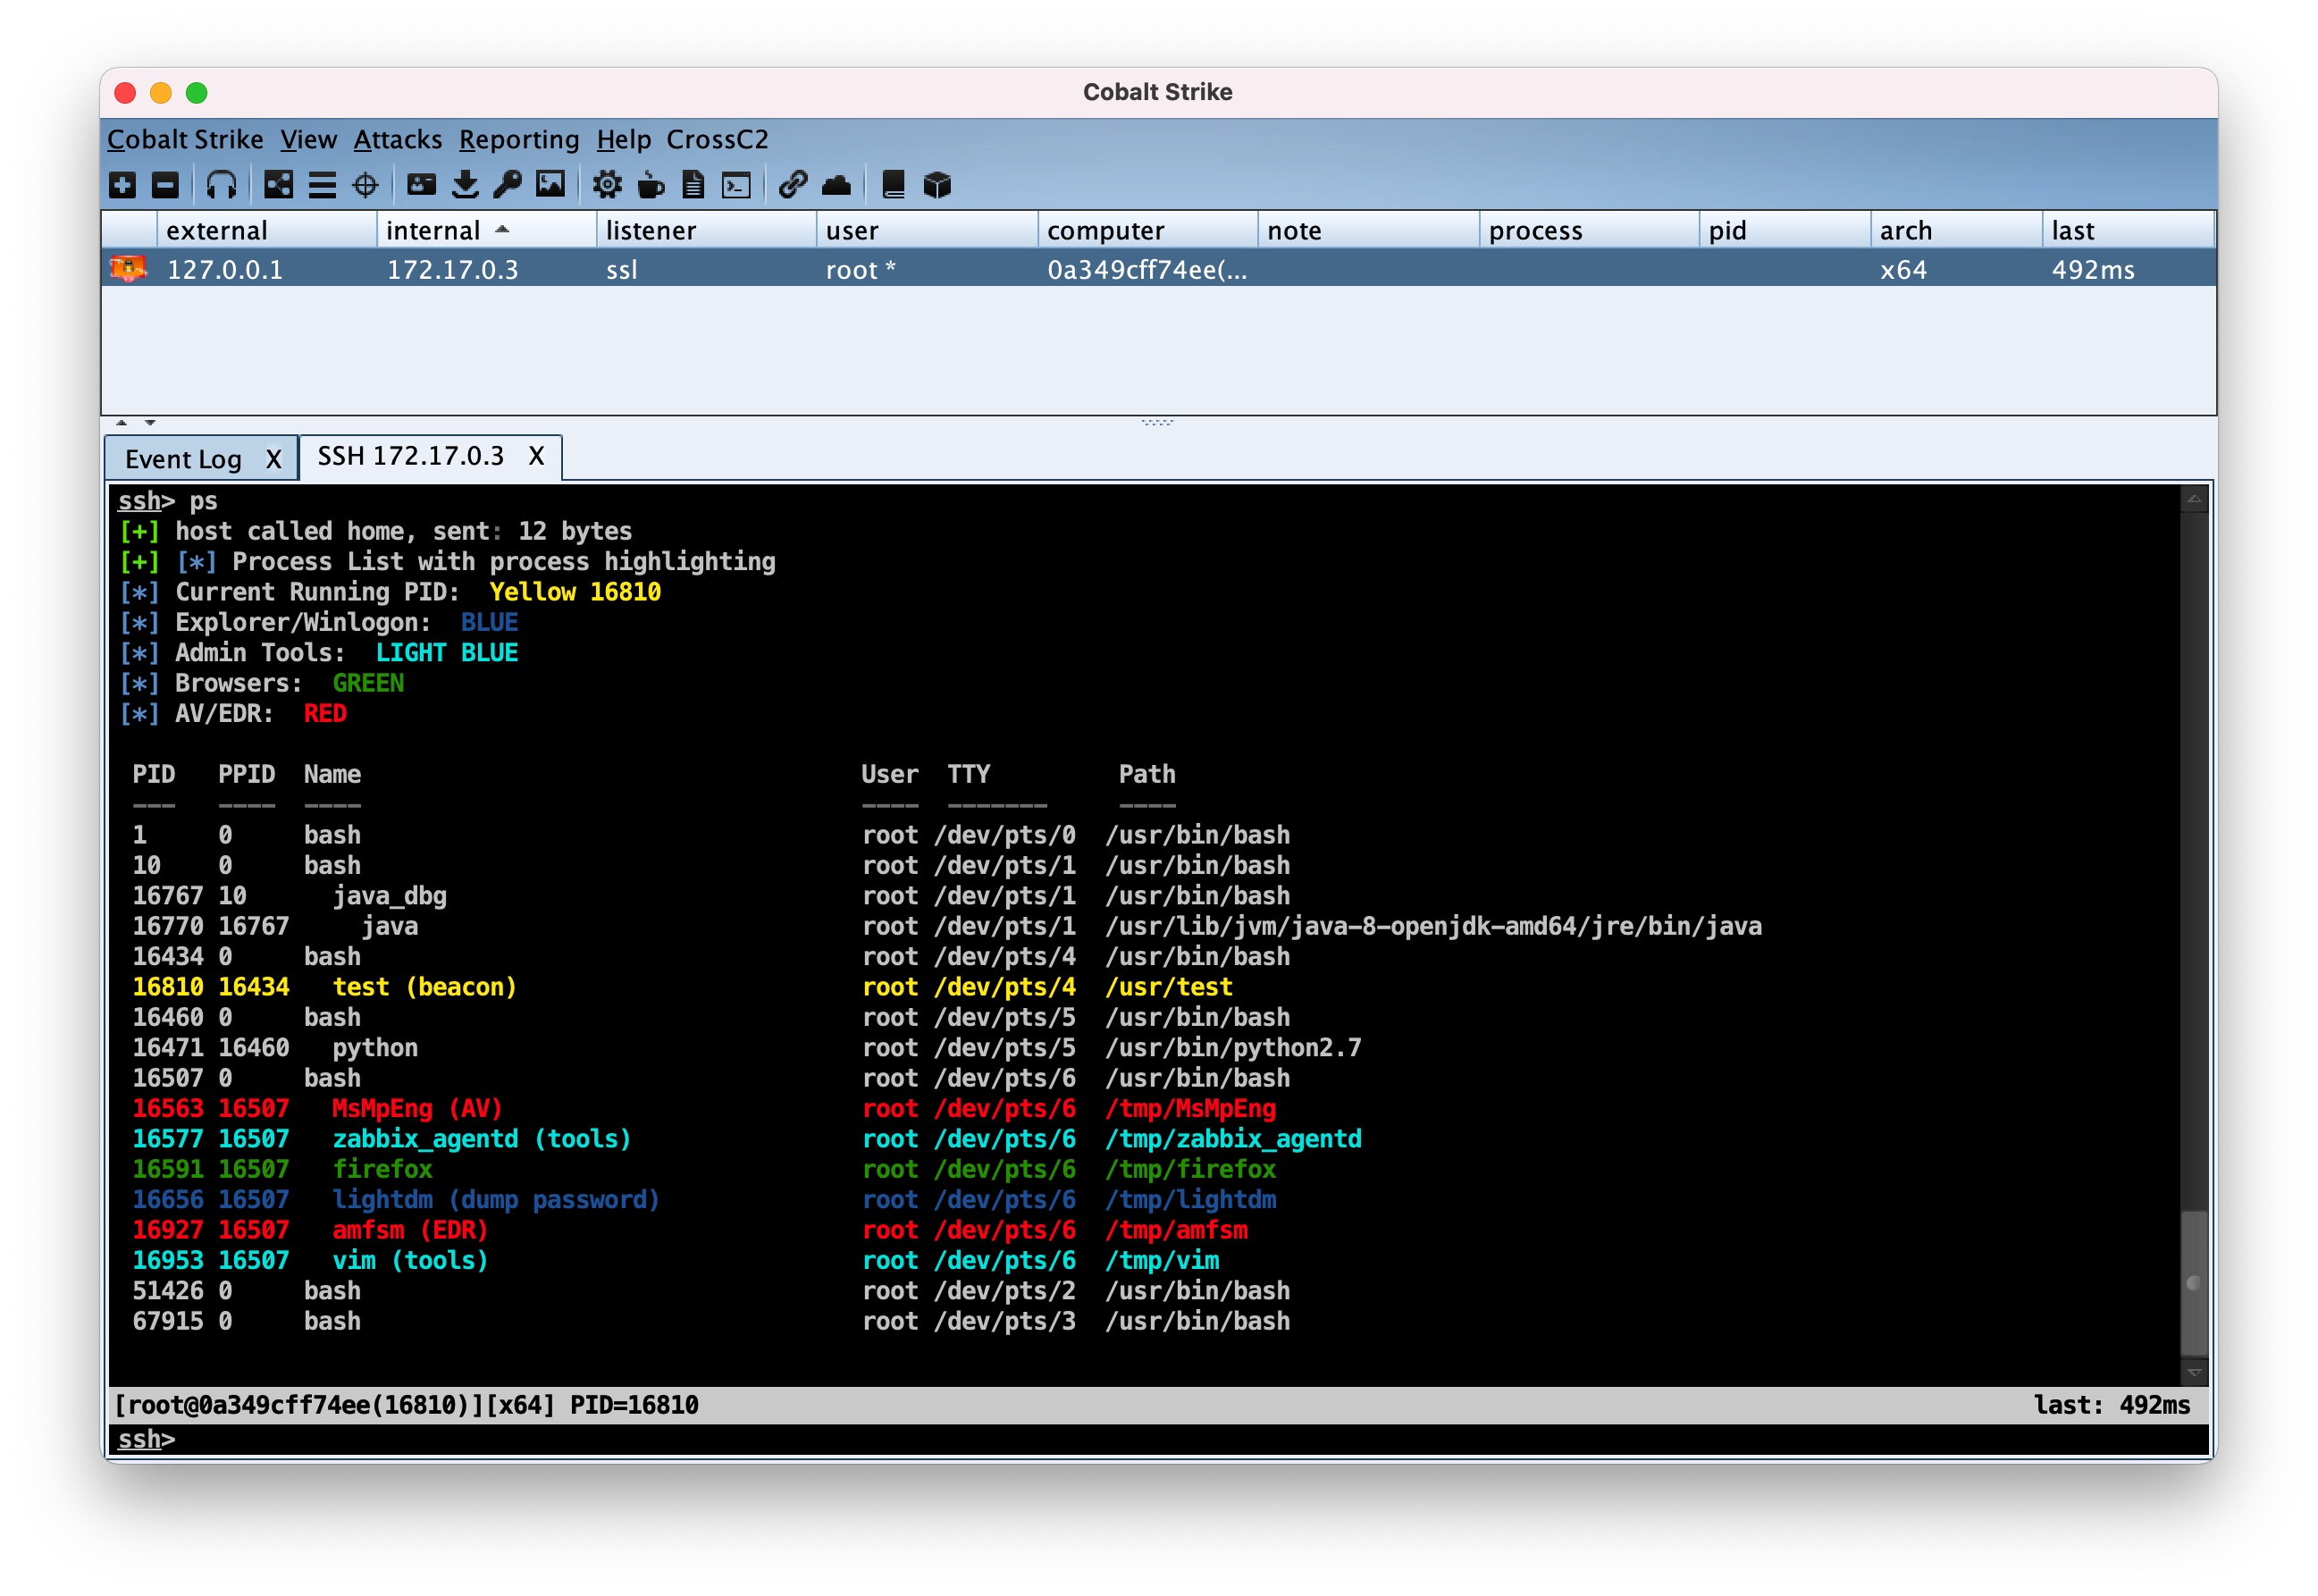 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…

 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 mdsecactivebreach/sharpshooter
Payload Generation Framework
 joelgmsec/autordpwn
The Shadow Attack Framework
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…