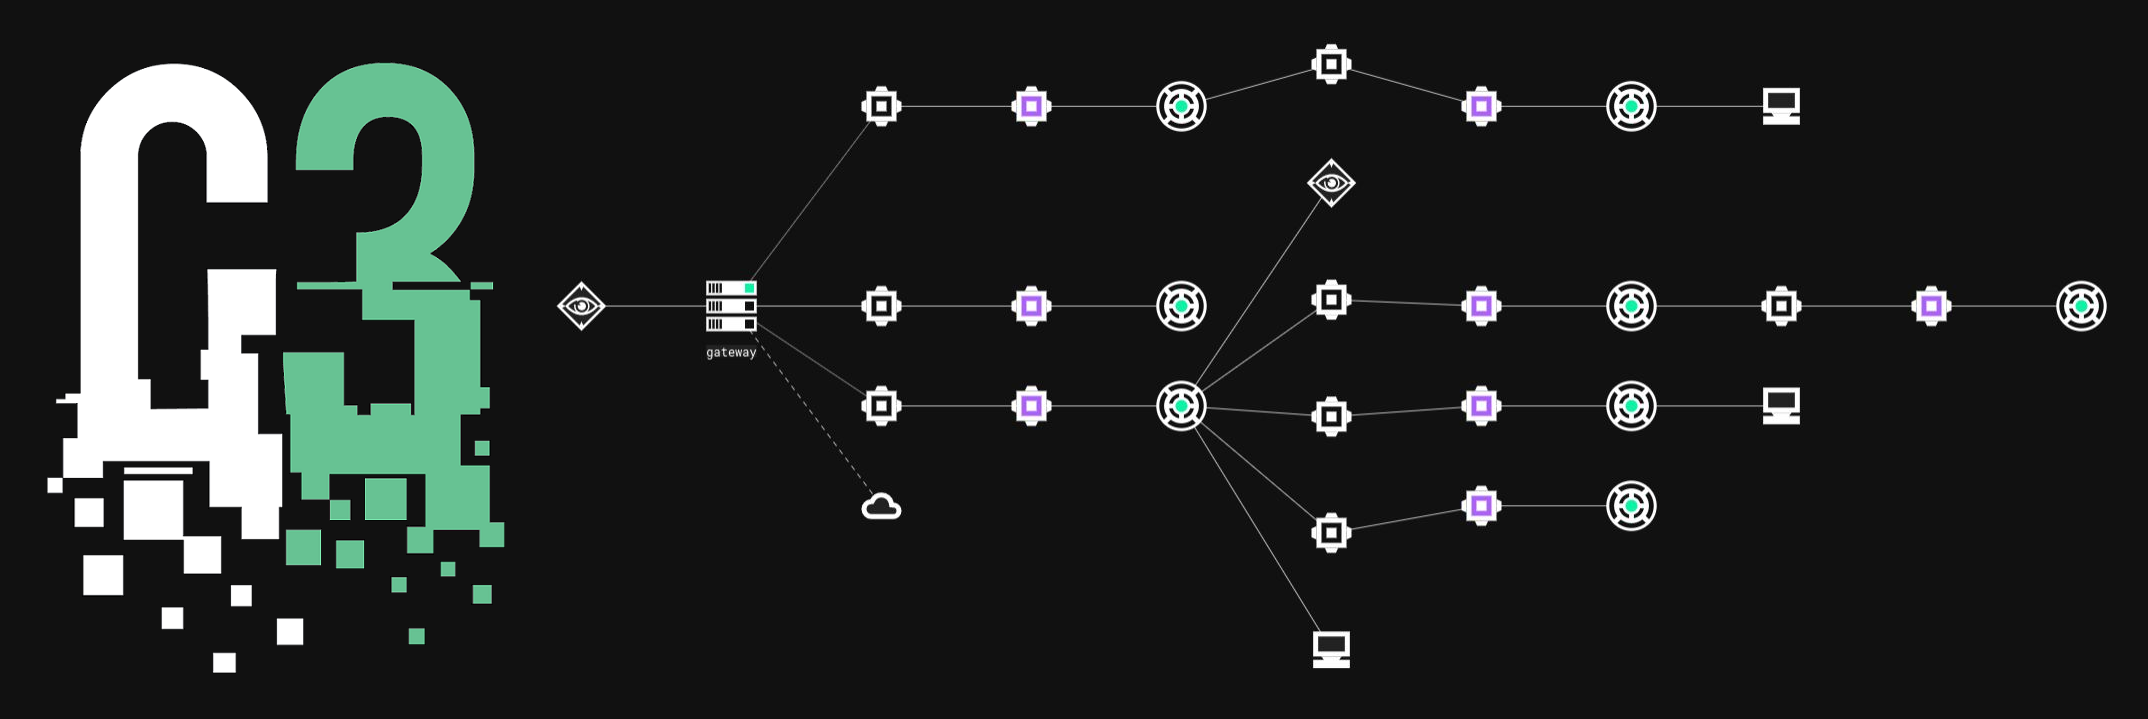
C3
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
command-and-controlexploit-frameworksids-ips-evasion+6
1.8k
reverseclabs/c3Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 bishopfox/sliver
Adversary Emulation Framework
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
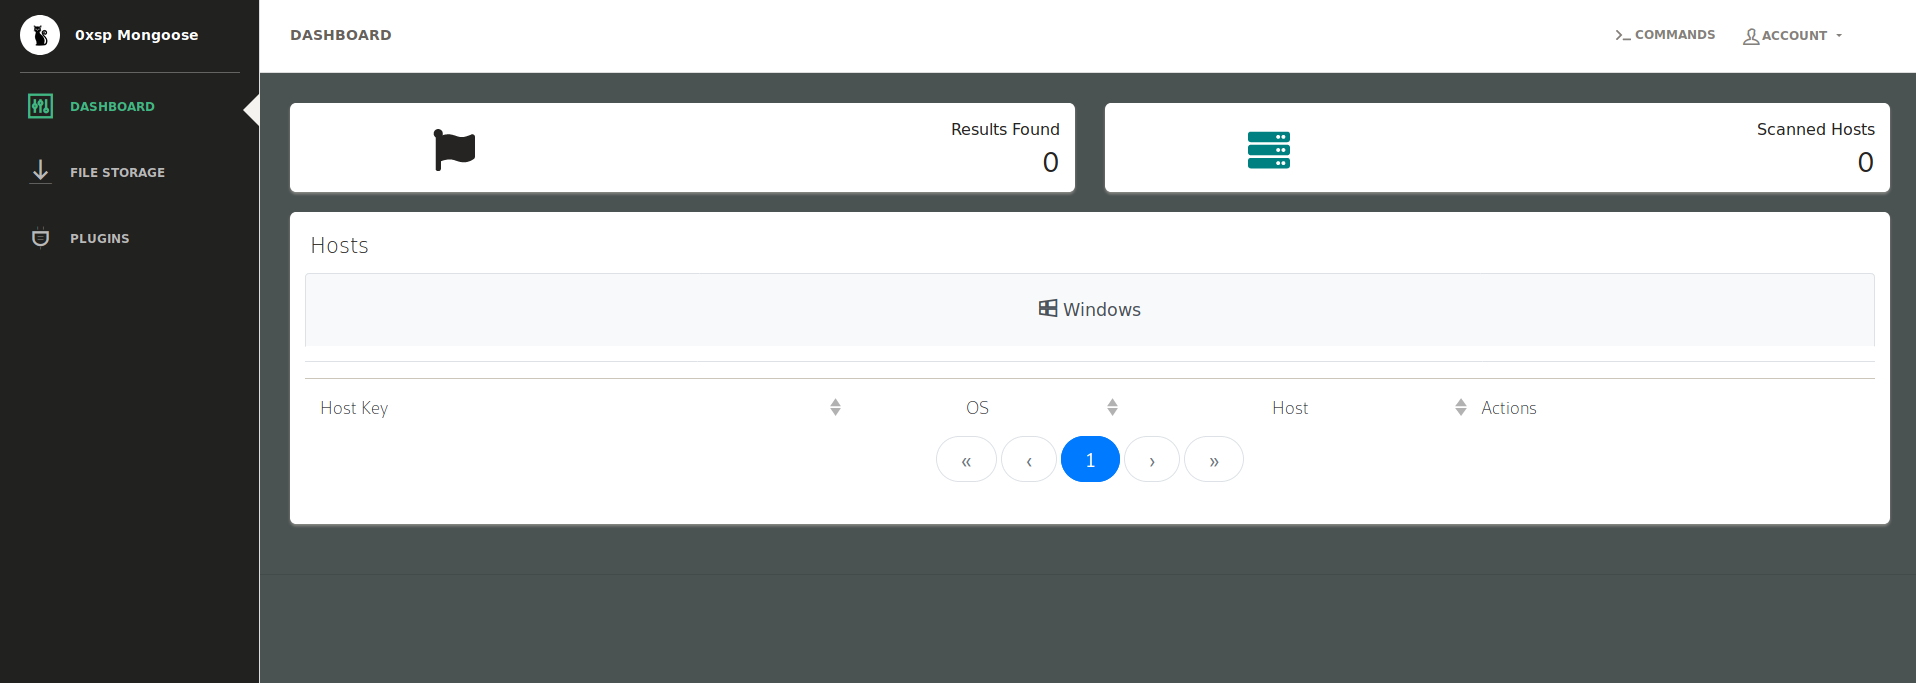 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
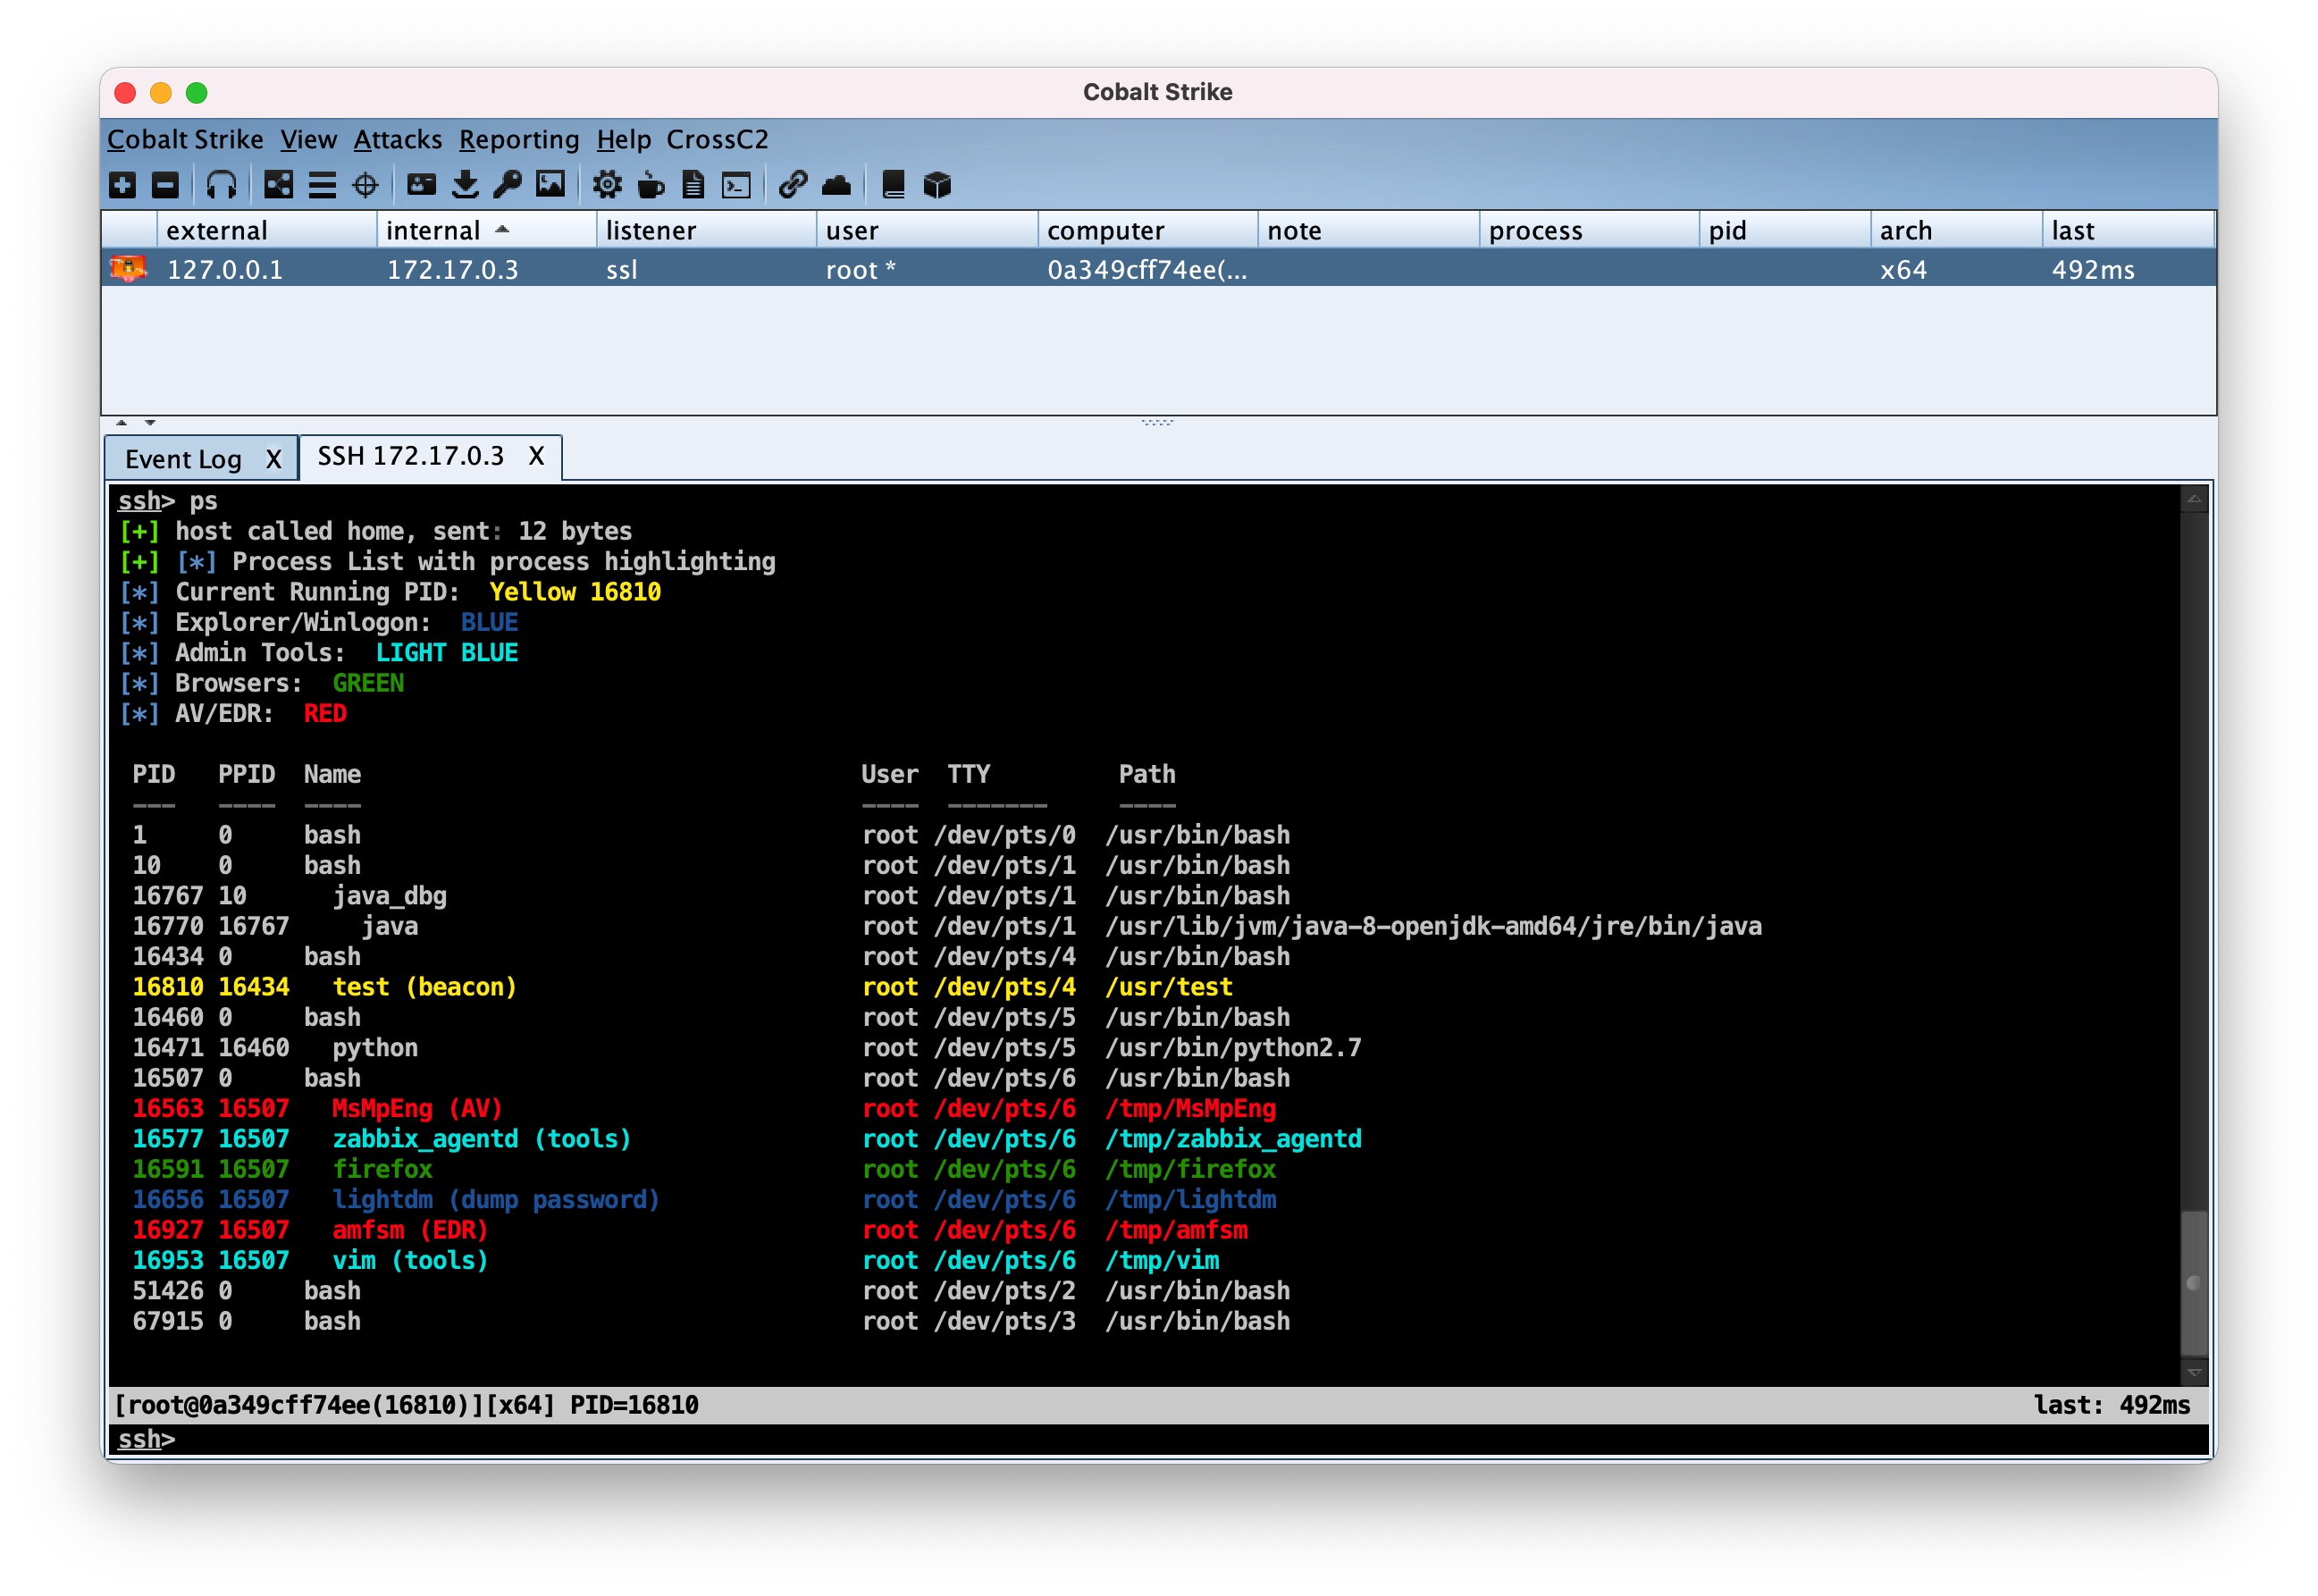 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 mdsecactivebreach/sharpshooter
Payload Generation Framework
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
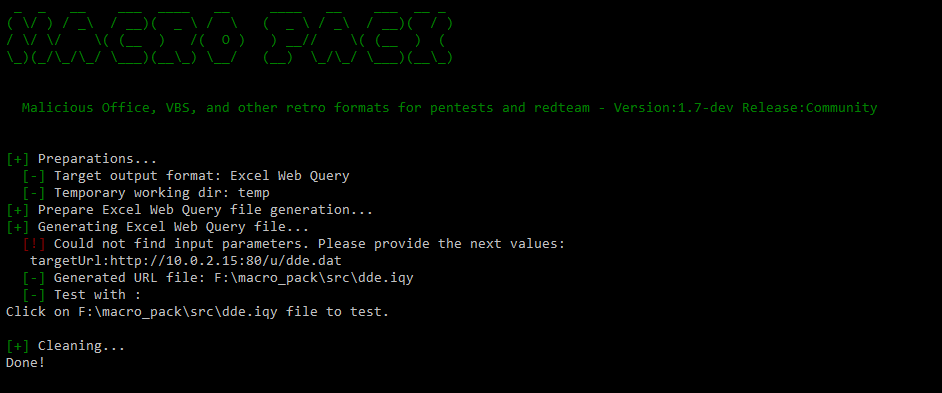 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup