veneficus-implant-public

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…

PoC for CVE-2009-0229 "Print Spooler Read File Vulnerability" LPE AFR (related to CVE-2020-1048)

Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.

Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…

CVE-2021-21220 Exploitation infrastructure

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability

An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…

Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).

Exploit for the CVE-2024-37010: access other user's external storage & lateral movement

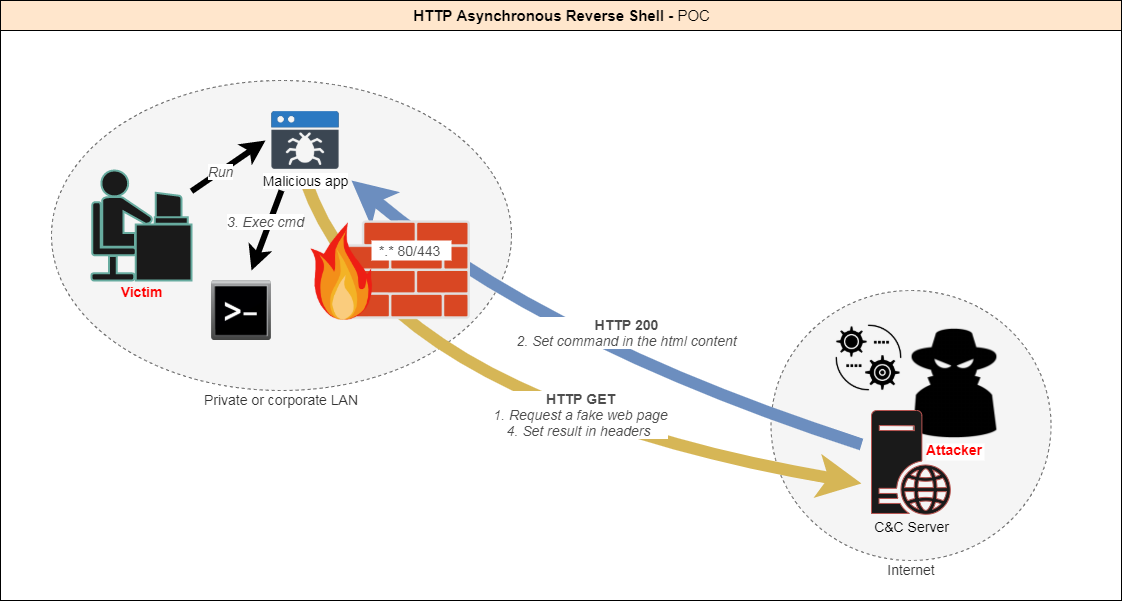
[POC] Asynchronous reverse shell using the HTTP protocol.

Discord Remote Administration Tool fully written in Python3

A simple remote tool in C#.

Browser-based C2 tunnel that exfiltrates payloads through Firefox's cookie.sqlite and auto-submitting HTML/JS, enabling stealthy firewall bypass for…

A simple python reverse shell written just for fun.

Remote administration service which uses twitter as a command and control server