

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
88 results
redamon preview

redamon

GitHubsamugit83/redamon

Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
ai-securityexploit-frameworkslateral-movement+8
3.2k
16h 56m ago
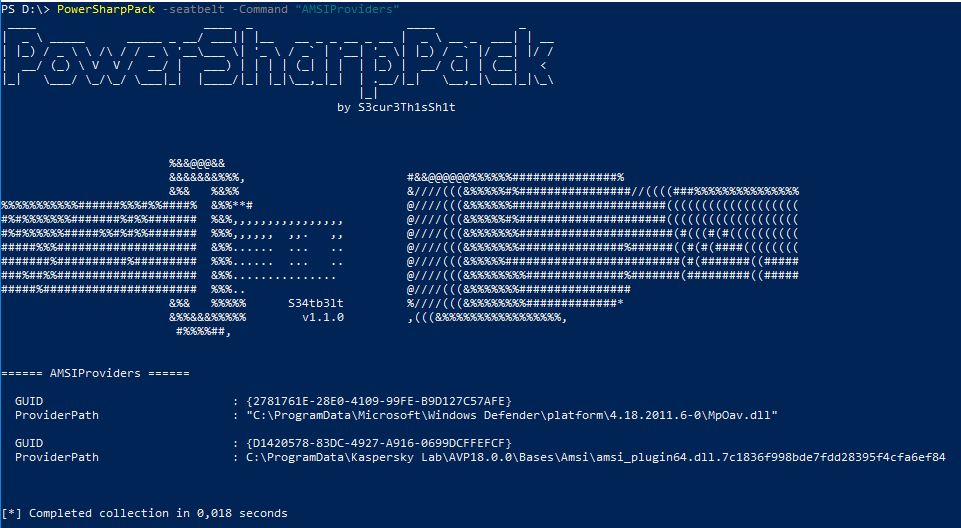
PowerSharpPack preview

PowerSharpPack

GitHubs3cur3th1ssh1t/powersharppack

PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
exploit-frameworksinformation-gatheringlateral-movement+5
1.7k1 year ago
C2-Tool-Collection preview

C2-Tool-Collection

GitHuboutflanknl/c2-tool-collection

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
command-and-controlexploit-frameworksinformation-gathering+8
1.4k3 years ago
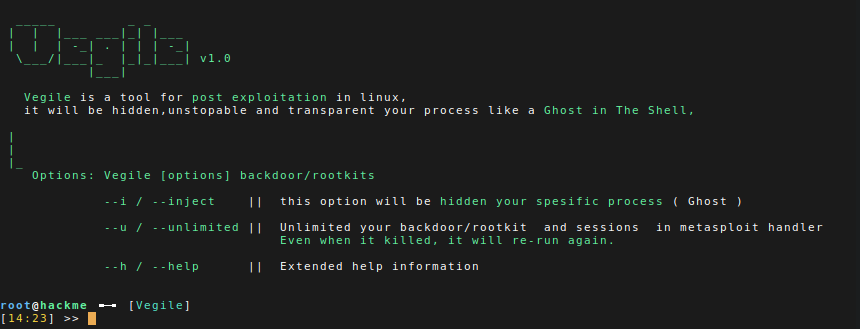
Vegile preview

Vegile

GitHubscreetsec/vegile

This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
exploit-frameworkslateral-movementpayload-generation+4
7537 years ago
pystinger preview

pystinger

GitHubfunnywolf/pystinger

Bypass firewall for traffic forwarding using webshell
command-and-controlexploit-frameworksids-ips-evasion+5
1.4k5 years ago
MoveKit preview

MoveKit

GitHub0xthirteen/movekit

Cobalt Strike kit for Lateral Movement
exploit-frameworkslateral-movementpenetration-testing+2
6766 years ago
thanatos preview

thanatos

GitHubmythicagents/thanatos

Mythic C2 agent targeting Linux and Windows hosts written in Rust

command-and-controlexploit-frameworkslateral-movement+4
4114 days ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

command-and-controlexploit-frameworkslateral-movement+8
2127 days ago
CobaltStrike-Toolset preview

CobaltStrike-Toolset

GitHubqax-a-team/cobaltstrike-toolset

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
command-and-controlexploit-frameworkslateral-movement+8
5957 years ago
PoshC2_Old preview

PoshC2_Old

GitHubnettitude/poshc2_old

Powershell C2 Server and Implants
command-and-controlexploit-frameworkslateral-movement+5
5746 years ago
Stracciatella preview

Stracciatella

GitHubmgeeky/stracciatella

OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
command-and-controlexploit-frameworksids-ips-evasion+7
5434 years ago
pyCobaltHound preview

pyCobaltHound

GitHubnvisosecurity/pycobalthound

pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.

exploit-frameworksinformation-gatheringlateral-movement+5
1354 years ago
CrystalSliver preview

CrystalSliver

GitHublicitrasimone/crystalsliver

Crystal Palace Evasion kit for Sliver

command-and-controlexploit-frameworksids-ips-evasion+9
1234 months ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

binary-analysiscommand-and-controlexploit-frameworks+9
1344 months ago
TornadoC2 preview

TornadoC2

GitHubkamalx06/tornadoc2

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
command-and-controlcryptographyids-ips-evasion+9
3412 days ago
MiniPlasma-Runner preview

MiniPlasma-Runner

GitHubalexlinov/miniplasma-runner

CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
command-and-controlexploitationexploit-frameworks+5
465 months ago
blankspace preview

blankspace

GitHubjbaines-r7/blankspace

Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)

exploitationexploit-frameworkslateral-movement+2
644 years ago
Overthrone preview

Overthrone

GitHubkarmanya03/overthrone

All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…

command-and-controlexploit-frameworksinformation-gathering+8
316 days ago
Previous12345Next