

Internal-Monologue
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
lateral-movementpassword-attackspenetration-testing+2
1.7k
eladshamir/internal-monologueInternal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 mr-un1k0d3r/scshell
Fileless lateral movement tool that relies on ChangeServiceConfigA to run command
 joelgmsec/autordpwn
The Shadow Attack Framework
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
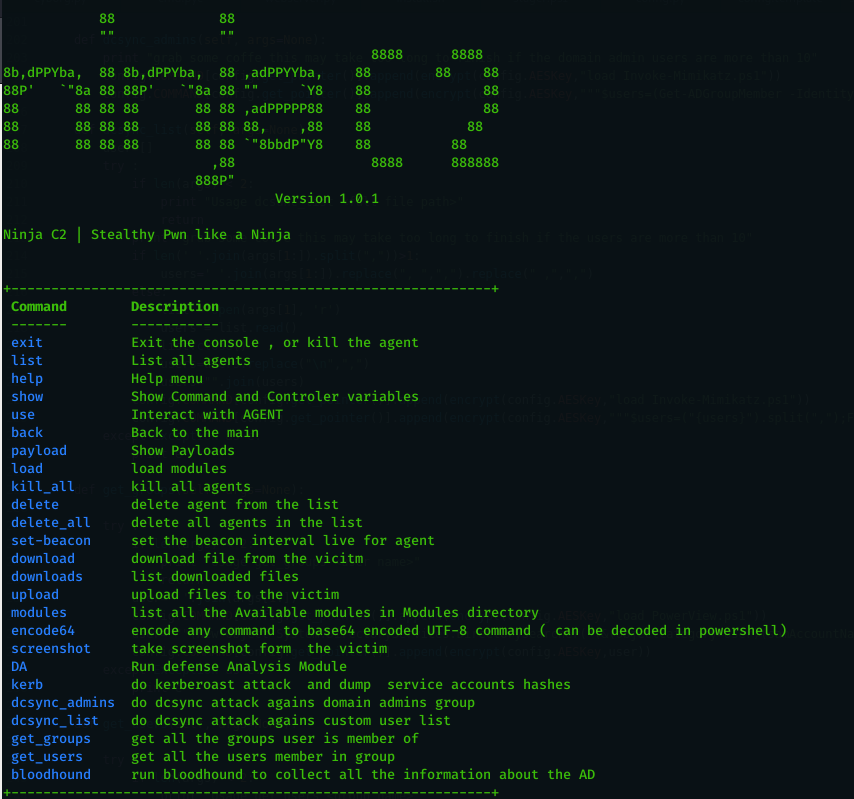 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 redcode-labs/neurax
A framework for constructing self-spreading binaries