

SessionHop
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
lateral-movementpenetration-testingpost-exploitation+2
350
3lp4tr0n/sessionhopWindows Session Hijacking via COM
 occamsxor/dragnmove
Infect Shared Files In Memory for Lateral Movement
 nettitude/sharpwsus
C# tool for lateral movement through WSUS by creating, approving, and deploying malicious updates to target Windows clients in Active Directory…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 sensepost/impersonate
A windows token impersonation tool
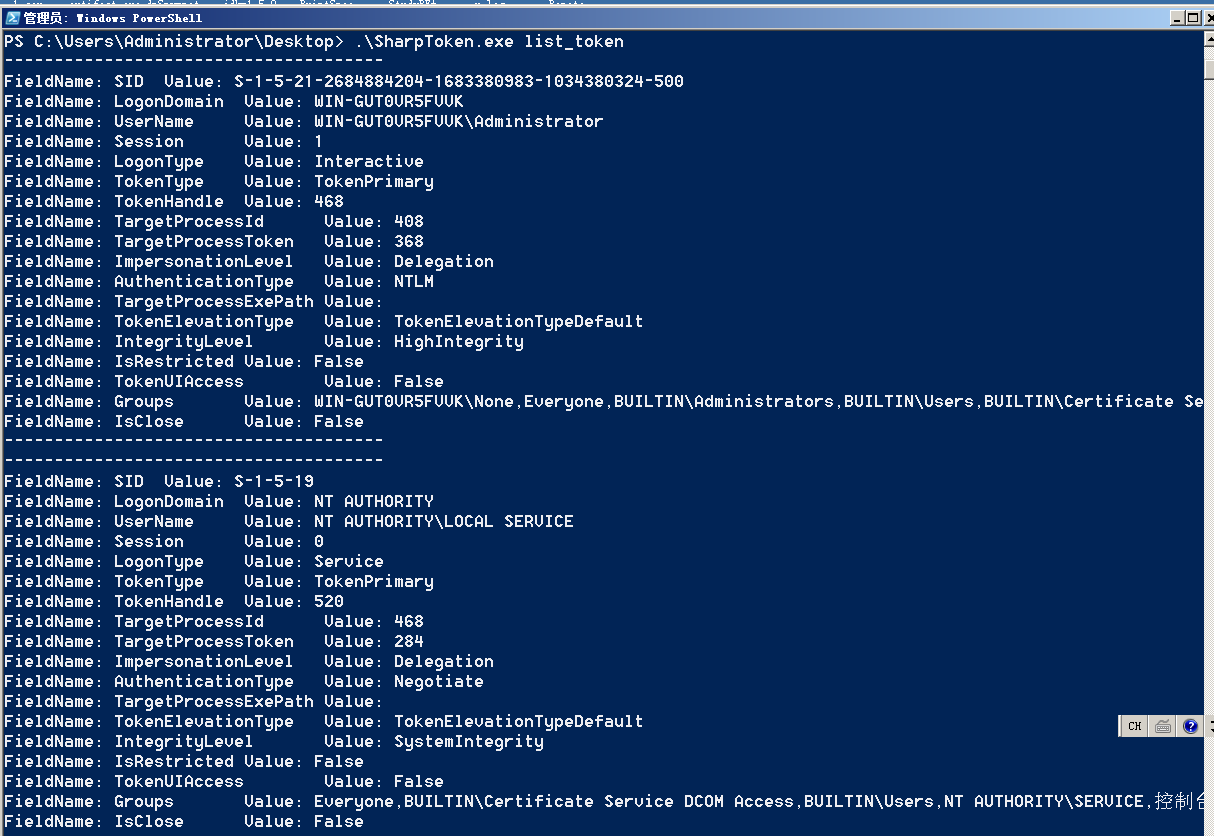 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 ttpreport/ligolo-mp
Multiplayer pivoting solution
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 blackarrowsec/mssqlproxy
mssqlproxy is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse
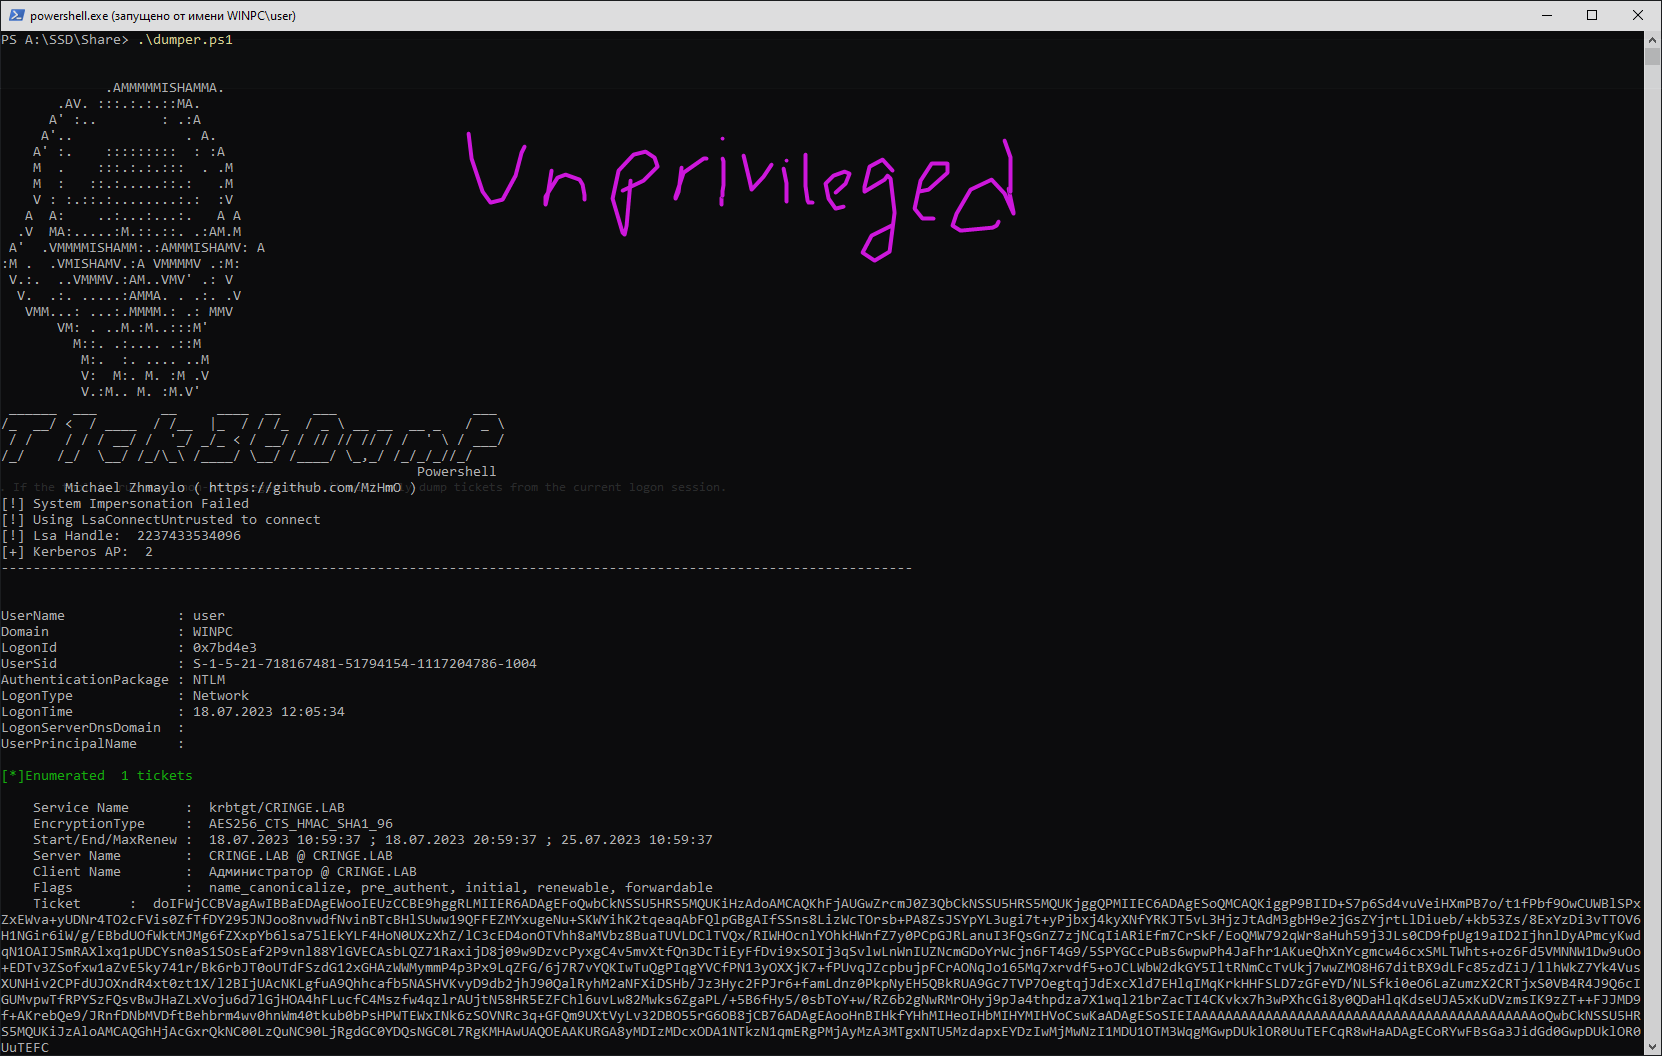 mzhmo/powershellkerberos
Some scripts to abuse kerberos using Powershell