
printnightmare
 glorisonlai/printnightmare
Proof-of-concept implementation of CVE-2021-34527 (PrintNightmare) for exploiting Windows Print Spooler remote code execution and privilege…
exploitationlateral-movementpenetration-testing+2
glorisonlai/printnightmareProof-of-concept implementation of CVE-2021-34527 (PrintNightmare) for exploiting Windows Print Spooler remote code execution and privilege…
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.
 charlesgargasson/cve-2024-32002
Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…
 fastmo/cve-2022-28672
CVE-2022-28672 Vulnerabilidad Foxit PDF Reader - UaF - RCE - JIT Spraying
 adminempire/meshdeck
MeshDeck port for Arch Linux ARM - Wilson
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 sp4cedogy/npe-cs-v-cve-2021-1675
Exploit code for CVE-2021-1675, a Windows Print Spooler remote code execution vulnerability, demonstrating the attack and providing a…
 saharattackit/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) targeting Windows Netlogon to achieve privilege escalation and domain controller compromise.
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 byt3bl33d3r/crackmapexec
A swiss army knife for pentesting networks
 coldzer0/reversesock5proxy
A tiny Reverse Sock5 Proxy written in C :V
 havocframework/modules
Modules used by the Havoc Framework
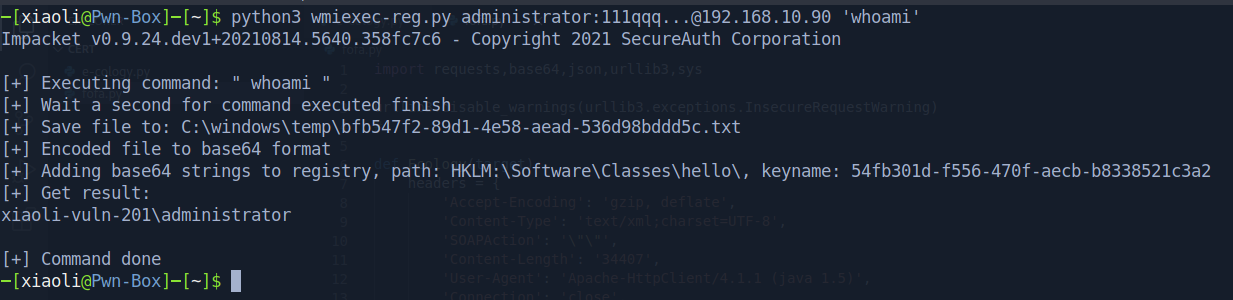 xiaolichan/wmiexec-regout
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 sp00kyskelet0n/discordrat
Discord Remote Administration Tool fully written in Python3
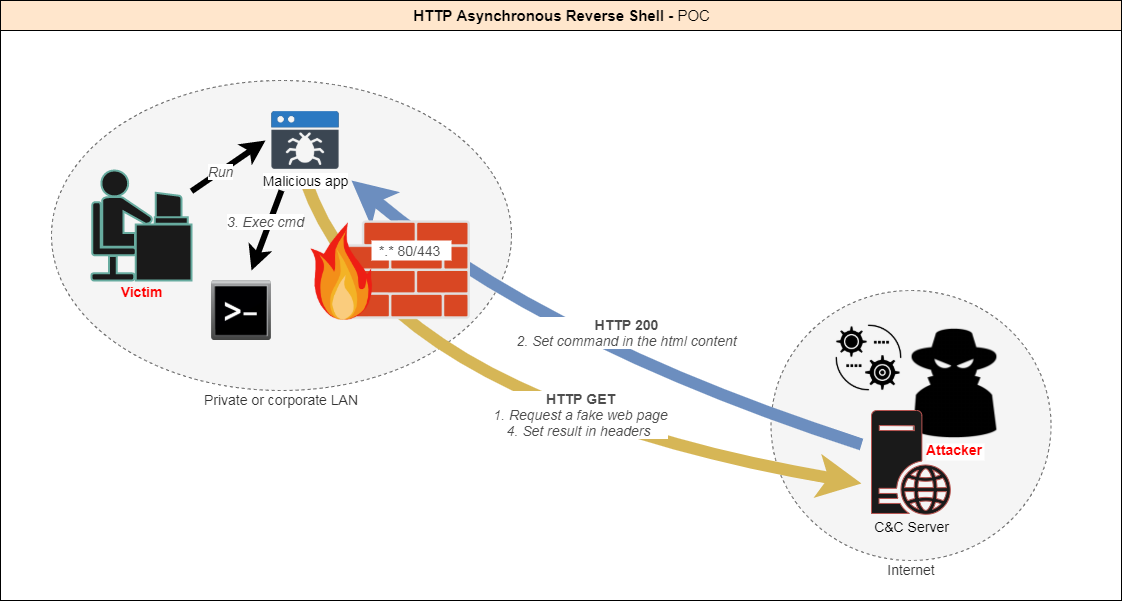 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.