
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
226 results
cloudfox preview

cloudfox

GitHubbishopfox/cloudfox

Automating situational awareness for cloud penetration tests.
cloud-infrastructure-securitycloud-securityexploitation+7
2.6k
1 month ago
C3 preview

C3

GitHubreverseclabs/c3

Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
command-and-controlexploit-frameworksids-ips-evasion+6
1.8k8 months ago
SocksOverRDP preview

SocksOverRDP

GitHubnccgroup/socksoverrdp

Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop

ids-ips-evasionlateral-movementpenetration-testing+3
1.3k3 years ago
SharpMapExec preview

SharpMapExec

GitHubcube0x0/sharpmapexec

Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
authenticationdata-exfiltrationexploitation+9
6684 years ago
SharpADWS preview

SharpADWS

GitHubwh0amitz/sharpadws

Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
authenticationexploitationlateral-movement+6
6052 years ago
RelayKing-Depth preview

RelayKing-Depth

GitHubdepthsecurity/relayking-depth

Dominate the domain. Relay to royalty.
exploitationids-ips-evasioninformation-gathering+7
3545 months ago
NimExec preview

NimExec

GitHubfrkngksl/nimexec

Fileless Command Execution for Lateral Movement in Nim
command-and-controlexploitationlateral-movement+2
3975 months ago
OUned preview

OUned

GitHubsynacktiv/ouned

The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
authenticationexploitationlateral-movement+3
16522 days ago
ATTPwn preview

ATTPwn

GitHubtelefonica/attpwn

ATTPwn

adversarial-attacklateral-movementpenetration-testing+3
2205 years ago
ntlm_relay_gat preview

ntlm_relay_gat

GitHubad0nis/ntlm_relay_gat

Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
command-and-controlexploitationinformation-gathering+5
1712 years ago
AD-PathFinder preview

AD-PathFinder

GitHubnetspi/ad-pathfinder

Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.

exploitationinformation-gatheringlateral-movement+7
2401 month ago
Cable preview

Cable

GitHublogangoins/cable

.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation

authenticationconfiguration-auditingexploitation+8
4011 year ago
peeko preview

peeko

GitHubb3rito/peeko

peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
command-and-controldata-exfiltrationinformation-gathering+7
2331 year ago
Hwacha preview

Hwacha

GitHubn00py/hwacha

Deploy payloads to *Nix systems en masse

command-and-controlexploitationlateral-movement+7
1086 years ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
binary-exploitationexploitationlateral-movement+7
2169 days ago
profilehound preview

profilehound

GitHubm4lwhere/profilehound

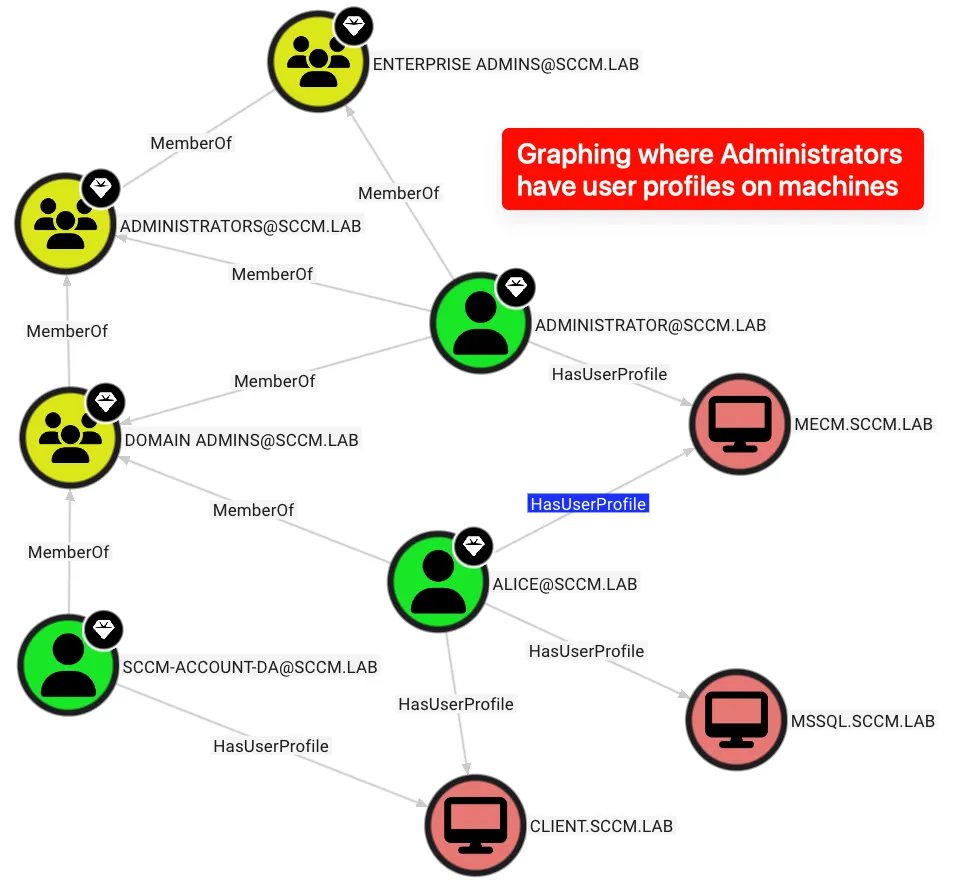
ProfileHound - BloodHound OpenGraph collector for user profiles stored on domain machines. Make informed decisions about looting secrets by…
information-gatheringlateral-movementosint+4
1644 months ago
TokenMan preview

TokenMan

GitHubsecureworks/tokenman

Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
authenticationcloud-securityinformation-gathering+2
1033 years ago
badsuccessor preview

badsuccessor

GitHubcybrly/badsuccessor

Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…

adversarial-attackexploitationinformation-gathering+7
1221 year ago
Previous1…111213Next