
redamon
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
ai-securityexploit-frameworkslateral-movement+8
2.3k
samugit83/redamonAutonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
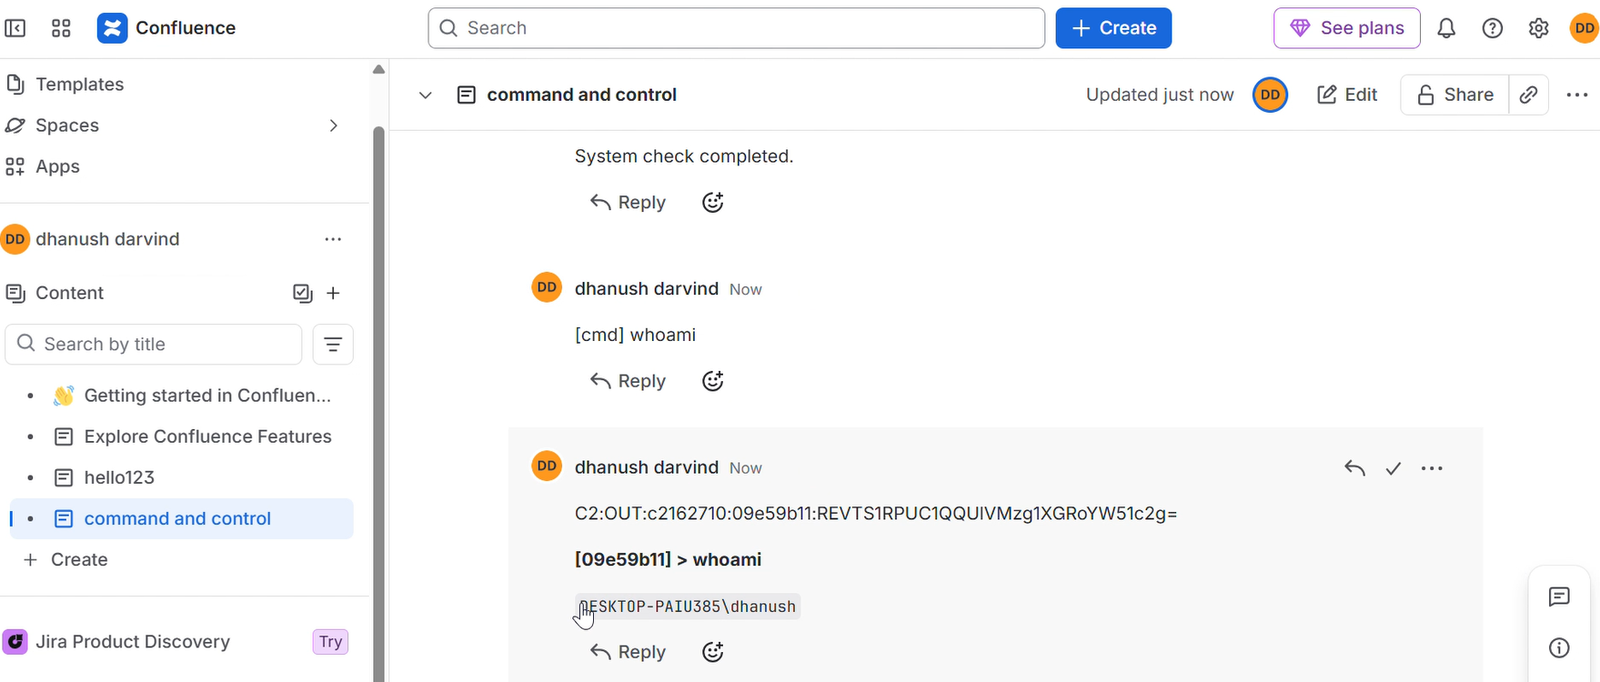 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 0xthirteen/sharprdp
Remote Desktop Protocol .NET Console Application for Authenticated Command Execution
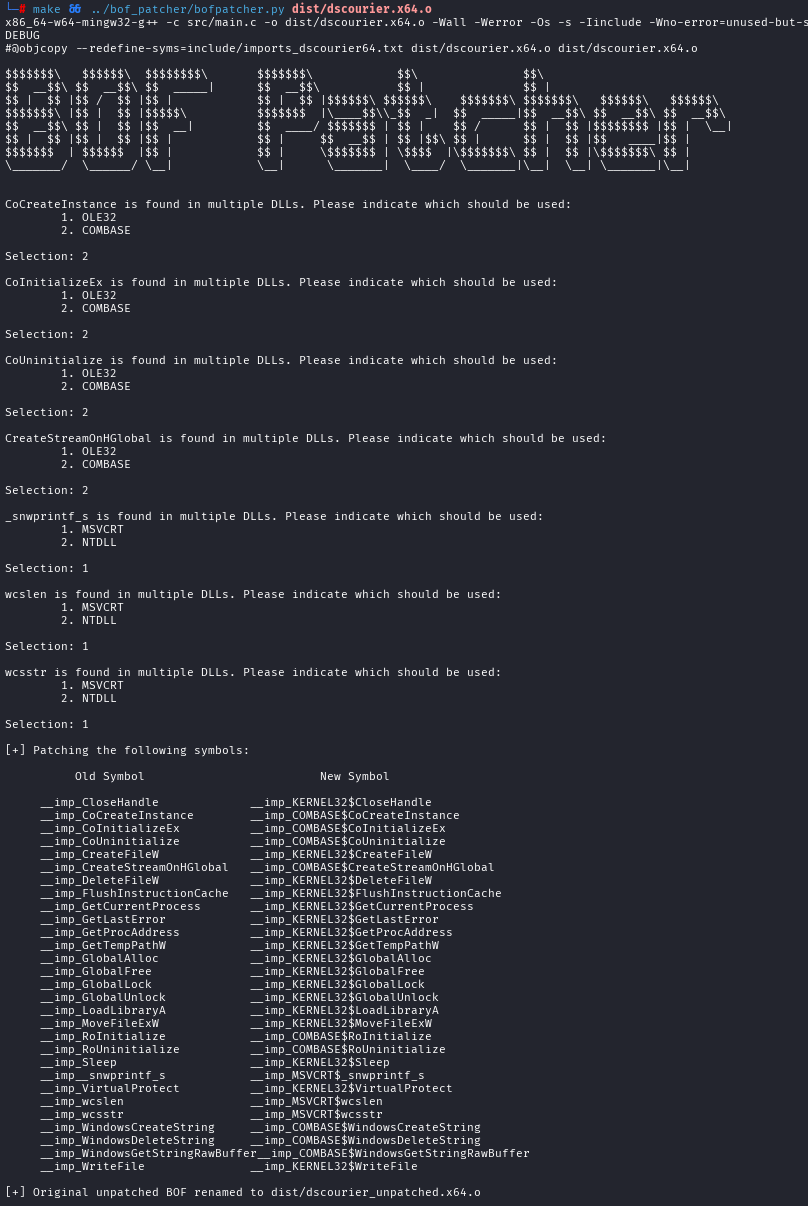 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
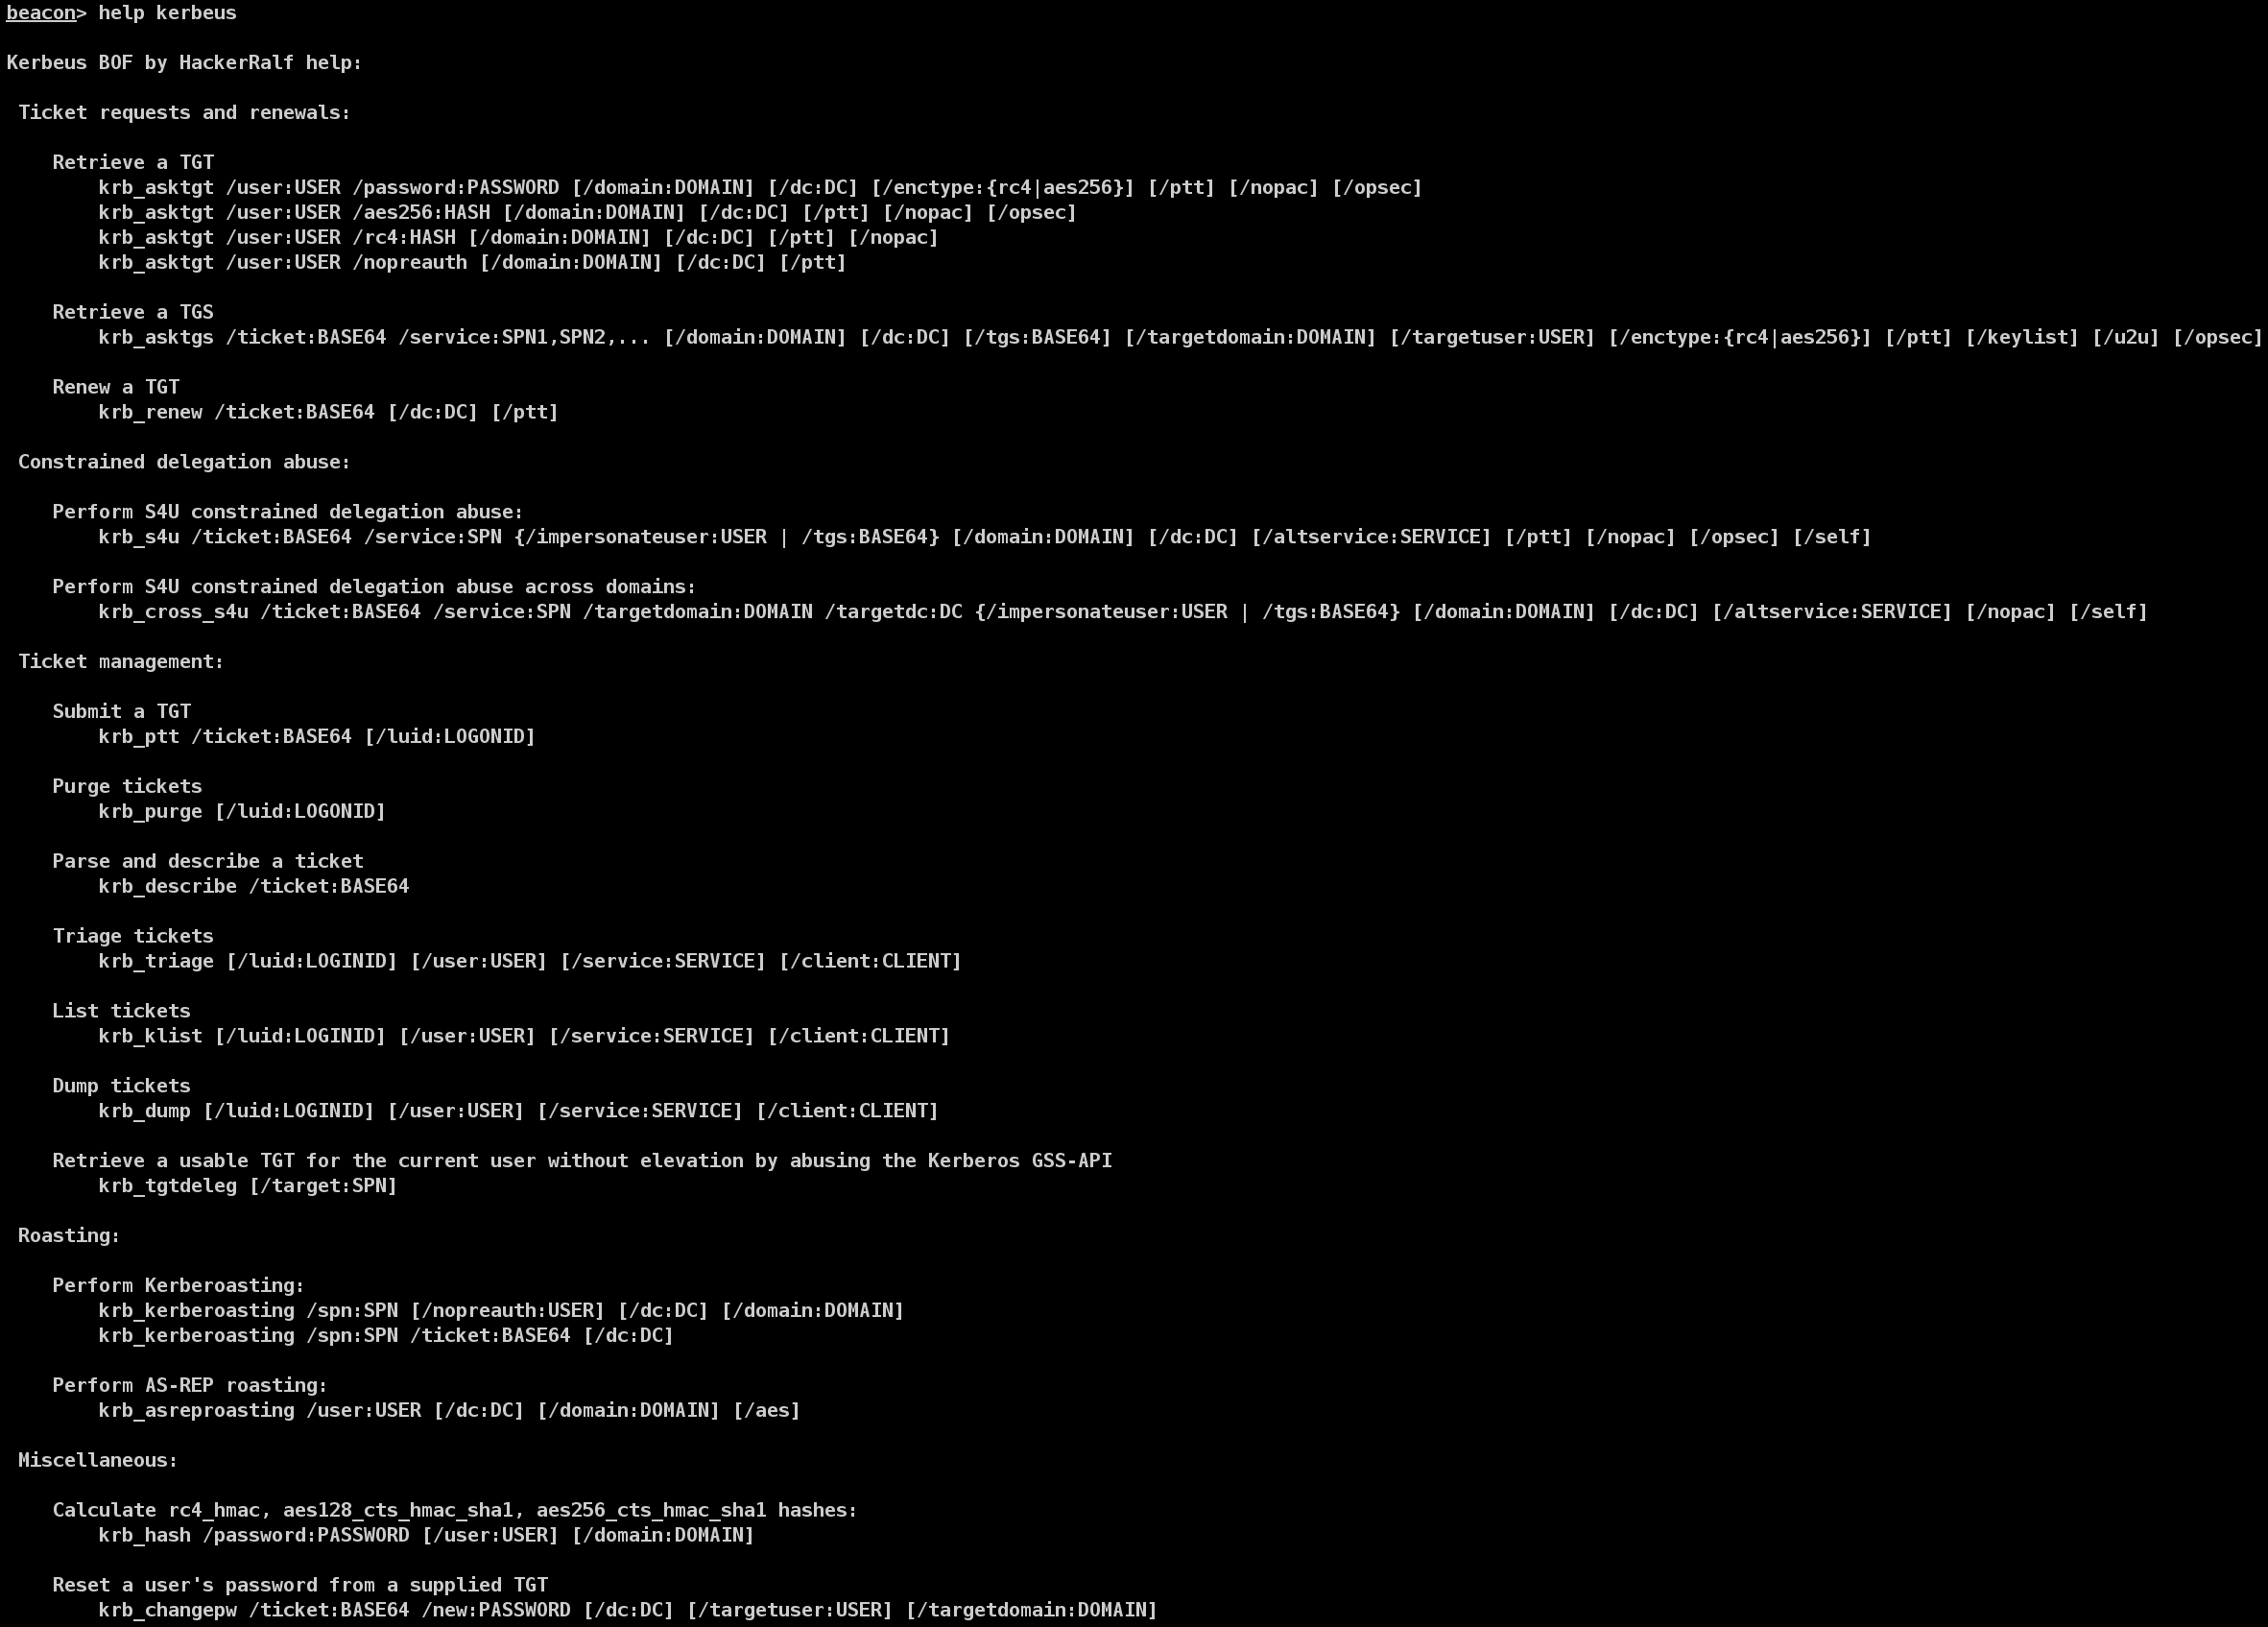 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
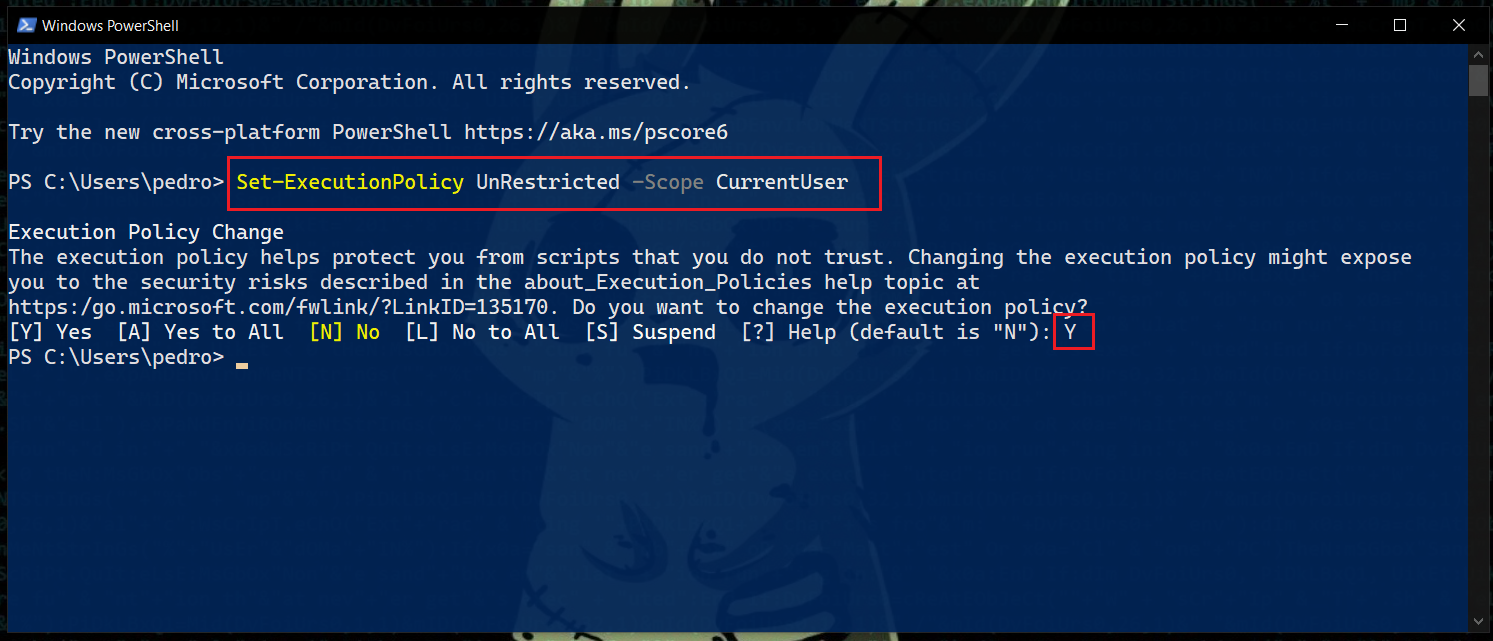 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 pswalia2u/cve-2025-24071_poc
Rust-based proof-of-concept that generates Windows Library (.library-ms) files with configurable network paths to demonstrate CVE-2025-24071 NTLM…
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
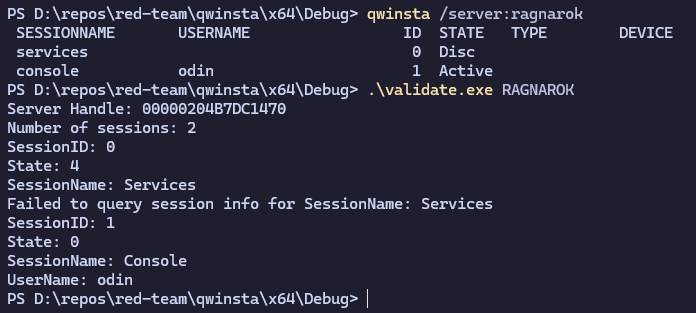 0xv1n/remotesessionenum
Remotely Enumerate sessions using undocumented Windows Station APIs
 edu0x01/hack-tools
Project that brings together several pentest tools