

HorusEye
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
defensive-toolsinformation-gatheringlateral-movement+6
omar-tamerr/horuseyeAI-Powered Active Directory Attack Platform
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
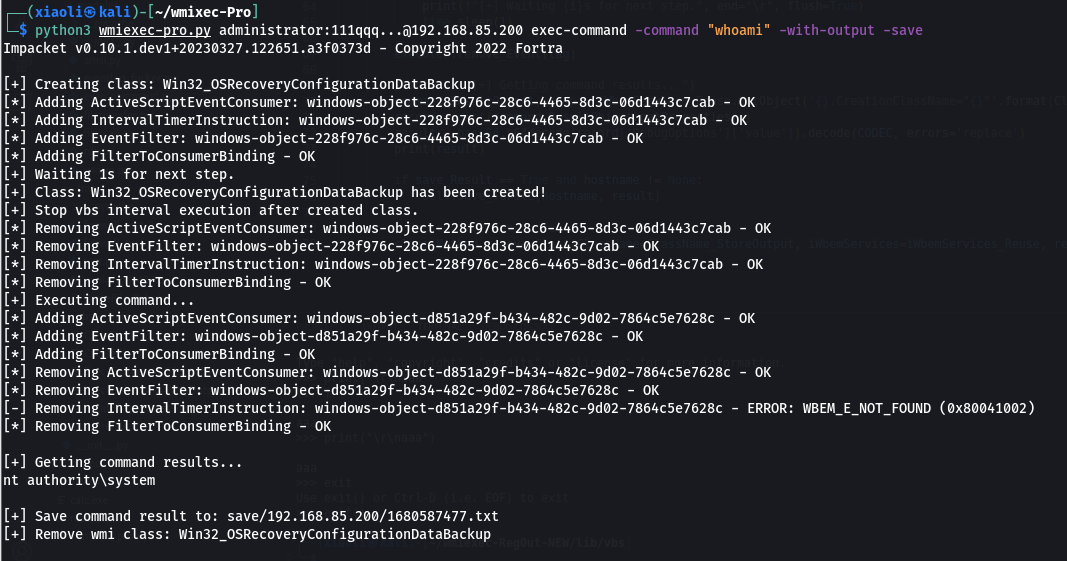 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 xforcered/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 mayyhem/maestro
Abusing Azure services over C2
 crowdstrike/sccmhound
A BloodHound collector for Microsoft Configuration Manager
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 nccgroup/wmicmd
A command shell wrapper using only WMI for Microsoft Windows
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 syss-research/ldap-swak
LDAP Swiss Army Knife
 al1ex/pentest-tools
Intranet penetration tools