

lockjaw
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
26
g13net/lockjawModular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
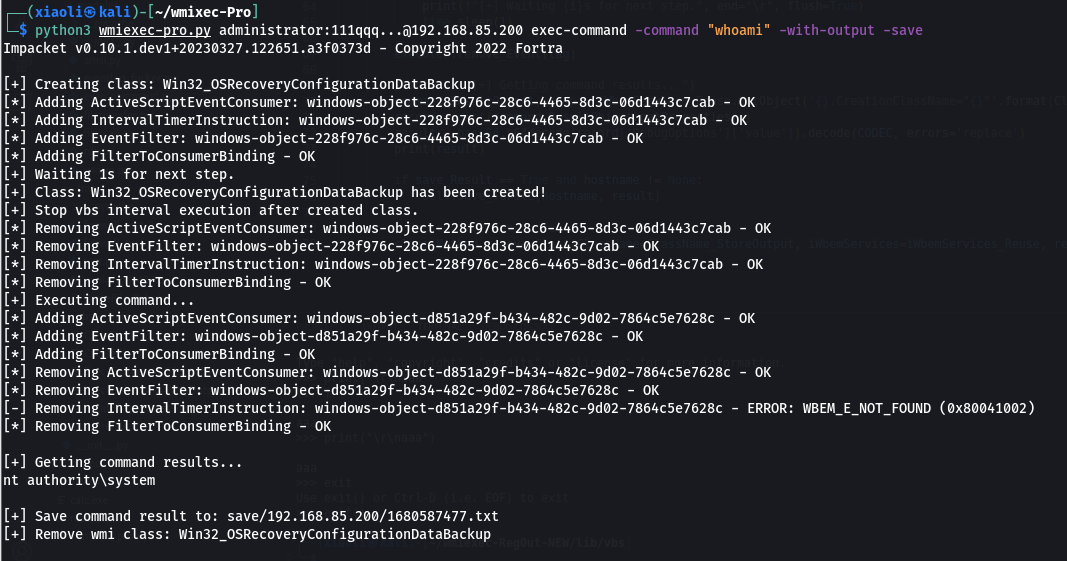 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 xforcered/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 crowdstrike/sccmhound
A BloodHound collector for Microsoft Configuration Manager
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 nccgroup/wmicmd
A command shell wrapper using only WMI for Microsoft Windows
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 d0n601/pwncity
Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…
 syss-research/ldap-swak
LDAP Swiss Army Knife
 al1ex/pentest-tools
Intranet penetration tools
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 blue0x1/rosemary
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.