
TornadoRevC2
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
command-and-controlinformation-gatheringlateral-movement+8
28
kamalx06/tornadorevc2Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
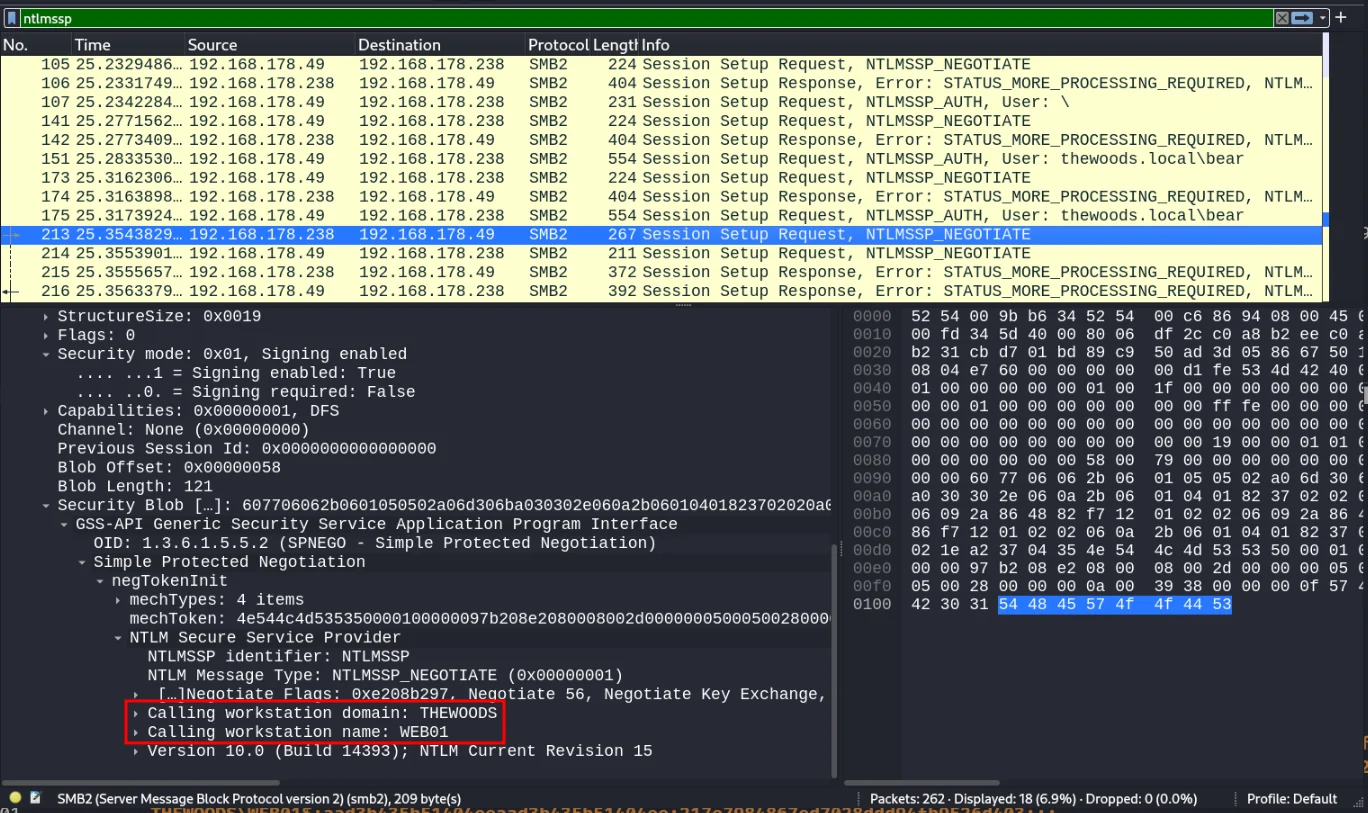 starscow/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
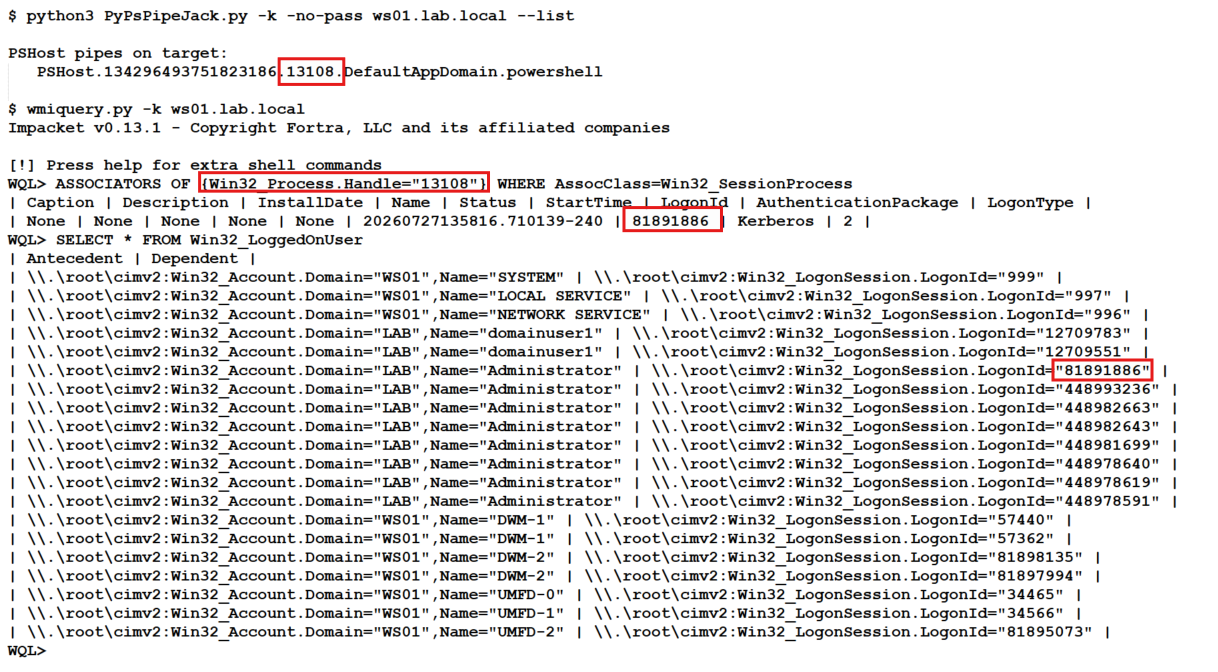 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
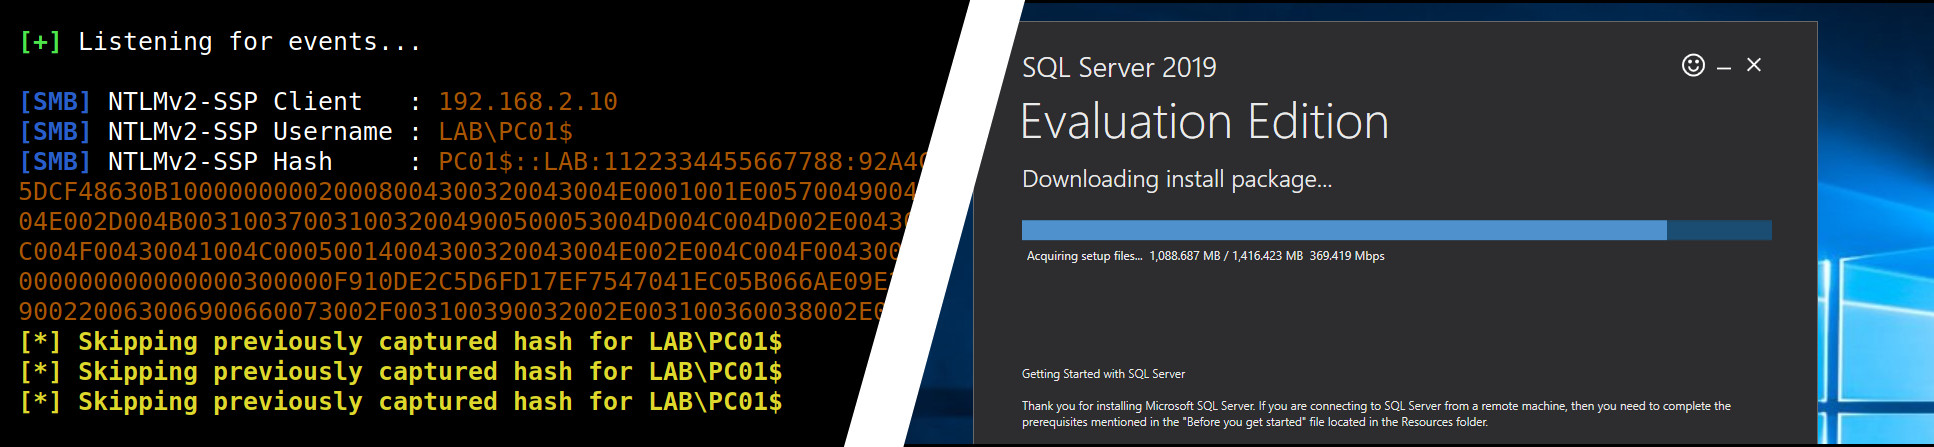 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
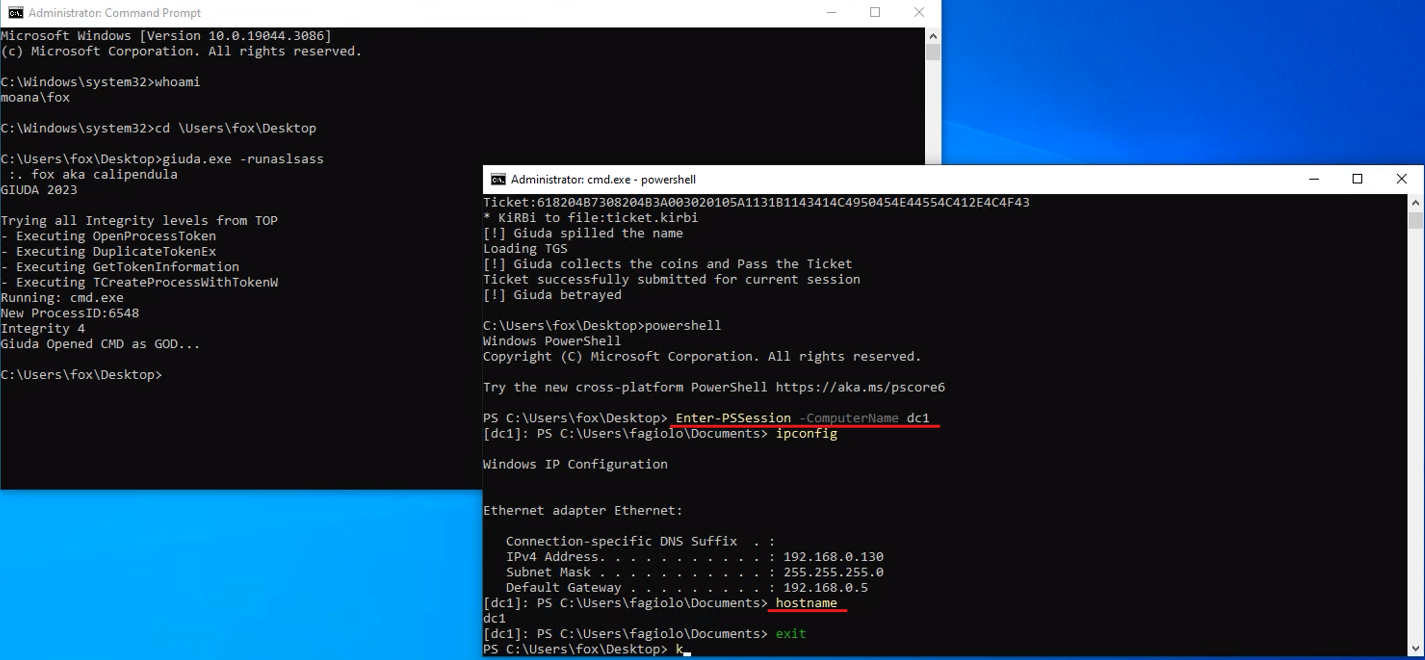 foxlox/giuda
Ask a TGS on behalf of another user without password
 hackerschoice/thc-tips-tricks-hacks-cheat-sheet
Various tips & tricks
 dopaminauta/onetwoseven-writeup
HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root
 n00py/outpacket
This cheatsheet maps common impacket workflows to their modern alternatives
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 adminempire/meshdeck
MeshDeck port for Arch Linux ARM - Wilson