
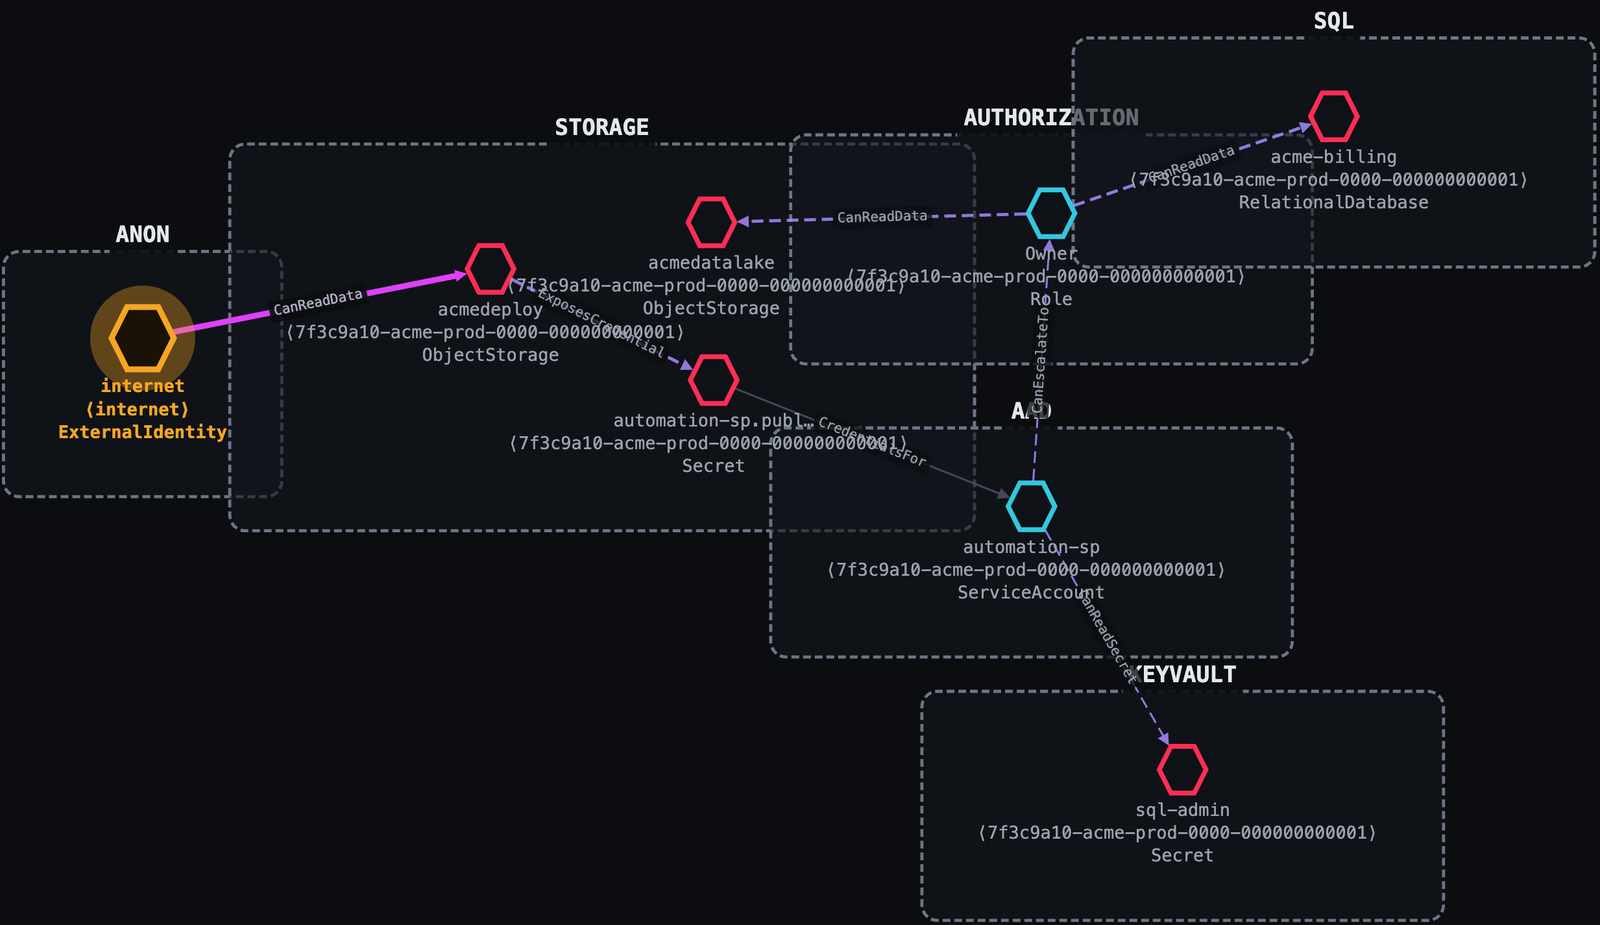
Thunderstorm
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
ustayready/thunderstormA collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 hkenzokimura/cve-2021-1675
Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
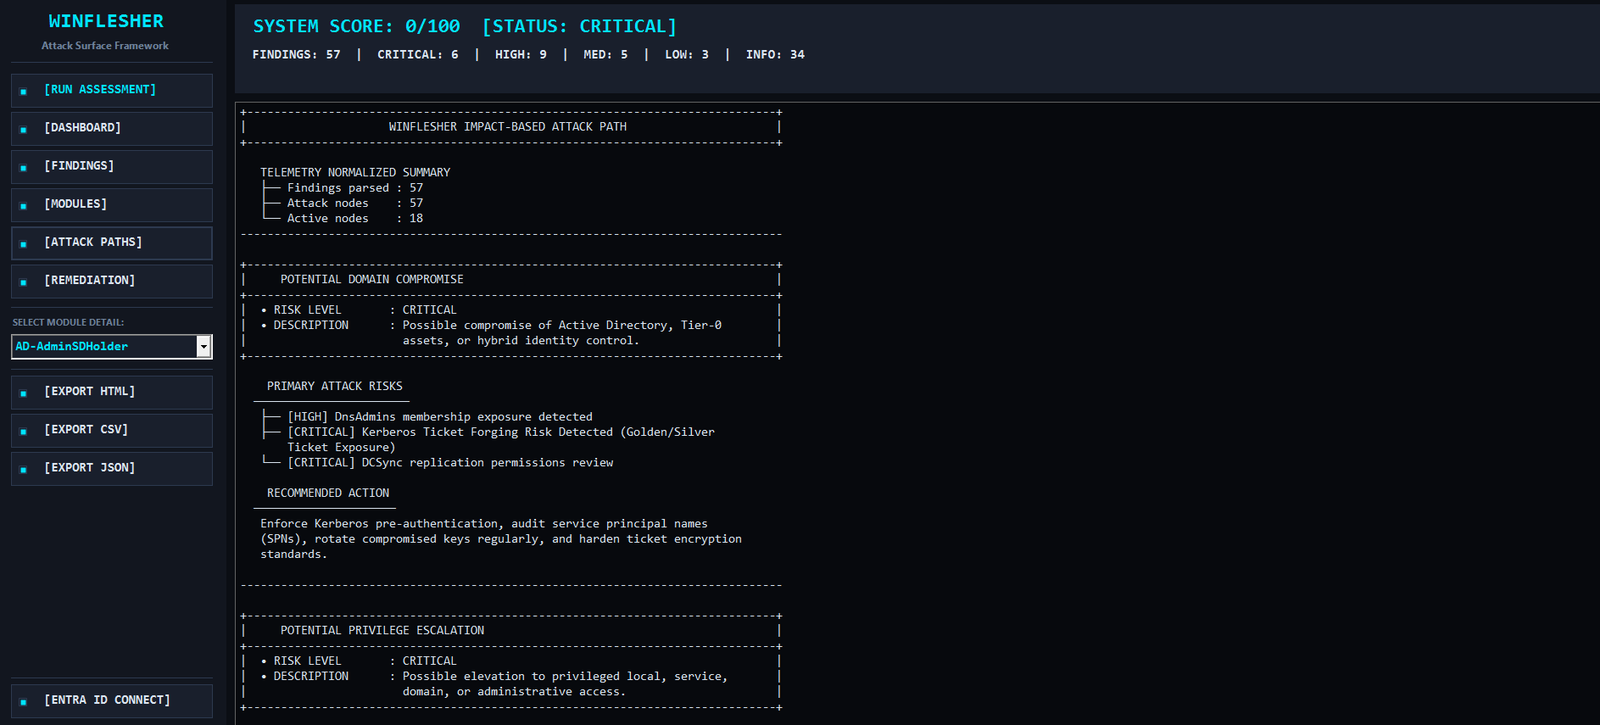 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 kaleth4/cve-2026-20180
In-depth technical analysis of Cisco ISE RCE vulnerabilities, including exploitation techniques, evasion methods, and remediation strategies for…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 dievus/powershellforpentesters
Course repository for PowerShell for Pentesters Course
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.