

sliver-gui
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
cloud-securitycommand-and-controllateral-movement+7
180
sliverarmory/sliver-guiCross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
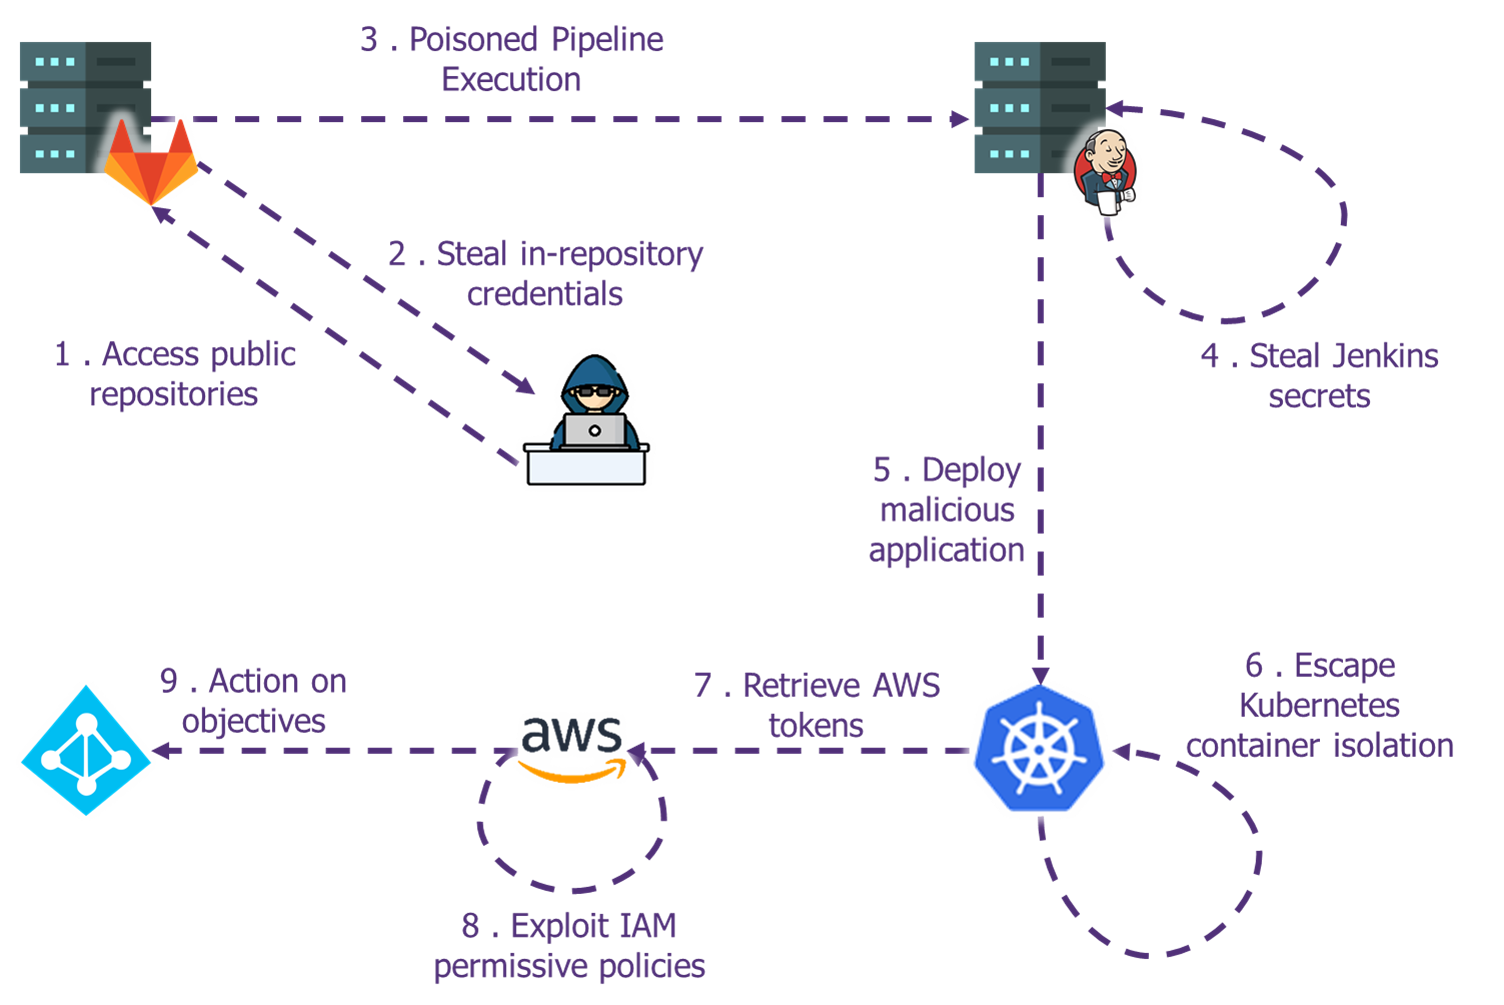 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 mayyhem/maestro
Abusing Azure services over C2
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 mrk336/patch-the-path-cve-2025-55234-detection-defense
This playbook outlines detection, containment, and remediation strategies for CVE-2025-55234, a critical Windows SMB privilege escalation flaw.
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…