
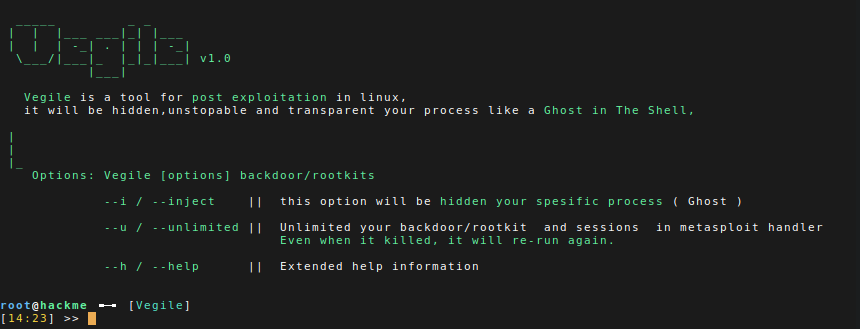
Vegile
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
exploit-frameworkslateral-movementpayload-generation+4
752
screetsec/vegileThis tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 horizon3ai/ivanti-epm-coercion-vulnerabilities
Proof of concept exploit for Ivanti EPM CVE-2024-13159 and others
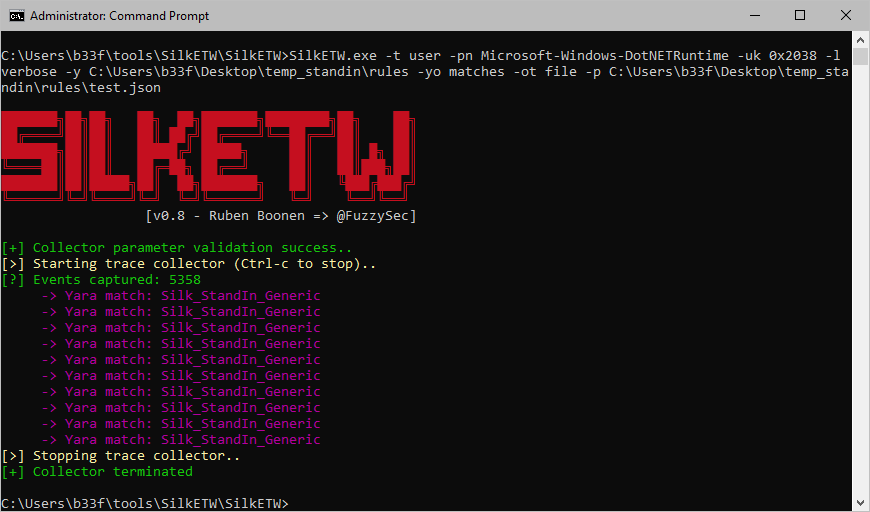 fuzzysecurity/standin
StandIn is a small .NET35/45 AD post-exploitation toolkit
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
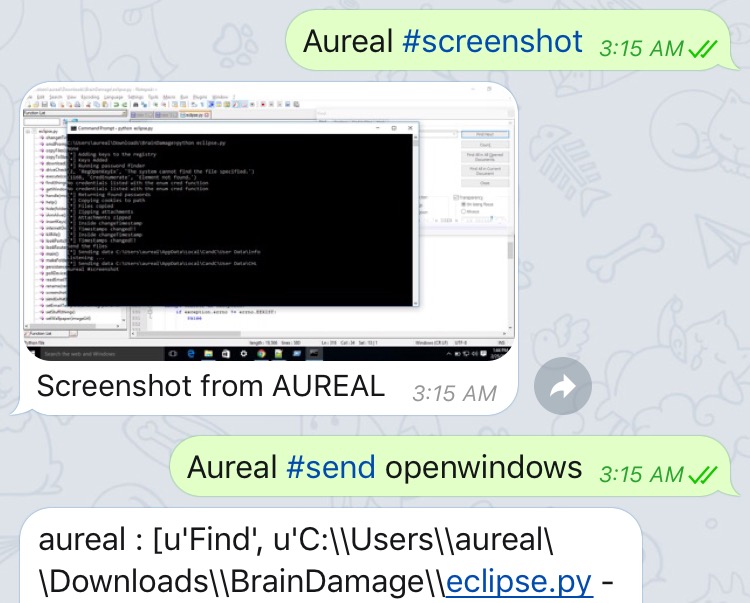 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server
 redteamoperations/pivotsuite
Network Pivoting Toolkit
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 nccgroup/chuckle
An automated SMB relay exploitation script.
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.